
Maersk NotPetya Attack: Recovery Time and Cost (2026)
- Maersk and NotPetya in 2026: the short answer
- Timeline: from the outbreak to the indictment
- What changed since 2018
- Lessons and risks for companies today (our analysis)
- Steps that would have shortened Maersk's outage
- What is still unknown
- Our original 2018 report
- "Basically average" cybersecurity management is not enough for companies
- NotPetya affected multiple high-profile organizations in 2017
- UPDATE: Russia is accused of being responsible for the cyber attack in June
- Related guides on 2-Spyware
Maersk and NotPetya in 2026: the short answer
Maersk needed about 10 days to rebuild its IT systems after NotPetya struck in June 2017. Chairman Jim Hagemann Snabe said the company reinstalled 4,000 servers, 45,000 PCs and 2,500 applications, and put the cost at $250 to $300 million. Those figures come from his World Economic Forum talk covered in our original report below.
Later reporting filled in how close the recovery came to failing. WIRED found that every Maersk domain controller was wiped except one in Ghana, which survived only because a power outage had taken it offline.[6] In October 2020 the U.S. Justice Department charged six Russian GRU officers over NotPetya and other attacks.[7]
| Question | Answer |
|---|---|
| When did it hit? | June 27, 2017[4] |
| How long was the recovery? | About 10 days for the full IT rebuild, per Maersk's chairman |
| What was rebuilt? | 4,000 servers, 45,000 PCs and 2,500 applications |
| What did it cost? | $250 to $300 million, per Maersk; staff told WIRED the real figure may be higher[6] |
| How did it get in? | Through M.E.Doc, Ukrainian tax software installed on a Maersk computer[8] |
| Who was blamed? | Officers of GRU Unit 74455, according to a 2020 U.S. indictment[7] |
Timeline: from the outbreak to the indictment
| Date | Event |
|---|---|
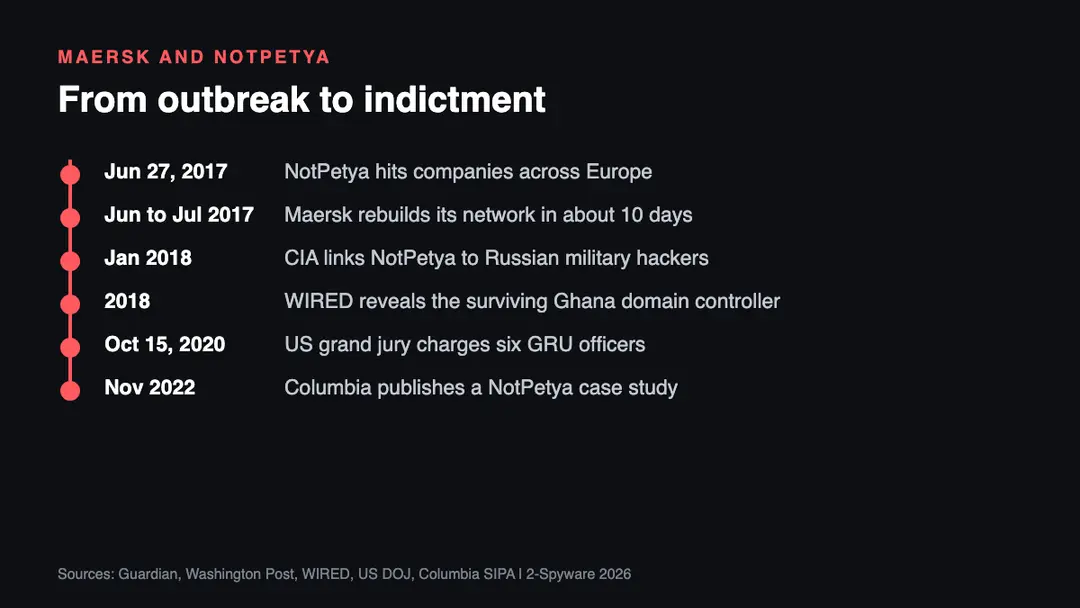
| June 27, 2017 | The NotPetya attack strikes companies across Europe, Maersk among them[4] |
| Summer 2017 | Maersk rebuilds servers, PCs and applications in about 10 days while running parts of its business by hand |
| January 2018 | The CIA concludes that Russian military hackers were behind NotPetya[5] |
| 2018 | WIRED reports the lone surviving domain controller in Ghana[6] |
| October 15, 2020 | A U.S. grand jury indicts six officers of GRU Unit 74455[7] |
| November 2022 | Columbia University publishes a case study on NotPetya and Maersk[8] |
What changed since 2018
Our 2018 report relied on what Maersk's chairman said in public. The later accounts add the detail that matters most for other companies. Maersk had around 150 domain controllers set to sync with each other, so each could back up the rest. That plan failed because NotPetya wiped them all at once.[6]
The one copy that survived sat in Ghana. Its link was too slow to send the data, so Maersk sent a Ghanaian employee with it to Nigeria, where he handed it to another employee for the rest of the trip to the recovery team.[6][8] WIRED also reports that some Maersk servers still ran Windows 2000 before the attack, and that staff suspected the official cost was low.[6]
The legal picture also moved. The 2020 indictment names six GRU officers and says NotPetya alone caused nearly $1 billion in losses to just three victims named in the case.[7] The charges are accusations, and the defendants are presumed innocent.[7] We found no report that any of them has been tried, as of 2026.
Lessons and risks for companies today (our analysis)
NotPetya looked like ransomware but worked as a wiper. Our reading of the Maersk case points to a few risks that still apply in 2026.
- Supply chain software. Maersk was exposed through a routine tax program used in Ukraine.[8] Any trusted update channel can carry malware.
- Synced backups are not offline backups. Data that replicates instantly can be destroyed instantly.[6]
- Old systems. Unsupported servers make a fast spread easier and a clean rebuild harder.[6]
- Flat networks. The worm moved from one office to offices and ports worldwide within minutes.[8]
- Fake ransom notes. Paying a wiper does not bring data back, so a ransom demand is not proof that recovery is possible.
Steps that would have shortened Maersk's outage
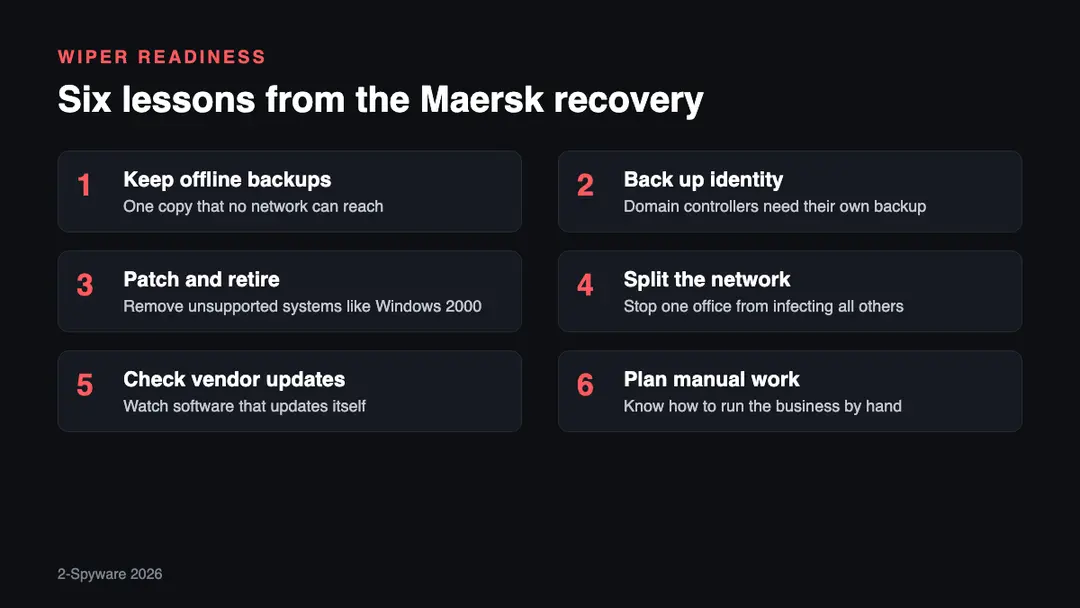
1. Keep offline backups. Keep at least one copy of critical data that no live network can reach. Maersk was saved by an accident, a server that happened to be offline.[6]
2. Back up identity systems. Domain controllers hold the map of who can reach what. Without them, Maersk staff said they could not recover anything.[6] Back them up on their own and test the restore.
3. Patch and retire old systems. NotPetya used the EternalBlue exploit against Windows machines.[3] Patch fast and replace software that no longer gets updates.
4. Split the network. Separate offices, factories and ports so that one infected site cannot reach all others at once.
5. Check vendor updates. Know which programs update themselves and from where. Watch for unusual behaviour right after an update.
6. Plan for manual work. Maersk kept much of its work going by hand during the rebuild. Write down how your key processes would run without computers, and practise it. Our virus removal guides cover the home side of ransomware cleanup.
What is still unknown
- The final cost of NotPetya to Maersk. Staff told WIRED they suspected the official figure was low.[6]
- Whether any of the six charged GRU officers will ever face trial. We found no report of an arrest as of 2026.
- How many companies still rely on synced backups alone. We found no reliable survey on that.
Our original 2018 report
The text below is our report as first published in 2018. We keep it unchanged for the record; the sections above bring it up to date.
The chairman of the logistics giant Maersk, Jim Hagemann Snabe, announced the full extent of the damages caused by the ransomware epidemic in the World Economic Forum. The company was hit by NotPetya[1] virus last summer. The cyber assault cost $250-$300 million and required 10 days to recover fully.
Due to the ransomware attack in June 2017, Maersk's entire IT infrastructure had to be shut down. 4000 new servers, 45,000 new PCs, and 2500 applications had to be reinstalled in the short period.
Snabe came from an IT industry and was expecting the full operation to last around six months. It is remarkable that the employees and partners managed to achieve the goal in just ten days, however.
While the work was on-going, the entire company had to process extensive amounts of shipping containers manually. Considering that Maersk operates in 121 countries, serving 343 ports, the task required tremendous efforts. While operating manually, the company managed to keep up with 80% of their typical workload.
Considering the damages caused by the cyber attack, Maersk chairman gave credit to "human resilience" which made it possible to overcome the dangerous ransomware strike.
"Basically average" cybersecurity management is not enough for companies
The damage caused by NotPetya was enormous and proved that businesses have to take more responsibility and put more effort into cyber security. Snabe claims that they had "basically average" cyber security management; however, the attack was a "wake-up call" to think about higher security standards.
Therefore, he urged global organizations, technology companies, and law enforcement to cooperate and create a more secure digital world. He explained that being good at cybersecurity can transfer into a competitive advantage. No matter how big or small the organization is – the virtual security could be breached at any time if no proper measures are undertaken.
However, human resilience is still an issue. Though, Snabe told that Maersk would be more digitalized in the future:
The next level of dependency is everything will be digital — all the documents will be digital, the boats will be autonomous, and hence the criticality of the infrastructure becomes even more urgent, and you cannot overcome with human resilience anymore.
NotPetya affected multiple high-profile organizations in 2017
Maersk was not the only giant which was affected by the treacherous ransomware. Similarly to Merck, FedEx[2] was hit with $310m bill, while TNT and WPP restrained themselves from revealing their losses.
NotPetya, a variant of Petya ransomware[3] that emerged in March 2016, started spreading mid-last year and was suspected of infecting IT infrastructure in Ukraine. Malware used NSA exploit EternalBlue[4] to penetrate Microsoft Windows machines.
NotPetya ransomware caused the worldwide hoax in June. Malware hit hundreds of organizations and companies in the United States, Russia, France, and the United Kingdom. However, the biggest damage was done to Ukraine.
UPDATE: Russia is accused of being responsible for the cyber attack in June
Security researchers assume that NotPetya attack was created and held by Russia in order to target organizations in Ukraine.These countries have a tense relationship, so political reasons seem legit to arrange a cyber attack too. But Russia did not accept responsibility.
However, Central Intelligence Agency (CIA) announced that the attack was held by Russian military hackers[5] in January 2018. The attack is said to be a part of "hybrid warfare" that combines traditional military aggression with cyber attacks to dominate in the country.
According to the investigation, Russian hackers used "watering hole" attack to infect the specific website that provides updates to M.E. Doc – one of the two accounting programs used by Ukraine companies.
Additionally, attackers hacked into industrial control system networks to cause havoc in the country. Finally, they used a ransomware-type cyber threat to camouflage state-based cyber attack. Typically, demands to pay the ransom for data recovery are held by individuals or hacking groups.
Related guides on 2-Spyware
Frequently asked questions
How long did it take Maersk to recover from NotPetya?
About 10 days for the full IT rebuild, according to chairman Jim Hagemann Snabe. In that time the company reinstalled 4,000 servers, 45,000 PCs and 2,500 applications. He had expected the job to take around six months, and staff ran much of the business by hand meanwhile.
How much did NotPetya cost Maersk?
Maersk put the cost at $250 to $300 million. Several Maersk staff told WIRED they suspected the accountants had set the figure low, because the company also paid customers for rerouting and storing stuck cargo.{6} A 2020 U.S. indictment says NotPetya caused nearly $1 billion in losses to three named victims.{7}
What did Jim Hagemann Snabe say about the 2,500 applications?
He said Maersk had to reinstall 2,500 applications along with 4,000 servers and 45,000 PCs within about 10 days. He described the company's earlier security as basically average and called the attack a wake-up call. He also credited human resilience for keeping about 80 percent of normal work going.
How did NotPetya get into Maersk?
Through M.E.Doc, an accounting and tax program used in Ukraine, which was installed on a Maersk computer.{8} The attackers abused the program's update channel, and the worm then spread across Maersk's network to offices and ports worldwide within minutes.{8}
Was NotPetya ransomware?
It looked like ransomware but acted as a destructive attack. Our original report notes that the ransom screen served as camouflage for a state attack. The U.S. Justice Department later called NotPetya some of the most destructive malware to date and charged six GRU officers.{7}
Who was behind the NotPetya attack?
Russian military intelligence, according to U.S. findings. The CIA linked the attack to Russian military hackers in January 2018,{5} and in October 2020 a U.S. grand jury charged six officers of GRU Unit 74455.{7} Russia has denied responsibility, and the charges remain accusations.
Sources
- 2-spyware. Security and spyware news
- Financial Times. News website with a special emphasis on business and economic news
- Internet Storm Center. A global cooperative cyber threat / internet security monitor and alert system.
- The Guardian. Latest US news, world news, sports, business, opinion, analysis and reviews
- The Washington Post. Breaking news and analysis on politics, business, world national news, entertainment more
- WIRED
- U.S. Department of Justice
- Columbia University SIPA
Log in to comment
No comments yet. Be the first.