
Microsoft OneNote Malware and Emotet: 2026 Update
- OneNote malware in 2026: the short answer
- Timeline: Emotet, OneNote and Microsoft's fix
- What changed since 2023
- Risks around OneNote and email attachments (our analysis)
- How to handle a suspicious OneNote file
- What is still unknown
- Our original 2023 report
- The new distribution method
- The Emotet campaign using OneNote files
- The aftermath
- Protection measures
- Related guides on 2-Spyware
OneNote malware in 2026: the short answer
Microsoft OneNote is safe to use, but OneNote files were a popular way to send malware in 2023. The Emotet botnet attached .one files to reply-chain emails and hid a script called click.wsf under a fake View button, as our original report below describes.[1] Microsoft answered by making OneNote block embedded files with dangerous extensions. The change began rolling out with Version 2304, reaching the Current Channel on May 1, 2023.[4]
By default OneNote now blocks the same extensions that Outlook, Word, Excel and PowerPoint block.[4] That closes the exact trick Emotet used. The protection covers OneNote for Microsoft 365 and certain Office versions on Windows, so older or unpatched installs can still be exposed.[4] We found no Emotet campaign using OneNote reported for 2025 or 2026 in the sources we read.
| Question | Answer |
|---|---|
| What did Emotet send? | OneNote attachments with a hidden click.wsf script under a fake View button[1] |
| Did Microsoft fix it? | Yes. OneNote blocks direct opening of embedded files with dangerous extensions[4] |
| Since when? | Version 2304; Current Channel on May 1, 2023, Monthly Enterprise on June 13, 2023[4] |
| Which apps are covered? | OneNote for Microsoft 365 and certain retail and volume licensed Office versions on Windows[4] |
| Which are not? | OneNote on Mac, Android, iOS, the web and OneNote for Windows 10, per Microsoft[4] |
| How big was Emotet? | About 1.6 million computers infected between April 2020 and January 2021, per the U.S. Justice Department[6] |
Timeline: Emotet, OneNote and Microsoft's fix
| Date | Event |
|---|---|
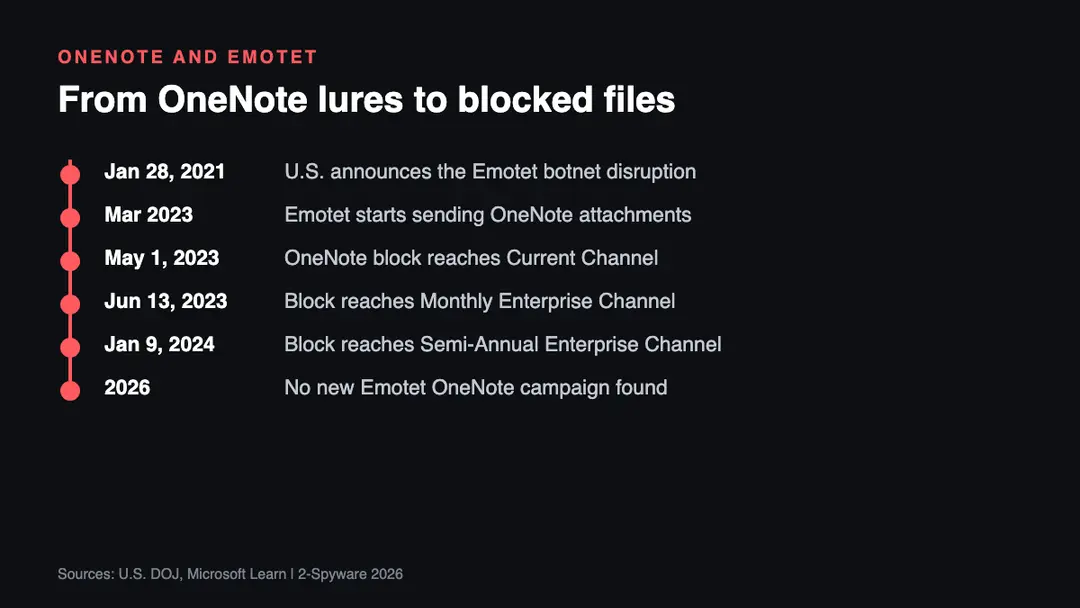
| January 28, 2021 | The U.S. Justice Department announces that the Emotet botnet was disrupted in an international operation[6] |
| March 2023 | Researcher Abel spots Emotet spam with malicious OneNote attachments[1] |
| May 1, 2023 | The OneNote embedded file block arrives in the Current Channel, Version 2304[4] |
| June 13, 2023 | The block arrives in the Monthly Enterprise Channel[4] |
| January 9, 2024 | The block arrives in the Semi-Annual Enterprise Channel, Version 2308[4] |
| 2026 | We found no new Emotet campaign using OneNote files in the sources we read |
What changed since 2023
In 2023 the only defence was a warning dialog that many users clicked away, plus Group Policy settings that administrators had to set themselves. Our original report advised admins to use those settings until Microsoft added more protection. That protection arrived. OneNote now refuses to open embedded files with dangerous extensions directly, and BleepingComputer reported that the list covers about 120 extensions.[4][5]
Admins can still adjust the list. The policy "Block additional file extensions for OLE embedding" adds more extensions, and "Allow file extensions for OLE embedding" lets chosen ones through.[4] Microsoft notes these policies work only with Microsoft 365 Apps for enterprise, not Microsoft 365 Apps for Business.[4] Allowing an extension back can reopen the risk, so do it only with a clear business need.
Emotet itself has a long history of disruption and return. The U.S. Justice Department said in January 2021 that it infected about 1.6 million computers and spread mainly through spam with malicious attachments or links.[6] The 2023 OneNote wave showed it had come back. We could not confirm its activity level in 2026.
Risks around OneNote and email attachments (our analysis)
The points below are our analysis of how attackers adapt after a block like this. They are not quoted from Microsoft.
- Old or unsupported Office installs. The block covers Microsoft 365 and listed Office versions on Windows.[4] A machine that never receives updates keeps the 2023 risk.
- Admin exceptions. An allowed extension added by policy can let a dangerous file through again.[4]
- Reply-chain emails. Emotet replied inside real email threads, so the message looked familiar.[1] A known sender is not proof of a safe file.
- "Protected document" lures. Any file that asks you to double-click a button or enable content to see the text is a warning sign.
- Moving to other file types. When one format is blocked, attackers switch formats. The 2023 move from Office macros to OneNote is an example, as our original report explains.
How to handle a suspicious OneNote file
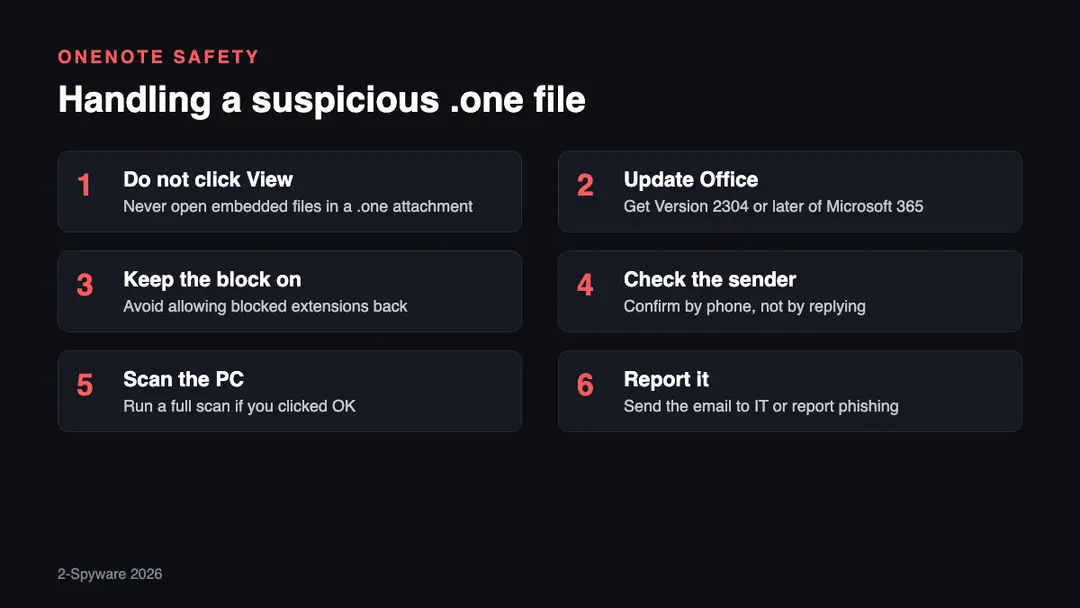
1. Do not click View or OK. In the 2023 campaign, the View button hid a script and the OK button in the warning ran it.[1]
2. Update Office. The OneNote block arrived with Version 2304 for most channels.[4] Install the latest updates on every Windows PC.
3. Keep the default block. Admins should not add allowed extensions unless they must.[4] Our original report also explains how Group Policy can block embedded files entirely.
4. Check the sender another way. A reply inside an old thread can be fake. Call or message the person before you open an unexpected attachment.
5. Scan the PC if you already clicked. Emotet downloads a DLL and can bring more malware, as our original report notes. Our virus removal guides explain the cleanup.
6. Report the email. Forward it to your IT team or follow our guide on how to report phishing.
What is still unknown
- How active Emotet is in 2026. We found no current vendor or government report on it.
- Whether attackers found ways around the OneNote block on unpatched systems. We found no report of that.
- Whether Microsoft will extend the block to OneNote on Mac, mobile and the web, which it lists as not affected.[4]
Our original 2023 report
The text below is our report as first published in 2023. We keep it unchanged for the record; the sections above bring it up to date.
After a three-month hiatus, the Emotet malware has reappeared with a new distribution method. Emotet is a malware botnet known for its rapid spread and ability to infect devices. Historically, this malware was distributed via Microsoft Word and Excel attachments containing malicious macros. When a user opens the attachment and enables macros, a DLL is downloaded and executed, resulting in the installation of the Emotet malware on the device.
Once installed, the malware will steal email addresses and content for future spam campaigns. The malware also downloads additional payloads that allow it to gain initial access to the corporate network. This access is used to carry out cyberattacks against the company, such as ransomware attacks, data theft, cyber espionage, and extortion.
The new distribution method
After being one of the most widely distributed malware in the past, Emotet took a break near the end of 2022. However, after three months of inactivity, the botnet was reactivated and began sending malicious emails all over the world earlier this month. This initial campaign, however, was flawed because it continued to use Word and Excel documents with macros.
This campaign would only infect a few people because Microsoft now automatically blocks macros in downloaded Word and Excel documents, including those attached to emails. As a result, it migrated to Microsoft OneNote files, which have become a popular method for malware distribution since Microsoft began blocking macros.
The Emotet campaign using OneNote files
The threat actors have now begun distributing the Emotet malware using malicious Microsoft OneNote attachments in an Emotet spam campaign first spotted by security researcher Abel.[1] These attachments are distributed through reply-chain emails that masquerade as guides, how-tos, invoices, job references, and other documents. Microsoft OneNote documents attached to the email display a message stating that the document is protected. It then asks users to double-click the 'View' button to properly display the document.
The aftermath
A malicious VBScript file called 'click.wsf' has been hidden beneath the "View" button by the threat actors. This VBScript contains a heavily obfuscated script that downloads and executes a DLL from a remote, most likely compromised, website. While Microsoft OneNote will display a warning when a user attempts to open an embedded file, many users simply click the 'OK' button to dismiss the alert.
When the user clicks the OK button, the embedded click.wsf VBScript file from OneNote's Temp folder is executed using WScript.exe from the Temp folder. After that, the script will download the Emotet malware as a DLL[2] and place it in the same Temp folder. It will then use regsvr32.exe to launch the randomly named DLL.
The malware will then run quietly on the device, stealing email addresses and waiting for further commands from the command and control server. While it is unknown what payloads this campaign ultimately drops, it frequently results in the installation of Cobalt Strike or other malware. Threat actors working with Emotet can use these payloads to gain access to the device and use it as a springboard to spread further in the network.
Protection measures
With multiple malware campaigns using these attachments, Microsoft OneNote has become a massive malware distribution problem. As a result, Microsoft will improve protections[3] against phishing documents in OneNote, but there is no set timeline for when this will be available to everyone.
Group policies can be configured by Windows administrators to protect against malicious Microsoft OneNote files by either blocking embedded files in OneNote entirely or specifying specific file extensions that should be prevented from running. It is strongly advised that Windows administrators use one of these options until Microsoft adds additional security to OneNote.
Related guides on 2-Spyware
Frequently asked questions
What is Microsoft OneNote?
Microsoft OneNote is Microsoft's digital notebook app for notes, drawings and attached files. It is a normal, safe program. The problem described here is OneNote files sent by criminals, which hid scripts behind fake buttons to install Emotet in 2023.{1}
Can a OneNote file contain malware?
Yes, a .one file can carry embedded files, and Emotet hid a click.wsf script in them in 2023.{1} Since Version 2304, OneNote blocks direct opening of embedded files with dangerous extensions on Microsoft 365 and certain Office versions for Windows.{4}
Does Microsoft block malicious OneNote attachments now?
Yes. OneNote blocks embedded files with the same dangerous extensions that Outlook, Word, Excel and PowerPoint block. The change reached the Current Channel on May 1, 2023 and the Semi-Annual Enterprise Channel on January 9, 2024.{4}
Is OneNote on Mac or the web protected the same way?
No. Microsoft says the block does not apply to OneNote on Mac, Android, iOS, OneNote for the web or OneNote for Windows 10.{4} Treat unexpected .one attachments with care on those platforms and do not open embedded files from unknown senders.
What is Emotet?
Emotet is a malware botnet that spreads mainly through spam with malicious attachments or links. The U.S. Justice Department said it infected about 1.6 million computers between April 2020 and January 2021.{6} It later came back, including the 2023 OneNote campaign.
Is Emotet still active in 2026?
We could not confirm it. We found no 2025 or 2026 vendor or government report of a new Emotet campaign in our searches. The 2023 OneNote wave showed that the botnet can return after a pause, so attachment safety rules still apply.{1}
Log in to comment
No comments yet. Be the first.