The Hacker News reports that UAT-11985 used fake event invites and malicious QR codes…

The Hacker News reports that UAT-11985 used fake event invites and malicious QR codes to target people affiliated with Taiwan research organizations. The phishing pages copied Google login screens to steal Google account credentials and MFA codes, so Windows users should be careful with event invitations, avoid scanning unknown QR codes, and check the sender and sign-in page before entering any login details.

The Hacker NewsUAT-11985 Uses Fake Event Invites to Target Taiwan Research Affiliates With Google AitM Phishing

Source: thehackernews.com

More in this rubric
all →

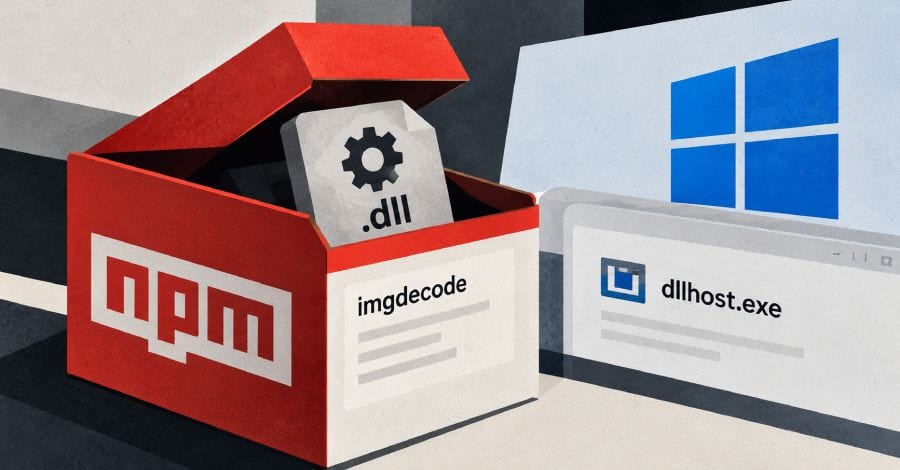
The Hacker News reports that a malicious npm package called imgdecode is part of the MALFEX campaign targeting Windows systems. The package hides a loader in a Windows native addon and can download encrypted shellcode from GitHub, then inject it into a new dllhost.exe process. Windows users should avoid untrusted npm packages and check what software they install from developer tools and command lines.

The Hacker NewsMALFEX npm Package 'imgdecode' Hides Shellcode Loader in Windows Native Addon

Source: thehackernews.com

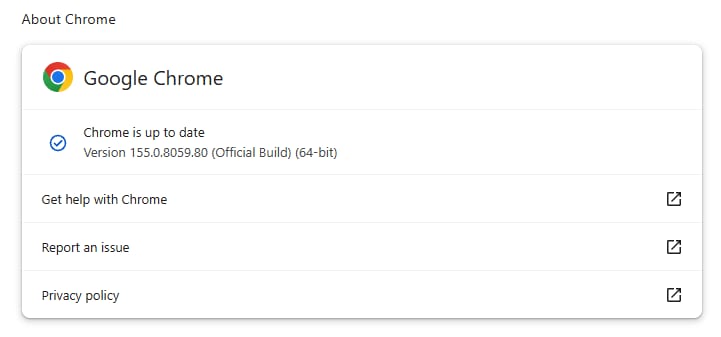
Malwarebytes Labs reports that Google has released Chrome 155.0.8059.79/.80 for Windows, and the update fixes 37 security flaws, including seven rated Critical. The easiest option is to let Chrome update automatically, but if the browser has not closed in a while or an extension blocks the update, open About Google Chrome and relaunch after checking for updates.

Malwarebytes LabsUpdate Chrome: Google fixes 37 security flaws, including seven critical bugs

Source: malwarebytes.com

SecurityWeek reports that Darktrace found a new malware campaign spreading a Rust-based RAT called CikaBika Bot through document-themed lures. Victims get a PDF with a Windows shortcut that opens a decoy document and launches hidden PowerShell to run the malware, which can steal system information, take screenshots, and exfiltrate data through Discord and Ngrok. Windows users should avoid opening unexpected PDF or Word-themed files.

SecurityWeekCikaBika Bot RAT Uses Discord for C&C

Source: securityweek.com

5,602 members already hereReading, writing, commenting and voting. 0 verified · 327 joined this year