KnowBe4 reports that researchers at ESET found a phishing campaign targeting YouTubers…

· in brief

KnowBe4 reports that researchers at ESET found a phishing campaign targeting YouTubers with phony sponsorship offers. The emails are personalized, use fake brand identities and domains, and try to get victims to grant access to their Google accounts. Users should verify sponsorship offers through official channels, check sender domains carefully, and not approve sign-in or access requests they do not recognize.

KnowBe4Phishing Attacks Target YouTubers With Phony Sponsorships

Source: blog.knowbe4.com

More in this rubric
all →

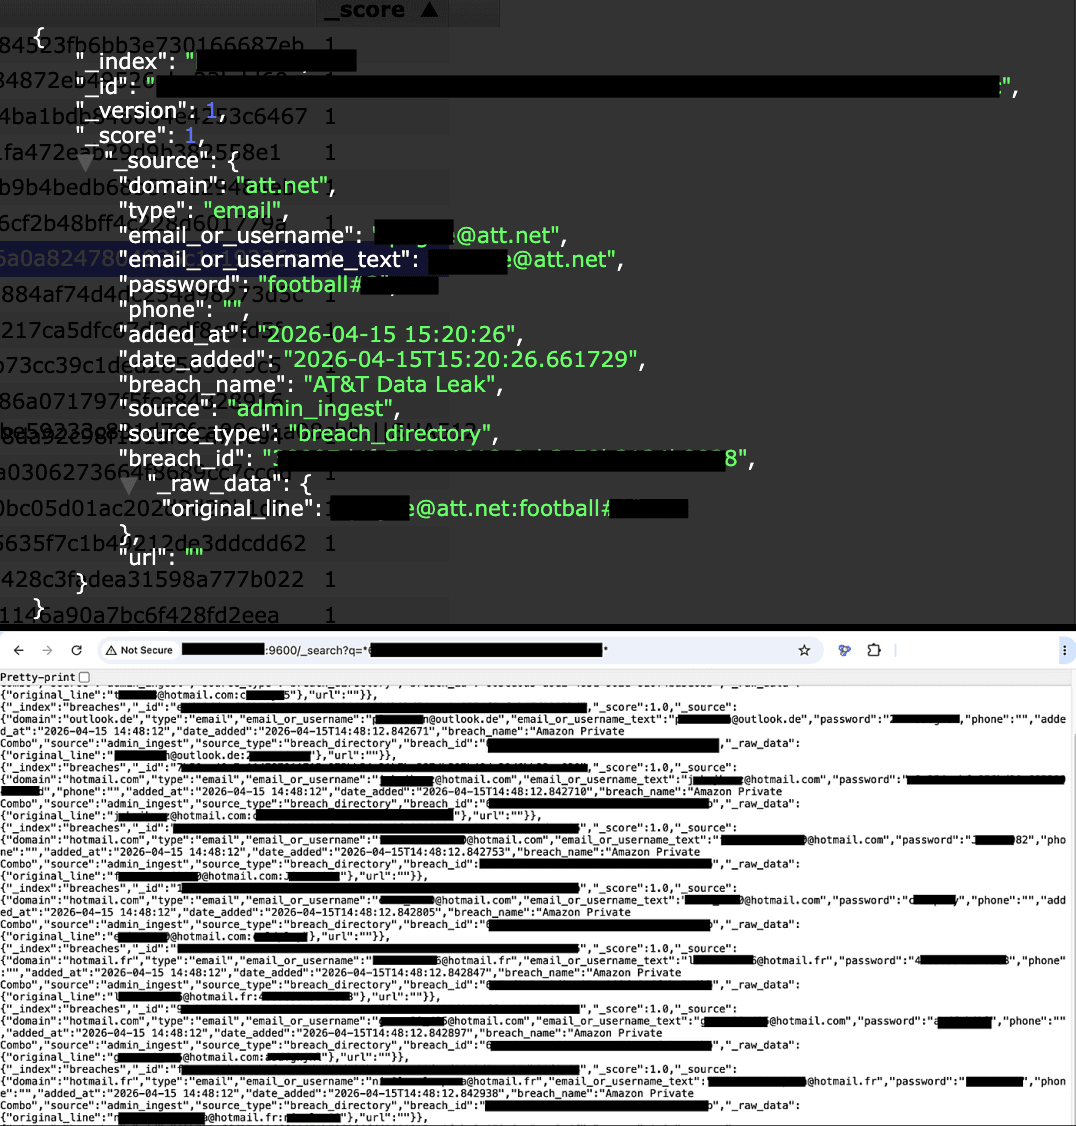
Hackread.com reports that an unprotected database linked to Vibetech exposed 13.7 million records, including names, phone numbers, email addresses, plaintext passwords and bank account details. The report says exposed passwords can be used to access email, shopping or financial accounts, steal personal information, make fraudulent purchases or impersonate victims, so users should change reused passwords and watch for phishing and account-takeover attempts.

hackread.comVibetech Database Exposes 13.7M Records Including AT&T and FBI Data

Source: hackread.com

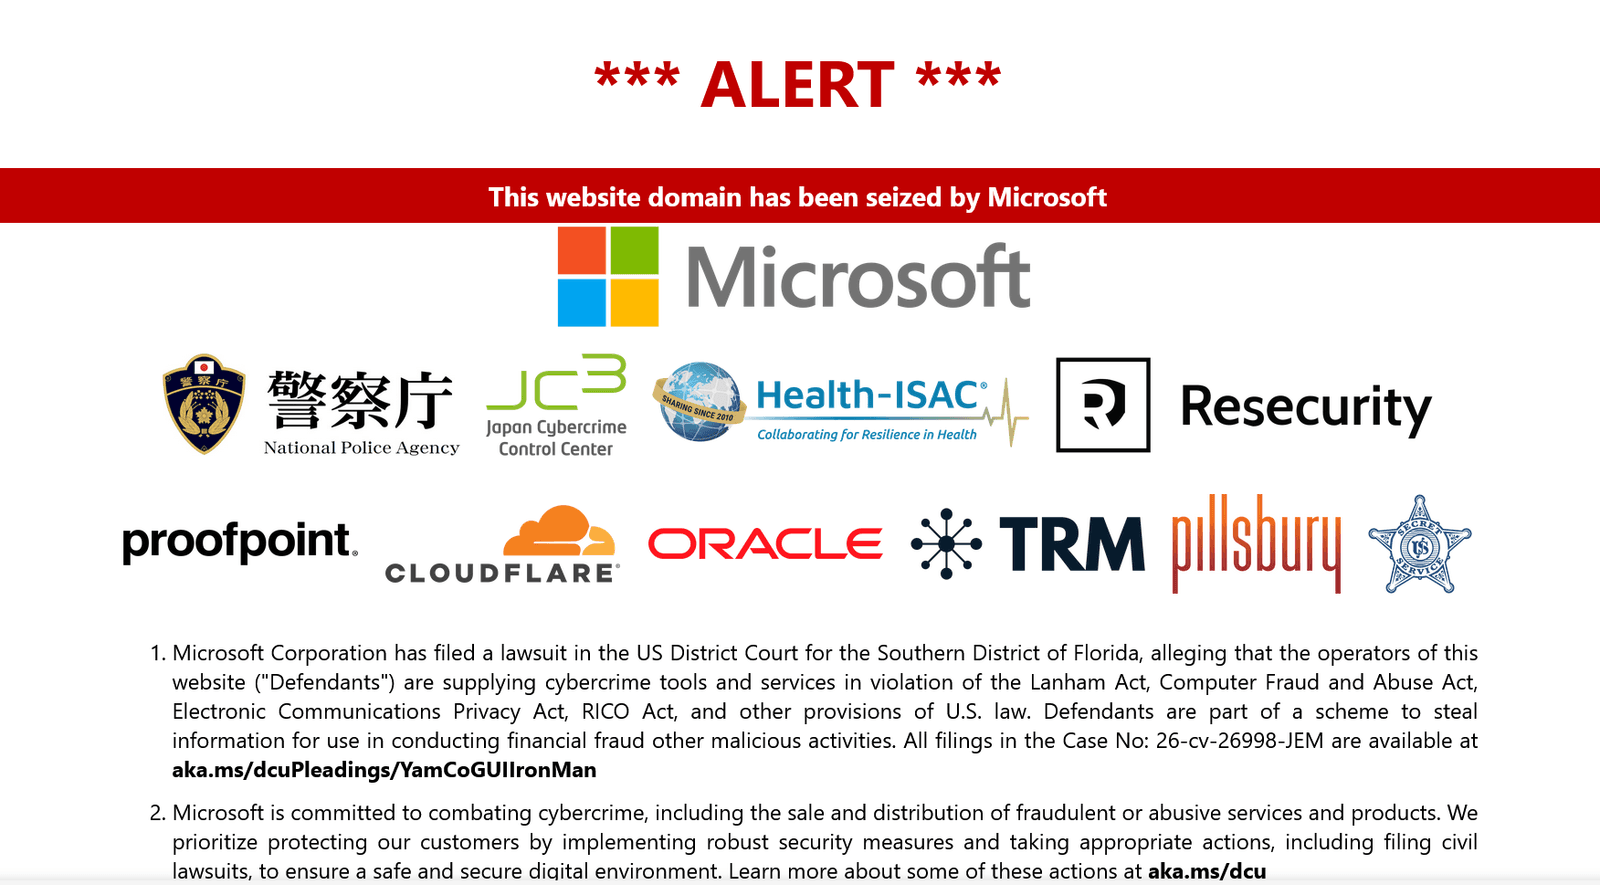
Hackread.com reports that Microsoft and Health-ISAC have seized and redirected domains linked to a Chinese-language cybercrime marketplace that supplied fraudulent accounts, phishing kits and infrastructure. The services helped send more than one billion malicious messages and impersonated banks, retailers, delivery services and government agencies. Windows users should be careful with messages asking for logins or payments, and review sign-in activity, inbox rules, forwarding changes and suspicious access to cloud accounts.

hackread.comMicrosoft Seizes YAM Store and Phishing Kit Domains Linked to 1B Malicious Messages

Source: hackread.com

KnowBe4 reports that Microsoft is tracking phishing campaigns that use meeting invitations, PDF-themed lures, software update prompts, and other social-engineering content to deliver a masqueraded MSP360 installer. The installer is a legitimate remote monitoring and management tool that attackers abuse to gain access to affected devices and keep control after the first compromise. Users should be cautious with unexpected download prompts and messages that impersonate document-sharing, collaboration, or software pages.

KnowBe4Business-Themed Phishing Lures Deliver RMM Tools

Source: blog.knowbe4.com

5,584 members already hereReading, writing, commenting and voting. 0 verified · 309 joined this year