
Hitler ransomware: what it is and how to get your files back
Hitler ransomware is a Windows lock screen with a one-hour timer that claims your files are encrypted and asks for a 25 euro Vodafone card code. It does not encrypt anything: it removes file extensions and then deletes the files in your user profile, so protect the disk first and never pay.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Once you can reach the desktop, a full scan can check for the program behind the Hitler-Ransomware lock and anything it brought.
Do it yourself · free Remove Hitler ransomware yourself 4 steps, about 12 minutes, no software needed.
Start the steps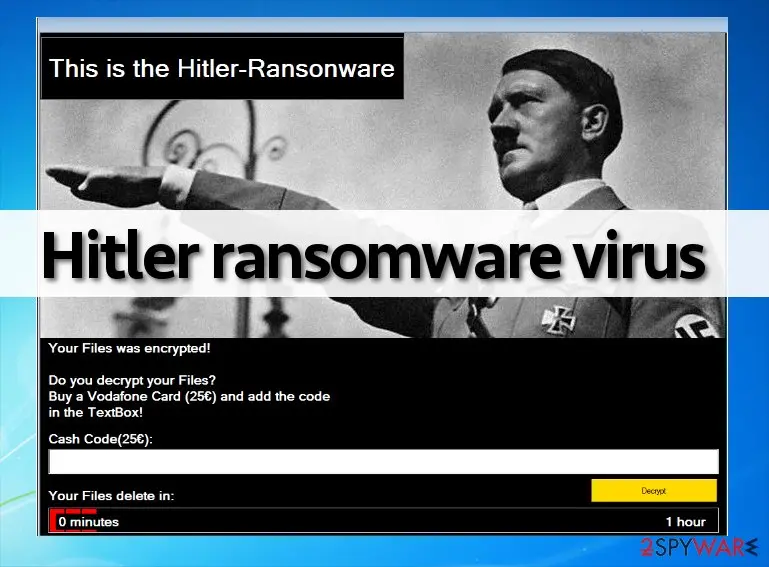
Hitler ransomware: summary
| Type | Screen locker and file deleter: it fakes encryption, strips file extensions and deletes the user profile after a crash |
|---|---|
| Risk | High if it runs: files in the profile are deleted at the next sign-in; the Recycle Bin is skipped |
| Symptoms | A full-screen window with Hitler's picture, a Vodafone code box and a one-hour bar; files without extensions; Task Manager and Command Prompt closing |
| How to get rid of it | Do not sign in to the infected Windows: delete firefox32.exe from the Startup folder in the recovery environment, scan, then restore from backups |
| Our check | Source check on 5 October 2026 (BleepingComputer, Ivanti, Wikipedia, Tripwire); no sample run |
| First seen | 8 August 2016 (BleepingComputer); our first report 30 November 2017 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 12 more facts
| Name | Hitler ransomware (also Hitler-Ransonware, Adolf Hitler ransomware, CainXPii) |
|---|---|
| Encrypted file extension | None in the first version: it removes the extension; a later variant is reported to use .CainXPii, not confirmed |
| Ransom note | Not a file: a lock-screen window; the German note of the 2017 versions is a window too |
| Decryptor | Not needed for the first version: nothing is encrypted |
| Contact | No address on the first version; later ones show an e-mail address (see the versions chapter) |
| Detection names | No Microsoft detection name is known: we found none in the sources we read |
| Distribution | Bundled installers, disguised programs (Minecraft account dispenser, New Folder.exe), and the routes our 2017 report named |
| Damage | Extensions removed, then every file under the user profile deleted; processes taskmgr, utilman, sethc and cmd closed |
| Evidence | 2 write-ups by security sites; details still limited |
| Lock screen claims to be | Hitler-Ransomware |
| Free decryptor | No free decryptor is known (checked 5 October 2026) |
| Facts checked | 5 October 2026 |
Facts checked on 5 October 2026 against BleepingComputer's 2016 analysis, Ivanti, Wikipedia, Tripwire's January 2017 summary, Microsoft's startup and file-recovery pages and our 2017 screenshots. We did not run the malware.
What Hitler ransomware is
Hitler ransomware is a Windows program that pretends to be file-encrypting ransomware. It encrypts nothing: it strips the extensions from your files, shows a lock screen with a one-hour countdown, and then deletes the files in your user profile.
Our 2017 report called it a "crypto-virus", which it is not. This page follows BleepingComputer's technical analysis of August 2016, which found no encryption code.
- Also called
- Hitler-Ransonware (the spelling on its first lock screen), Adolf Hitler ransomware, Hitler 2 / CainXPii, "FINAL version of Hitler Ransomware"
- Written as
- A batch file turned into an installer, bundled with other applications (BleepingComputer)
- First reported
- 8 August 2016 by AVG analyst Jakub Kroustek; our report 30 November 2017
- Demand
- A cash code for a 25 euro Vodafone card, typed into a box on the lock screen
- Deadline
- One hour on a countdown
- Real damage
- Extensions removed, then the user profile deleted after a crash and restart
The first version was a test: its batch file says, in German, "This is a test, rather a Hello World" (BleepingComputer's translation). That is why the old guide called it "rather a silly joke". The joke does real damage, because the delete step works.
What we checked and what we did not
Hitler ransomware is a program, not a website, so there was no site test. This is a source check, and we ran no sample.
Hitler ransomware · source check · 5 October 2026
- Technical analysisBleepingComputer's 2016 write-up lists the files, folders and the delete command; Ivanti and Wikipedia agree.
- Lock screenOur 2017 screenshot shows the picture, the 25 euro code box and the one-hour bar.
- Live sampleNot run. The removal and recovery steps follow the 2016 analysis and Microsoft's pages, not a test of ours.
- Later versionsThe 2017 versions have no second source, and whether they encrypt anything is not confirmed.
- Detection namesNone confirmed in the sources we read.
Harmless to read, destructive if run The lock screen is a bluff but the delete step is real. The latest version we know is from 2017, so a new infection is unlikely.
How Hitler ransomware behaves
What it does on the PC, step by step
The files are deleted at the first sign-in after the crash, not when the timer ends.
- 1
A batch file strips the extensions
It removes the extension from every file in Pictures, Documents, Downloads, Music, Videos, Contacts, Links and Desktop, and three Windows sample folders.
report.docxbecomesreport. - 2
Three files go to %Temp%
chrst.exe(lock screen),ErOne.vbs(a fake "The file could not be found!" error) andfirefox32.exe(the deleter). - 3
The deleter joins Startup
firefox32.exeis copied to the Common Startup folder, so it runs at every sign-in. - 4
The lock screen starts the timer
chrst.exeshows Hitler's picture, says your files were encrypted and asks for the Vodafone code. - 5
At zero, Windows is crashed
The program terminates
csrss.exe, which causes a blue screen and a restart. - 6
At the next sign-in, the files go
firefox32.exeruns a batch command that deletes every file under%UserProfile%.
Processes it keeps closing while it runs
- taskmgr
- utilman
- sethc
- cmd
Task Manager, Ease of Access, Sticky Keys and Command Prompt (BleepingComputer, 9 August 2016).
The command is del *.* /s /q, which, Ivanti notes, does not send files to the Recycle Bin.
The versions, from August 2016 to Minecraft in 2017
Only the first version has a published technical analysis. The rest come from Wikipedia, Tripwire and our own 2017 reports.
| Version | What it shows | Source |
|---|---|---|
| Hitler-Ransonware, August 2016 | English lock screen, 25 euro Vodafone code, one-hour timer; extensions removed, files deleted | BleepingComputer |
| Hitler 2 (CainXPii) | Same, with "ransomware" spelled correctly and no countdown | Wikipedia |
| "FINAL version", January 2017 | A German note and a contact e-mail address; title "You've infected by FINAL version of Hitler Ransomware!" | Tripwire, our screenshot |
| "Minecraft account dispenser", September 2017 | Obfuscated 8623o9d8423vgb.exe; a "Destroyer Ransomware" window with a German note; 10 euros in 24 hours; threatens to publish data on Dropbox | Our 2017 report only |
| "New Folder.exe", November 2017 | Looks like a folder; contact TheYuCheng@yeah.net; reported by Karsten Hahn | Our 2017 report only |
The January 2017 address in our screenshot reads 3r4wm0sn4r3lt1h@mail.com; our 2017 text spelled it a little differently, so check the picture. Wikipedia puts Hitler 2 before the FINAL version, so the FINAL one was not the first update, as we wrote. The price falls from 25 euros to 10. The German points to a German-speaking author of the test version, but nothing shows who the later victims were meant to be.
A short history, from 2016 to our 2017 report
8 August 2016
First report
BleepingComputer describes a test version that deletes files.
10 August 2016
Readers start asking
A reader asks how to protect a PC against Hitler ransomware.
January 2017
The FINAL version
Tripwire reports a lock screen announcing the "FINAL version", now with a German note and a mail address.
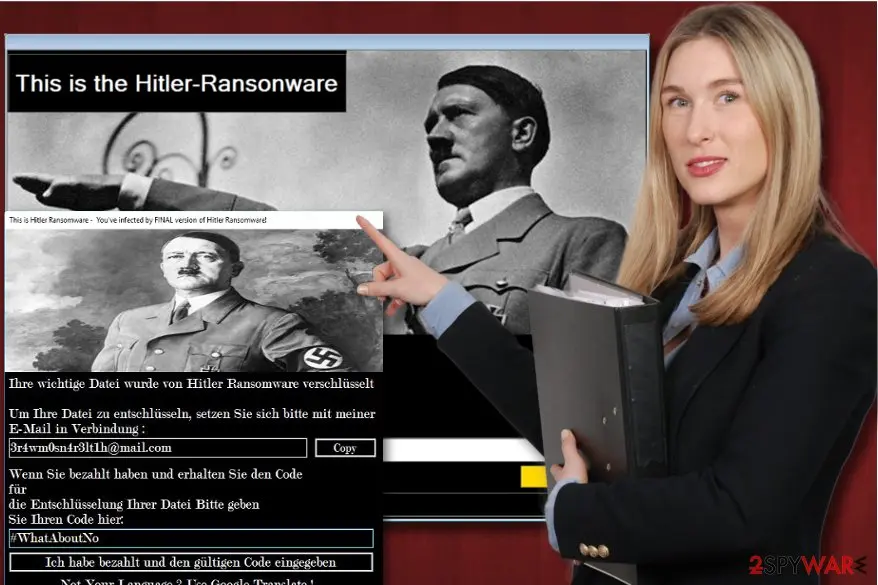
The FINAL version's German window (front) over the older lock screen, from our 2017 report. The woman and the pointing hand are report artwork, not part of the malware. September 2017
The Minecraft account dispenser
A reader asks whether a Hitler picture and a 10 euro demand after a Minecraft tool is a joke.
30 November 2017
Our report
We publish the guide after Karsten Hahn's report of the New Folder.exe version.
5 October 2026
Our recheck
We rewrote the guide: the malware deletes files, and the "encryption" is a bluff.
How it reaches PCs, and what it is not
BleepingComputer says the installer came bundled with other applications.
Our 2017 report added malicious e-mail attachments and corrupted links or ads, and showed disguises: a Minecraft account dispenser and a file that looks like a folder.
| Name | How it differs | What to do |
|---|---|---|
| Locky, CryptoWall, Cerber | Real encryption with keys held by the attacker | Look for a decryptor on No More Ransom; backups are the sure way |
| Police virus and other lockers | Block the screen, delete nothing | Safe Mode or System Restore |
| Hitler 2 (CainXPii) | The same idea without the countdown | Follow this guide and check that files open |
Was anything stolen?
No source describes data theft by Hitler ransomware, and the Dropbox publishing threat of the Minecraft version has nothing behind it that we found. The installer was bundled with other applications we cannot name, so scan for more and change your main passwords from a clean device if you find any.
What to do first, depending on where you are
Do not sign in to the infected Windows again until firefox32.exe is gone: the files are deleted at sign-in.
| Where you are | What to do |
|---|---|
| The lock screen is up, the timer running | Do not type a code or pay. Switch off with the power button and use the recovery steps below. |
| The PC restarted and shows the sign-in screen | Do not sign in. Switch off and use the recovery steps. |
| You signed in and the folders are empty | Stop using the PC and go to the recovery chapter. |
| Files have no extension but are still there | Copy them out, then add the extensions. |
- 1
Open the recovery environment
Switch on and switch off again with the power button when the Windows logo appears; after two or three interrupted starts Windows opens the recovery screen. Microsoft's Startup Settings route is Troubleshoot > Advanced options > Startup Settings > Restart. With BitLocker you need your recovery key.
- 2
Choose Command Prompt
Under Advanced options; the name can vary. We have not tested this on a live sample.
- 3
Find the Windows drive
Letters differ in recovery: run
dir C:\Users, thendir D:\Users, until you see your folders. - 4
Delete the deleter
Run
del "X:\ProgramData\Microsoft\Windows\Start Menu\Programs\Startup\firefox32.exe", X being that letter. The path is from BleepingComputer. - 5
Restart and scan
Sign in, run a full Microsoft Defender scan and search
%Temp%forchrst.exeandErOne.vbs.
If the recovery environment will not open, connect the disk to another computer as an external drive and copy your files off. Do not open anything on it.
The Hitler ransomware note
This is the Hitler-Ransonware
Your Files was encrypted!
Do you decrypt your Files?
Buy a Vodafone Card (25€) and add the code in the TextBox!
Cash Code(25€):
Your Files delete in: 1 hour
Can Hitler ransomware files be decrypted?
Are my files encrypted? The renamed files
In the original version they are not: only the ending is removed, so a file opens again once the right extension is back. Deleted files are a separate problem, in the recovery chapter.
| What you see | What it is | Can you get it back? |
|---|---|---|
holiday, report with no ending, still in their folders | The extension was stripped, the content is untouched | Yes: add the right extension |
| The folders are empty after a restart | The delete step ran at sign-in | Only from backups or file recovery |
A new ending such as .CainXPii | One tracker reports this for a later variant; we could not confirm it | Do not rename: check with ID Ransomware and No More Ransom |
- 1
Copy the files first
Copy them to another drive and work on the copies.
- 2
Show file extensions
In File Explorer on Windows 11 or 10 choose View > Show > File name extensions.
- 3
Guess the type from the folder
Pictures are usually
.jpgor.png, Music.mp3, Documents.docxor.pdf; file size helps too. - 4
Rename one file and open it
Right-click, Rename, type
holiday.jpg. If it opens, the guess was right; if not, undo it and try another ending.
The old guide said the FINAL version only claimed to encrypt. That matches BleepingComputer for the first version; we found no analysis of the later ones, so a file that will not open with the right ending may be damaged.
Should you pay the 25 euro ransom?
No. The claim that your files are encrypted is false, a prepaid code cannot be taken back, and the sender is anonymous.
| The lock screen says | What is true |
|---|---|
| Your files were encrypted | They were not (BleepingComputer, Ivanti) |
| Buy a Vodafone card and type the code | A prepaid code works for whoever has it; no source shows it stopping anything |
| Your files delete in one hour | The delete is real, but the fix is protecting the disk, not paying |
How to remove Hitler ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove the Hitler ransomware lock screen
Your files are not encrypted.
The steps get you past the lock screen first, then remove what starts it.
Step 1: Get past the lock screen
Hitler ransomware only blocks the screen, so your files are still there. Start Windows in Safe Mode with Networking from the sign-in screen: Shift + Restart, then Troubleshoot > Advanced options > Startup Settings > Restart > 5.
In Safe Mode the locker stays off, which lets you remove its startup entry, delete its file and run the scan.
The message claims to come from Hitler-Ransomware, but it is fake, and the code it asks you to buy unlocks nothing on Windows 11 or Windows 10.
Full procedure with screenshots: Start Windows or a Mac in Safe Mode On uGetFix
Step 2: Remove it from startup
Whatever Hitler ransomware installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Getting files back after the delete step ran
The Recycle Bin will be empty. Try these in order, and write nothing new to the disk.
- 1
Your own backup
An external drive, NAS or cloud copy. Connect it only after the PC is clean.
- 2
Cloud version history
OneDrive, Dropbox and iCloud keep deleted files and older versions for a while.
- 3
Previous Versions
Right-click the folder, Properties > Previous Versions (Windows 11: Show more options first). Nothing listed means no copy.
- 4
Windows File Recovery
Microsoft's free
winfrworks on Windows 10 and 11. Run it with a second drive as destination:winfr C: E: /regular /n \Users\<name>\Documents\; if that finds nothing, try/extensive.
Microsoft warns that deleted data can be overwritten at any time, especially on an SSD, and that the source and destination drives must differ.
How to prevent Hitler ransomware and the next attack
The 2017 guide's first rule still holds: keep a copy of your data that malware cannot reach.
Do
- Back up to an external drive and unplug it afterwards, so a connected drive cannot be touched
- Use the 3-2-1 rule that CISA recommends: three copies, two kinds of storage, one away from the PC
- Keep real-time anti-malware protection switched on at all times
- In Startup Settings you can choose Disable automatic restart on system failure (Microsoft), so a crash does not return you to sign-in
- Delete unexpected e-mail from unknown senders, since criminals copy well-known brands
Don't
- Do not open attachments or links from unknown senders
- Do not run a file that looks like a folder or a game account tool
- Do not keep the only copy of photos in the profile folders
Questions about Hitler ransomware
What is Hitler ransomware?
Hitler ransomware is a Windows program that fakes file encryption to scare people into paying. BleepingComputer found it in August 2016 as a batch file packed into an installer. It strips the extensions from your files, shows a lock screen with Hitler's picture and a one-hour timer, and asks for a 25 euro Vodafone card code.
When the timer ends it crashes Windows, and at the next sign-in a second program deletes the files in your user profile. Its author's own comments called it a test. Later versions in 2017 changed the picture, the language and the price, but not the idea.
How do I open .jpg, .docx and other files that lost their extension?
Add the right extension back to a copy of the file. The first version only removes the ending, so the content is untouched. Copy the files to another drive, turn on file name extensions in File Explorer, then rename one file, for example holiday to holiday.jpg, and open it.
If you are unsure about the type, the folder helps: photos are usually jpg or png, music mp3, documents docx or pdf. If the file will not open, undo the rename and try another ending. Later variants may do more than the first one, and we could not confirm that.
Is there a decryptor for Hitler ransomware?
No decryptor exists and none is needed for the first version, because nothing is encrypted. BleepingComputer's analysis found no encryption code, only a command that removes extensions and a batch file that deletes files. What you need is the extensions back, or a backup if the files were already deleted.
Be careful with websites that offer a free Hitler ransomware decryptor, since they are a common way to spread more malware. If a later variant really did add an extension such as .CainXPii, check it with ID Ransomware and the No More Ransom list before you rename anything.
Should I pay the 25 euro Vodafone ransom?
No, do not pay and do not type a code. The claim that your files are encrypted is false, so a code unlocks nothing that you cannot repair yourself. A prepaid card code goes to whoever types it in, and the author is anonymous.
The author's own batch-file comments call the first version a test, and no source we read says a code stopped the deletion. Instead, protect the disk, because the real danger is the delete step that runs at the next sign-in. Follow the first-steps chapter and keep every photo of the screen.
Can a data recovery company or paid service help?
A recovery service can help only with files that were already deleted, and you can try the free route first. If the files only lost their extension, you need no service, just the right ending.
If the delete step ran, the Recycle Bin is empty because the command skips it, but Microsoft's Windows File Recovery may find files that have not been overwritten. Avoid anyone who guarantees results or offers to negotiate with the criminals. On an SSD deleted data often disappears quickly, so stop using the PC at once and try backups first.
How did Hitler ransomware get on my PC?
Most likely you ran a program that looked harmless. BleepingComputer says the installer was bundled with other applications. Our 2017 reports showed a file posing as a Minecraft account dispenser and another posing as a folder called New Folder.exe.
The same report also named malicious e-mail attachments and corrupted links or ads as possible routes, which are general for ransomware and not specific to this one. Think about what you opened shortly before the lock screen, keep that file for the scan and do not run it again.
Was my data stolen by Hitler ransomware?
No source describes any data theft by this malware. BleepingComputer lists a lock screen, a fake error message and a file deleter, and no password stealer. The Minecraft version's note threatens to publish your data on Dropbox, but we found no case where that happened.
The installer was bundled with other applications, though, and we do not know which. After cleaning the PC, run a full scan and, as a precaution, change your main passwords from another device, starting with e-mail and banking.
How is Hitler ransomware different from other ransomware?
It does not encrypt files at all. Locky, CryptoWall and Cerber, which our 2017 guide named, lock files with keys that only the attacker holds. Hitler ransomware only removes extensions and then deletes files, so its danger is the delete step, not a key.
The price is also unusual: a Vodafone card code instead of Bitcoin. Do not confuse it with a screen locker such as the Police virus, which blocks the screen but does not delete anything. Its later versions, such as Hitler 2 or CainXPii, look similar, so check whether your files really open.
The timer is running. Will my files really be deleted in one hour?
The deletion is real, but in the original version it does not start when the timer ends. At zero the program crashes Windows by terminating csrss.exe, and the deleter, firefox32.exe, runs from the Startup folder at the next sign-in.
So your files are safe until you sign in again. Switch the PC off, open the recovery environment and delete that file before Windows starts normally, as the first-steps chapter explains. We have not tested this on a live sample, so keep a copy of anything you can reach.
Will Fortect remove Hitler ransomware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Hitler ransomware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- BleepingComputer: Development version of the Hitler-Ransomware Discovered (read October 5, 2026)
- Ivanti: Hitler Ransomware, How Low (and How Lame) Can They Go? (read October 5, 2026)
- Wikipedia: Hitler-Ransomware (read October 5, 2026)
- Tripwire: January 2017, The Month in Ransomware (read October 5, 2026)
- Microsoft Support: Windows startup settings (read October 5, 2026)
- Microsoft Support: Windows File Recovery (read October 5, 2026)