
steelstanleystaystrong.top: a server that handed out Linux botnet files, and what to do if a router or camera asked for them
steelstanleystaystrong.top is a web address that URLhaus lists 14 times on 15 October 2026: one shell script (1.sh) and 13 Linux programs named Space.x86, Space.mips, Space.arm7 and so on, all tagged botnetdomain.
It is not a program on your PC; it is a server that gave out malware for routers, cameras and other small Linux devices, and all 14 files are now marked offline. If you only saw the name in a log, nothing is proven, but the device that asked for it should be disconnected, rebooted, given a new password and updated.
Facts checked October 17, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan checks installed programs, startup items and browser extensions for anything that came with a script or device that downloads Space.* files from steelstanleystaystrong.top.
Do it yourself · free Remove steelstanleystaystrong.top (Linux botnet loader files) yourself 5 steps, about 15 minutes, no software needed.
Start the steps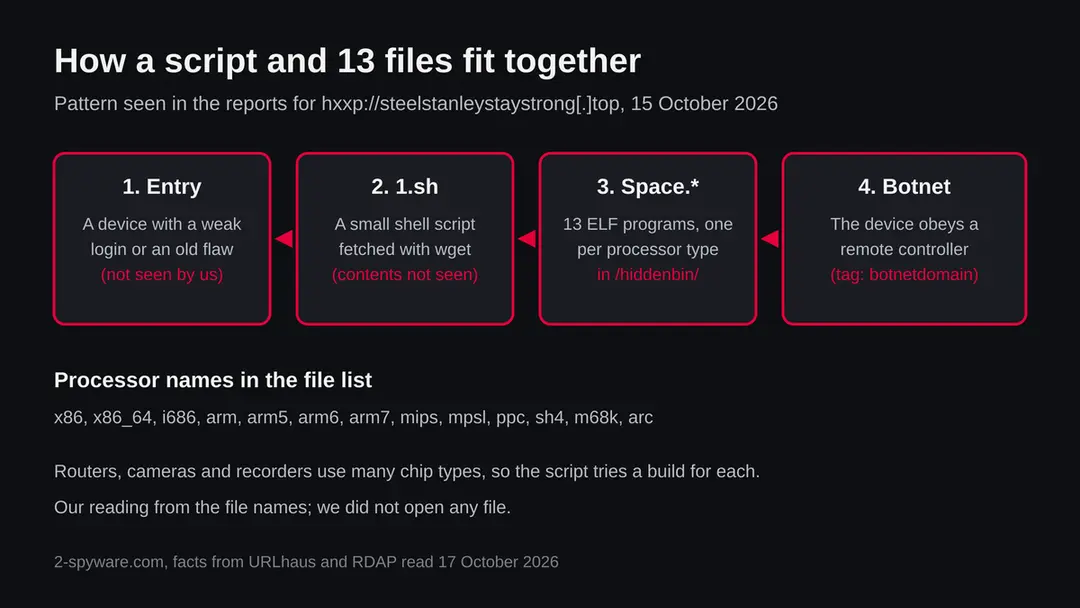
Steelstanleystaystrong.top (Linux botnet loader files): summary
| Type | A malware server: URLhaus lists a shell script and 13 Linux ELF files tagged botnetdomain, in a folder called hiddenbin |
|---|---|
| Risk | High for a router, camera or small Linux server that fetched its files: the device can be used in attacks. Low if you only saw the name |
| Symptoms | Often none. The device page no longer opens, the connection is slow, or a log shows requests to the address |
| How to get rid of it | Disconnect the device, reboot it offline, change the password, update the firmware, close remote login, reconnect and watch the log |
| Our check (17 October 2026) | One plain request from our server: the name could not be resolved. That clears nothing; the rating comes from URLhaus |
| Running since / first seen | Domain registered 7 August 2026; files first reported 15 October 2026 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Platform | Linux and embedded Linux devices. Nothing we read says Windows, Mac or phones are affected |
|---|---|
| Detection names | No detection name is known for the files on this server, because we did not open them. If they are Mirai builds, as we suspect, Microsoft's Mirai family names look like Trojan:Linux/Mirai.AA (Microsoft Security Intelligence lists 18 Mirai variants, all severe; read 17 October 2026) |
| Name | Steelstanleystaystrong.top |
| Domain registered | 7 August 2026 |
| Evidence | 14 write-ups by security sites; details still limited |
| First seen | 15 October 2026 |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 17 October 2026 |
Facts checked on 17 October 2026 against the URLhaus rows for steelstanleystaystrong.top held in our database (the abuse.ch site itself is not fetched by our tool), RDAP, one plain request of our own, and published pages by MalwareBazaar, CIS, CISA and the SANS Internet Storm Center.
We did not download the files and we infected no device; the cleaning steps follow CISA and CIS guidance on Mirai and were not tested on a live infection.
What steelstanleystaystrong.top is, and what we know about it
steelstanleystaystrong.top is a web address, not software you installed. The abuse.ch project URLhaus lists it for a shell script and 13 Linux programs, all reported on one evening, 15 October 2026. We found no public write-up of this exact address, so this page is built from the URLhaus rows we hold, the registration record, one request from our own server, and what security organisations have published about the same kind of file set.
- 1
What URLhaus lists
Fourteen file addresses on steelstanleystaystrong.top. Thirteen sit in a folder called hiddenbin and are named Space followed by a processor name: x86, x86_64, i686, arm, arm5, arm6, arm7, mips, mpsl, ppc, sh4, m68k and arc. The fourteenth is a script called 1.sh in the top folder. All carry the threat label malware_download, the tag botnetdomain and the tag ua-wget, and all were added by the same reporter, NDA0E.
- 2
What the tags mean
botnetdomain means the reporter considers the domain a home for a botnet, a network of hacked devices that obey one controller. elf is the file type of programs on Linux. sh is a shell script. ua-wget means the reporter fetched the files with the wget tool, whose name shows up as the user agent. Nothing in the tags names a malware family.
- 3
What we could not confirm
We did not download any file, so we cannot say what is inside, which family it is, or where it reports to. The 13 file names match the layout of other sample pages on MalwareBazaar (abuse.ch) that are tagged Mirai and are served from a hiddenbin folder on other numeric addresses. That makes a Mirai style botnet loader the likely reading. It is our reading, not a result.
- 4
What this means for you
If the name appeared in a router log, a DNS log or a firewall alert, the device that asked for it is the one in question. A person does not type this address by hand. The risk is for a router, camera, recorder, NAS or small server that was already compromised and went to fetch the script. If you only read the name in a block list, you are not infected by that.
- Kind of threat
- A server that hosted a loader script and 13 Linux ELF files for different processors, tagged botnetdomain by URLhaus
- Where the files were
- hxxp://steelstanleystaystrong[.]top/1.sh and hxxp://steelstanleystaystrong[.]top/hiddenbin/Space.x86 (and 12 more Space.* names): plain http
- Domain registered
- 7 August 2026 at 17:23 UTC, registrar Global Domain Group LLC, status client transfer prohibited (RDAP, read 15 October 2026)
- URLhaus entries
- 14 file addresses, all added on 15 October 2026 between 18:52 and 19:07 UTC; all 14 are marked offline in our copy of the data
- Our check
- One plain request from our server on 17 October 2026: the name could not be resolved (getaddrinfo ENOTFOUND)
- Platform
- Linux and embedded Linux devices (routers, cameras, recorders). The files are ELF programs, which do not run on Windows, Mac, iPhone or Android as they are
What steelstanleystaystrong.top (Linux botnet loader files) does on an infected PC
What we checked on 17 October 2026, and what we could not
Our check was a plain request from our own server, not a browser visit. It failed at the first step: the server could not find the address in DNS (error ENOTFOUND). That means the name did not resolve for us on 17 October. It does not clear anything.
Our check, 17 October 2026
- The address did not resolvegetaddrinfo ENOTFOUND steelstanleystaystrong.top. The name had no address for our server. Common reasons are that the domain was suspended or removed, that its DNS records were deleted, or that the operator moved on. We do not know which.
- Why that is not a clean resultBotnet operators drop a domain once reports start and bring up the same files on a new one. A name that no longer answers says nothing about the files already copied to devices, or about a replacement address.
- Notification request, pop-ups, redirects, ad networksNone seen, because nothing loaded. This is a file server, not a website for visitors.
- URLhaus listingOne script and 13 ELF programs tagged botnetdomain, reported on 15 October 2026. All 14 show as offline in our data, so we do not know for how long they were served.
- Downloads and the files themselvesWe did not download any file and did not try to run one. We cannot tell you what they contain.
Dangerous: treat it as a malware server Our request was one attempt that ended in a DNS error, so it proves nothing either way. The rating comes from the 14 URLhaus reports and their tags. Do not request files from this address, and do not run anything that does.
What happened to steelstanleystaystrong.top, from registration to our check
The domain is about ten weeks old and the reports come from a single quarter of an hour. Dates come from RDAP and from the URLhaus rows we hold; times are UTC.
7 August 2026
The domain is registered
RDAP shows steelstanleystaystrong.top registered on 7 August 2026 at 17:23 UTC through Global Domain Group LLC, with the status client transfer prohibited. That status stops the domain being moved to another registrar by accident or theft; it says nothing about how the domain is used.
15 October 2026, 18:52 UTC
Thirteen Space files are reported
Within 16 seconds, from 18:52:17 to 18:52:33, URLhaus adds Space.arm, Space.m68k, Space.arm7, Space.x86_64, Space.ppc, Space.sh4, Space.arm5, Space.arm6, Space.mips, Space.mpsl, Space.i686, Space.arc and Space.x86. All are ELF files in /hiddenbin/, tagged botnetdomain and ua-wget. Such a burst looks like a tool that walks through a file list, not a person.
15 October 2026, 19:07 UTC
The script 1.sh is reported
About 15 minutes later the same reporter adds http://steelstanleystaystrong.top/1.sh, tagged sh. It is the only entry that is not an ELF file. A script at the root next to a folder of builds for every processor is the usual shape of a loader that picks the build matching the device.
15 to 17 October 2026
Everything goes offline
In our copy of the data all 14 entries are marked offline. On 17 October our server could not resolve the name at all.
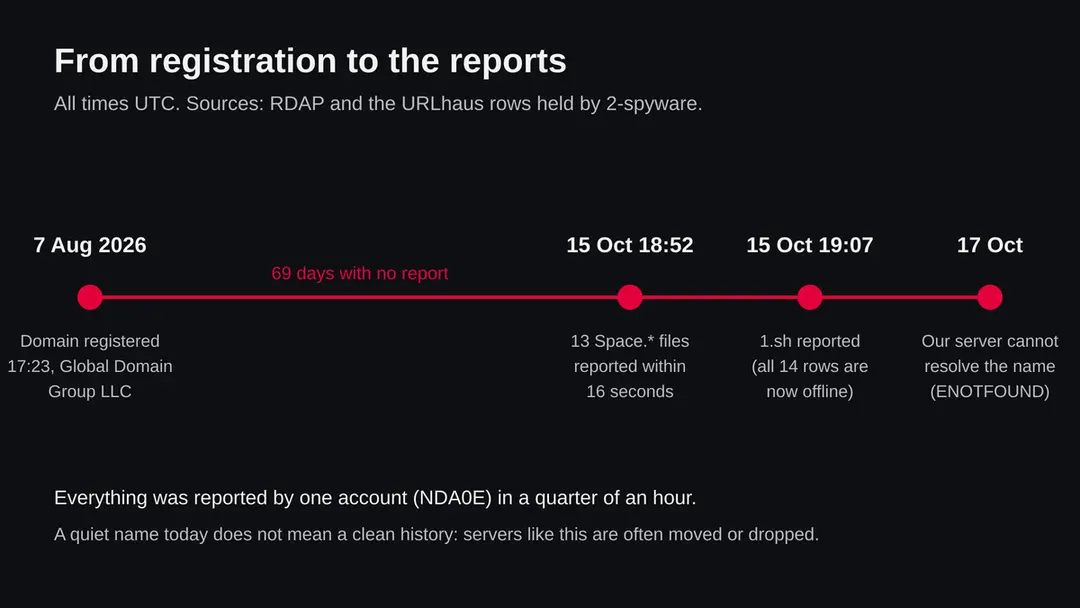
From registration on 7 August 2026 to our failed lookup on 17 October 2026. The reports all fall in a quarter of an hour on 15 October.
What the pattern suggests, and what it does not: a domain bought in August and used for malware files in October fits a throwaway address for a campaign. That is our reading of the dates. No report says who runs it, how many devices were infected, or whether the files are live elsewhere.
How a script and thirteen files turn a router into a bot
The set of files tells a story even without opening them. This is how the same pattern is described for Mirai, the best known family of this kind. We did not see this server's files, so treat it as the likely shape, not a proven account.
- 1
The device is reached first
The CIS write-up of Mirai says the malware targets routers, DVRs, IP cameras and Linux servers running BusyBox, and that attackers usually get a shell through default telnet or SSH logins. Later Mirai variants also use known flaws in exposed devices; the SANS Internet Storm Center and SOC Prime describe variants that exploit many vulnerabilities.
- 2
A script is pulled with wget
Once the attacker can type commands on the device, a short script such as 1.sh downloads the next piece. The ua-wget tag shows that this server was asked for its files with wget, which is also installed on many small Linux devices. The SANS ISC describes this style of shell script as a Command and Scripting Interpreter: Unix Shell, technique T1059.004.
- 3
The script picks the right build
Small devices use many different processors. A loader tries one file per type, in turn, until one starts. That is why the folder holds x86, x86_64, i686, arm, arm5, arm6, arm7, mips, mpsl, ppc, sh4, m68k and arc builds. MalwareBazaar lists samples with exactly these Space.* names on other addresses, tagged Mirai.
- 4
The program runs from memory and disables rivals
According to the CIS write-up, Mirai shuts down Telnet, SSH and HTTP on the device so that administrators and other malware cannot log in, and it binds a local port to run only one copy. The CISA alert on Mirai adds that the malware lives in dynamic memory, so a reboot removes it. That is why reinfection happens quickly if the password stays unchanged.
- 5
The device joins the botnet
From then on the device waits for orders from a controller. The reports we read describe denial of service attacks, where thousands of devices flood one target, as the main use. We do not know what the controller behind this domain ordered.
None of this applies to a laptop or a phone running Windows, Mac, iOS or standard Android, because the files are ELF programs built for embedded chips. It does apply to the internet facing boxes in a home or office that nobody updates.
Is it Mirai? What the evidence supports
The honest answer is: likely a Mirai style loader, not proven. We list what points that way and what is missing.
| Question | What we know | Source |
|---|---|---|
| Does the file list match known Mirai droppers? | Yes in shape: a folder of builds named after processors and a shell script that fetches them. MalwareBazaar pages for Space.* files in a hiddenbin folder on other addresses carry the tag Mirai | MalwareBazaar |
| Is the family named for this domain? | No. URLhaus only says botnetdomain and no tag names a family | URLhaus rows held by 2-spyware |
| What does Mirai usually do? | Scans for devices with default logins, takes them over and uses them for denial of service attacks | CIS; CISA alert |
| Does a reboot clear it? | For classic Mirai yes, because it lives in memory, but the device is reinfected within minutes if the password is still the default | CISA alert, as quoted in the search result we read |
| Are the files still downloadable? | Not from this address in our data: all 14 are offline and the name did not resolve for us | URLhaus rows; our request |
| Who is behind it? | Not known. The reporter NDA0E is the one who submitted the rows, not the operator | URLhaus rows |
What steelstanleystaystrong.top (Linux botnet loader files) can steal or download
Who can run into this: devices that may have asked for these files
Nobody visits this address on purpose. A device was told to fetch from it. The list below is the kind of device the sources name, not a list of confirmed victims.
Devices where this pattern can matter
- Home and office routers
- IP cameras and doorbells
- Network video recorders (DVR, NVR)
- Network storage boxes (NAS)
- Small Linux servers and VPS
- Smart TV boxes and media players
- Industrial gateways
- Old devices that no longer get updates
- 1
A default or weak login reachable from the internet
The CIS write-up says Mirai relies on default telnet and SSH credentials. A router with remote administration turned on and the password from the sticker is the textbook victim. CISA's December 2023 alert to manufacturers also tells users to change default passwords on routers, firewalls and access points.
- 2
A known flaw in an unpatched device
Some variants skip passwords and use a bug in the web interface or a service. Updating the firmware closes known bugs; a device that no longer gets updates cannot be fixed this way.
- 3
A server with a weak SSH login
A small Linux server on a hosting plan can be reached the same way. If you run one, the log of failed and successful sign ins is the first place to look.
What this can cost you
Reading the address costs nothing. The risks below apply to a device that was compromised and joined a botnet. Botnet bots rarely read your files; they use your connection.
- High
Your device is used to attack others
A bot sends traffic to targets chosen by the controller. Your address can end up in attack logs and on block lists.
- Medium
A slow or unstable connection
Attack traffic uses your upload speed. Streaming, calls and games may stutter while the device is busy.
- Medium
The device is locked to you
Mirai style malware closes Telnet, SSH and web access to keep others out, so you may suddenly be unable to open the router page or the camera app.
- Medium
A way into the rest of your network
A compromised router or camera sits inside your network. We found no report that these files go further, but an attacker with a foothold there can try.
- Low
Nothing, if you only saw the name
A name in a log or a warning is not an infection. It tells you a device asked, so find that device.
What you may notice, and what you may not
Most owners notice nothing. The signs below come from the sources or follow from them; none is certain.
| Sign | What it means |
|---|---|
| The router or camera page no longer opens | The CIS write-up says Mirai shuts down Telnet, SSH and HTTP on the device. It can also be an ordinary fault |
| The connection is slow with no reason | Our reading: attack traffic uses upload capacity. Check the device's traffic page if it has one |
| The device runs hot or restarts | Our reading, not a source claim. Small chips work hard when flooding traffic |
| Router log shows requests to steelstanleystaystrong.top or a numeric address | That device asked for the files. This is the clearest sign and the reason for this page |
| Unknown programs in /tmp or a hidden folder (for Linux owners) | Loader files are often placed in temporary folders. A normal device has no reason to hold programs named Space |
| Nothing at all | Bots are built to stay quiet |
How to check the PC for steelstanleystaystrong.top (Linux botnet loader files)
Start with one question: which device asked for steelstanleystaystrong.top, and when? A router log, a DNS filter, a firewall alert or a hosting provider's abuse notice normally names the source. If you have no such record, treat the reachable devices on the network as the ones to review.
None of the checks below deletes anything. Write down what you see before you change it.
- 1
Find the source in your log
Open the log or event page of your router, firewall or DNS service and search for steelstanleystaystrong.top and for hiddenbin. Note the device name or local address and the time. A DNS log shows which machine asked; a router log may only show the router itself.
- 2
Look at what is open to the internet
In the router's settings look for remote administration, port forwarding and UPnP. Anything that lets the internet reach Telnet (port 23), SSH (port 22) or the web page of the device is a way in. Turn off what you do not use.
- 3
Try the login
If the device page used to open and now does not, or the usual password stopped working, that fits a takeover, but it can also be a fault. Do not guess more passwords on the live network.
- 4
On a Linux server, list processes and files
Run ps aux and look for programs you do not know, especially from /tmp, /var/tmp or /dev/shm. Run ls -la /tmp. Check the user's crontab with crontab -l and the sign in log (journalctl -u ssh or the auth log). Programs named Space.something, or a file called 1.sh you did not create, are reason to disconnect.
- 5
Check your other devices for the same name
Search the same log for other local addresses that asked for the name. More than one source means more than one device to clean.
- 6
A clean result does not clear it
No log entry may only mean the log is short or the request went through another path. Treat any compromise sign as real, and a clean look as one data point.
How to remove steelstanleystaystrong.top (Linux botnet loader files)
How to remove steelstanleystaystrong.top
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Programs like steelstanleystaystrong.top add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 2: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after steelstanleystaystrong.top, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of steelstanleystaystrong.top that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Steelstanleystaystrong.top can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
How to clean a router, camera or other small Linux device
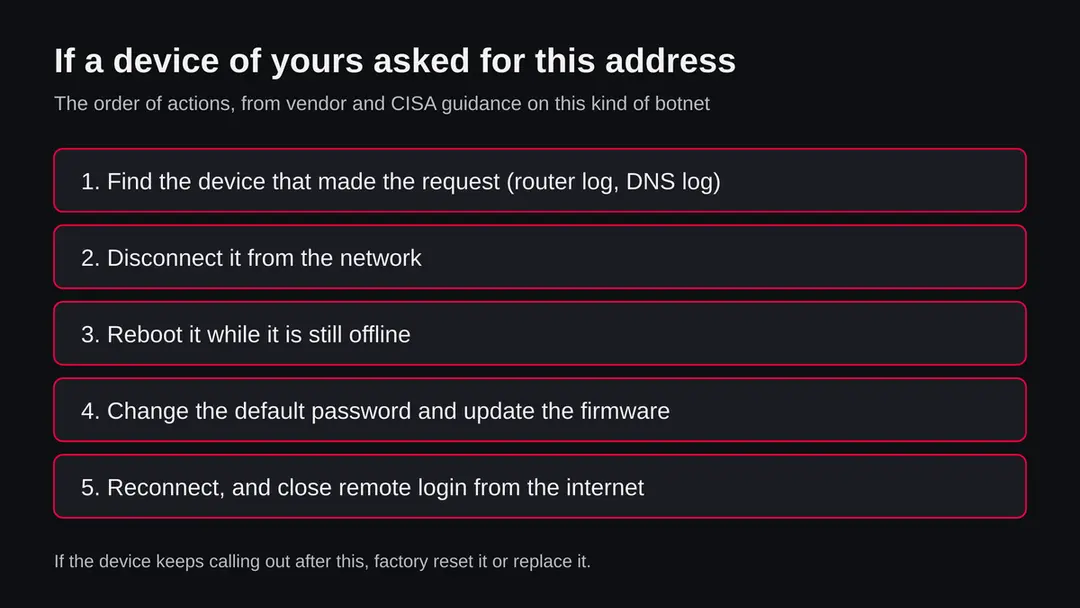
The order below follows the CISA alert on Mirai and the CIS guidance, which say to disconnect, reboot, change the password and keep the device off the open internet. Exact menus differ by maker, so use your device's manual for the screens. We did not infect a device to test this.
- 1
Disconnect the device
Pull the network cable and turn off Wi-Fi on the device. The CISA alert says to disconnect first, so the controller cannot reach it and it cannot be reinfected.
- 2
Reboot it while it is offline
Because Mirai lives in dynamic memory, the CISA alert says a reboot clears it. Power the device off, wait a minute, and turn it on again, still without a network connection.
- 3
Change the password before you reconnect
The CISA alert warns that a device reconnected with the default password can be reinfected quickly. Set a long, unique password for the device login and for the Wi-Fi. Connect a laptop directly to the device if you need to reach its page.
- 4
Update the firmware
Download the newest firmware from the maker's own site and install it. A US government guide for IoT users advises signing up for automatic updates where the maker offers them. If the maker no longer offers updates, plan to replace the device.
- 5
Close remote login from the internet
Turn off remote administration, Telnet and UPnP unless you need them. FBI guidance quoted with the Mirai alert advises blocking inbound ports 23, 2323 and 103 at the firewall or gateway.
- 6
Reconnect and watch the log
Plug it back in and watch the log for several days. If the device again asks for steelstanleystaystrong.top or another strange address, it is compromised again.
- 7
If it keeps coming back, reset or replace
Use the maker's factory reset, set up the device again from scratch and apply the first four steps before it touches the internet. If the device is old and has no updates, buying a new one is the safe answer.
- 8
On a Linux server, rebuild from a clean image
If you found unknown programs or sign ins on a hosting server, the safest path is a fresh install from a trusted image, restoring only your data. Change all keys and passwords that were on the server and add key based SSH login with passwords disabled.
If you own a server that was used to host these files
Some addresses on lists like this belong to a hacked site, not to the attacker. We have no evidence that steelstanleystaystrong.top was a hacked third party site; it looks like a domain registered for this purpose. If you own a domain or server where files like these turned up, the steps below apply.
- 1
Do not delete the evidence first
Copy the web folder and the logs to a safe place before you clean. The access log shows when the files appeared and which login or flaw was used.
- 2
Find how the files got there
Look for outdated content management software, weak admin or FTP passwords and exposed management panels. Change every password and key, and update the software.
- 3
Remove the files and the backdoor
Delete the hiddenbin folder and 1.sh, and look for other unknown files and scheduled tasks. A rebuild from a clean backup is safer than hand cleaning.
- 4
Ask for a re-check
When the server is clean, tell your host. Blocking services normally re-test an address after the listed files are gone.
If you use Windows, a Mac, an iPhone or an Android phone
The 13 files are ELF programs for embedded Linux processors. They do not run on a desktop or phone as they are, and we found no source that says this server affected them.
| Your device | What we know | What to do |
|---|---|---|
| Windows PC or Mac | ELF is the Linux program format. Nothing we read says these files have a build for desktops | Nothing to remove for this threat. If your router is the device that asked, clean the router |
| iPhone or iPad | No source describes this file set on iOS | Nothing to remove. Check your home router |
| Android phone | Android is built on Linux, but we found no source that links these files to Android phones | Nothing to remove for this threat; keep the phone updated and install apps only from the official store |
| Router or camera on your network | This is the target type for the file list | Follow the cleaning steps above |
After removal: passwords, accounts and prevention
Botnets like this do not need clever tricks. They take what is open and weak.
Do
- Change the default password on every router, camera and recorder the day you install it.
- Turn on automatic updates, or check the maker's site every few months.
- Turn off remote administration, Telnet and UPnP if you do not use them.
- Put cameras and smart devices on a guest or separate network where the router allows it.
- Replace devices that no longer get security updates.
- Use key based SSH login on servers and block password logins.
Don't
- Do not leave the password from the sticker or the manual.
- Do not forward ports to a device you cannot update.
- Do not reconnect a cleaned device before you change its password.
- Do not rely on a quiet log or a clean scan to say you are safe.
- Do not request files from steelstanleystaystrong.top.
Questions about steelstanleystaystrong.top (Linux botnet loader files)
What is steelstanleystaystrong.top?
It is a web address that URLhaus, the malware tracking project run by abuse.ch, lists 14 times on 15 October 2026. One entry is a shell script called 1.sh and 13 are Linux programs named Space.x86, Space.arm7, Space.mips and similar, all in a folder called hiddenbin.
All carry the tag botnetdomain. It is not a program on your computer and not a website for visitors. We did not download the files, so what they contain is not confirmed by us.
Is steelstanleystaystrong.top safe to open?
No. Do not request files from it and do not run anything that does. Our own request on 17 October 2026 could not even find the address, which proves nothing: botnet operators drop a domain once it is reported and often bring the same files up on a new one.
The rating comes from the 14 URLhaus reports and their tags, not from our request. If you already opened it in a browser, you only saw an error or a download prompt, so check that nothing was saved.
Is steelstanleystaystrong.top a virus?
The address itself is not a virus; it is a server that gave out files. URLhaus tags the files botnetdomain, which means they are meant to turn devices into part of a botnet.
The file names match a pattern that MalwareBazaar tags as Mirai on other addresses, but no source names a family for this domain. The files are ELF programs for Linux chips, so they do not run on Windows, Mac or phones as they are.
What are the Space.x86, Space.mips and Space.arm7 files?
They are the same kind of program built for different processors. Routers, cameras and recorders use many chip types, such as ARM, MIPS and PowerPC, and a loader script tries the build that fits.
The names x86, x86_64, i686, arm, arm5, arm6, arm7, mips, mpsl, ppc, sh4, m68k and arc cover most of them. We did not open the files, so what each one does is not confirmed.
I saw steelstanleystaystrong.top in my router or DNS log. Am I infected?
Not necessarily, and the name alone proves nothing. It does mean a device on your network asked for it, and a person does not do that by hand.
Find which device it was from the log, disconnect it, reboot it while it is offline, change its password, update its firmware and close remote login. Then watch the log for a few days. If the same name or another strange address shows up again, reset or replace the device.
How do I remove this from a router or camera?
Disconnect the device from the network, reboot it, and change the default password before you reconnect it. The CISA alert on Mirai says a reboot clears the malware because it lives in memory, and that a device reconnected with the default password can be reinfected quickly.
Then install the newest firmware from the maker, turn off remote administration, Telnet and UPnP, and watch the log. If it returns, use the factory reset or replace the device.
Does a reboot remove it?
For classic Mirai, yes: CISA says the malware exists in dynamic memory, so a reboot clears it. But the reboot alone is not enough. If the device comes back online with the default password or the same open service, it can be taken over again within minutes.
We do not know whether the files on this server persist across restarts, since we did not open them. Reboot offline, change the password, update, and only then reconnect.
Does it affect Windows, Mac, iPhone or Android?
We found nothing that says so. The files are ELF programs, the Linux format, built for embedded chips. They do not run on Windows or macOS as they are, and we found no source that links them to iPhone or Android.
The risk is for routers, cameras, recorders, network storage and small Linux servers. If your router is the device that asked for the address, clean the router. Your computers and phones need no special steps for this threat.
The address no longer works. Is the danger over?
Not for a device that already ran the files. All 14 entries are marked offline in our data and our server could not resolve the name on 17 October 2026, but a device that was infected before keeps running its copy until it is rebooted and secured.
The operator can also use the same files on another address. Check the device that asked, clean it, and keep its login and updates in order.
Will Fortect remove steelstanleystaystrong.top?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For steelstanleystaystrong.top, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- MalwareBazaar (abuse.ch): sample page for a Space.* file from a hiddenbin folder, tagged Mirai and sh (another address) (read October 17, 2026)
- Center for Internet Security: The Mirai Botnet, Threats and Mitigations (read October 17, 2026)
- CISA: Alert TA16-288A, Heightened DDoS Threat Posed by Mirai and Other Botnets (archived; the page returned an access error to our tool, so we used the text shown in search results) (read October 17, 2026)
- SANS Internet Storm Center: Mirai, Mirai on the Wall (guest diary) (read October 17, 2026)
- The Hacker News: CISA urges manufacturers to eliminate default passwords (December 2023) (read October 17, 2026)