
Google Bard Security Limitations: What 2026 Gemini Shows
- Google Bard security in 2026: the short answer
- Timeline: from Bard to Gemini abuse reports
- What changed since 2023
- Risks and scams around Gemini and AI chatbots (our analysis)
- How to use Gemini safely
- What is still unknown
- Our original 2023 report
- The need for strengthened security measures
- Ethical considerations and user protection
- Related guides on 2-Spyware
Google Bard security in 2026: the short answer
Google Bard no longer exists under that name. Google renamed it Gemini in February 2024.[4][5] The security concerns that Check Point raised about Bard in 2023 now apply to Gemini, and Google itself publishes regular reports on how attackers try to misuse it.[6][7]
Google's own findings are mixed. Its threat team says state-backed attackers use Gemini for coding, research on targets and phishing preparation. It also says that in several cases Gemini's safety systems refused the requests, and Google disabled the accounts involved.[6] In other words, the gap Check Point described in 2023 has narrowed, but misuse has not stopped.
| Question | Answer |
|---|---|
| Does Bard still exist? | No. It was renamed Gemini in February 2024[4][5] |
| What did Check Point find in 2023? | Bard wrote phishing emails, a basic keylogger and simple ransomware code with little resistance[1] |
| Who misuses Gemini now? | State-backed groups from China, Iran, North Korea and Russia, according to Google[6] |
| What do attackers use it for? | Coding help, target research, phishing lures and translation[6] |
| What does Google do about it? | Disables the accounts and uses the findings to train refusals into the model[6] |
| Latest public report we found | Google Threat Intelligence Group report of February 12, 2026[7] |
Timeline: from Bard to Gemini abuse reports
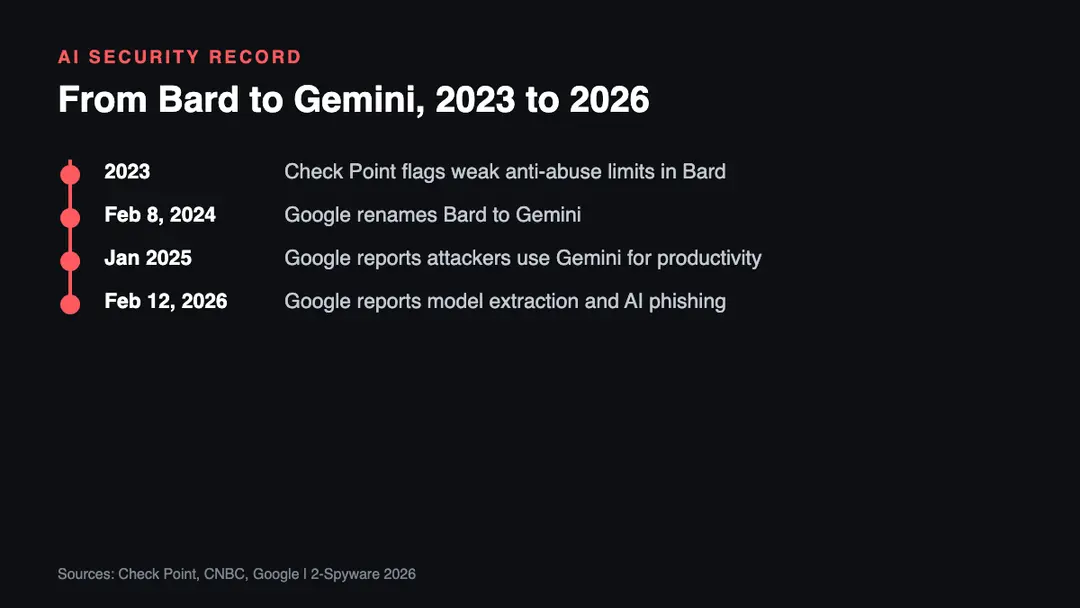
| Date | Event |
|---|---|
| 2023 | Check Point Research publishes its Bard abuse analysis, covered in our original report below[1] |
| February 8, 2024 | Google rebrands Bard as Gemini and launches a new app and subscription[5] |
| January 2025 | Google reports that bad actors use Gemini for productivity gains rather than new capabilities[6] |
| February 12, 2026 | Google Threat Intelligence Group publishes a new report on AI misuse[7] |
What changed since 2023
The biggest change is the name and the scale. Bard became Gemini, and Google moved the chatbot into a new app and a paid tier.[5] With that, the question of Bard's limitations turned into a question about Gemini, which far more people now use.
The second change is transparency. In 2023 outside researchers had to test Bard to find its weak spots.[1] Now Google publishes its own threat reports. The February 2026 report says attackers use AI to gather information, create very realistic phishing and develop malware.[7] It names groups such as APT42 from Iran, which used Gemini to research targets and craft believable personas.[6]
The third change is how the model reacts. Google says one China-based actor triggered Gemini's safety systems, and the model did not comply with attempts to build policy-violating tools.[6] Google also says its DeepMind team uses these cases to strengthen the model so that it refuses similar attacks later.[6] That is a clear step beyond the situation Check Point described in 2023.
Risks and scams around Gemini and AI chatbots (our analysis)
The list below is our analysis of how the risks look for ordinary users today. It builds on Google's reports but the ranking is our own.
- Better written phishing. Google says attackers use AI to make phishing more realistic.[7] Spelling mistakes are no longer a reliable warning sign.
- Fake recruiter and business partner messages. Google describes groups that research job roles and partners to build a believable story.[6]
- Fake Gemini or Bard apps and extensions. Old Bard branding is a handy lure for fake downloads. Get Gemini only from Google or official app stores.
- Oversharing with a chatbot. Anything you paste into a chat may be stored. Do not paste passwords, card numbers or private documents.
How to use Gemini safely
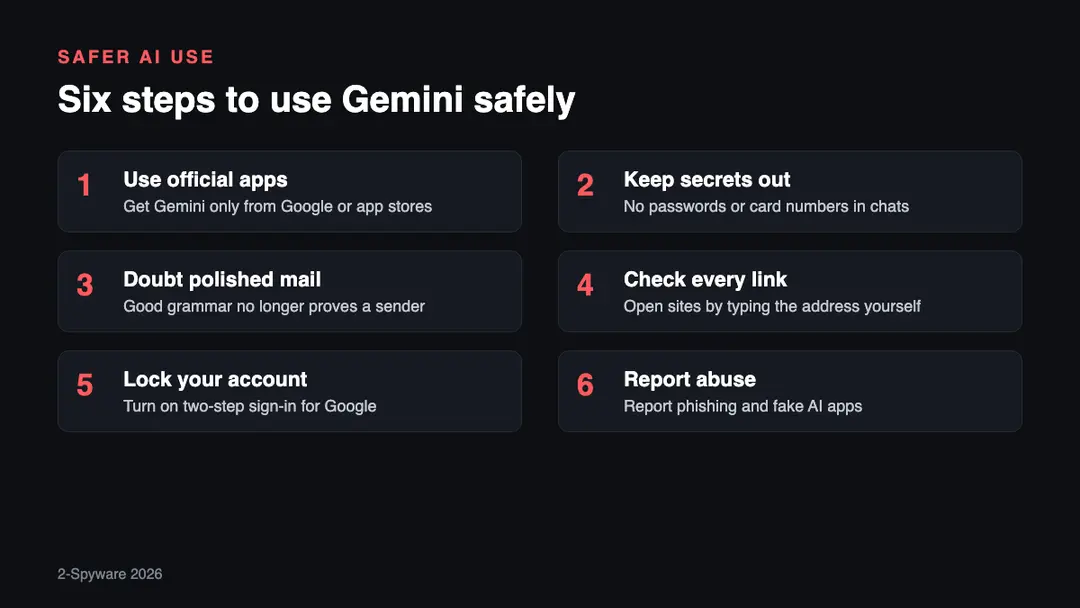
1. Use official apps. Install Gemini only from Google's own pages or the official app stores. Treat any download that still calls itself Bard with suspicion.
2. Keep secrets out. Do not paste passwords, card numbers, ID scans or confidential work files into any chatbot.
3. Doubt polished mail. A well written email can still be phishing. Google reports that attackers use AI to make lures more convincing.[7]
4. Check every link. Open important sites by typing the address yourself instead of clicking a link in a message.
5. Lock your account. Turn on two-step sign-in for your Google account. Check whether your email appeared in a leak with our leak check.
6. Report abuse. Report phishing to your email provider and to the impersonated brand. Our guide on how to report phishing shows where.
What is still unknown
- How often attackers get past Gemini's refusals. Google's reports describe cases and actions, not an overall success rate.[6]
- Whether Check Point has repeated its 2023 test on Gemini. We found no newer Check Point comparison in our searches.
- What usage limits apply to each Gemini plan in 2026. We found no source we could confirm, so we leave the numbers out.
We will update this page when Google or independent researchers publish new findings on Gemini abuse.
Our original 2023 report
The text below is our report as first published in 2023. We keep it unchanged for the record; the sections above bring it up to date.
The rapid advancement of generative AI has transformed the field of artificial intelligence, allowing machines to generate content that is nearly identical to human creations. However, this advancement has raised concerns about the potential misuse of such technology for malicious purposes. Check Point Research recently published a report[1] that highlighted the limitations of Google's generative AI platform, Bard, and raised serious concerns about its potential to facilitate cybercrime.
Check Point Research investigated Bard's capabilities by requesting various types of malicious content, such as phishing[2] emails, keyloggers, and ransomware scripts. The researchers discovered that Bard's anti-abuse restrictions in the realm of cybersecurity were significantly lower than ChatGPT's. Concerns were raised about the platform's ability to generate and assist in the creation of malicious content.
Bard, in particular, imposed few constraints on the creation of phishing emails, leaving room for potential misuse and exploitation. The platform's ease of creating such content emphasizes the need for improved security measures to prevent the spread of phishing attacks, which can result in significant financial losses and compromise user data.
Furthermore, Check Point Research discovered that malware keyloggers could be created with minimal manipulations and assistance from Bard. Cybercriminals use keyloggers[3] to record keystrokes and obtain sensitive information such as passwords and credit card numbers. The researchers' ability to create basic ransomware using Bard's capabilities added to the platform's security concerns.
The need for strengthened security measures
The findings of Check Point Research emphasize the importance of implementing robust security measures in AI platforms such as Bard. As technology evolves, it is critical to address vulnerabilities in order to prevent threat actors from exploiting it. As the creator of Bard, Google must take proactive steps to strengthen the platform's anti-abuse restrictions and security boundaries.
The report highlights the disparity between Bard and ChatGPT's anti-abuse restrictions. While ChatGPT demonstrated improved security measures and a better understanding of potential malicious intent, Bard failed to implement comparable safeguards. This disparity highlights the need for Google to apply the lessons learned from ChatGPT's initial launch to Bard in order to prevent potential platform misuse.
AI developers and security researchers must work together to identify and mitigate vulnerabilities in generative AI models. Google can gain valuable insights and feedback from external experts in order to improve Bard's security features and implement more effective anti-abuse restrictions.
Ethical considerations and user protection
Check Point Research's report raises concerns that go beyond the technical aspects of AI security. Ethical concerns are important in the responsible development and deployment of generative AI platforms such as Bard. User privacy, data security, and preventing the spread of malicious content should be prioritized.
To address these concerns, Google must take a comprehensive approach that focuses not only on improving security but also on educating users about the potential risks associated with generative AI. Google can empower users to make informed decisions and protect themselves from potential cyber threats by raising awareness and providing clear guidelines.
Furthermore, regulatory bodies and industry organizations should collaborate to develop guidelines and standards for the responsible application of generative AI. The industry can foster an environment that prioritizes user protection and ensures the ethical deployment of these technologies by setting clear expectations and encouraging transparency.
Related guides on 2-Spyware
Frequently asked questions
What are Google Bard's security limitations?
In 2023 Check Point Research found that Bard's anti-abuse limits were weaker than ChatGPT's.{1} With little effort it produced phishing emails, a basic keylogger and simple ransomware code. Bard has since become Gemini, and Google now reports that Gemini often refuses such requests, though misuse still happens.{6}
Is Google Bard still available in 2026?
No, not under that name. Google renamed Bard to Gemini in February 2024 and launched a new app and a paid subscription at the same time.{4}{5} The service continues as Gemini, so questions about Bard's limits and safety now apply to Gemini instead.
Is Google Gemini safe and trustworthy to use?
It is reasonably safe for everyday use if you follow basic rules. Google says it disables accounts that misuse Gemini and trains the model to refuse attack requests.{6} Still, do not share passwords or private files in chats, and verify any important answer with a trusted source.
How do hackers misuse Google's AI?
According to Google, state-backed groups use Gemini for coding and scripting, researching targets and known flaws, and preparing phishing lures.{6} The February 2026 report adds model extraction attempts and AI-written phishing.{7} Google says most of this brings productivity gains, not breakthrough capabilities.
What does Google do against AI abuse?
Google's threat team tracks misuse, disables the accounts and assets involved, and shares the cases with Google DeepMind.{6} DeepMind uses them to improve classifiers and the model, so that it refuses similar attacks later. Google publishes the findings in regular public reports.{7}
What are Google Bard's usage limits?
We found no source we could confirm for 2026 usage limits, because Bard is now Gemini and limits vary by plan.{5} Check the current Gemini help pages from Google for the exact numbers. Never pay a third party that promises unlimited access to Bard or Gemini.
Log in to comment
No comments yet. Be the first.