
Clop MOVEit Breach 2026: Siemens Energy and Victims
- Clop and the MOVEit breach in 2026: the short answer
- Timeline: MOVEit from zero-day to 600 breaches
- What changed since 2023
- Risks after a file transfer breach (our analysis)
- Steps for organizations that run file transfer tools
- What is still unknown
- Our original 2023 report
- Clop exploits MOVEit zero-day vulnerability
- Implications and response to the MOVEit attack
- Related guides on 2-Spyware
Clop and the MOVEit breach in 2026: the short answer
Clop is the ransomware gang, also known as TA505, that exploited the MOVEit Transfer zero-day CVE-2023-34362 starting on May 27, 2023, and Siemens Energy was one of its victims.[9] Siemens said none of its critical data was compromised and its operations were unaffected.[7] Reuters later reported that the MOVEit hack led to over 600 breaches affecting nearly 40 million people by August 8, 2023.[8]
We found no 2026 report in the sources we read that adds new Siemens Energy details. The MOVEit story is now mostly a lesson about file transfer tools and supply chains. This update gives the dated timeline, what the final scale looked like in 2023 reporting, and what organizations should do.
| Question | Answer |
|---|---|
| Flaw | CVE-2023-34362, an SQL injection flaw in MOVEit Transfer[2][9] |
| Attacker | The CL0P Ransomware Gang, also known as TA505[9] |
| Exploitation began | May 27, 2023[9] |
| Siemens Energy | Said no critical data was compromised and operations were unaffected[7] |
| Scale by August 2023 | Over 600 organizations and nearly 40 million people, per Reuters tallies[8] |
| Web shell used | LEMURLOOT, named by CISA and the FBI[9] |
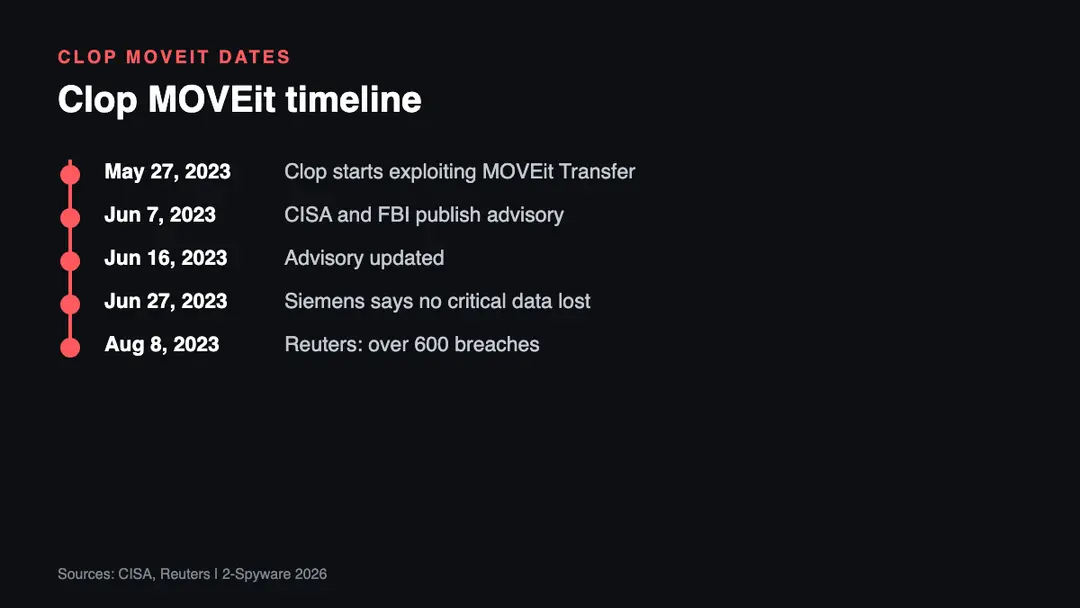
Timeline: MOVEit from zero-day to 600 breaches
| Date | Event |
|---|---|
| May 27, 2023 | Exploitation of CVE-2023-34362 begins[9] |
| June 7, 2023 | CISA and the FBI release a joint advisory on the Cl0p gang[9] |
| June 16, 2023 | The CISA advisory is updated[9] |
| June 27, 2023 | Reuters reports Siemens said no critical data was compromised and operations were unaffected[7] |
| August 8, 2023 | Reuters reports over 600 organizations hit and nearly 40 million people affected[8] |
What changed since 2023
When our original report appeared, the full fallout was unknown. Reuters then reported analyst tallies of over 600 breached organizations and nearly 40 million affected people, and it noted that experts believed the true number of companies could be in the thousands.[8] The breach reached many victims indirectly, because Clop attacked the MOVEit software used by service providers, and their clients' data was exposed too.[8]
CISA and the FBI described how the attack worked. The gang exploited a previously unknown SQL injection flaw in Progress Software's MOVEit Transfer and infected internet-facing web applications with a web shell named LEMURLOOT, which it used to steal data from the underlying databases.[9] This matches the vulnerability description in the National Vulnerability Database that our original report cites.[2]
For Siemens Energy, the public record we found is the 2023 statement that no critical data was compromised and operations were not affected.[7] We found no later public report that changes that.
Risks after a file transfer breach (our analysis)
Our analysis is that a breach through a vendor leaves people unsure where their data went, which is exactly what scammers want.
- Phishing that names the vendor. Messages claiming to be from a company hit by MOVEit and asking you to confirm details. Contact the organization using its official website.
- Extortion emails. Clop used data theft and leak threats instead of only locking files. Do not engage with unsolicited threats about your data.
- Third party exposure. You may be affected by a service provider you never heard of, as Reuters described with pension and insurance data.[8]
- Exposed file transfer servers. CISA recommends prioritizing patches for known exploited flaws in internet-facing systems.[9]
Steps for organizations that run file transfer tools
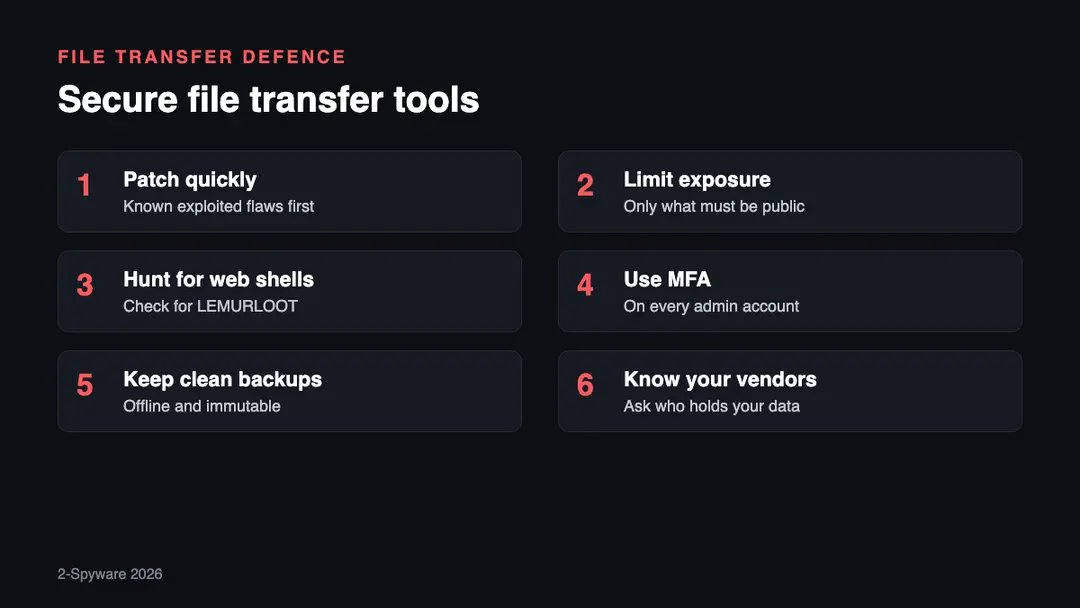
1. Patch quickly. CISA advises prioritizing patches for known exploited vulnerabilities in internet-facing systems.[9]
2. Limit exposure. Keep file transfer servers off the open internet where possible and disable unused ports.[9]
3. Hunt for web shells. Review servers for new or unrecognized accounts and files, and use endpoint detection to spot odd activity.[9]
4. Use multifactor sign-in. CISA recommends multifactor authentication for all services where possible, especially VPNs and critical accounts.[9]
5. Keep offline backups. Maintain encrypted, immutable, offline backups and a recovery plan.[9]
6. Map your vendors. List which providers handle your data and ask how they secure file transfers. The Reuters tally shows indirect victims were common.[8] Check exposure with our leak check.
What is still unknown
- Whether any Siemens Energy data was published after the 2023 statements. We found no public report of that.
- The exact number of MOVEit victims. Reuters describes tallies, and analysts quoted there believe the true number is higher.[8]
- Whether Clop still holds data not yet leaked. We found no public information.
Our original 2023 report
The text below is our report as first published in 2023. We keep it unchanged for the record; the sections above bring it up to date.
Siemens Energy, along with other energy and technology giants, has confirmed being targeted by the notorious Clop ransomware group, which exploited a zero-day vulnerability in Progress Software's MOVEit managed file transfer (MFT) software. The Munich-based energy technology company, which employs 91,000 people and posts annual revenue of $35 billion, confirmed that no critical data was compromised, and business operations were not significantly impacted.
According to Clop's modus operandi, the group leverages ransomware data-theft attacks, often threatening to leak stolen data to apply pressure on victims. Following the MOVEit attack, Siemens Energy featured on the group's leak site, indicating a breach had occurred. However, Siemens Energy has assured stakeholders that immediate action was taken upon learning about the incident.
This breach comes as part of a larger campaign impacting several major organizations, such as Schneider Electric, Sony, EY, PwC, Cognizant, AbbVie, and UCLA. The extent to which each entity was targeted in the MOVEit attack remains unclear, as investigations are still ongoing.[1]
Clop exploits MOVEit zero-day vulnerability
The Clop ransomware group is reported to have known about the MOVEit zero-day vulnerability since 2021, but mass attacks exploiting it only commenced in late May 2023. As a result of these breaches, the group claims to have accessed files of hundreds of organizations using the MFT product. Furthermore, the cybercriminals assert that they are the sole group to have exploited the zero-day before it was patched and, thus, are the only ones in possession of the data obtained during the attack.
Notably, the vulnerability exploited in the MOVEit Transfer platform, known as CVE-2023-34362 [2] is a SQL injection vulnerability. This type of vulnerability can be exploited by unauthenticated attackers to gain unauthorized access to MOVEit Transfer's database. This attack technique raises significant concerns about the security of data being transferred using such platforms.
Implications and response to the MOVEit attack
While the full fallout of the MOVEit attack continues to be assessed, it is evident that it has far-reaching implications. Numerous entities, including companies, federal government agencies, and local state agencies, have reported data breaches exposing sensitive data of millions of individuals.
For instance, Shell confirmed that it had been targeted in the MOVEit attack, and data allegedly stolen from the energy giant has begun leaking.[3] In another instance, the New York City Department of Education admitted that documents containing sensitive personal information of up to 45,000 students were stolen by Clop.[4]
In response to these threats, victims such as Schneider Electric and Siemens Energy have promptly deployed mitigations to secure their data and infrastructure. Schneider Electric became aware of the MOVEit software zero-day on May 30, 2023, and implemented measures to enhance its cybersecurity. Their cybersecurity team is currently investigating the claims made by Clop further:[5]
On May 30th, 2023, Schneider Electric became aware of vulnerabilities impacting Progress MOVEit Transfer software. We promptly deployed available mitigations to secure data and infrastructure and have continued to monitor the situation closely. Subsequently, on June 26th, 2023, Schneider Electric was made aware of a claim mentioning that we have been the victim of a cyber-attack relative to MOVEit vulnerabilities. Our cybersecurity team is currently investigating this claim as well.
Clop ransomware attacks via the MOVEit vulnerability highlight the growing concern for robust cybersecurity measures, especially in the sectors responsible for critical national infrastructure. The U.S. government is offering up to a $10 million bounty[6] under its Rewards for Justice program for information that links the Clop Ransomware Gang, or any threat actors targeting U.S. critical infrastructure, to a foreign government, reflecting the severity of the issue at hand.
Related guides on 2-Spyware
Frequently asked questions
What is the MOVEit breach?
It is a mass data theft campaign in which the Cl0p gang, also called TA505, exploited the MOVEit Transfer flaw CVE-2023-34362 starting on May 27, 2023.{9} Reuters counted over 600 affected organizations by August 8, 2023.{8}
Did Siemens Energy lose data in the Clop attack?
Siemens said none of its critical data was compromised and its operations remained unaffected, according to Reuters on June 27, 2023.{7} Our original report notes that Siemens Energy appeared on the Clop leak site.
What are the Clop MOVEit victims?
Victims included Siemens Energy and a very wide range of organizations. Reuters says tallies show more than 600 organizations and nearly 40 million people, with indirect victims through service providers.{8}
What is CVE-2023-34362?
It is an SQL injection vulnerability in Progress Software's MOVEit Transfer. CISA says Cl0p exploited it as a zero-day and used a web shell named LEMURLOOT to steal data from the underlying databases.{9}
What is an MFT breach?
An MFT breach is an attack on a managed file transfer tool, which companies use to exchange large or sensitive files. Because one product serves many customers, one flaw can expose many organizations at once, as MOVEit showed.{8}
Is Clop the same as TA505?
Yes. CISA says the CL0P Ransomware Gang is also known as TA505.{9} Our older guide on [TA505 and ServHelper](/ta505-hackers-take-up-servhelper-backdoor-and-flawedgrace-rat) covers the group's earlier malware.
Log in to comment
One practical point that gets missed: if you used MOVEit or got a notice from a company that did, don’t just watch for password resets. Check your email account for forwarding rules and recovery changes too. In Outlook on Windows, open Settings > Mail > Rules, and in Windows Security make sure nothing odd is running in the background. If a stolen mailbox gets a forwarding rule, the attacker can keep seeing recovery emails. That part is annoyingly efficient.