
Agent Tesla Malware in 2026: What the Trojan Steals Now
- Agent Tesla malware in 2026: the short answer
- Timeline: Agent Tesla from 2018 to 2026
- What changed since 2020
- Risks and scams linked to Agent Tesla (our analysis)
- How to remove Agent Tesla and protect your accounts
- What is still unknown
- Our original 2020 report
- Agent Tesla's commercial availability ensures large infection rates
- New version of Agent Tesla RAT steals credentials from more than 70 clients and apps
- Related guides on 2-Spyware
Agent Tesla malware in 2026: the short answer
Agent Tesla is still active in 2026. It is a .NET remote access trojan and keylogger that steals passwords, cookies and other data from Windows computers. In February 2026 Fortinet researchers described it as one of the most persistent threats around and analysed a new campaign that hides the malware in memory.[6]
The way it spreads has barely changed since our 2020 report below. It still arrives in phishing emails dressed up as business documents, now often purchase orders and order requests packed in RAR or 7z archives.[6][7] What changed is the delivery chain, which is now longer and harder for security tools to see.
| Question | Answer |
|---|---|
| What it is | A .NET remote access trojan, keylogger and information stealer sold as malware as a service[6] |
| Who it targets | Windows users, mostly businesses reached through phishing email[6][7] |
| Typical lure | Fake purchase orders or order release requests with an archive attached[6][7] |
| What it steals | Logins from browsers, mail, FTP and VPN clients, plus keystrokes, cookies and contacts[1][6] |
| How data leaves | In the February 2026 campaign, by email over SMTP to the attacker's mail server[6] |
| Still active in 2026? | Yes, Fortinet analysed a new campaign in February 2026[6] |
Timeline: Agent Tesla from 2018 to 2026
| Date | Event |
|---|---|
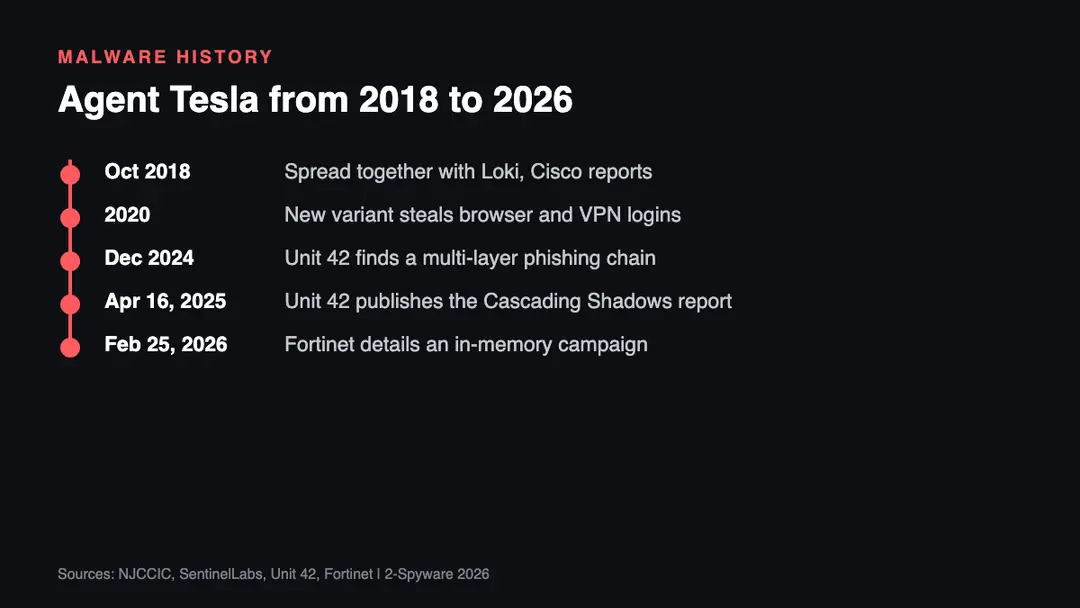
| October 2018 | Agent Tesla is distributed along with Loki in a malware campaign, per Cisco as cited by NJCCIC[8] |
| 2020 | SentinelLabs reports a variant that steals logins from browsers, VPN, mail and FTP clients[1] |
| December 2024 | Unit 42 uncovers a multi-stage chain delivering Agent Tesla, Remcos RAT or XLoader[7] |
| April 16, 2025 | Unit 42 publishes its analysis of that campaign[7] |
| February 25, 2026 | Fortinet publishes a detailed analysis of a new multi-stage Agent Tesla campaign[6] |
What changed since 2020
In 2020 Agent Tesla relied on booby-trapped Office documents that abused old Office flaws.[1][4] Recent campaigns use archives instead. Unit 42 found an email posing as an order release request with a 7z archive holding an encoded JavaScript file.[7] Fortinet found a "New purchase order" email with a RAR archive holding a similar script.[6]
The later stages now run mostly in memory. In the Fortinet case the script pulled PowerShell code, which loaded a .NET loader and then Agent Tesla itself without writing the final payload to disk.[6] The malware then hid inside a legitimate Windows .NET program through process hollowing, and checked whether it ran in VMware, VirtualBox or Hyper-V to avoid researchers.[6]
The business model also stays the same. Fortinet says Agent Tesla works as malware as a service, so even low-skilled criminals can run it.[6] NJCCIC notes that its sellers claimed to revoke licenses of abusers, while their support staff still explained how to evade antivirus tools.[8]
Risks and scams linked to Agent Tesla (our analysis)
The list below is our analysis of where Agent Tesla hurts people most. It draws on the vendor reports cited, but the ranking is ours.
- Stolen work logins. VPN and email passwords taken from one PC can open the whole company network, as our original report warned.[5]
- Hijacked browser sessions. Stolen cookies can let criminals enter accounts without the password.[6]
- Follow-up malware. The same delivery chains also drop Remcos RAT or XLoader, so one infection can bring more.[7]
- Fake invoices and orders. Finance and purchasing staff get the most lures, because order documents look routine.
How to remove Agent Tesla and protect your accounts
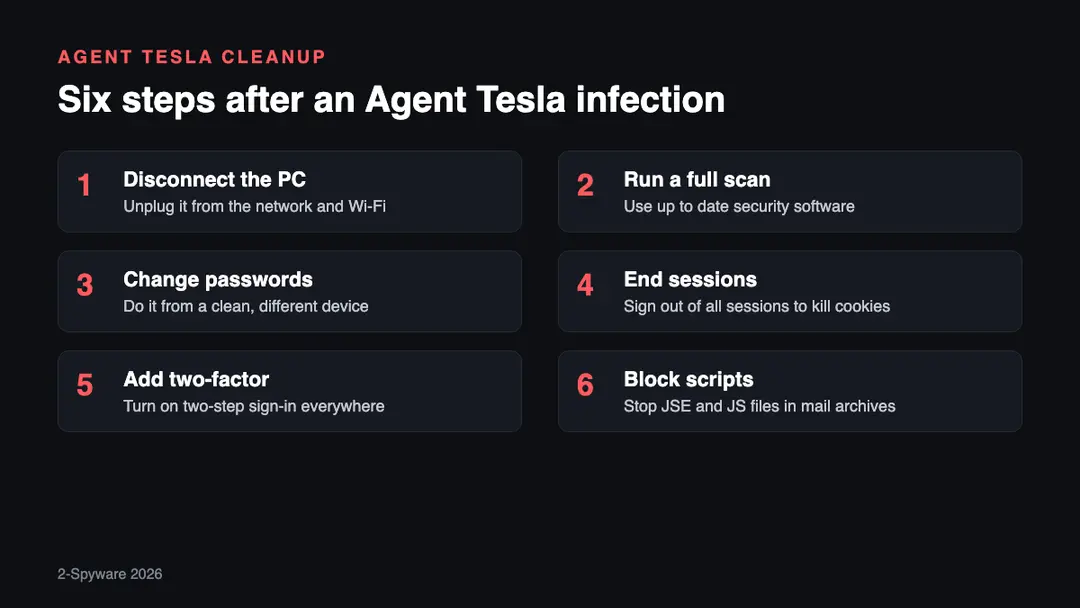
1. Disconnect the PC. Take the computer off the network so the malware cannot send more data or fetch other programs.
2. Run a full scan. Use reputable, up to date security software. Our malware removal guides explain the process step by step.
3. Change passwords. Change passwords saved in browsers, mail, FTP and VPN clients, but do it from another, clean device. Agent Tesla records keystrokes, so typing new passwords on the infected PC defeats the purpose.[1]
4. End sessions. Sign out of all sessions in your important accounts, because stolen cookies can keep criminals logged in.[6]
5. Add two-factor. Turn on two-step sign-in for email, VPN and banking. Check whether your address shows up in leaks with our leak check.
6. Block scripts. Ask your email admin to block JSE and other script files inside archives. Both recent campaigns started with such a file.[6][7]
What is still unknown
- Who sells and maintains Agent Tesla today. The reports we read describe campaigns, not the current sellers.
- How many computers are infected in 2026. We found no reliable public count.
- Whether the malware will move to new exfiltration channels in later campaigns. The February 2026 case used email.[6]
We will update this page when security researchers publish new Agent Tesla findings.
Our original 2020 report
The text below is our report as first published in 2020. We keep it unchanged for the record; the sections above bring it up to date.
Agent Tesla is a relatively old Remote Access Trojan (RAT) that resurfaced at the start of 2020 – threat actors began to actively update its code with new capabilities and functions. Security researchers at Sentinel One now observed a new variant of malware that is has been mostly used to attack businesses and organizations.[1]
The prevalence of the Trojan, especially since the COVID-19 pandemic began, has increased exponentially – Agent Tesla is now more rampant than other data-stealing malware strains of the similar functionality, such as Emotet o TrickBot (nonetheless, researchers specified that Dridex attacks are the most dominant).[2] The new variants that emerged at the start of the global health crisis were also widely observed being delivered via phishing email attacks.
While initially Agent Tesla was primarily used as a keylogger, this .Net-based Trojan has now been equipped with new modules, and this time, it is capable of stealing personal login account data from all the commonly-used browsers, as well as VPN, email, and FTP clients. Besides the new functions, Agent Tesla can also gather system information, disable anti-malware software, copy clipboard data, gather system information, and more.
Agent Tesla's commercial availability ensures large infection rates
Agent Tesla has been around for several years and has been offered for anyone willing to rent it. Malware authors were using its own website Agenttesla[.]com (not obsolete), as well as multiple underground marketplaces and forums for distribution. The so-called packages, similar to those used by legitimate software developers, allowed the access administration and data collection panels.
As noted by security researchers, the Trojan was quickly equipped with modern RAT functionality, including multi-language support, automatic activation upon payment, multiple operating system support, and much more. Prices were also relatively low:
At the time, pricing was quite competitive with a 1 month license selling for $12.00 USD all the way up to 6 month licenses going for $35.00.
New version of Agent Tesla RAT steals credentials from more than 70 clients and apps
Agent Tesla, just like many other malware of such type, is mainly distributed via targeted phishing emails. The recent variants are mostly using emails that present themselves as information leaflets distributed by the World Health Organization (WHO), United Nations (UN),[3] or similar authority agencies.
Most of the phishing emails are appended with a boobytrapped attachment, which, once opened abuses common MS Office vulnerabilities, such as CVE-2017-11882[4] and CVE-2017-8570, to proceed with the second stage infection routine.
Once broken in, Agent Tesla RAT is capable of stealing login credentials and other data from more than 70 different applications and clients, including MS Outlook, Google Chrome, Opera, Safari, MS Edge, CFTP, SmartFTP, Yandex, OpenVPN, Thunderbird, and many more. The harvested data is then sent via the FTP or STMP to cybercriminals' Command & Control servers. Experts from Sentinel One also found that malware is also capable of retrieving other malicious executables, which menas that other malware can be delivered in the process.
Especially concerning is that a VPN is one of the mostly wide-spread privacy and security tool used by regular consumers and corporations.[5] By stealing credentials of a VPN which is used to, for example, work from home during the COVID-19 pandemic, cybercriminals might bypass the extra defenses provided by the software.
To ensure that Agent Tesla or any other keylogger would not successfully exploit regular users and enterprises by stealing credentials of popular clients
Related guides on 2-Spyware
Frequently asked questions
What is Agent Tesla malware?
Agent Tesla is a .NET remote access trojan and keylogger that steals data from Windows computers.{6} It records keystrokes and takes saved logins from browsers, mail, FTP and VPN clients.{1} Criminals rent it as malware as a service, so even low-skilled attackers can use it in phishing campaigns.{6}
Is Agent Tesla still active in 2026?
Yes. Fortinet published an analysis of a new multi-stage Agent Tesla campaign on February 25, 2026, and called it one of the most persistent threats today.{6} Unit 42 also reported a campaign uncovered in December 2024 that delivered Agent Tesla variants.{7}
How does the Agent Tesla trojan infect computers?
Mostly through phishing email. Recent lures pose as purchase orders or order release requests with a RAR or 7z archive attached.{6}{7} The archive holds a script that starts a chain of PowerShell and .NET loaders, and the final malware runs in memory inside a legitimate Windows program.{6}
Is Agent Tesla a keylogger?
Yes, it started mainly as a keylogger and still records keystrokes.{1} Over time it gained modules that steal saved passwords, browser cookies, contacts and system information.{1}{6} That is why researchers now usually call it an information stealer and remote access trojan rather than just a keylogger.
What is the Tesla virus?
People often say Tesla virus when they mean Agent Tesla. The malware has no link to the car maker Tesla. It is a Windows trojan that steals passwords and other data and spreads through phishing emails with fake business documents.{6}{7}
How do I remove Agent Tesla?
Disconnect the computer from the network and run a full scan with reputable security software. Then change all saved passwords from a clean device and sign out of all sessions, because the malware steals logins and cookies.{1}{6} Turn on two-step sign-in for email and VPN accounts.
Log in to comment
No comments yet. Be the first.