
Telegram Spy Apps in 2026: Fake Telegram and Threema Spyware
- Telegram spy apps in 2026: the short answer
- Timeline: APT-C-23 and fake messenger spyware
- What changed since 2020
- Risks around Telegram spy apps (our analysis)
- Six steps to check your phone for fake messenger spyware
- What is still unknown
- Our original 2020 report
- APT-C-23 activity started 3 years ago and new variants get discovered every year
- The malware is capable of spying your Android device and even stealing files
- Related guides on 2-Spyware
Telegram spy apps in 2026: the short answer
Fake Telegram apps remain a common way to spy on Android users. The group behind the 2020 fake Telegram and Threema apps, known as APT-C-23 or Arid Viper, kept building new Android spyware after our report.[8][9] Security firm ESET also found trojanized Telegram and Signal apps that spread the BadBazaar espionage tool.[10]
The real Telegram and Threema apps are not the problem. The danger is a copy that looks the same but carries spyware, usually installed from a website or a fake store rather than an official one. ESET lists trojanized Telegram and WhatsApp apps among the Android campaigns it found between 2023 and 2026.[11] If you searched for a "Telegram spy" app to watch someone else, know that such tools are a common malware bait and can be illegal to use on another person's phone.
| Question | Answer |
|---|---|
| Who made the 2020 fake apps | APT-C-23, also called Arid Viper and Two-tailed Scorpion[2][8] |
| Spyware name in 2020 | Android/SpyC23.A, listed by MITRE as SpyC23[2][8] |
| Later spyware from the group | AridSpy, a multistage trojan spread through dedicated websites[9] |
| Other fake Telegram spyware | BadBazaar, hidden in trojanized Signal and Telegram apps[10] |
| What it can take | Calls, contacts, SMS, notifications, files, location, screenshots[2][8] |
| Main defence | Install messengers only from official stores and check permissions[2] |
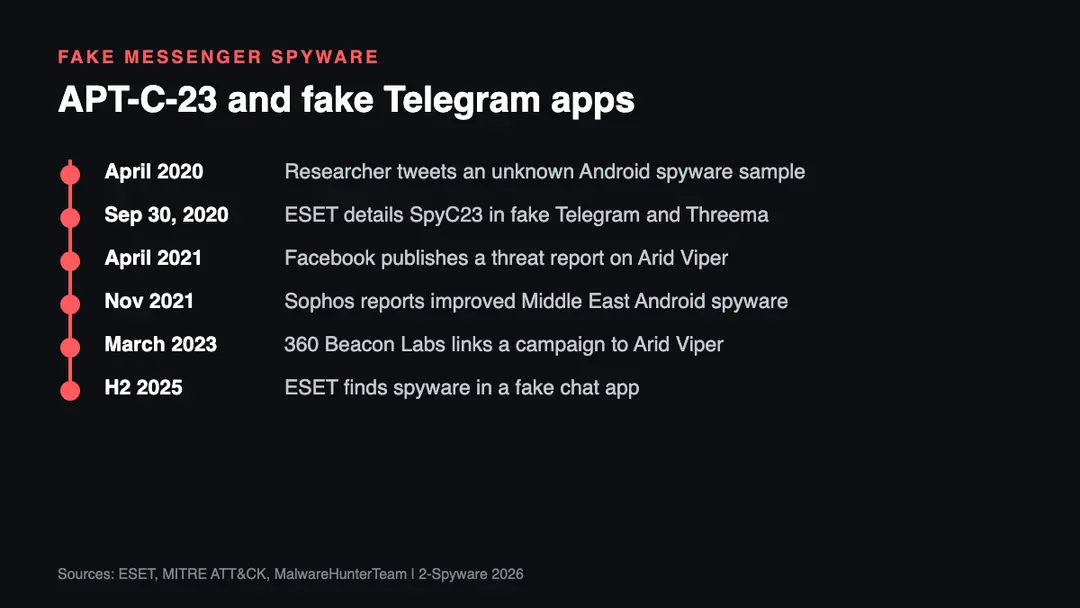
Timeline: APT-C-23 and fake messenger spyware
| Date | Event |
|---|---|
| April 2020 | MalwareHunterTeam tweets about an unknown Android malware sample[1] |
| September 30, 2020 | ESET publishes its analysis of Android/SpyC23.A in fake Telegram and Threema apps[2] |
| April 2021 | Facebook publishes a technical threat report on Arid Viper, cited by MITRE[8] |
| November 2021 | Sophos reports that Android spyware targeting the Middle East improved its capabilities, cited by MITRE[8] |
| March 2023 | 360 Beacon Labs links the Kora442 campaign to Arid Viper[9] |
| Second half of 2025 | ESET uncovers an Android spyware campaign using a fake chat platform[11] |
What changed since 2020
The group did not stop. MITRE ATT&CK now tracks APT-C-23 as a named group and lists SpyC23 with abilities such as call control, audio and video capture, location tracking, screen capture and hiding its own app icon.[8] Those abilities go beyond the list in our original report, which already included call and screen recording.
Delivery changed too. In 2020 the fake apps sat in a fake store called DigitalApps.[2] Later, ESET found five campaigns that spread a new spyware called AridSpy through dedicated websites, with the malicious code planted inside trojanized apps.[9] AridSpy became a multistage trojan that downloads further payloads from its command server after the first install.[9]
Other actors copy the same trick. ESET reported BadBazaar espionage code inside trojanized Signal and Telegram apps.[10] Its overview of Android campaigns from 2023 to 2026 also lists trojanized WhatsApp and Telegram apps that hijack the clipboard to steal cryptocurrency.[11] A fake messenger is now a standard lure, not a rare one.
Risks around Telegram spy apps (our analysis)
This is our reading of the threats that hide behind searches like "telegram spy" or "spy on telegram".
- Fake Telegram downloads. Websites offer modified Telegram builds with extra features outside the official stores. Many are the same app with spyware inside.[10][11]
- Spy tools that spy on the buyer. Apps sold to monitor someone else's Telegram often ask you to disable protection and sideload a file. The buyer's phone is the first victim.
- Romance and chat lures. A new contact asks you to move to a "safer" chat app and sends a download link. ESET saw this pattern in a 2025 campaign.[11]
- Permission tricks. The 2020 spyware disguised a notification access request as a message encryption feature.[2]
- Crypto clipboard theft. Trojanized messengers can swap a wallet address you copy for the attacker's address.[11]
- Legal risk. Installing spyware on another person's phone without consent can break the law in many countries. We do not give legal advice.
Six steps to check your phone for fake messenger spyware
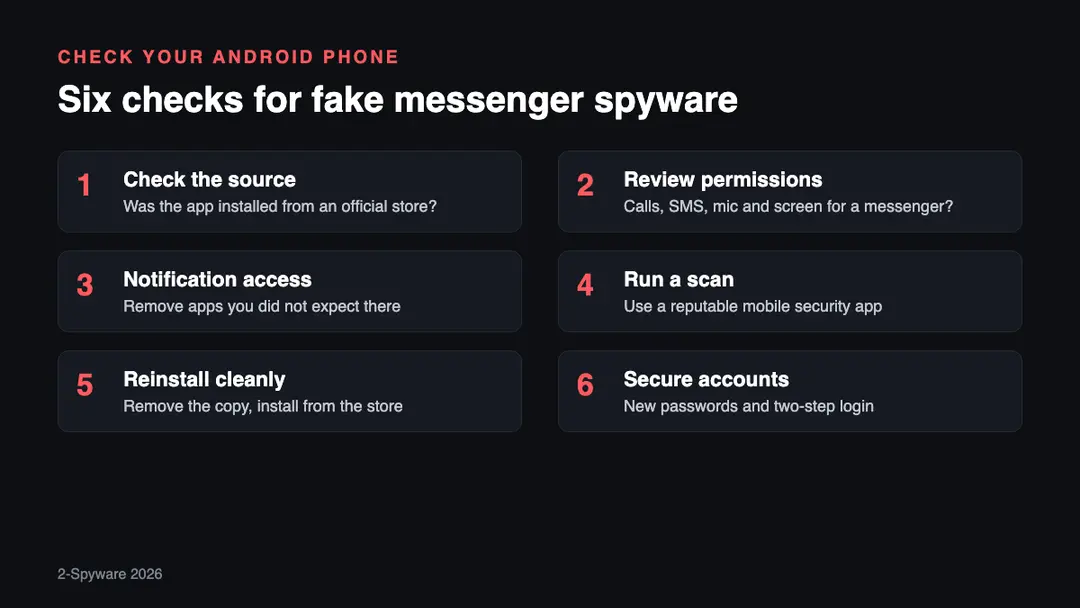
1. Check where the app came from. Open the app details in Android settings. If your Telegram or Threema did not come from an official store, treat it as suspect. ESET advised installing apps only from the official Google Play Store.[2]
2. Review its permissions. A messenger that also holds call log, SMS, microphone and screen recording rights deserves a closer look. SpyC23 used such rights to record calls and screens.[2][8]
3. Check notification access. Go to the special app access settings and look at which apps can read notifications. The 2020 spyware hid this request behind a fake encryption feature.[2]
4. Run a mobile security scan. Use a reputable security app and keep it updated. Our Android virus removal guide shows the usual signs of infection.
5. Reinstall from the official store. Uninstall the suspect copy, then install the real app again. If the app refuses to uninstall, check device admin settings first.
6. Secure your accounts. From a clean device, change passwords, turn on two-step verification in Telegram and review active sessions. Check whether your email appeared in a leak with our leak check.
What is still unknown
- How many people installed the 2020 fake Telegram and Threema apps. ESET did not publish an install count in the report we cite.[2]
- Whether APT-C-23 still runs the DigitalApps store or has moved fully to other websites.[9]
- Whether the 2025 fake chat campaign is linked to the same group. ESET describes it separately.[11]
We will update this page when researchers publish new campaigns that use fake Telegram or Threema apps.
Our original 2020 report
The text below is our report as first published in 2020. We keep it unchanged for the record; the sections above bring it up to date.
A group of hackers, known at least since 2017, recently started using fake messaging apps to infect Android devices with new malware that can secretly record phone calls. They created a fake Android app store called "DigitalApps" and using it to spread previously undocumented infection through such impersonated apps as Telegram, Threema, and weMessage.
Cybersecurity firm ESET started investigating and finally has discovered this new Android spyware after their fellow researcher tweeted[1] about an unknown Android malware sample in April 2020. One of the ESET researchers explained:[2]
Compared to the versions documented in 2017, Android/SpyC23.A has extended spying functionality, including reading notifications from messaging apps, call recording and screen recording, and new stealth features, such as dismissing notifications from built-in Android security apps. One of the ways the spyware is distributed is via a fake Android app store, using well-known apps as a lure.
APT-C-23 activity started 3 years ago and new variants get discovered every year
These newly discovered Android spyware creators have different names: APT-C-23,[3] Two-tailed Scorpion, and Desert Scorpion. This group is mainly targeting users from the Middle East. The APT-C-23 likes to use Windows and Android components to accomplish the particular attack goals. These cybercriminals were firstly detailed by Quihoo 360 in 2017. Then their malware had the ability to spy on the victim's device, exfiltrate contacts, call logs, messages, location details, photos, files, and more.
Another version of APT-C-23-created malware was found in 2018 by Symantec.[4] Cybercriminals used malicious media player to obtain information from the victim's device. Moreover, this malware tried to trick users into installing other malware furthermore.
Also, in February of this year, the Check Point Research team reported another APT-C-23 group activity.[5] The threat was named as Hamas Android malware. Its operators tried to pose as teenage girls on Instagram, Facebook, and Telegram to lure soldiers from Israel into downloading malware-infected applications on their devices.
The malware is capable of spying your Android device and even stealing files
Now, the ESET cybersecurity team discovered a new Android malware created by APT-C-23/ Two-tailed Scorpion. When the ESET team analyzed the fake Android app store, they discovered that it contained not only malicious but also clean apps too. The newest spyware version named as Android/SpyC23.A was hiding malicious features posing as Threema, Telegram, AndroidUpdate, and weMessage applications.
After the download, spyware requests permissions and the victim accepts them because requests are disguised ar privacy and security features. The ESET cybersecurity researcher Lukas Stefanko said[6] that the malware request is really tricky. For example, it masks the permission to read notifications as a message encrypting feature.
After permissions are granted, the Android virus[7] can start different types of espionage activities based on commands from its C&C server. This malware can act like a very powerful spying tool. It is capable of:
- making screen and call recordings;
- exfiltrating call logs, contacts, and SMS;
- recording audio;
- reading notifications from messaging applications;
- stealing files;
- dismissing notifications from some security apps.
The ESET team recommends installing applications only from the official Google Play Store if users want to avoid this and other threats. Also, users should always remember to double-check what permissions the downloaded app is requiring and use the newest version of powerful mobile anti-malware software. This malware is not the only one on the internet, so users should be extra careful when surfing the internet and especially when downloading apps from suspicious, unofficial stores.
Related guides on 2-Spyware
Frequently asked questions
Can someone spy on my Telegram?
Yes, if spyware is on your phone, it can read what Telegram shows on screen and in notifications. The 2020 fake Telegram apps could record the screen, read notifications from messaging apps and steal files.{2} Install Telegram only from an official store and check which apps have notification access.
Is there a fake Telegram app with spyware?
Yes, several have been found. In 2020 ESET found fake Telegram and Threema apps carrying Android/SpyC23.A.{2} ESET later found BadBazaar espionage code inside trojanized Telegram and Signal apps.{10} Others steal cryptocurrency by swapping copied wallet addresses.{11}
What is the Threema spybot?
There is no official Threema spy bot; the name usually points to fake Threema apps that hide spyware. In 2020 ESET found a fake Threema app from the APT-C-23 group that carried the SpyC23 spyware.{2} The real Threema app from an official store is not affected by that campaign.
Do Telegram spy apps work?
Apps sold to spy on someone else's Telegram usually need full access to that person's phone, and many are malware themselves. Our analysis is that the buyer often ends up infected. Using spyware on another person's device without consent can also be illegal, so avoid such tools.
Who is behind the fake Telegram and Threema apps?
The group is APT-C-23, also known as Arid Viper and Two-tailed Scorpion.{2}{8} It mainly targets users in the Middle East, and ESET later linked it to the AridSpy spyware, spread through trojanized apps on dedicated websites.{9} MITRE ATT&CK tracks the group as G1028.
How do I know if my Android has spyware?
Look for apps you did not install from an official store, apps with unusual permissions, and unknown apps with notification access. Battery drain and data use can also hint at it. Run a reputable mobile security scan and reinstall messengers from the official store if in doubt.{2}
Sources
- Twitter. Social Network
- WeLiveSecurity. Award-winning security articles, views, insight and research directly from ESET's experts
- CPR. Check Point Research
- Symantec Blogs. Symantec Enterprise blogs
- CPR. Check Point Research
- Security Magazine. The business magazine for security executives
- 2-Spyware. Security and spyware news
- MITRE ATT&CK
- WeLiveSecurity
- WeLiveSecurity
- ESET
Log in to comment
No comments yet. Be the first.