The FBI has arrested another suspected co-conspirator of ShinyHunters after the group…

The FBI has arrested another suspected co-conspirator of ShinyHunters after the group said it breached the FBI’s jobs portal and stole sensitive data on almost all FBI agents and job applicants, The Hacker News reports. The FBI said the breach happened after a contractor failed to implement a security patch for the platform. The agency has removed the contractor.

The Hacker NewsFBI Arrests Another ShinyHunters Suspect Reportedly Involved in Its Jobs Portal Hack

Source: thehackernews.com

More in this rubric
all →

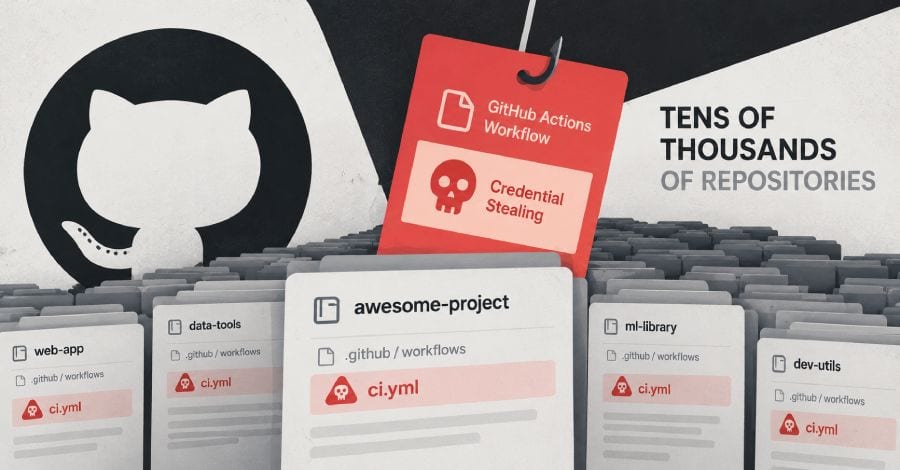
The Hacker News reports that attackers have compromised open-source maintainer accounts to push a malicious GitHub Actions workflow into more than 340 repositories, with more than 500 GitHub accounts affected since October 7. The workflow is designed to steal secrets, including cloud, SaaS and AI credentials. Developers should check for the named workflows, revoke compromised GitHub credentials, rotate secrets, and delete the malicious workflow from all branches.

The Hacker NewsCredential-Stealing GitHub Actions Workflows Planted in Tens of Thousands of Repositories

Source: thehackernews.com

SecurityWeek reports that Bitdefender found Midnight Mimosa, a campaign that ships malware preinstalled in the firmware of low-cost Android devices built on MediaTek platforms. The malware can silently install and remove apps, grant permissions, and load code remotely, and some related apps were also found on Google Play. Windows users should be cautious with cheap devices and avoid installing apps from untrusted sources.

SecurityWeekPre-Baked Firmware Malware Hits Budget Android Devices in 150+ Countries

Source: securityweek.com

Malwarebytes Labs reports that attackers compromised infrastructure behind the .gh, .sl, and .as country-code domain namespaces and used it to obtain unauthorized HTTPS certificates for Google domains and other organizations. Google blocked the certificates in Chrome and worked with certificate authorities to revoke them. Windows users should keep their browser and operating system updated and never bypass certificate warnings.

Malwarebytes LabsAttackers hijack country-code domains to impersonate Google and other services

Source: malwarebytes.com

5,465 members already hereReading, writing, commenting and voting. 0 verified · 190 joined this year