Bitdefender reports that Ireland’s police force had two of its X accounts hijacked and…

· in brief

Bitdefender reports that Ireland’s police force had two of its X accounts hijacked and used to post cryptocurrency messages. The posts claimed followers could claim free cryptocurrency through an airdrop, but the link could lead victims to hand over the keys to their crypto wallet. Users should be cautious with unexpected messages from trusted accounts and use multi-factor authentication and unique, strong passwords.

bitdefender.comIrish police force has its Twitter hacked in cryptocurrency scam

Source: bitdefender.com

More in this rubric
all →

KnowBe4 reports that Microsoft’s disruption of YAM Store, CoGUI and Iron Man exposed a cloud-based impersonation industry behind phishing. Criminals were buying accounts, hosting and templates that mimicked banks, retailers, healthcare providers, police and government agencies, then used fake CAPTCHA screens and live monitoring to capture credentials and payment details. The post says ordinary users and small offices should not rely only on spotting bad grammar. It recommends phishing-resistant authentication, rapid reporting and training that keeps up with changing social engineering…

KnowBe4Phishing Is Now A Criminal Impersonation Industry. Here Is How To Fight Back

Source: blog.knowbe4.com

KnowBe4 reports that researchers at ESET found a phishing campaign targeting YouTubers with phony sponsorship offers. The emails are personalized, use fake brand identities and domains, and try to get victims to grant access to their Google accounts. Users should verify sponsorship offers through official channels, check sender domains carefully, and not approve sign-in or access requests they do not recognize.

KnowBe4Phishing Attacks Target YouTubers With Phony Sponsorships

Source: blog.knowbe4.com

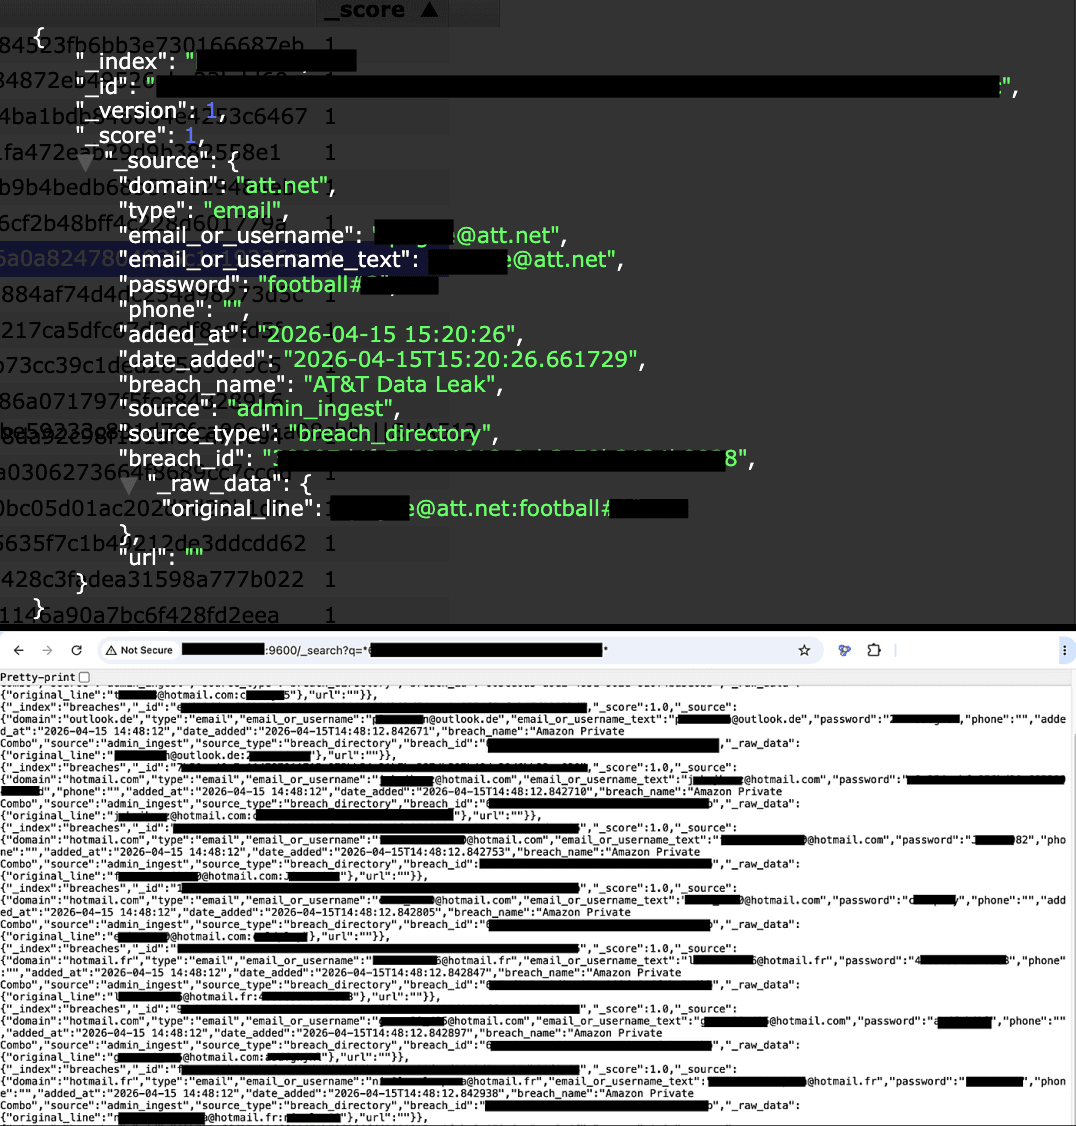
Hackread.com reports that an unprotected database linked to Vibetech exposed 13.7 million records, including names, phone numbers, email addresses, plaintext passwords and bank account details. The report says exposed passwords can be used to access email, shopping or financial accounts, steal personal information, make fraudulent purchases or impersonate victims, so users should change reused passwords and watch for phishing and account-takeover attempts.

hackread.comVibetech Database Exposes 13.7M Records Including AT&T and FBI Data

Source: hackread.com

5,621 members already hereReading, writing, commenting and voting. 0 verified · 346 joined this year