
BrowserModifier: what the Defender alert means and how to remove it
BrowserModifier is the word Microsoft Defender puts in front of the name of a program that changes your browser, and it covers many different programs, not one virus. Find which family the alert names and where the file is, then follow the check, scan and removal steps.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If a BrowserModifier alert in Windows Security keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove BrowserModifier yourself 2 steps, about 6 minutes, no software needed.
BrowserModifier: summary
| Type | A Microsoft Defender detection category for programs that change browser settings; not one virus. The families range from search toolbars to the payload of a trojan downloader |
|---|---|
| Risk | Medium for the adware families (Zwangi, Prifou): ads, redirects, changed search results and shortcuts. High if the report also names a trojan downloader, as with Foniad |
| Symptoms | The alert itself, often the only sign; ads on every site, searches opening on another page, a changed home page, redirects, notifications, a shortcut that opens another address |
| How to get rid of it | Quarantine and remove the item in Protection history, run a full scan, uninstall programs you did not add, check scheduled tasks and browser shortcuts, remove extensions, reset each browser, run Defender Offline |
| Our check (6 October 2026) | No site or PC test: we read Microsoft's entries for Foniad, Zwangi, Prifou and Pokki and the reader threads; no sample was run |
| First seen | Zwangi entry 16 September 2009; Prifou 19 November 2015; Foniad 9 April 2018; our first guide 10 January 2020 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Detection | Microsoft: BrowserModifier:Win32/<Family>, for example Foniad, Zwangi, Prifou or SupTab!blnk. Pokki has not been detected since November 2015 |
|---|---|
| Not to be confused with | Dofoil, the coin-miner campaign Microsoft compared Foniad with, and with the browser hijackers of Mac and Android, which use other names |
| Distribution | Software bundles, third-party download sites, ads and fake updates; for Foniad a trojan downloader with a compromised media app |
| Damage | No encrypted files. Documented: ads, redirects, changed search results, allowed notifications and changed shortcuts. Passwords and money are not documented for the modifiers themselves, only for a trojan that came with one |
| Evidence | Microsoft's entries for four families, Microsoft's posts on Foniad and three reader threads; no sample was run |
| Browsers | Internet Explorer, Firefox and Chrome in Microsoft's old entries; Chrome for Foniad. Edge and Safari steps are kept from our 2020 guide |
| Name | BrowserModifier |
| Program | A BrowserModifier alert in Windows Security |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against Microsoft's encyclopedia entries for Foniad, Zwangi, Prifou and Pokki, Microsoft's posts on Foniad of 10 and 13 April 2018, Microsoft Learn and Microsoft Support pages, and a Stack Exchange thread from 2016.
We ran no sample and tested no PC; the removal steps follow Microsoft's pages and were not tried on a live infection. A quiet result from any check does not clear a PC.
What BrowserModifier is, and what it is not
BrowserModifier is the category word at the start of many Microsoft Defender detection names, not the name of one virus. A name such as BrowserModifier:Win32/Zwangi says what Microsoft thinks the program does, which is change the browser, and what it runs on, which is a Windows program. Our 2020 guide called it a malicious program that diverts traffic; that fits some entries and not others.
- 1
What the name is
Microsoft names a detection as Type:Platform/Family. BrowserModifier is the type, Win32 is the platform and the last part is the family, such as Zwangi or Prifou. Microsoft's entry for Prifou describes the type as a program that can change your web browser settings without adequate consent. Our 2020 guide called it a heuristic name for programs that hijack browsers; the word heuristic is ours, and the Microsoft entries we read do not use it.
- 2
How wide the name is
Our 2020 guide said it covers everything from harmless adware extensions to a trojan, and it spoke of thousands of programs. We cannot confirm that count. What we can confirm is the spread: the Microsoft entries we read range from an unwanted search toolbar (Zwangi) and an ad injector (Prifou) to a polymorphic program that a trojan downloader installed (Foniad).
- 3
Why it shows on a PC
Most of these programs arrive in a bundle with software you chose, after an ad, or with a fake update prompt, and a few come from a trojan downloader that is already on the PC. The alert is what your security software says when it finds one. It does not tell you which of those routes you were on.
- Shown by
- Microsoft Defender Antivirus and the other Microsoft antimalware products, in Windows Security and in the older Windows Defender window
- Usual form
- BrowserModifier:Win32/Family, sometimes followed by a suffix such as !blnk or !rfn
- Platform
- Windows programs. Win32 does not mean your Windows is 32-bit. The entries we read are all for Windows, so a Mac would show other names
- Is it one program?
- No. Each family is a different program with its own files, behaviour and alert level
- Still in use
- Microsoft's encyclopedia still carries the type: we found current entries such as Xeelyak, Linkhortry and Neobar in search results. We did not check when each was written
So the useful questions are which family the alert names, which file or shortcut it points to, and whether you installed something around the time it began. The next chapters help you answer them before you delete anything or allow anything.
Is BrowserModifier dangerous? What it collects
What we checked on 6 October 2026, and what we could not
There is no website behind this name, so our usual site test (notification request, pop-ups, redirects, service worker) had nothing to load. We ran no sample and tested no PC. We read the Microsoft entries and the threads where readers asked about the alert.
BrowserModifier detections · sources read on 6 October 2026
- The name is a real Microsoft labelWe opened Microsoft's encyclopedia entries for BrowserModifier:Win32/Foniad, Zwangi, Prifou and Pokki on 6 October 2026. An alert with this name is a security product's finding, not a scam message that only imitates one.
- A site to testNone. The name belongs to programs and shortcuts on a PC, not to a domain, so we cannot say anything from our side about notifications, pop-ups or redirects.
- A sample of any familyNot run. What the families do comes from Microsoft's entries and tweets of 2015 to 2018. A copy that reaches a PC today may differ.
- Whether the old families still circulateNot known. The newest entry we read, Foniad, is from April 2018; Zwangi and Prifou were last updated in September 2017. We did not look for newer copies.
- Whether a quiet PC is cleanNot something we can say. Adware is built to hide, and a scan that finds nothing today is one scan on one day.
Medium risk The alert is real, and what is behind it ranges from an ad-injecting program to the payload of a trojan downloader. A quiet result on this one reading of the sources clears nothing; the steps below are written for the worst case and stop early if the first scan is clean and the alert does not return.
How to read the alert, part by part
Microsoft explains the type and the platform but not every suffix, so the table separates what the alert shows from what it does not.
| Part | What it shows | What it does not show |
|---|---|---|
| BrowserModifier: | Microsoft's category: a program that changes browser settings | Whether it is a harmless-looking toolbar or part of a trojan's payload. Zwangi is the first, Foniad was installed by the second |
| Win32/ | A Windows program, file or shortcut | That your Windows is 32-bit |
| Zwangi, Prifou, Foniad, SupTab | The family name Microsoft gave | The name you see in your list of programs. Zwangi alone appears under 57 different names |
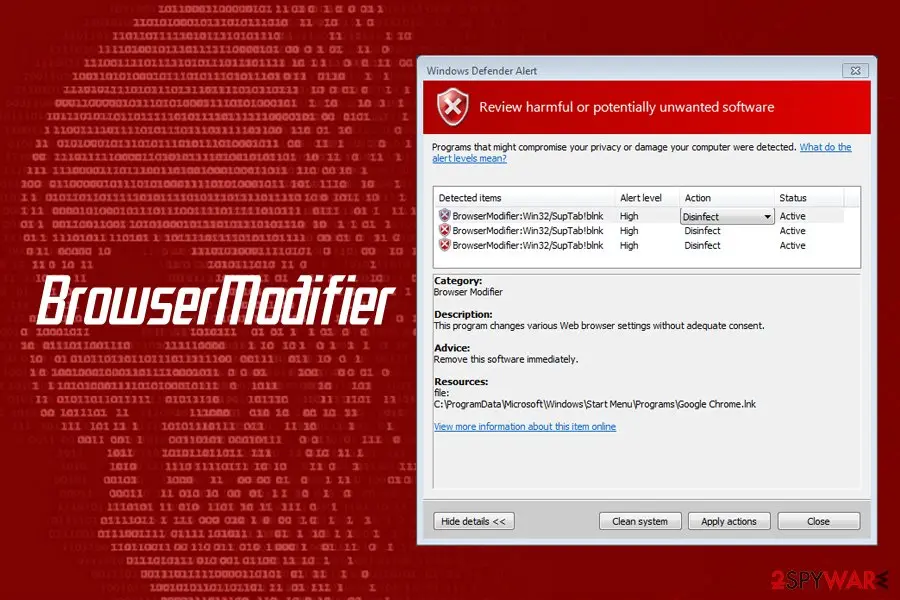
| !blnk, !rfn | A suffix after the family name | What it means. We found no Microsoft page that explains it. Microsoft's !rfn pages carry only a general text about a threat that can perform actions of a malicious actor's choice, and our 2020 picture shows !blnk on a shortcut file |
| Alert level High | Microsoft's alert level for the family. Zwangi and Prifou are listed as a high threat | That anything bad has happened on your PC |
| Resources: file | The file Defender flagged. In our 2020 picture it is the Google Chrome shortcut in the Start Menu folder | That Chrome itself is damaged. A shortcut can be changed so that it opens another address |
The families named most often
Our 2020 guide said it would look over the most prolific versions. These are the ones it named, with what Microsoft's own entry says today, plus two more that readers meet.
| Family | What Microsoft says | What our 2020 guide said | Status |
|---|---|---|---|
| BrowserModifier:Win32/Foniad | A prevalent browser modifier that opens the browser and visits several sites in a series of redirects, and configures Chrome to allow desktop notifications. Highly polymorphic: thousands of distinct files in the first hours. Published 9 April 2018 | Acts as a trojan and installs a cryptominer | Corrected: the miner and the DNS change came from the trojan downloader that installed it |
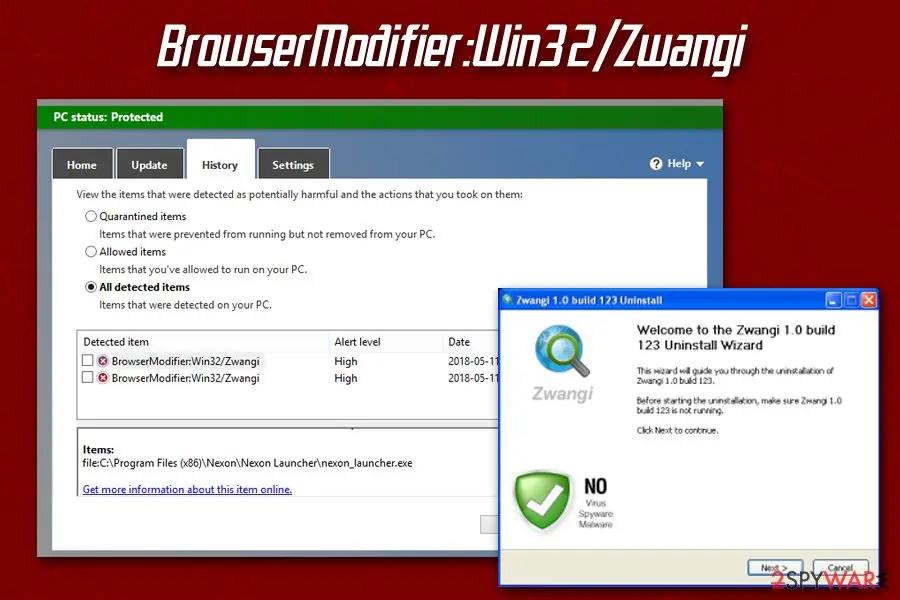
| BrowserModifier:Win32/Zwangi | Changes your search results and shows pop-up ads. Published 16 September 2009, updated 15 September 2017. High threat | Also known as Zwangi 1.0 build 127; renamed several times; drops hundreds of files; takes screenshots | Mostly confirmed; the file count and the screenshots are corrected below |
| BrowserModifier:Win32/Prifou | Can change browser settings without adequate consent; installed with software from third-party sites. Published 19 November 2015, updated 15 September 2017. High threat | A standalone PriceFountain application plus an add-on; ads marked PriceFountain | Confirmed in part; the infection count could not be re-checked |
| BrowserModifier:Win32/Pokki | No longer detected after definition 1.209.1398.0 in November 2015, because it does not violate Microsoft's criteria for unwanted software | No longer recognized by most anti-malware engines and considered safe to use since November 2015 | Corrected: Microsoft says it stopped detecting it. Other products may differ |
| BrowserModifier:Win32/SupTab!blnk | We found no entry with this exact name; the alert appears in the picture of our 2020 guide and in 2016 reader threads, on browser shortcut files | Not discussed; it is the alert in the guide's first picture | Added: see the reader cases |
| BrowserModifier:Win32/Linkhortry | Modifies browser shortcut files, so that the browser opens certain websites when started from them (Microsoft's summary, seen in search results) | Not mentioned | Added: it explains why a shortcut is flagged |
| BrowserModifier:Win32/Xeelyak | Unwanted software that alters the Windows experience without your consent or control (Microsoft's summary, seen in search results) | Not mentioned | Added: a newer entry of the same type |
Foniad, April 2018: one family and the trojan that carried it
Our 2020 guide said Foniad acts as a trojan, changes DNS settings and installs a cryptominer. Microsoft's own posts split that between two programs: Foniad is the browser modifier, and a trojan downloader installed it, the miner and the DNS change.
| Piece | Microsoft detection name | What Microsoft says it does |
|---|---|---|
| The downloader | TrojanDownloader:Win32/Esendi.A | Installs the other pieces. It modifies the DNS server settings, which lets attackers control answers to DNS queries and manipulate where most network connections go |
| The compromised media app | TrojanDropper:Win32/Adpernok | One of the downloader's payloads. Microsoft traced infections to a compromised media app |
| The browser modifier | BrowserModifier:Win32/Foniad | Runs as xsetup.exe, opens Chrome and visits several sites in a series of redirects, and sets Chrome to allow notifications from those sites |
| The coin miner | Trojan:Win32/CoinMiner.CZ | A trojanized version of an XMR miner that mines Monero. Installed in some cases |
| The adware component | Adware:Win32/Adposhel | A .dll adware component the downloader also installs |
- File name
- xsetup.exe, used by every copy Microsoft saw although the files differ
- How many copies
- Several millions of versions, Microsoft said on 10 April 2018, trying to infect and re-infect hundreds of thousands of machines. Versions are not victims, so the old figure of hits is not a count of infected PCs
- Re-infection
- One component tries to infect again with a scheduled task, per Microsoft on 13 April 2018. That is why a manual removal can seem to come undone
- Chrome registry keys
- It sets DefaultNotificationsSetting under HKEY_LOCAL_MACHINE\SOFTWARE\Policies\Google\Chrome, and adds addresses to NotificationsAllowedForUrls under the same key
- Site addresses in Microsoft's entry
- acinster[.]info, aclassigned[.]info, efishedo[.]info, enclosely[.]info, insupposity[.]info, maraukog[.]info, suggedin[.]info
- Money
- Microsoft says the sites it visits might be generating revenue through ad impressions
If your alert names Foniad, treat the PC as one that a trojan downloader may have visited, not only as one with a browser add-on. The check and removal chapters below include the DNS, notification and scheduled-task steps for that case. We did not test them against a live Foniad copy.
Zwangi: one program under 57 names
Zwangi is the oldest family in our 2020 guide and the best documented. Microsoft lists the folders, files, registry entries and the service it creates, which is the easiest route to checking whether a PC has it.
| What | What Microsoft's entry says | Note |
|---|---|---|
| Entry dates | Published 16 September 2009, updated 15 September 2017. Aliases Mal/BHO-S (Sophos) and Spyware.Screenspy (Symantec) | Our 2020 guide said first detected in 2009: correct |
| Uninstall entry | May be called Zwangi 1.0 build 127. The entry says the program may create an uninstaller in the Control Panel | Our 2020 picture shows the uninstall wizard of build 123, so the build number varies |
| Screen names | 57 names, among them QueryExplorer, SeekService, Findbasic, QuestBrwSearch, Weemi, Wyyo and Zwangi itself. Each copy uses one | Our 2020 guide named QueryExplorer, SeekService and Findbasic: correct |
| Folders | %ProgramFiles%\<Screen name> and %APPDATA%\<Screen name> | Our 2020 guide said hundreds of .dll and .exe files; the entry lists three files per name: <Screen name>.dll, <Screen name>.exe and Uninstall.exe, plus one dropped installer such as zwangi127.exe |
| Registry and service | Values under HKLM\Software\<Screen name> and an Uninstall key. It installs a service, for example ZwangiSearch Service, that starts automatically under LocalSystem | Our 2020 guide said a scheduled task. Microsoft's entry lists a service, not a task, so we corrected it |
| Browsers | Seen in the wild on Internet Explorer 6, 7 and 8, Firefox 3.6 and Chrome Beta | Our 2020 list of browsers was cut off; this is Microsoft's list. The browsers are old, which tells you the age of the family |
| Search results | Turns what you type in the address bar into a search on its own pages: questbrowse.com, weemi.com or zwangi.com | Matches our 2020 guide |
| 404 page | May replace the error page the browser shows for an address that cannot be resolved | Matches our 2020 guide |
| Pop-ups | Shows pop-up messages tied to about a hundred keywords, among them auction, book, free, game, shop, travel and weather in several languages | Matches our 2020 guide, which said keywords |
| Screenshots | Not in the entry. The only hint is Symantec's alias name Spyware.Screenspy | Our 2020 guide said it takes screenshots without permission. We could not confirm it, so treat it as not confirmed |
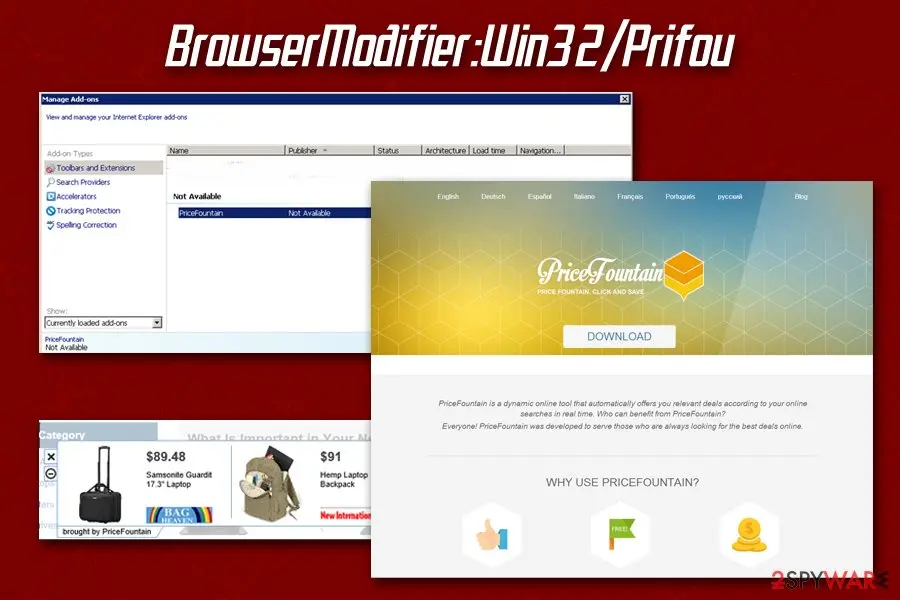
Prifou and PriceFountain
Prifou is the family behind ads marked PriceFountain. Microsoft lists it as a high threat and says it can install when you download other software from third-party websites.
| What | What Microsoft's entry says | Note |
|---|---|---|
| Entry dates | Published 19 November 2015, updated 15 September 2017. Microsoft links its post about the September 2016 release of the Malicious Software Removal Tool | We could not open that post, so we could not re-check the number our 2020 guide gave |
| How it arrives | With other software downloaded from third-party websites | Matches our 2020 guide |
| Program name | The entry in the program list may be called PriceFountain | Our 2020 guide called it a standalone application: correct |
| Ads | Ads carry the attribution name Price Fountain. It uses two ways: a browser add-on that it enables by itself, and rundll32.exe running a DLL that injects ads into the browser | Our 2020 guide listed phrases such as Ads by PriceFountain. We could confirm only the name Price Fountain and the words brought by PriceFountain in our picture |
| Scheduled tasks | Adds scheduled tasks that run it and check for and download updates | Not in our 2020 guide. A task you did not create is one of Microsoft's listed signs |
| Uninstaller | Adds an uninstall option. Microsoft says to remove the program from the list of programs and the add-on from the browser | Matches the normal removal below |
| Infection count | Not given in the entry | Our 2020 guide said around 6.8 million infections in two months, mostly in the USA and Europe. We could not re-check it, so it is not repeated as a fact |
| Slowdowns and crashes | Not stated for Prifou | Our 2020 guide said slowdowns and crashes. Plausible for an ad injector, but not something Microsoft's entry says |
The families over time, 1994 to 2026
The dates come from Microsoft's own entries and posts, the reader threads we found and our 2020 guide. The 1994 line is the old guide's starting point and not a Microsoft date.
27 October 1994
The first banner ad
Our 2020 guide began with online advertising as a gold mine from 1994. The first banner ad is usually dated 27 October 1994, an AT&T banner on HotWired (thefirstbannerad.com). We did not check the date further. The next step it described is the one that matters here: people building programs that put ads on thousands of PCs, paid per click and per install.
16 September 2009
Zwangi enters Microsoft's list
The entry for BrowserModifier:Win32/Zwangi is published and is last updated on 15 September 2017.
29 October 2015
Pokki entry published
Microsoft stops detecting Pokki after definition 1.209.1398.0 in November 2015, because it does not violate the criteria for unwanted software.
19 November 2015
Prifou entry published
The entry for Win32/Prifou, last updated 15 September 2017. In September 2016 Microsoft wrote about Prifou in its Malicious Software Removal Tool post.
December 2016
Readers ask why SupTab!blnk keeps coming back
A reader on Information Security Stack Exchange (12 December 2016) and one on Reddit describe the alert returning after Clean system. See the reader cases below.
7 to 13 April 2018
Foniad
Microsoft says on 10 April that since Saturday (7 April) a highly polymorphic browser modifier has been trying to infect and re-infect hundreds of thousands of machines. On 13 April it names the downloader and the other pieces.
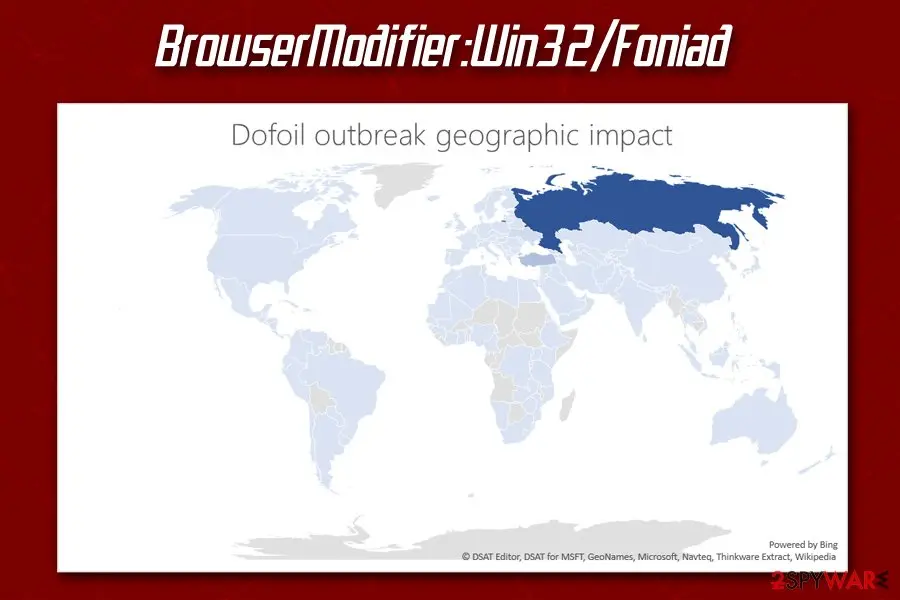
From our 2020 guide, captioned there as Foniad: a Microsoft map titled Dofoil outbreak geographic impact, darkest on Russia. It shows Dofoil, the coin-miner campaign Microsoft compared Foniad with, and not Foniad. We found no country map for Foniad itself. 11 May 2018
A game launcher flagged as Zwangi
Our 2020 picture of the Windows Defender history shows two High detections of Zwangi on a file of the Nexon Launcher game client, dated 11 May 2018. We do not know whether it was a false alarm.
10 January 2020
Our first guide
The guide that this page replaces. It was 1,572 words, written as if BrowserModifier were one infection.
6 October 2026
This rewrite
Read against Microsoft's entries, with the Foniad and Zwangi claims corrected.
Reader cases: when the alert keeps coming back
These are the cases we could read. They are second-hand, from forums, and they show what readers tried. They are not proof of what your alert is.
| Case | What the source says | How it ended |
|---|---|---|
| BrowserModifier:Win32/SupTab!blnk, Information Security Stack Exchange (12 December 2016) | The reader's Defender kept detecting it, and it came back a few seconds after Clean system or Apply actions. BitDefender 2017, AdwCleaner, Malwarebytes and HitmanPro found nothing. The browsers looked healthy, with no extensions or changed search engine and no CPU load | An answerer pointed to Microsoft Answers threads where a program called VulcanRT appeared in common, and suggested checking add-ons, resetting browsers and cleaning temp files. The page shows no reply from the asker |
| The same alert, quoted in that answer from Microsoft Answers | A reader reset Internet Explorer and ran several tools. Only RogueKiller found anything. Defender's alert then pointed to VulcanRT, which they uninstalled, with Chrome, two redistributables and a Steam game | The warning did not return. The reader did not know which step helped |
| The same alert, quoted from Reddit r/techsupport | A reader deleted the shortcut files listed in the alert, for Chrome and Internet Explorer, and said it looked like a false positive. A System Restore to an earlier point did not help | Fixed for that reader, who lost the Start Menu shortcuts and said they could live without them |
The pattern fits what Microsoft says about Linkhortry, a family that modifies browser shortcut files. A shortcut that is flagged and keeps coming back is a different problem from an extension you can remove in the browser, so the removal chapter checks the shortcut first.
How the money is made
A browser modifier is paid for what it sends you to. That is the reason for the ads, the changed search results and the redirects, and it is also why removing one thing does not always stop it.
| Route | How it earns | Source |
|---|---|---|
| Ads shown on the sites you visit | Pay-per-click and pay-per-install: ads carry links to third-party websites, such as shops, services and gaming portals. Prifou injects them and marks them with its attribution name | Our 2020 guide; Microsoft's Prifou entry |
| Search results on its own pages | The address bar becomes a search box on pages run by the program's makers, as Zwangi does with questbrowse.com, weemi.com and zwangi.com | Microsoft's Zwangi entry |
| Redirects to sites that earn from impressions | Foniad opens sites in a series of redirects. Microsoft says they might be generating revenue through ad impressions | Microsoft's Foniad entry |
| Traffic generated in the background | Our 2020 guide said malware can also be installed on a PC to make background traffic to preset sites. We found no Microsoft entry for a browser modifier that does only this | Our 2020 guide; not confirmed |
What can actually go wrong
Our 2020 guide said these programs can steal personal information, cost you money and even lead to identity theft. The Microsoft entries we read for the browser modifiers say nothing like that. The higher risks belong to a trojan that installed one.
- Medium
Ads and search results you did not choose
Intrusive ads on every site, sponsored links in search results and a changed start page or new tab. This is what Zwangi and Prifou are documented to do, and it can lead you to a page that sells you something.
- Medium
Redirects to pages you did not ask for
Foniad opens websites in a series of redirects. Zwangi sends your searches to its own pages and can replace the 404 page. A redirect can end on a shop, a scam page or a download.
- Medium
Notifications allowed without asking
Foniad sets Chrome to allow desktop notifications for the sites it visits, through registry keys under the Chrome policy key. Those notifications can show ads after the sites are closed.
- Medium
Shortcuts that open another address
A shortcut file can be modified so that the browser opens certain websites when started from it. That is what Microsoft says Linkhortry does, and our 2020 picture shows the shortcut as the flagged resource.
- High
Other malware, if a trojan installed it
Foniad was installed together with a DNS changer, a Monero coin miner and an adware DLL. Our 2020 guide put the miner and the DNS change on Foniad itself. Microsoft puts them on the downloader. Either way, when Foniad is on a PC the rest may be too.
- Low
Registry changes, crashes and slowdowns
Our 2020 guide said registry changes can corrupt Windows and cause persistent crashes. The Microsoft entries we read list registry changes, services and scheduled tasks but do not say the PC crashes. An ad injector can slow a browser, so slowness is a reason to scan, not a symptom of one family.
- Low
Passwords, money and identity
Nothing in Microsoft's entries for Zwangi, Prifou or Foniad says they take passwords or card numbers. A trojan that came with them, such as a downloader, could. That is why the after-clicked chapter is written for the trojan case, and we do not claim it happened to you.
What you may notice
Our 2020 guide said the symptoms vary by version and that some background activity cannot be seen without advanced knowledge. Both are true. The signs below are the ones we can tie to a source.
| Sign | What we found |
|---|---|
| The alert itself | Often the only sign. It came from Windows Defender or Windows Security in every case we read |
| Intrusive ads on every site | Documented for Prifou: ads marked Price Fountain. Our 2020 guide listed ads on all sites as the first symptom |
| Search results full of extra links, or your searches opening on another page | Documented for Zwangi: address-bar searches open on questbrowse.com, weemi.com or zwangi.com |
| Random redirects to suspicious websites | Documented for Foniad: the browser opens sites in a series of redirects |
| Home page and new tab changed, extensions you did not add | Our 2020 guide listed them. Prifou adds an add-on that it enables by itself. We found no Microsoft entry that gives a name for one extension to look for |
| New registry keys, scheduled tasks, services, processes or files | Documented: Zwangi adds a service and folders in %ProgramFiles% and %APPDATA%, Prifou adds scheduled tasks, Foniad adds Chrome policy keys and a re-infection task |
| Nothing visible | Our 2020 guide said some variants run activities that users cannot see. Nothing here lets us rule out a quiet copy |
How BrowserModifier got into your browser
Our 2020 guide listed bundles, ads and fake updates, and a trojan downloader for some. Microsoft's entries agree. None of them says one route for the whole category.
- 1
Bundled with software you wanted
Most of these programs ride with another installer, and the optional parts are often hidden in it on purpose. Microsoft's entry for Prifou says it can install when you download other software from third-party websites. Our 2020 guide said many people do not read the installer, which is why bundling worked so well.
- 2
Third-party download sites
The bundled installers sit on download portals. Our 2020 guide said some of the sites might be trusted and others shady. Pirated software and cracks are the worst place to look, and one reader case below lists a Steam game and two redistributables among the suspects.
- 3
Tricks inside the installer
Our 2020 guide listed pre-ticked boxes, fine print, misleading offers and misplaced buttons. Microsoft's own criteria say software must not install other software without a clear indication of its relationship to the main program, and must not circumvent the browser's consent dialogs.
- 4
An attractive ad or a fake update prompt
Our 2020 guide said some copies arrive after an ad or a fake update message. We have no case of our own to show for it, but it is the same route used by many other adware families.
- 5
A trojan downloader already on the PC
Foniad was installed by TrojanDownloader:Win32/Esendi.A with a compromised media app. Our 2020 guide said some variants were injected by a trojan downloader that was already present. Microsoft's post is the source for that.
The same few habits cover all of them: take software from its maker, choose the Custom or Advanced setup when it is offered, and read the screen before you click Next.
How to remove BrowserModifier
How to remove BrowserModifier and get your search engine back
Remove the extension first.
The search settings only stay fixed once nothing on the PC can change them again.
Which browser shows the ads?
Do not click Allow on device and do not delete a file yet. Our 2020 guide said an alert must not be ignored, and Microsoft says that choosing Allow lets the file run. First write down what Windows says.
Set your search engine and start page
Open Settings > Search engine, choose Change next to the address-bar engine and pick yours, then delete unknown entries under Manage search engines and site search. Under On startup, remove any address you did not set.
Remove extensions you do not recognise
Paste
chrome://extensionsinto the address bar and click Remove on anything you did not install.Full procedure with screenshots: Remove a browser extension
Check the Chrome shortcut and notifications
Right-click the Chrome shortcut, choose Properties and check that Target ends with chrome.exe. Open Settings > Privacy and security > Site settings > Notifications and remove sites you did not allow. If
chrome://policylists notification settings you did not set, see the Foniad chapter.Full procedure with screenshots: Stop website notifications and pop-ups
Reset Chrome
Open Settings > Reset settings > Restore settings to their original defaults and confirm. Start page, search engine and pinned tabs reset and extensions turn off; bookmarks and saved passwords stay.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Set your search engine and start page
Open Settings > Privacy, search, and services > Address bar and search and choose your engine; check Manage search engines for entries you did not add. Under Start, home, and new tabs, remove any address you did not set from When Edge starts and Home button.
Remove extensions you do not recognise
Paste
edge://extensionsinto the address bar and click Remove under anything you did not install.Full procedure with screenshots: Remove a browser extension
Reset Edge
Open Settings > Reset settings > Restore settings to their default values and confirm. Extensions turn off and the start page resets; favourites, history and passwords stay.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Set your search engine and home page
Open Settings > Search and pick another Default Search Engine, removing engines you did not add under Search Shortcuts. In Settings > Home, set Homepage and new windows to Firefox Home (Default) if it shows an address you did not set.
Remove the add-on, or try Troubleshoot Mode
Paste
about:addonsinto the address bar, open Extensions and choose Remove from the three-dot menu of any add-on you do not recognise. If there is no Remove option, the program that installed it controls it: uninstall that program in Windows, then use the menu > Help > Troubleshoot Mode and try again.Full procedure with screenshots: Remove a browser extension
Refresh Firefox
Open the menu > Help > More troubleshooting information and click Refresh Firefox. Add-ons and custom settings are removed; bookmarks, history and passwords stay.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Set your search engine and homepage
Open Safari > Settings > Search and choose a different Search engine. In General, clear or change the Homepage address if it shows an address you did not set.
Remove extensions you do not recognise
In Safari > Settings > Extensions, select anything you did not install and click Uninstall. Check Finder > Applications for a program you did not install and move it to the Bin. BrowserModifier is a Windows name, so this is a general check for Safari, kept because our 2020 guide had Safari steps.
Then, whichever browser you use
Step 1: Uninstall a BrowserModifier alert in Windows Security
A BrowserModifier alert in Windows Security is removed like any other program, from the list of installed apps.
In Windows 11 that is Settings > Apps > Installed apps, in Windows 10 Settings > Apps > Apps & features, and in both you can also use Control Panel > Programs and Features.
Select a BrowserModifier alert in Windows Security, click Uninstall and follow the uninstaller to the end. Then look at the entries just above and below it when the list is sorted by date: bundled programs install at the same minute.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 2: Scan the PC, then run the offline scan
A scan finds the parts of BrowserModifier that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Remove it from Windows 11 and Windows 10
Do the steps in order and stop when a scan from outside normal Windows is clean and the alert has not returned. We did not run these steps on a live infection; they follow Microsoft's pages. Keep Microsoft Defender or your own security product on while you do them.
- 1
Remove the quarantined item
In Protection history open the quarantined item and choose Remove. Microsoft says Remove deletes the threat from your device. Our 2020 guide said an unwanted program can usually be taken out in the Control Panel and that a malware infection needs a scan; both are right, which is why the next steps follow.
- 2
Update and run a full scan
Open Windows Security > Virus & threat protection > Scan options, choose Full scan and click Scan now. Microsoft says a full scan might find hidden threats. Windows Update brings the newest definitions. A scan cannot promise to find every trace.
- 3
Uninstall what came with it
In Settings > Apps > Installed apps uninstall anything you did not install, starting with PriceFountain, a Zwangi screen name or whatever was installed the day the alert began. The program names and uninstall steps are in Uninstall a program or app in Windows On uGetFix. Our 2020 guide said some versions have no uninstaller, are not in the list or install themselves again, so keep the next steps even if the list is clean.
- 4
Check scheduled tasks and services
Press Windows logo + R, type
taskschd.mscand open Task Scheduler Library. Prifou adds scheduled tasks and Foniad re-infects with one, so write down tasks you did not create, with the file each one runs. For a Zwangi service, press Windows logo + R, typeservices.mscand look for a service with a name such as ZwangiSearch Service. We could not confirm the exact name of tasks for any family. - 5
Fix the shortcuts
For each browser shortcut, right-click it, choose Properties and remove any web address after the browser file name in Target. If you are unsure, delete the shortcut and make a new one from the program in Start.
- 6
Remove extensions and reset the browsers
Use the browser tabs above. Our 2020 guide said security experts recommend resetting every installed browser, and that unwanted ads can remain if you skip it. That is right for a modifier of browser settings, so reset each browser after the program is gone, not before.
- 7
Run Microsoft Defender Offline as a second opinion
The steps are in Run a Microsoft Defender Offline scan. It restarts the PC and scans from outside normal Windows, where a program that hides from a running system cannot. Then open Protection history to read the result.
- 8
If Foniad was named: check DNS and notifications
Open Settings > Network & internet, open your Wi-Fi or Ethernet connection and look at DNS server assignment. If you never set a DNS server, it should be automatic. Our 2020 guide said Foniad changes DNS; Microsoft says its downloader does. In Chrome open Settings > Privacy and security > Site settings > Notifications and remove sites you did not allow (Stop website notifications and pop-ups). Our menu names follow Microsoft and Google pages and were not tried on a live copy.
- 9
Update Windows and scan again
Install every update under Settings > Windows Update, then run a quick scan. If the same alert returns after a restart, something still recreates it. Go back to the scheduled tasks and the shortcuts, or restore the PC to a point before the alert with System Restore.
Never download a removal program because a pop-up, a stranger or a phone number tells you to. A real threat does not need a payment page to fix. We name no product as a remover; Windows Security and its Offline scan are already on your PC.
Could it be a false alarm? How to tell and what to do last
Sometimes. Microsoft says potentially unwanted applications are not malware, and it stopped detecting Pokki because it does not violate the criteria. Only Microsoft can confirm that your file is a false positive.
| Points to a real program or infection | Points to a false alarm |
|---|---|
| The file came from a bundle, a download portal, a crack or an email | The file came from the maker's own site and you were expecting it |
| You see ads, a changed home page or redirects as well | The browser works normally and the alert came once |
| Other detections sit beside it, including trojan or miner names | Only one detection, and no other scanner agrees |
| A folder, service or scheduled task with a Zwangi screen name or PriceFountain | A game launcher or program you know, as in our 2020 picture of the Nexon Launcher file |
| The alert returns after Remove and a restart | It stays quarantined after Remove |
- 1
Do not allow it first
Allowing a file lets it run. If you allowed one by mistake, open Virus & threat protection > Protection history, then Allowed threats, and use Don't allow; Microsoft says Windows Security will act on it again the next time it sees it.
- 2
Send it to Microsoft
Microsoft takes files for analysis at microsoft.com/wdsi/filesubmission and says submissions help it decide whether software is malware or unwanted. We did not use the form, so check its wording.
- 3
Turn on blocking for unwanted apps
Microsoft says blocking of potentially unwanted applications is off by default. In Windows Security open App & browser control > Reputation-based protection settings and turn it on, with both Block apps and Block downloads. Block downloads works in Microsoft Edge only.
After removal: keep your search engine and start page
If a trojan came with it: what to do about accounts and files
The scans deal with the PC. These steps deal with what a trojan downloader could have seen or done. Do them if the report named TrojanDownloader, Foniad, a coin miner or DNS changes.
- 1
Change passwords from another device
Email first, then banking, then everything else. Turn on two-step sign-in. Do this before you use banking on the PC.
- 2
Sign out everywhere
Use the sign out of all sessions option in your Google, Microsoft and social accounts so stolen cookies stop working.
- 3
Check your money
Look at card statements and any wallets for payments you did not make. We found no source that says the browser modifiers take card numbers; a trojan could.
- 4
Look for a miner
A coin miner such as Trojan:Win32/CoinMiner.CZ makes the PC slow and hot. Open Task Manager with Ctrl + Shift + Esc and sort by CPU. A process you do not know that uses a lot of it for no reason is a reason to scan again.
- 5
Check browser settings
If the home page, new tab or search engine changed, remove the extension and reset the browser settings. See the browser tabs above.
- 6
Scan again in a week
Run another full scan and a Defender Offline scan a week later, and keep a screenshot of the first alert.
Keep browser modifiers off your PC
The advice of 2020 still holds. These are the habits, with current menu names.
Do
- Download programs from their makers' sites or the Microsoft Store, and take the Custom or Advanced setup when it is offered, so bundled extras can be declined.
- Read each installer screen. Pre-ticked boxes, fine print and a button in an unusual place are the tricks our 2020 guide listed, and Microsoft's criteria say installing other software without a clear indication is not allowed.
- Turn on potentially unwanted app blocking in Windows Security > App & browser control > Reputation-based protection settings. Microsoft says it is off by default.
- Keep Windows Security with Real-time protection on and update it with Windows Update.
- Open each browser's home page and search settings once after installing free software.
- Keep a backup of your documents on a disk you unplug (File History or OneDrive), so a clean-up never costs you files.
- On a public network a VPN hides your IP address from the sites you visit. It does not block a modifier that is already installed.
Don't
- Do not use cracks, keygens or pirated software, or installers from sites that bundle them.
- Do not click an ad or a pop-up that says your browser or player is out of date.
- Do not use Allow on device to stop an alert you have not checked.
- Do not click Next without reading, even if the program is one you wanted.
Questions about BrowserModifier
What is BrowserModifier?
BrowserModifier is the category word that Microsoft Defender puts at the start of a detection name, as in BrowserModifier:Win32/Zwangi, and it is not one virus. It tells you that Microsoft judged a Windows program to change browser settings, such as the home page, the search engine or the shortcuts, without adequate consent. What sits behind the name differs by family:
- an unwanted search toolbar
- an ad injector or
- in Foniad's case
- the payload of a trojan downloader
Read the family name and the file path in the alert, because they decide what to do, not the category word.
Is BrowserModifier a virus?
Usually not in the strict sense, but it can come with one. Microsoft classes Zwangi and Prifou as unwanted software that changes your browser and shows ads, and Microsoft's own criteria say potentially unwanted applications are not malware.
Foniad was different: Microsoft says a trojan downloader installed it together with a coin miner and a DNS changer. So the word on its own does not tell you whether the PC is infected. Check which other detections sit beside it, and remove the program rather than ignore the alert.
How do I remove BrowserModifier from Windows 11 or 10?
Open Windows Security, go to Virus & threat protection and Protection history, and choose Remove on the quarantined item. Then run a Full scan, uninstall any program you did not install, check scheduled tasks and browser shortcuts, remove unknown extensions and reset each browser.
A Microsoft Defender Offline scan is a good second opinion. If the report names Foniad or a trojan, also check DNS and notifications and change your passwords from another device. We did not test these steps on a live copy, so stop only when a scan is clean and the alert stays away.
Why does Windows Defender keep finding BrowserModifier after I clean it?
Something still recreates it, or the alert points to a shortcut that stays modified. Readers in 2016 saw BrowserModifier:Win32/SupTab!blnk return within seconds of Clean system, and other scanners found nothing. One later uninstalled a program called VulcanRT and the alert stopped, though they did not know which step helped.
Foniad is documented to re-infect with a scheduled task. Check Task Scheduler, the browser shortcuts and recently installed programs, and run the Defender Offline scan. If nothing else helps, a restore point from before the alert is an option.
What is BrowserModifier:Win32/Foniad?
It is a polymorphic browser modifier that Microsoft described in April 2018. It runs as xsetup.exe, opens Chrome and visits listed sites in a series of redirects, and sets Chrome to allow notifications from them.
Microsoft says a trojan downloader, TrojanDownloader:Win32/Esendi.A, installed it along with a compromised media app, a Monero coin miner and an adware DLL, and that the downloader changes the DNS settings. Our 2020 guide put the miner and the DNS change on Foniad itself, which Microsoft's posts do not. Treat a Foniad alert as a possible trojan case.
What is BrowserModifier:Win32/Zwangi?
It is a browser modifier that Microsoft first listed on 16 September 2009 and last updated in September 2017. It changes your search results and shows pop-up ads, turns address-bar searches into searches on questbrowse.com, weemi.com or zwangi.com, and can replace the 404 page.
It installs under one of 57 screen names, such as QueryExplorer or Findbasic, with a folder in Program Files and AppData and a service that starts automatically. The program list may show Zwangi 1.0 build 127. Microsoft rates it a high threat, and it was built for old browsers.
Could the BrowserModifier alert be a false positive?
Yes, in some cases, though only Microsoft can confirm one. Microsoft stopped detecting Pokki in November 2015 because it does not violate its criteria, and our 2020 picture shows Zwangi flagged on a game launcher file, which looks odd.
A single detection on a program from its maker's own site, with no ads or changed settings, points that way. A detection on a shortcut after a bundled download, or beside a trojan name, does not. Do not choose Allow on device; send the file to Microsoft through its submission page and keep it quarantined meanwhile.
How does BrowserModifier get on my PC?
Mostly in a bundle with software you chose. Microsoft says Prifou can install when you download other software from third-party websites, and our 2020 guide added pre-ticked boxes, fine print, misleading offers and fake update prompts. A few came from a trojan downloader that was already on the PC, as with Foniad.
Cracks and pirated software are the worst source. Choose the Custom or Advanced setup, read each screen and download only from the maker's site or the Microsoft Store. Microsoft also lets you turn on blocking for unwanted apps, which is off by default.
Can BrowserModifier steal my passwords or money?
Nothing in Microsoft's entries for Zwangi, Prifou or Foniad says they take passwords or card numbers. Our 2020 guide said these programs can lead to scams and identity theft, and we could not confirm it for the modifiers themselves.
Their documented harm is ads, redirects, changed search results, notifications and changed shortcuts. The risk rises if a trojan downloader came with them, so check the other names in the report. If one did, change passwords from another device, sign out everywhere and watch your statements.
Will Fortect remove BrowserModifier?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For BrowserModifier, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Microsoft Security Intelligence: BrowserModifier:Win32/Foniad (published 9 April 2018) (read October 6, 2026)
- Microsoft Threat Intelligence (@MsftSecIntel) on Foniad, Esendi and CoinMiner.CZ, 10 and 13 April 2018 (read October 6, 2026)
- Microsoft Security Intelligence: BrowserModifier:Win32/Zwangi (published 16 September 2009, updated 15 September 2017) (read October 6, 2026)
- Microsoft Security Intelligence: Win32/Prifou (published 19 November 2015, updated 15 September 2017) (read October 6, 2026)
- Microsoft Security Intelligence: BrowserModifier:Win32/Pokki (published 29 October 2015, updated 13 July 2017) (read October 6, 2026)
- Microsoft Security Intelligence: BrowserModifier:Win32/Linkhortry (summary read in search results) (read October 6, 2026)
- Microsoft Security Intelligence: BrowserModifier:Win32/Xeelyak (summary read in search results) (read October 6, 2026)
- Microsoft Learn: How Microsoft identifies malware and potentially unwanted applications (updated 10 September 2026) (read October 6, 2026)
- Microsoft Support: Protect your PC from potentially unwanted applications (read October 6, 2026)
- Microsoft Support: Protection History in the Windows Security App (search excerpt) (read October 6, 2026)
- Microsoft Support: Virus and Threat Protection in the Windows Security App (search excerpt) (read October 6, 2026)
- Information Security Stack Exchange: Microsoft Windows Defender keeps detecting BrowserModifier:Win32/SupTab!blnk (12 December 2016) (read October 6, 2026)
- The First Banner Ad: AT&T "You Will", 27 October 1994 (search excerpt) (no longer online) (read October 6, 2026)
- 2-spyware.com: Remove BrowserModifier (our own guide of 10 January 2020, replaced by this one) (read October 6, 2026)