
Luca Stealer: what it is and how to remove it
Luca Stealer is a menacing malware that has been recently discovered by security researchers at Cyble. According to the report, the virus stems from an already existing malware written in Rust, which operates as a data stealer.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If Luca Stealer keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove Luca Stealer yourself 3 steps, about 9 minutes, no software needed.
Start the steps
Luca Stealer: summary
| Name | Luca Stealer |
|---|---|
| Type | Trojan, malware |
| Symptoms | No symptoms are present on the infected computer |
| Capabilities | Steals data from multiple communication platforms, gaming platforms, and browsers. Can take screenshots and determine user's personal information |
| Dangers | Personal information disclosure to cybercriminals, account loss, financial losses, identity theft |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Distribution | Not recorded in the old report |
|---|---|
| Damage | Not recorded in the old report |
| Evidence | 4 write-ups by security sites; details still limited |
| First seen | 27 July 2022 |
| Facts checked | 6 October 2026 |
What Luca Stealer does
From our report of Jul 2022 · not reviewed since
More from our earlier report on Luca Stealer
- Perform a full system scan with security software
- Malware can seriously tamper with Windows systems, causing errors, crashes, lag, and other stability issues after it is terminated.
- The developer of the stealer appears to be new on the cybercrime forum and likely leaked the source code of the stealer to build a reputation for themselves.
- The developer has also provided the steps to modify the stealer and compile the source code for ease of use.
- The stealer has been updated thrice, and the malware developer is continuously adding multiple functionalities at the time of our analysis.
- Luca Stealer also affects other applications installed on the system, such as communication apps (Skype, ICQ, Telegram, Element, Steam, Discord), gaming apps (Uplay), crypto add-ons installed on the browser (Coin98, Coinbase Wallet, BitApp Wallet, OneKey, Nabox Wallet, etc.), and even password managers (1Password, Norton Password Manager, Dashlane, KeePassXC, Bitwarden, etc.), which is relatively uncommon for this type of malware.
What Luca Stealer collects and where it sends it
From our report of Jul 2022 · not reviewed since
Luca Stealer malware: a dangerous threat that can steal your valuable data
Luca Stealer is a menacing malware that has been recently discovered by security researchers at Cyble.
According to the report, the virus stems from an already existing malware written in Rust, which operates as a data stealer. Since the source code of this malware was published on GitHub for everybody to see on July 3, 2022, it seems like other parties decided to make it their own and now are actively spreading Luca Stealer around.
The main purpose of the virus is to steal various data using exfoliation techniques. The main targets of malware are those who enjoy gaming and are into crypto, as it collects account details of various gaming platforms, crypto-wallets, chat applications, Chrome-related data, and similar.
Even though its detection levels are currently relatively low, it is recommended to remove the Luca Stealer virus as soon as possible, as serious privacy issues could be experienced by those affected.
From our report of Jul 2022 · not reviewed since
Luca Stealer analysis
Rust is a cross-platform programming language, which allows the info-stealer to expand its operations to a much larger scale potentially.
However, since malware is relatively new, it is currently only operating on Windows operating systems, so users who run use this platform should be wary.
According to researchers at Cyble, the developer of the stealer malware is relatively new to the hacker forums, although they already provided instructions on how to modify it:
While the malware strain is relatively new, its data-stealing capabilities are quite broad. First of all, it targets 30 Chromium-based browsers, including Chrome, Opera, MS Edge, Vivaldi, Dragon, Brave, and more. Most users rely on Chromium-based browsers nowadays, so choosing it was not accidental. Malware can pick up and deliver passwords, credit card details, and other crucial information harvested from browsers.
Besides sensitive details, the malware also collects a variety of technical details about the device used. For example, it uses "distro_os" function to get the name of the operating system distribution or version, while "devicename" is used to get the device name used to identify the device for Bluetooth pairing. In addition, it collects information about network transmission rates, total memory, a list of running processes, and more.
The data stealing process is done via Discord or Telegram bots - the former will be used if the collected data exceeds 50MB. It is worth noting that the large size of data may come from the fact that the malware makes screenshots and saves them as PNG files.
All the collected files are packed into a ZIP archive, which is then named based on the contents inside, making it easier for the attackers to access the information they need.
How Luca Stealer got on your PC
From our report of Jul 2022 · not reviewed since
A trojan is an umbrella term for a type of malware that's defined by its distribution rather than functionality.
In this case, we are, of course, talking about an info-stealer, although ransomware, for example, may also be identified as such. To make it clear, a trojan is defined by the fact that users believe they are installing something harmless, while in reality, they are letting malware infiltrate their device.
As such, there could be plenty of methods that can put users in such a situation, for example, malicious spam email might include a misleading message and an attachment, which would look like it was delivered from a reputable company or from a person a victim already knows. While the victim believes that the attachment is safe, opening it would immediately download and install a malicious payload on their machine.
Trojans can also be spread in the following ways:
To avoid being a victim of a trojan attack such as Luca Stealer, you should always be vigilant and follow the best security practices. For example, you should never download pirated software or cracks, as the infection rate of various malware - not only Luca Stealer - is likely.
Employing effective ad-blockers might prevent the execution of malicious ads and fake updates, although it is not a secret that you should never download software from random websites which claim that something is missing or needs to be updated.
- Repacked software
- Pirated programs and software cracks
- Fake updates
- Malicious ads, etc.
How to remove Luca Stealer
How to remove Luca Stealer and secure your accounts
A stealer usually takes what it wants within minutes and may already be gone.
The scan comes first, then the accounts.
Step 1: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 2: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Access Safe Mode to remove malware from Windows
If malware is not letting you use antivirus in normal mode, access Safe Mode and perform a full system scan from there. Safe Mode reduces the number of active processes, which may prevent some malware from interfering with security tools.
Windows 10 / Windows 11
- Right-click on Start button and select Settings.
- Select System (Windows 11) or Update & Security (Windows 10).
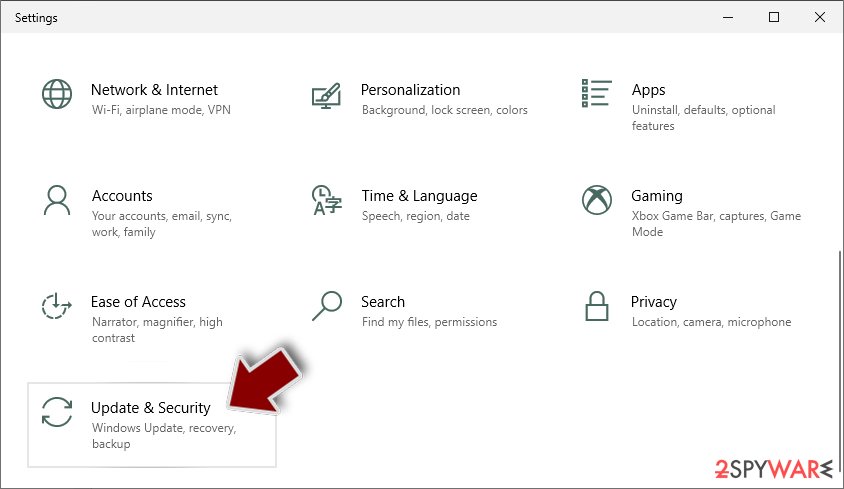
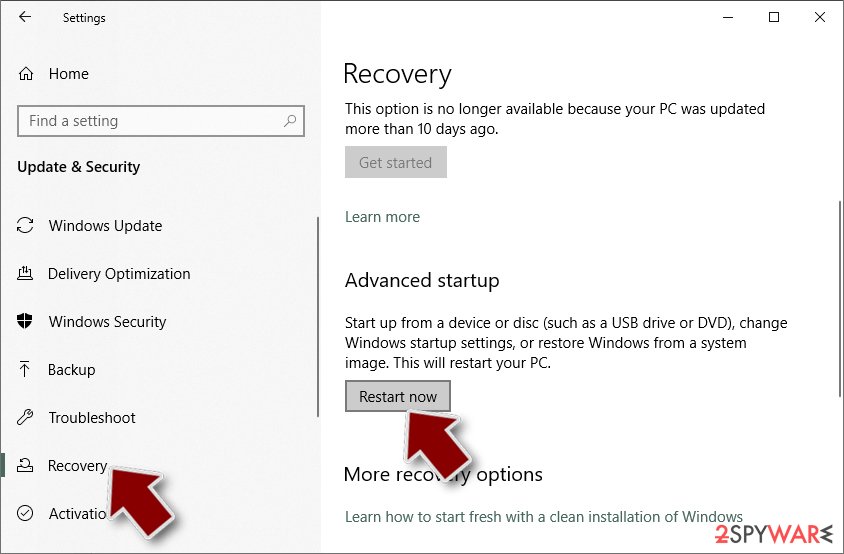
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
- Select Troubleshoot.
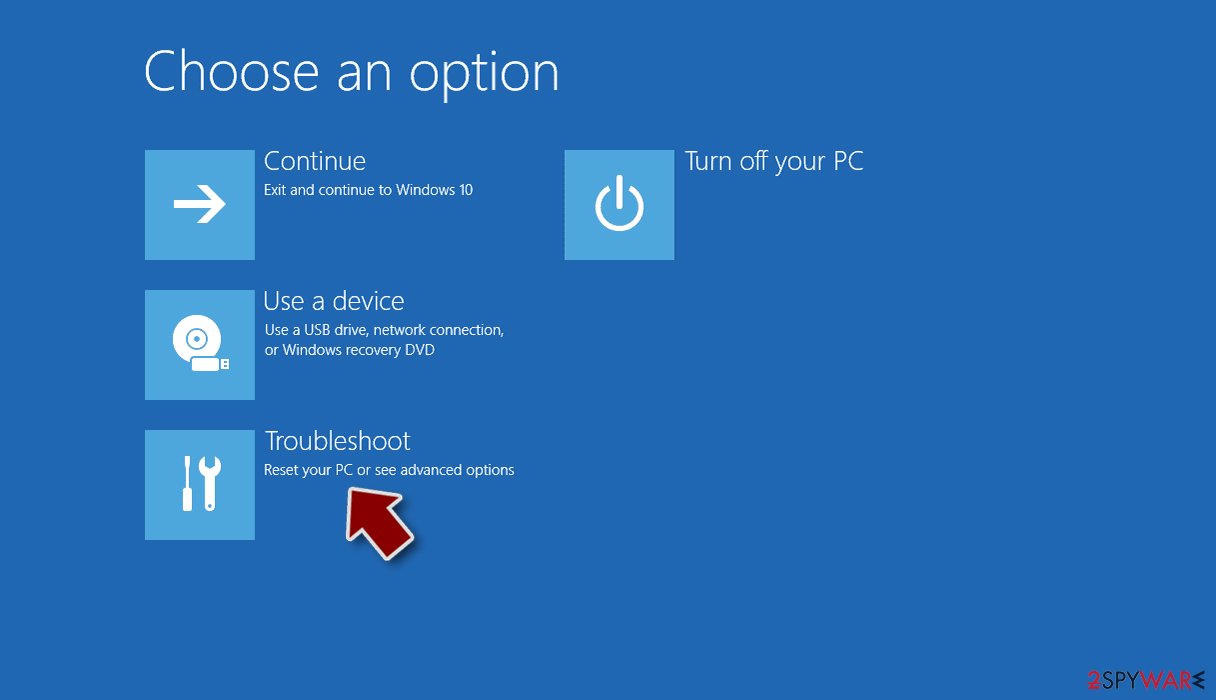
- Go to Advanced options.
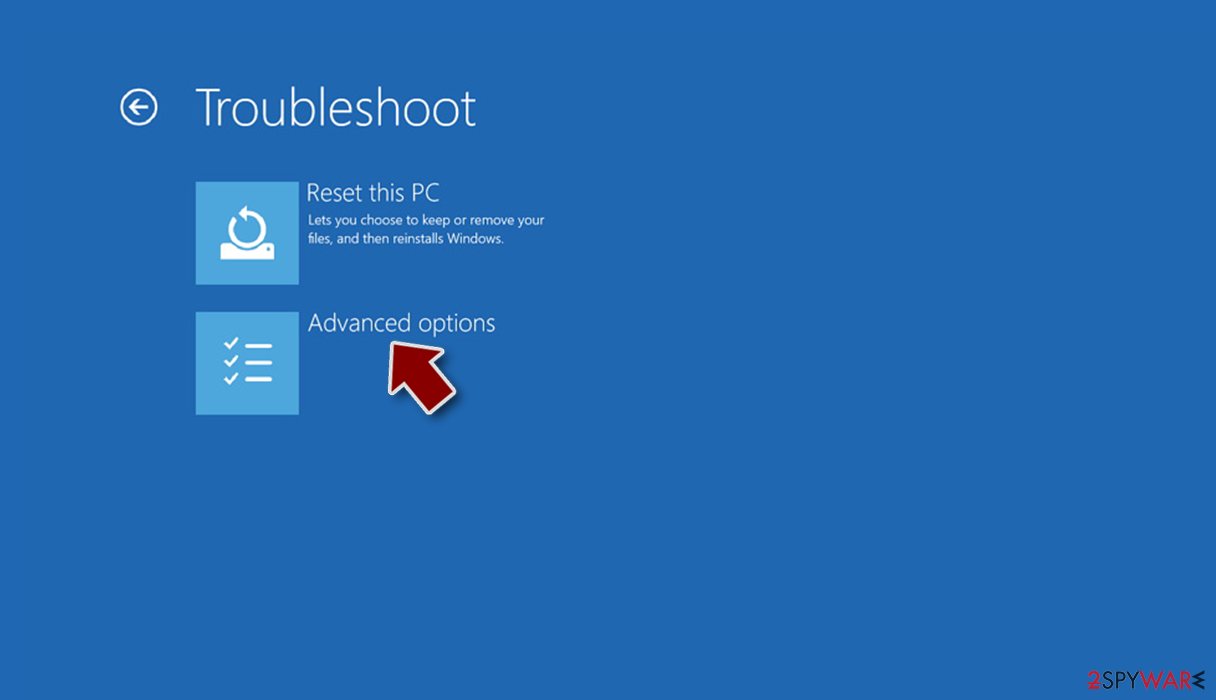
- Select Startup Settings.
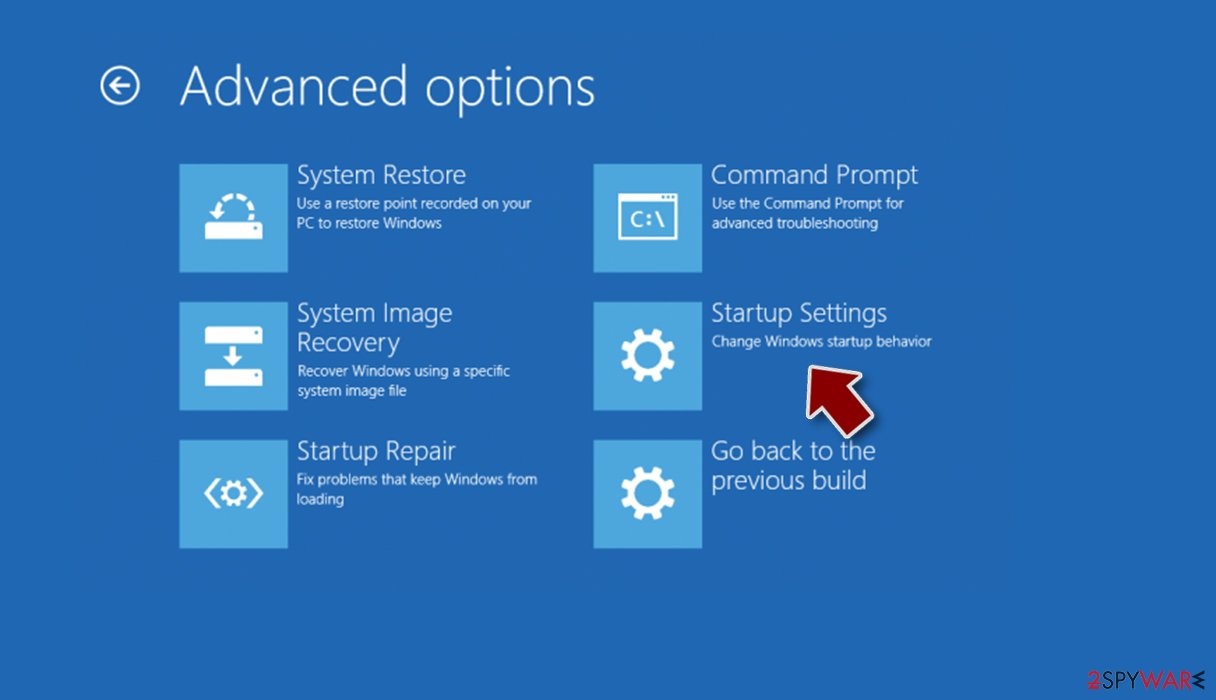
- Click Restart.
- Press 5 or click 5) Enable Safe Mode with Networking.
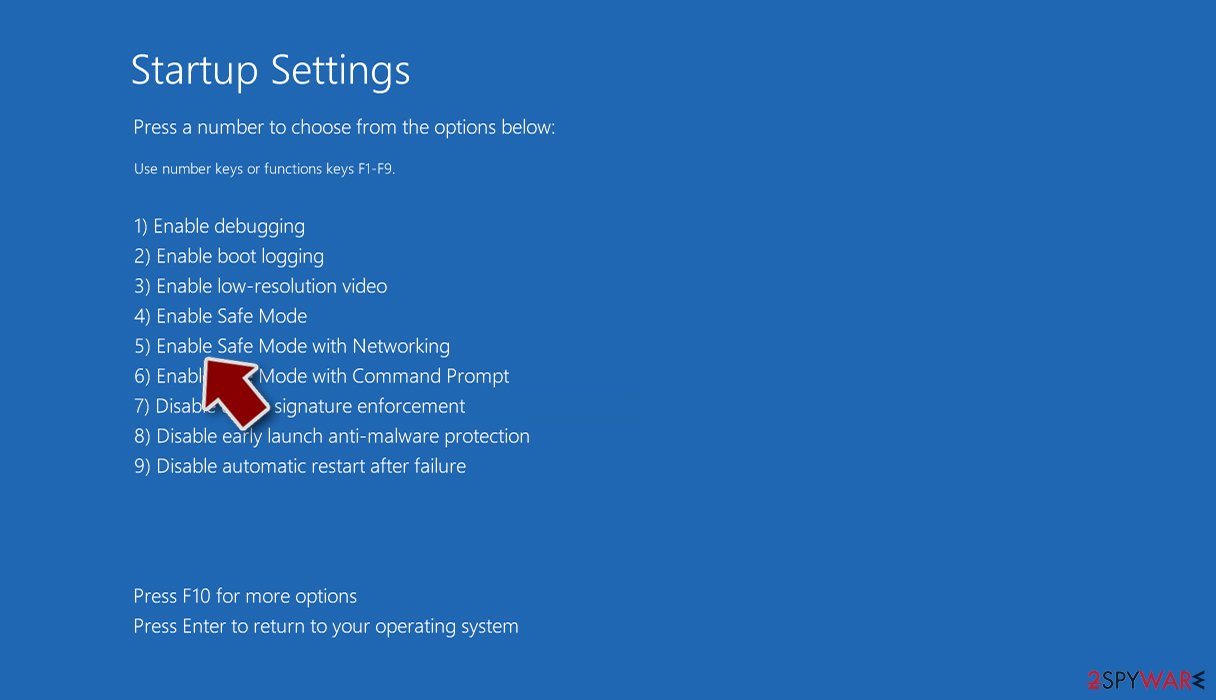
Once you reach Safe Mode, launch , , or another reputable antivirus, update it with the latest definitions, and perform a full system scan to eradicate malware and all its malicious components.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
From our report of Jul 2022 · not reviewed since
Luca Stealer malware removal
We strongly recommend performing automatic Luca Stealer removal, as complex malware samples are difficult to detect and remove manually, at least for regular computer users.
Instead, go ahead and download or security software and initiate a full system scan (don't forget to update the definition database, as malware is relatively new). If you still want to attempt manual elimination, follow the steps at the bottom of this post.
Once the infection is terminated, you have to remember that your personal data may be compromised. You should also monitor your online banking and expect to receive more malspam, as well as targeted phishing attacks.
Questions about Luca Stealer
Is Luca Stealer a virus?
Most programs that appear the way Luca Stealer did are not viruses in the strict sense. They are potentially unwanted programs:
- real software that arrives bundled with other downloads and then shows offers
- changes browser settings
- starts with Windows
Some are harmless, some are annoying and a few carry adware. What makes it worth removing is that you did not choose it.
Uninstall it from Installed apps and check the startup list and the browsers for anything added the same day. If it refuses to uninstall or returns after a restart, treat it as more serious and run a Microsoft Defender offline scan.
Luca Stealer will not uninstall. What can I do?
First restart the PC and try again, because the program may have been running and locked its own files. If the uninstaller is missing or fails, start Windows in Safe Mode, where most third-party programs do not start, and remove Luca Stealer from Installed apps there.
If it still refuses, delete its startup entry and its scheduled task, restart, and try once more. A program that actively prevents removal is behaving like malware, so finish with a Microsoft Defender offline scan. Avoid third-party uninstallers offered on search ads; several of them are unwanted programs themselves.
Is Luca Stealer a known stealer?
Not as a named family yet. The sign, luca Stealer in the list of installed apps, is typical of information stealers, keyloggers or clippers, but no analysis links Luca Stealer to a specific one. That is common:
- victims notice the effects
- such as lost accounts or swapped addresses
- before anyone sees the file
You do not need the family name to act. Change passwords from a clean device, sign out of all sessions, move crypto to a new wallet and run a Microsoft Defender offline scan on the PC. If a scan gives a detection name, note it for the report.
What happens to the stolen data?
Stolen data is packed into "logs", one per infected PC. The criminal who ran the stealer uses them directly or sells them in online markets, where others search them for bank, crypto, e-mail, gaming and business accounts.
This can happen days or months after the infection. That is why changing passwords and ending sessions matters even if nothing has happened yet. Breach notification services such as Have I Been Pwned can tell you when your e-mail address appears in known leaks.
Should I report Luca Stealer to the police?
Yes, if money was lost or accounts were misused. A police report gives you a reference number that banks, exchanges and insurers often ask for. Include when you first saw luca Stealer in the list of installed apps, the accounts and amounts involved, any wallet addresses or messages, and what you downloaded before it started.
In the US, use the FBI's IC3; in the UK, Report Fraud; in other countries, the national police cybercrime unit. Reporting rarely brings money back quickly, but it helps link cases and is often required for refunds.
The scan found nothing. Am I safe from Luca Stealer?
The PC may well be clean, but your data may not be. Many stealers run for a minute, send what they find and delete themselves, so a clean scan after luca Stealer in the list of installed apps is common. What matters now is the accounts:
- change passwords from another device
- sign out of all sessions
- turn on two-step verification
Move crypto to a new wallet. Watch for sign-in alerts and password-reset e-mails for a few weeks. If anything suspicious starts with Windows again, scan offline once more or reset the PC.
Should I reset my PC because of Luca Stealer?
Only if the signs point to deeper access. Reset when you see luca Stealer in the list of installed apps again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
Should I stop using this PC?
Only for sensitive things, and only until it is clean. Do not log in to banking, e-mail or crypto on it until the offline scan finds nothing. You can keep using it to follow the removal steps.
If the scans keep finding new items, or protection keeps switching off, back up your documents and reset Windows. After that the PC is as safe as a new one, but the accounts still need the steps in this guide, because a reset cannot undo data that was already sent.
Should I report a stealer infection?
Report it if money was taken, accounts were used for fraud, or your identity was misused. The report gives you a reference number for your bank and helps police link cases. Also tell the services involved:
- banks
- PayPal
- crypto exchanges and e-mail providers have their own fraud teams that can freeze transfers
- restore accounts
An infection with no misuse yet does not need a police report, but acting on your accounts does. Keep the antivirus log that shows Luca Stealer; it helps explain the case.
Will Fortect remove Luca Stealer?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Luca Stealer, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Cyble: Luca Stealer Source Code Leaked On A Cybercrime Forum (read October 6, 2026)
- Virus Total: Nixware by x777.exe (read October 6, 2026)
- Norton: What are bots? (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)