
OpenCandy ads: what it is and how to remove it
OpenCandy (PUA:Win32/CandyOpen) is adware created by SweetLabs that bundles unwanted software like hijackers and toolbars into popular freeware installers. It hijacks browsers and modifies system settings.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan checks installed programs, startup items and browser extensions for anything that came with OpenCandy ads.
Do it yourself · free Remove OpenCandy ads yourself 5 steps, about 15 minutes, no software needed.
Start the steps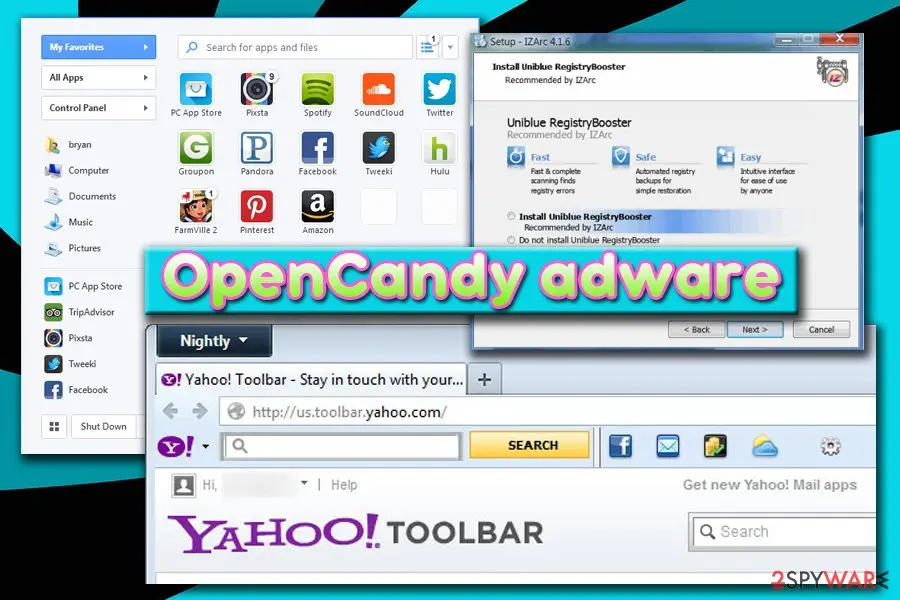
OpenCandy ads: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | OpenCandy ads |
| Type | Ad-supported program |
| Symptoms | An unknown program in Installed apps |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Evidence | 6 write-ups by security sites; details still limited |
|---|---|
| Program | OpenCandy ads |
| First seen | 7 October 2020 |
| Microsoft Defender name | PUA:Win32/CandyOpen |
| Facts checked | 5 October 2026 |
Is OpenCandy ads dangerous?
From our report of Oct 2020 · outdated details corrected in October 2026
OpenCandy is an application that injects computers with unwanted programs
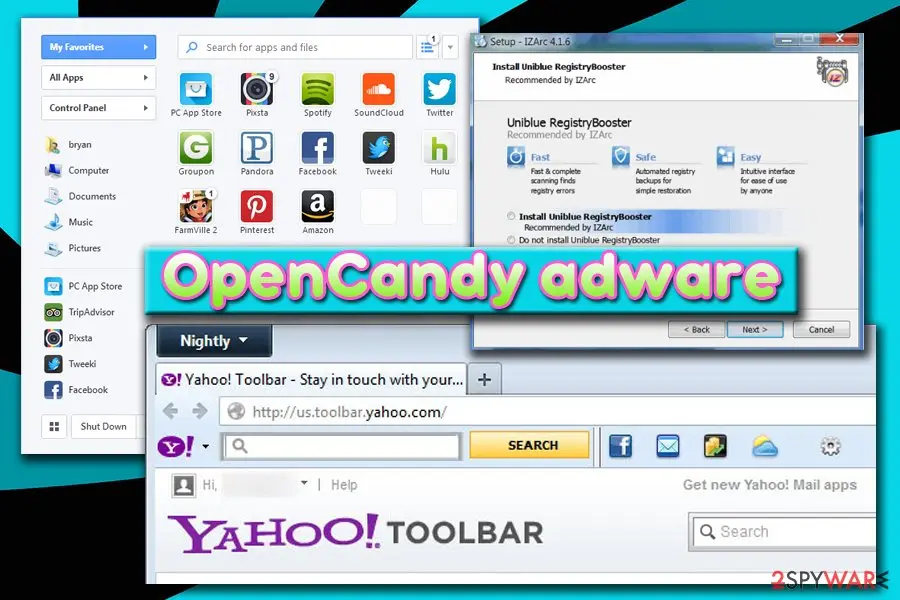
Adware OpenCandy is a dubious application created by SweetLabs which infiltrates machines with other unwanted software, including browser hijackers, browser add-ons or toolbars, other adware programs, system optimizers, questionable security software, etc. Adware comes bundled together with most popular Windows programs, such as uTorrent, Flvto YouTube Downloader, Freemake Video Converter, and many others.
The suspicious app also spies on users by gathering a certain type of information without their knowledge and sends it out to third-parties for marketing purposes.
Unlike many other adware apps that are easy to get rid of, OpenCandy acts more like a virus during the installation - it forcefully changes DNS settings, appends local proxy, modifies boot configuration data, stops Windows updates. injects processes into system, etc. With the help of these modifications, it is capable of hijacking Google Chrome, Mozilla Firefox, MS Edge, or another browser, redirect traffic, inject ads, and render a Windows computer vulnerable to cyber attacks.
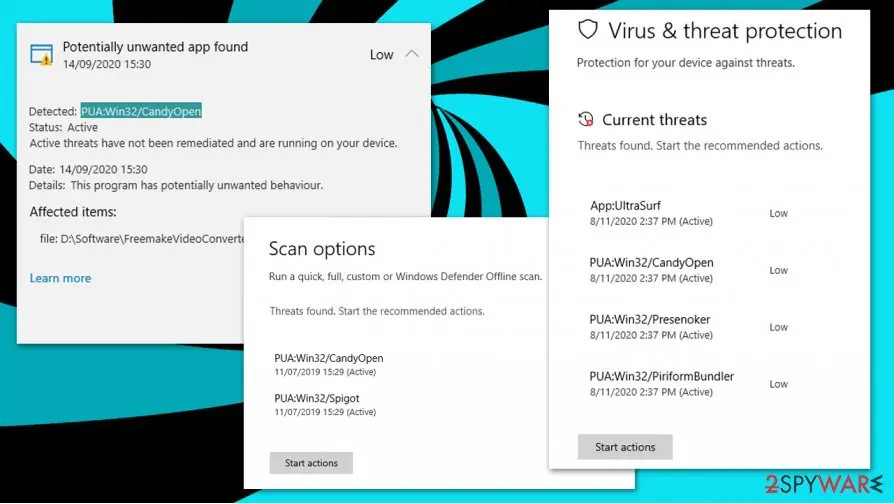
Due to its deceptive distribution, operation and persistence techniques, OpenCandy is detected by multiple security vendors under the following names:
- PUA:Win32/CandyOpen
- OpenCandy (PUA)
- PotentialRisk.PUA/OpenCandy.Gen
- A Variant Of Win32/OpenCandy.A Potentially Unsafe
- Adware.OpenCandy.137
- Win32:OpenCandy-D
- others
OpenCandy can change startup page by modifying Google Chrome, Microsoft Edge, Mozilla Firefox, Safari or other browser's settings, install additional components without permission (such as Pokki), which can ultimately lead to intrusive advertisement and rerouting practices.
It is not a secret that adware dramatically diminishes web surfing experience and is never welcomed on any PC. Nevertheless, the app enters machines legally, as users technically (although most likely unintentionally) accept the installation.
Open Candy is a Windows executable file which was first noticed in November 2010. The software module consists of a Microsoft Windows library, that can be hidden in any Windows installer.
The Task Manager usually shows the following processes running: spidentifier.exe and rundll32.exe, although other processes used by unintentionally installed programs may run as well. Users should remove OpenCandy virus to stop these processes, as well as prevent the infiltration of additional unwanted programs.
PUA:Win32/CandyOpen also modifies Windows registry to launch with every system boot for persistence reasons. As a result, users who want to uninstall the app from their systems might not be able to. Additionally, possibly the most dangerous trait of this adware is that it prevents Windows from automatically download system updates and disables User Account Control - both of these features are used for security and cyberattack prevention.
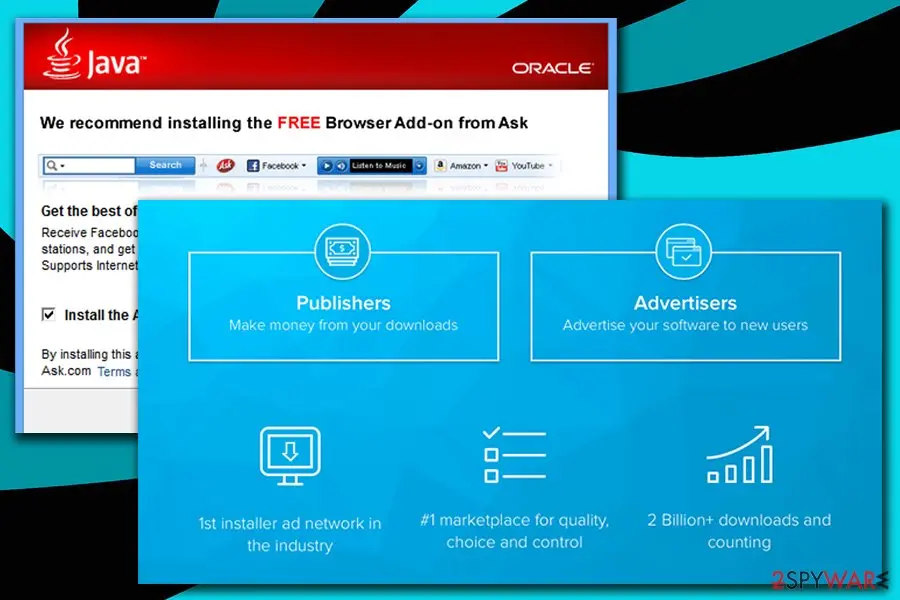
Some of the applications that distribute OpenCandy adware are well-known and reputable. One might ask why respected developers would include such dubious app in their installers? The answer is quite simple - revenue. Software development often costs a lot of money and authors simply want to gain extra cash by bundling unwanted programs.
It has been publicized minimally before, and developers do not like to speak about it. Nevertheless, it is slowly coming to light: we all know that Java popularized the notorious Ask toolbar, which is now considered malware by Microsoft.
Be careful when installing one of these applications, as they might include Open Candy bundled:
As we already mentioned, OpenCandy is adware program which seeks to gain monetary benefit by injecting additional programs into as many users' PCs as possible. Every install results in revenue, therefore, it is the biggest developers' interest. Ultimately, installed programs clutter and bloat the system, resulting in a frustrating experience for users. Thus, even though it might seem like some programs are "free" - they are not.
To further increase the benefit for themselves, Open Candy creators gather data about users' browsing activities and share it with third parties. This is widely practiced across many platforms; however, it is done without users' consent, which is highly controversial practice.
Adware programs do not bring any benefit and only flood the PC with unnecessary software. Thus, we suggest performing OpenCandy removal as soon as possible. The easiest way to terminate potentially unwanted apps along with the invisible malware is to scan the device with , , or other reputable security software.
- DivX
- FileZilla
- uTorrent
- PDFCreator
- mIRC, etc.
From our report of Oct 2020 · not reviewed since
Adware slips in into machines undetected due to software bundling
Seemingly, unwanted apps may show up entirely out of nowhere.
It is not true, however, and you did give your permission to install these applications (even without noticing it). Next, Next, Next, Next... done! That is what most people do during the installation of software.
Do we need to mention Term and Conditions? Nobody reads that. Right? Well, it is a bad practice, as these documents can provide vital information on what you agree to.
Unfortunately, not many of us do that, as we all want to be done with the installation as soon as possible. It is a wrong way to approach it, as this behavior can compromise your virtual safety and computer security. Thus, be attentive and do not rush.
Carefully look at each of the installation steps, and always pick Advanced settings when prompted. Then, eliminate all the pre-ticked components before the process is complete. Naturally, Recommended or Quick method should be avoided at all times - it might hinder the option to opt out of unwanted programs.
From our report of Oct 2020 · not reviewed since
More from our earlier report on OpenCandy ads
- Software bundling, deceptive ads, fake update prompts
- Changed homepage, extra apps installed without consent, advertisements, redirects, etc.
- You can delete potentially unwanted programs manually, although not all elements might be deleted this way - you should employ anti-malware and use it to delete PUPs automatically instead
- PUA:Win32/CandyOpen performs a variety of unwanted changes on the system - these might not be reverted/fixed by security software.
Check your browser and PC
Microsoft's name for OpenCandy ads is PUA:Win32/CandyOpen.
Defender sorts threats by category first, so the word before the colon tells you what kind of program was found, even if the family name means nothing to you.
Do not search for a removal tool by the detection name alone; fake "removal tools" use the same keywords. How the naming works is explained in our guide to antivirus detection names.
How to remove OpenCandy ads
Uninstall first, then remove what stays behind, so the ads do not come back after a restart.
Step 1: Uninstall OpenCandy ads
Open Settings > Apps > Installed apps in Windows 11, or Settings > Apps > Apps & features in Windows 10. Sort the list by install date and find OpenCandy ads, then choose Uninstall from the three-dot menu next to it (in Windows 10, click the entry and then Uninstall).
Remove anything else installed on the same day that you do not recognise, because such programs usually arrive together in one installer. If the uninstaller opens a browser page with an offer or a survey, close it: the program is removed either way.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 2: Remove it from startup
Whatever OpenCandy ads installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Reset the browser
Finish the browser part with a reset, which puts the search engine, start page, new tab page and site permissions back to their defaults and switches extensions off. Chrome: Settings > Reset settings > Restore settings to their original defaults.
Edge: Settings > Reset settings. Firefox: Help > More troubleshooting information > Refresh Firefox, which also removes its extensions. Your bookmarks and saved passwords are kept, and the menus are the same on Windows 11 and Windows 10.
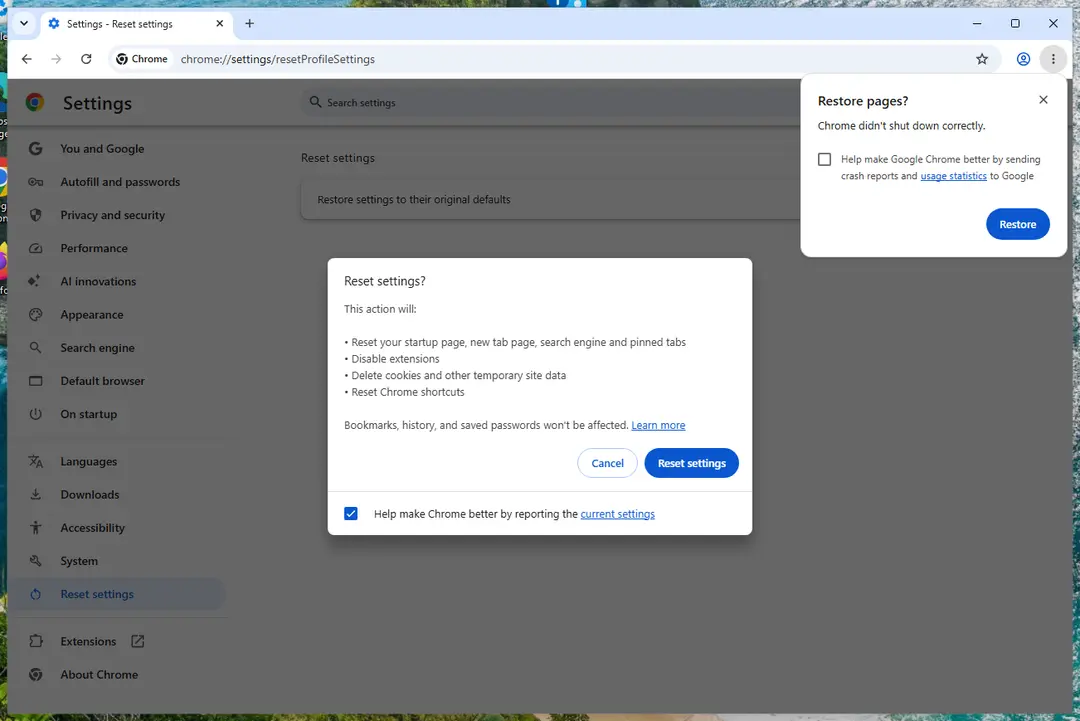
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
To delete OpenCandy adware from Windows OS, follow these steps:
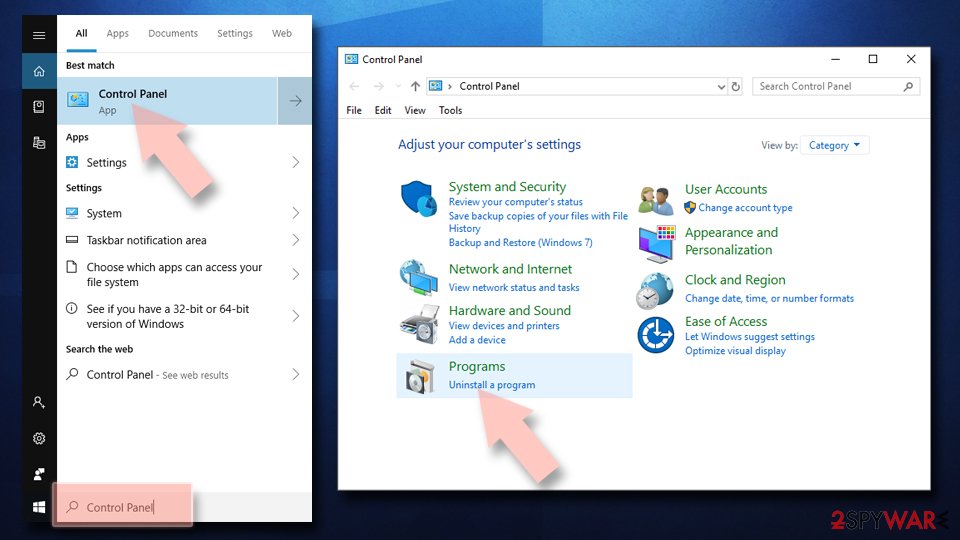
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
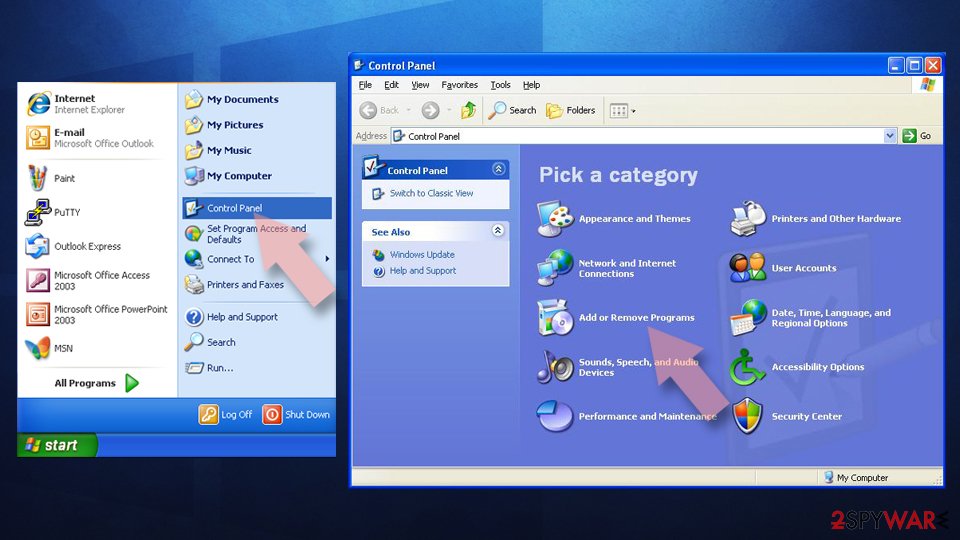
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
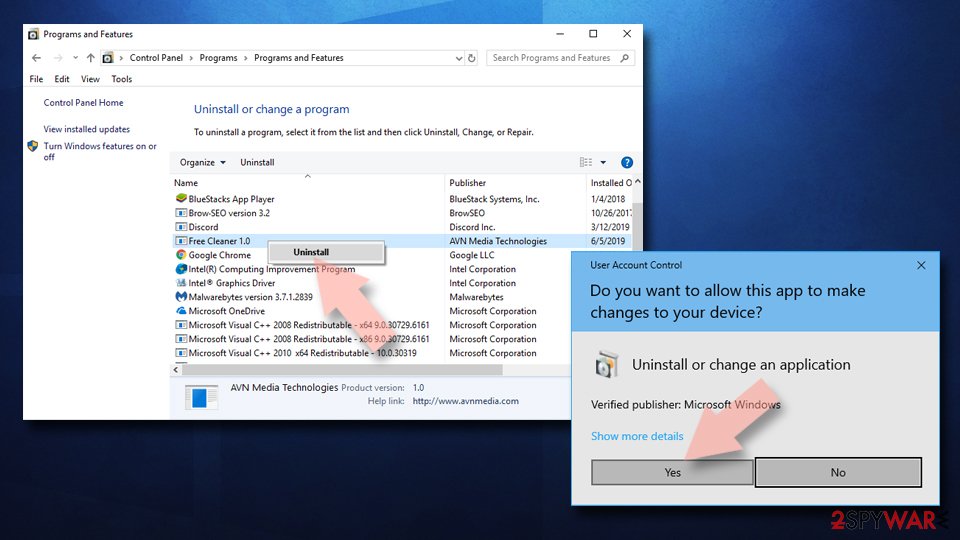
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
You have to manually reset Google Chrome after uninstallation of the PUP is complete:
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
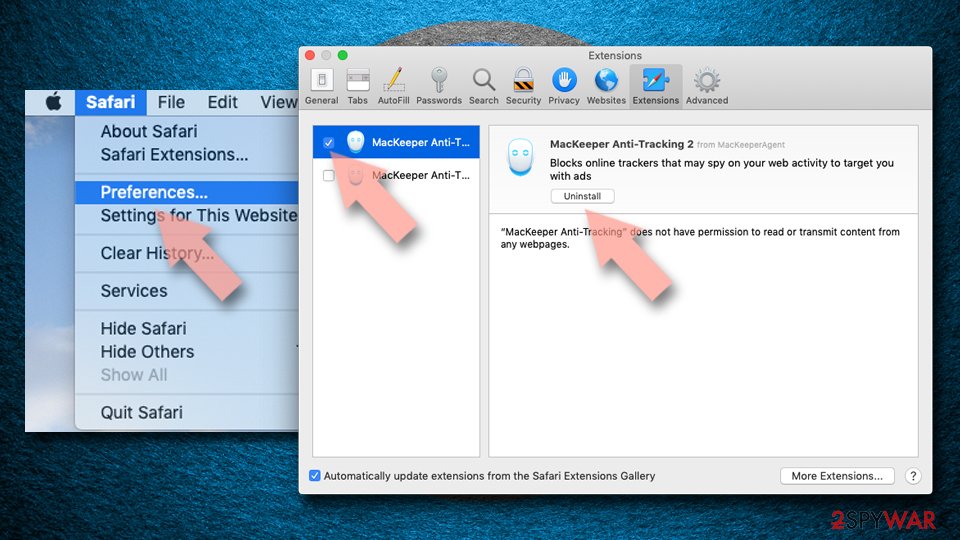
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
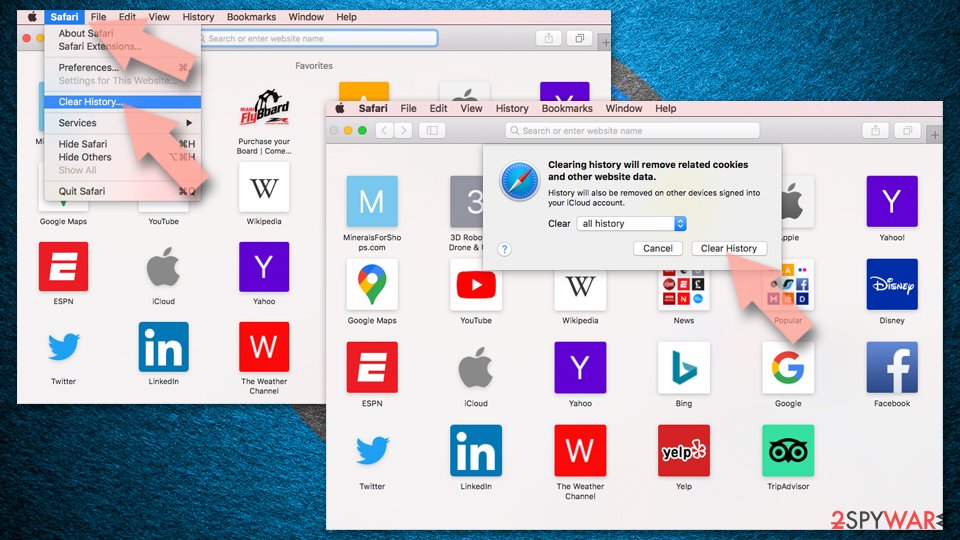
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
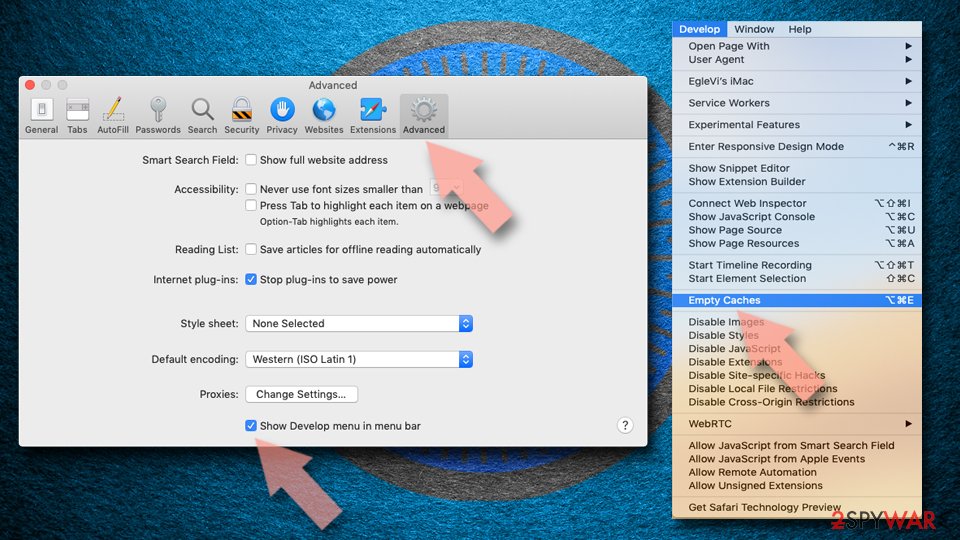
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
If you want to get rid of the PUP from Mac, follow these instructions:
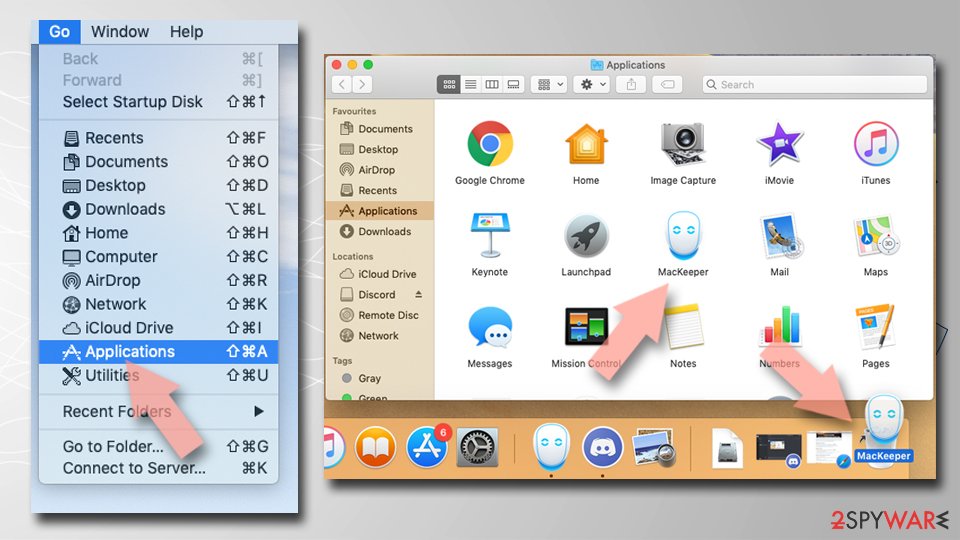
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
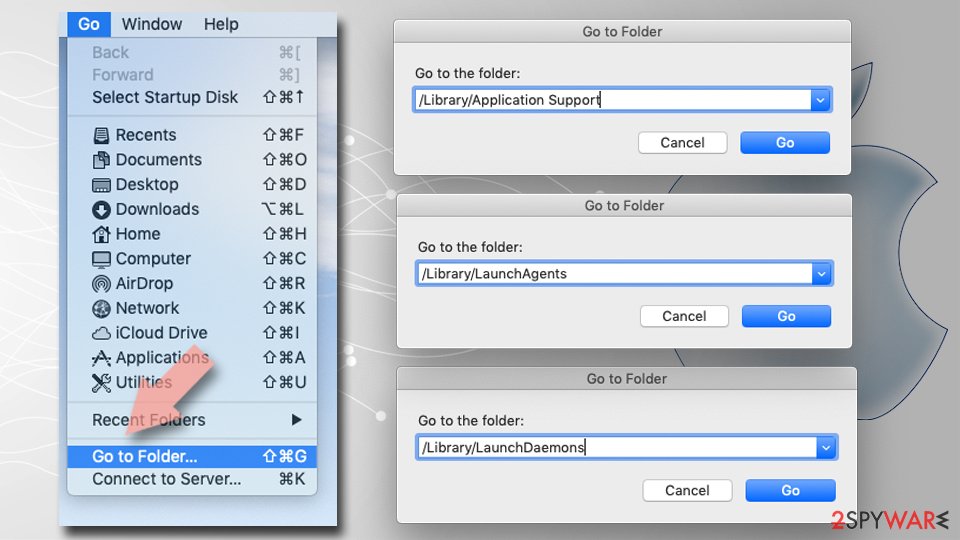
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
Remove dangerous add-ons:
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
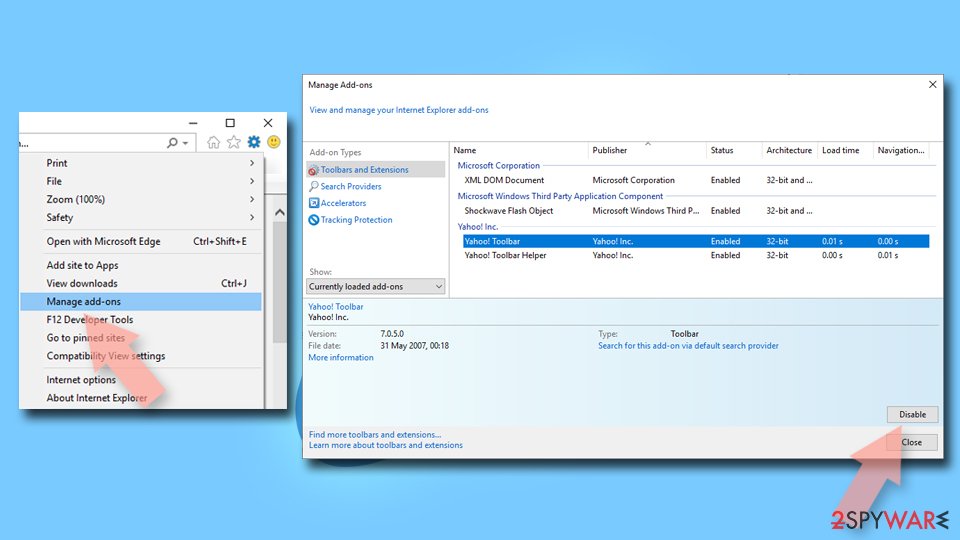
Change your homepage if it was altered:
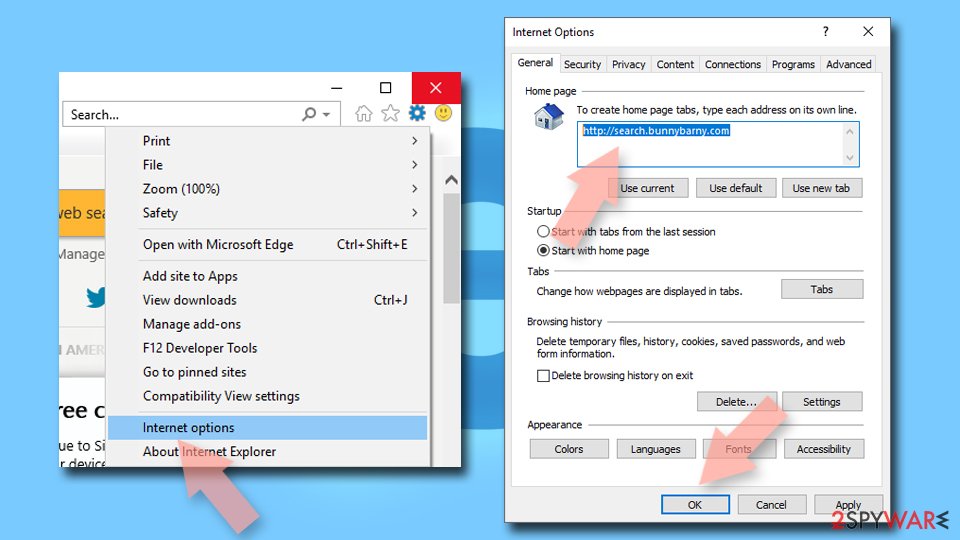
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
Delete temporary files:
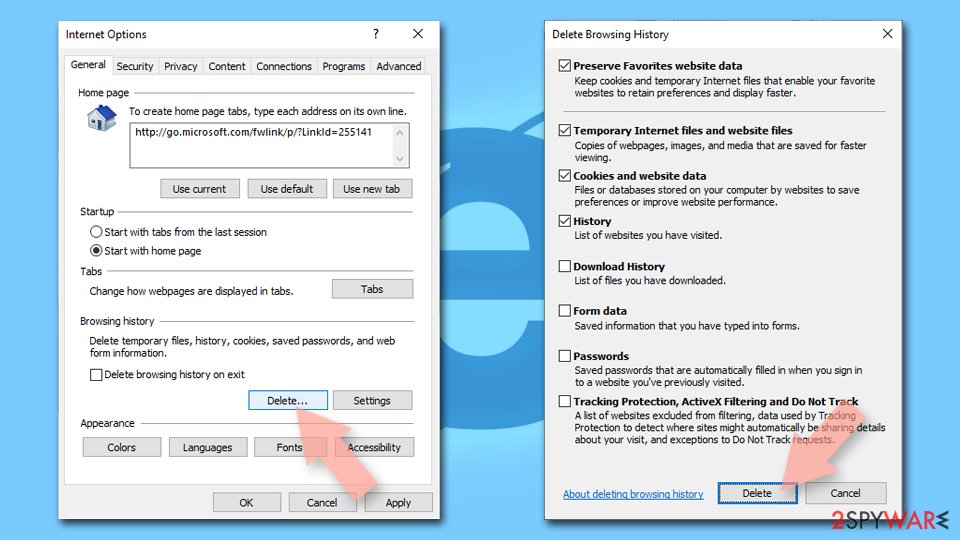
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
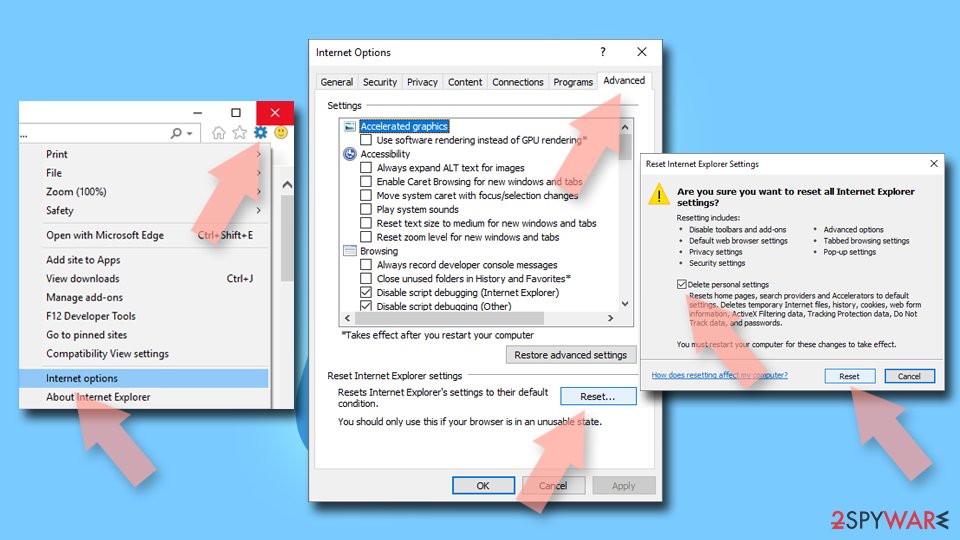
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
From our report of Oct 2020 · not reviewed since
Best strategies to remove OpenCandy virus from the infected computer
Technically, OpenCandy virus belongs to the category of potentially unwanted programs and is, mostly, harmless.
However, security experts note that it may also cause a bunch of various inconveniences during your browsing sessions, such as system slowdowns, suspicious redirects, the appearance of annoying advertisements and so on.
For that, you can either follow a guide provided below and get rid of this adware manually or install one of the anti-spyware programs to perform automatic elimination on your computer. In fact, we highly recommend you to select automatic OpenCandy removal option to make sure that every component related to this adware is gone.
Additionally, since PUA:Win32/CandyOpen also modifies the DNS settings, you should ensure that you reset them to default. Here's how to do that:
After the app is gone, ensure that you check for the latest Windows updates via the settings panel and install them as required.
- Right-click on Start and select Settings
- Go to Network & Internet and select Ethernet on the left
- On the right, pick Change adapter options
- Right-click on your connection and select Properties
- Select Internet Protocol Version 4 (TCP/IPv4) and pick Properties
- Check Obtain DNS server automatically and click OK.
Questions about OpenCandy ads
What is OpenCandy?
OpenCandy is adware created by SweetLabs that forces unwanted software onto PCs through deceptive bundling. It comes bundled with legitimate programs like uTorrent, Flvto YouTube Downloader, and Freemake Video Converter.
Upon installation, it changes DNS settings, appends local proxy, modifies boot configuration data, stops Windows updates, and injects processes into system memory. It hijacks Google Chrome, Mozilla Firefox, Microsoft Edge, and other browsers to redirect traffic, inject ads, and render computers vulnerable to attacks.
How does OpenCandy get on my computer?
OpenCandy spreads via software bundling and deceptive ads on websites. When you download popular free programs, the installer includes OpenCandy as an optional component—usually pre-checked by default.
During Quick installation, users unknowingly accept the bundle. Fake update prompts also trick users into downloading it. The application enters machines legally because users technically accept installation in Terms and Conditions that most never read.
What damage does OpenCandy cause?
OpenCandy modifies your browser homepage and search engine without permission. It disables Windows automatic updates and User Account Control—both critical security features. It prevents Windows from downloading security patches, leaving your system exposed to attacks.
The adware injects numerous advertisements, redirects to affiliate sites, and may monitor your browsing habits to generate targeted ads. Multiple copies may install simultaneously, greatly slowing your computer.
Is OpenCandy a virus?
No, OpenCandy is classified as a potentially unwanted program (PUP) and adware, not a virus. However, it behaves maliciously by hijacking browsers, modifying system settings without consent, and disabling security features. Multiple security vendors detect it: PUA:Win32/CandyOpen, PotentialRisk.PUA/OpenCandy.Gen, Adware.OpenCandy.137, and Win32:OpenCandy-D. Despite not being a true virus, it poses serious security and privacy risks.
What programs are known to bundle OpenCandy?
Popular programs that bundled OpenCandy include uTorrent, Flvto YouTube Downloader, Freemake Video Converter, and many others from developers seeking extra revenue. Java famously bundled the Ask toolbar, now considered malware by Microsoft.
These developers argue they provide free software and need monetization. However, bundling without explicit user consent is deceptive. Always check Advanced settings during installation to opt out of extra software.
How do I remove OpenCandy from my PC?
Uninstall the program through Control Panel's Programs and Features list. You may need to stop the spidentifier.exe and rundll32.exe processes in Task Manager first. After uninstall, check browser extensions and remove any unfamiliar add-ons.
Reset your browser homepage and search engine to default settings. Ensure DNS settings are configured to obtain servers automatically. Run a full antivirus scan to detect and remove any remaining components or bundled malware.
Why does OpenCandy disable Windows security features?
OpenCandy disables Windows automatic updates and User Account Control to increase its persistence and prevent security software from removing it. Disabled Windows updates leave systems vulnerable to known exploits. Disabled UAC reduces system protection.
These modifications allow the adware to remain active and generate revenue through ad clicks without user interference. The modifications are difficult to undo even after uninstall, requiring manual registry changes and system repair.
How can I prevent OpenCandy and similar bundled adware?
Download software only from official websites and trusted developers. Always choose Advanced or Custom installation settings instead of Recommended or Quick options.
Carefully review each step and uncheck all pre-selected boxes for additional software. Read the Terms and Conditions before clicking Agree.
Avoid torrent sites and third-party download platforms. Keep Windows and all software updated. Use reputable antivirus software and enable automatic scanning.
Will Fortect remove OpenCandy ads?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For OpenCandy ads, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: Browser hijacking (read October 5, 2026)
- The Conversation: What are software vulnerabilities, and why are there so many of them? (read October 5, 2026)
- Virus Total: 365dbd92671dfe1627e603571ef85fe835773a9966d0b9c37cd02d418317b27d (read October 5, 2026)
- LesVirus: LesVirus (read October 5, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 5, 2026)