
Carbanak Leader Arrested in Spain: 2026 Update
- Carbanak leader arrest in 2026: the short answer
- Timeline: from the Alicante arrest to the US sentences
- What changed since 2018
- Risks and scams around the Carbanak story (our analysis)
- What a reader should do in 2026
- What is still unknown
- Our original 2018 report
- Hackers used three different malware infections which were developed by themselves
- Cybercriminals had multiple options to cash out the stolen money
- Related guides on 2-Spyware
Carbanak leader arrest in 2026: the short answer
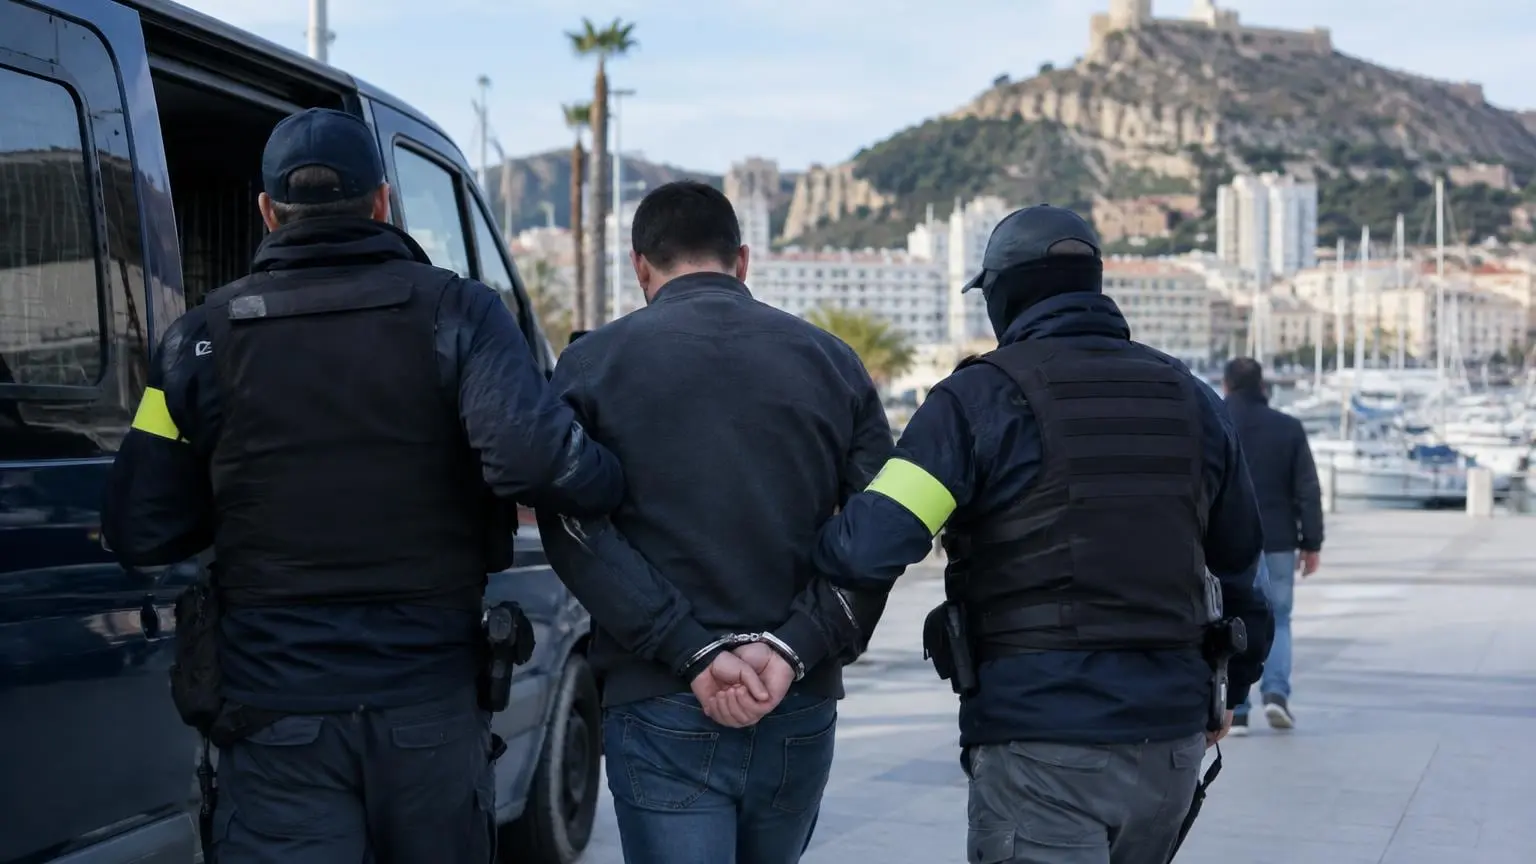
The man Europol called the leader of the Carbanak and Cobalt gangs was arrested in Alicante, Spain, and the arrest was announced on March 26, 2018.[7] We found no public record of his trial or sentence as of 2026. Europol did not name him in the release we read, and we will not guess a name.
The wider story did end in court. Several members of the related FIN7 group, which US prosecutors also call the Carbanak Group, were arrested in Germany, Poland and Spain and later sentenced in the United States.[6][8] Attacks by the surviving crews did not stop right after the Alicante arrest.[7]
| Question | Answer |
|---|---|
| Who was arrested in Alicante | The suspected gang leader; Europol gave no public name in the release we read[7] |
| When it was announced | March 26, 2018[7] |
| Did attacks stop | No. Group-IB tracked new Cobalt phishing waves in March and May 2018[7] |
| Jailed FIN7 members | Fedir Hladyr, 10 years in April 2021[8]; Andrii Kolpakov, 7 years in June 2021[6] |
| Alicante suspect's trial result | We found no public ruling as of 2026 |
| Names used for the crews | Anunak, Carbanak, Cobalt, FIN7, Navigator Group[8][9] |
Timeline: from the Alicante arrest to the US sentences
| Date | Event |
|---|---|
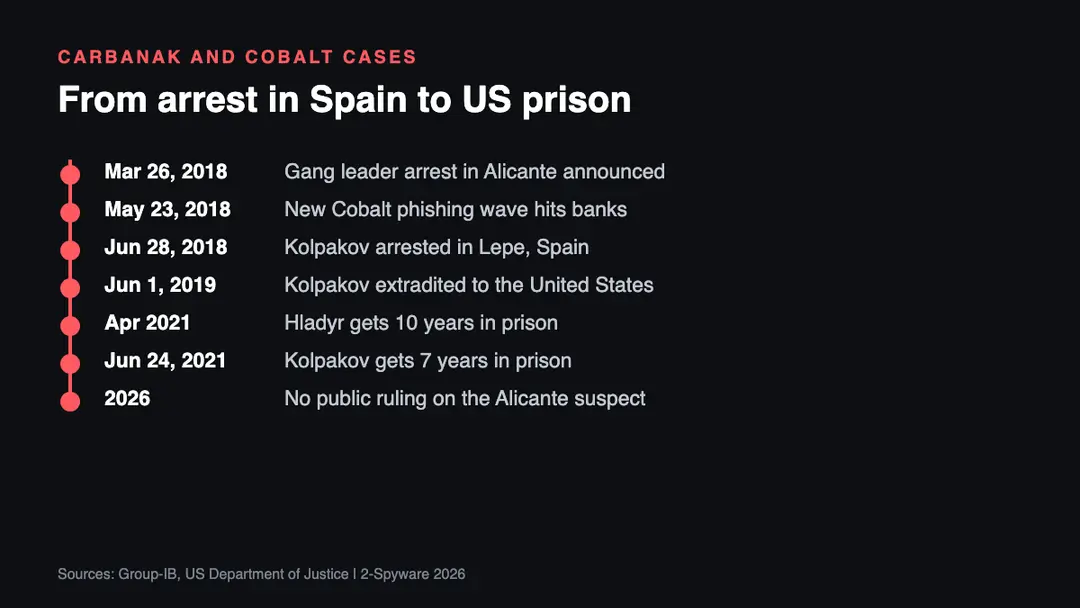
| March 26, 2018 | Europol announces the arrest of the Cobalt gang leader in Alicante[7] |
| May 23, 2018 | Group-IB tracks a large Cobalt phishing attack on banks in Russia and the CIS[7] |
| June 28, 2018 | Andrii Kolpakov, a FIN7 member, is arrested in Lepe, Spain[6] |
| June 1, 2019 | Kolpakov is extradited to the United States[6] |
| April 2021 | Fedir Hladyr, arrested in Dresden, Germany, is sentenced to 10 years[8] |
| June 24, 2021 | Kolpakov is sentenced to seven years and ordered to pay $2,500,000 in restitution[6] |
What changed since 2018
In 2018 the story looked finished: the boss was in custody. Group-IB, a security firm that tracked the gang, said otherwise. It reported that the leader and the malware writer were arrested, yet Cobalt kept attacking, and it expected the remaining members to join other groups or form a new one.[7]
The court record then moved to a different set of names. US prosecutors describe FIN7, also known as the Carbanak Group, as a crew that stole card data from businesses.[9] Hladyr was its systems administrator and Kolpakov was a high-level hacker the group called a pen tester.[6][8] Both pleaded guilty and were jailed.[6][8]
The scale numbers also grew. A case page from the US attorney in Seattle counted over 15 million stolen card records from more than 3,600 business locations.[9] By the 2021 sentencing, the Justice Department said more than 20 million card records and over $1 billion in estimated damage.[6] The old report above uses the bank-theft figure of one billion dollars, which comes from a different type of loss.
One naming point matters when you read other sources. Group-IB treats Cobalt and Anunak (Carbanak) as separate groups that worked together.[7] Other writers and US prosecutors use Carbanak, Cobalt and FIN7 as overlapping names.[8][9] That is why you will see different people called the leader.
Risks and scams around the Carbanak story (our analysis)
- Spear phishing with a document or link. The gang's method was an email that looked like it came from a known company, such as an antivirus vendor, IBM or the European Central Bank.[7] The same trick still works on staff in any company.
- Fake sentencing or leak emails. News about arrests is used as bait. An email that claims to hold a Carbanak leak file or a victim list is a lure. Do not open it.
- Cobalt Strike confusion. Cobalt Strike is a real penetration testing tool that the gang abused.[8] Seeing the name in a report does not mean a company runs criminal software, but unknown copies on your network need a check.
- USB lures. The FBI warned in March 2020 about FIN7 packages with USB devices that act as a keyboard when plugged in.[8] Never plug in a device that arrived unasked.
What a reader should do in 2026
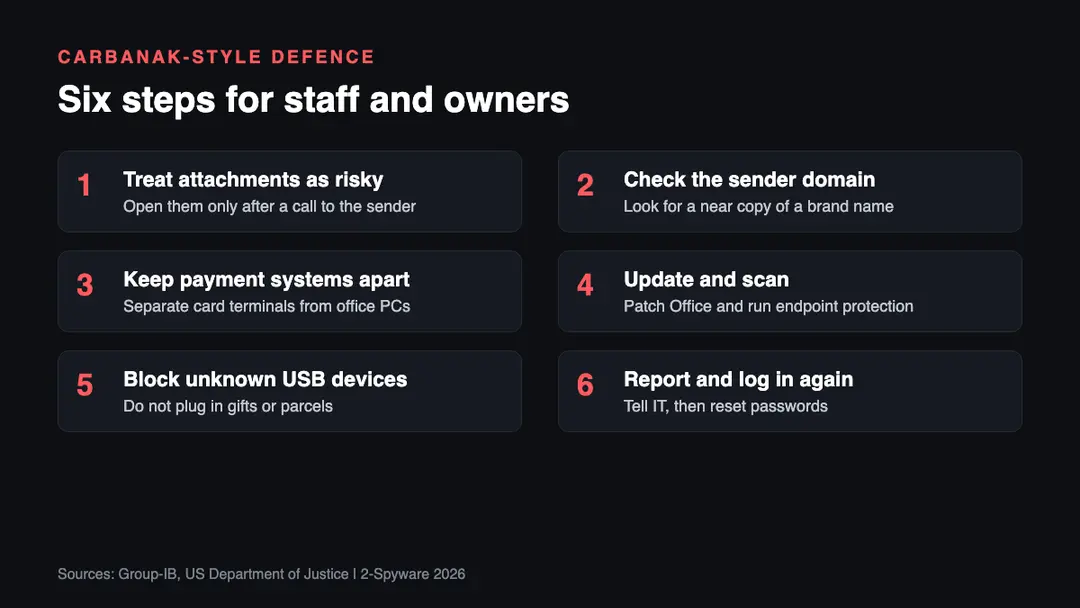
1. Treat attachments as risky. The gang's entry point was an email with a file that looked routine.[7] Confirm unexpected files with the sender by phone, using a number you already had.
2. Check the sender domain. Group-IB found fake domains that copied well-known names.[7] Read the address letter by letter before you click.
3. Keep payment systems apart. FIN7 went after point-of-sale terminals in restaurants and shops.[9] Card terminals should not share a network with general office computers.
4. Update and scan. Group-IB noted that the gang used public exploit code within hours of its release.[7] Install Office and Windows updates promptly and run endpoint protection.
5. Block unknown USB devices. The 2020 FBI warning about FIN7 USB parcels shows that physical lures were used.[8] Do not plug in any device you did not order.
6. Report and log in again. If someone opened a suspect file, tell your IT contact at once and change passwords from a clean device. Our guide on how to report phishing shows where to send the message.
What is still unknown
- The trial result or sentence of the man arrested in Alicante. We found no public court record for him as of 2026.
- Whether the Alicante suspect is the same person as any FIN7 member jailed in the United States. The sources we read do not link them.[6][7]
- How many of the Cobalt and Carbanak crews are still active. Group-IB expected survivors to regroup.[7]
- The true total of losses, since the one-billion figure is an estimate and different sources count different things.[6][9]
Our original 2018 report
The text below is our report as first published in 2018. We keep it unchanged for the record; the sections above bring it up to date.
Law enforcement has announced that the supposed leader of one of the most famous hacking groups known as Carbanak and Cobalt has been arrested in Alicante, Spain. The malware attacks conducted by these cyber gangs generated more than one billion dollar profit for the crooks[1].
Europol has reported that the arrest was a result of a complex investigation which has been supported by private cybersecurity firms, Spanish National Police, FBI, Taiwanese, Romanian, Belarussian, and Moldovan authorities. The attackers have targeted over 100 financial institutions across 40 different countries[2].
In the official press release, Europol authorities provide the following information[3]:
Since 2013, the cybercrime gang has attempted to attack banks, e-payment systems and financial institutions using pieces of malware they designed, known as Carbanak and Cobalt. <…> The magnitude of the losses is significant: the Cobalt malware alone allowed criminals to steal up to EUR 10 million per heist.
Hackers used three different malware infections which were developed by themselves
The infamous cyber gang has been first spotted by the law enforcement in late 2013 when they had started targeting ATMs and financial institutions with Anunak malware. In 2014, the attackers upgraded the Anunak to a new and more sophisticated variant, called Carbanak malware.
While the previous virus has been used until 2016, hackers created an even more advanced cyber infection version of a popular Cobalt Strike software which is used for penetration testing. Law enforcement has analyzed the attacks and found undeniable similarities[4]:
In all these attacks, a similar modus operandi was used. The criminals would send out to bank employees spear phishing emails with a malicious attachment impersonating legitimate companies.
Unfortunately, as soon as the person downloads the infected attachment, his/her computer becomes accessible by the hacker group remotely. They then are able to collect information from the banking network and take over the servers which are controlling ATMs.
Cybercriminals had multiple options to cash out the stolen money
IT experts report that Cobalt and Carbanak members were able to get the illegally gained money three ways. One of them is to take the cash spit by the ATM at the pre-set time by programming the machine to give the money automatically. Likewise, someone from the group had to go and collect the stolen money from the hijacked ATMs.
Another technique the criminals had employed was to take advantage of the remote access to the banking network. In other terms, they have automatically transferred the money from the e-payment servers of the financial institutions to their accounts.
And finally, Europol indicates the last cash out technique used by the attackers[5]:
Databases with account information were modified so bank accounts balance would be inflated, with money mules then being used to collect the money.
Related guides on 2-Spyware
Frequently asked questions
Who was the Carbanak leader arrested in Spain?
Europol said the leader of the Carbanak and Cobalt gang was arrested in Alicante, Spain, announced on March 26, 2018.{7} The release we read gave no public name, so we do not name him. Separate US cases involve FIN7 members such as Fedir Hladyr and Andrii Kolpakov, who are not shown to be the same man.{6}{8}
Was the Carbanak mastermind convicted?
We found no public conviction for the man arrested in Alicante as of 2026. Other members tied to the Carbanak Group name were convicted in the United States: Hladyr received 10 years in April 2021 and Kolpakov seven years in June 2021.{6}{8} Treat any claim about the Alicante suspect's sentence as unconfirmed.
How much did the Carbanak heist steal?
Europol linked the gangs to about one billion euros stolen from over 100 banks in 40 countries.{7} US prosecutors separately said FIN7 stole more than 20 million card records and that estimated damage to banks, merchants and consumers exceeded $1 billion.{6} These are estimates, and the two figures measure different losses.
Is the Carbanak gang still active in 2026?
We found no 2026 source that confirms current activity under the Carbanak name. Group-IB warned in 2018 that surviving Cobalt members would likely join other groups or form a new one.{7} The tools and methods, such as spear phishing and Cobalt Strike, remain in wide criminal use, so the risk did not end with the arrests.
Are Carbanak and Cobalt the same hackers?
Not exactly. Group-IB describes Cobalt and Anunak (Carbanak) as separate groups that ran joint operations.{7} US prosecutors and some press use Carbanak, Cobalt and FIN7 as overlapping names for related crews.{8}{9} Because the naming differs by source, read who is being described before you compare cases.
What was Carbanak malware used for?
It was used to break into banks and later into shops and restaurants. The attackers sent spear phishing emails with a malicious file, then took control of internal systems, ATMs and payment servers.{7} In the US cases the same crew stole card numbers from point-of-sale terminals at thousands of business locations.{9}
Sources
- IT News. Top Technology Stories
- ZDNet. Technology News, Analysis, Comments and Product Reviews
- The Hacker News. Online Cyber Security News & Analysis
- Computing. The UK's leading source for the analysis of business
- Europol. European Cybercrime Centre
- US Department of Justice
- Group-IB
- Cyber Defense Magazine
- US Attorney's Office, Western District of Washington
Log in to comment
ugh, if the boss got arrested in 2018, why did the phishing still keep going after that? does that mean the same people were still on the laptops, or did it just spread to others?
Good question, Megan. The arrest of one leader doesn’t usually stop a whole phishing operation right away. Most of these crews are split up: some people handle phishing emails, others manage stolen logins, and others run the malware or sell access. So even if the top person is arrested, the same campaign can keep going if the lower-level operators are still active, or if the tools and stolen data get passed to new people. That’s why two-step verification is so important, because it can block a lot of these follow-up logins even after a password gets stolen.
One practical point readers often miss here: after a phishing email like this, check the browser you use for your bank, not just the inbox. In Chrome, Edge, or Firefox on Windows, open Settings and look at Extensions, then remove anything you do not recognize. Attackers often rely on a fake attachment or link, but a bad extension can keep showing login pages or stealing what you type even after the email is gone. I also like turning on two-step verification for banking and email accounts.
Good point, and I’d add one caution: a bad extension is worth checking, but it is not the only place a phish can leave trouble behind. 1. Remove anything you do not recognize from the browser extensions page. 2. If you clicked or downloaded something, run a Microsoft Defender Offline scan too. 3. Change the bank password from a clean device, then turn on 2FA. If the browser still acts odd afterward, reset it rather than poking at random settings. That usually saves time, which is rare and therefore suspicious. If you want the cleanup steps, see /how-to/remove-browser-extension and /how-to/defender-offline-scan.
One practical point readers often miss here: if a phishing email claims to be from a bank or payment service, don’t just delete it — check whether the message is trying to push you to enable macro content or open a file in Windows. In Chrome, Edge or Firefox on Windows, the safest move is to close the tab, then report the email as phishing in your mail app and change the password from a different tab or device if you already clicked anything. Two-step verification is worth having on that account too.
Yes, that’s the bit people miss most often. On Windows, the red flag is usually the attachment or the link pushing you to enable macros, open a file, or run something from File Explorer. If you only opened the email, that’s usually enough to delete it and report it as phishing. If you clicked or entered a password, change it straight away and turn on 2FA. Our /how-to/report-phishing guide covers the reporting part neatly.