
Microsoft OneNote Malware in 2026: Is OneNote Safe Now?
- Microsoft OneNote malware in 2026: the short answer
- Timeline: from OneNote malspam to Microsoft's block
- What changed since 2023
- OneNote phishing risks that remain (our analysis)
- How to handle OneNote files safely
- What is still unknown
- Our original 2023 report
- OneNote allows users to insert attachments which was exploited by hackers
- Follow security measures
- Related guides on 2-Spyware
Microsoft OneNote malware in 2026: the short answer
Microsoft OneNote itself is safe to use, and the big wave of OneNote malware from late 2022 and early 2023 lost its main trick. Since Version 2304, rolled out from April and May 2023, OneNote for Microsoft 365 on Windows blocks users from opening embedded files with dangerous extensions. Before, a warning appeared, but a click on OK still ran the file.[4]
The block covers 120 extensions, including .vbs, .js, .hta, .bat, .exe, .lnk and .iso, the same list that Outlook, Word, Excel and PowerPoint already block.[4][6] It does not apply to OneNote on the web, OneNote for Windows 10, Mac, Android or iOS.[6] A OneNote file can still carry a link to a phishing page, so a .one attachment from a stranger still deserves suspicion.
| Question | Answer |
|---|---|
| When the wave started | Six campaigns in December 2022, over 50 in January 2023[5] |
| What it delivered | AsyncRAT, Redline, AgentTesla, Qbot, Quasar RAT, XWorm, Netwire and DOUBLEBACK[5] |
| Typical lures | Invoices, remittances, shipping notices, Christmas bonuses, machine parts[5] |
| Microsoft's fix | Blocking embedded files with 120 dangerous extensions, from Version 2304[4][6] |
| Where the fix applies | OneNote for Microsoft 365 on Windows only[6] |
| Is OneNote safe in 2026 | Yes for normal use; still be careful with .one files from strangers |
Timeline: from OneNote malspam to Microsoft's block
| Date | Event |
|---|---|
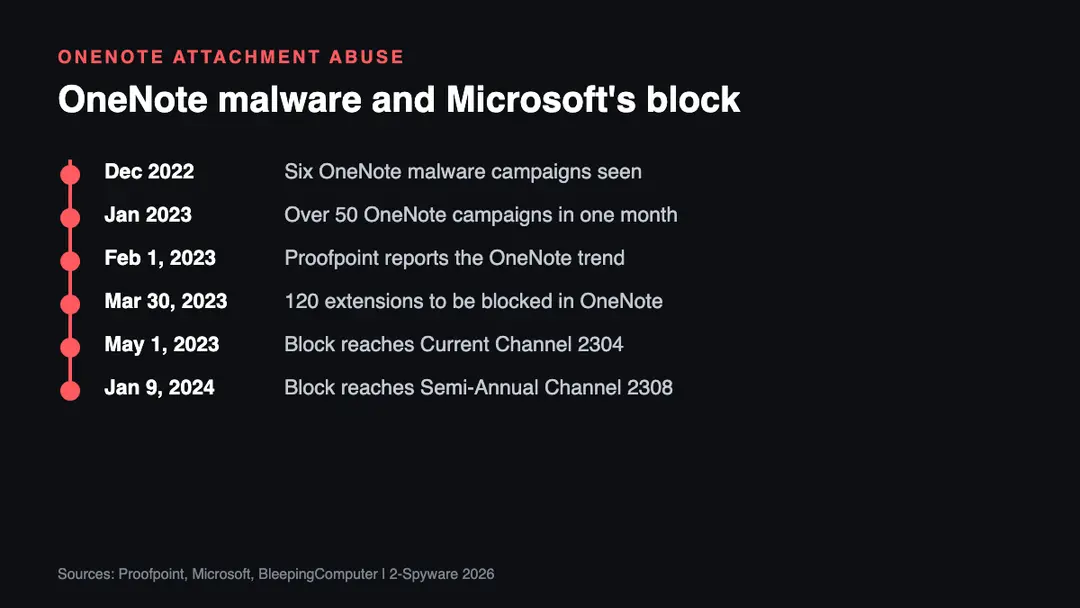
| December 2022 | Proofpoint sees six campaigns using OneNote attachments[5] |
| January 2023 | More than 50 OneNote campaigns in one month[5] |
| February 1, 2023 | Proofpoint publishes its report on the trend[5] |
| March 30, 2023 | BleepingComputer reports OneNote will block 120 dangerous extensions[6] |
| May 1, 2023 | The block reaches Current Channel Version 2304[4] |
| June 13, 2023 | The block reaches Monthly Enterprise Channel[4] |
| January 9, 2024 | The block reaches Semi-Annual Enterprise Channel Version 2308[6] |
What changed since 2023
Our original report below describes the trick: a fake "Double click to view file" bar hid a row of VBS attachments, and one double click plus one OK ran a script that installed a remote access trojan. Microsoft removed the OK button from that path. With the change, OneNote blocks the file and shows a dialog instead of a warning that users could click through.[4]
Proofpoint counted how fast the trick spread. It saw six OneNote campaigns in December 2022 and over 50 in January 2023, from both small and well-known groups. TA577 used OneNote to deliver Qbot, and TA579, which earlier used DOUBLEBACK, joined in too.[5] BleepingComputer also named Emotet, IcedID and Chromeloader among the malware pushed through OneNote files.[6]
Admins have more control too. In Microsoft 365 Apps for enterprise, they can block more extensions or allow ones blocked by default through policy. Microsoft says the separate OneNote policy called "Embedded Files Blocked Extensions" should not be used for this.[4] This option is not available in Microsoft 365 Apps for Business.[4]
OneNote phishing risks that remain (our analysis)
The attachment block closed one door. Our analysis of what still works against OneNote users:
- Links inside OneNote pages. A notebook can show a fake "View document" button that opens a phishing site asking for your Microsoft 365 password. The block does not stop links.
- Shared notebooks from hacked accounts. A file shared from a real business account looks trusted. If you did not expect it, confirm with the sender by phone.
- Older or unmanaged OneNote versions. The block applies to OneNote for Microsoft 365 on Windows.[6] Out-of-date installs may still show only a warning.
- Allowed extensions. If an admin allows a blocked type through policy, that file type can run again.[4]
- Same lures, new file types. Invoices, shipping notices and bonus messages were the main bait in 2023.[5] The same themes now come with other attachments.
How to handle OneNote files safely
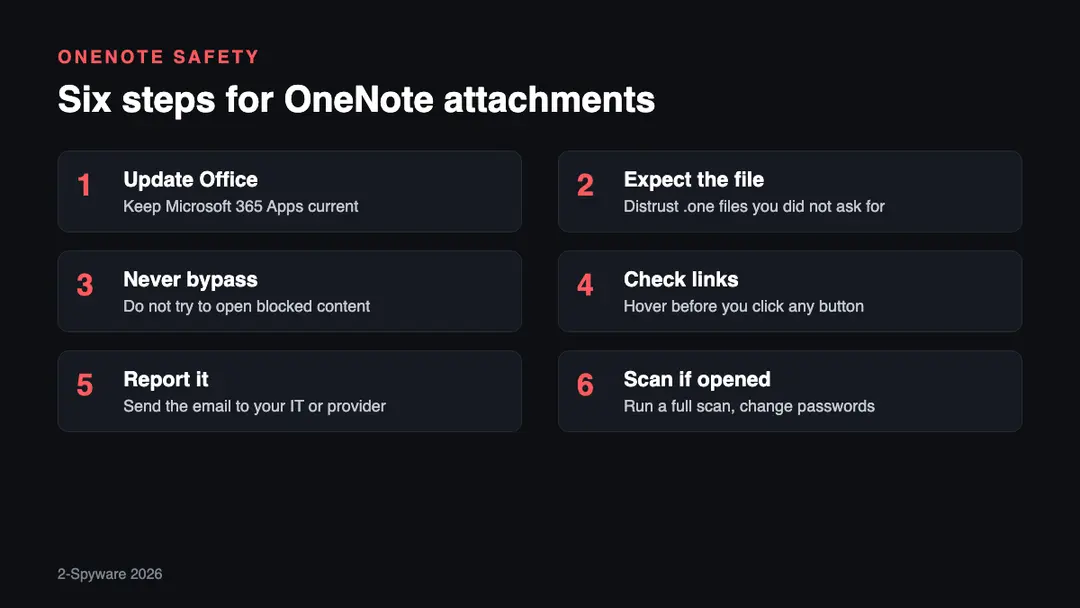
1. Update Office. Keep Microsoft 365 Apps up to date. The embedded file block arrived with Version 2304 and later builds.[4]
2. Expect the file. A .one attachment about an invoice, a parcel or a bonus that you did not expect is a red flag. Those were the exact lures in the 2023 wave.[5]
3. Never bypass. If OneNote says the file type is blocked, do not try to extract or open it another way.
4. Check links. Hover over buttons and links in a notebook. If they lead to a login page outside microsoft.com, close it.
5. Report it. Forward the email to your IT team or mail provider. Our guide on how to report phishing shows where.
6. Scan if opened. If you clicked OK on an old version, run a full scan and use our malware removal guides. Change passwords from a clean device and check your email with our leak check.
What is still unknown
- How many OneNote infections happened before the block. We found no total count.
- How often OneNote is used for phishing links in 2026. We found no recent public figures.
- Whether Microsoft will extend the block to OneNote on the web, Mac or mobile. We found no announcement.
Our original 2023 report
The text below is our report as first published in 2023. We keep it unchanged for the record; the sections above bring it up to date.
Microsoft OneNote is a free digital notebook application that comes with Microsoft Office 2019 and Microsoft 365. Even if a Windows user does not actively use the application, the file format can still be opened because it is installed by default in all Microsoft Office/365 installations. However, cybersecurity researchers have warned that cybercriminals have been sending malicious spam emails[1] with OneNote attachments since mid-December.[2]
These malicious emails masquerade as DHL shipping notifications, invoices, ACH remittance forms, mechanical drawings, and shipping documents. For years, attackers have distributed malware in emails via malicious Word and Excel attachments that launch macros to download and install malware. However, in July, Microsoft disabled macros by default in Office documents, rendering this method untrustworthy for malware distribution.
As a result, attackers started using new file formats like ISO images and password-protected ZIP files. These file formats became more popular as a result of a Windows bug that allowed ISOs to bypass security warnings and the popular 7-Zip archive utility's failure to propagate mark-of-the-web flags to files extracted from ZIP archives. However, both 7-Zip and Windows have recently fixed these bugs, resulting in Windows displaying security warnings when a user tries to open files in downloaded ISO and ZIP formats.
OneNote allows users to insert attachments which was exploited by hackers
OneNote, unlike Word and Excel, does not support macros, which were previously used by threat actors to launch scripts that installed malware. Instead, OneNote allows users to insert attachments into notebooks that will launch the attachment when double-clicked. Threat actors are taking advantage of this feature by attaching malicious VBS attachments that, when double-clicked, launch a script that downloads and installs malware from a remote site.
However, because the attachments appear as a file icon in OneNote, threat actors hide them by placing a large "Double click to view file" bar over the inserted VBS attachments. When the "Click to View Document" bar is moved out of the way, the malicious attachment is revealed to contain multiple attachments. This row of attachments makes it so that if a user double-clicks anywhere on the bar, the attachment will be launched when they do so. Fortunately, when users launch OneNote attachments, the program warns them that doing so may damage their computer and data.
Unfortunately, these types of prompts are frequently ignored, with users simply clicking the OK button. When you click the OK button, the VBS script will start downloading and installing malware. The OneNote files install remote access trojans[3] with information-stealing capabilities.
Follow security measures
Once installed, malware allows threat actors to remotely access a victim's device and steal files, saved browser passwords, screenshots, and, in some cases, record video using webcams. Furthermore, cybercriminals frequently use this type of malware to steal cryptocurrency wallets from victims' devices, making it a costly infection.
Avoiding opening files from unknown sources is the most effective way to protect yourself from malicious attachments. If you open a file by mistake, it's critical not to ignore warnings from the operating system or application.
If you receive a warning that opening an attachment or clicking on a link could harm your computer or files, simply do not press OK and exit the application. If you suspect an email is legitimate, share it with a security or Windows administrator who can help you determine whether the file is safe.
Related guides on 2-Spyware
Frequently asked questions
Is Microsoft OneNote safe to use?
Yes. OneNote is a normal Microsoft app, and since 2023 OneNote for Microsoft 365 on Windows blocks embedded files with dangerous extensions instead of only warning about them.{4} The risk comes from .one files sent by strangers, not from the app. Keep Office updated and do not open unexpected notebooks.
What is OneNote malware?
OneNote malware is a OneNote file that hides a script or program behind a fake "double click to view" button. In 2022 and 2023, such files delivered AsyncRAT, Redline, AgentTesla, Qbot and other malware through emails about invoices and shipping.{5} Clicking the hidden attachment ran the malware.
Can a OneNote file contain a virus?
A OneNote file can carry an embedded file, and that file can be malware. Since Version 2304, OneNote for Microsoft 365 on Windows blocks 120 dangerous file types, such as .vbs, .js, .exe and .lnk.{4}{6} Other OneNote versions do not have this block, and links in a notebook can still lead to phishing.
Which OneNote versions block dangerous attachments?
Only OneNote for Microsoft 365 on Windows. The block does not apply to OneNote on the web, OneNote for Windows 10, OneNote on Mac or on Android and iOS.{6} It reached Current Channel on May 1, 2023 and other channels later.{4}
What is OneNote phishing?
OneNote phishing uses a OneNote file or shared notebook to trick you into opening malware or entering your password on a fake page. In early 2023, lures included invoices, remittances, shipping notices and Christmas bonuses.{5} If a notebook asks you to log in, go to the real site yourself instead.
What should I do if I opened a malicious OneNote attachment?
Disconnect the computer, run a full malware scan and change your passwords from a clean device. OneNote malware often installed remote access trojans and stealers that take saved browser passwords and crypto wallets.{5} Tell your IT team if it happened on a work computer.
Sources
- Malwarebytes. Security Tips, Tricks and How-Tos
- Trustwave. SpiderLabs Blog (no longer online)
- Proofpoint. Data Protection
- Microsoft Learn
- Proofpoint
- BleepingComputer
Log in to comment
No comments yet. Be the first.