Exploited now
6 this week
Data breaches
Neogen
Is it safe?
check a site
Browser updates
Chrome 155.0.8059.40
Scam emails
examples
12,230
guides
5,454
members
Removal guides
Pop-ups & adware
Browser hijackers
Ransomware
Trojans & backdoors
Spyware & keyloggers
Rogue anti-spyware
Malware
Unwanted programs
Scams
Scam alerts
Fake alerts
News
Malware news
Data breaches
Exploited flaws
Browser security
Security
Browsers & vulnerabilities
General
Software
Files
System files
Spyware-related files
Log in
Exploited now
6 this week
Data breaches
Neogen
Is it safe?
check a site
Browser updates
Chrome 155.0.8059.40
Scam emails
examples
Now
20:12
service@paypal scam: fake PayPal invoices with a callback number, and what to do
20:08
McDonald's Monopoly scam: the 2001 fraud, fake prize messages and what to do
19:08
FedEx scam: fake delivery texts, e-mails and calls and what to do
17:08
armoniamiddleeast.ae: a site that served fake Chrome installers for Windows, and what to do
16:08
royalcuts.co.uk: a barber shop site that served fake Chrome installers and CoinMiner files, and what to do
15:08
0807.st: archives tagged SmartLoader and Stealc, and what to do if you ran one on Windows
14:08
cablewireltd.site: a Windows VIP Keylogger host serving Crypted.ps1 PowerShell files, and what to do if one ran
12:46
Facebook Messenger Malware Flaw: 2026 Status and Safety
2-Spyware — page 2
Top today
URL
hxxp://delphiaonline[.]top
TYPE
TR
RISK
High
HITS
Windows
FILED
Oct 9, 2026
TR · High risk
delphiaonline
[.]top
TR
High risk
Remove delphiaonline.top: a Windows malware download site with PowerShell and JavaScript stubs, and what to do if one ran
delphiaonline.top is a website that URLhaus lists for malware downloads: a JavaScript file and two PowerShell scripts both named secured_stub.ps1, all kept in open folders on the…
Ugnius Kiguolis ·
Oct 9, 2026
URL
hxxp://uasputnik[.]com
TYPE
TR
RISK
High
HITS
Windows
FILED
Oct 9, 2026
TR · High risk
uasputnik
[.]com
TR
High risk
Remove uasputnik.com: a Windows ClickFix malware site serving .msi installers, and what to do if you ran one
uasputnik.com is a website that URLhaus lists for three Windows installer (.msi) malware downloads, two of them tagged ClickFix and one tagged Loader, and it refused our test…
Ugnius Kiguolis ·
Oct 9, 2026
URL
hxxp://reinigung-kosanke[.]de
TYPE
TR
RISK
High
HITS
Windows
FILED
Oct 9, 2026
TR · High risk
reinigung-
kosanke
[.]de
TR
High risk
Remove reinigung-kosanke.de: a hacked WordPress site that served Formbook PowerShell scripts, and what to do
reinigung-kosanke.de is a German cleaning business website that URLhaus lists for four PowerShell (.ps1) malware downloads tagged Formbook, and it answered our test with a 503…
Ugnius Kiguolis ·
Oct 9, 2026
URL
hxxp://evacompltd[.]site
TYPE
TR
RISK
High
HITS
Windows
FILED
Oct 9, 2026
TR · High risk
evacompltd
[.]site
TR
High risk
Remove evacompltd.site: a Windows VIP Keylogger malware site (script files and PowerShell) and what to do if one ran
evacompltd.site is a website that URLhaus lists for malware downloads: The site no longer answers when we look it up. If you opened a script file that came from it on Windows,…
Ugnius Kiguolis ·
Oct 9, 2026
URL
hxxp://johnsonsvalves[.]cam
TYPE
TR
RISK
High
HITS
Windows
FILED
Oct 9, 2026
TR · High risk
johnsonsvalves
[.]cam
TR
High risk
Remove johnsonsvalves.cam: a Windows XWorm malware site that hides code in a PNG, and what to do if a script from it ran
johnsonsvalves.cam is a website that URLhaus lists for malware downloads: The site no longer answers when we look it up. If you ran a script or a pasted command from it on…
Ugnius Kiguolis ·
Oct 9, 2026
URL
hxxp://stanarcservice[.]com
TYPE
TR
RISK
High
HITS
Windows
FILED
Oct 9, 2026
TR · High risk
stanarcservice
[.]com
TR
High risk
Remove stanarcservice.com: a Windows ClickFix malware site (s.ps1) and what to do if you pasted its command
Ugnius Kiguolis ·
Oct 9, 2026
TYPE
AD
RISK
High
HITS
Windows
FILED
Oct 9, 2026
AD · High risk
How to delete a Flirt account and stop Flirt dating ads on Android and iPhone
AD
High risk
Remove How to delete a Flirt account and stop Flirt dating ads on Android and iPhone
Ugnius Kiguolis ·
Oct 9, 2026
TYPE
FL
RISK
Medium
HITS
Windows
FILED
Oct 9, 2026
FL · Medium risk
@wcache folder on an SD card: what it is and how to delete it
FL
Medium risk
Remove @wcache folder on an SD card: what it is and how to delete it
Ugnius Kiguolis ·
Oct 9, 2026
TYPE
FL
RISK
Medium
HITS
Windows
FILED
Oct 9, 2026
FL · Medium risk
Sys Stasl on Tecno and Infinix phones: what it is, is it malware, and how to disable it
FL
Medium risk
Remove Sys Stasl on Tecno and Infinix phones: what it is, is it malware, and how to disable it
Ugnius Kiguolis ·
Oct 9, 2026
Scam alerts
4 d ago
KnowBe4 reports that a phishing campaign is targeting Google accounts with fake offers of free Claude Max subscriptions. The site uses a browser-in-the-browser trick to show a fake Google login window, so users should avoid signing in from unexpected giveaway pages and check the real web address before entering credentials.
Oliver Grant
4 d ago
Had a weird one on my Windows 11 box today: a browser page suddenly threw up a security warning saying my profile was “corrupted” and wanted me to sign in again through a cracked-looking prompt. Bit of a cheeky attempt, that. I closed it, checked Task Manager, and it was gone. Anyone else seen that sort of nonsense lately?
Exploited flaws
4 d ago
The Register reports that Microsoft is adding .msix and .msixbundle to Outlook’s block list. New Outlook for Windows and Outlook on the Web in Exchange Online will stop users from downloading or opening those attachments by default, because a malicious package could compromise a device. Administrators who need them can allow the file types before the rollout in early to mid-November 2026.
Gary Whitfield
4 d ago
Got an email on my Windows 11 PC saying my mailbox was nearly full and I had to click a button to keep it active. It looked a bit off, but the sender name was familiar enough. I left it alone. Is this likely a scam, and what’s the safest way to check without clicking anything?
TYPE
FL
RISK
Medium
HITS
Windows
FILED
Oct 9, 2026
FL · Medium risk
AIGPUSniffer: what it is, is it a virus, and how to remove it
FL
Medium risk
Remove AIGPUSniffer: what it is, is it a virus, and how to remove it
AIGPUSniffer.exe is a small Adobe helper that Illustrator and InDesign start for a second or two to test your graphics card before they turn on GPU acceleration. It is not a virus…
Ugnius Kiguolis ·
Oct 9, 2026
URL
hxxp://com[.]google[.]android[.]googlequicksearchbox
TYPE
FL
RISK
Medium
HITS
Windows
FILED
Oct 9, 2026
FL · Medium risk
com
[.]google
[.]android
[.]googlequicksearchbox
FL
Medium risk
Remove com.google.android.googlequicksearchbox referral in Google Analytics: not spam
com.google.android.googlequicksearchbox is the package name of the Google app for Android, and in Google Analytics it marks real visitors who tapped your page in Discover or in a…
Ugnius Kiguolis ·
Oct 9, 2026
CLASS
PC Optimizers
RUNS
Windows only; discontinued, no official
SCORE
1.0 / 10, editors' rating
FILED
Oct 9, 2026
1.0
Review · PC Optimizers
Restoro Cyprus Limited
PC Optimizers
Restoro Review 2026: FTC Case, PUP Flag, Uninstall, Refund review
Restoro review 2026: no longer sold after a $26M FTC case. Why Malwarebytes flags it as a PUP, how to uninstall it, stop charges and get FTC refunds.
Our rating 1.0/10 · 2-Spyware Editorial Team ·
Oct 9, 2026
URL
hxxp://meteorrejects[.]net
TYPE
TR
RISK
High
HITS
Windows
FILED
Oct 9, 2026
TR · High risk
meteorrejects
[.]net
TR
High risk
Remove meteorrejects.net: a Minecraft cheat-addon site that URLhaus lists for SilentNet stealer files
meteorrejects.net is a polished website for a Minecraft addon called Meteor Rejects, and URLhaus lists three of its .jar files as malware tagged SilentNet and stealer. If you…
Ugnius Kiguolis ·
Oct 9, 2026
URL
hxxp://porterneuman[.]mx
TYPE
Trojans
RISK
High
HITS
Windows
FILED
Oct 8, 2026
Trojans · High risk
porterneuman
[.]mx
Trojans
High risk
Remove porterneuman.mx: PowerShell and JavaScript files tied to the AveMaria remote access trojan, and what to do
porterneuman.mx is a web address where URLhaus found five script files in a WordPress plugin folder on 30 September 2026: four PowerShell stubs and one JavaScript file. One stub…
Ugnius Kiguolis ·
Oct 8, 2026
URL
hxxp://donutclientsmods[.]xyz
TYPE
Trojans
RISK
High
HITS
Windows
FILED
Oct 8, 2026
Trojans · High risk
donutclientsmods
[.]xyz
Trojans
High risk
Remove donutclientsmods.xyz: fake DonutSMP Minecraft mods tagged SilentNet, and what to do if you ran one
Ugnius Kiguolis ·
Oct 8, 2026
URL
hxxp://sqpengg[.]com
TYPE
Trojans
RISK
High
HITS
Windows
FILED
Oct 8, 2026
Trojans · High risk
sqpengg
[.]com
Trojans
High risk
Remove sqpengg.com: a server handing out crypted PowerShell scripts, and what to do if one ran on your PC
Ugnius Kiguolis ·
Oct 8, 2026
URL
hxxp://donutsmpcheats[.]org
TYPE
Trojans
RISK
High
HITS
Windows
FILED
Oct 8, 2026
Trojans · High risk
donutsmpcheats
[.]org
Trojans
High risk
Remove donutsmpcheats.org: fake Minecraft cheat mods with the SilentNet stealer, and what to do if you installed one
Ugnius Kiguolis ·
Oct 8, 2026
URL
hxxp://maciejbi[.]hosting24[.]pl
TYPE
Trojans
RISK
High
HITS
Windows
FILED
Oct 8, 2026
Trojans · High risk
maciejbi
[.]hosting24
[.]pl
Trojans
High risk
Remove maciejbi.hosting24.pl: a hosting subdomain that served Remcos scripts and a stego picture, and what to do if your PC fetched them
Ugnius Kiguolis ·
Oct 8, 2026
Scam alerts
4 d ago
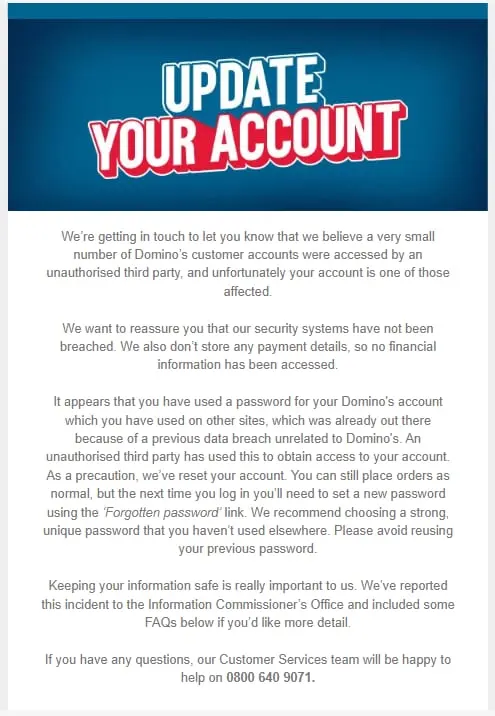
Malwarebytes Labs reports that Domino’s customers have received emails saying their account was accessed by a third party. Domino’s says its systems were not breached, and that the logins used a password and email combination stolen from another online account. The company reset affected accounts and says customers should use a strong, unique password for every site, turn on two-factor authentication where available, and avoid following links in unsolicited emails. Unsolicited account-update emails claiming to be from Domino’s may be phishing attempts.
Hannah Price
5 d ago
This evening on my Windows 11 laptop I got a message in my browser saying my payment info had been “verified” and I should review a failed delivery charge. It looked almost normal, but the sender address and the timing felt off, so I closed it and checked my account directly. Has anyone else seen these fake payment notices lately?
Malware news
5 d ago
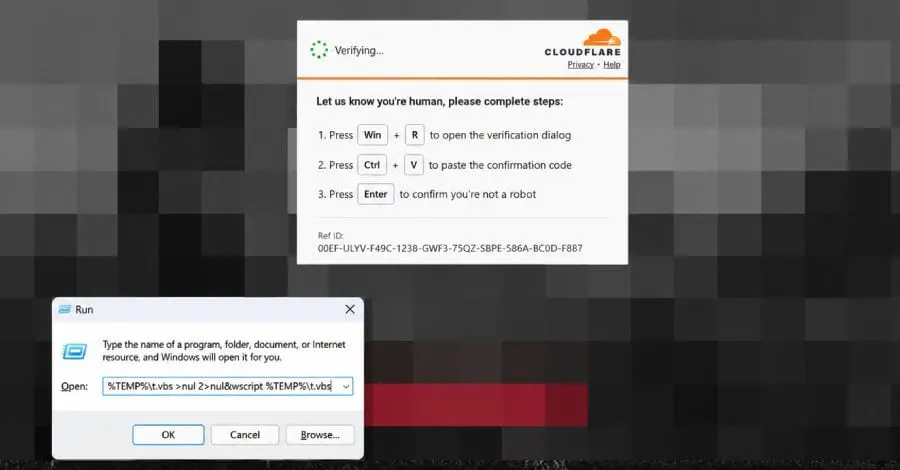
The Hacker News reports that a new ClickFix attack is using compromised websites to trick Windows users into running a malicious payload cached in the browser. The attack hides a script in browser cache, then uses it to fetch more payloads and target browser and device credentials. Windows users should avoid copying and running commands from unexpected sites or pop-ups, and be cautious of fake error, CAPTCHA, or browser update prompts.
Data breaches
5 d ago
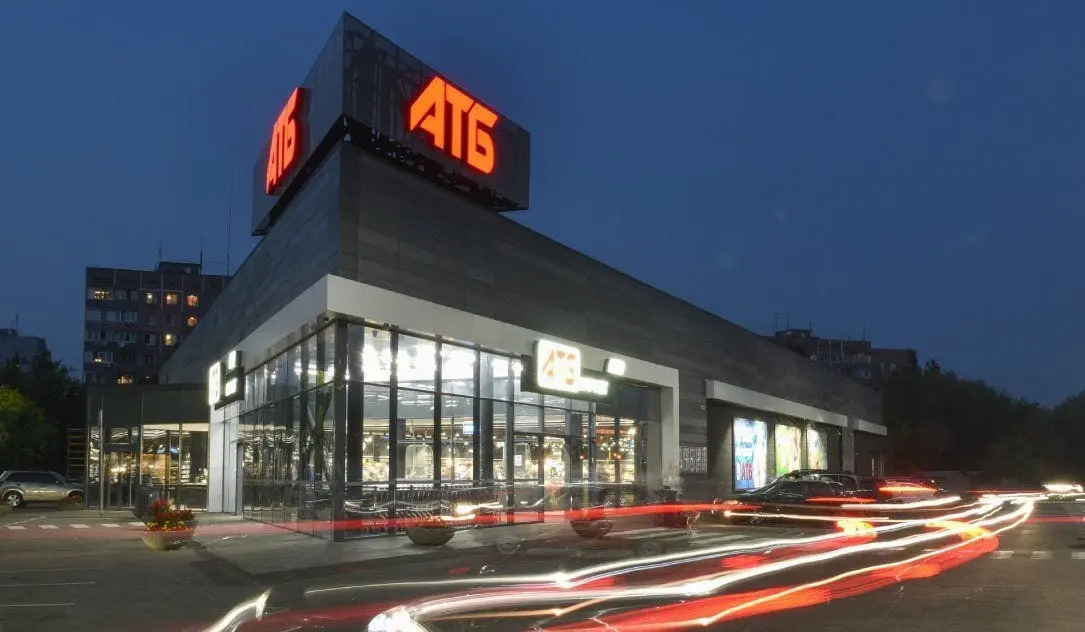
The Record reports that Ukraine’s largest grocery store chain, ATB, confirmed a cyberattack after hackers posted an extortion demand on its website and claimed they had stolen data from millions of customers. The hackers said the data included names, phone numbers, email and physical addresses, password hashes, and employees’ passport information. People who shopped there should watch for phishing, change reused passwords, and monitor accounts for suspicious activity.
URL
hxxp://87130921-60-20220830152356[.]webstarterz[.]com
TYPE
Trojans
RISK
High
HITS
Windows
FILED
Oct 8, 2026
Trojans · High risk
87130921-
60-
20220830152356
[.]webstarterz
[.]com
Trojans
High risk
Remove 87130921-60-20220830152356.webstarterz.com: an open folder serving Formbook and XWorm PowerShell scripts, and what to do if one ran
87130921-60-20220830152356.webstarterz.com is a subdomain that URLhaus lists six times in September and October 2026 for PowerShell scripts (crypted.ps1, secured_stub.ps1) and a…
Ugnius Kiguolis ·
Oct 8, 2026
URL
hxxp://ficus[.]in
TYPE
Trojans
RISK
High
HITS
Windows
FILED
Oct 8, 2026
Trojans · High risk
ficus
[.]in
Trojans
High risk
Remove ficus.in: picture files hiding the Remcos remote access trojan, and what to do if a script fetched them
ficus.in is a web address, registered since 2010, that URLhaus lists ten times between 15 September and 1 October 2026 for picture files (img_*.png in its img folder) tagged…
Ugnius Kiguolis ·
Oct 8, 2026
URL
hxxp://web[.]opendrive[.]com
TYPE
Trojans
RISK
High
HITS
Windows
FILED
Oct 8, 2026
Trojans · High risk
web
[.]opendrive
[.]com
Trojans
High risk
Remove OpenDrive virus: why web.opendrive.com shows up in malware alerts, and what to do if a file from it installed Remcos
OpenDrive is a legitimate cloud storage service, not a virus, but criminals upload files to it that hide malware and point their loaders at them. On 9 and 10 September 2026…
Ugnius Kiguolis ·
Oct 8, 2026
URL
hxxp://res[.]cloudinary[.]com
TYPE
Trojans
RISK
High
HITS
Windows
FILED
Oct 8, 2026
Trojans · High risk
res
[.]cloudinary
[.]com
Trojans
High risk
Remove Cloudinary virus: why res.cloudinary.com shows up in malware alerts, and what to do if a loader fetched its pictures
Cloudinary is a legitimate image hosting service, not a virus, but criminals upload JPG pictures that hide malware and point loaders at them. In September 2026 URLhaus listed…
Ugnius Kiguolis ·
Oct 8, 2026
URL
hxxp://cdn[.]jsdelivr[.]net
TYPE
Trojans
RISK
High
HITS
Windows
FILED
Oct 8, 2026
Trojans · High risk
cdn
[.]jsdelivr
[.]net
Trojans
High risk
Remove jsDelivr virus: why cdn.jsdelivr.net shows up in malware alerts, and what to do if you ran a pasted command
jsDelivr is a legitimate free CDN, not a virus, but criminals publish malware on GitHub and link to it through cdn.jsdelivr.net. In September 2026 URLhaus listed five such files:…
Ugnius Kiguolis ·
Oct 8, 2026
URL
hxxp://c2[.]teamzeroday[.]net
TYPE
Trojans
RISK
High
HITS
macOS
FILED
Oct 8, 2026
Trojans · High risk
c2
[.]teamzeroday
[.]net
Trojans
High risk
Remove c2.teamzeroday.net: a Mirai botnet host that offered manta files for routers and other small devices, and how to clean one
Ugnius Kiguolis ·
Oct 8, 2026
URL
hxxp://xiangduck[.]sld[.]tw
TYPE
Trojans
RISK
High
HITS
Windows
FILED
Oct 8, 2026
Trojans · High risk
xiangduck
[.]sld
[.]tw
Trojans
High risk
Remove xiangduck.sld.tw: a server that handed out Mirai bot files for routers and cameras, and what to do if a device fetched them
Ugnius Kiguolis ·
Oct 8, 2026
URL
hxxp://fahrzeugvergabe[.]de
TYPE
Trojans
RISK
High
HITS
Windows
FILED
Oct 8, 2026
Trojans · High risk
fahrzeugvergabe
[.]de
Trojans
High risk
Remove fahrzeugvergabe.de: a German FileFix page that made visitors paste a PowerShell command, and what to do if you did
Ugnius Kiguolis ·
Oct 8, 2026
TYPE
News
FILED
Oct 7, 2026
News
Bulgaria Tax Agency Data Leak: 2026 Facts and Status
News
Bulgaria Tax Agency Data Leak: 2026 Facts and Status
Jake Doevan ·
Oct 7, 2026
Jessica Lane
5 d ago
That’s pretty unsettling, especially if MicroVMs were being used to keep things nicely separated. I’m on a Windows 11 laptop at home, so I always pay attention when a “guest to host” issue shows up because it makes me wonder how much trust is really left in the isolation layer. What do you think—does this sound like a real escape risk or something that still needs a lot more proof?
Paul Stevens
5 d ago
Another thing that keeps coming up is the so-called Windows support call scam. The pattern is usually the same: a pop-up or message says there is a serious problem, then pushes you to call someone right away. If you spot one, what do you do first: close the browser, check Task Manager, or just ignore it?
Ethan Cole
5 d ago
One small Windows habit people often miss: check your browser’s saved passwords and autofill entries now and then. If an old site, strange login, or typo is sitting there, delete it. It only takes one reused or saved password on a fake login page to cause trouble.
Linda Harper
5 d ago
This afternoon on my Windows 10 laptop, I got an e-mail that said my Microsoft account storage was full and I needed to click a link right away or some files might be deleted. It looked a little off to me, but I am not sure. Does this sound like phishing, and what should I do with it?
Loading…
No more articles
Could not load, try again
Try again
« Previous
1
2
3
4
…
472
Next »
5,454 members already here
Reading, writing, commenting and voting. 0 verified · 179 joined this year
All members
Join
News
Members
Publish
Me