
Google WebHP virus: what it is and how to remove it
Google WebHP virus is browser hijacker activity redirecting to google.com/webhp, typically not a dangerous virus. The 2020 guide identified it as PUP infection often bundled with legitimate software during quick installations.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Not sure what changed your search to google.co.uk? An automatic scan checks extensions, programs and browser settings in one pass.
Do it yourself · free Remove Google WebHP virus yourself 5 steps, about 15 minutes, no software needed.
Start the steps
Google WebHP virus: summary
| Distribution | Freeware installations lead to such infiltrations of questionable programs because users tend to choose recommended or quick options instead of Advanced or Custom ones |
|---|---|
| Name | Google WebHP virus |
| Type | Browser hijacker |
| Issues | The program replaces the homepage, search engine, new tab preferences, so the content can be controlled and users exposed to shady advertising pages |
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Symptoms | A changed search engine |
|---|---|
| Evidence | 4 write-ups by security sites; details still limited |
| Search page | google.co.uk |
| Browsers | Chrome, Edge and Firefox |
| First seen | 31 December 2020 |
| Facts checked | 5 October 2026 |
Is Google WebHP virus dangerous? What it collects
What readers reported about Google WebHP virus
I need to remove Google WebHP. Is there a free malware program?. I need to remove Google WebHP. Is there a free malware prog which will effectively remove this pl?
I am infected with Google.com/webhp virus. I am infected with Google.com/webhp virus. I recognize that the URL is wrong because it is not the similar one as it usually appears. The first thing I noticed was that the URL is much longer than it typically is. Can you recommend something to remove Googl…
From the comments under our earlier guide; names and contact details removed.
From our report of Dec 2020 · not reviewed since
WebHP - a term used to describe a suspicious Chrome redirect activity
WebHP virus is a term that many users adapted after they saw a suspicious behavior when using their Google Chrome web browser.
According to users, each time when they load their homepage or search for something online, they are instead redirected to google.com/webhp. In most cases, the activity is only prevalent when searching through the omnibar.
This activity is difficult for many users to explain, as they seek to find the root causes of such redirects. While the term "WebHP virus" sounds dangerous, in reality, it is not likely to be a virus.
First of all, suspicious homepage and new tab address changes can be related to a browser hijacker - a type of a potentially unwanted program that modifies web browser settings to insert ads into users' searchers.
This is especially true if any attempt to search online using the assigned engine results in the list filled with advertisements, redirects, banners, and in-text links the lead to suspicious material online with the purpose of rerouting to sponsored pages.
Experts report that computer users that experience continuous redirects to http://google.com/webhp should also check their computers for the Conduit virus. These are the computer intruders that focus on forcing users to visit low-quality websites, possible advertising platforms, so the revenue can get easily made from all the page visits and clicks on pop-ups ads.
However, this activity also might be related to internal Google processes, namely ones related to how the company handles search results and implements security certificates, known as SSL. Therefore, users might also encounter similar behavior with https //www.google.com/ gws_rd=ssl redirect.
Google also uses different scripts that are based on users' location. Therefore, some users might also encounter https //www.google.es/ gws_rd=ssl if they are coming from Spain, for example.
HTTP redirects are usually considered suspicious, as they might indicate an infection of a browser hijacker or another potentially unwanted program. These apps are typically installed unintentionally by users due to a well-known, deceptive distribution technique known as software bundling.
Alternatively, they might also be tricked by misleading advertisements, or fake update prompts. However, some might also install PUPs on their systems when believing that it could be a good addition to web browsing activities.
The so-called Chrome WebHP virus infiltrates the computer system silently and adds a hazardous browser extension to an affected web browser. It can also change the browser's homepage to google.com/webhp or google.co.uk/webhp.
Google WebHP can also display misleading ads pushing users into installing fake updates and useless programs. Promotional ads can have direct download scripts and lead to other related intruder installations like Searchou. This redirect issue occurs on Firefox, Chrome, Safari browsers, and can lead to serious problems with performance, speed, security, or privacy issues.
These websites look exactly like the real Google search engine. Unfortunately, due to its resemblance to the real Google search, it can deceive the computer user and trick him/her into using it, thinking that it is a safe search engine.
Unfortunately, the fake search engine that is provided by this virus is dangerous to use because it can trigger redirects to various third-party websites, which can be malicious or provide misleading content. Please, do not use this search engine if you see the webhp appended to the URL.
The hijacker can compromise your search settings despite the country you live in, so for example, French PC users might start experiencing redirects to google.fr/webhp. In this case, make sure you initiate Google WebHP redirect removal.
Reportedly, this hijacker slithers into the computer system along with the infamous Conduit Toolbar, so make sure you remove it as well. Beware that sometimes the hijacker doesn't even change the homepage address in the browser, causing additional problems while trying to eliminate it. In this case, check Chrome's Omnibox which should deliver you altered search results each time you attempt to search via URL box.
If you cannot remember installing Conduit or similar third-party software, you need to remove it together with other suspicious files from your computer. This should fix the issue with the Google WebHP virus. The best way to do so would be running a scan with anti-malware tools like or .
From our report of Dec 2020 · not reviewed since
Potentially unwanted programs might appear on your system without permission
The most of redirect viruses manage to enter computer systems in a rather subtle way.
They typically pretend to be safe-to-use programs and even present themselves as "recommended" software. However, they do not reveal themselves in a direct way. They spread along with other free applications and get installed in one software bundle.
As you have understood, the browser hijacker is distributed in software packs, so in order to avoid installing it, you need to decompose such software packs. When you launch the installer of software you have just downloaded, do not rush!
Please read absolutely all information the installer provides, including Terms of Use/Privacy Policy documents. After that, proceed to the next step. Once you reach installation "settings," choose either Advanced or Custom option (NOT Default/Standard ones!). Then simply deselect all suspicious-looking components.
From our report of Dec 2020 · not reviewed since
More from our earlier report on Google WebHP virus
- Google WebHP virus elimination is possible with anti-malware tools and similar programs that can check the machine for any suspicious applications and files.
- All traces of the potentially unwanted program get deleted this way
- There are parts of the system that can get damaged by this program directly.
- It ads files or removes them, affects processes and system functions, so run to find such altered parts and fix possible damage automatically
Check your browser and PC
- Address:
google.co.uk
How to remove Google WebHP virus
How to remove Google WebHP virus and get your search engine back
Remove the extension first.
The search settings only stay fixed once nothing on the PC can change them again.
Step 1: Remove extensions you did not add
Google WebHP virus often works through an extension, so go through the extension list of each browser:
chrome://extensionsedge://extensions- Extensions and themes in Firefox
Switch suspicious extensions off one at a time and reload the page where the problem shows, then remove the one that stops it, and any other you did not add.
Remember the other browsers and profiles on the PC. If Remove is missing or greyed out, a policy forces the extension, which the policy step deals with. Windows 11 and Windows 10 show the same pages.
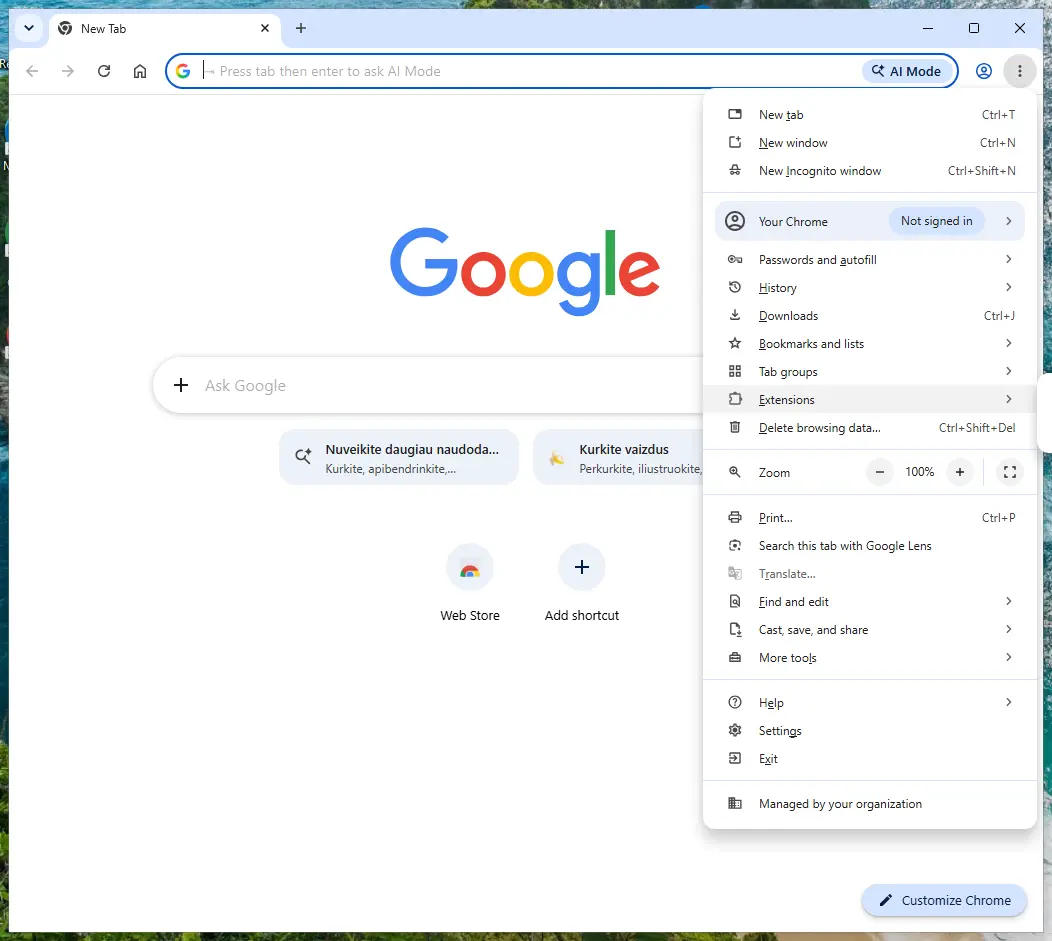
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Put the search engine back and delete google.co.uk
Searches that pass through
google.co.ukmean the browser's default search engine was replaced. Chrome: Settings > Search engine > Manage search engines and site search, then Make default on Google, Bing or another engine you chose, and Delete on google.co.uk.Edge has the same list under Manage search engines (search the Settings page for it), and Firefox under Settings > Search.
Look at On startup and the homepage settings too and remove the hijacker's address there. Nothing in this step differs between Windows 11 and Windows 10.
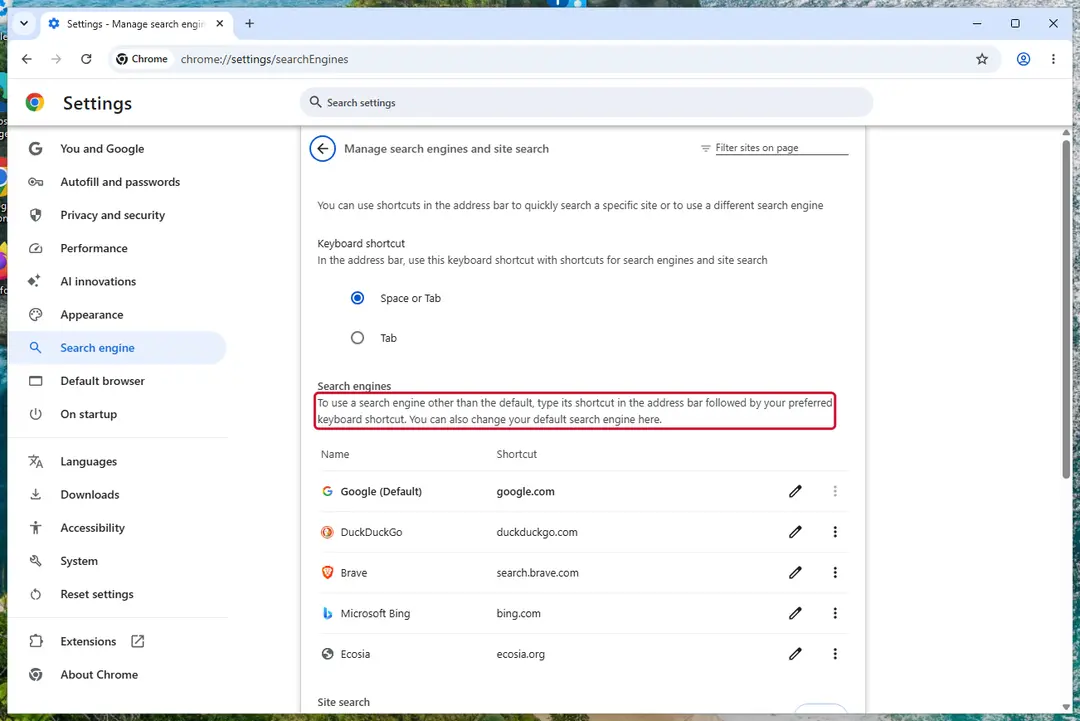
Chrome on Windows 11: check Search engine and On startup. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 3: Uninstall programs you did not mean to install
Open Settings > Apps > Installed apps in Windows 11, or Settings > Apps > Apps & features in Windows 10, and sort the list by install date. Look at what appeared around the day the problem started and uninstall every program you do not recognise or did not choose.
Free converters, PDF and video tools, "system optimizers" and unknown browsers are the usual carriers of Google WebHP virus. If a name is unclear, search for it before you remove it, so you do not uninstall a driver or a Windows component.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 4: Reset the browser
Finish the browser part with a reset, which puts the search engine, start page, new tab page and site permissions back to their defaults and switches extensions off. Chrome: Settings > Reset settings > Restore settings to their original defaults.
Edge: Settings > Reset settings. Firefox: Help > More troubleshooting information > Refresh Firefox, which also removes its extensions. Your bookmarks and saved passwords are kept, and the menus are the same on Windows 11 and Windows 10.
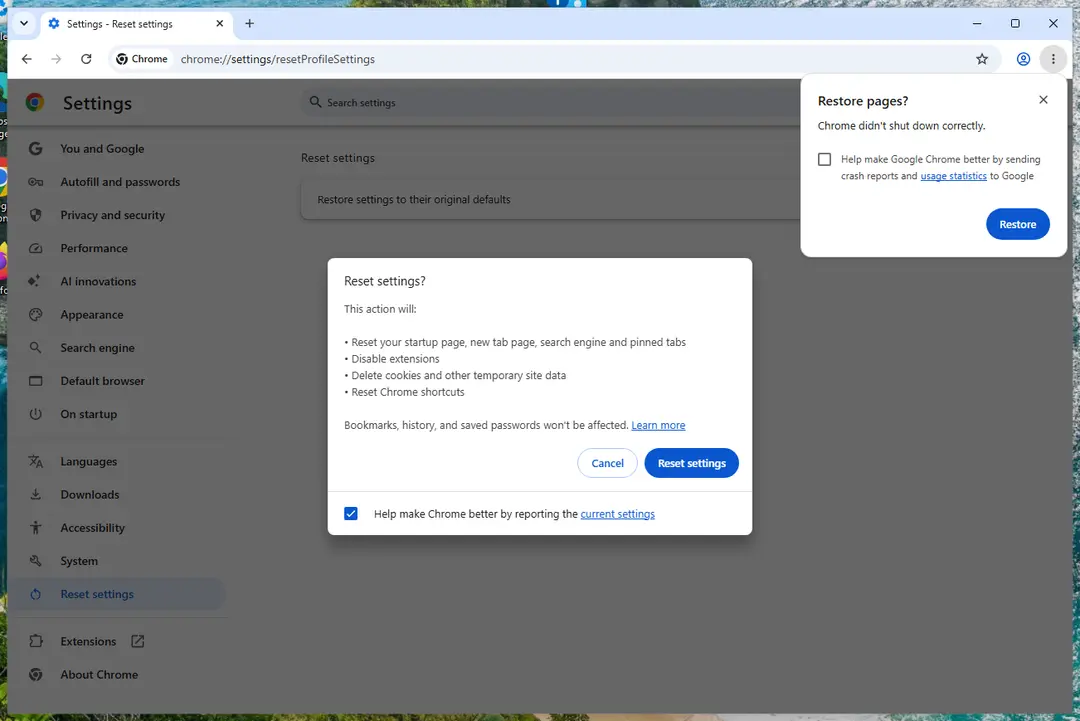
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
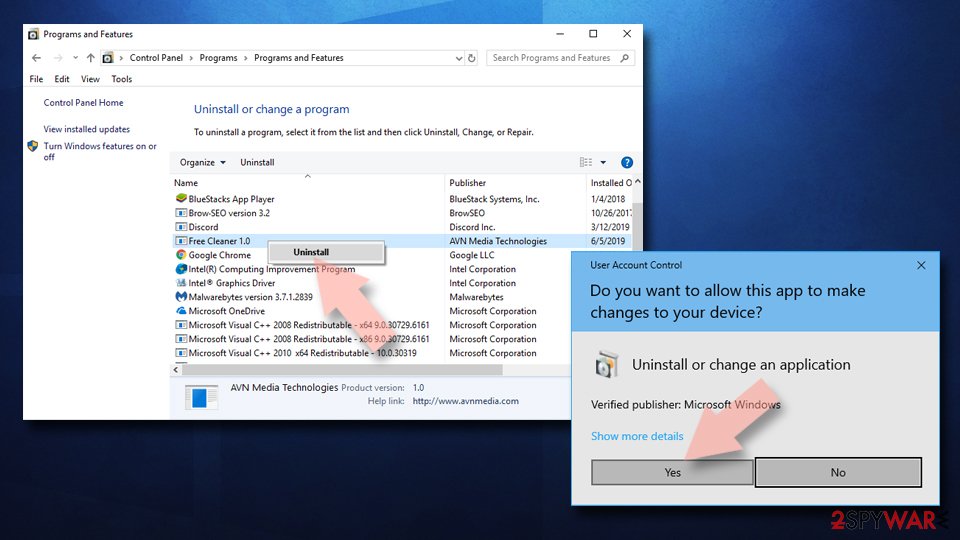
Uninstall from Windows
First of all, uninstall all shady programs such as Conduit Search, SearchProtect, and other suspicious programs from the system. Then press Windows key + R to launch Run prompt and type regedit. Press Enter. In Windows Registry Editor, go to Edit > Find and search for Conduit. Delete all keys that the search finds for you.
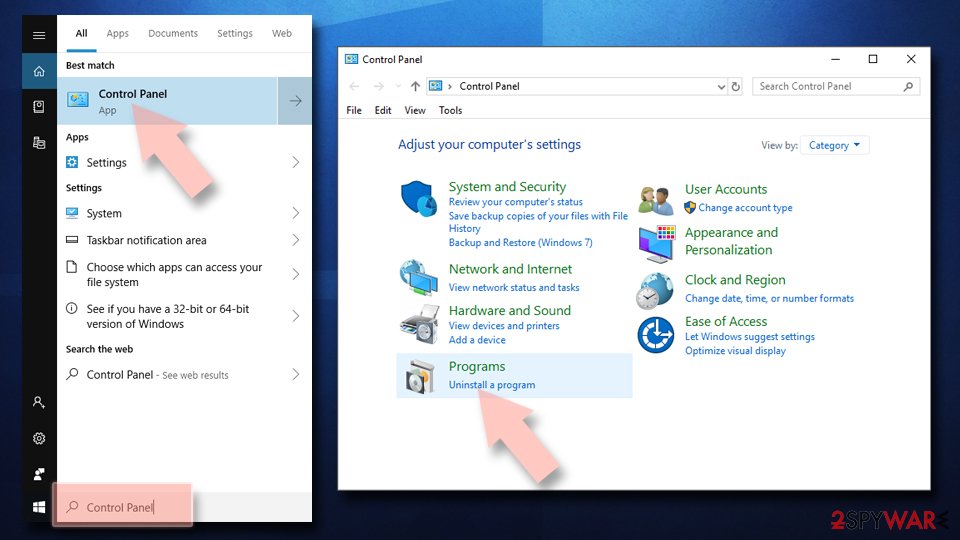
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
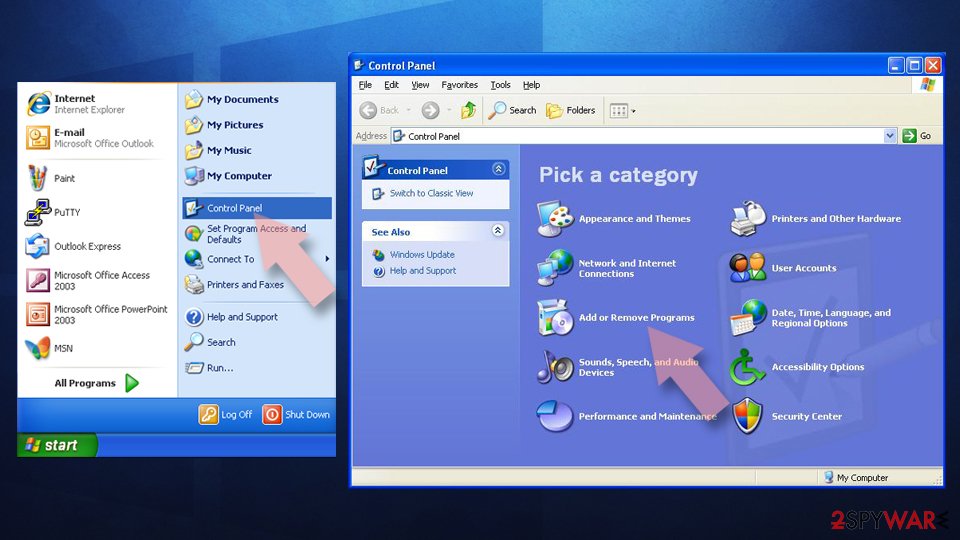
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
Delete Conduit from Chrome to stop persistent redirects to google.com/webhp. Reset search settings using the example provided below.
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Use the provided guide to remove the hijacker from your PC. To complete the task successfully, refresh Firefox afterward.
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
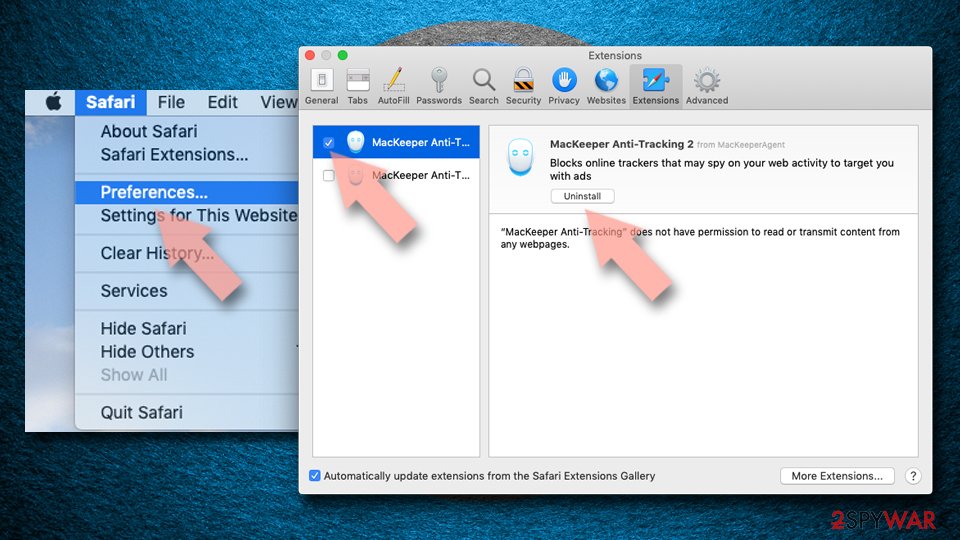
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
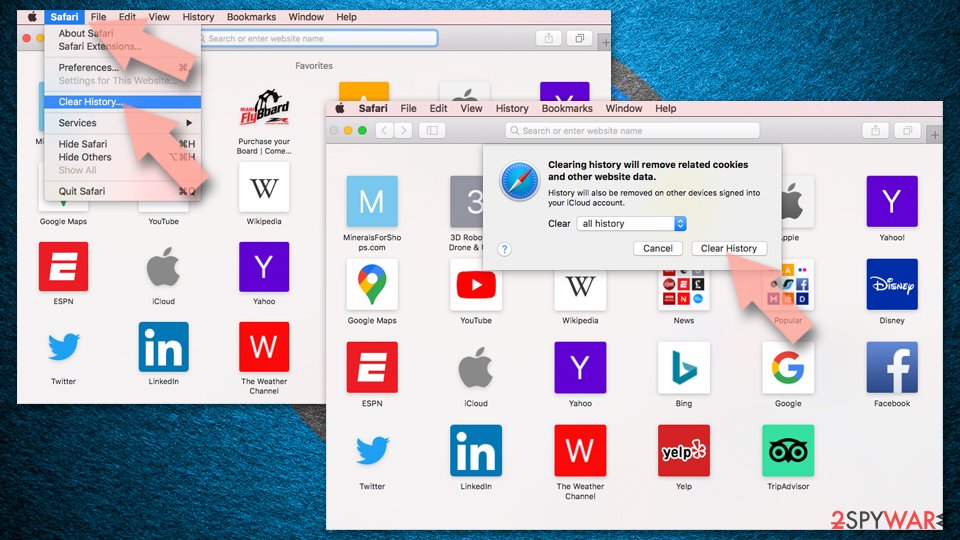
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
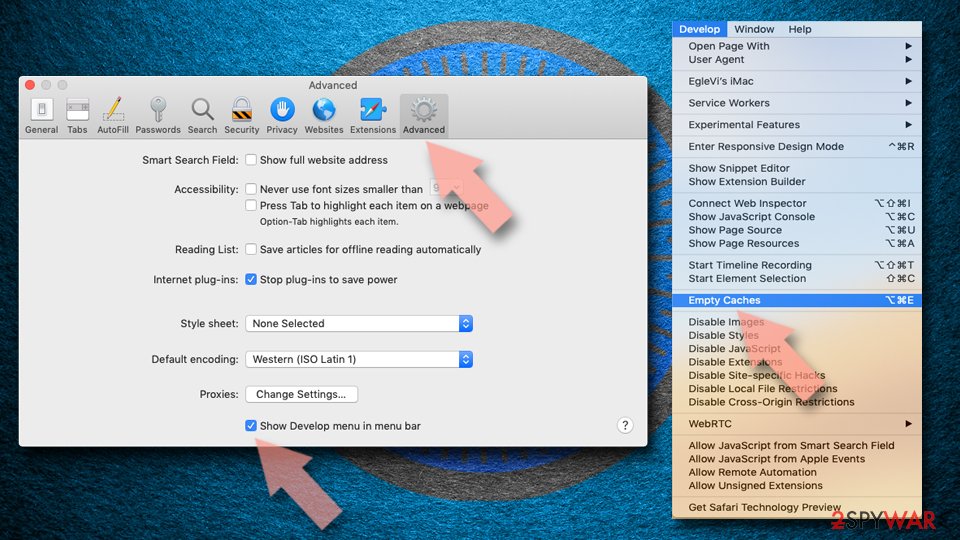
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
Remove the unwanted application:
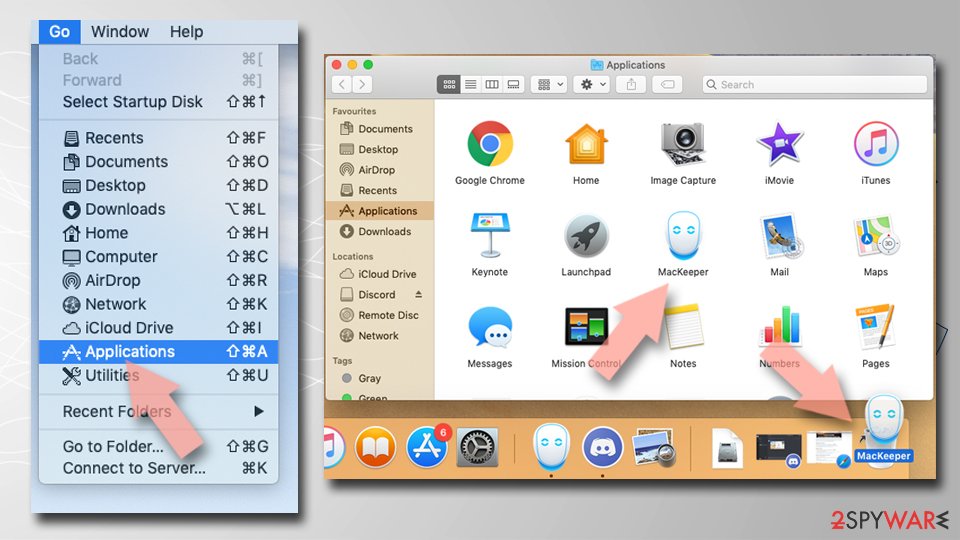
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
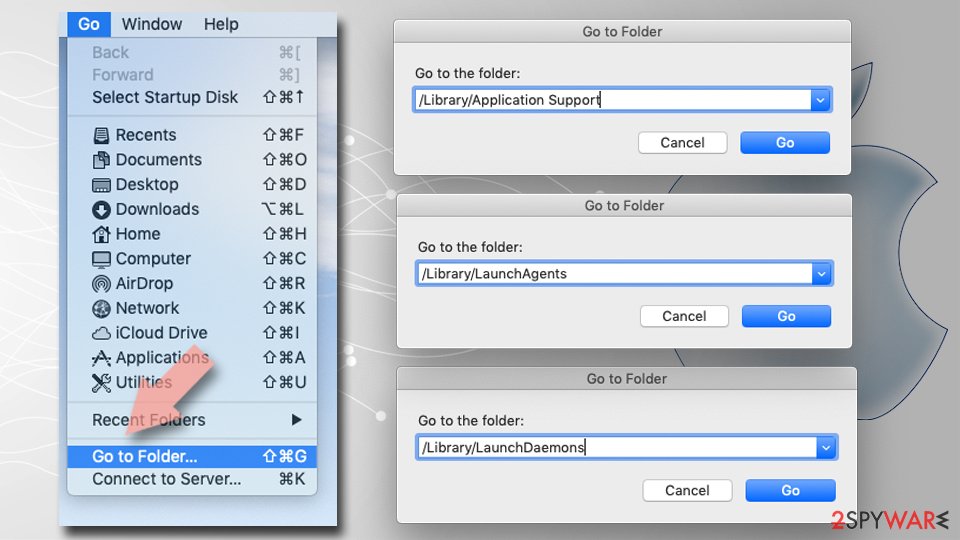
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
Remove dangerous add-ons:
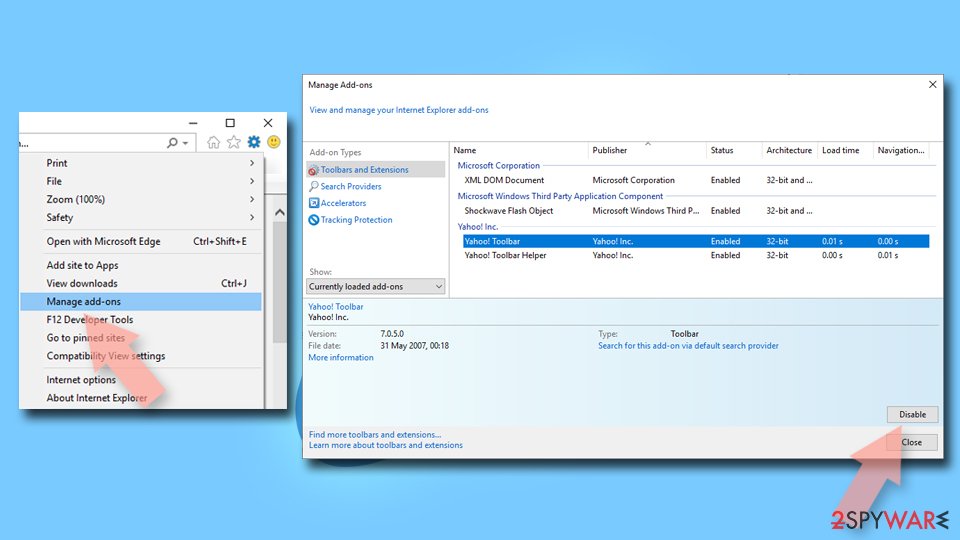
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
Change your homepage if it was altered:
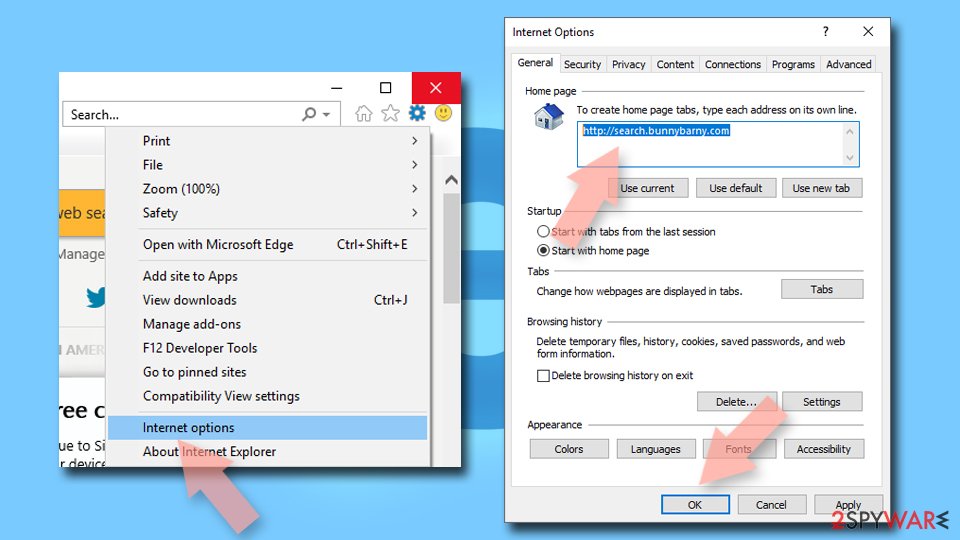
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
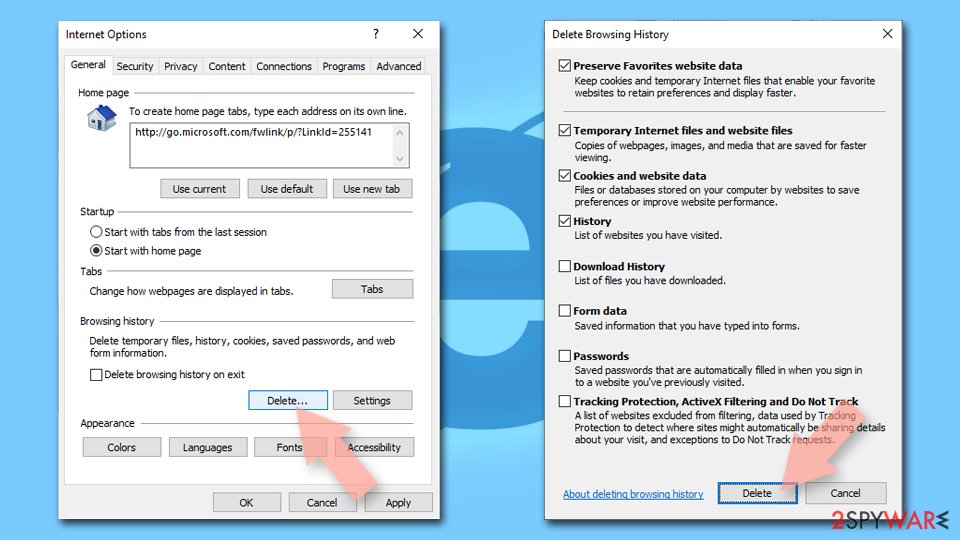
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
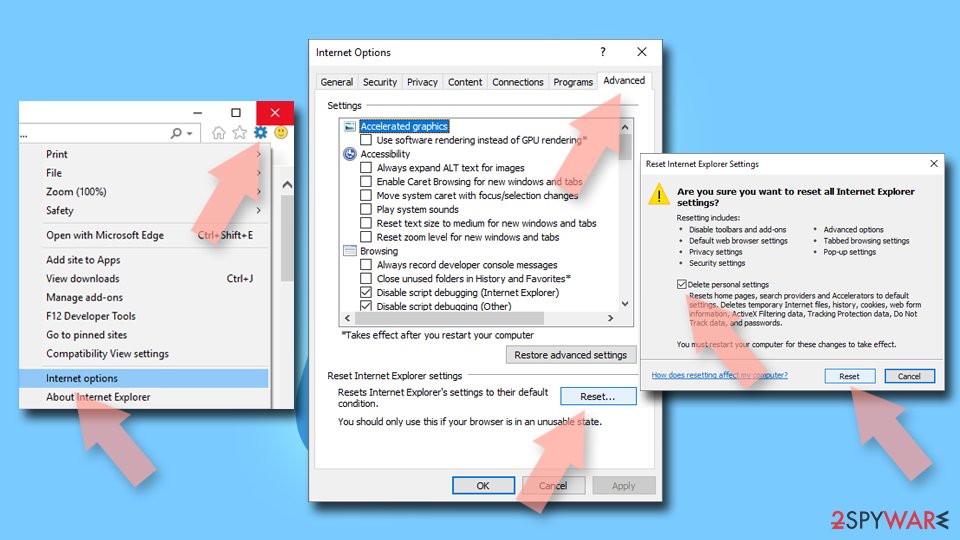
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
From our report of Dec 2020 · not reviewed since
Google WebHP removal instructions
To remove Google WebHP, you need to carefully review the list of programs that were recently installed on your computer, and also all browser extensions that were added without your knowledge. You have to delete all programs and extensions that you cannot remember installing.
WebHP virus can be related to potentially unwanted programs and you should not ignore its existence because it can pose a threat to your computer. The sooner you run the anti-malware program the better because you can clear threats properly from the machine and avoid further damage.
Please follow the Google Webhp removal instructions provided under this article and you will easily banish the malware from your computer.
It is also important to note that you will most likely be unable to remove the so-called https //www.google.com/ gws_rd=ssl virus from your system, as it is not related to malicious activity but used by Google itself.
Conduit Search, SearchProtect, and other suspicious programs from the system. Then press Windows key + R to launch Run prompt and type regedit.
Press Enter. In Windows Registry Editor, go to Edit > Find and search for Conduit. Delete all keys that the search finds for you.
Questions about Google WebHP virus
What is Google WebHP virus?
Google WebHP virus is a term describing suspicious Chrome redirect activity to google.com/webhp. Despite the alarming name, it is not typically a dangerous virus but rather a browser hijacker—a potentially unwanted program modifying browser settings.
The 2020 guide noted that WebHP redirects occur mainly in Chrome's omnibar search, making users worry their browsers are infected. In most cases, this activity relates to browser hijackers or, less commonly, internal Google security certificate processes.
Why does my browser redirect to google.com/webhp?
The most likely cause is infection with a browser hijacker that modifies your homepage or search settings to google.com/webhp. The 2020 guide specifically mentioned the Conduit virus as a common cause.
When you search via the omnibar or load your homepage, the hijacker forces the redirect. Some users also encounter https://www.google.com/gws_rd=ssl redirects due to Google's internal SSL processes. Each case requires diagnosis to determine the root cause.
Is google.com/webhp safe to use?
The legitimate google.com/webhp is a safe Google search page variant, but fake search engines mimicking it are dangerous. The 2020 guide warned that these counterfeits trigger further redirects to malicious or misleading websites.
The fake pages look identical to the real Google search, deceiving users into trusting them. If you see "webhp" appended to your URL unexpectedly, you likely have a hijacker installed, not legitimate Google functionality.
How does the WebHP browser hijacker get installed?
Like most PUPs, WebHP hijackers distribute through software bundling and deceptive tactics. The 2020 guide explained that users typically install them unintentionally by choosing Recommended or Quick installation options instead of Advanced/Custom settings.
Misleading advertisements and fake update prompts can also trick users into accepting the hijacker. Users may even believe they are installing a useful browser addition without realizing it is unwanted software.
Can WebHP hijacker damage my computer?
While WebHP itself is not malicious malware, it degrades browsing experience and potentially exposes you to harm. The hijacker can display misleading ads pushing fake updates and useless programs, redirect you to phishing sites, and compromise your privacy through data tracking.
The 2020 guide noted it affects performance, speed, and security. Leaving it installed allows continuous exposure to promotional scams and malicious third-party content.
Is WebHP related to Conduit virus?
Yes. The 2020 guide reported that the WebHP hijacker is often installed alongside the Conduit Toolbar, another browser hijacker. Conduit focuses on forcing users to visit low-quality websites for ad revenue, similar to WebHP.
If you have WebHP redirects, you should also check for and remove Conduit and any related suspicious extensions from your browser.
How is WebHP different from Google's legitimate ssl redirects?
The 2020 guide distinguished between malicious WebHP hijacking and legitimate Google processes. Legitimate redirects include https://www.google.com/gws_rd=ssl and country-specific variants like https://www.google.es/gws_rd=ssl based on your location.
These serve legitimate security purposes. However, unexpected redirects to google.com/webhp in your search results indicate browser hijacking. Legitimate Google redirects occur silently in the background; hijacker redirects interrupt your intended browsing.
How do I remove the WebHP hijacker?
Scan your system with anti-malware software to detect and remove the browser hijacker and any associated PUPs. The 2020 guide recommended full system scans to eliminate all related files.
After removal, reset your browser settings to default to undo homepage and search engine changes. Carefully review your browser extensions for any suspicious add-ons installed without your consent. If WebHP redirects persist after removal, perform a second scan to ensure complete elimination.
Will Fortect remove Google WebHP virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Google WebHP virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- LesVirus: LesVirus (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)
- Microsoft Learn: How Microsoft names malware (read October 5, 2026)