
RarGenie virus: what it is and how to remove it
RarGenie is a shady ad-supported application designed for Mac OS X . If your Mac suddenly started acting suspiciously, display ads and cause redirects during your browsing sessions, you should remove RarGenie right away.
Facts checked October 6, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
If redirects to dieviren.de keep coming back, a free scan can check extensions, programs and browser settings in one pass.
Do it yourself · free Remove RarGenie virus yourself 4 steps, about 12 minutes, no software needed.
Start the steps
RarGenie virus: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | RarGenie virus |
| Type | Adware extension |
| Symptoms | Redirects to an unknown domain |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Evidence | 4 write-ups by security sites; details still limited |
|---|---|
| Domains | dieviren.de |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 31 July 2017 |
| Facts checked | 6 October 2026 |
Is RarGenie virus dangerous?
From our report of Jul 2017 · not reviewed since
RarGenie adware attacks Mac users and tries to avoid detection
RarGenie is a shady ad-supported application designed for Mac OS X .
If your Mac suddenly started acting suspiciously, display ads and cause redirects during your browsing sessions, you should remove RarGenie right away. This program might also change your browsers' settings and set Bing search page as your default search engine provider and home page.
In addition, this adware can hijack your Mac together with other potentially unwanted programs (PUPs) such as:
It is important to uninstall these programs at the same time you decide to remove RarGenie virus. They are highly untrustworthy programs that are meant to serve you sponsored content in various forms. Most of the time, they generate pop-up ads, although you can also run into banners or sponsored search results delivered through the new search engine that RarGenie forces you to use.
During its stay on your Mac OS, RarGenie can deliver coupons, discount codes, special offers, and present similar time and money saving offers that might look tempting to you. Sadly, these ads can be used as bait to lure you into vague websites.
Ads delivered by this adware program can also suggest installing some free programs, for example, system optimizers, search tools or software updates, but you have to be careful and stay away from them.
Staying away from unknown files and programs is a key rule that can help you avoid spyware or malware . So it goes without saying that RarGenie removal is essential if you do not want to accidentally click on deceptive or simply untrustworthy ads.
For a precise adware elimination, we highly suggest using anti-malware software compatible with Mac operating system because manual removal typical requires much more time and patience. You might want to try software.
- InstallMac;
- Genieo;
- SearchBenny;
- ZipCloud.
How RarGenie virus got into your browser
From our report of Jul 2017 · not reviewed since
There are several ways to get infected with the described Mac adware.
Remember that Windows users aren't the only ones who can get tricked by software bundling technique - Mac users are targets, too. DieViren.de confirms that this technique deceives many German-speaking computer users, although it can trick any computer user worldwide.
Therefore, we strongly recommend that you check every statement provided in software setup before allowing the installer to make changes to the system. If you notice some suspicious statements about additional programs that will be added to your computer, try to drop the additions via Custom/Advanced installation settings.
If the installer doesn't provide you with an option to configure the components of your download, better do not install such program at all. Try to find a better alternative for it. Besides, it is highly recommended that you check program's reputation in online forums before you decide to add it to your system.
Check your browser and PC
- Address:
dieviren.de
How to remove RarGenie virus
How to remove RarGenie virus from a Mac
Remove the app and what starts it, then check the browsers.
Step 1: Delete apps and downloads you did not intend to install
Open the Applications folder and your Downloads folder. Drag any app you did not install, and any disk image (
.dmg), installer (.pkg) or archive (.zip) that came from RarGenie virus or a site you do not trust, to the Bin, then empty the Bin.Also check
~/Library/Application Supportfor a folder with the same name as the app you removed.Step 2: Remove unknown login items and background items
Open System Settings > General > Login Items & Extensions. Under Open at Login and Allow in the Background, switch off or remove anything you do not recognize, especially items whose developer is shown as an unknown name or that appeared on the day you ran the command.
Then open Finder, choose Go > Go to Folder and check
~/Library/LaunchAgents,/Library/LaunchAgentsand /Library/LaunchDaemons for property list (.plist) files you did not add. Drag suspicious ones to the Bin, then restart the Mac.Step 3: Check the browsers for extensions and changed settings
In Safari open Settings > Extensions and General (homepage). In Chrome open
chrome://extensions, in Firefoxabout:addons.Remove any extension you did not add, and reset the homepage and search engine if they changed. Browsers hold saved passwords and cookies, which is why the password step comes first.
Step 4: Quit what is running that you do not recognize
Open Activity Monitor (in Applications > Utilities, or search for it with Command + Space).
In the CPU or Network tab, look for a process you did not install or whose name is random, select it, click the stop button (the octagon with an X) and choose Quit or Force Quit.
Note the name first: you will look for the same name in the next steps. Malware that comes back after a restart is handled in the next two steps.
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
Reset Chrome browser using the given instructions. If you find any suspicious extensions installed on browser, remove them using the same tutorial.
Delete malicious extensions from Google Chrome:
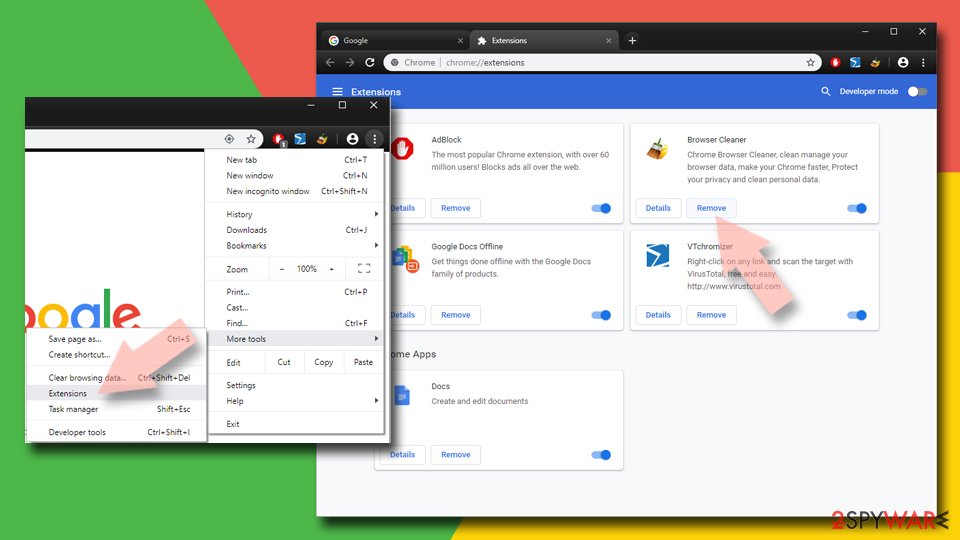
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
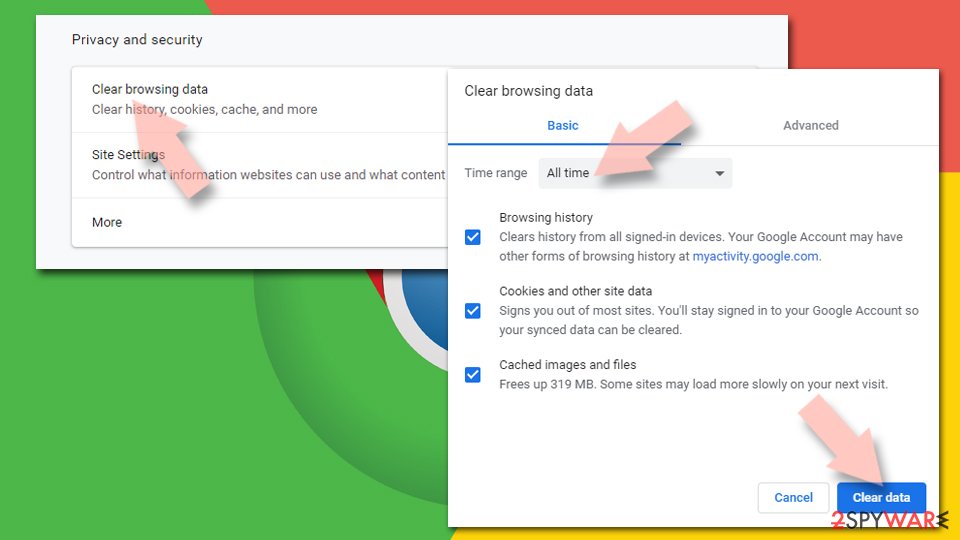
Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
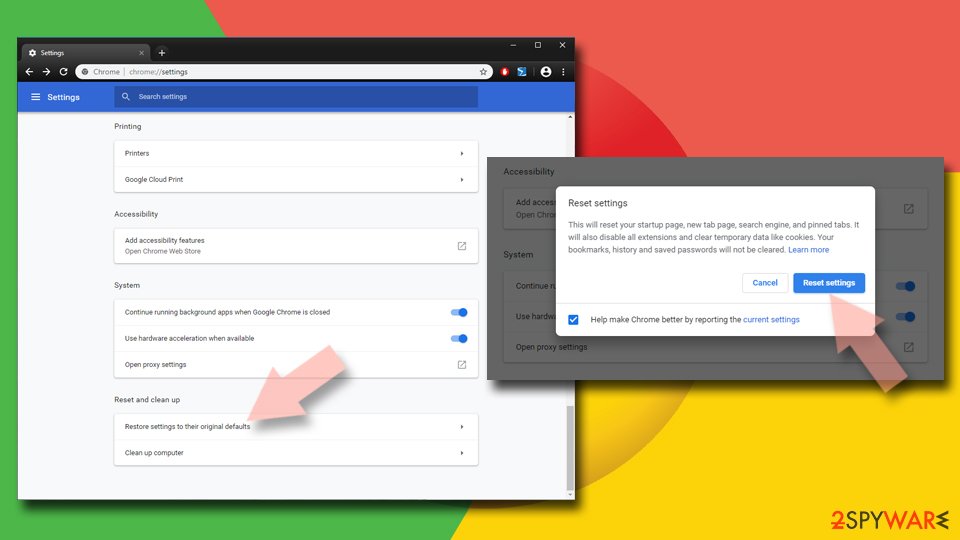
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
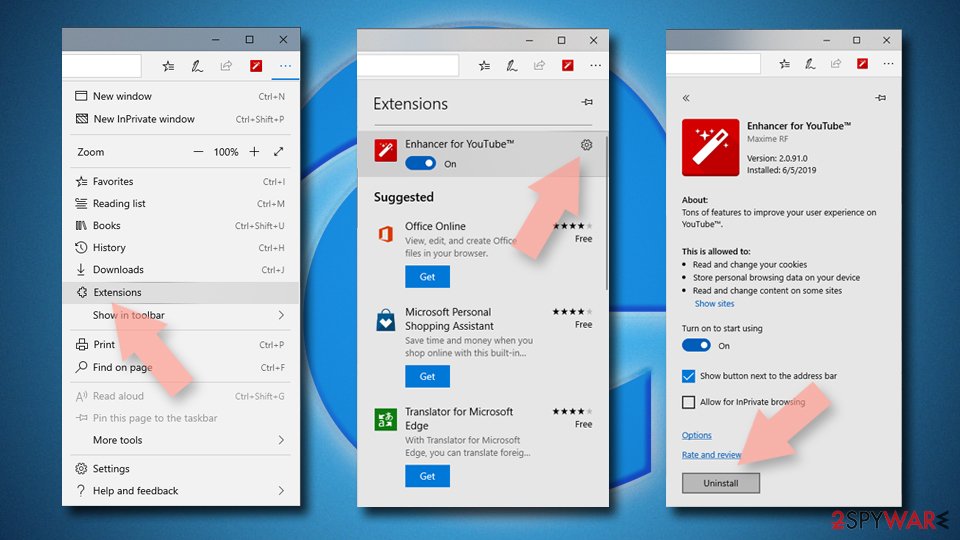
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
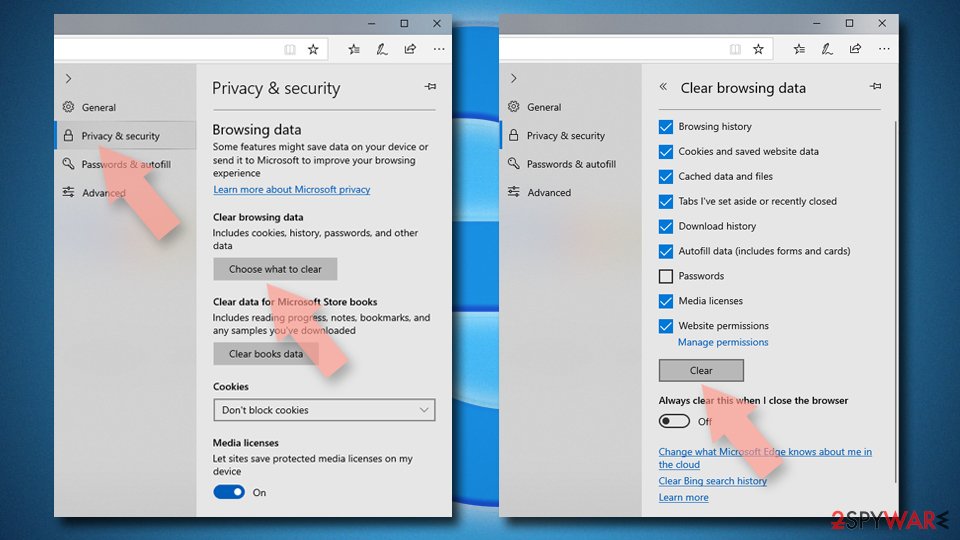
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
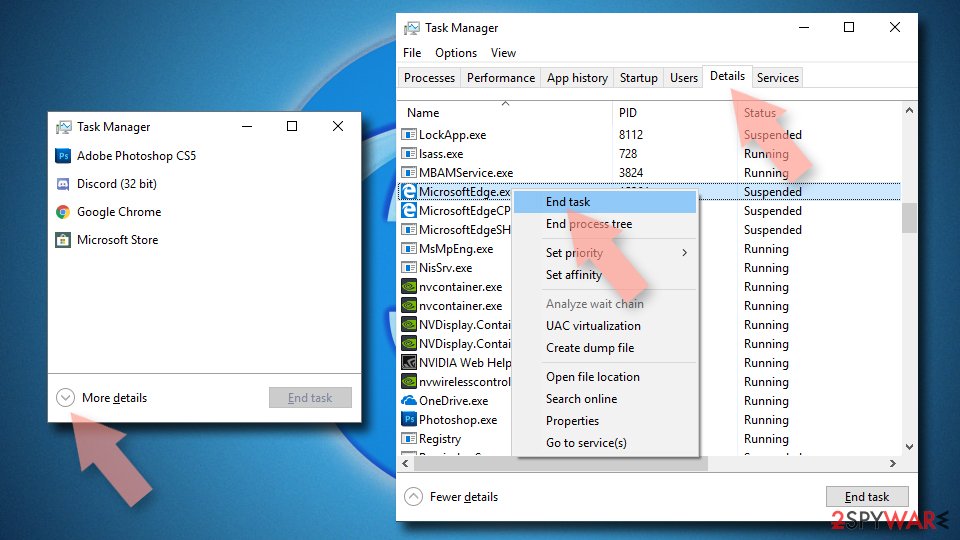
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
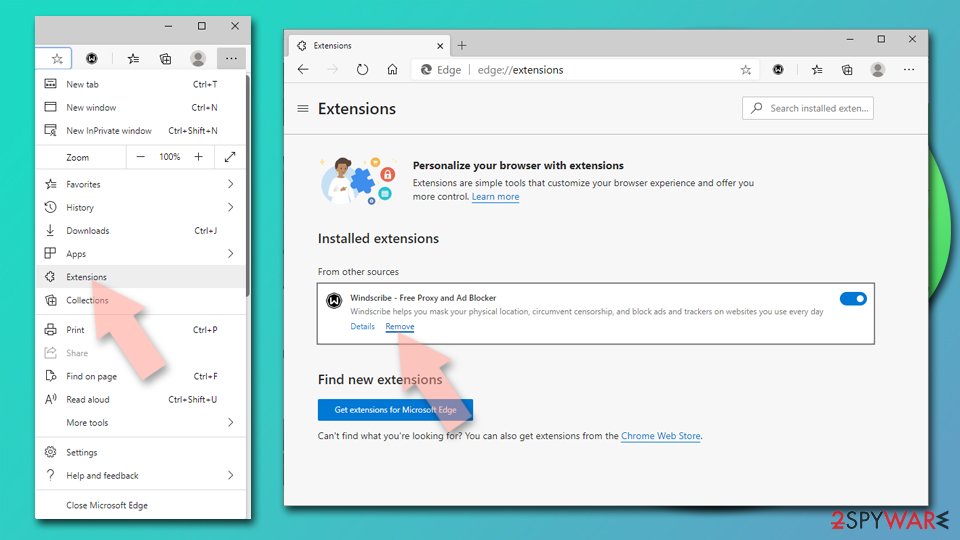
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
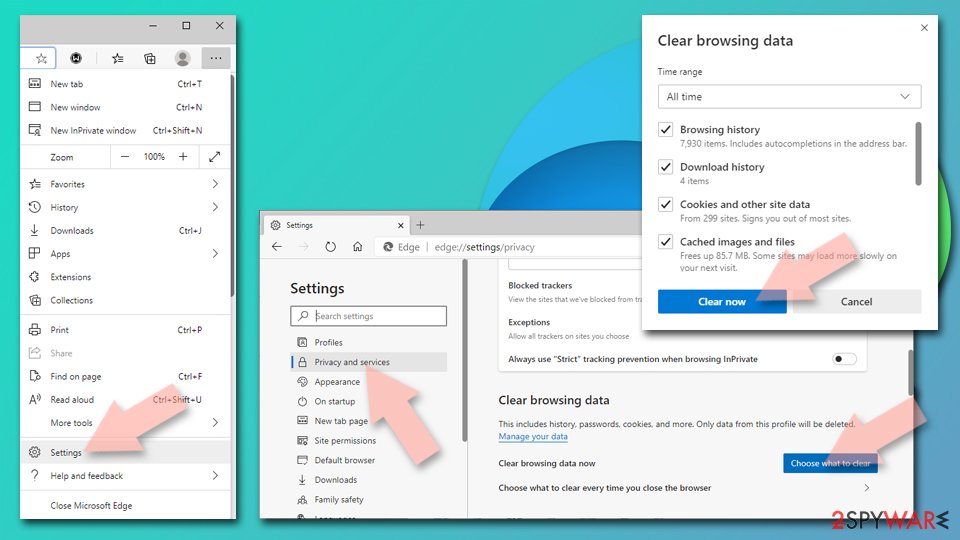
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
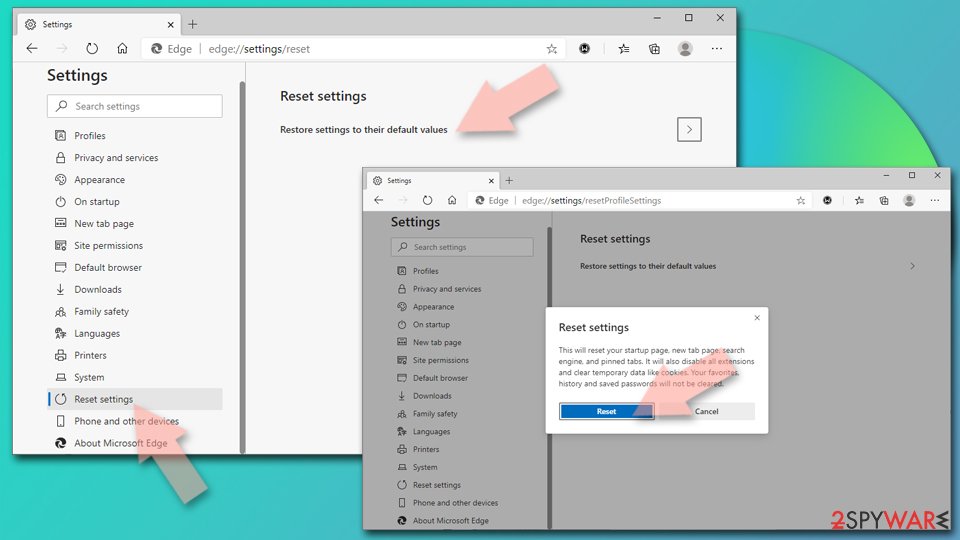
Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
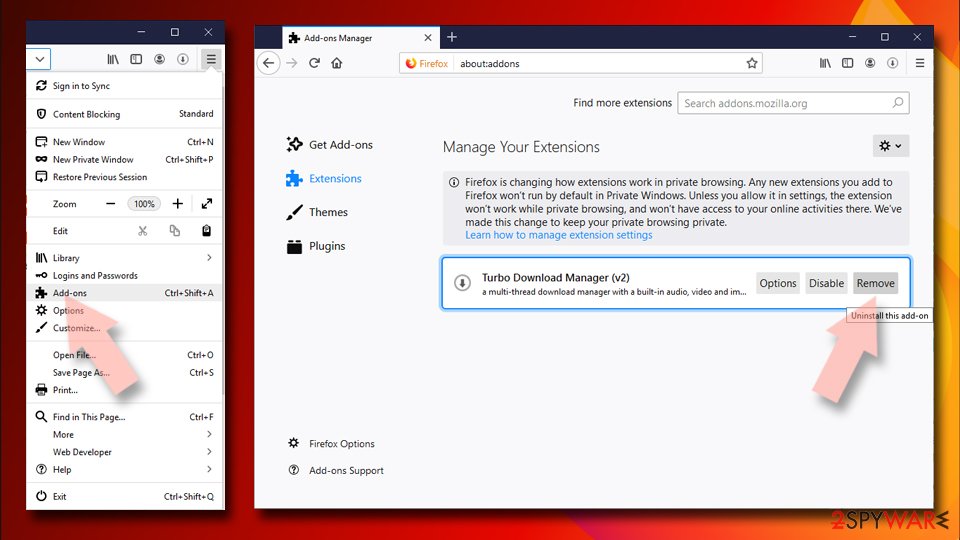
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
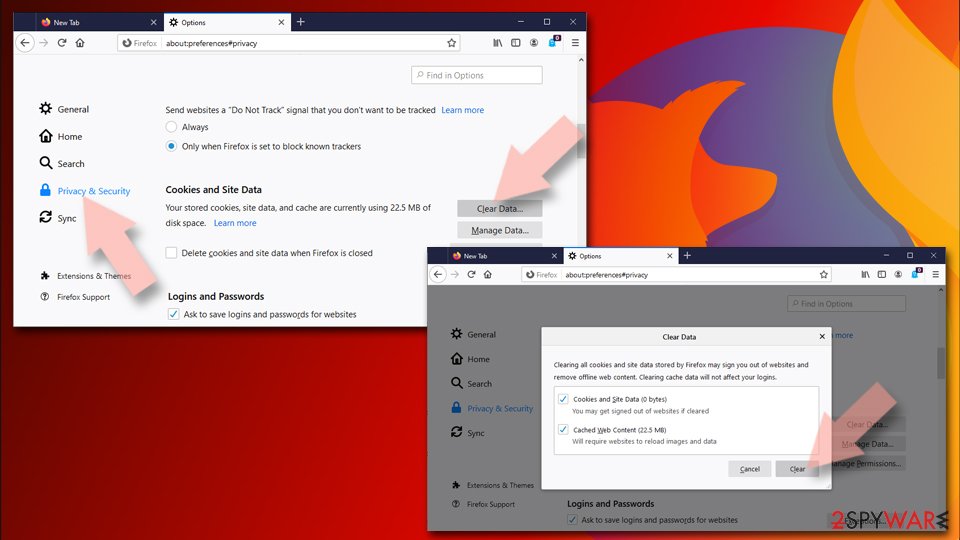
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
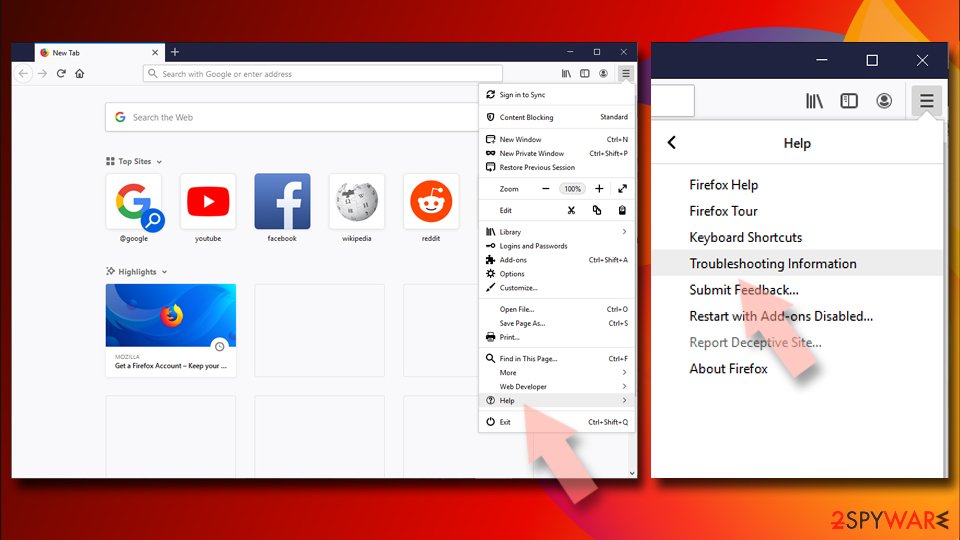
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
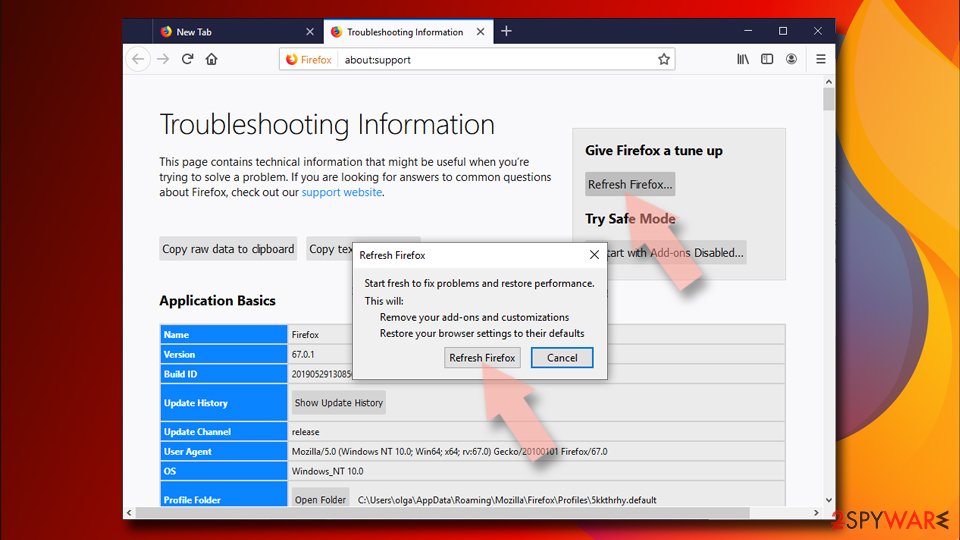
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
To fix Safari browser so that it could no longer redirect you to suspicious sites, follow instructions we provided below.
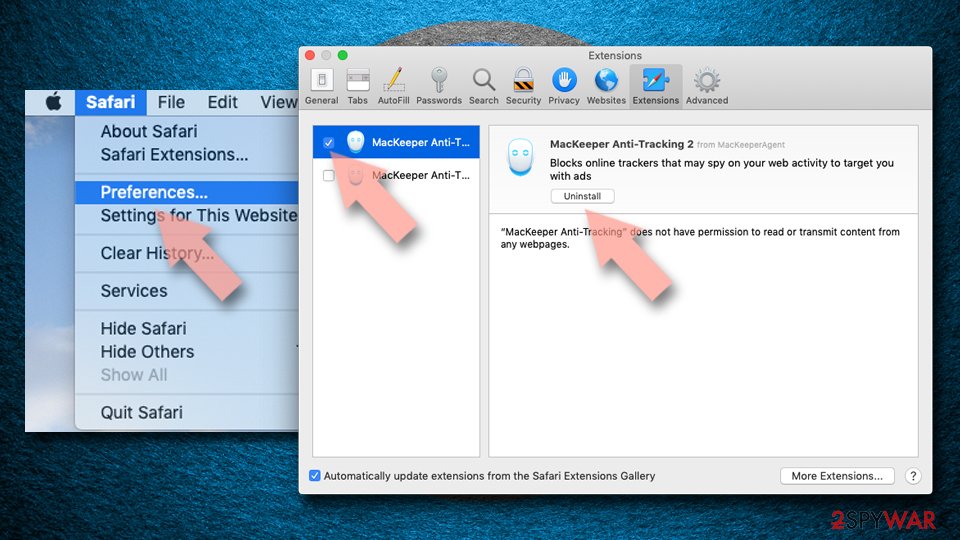
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
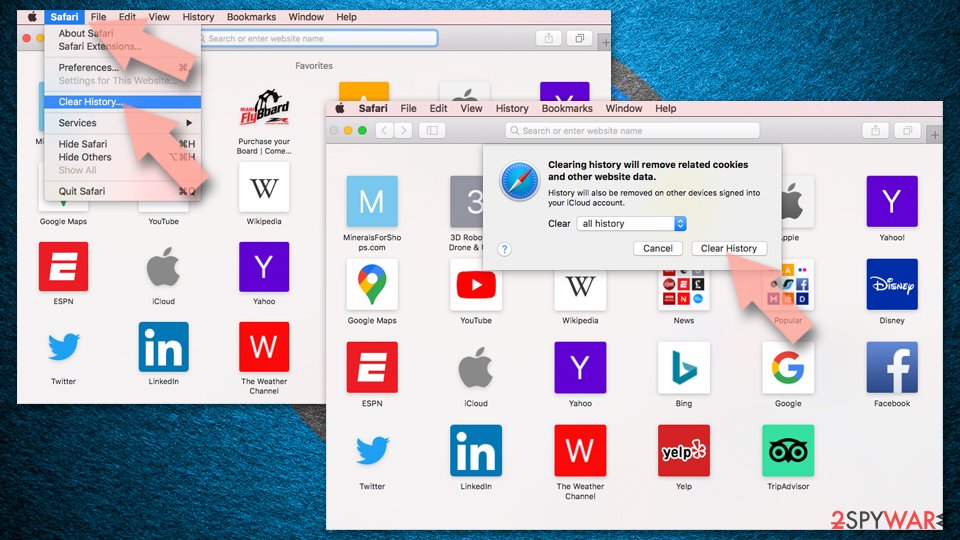
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
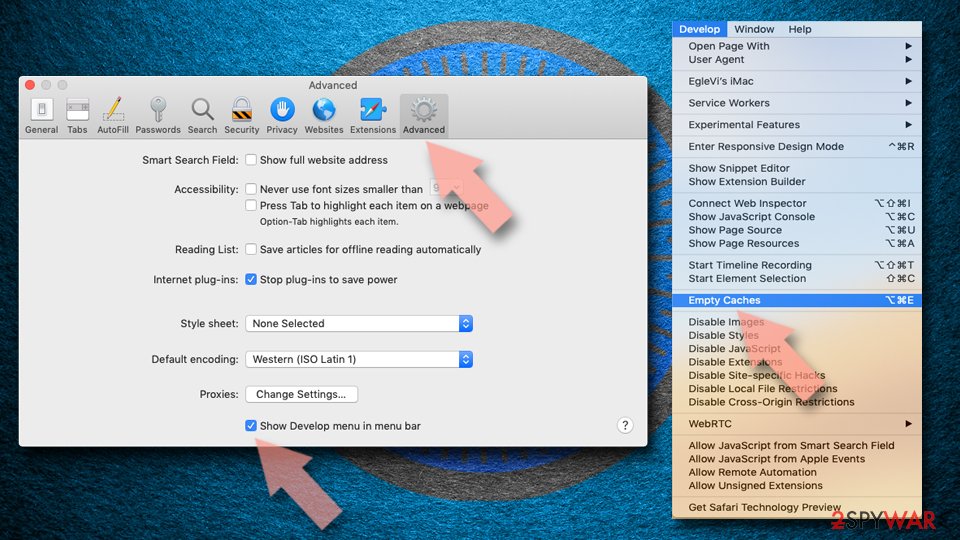
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
RarGenie adware can compromise your Mac computer and initiate unpleasant changes to the operating system, therefore we recommend removing it. These instructions will help you to uninstall the indicated adware as well as other programs such as ZipCloud, SearchBenny, InstallMac and others. 1. First of all, follow instructions with pictures provided below and move all shady Mac apps to Trash. Empty it afterward. 2. Now, wipe associated files from the system. You will need to use Mac's search to find the following folders: /Library/LaunchAgents; /Library/Application Support; ~/Library/LaunchAgents; /Library/LaunchDaemons. 3. Here, delete the following and similar files: installmac.AppRemoval.plist, mykotlerino.ltvbit.plist, kuklorest.update.plist, myppes.download.plist, com.aoudad.net-preferences.plist, com.myppes.net-preferences.plist, com.kuklorest.net-preferences.plist, com.avickUpd.plist.
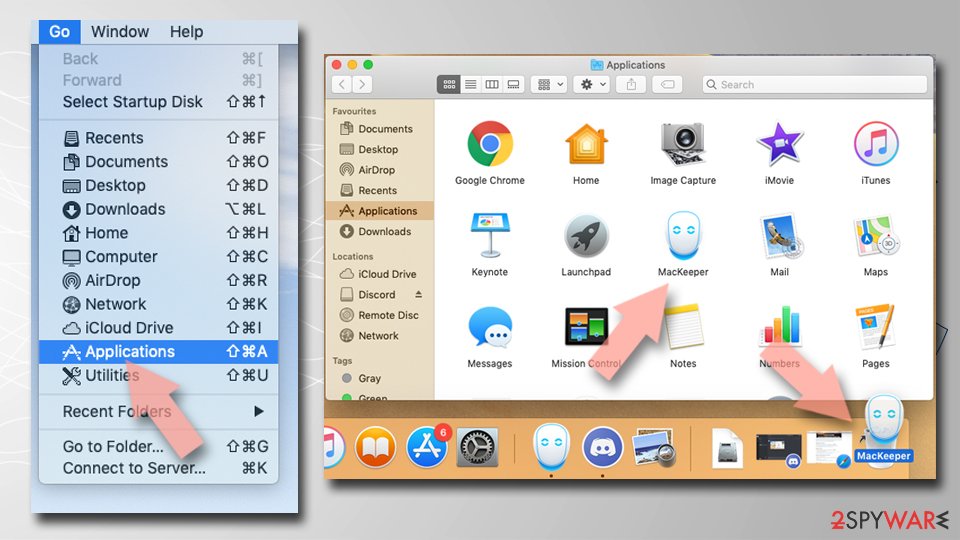
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
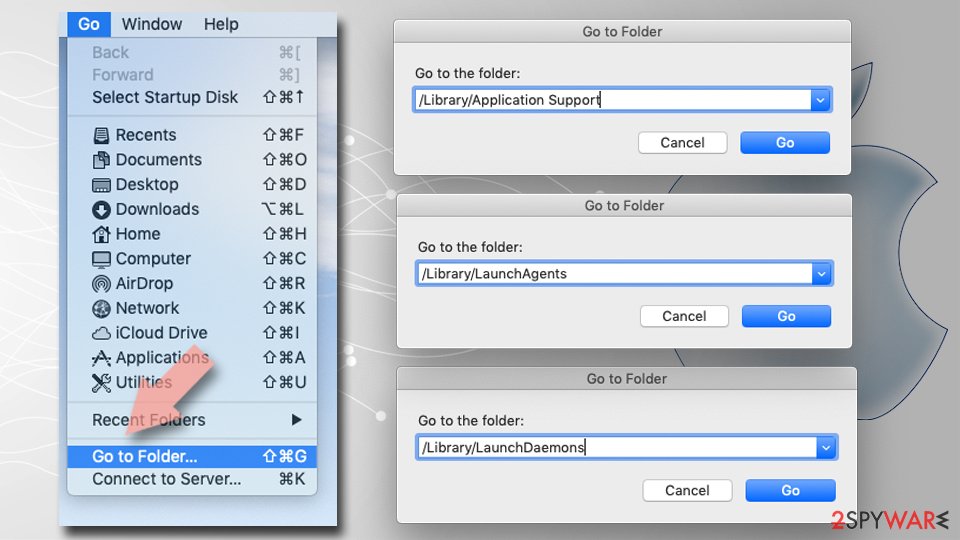
- Finally, empty the Trash to permanently remove the leftovers.
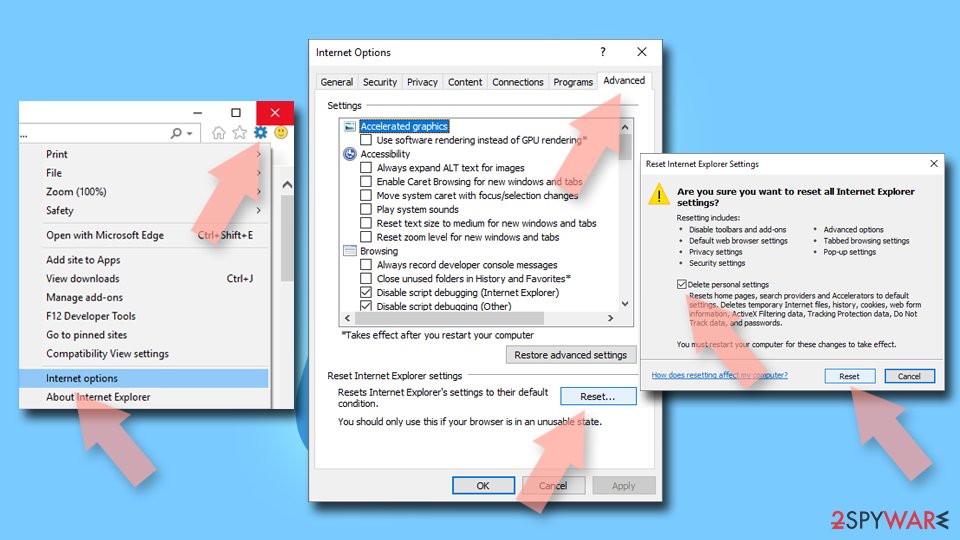
Reset Internet Explorer
Remove dangerous add-ons:
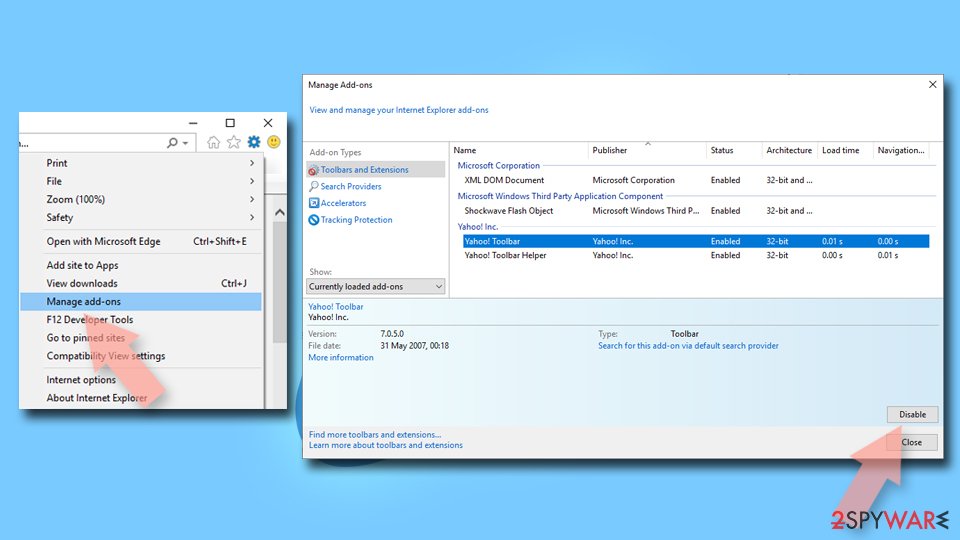
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
Change your homepage if it was altered:
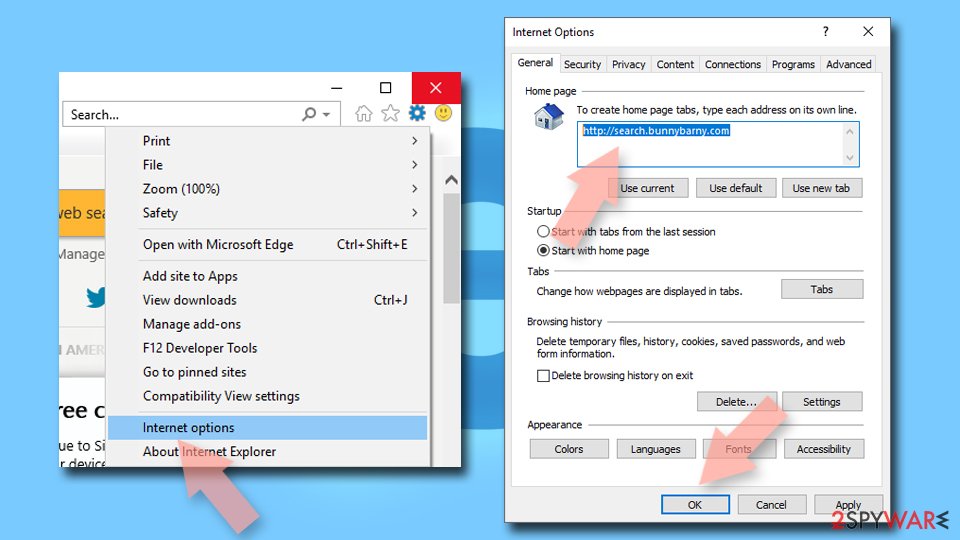
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
Delete temporary files:
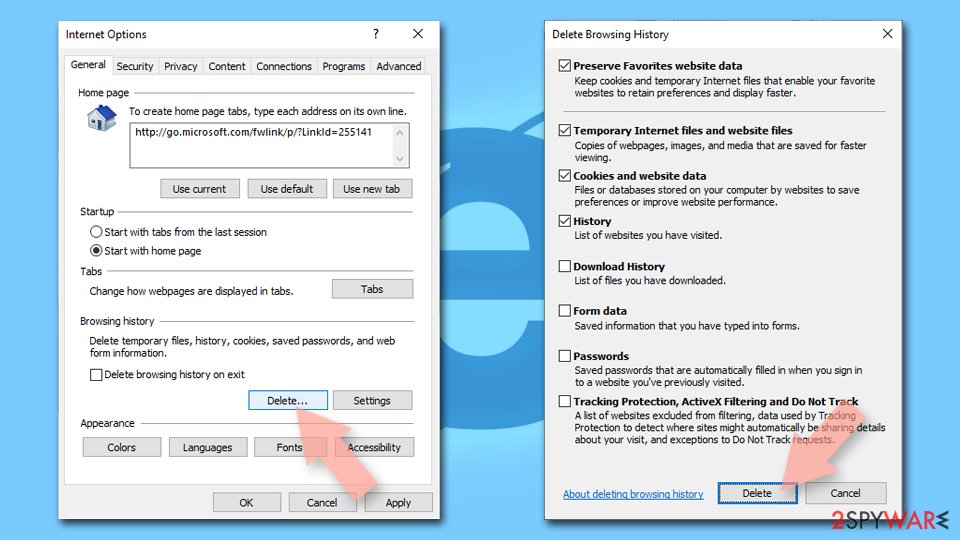
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
From our report of Jul 2017 · not reviewed since
Remove RarGenie from Mac and reset your browsers
To make your Mac work normally again, you will need to remove RarGenie virus along with some other suspicious applications.
We have provided a list of suspicious applications that might be related to the adware in the tutorial that you can find below.
However, if the virus keeps coming back and it seems that it is simply too hard to eliminate it manually, trust or another anti-malware software compatible with Macs. It will complete RarGenie removal quickly and delete all of its components together with ones that belong to other spyware or malware type applications.
ZipCloud, SearchBenny, InstallMac and others.
1. First of all, follow instructions with pictures provided below and move all shady Mac apps to Trash. Empty it afterward.
2. Now, wipe associated files from the system. You will need to use Mac's search to find the following folders:
3. Here, delete the following and similar files:
installmac.AppRemoval.plist, mykotlerino.ltvbit.plist, kuklorest.update.plist, myppes.download.plist, com.aoudad.net-preferences.plist, com.myppes.net-preferences.plist, com.kuklorest.net-preferences.plist, com.avickUpd.plist.
Questions about RarGenie virus
Why does my browser keep going to dieviren.de?
Something is sending it there. On one site only, that site's ads are the cause and leaving the site ends it.
On many different sites, the usual causes are an extension you installed with something else, a site you once allowed to send notifications, or an ad-supported program in Windows that changes how the browser behaves. dieviren.de itself is only a stop on the way: it records the visit and forwards you to whatever advertiser pays most.
Check the extensions page, then the list of sites allowed to send notifications, then Installed apps sorted by date. Removing the cause stops the redirects; blocking the domain alone usually does not, because the network moves to a new one.
Is it safe that my browser was redirected to dieviren.de?
Landing on dieviren.de does not infect the PC by itself. A browser does not run programs from a page without your action. The danger is in the pages that come next:
- some ask you to allow notifications
- some show fake virus warnings
- some offer downloads
- ask for card details
If you only saw those pages and closed them, nothing more is needed than removing whatever caused the redirect. If you allowed notifications, remove that permission.
If you downloaded a file, delete it unopened, or uninstall it if you ran it. If you typed a password or card number on one of the pages, change the password and call your bank.
Why does RarGenie virus show me ads?
Because that is its whole purpose. RarGenie virus is an adware extension, and its operators are paid for every ad it displays and every click it gets. In this case the ads take the form of redirects through ad pages.
They are chosen by ad networks that accept almost any advertiser, which is why so many look like warnings or prizes. The ads are not a sign that your PC is broken or infected with something worse; they are a sign that something on it, or in the browser, has permission to advertise. Removing that permission or program stops them.
Do I have to clean every browser?
Yes, if you use more than one. We saw RarGenie virus in Chrome, Edge and Firefox, and each browser keeps its own extensions, notification permissions and settings. Chrome and Edge share the same extension format, so one installer can add the same adware to both, while Firefox has its own add-ons.
Check every browser on the PC, including ones you rarely open. If you sync a browser with an account, clean it while signed in, so that the removal reaches your other computers rather than the adware returning from them.
How do I know the ads come from RarGenie virus?
Look for redirects to dieviren.de. That is the trace RarGenie virus leaves, and it shows up as redirects through ad pages. Ads that appear on every site, including ones that never carried ads before, point to something on your PC or in the browser rather than to the sites themselves.
A quick test is a private window, where extensions are off by default: if the ads disappear there, an extension is responsible. If they appear even with the browser closed, the source is a notification permission or a program in Windows.
Does adware steal passwords?
Ordinary adware is built to show ads, not to steal logins, and most of it never touches saved passwords. The line is blurry, though. Extensions that can read every page could capture what you type, and adware ads sometimes lead to phishing pages that ask for passwords directly.
If you entered credentials on a page reached through an ad, change that password from a clean device and turn on two-step verification. Otherwise, removing adware extension and clearing cookies is usually enough.
I clicked on one of the ads. Am I infected?
Probably not. Clicking an ad usually only opens a page, and a page cannot install programs on an up-to-date Windows PC without your help.
You are at risk only if you then downloaded and ran a file, allowed notifications, entered card or login details, or called a phone number shown on the page. Delete any download and run a full and offline scan.
Change passwords you typed, from a clean device. Call your bank if you gave card details. If you called a number or allowed remote access, see the next question.
Can adware slow down my PC?
Yes. Adware runs in the background, loads ad scripts, opens extra tabs and contacts its servers, all of which use processor time, memory and bandwidth. Ad-heavy extensions also slow down every page, because they inspect and change it before you see it.
The effect is strongest on older PCs and when several adware programs arrived together. After removal, restart the PC and check Task Manager for anything still using a lot of resources that you do not recognise. Speed usually returns to normal once the ads stop.
An ad showed a phone number and I called it. What now?
The number belongs to scammers, not to Microsoft or an antivirus company. If you only talked, hang up and do not call back. If you let them connect to the PC, disconnect it from the internet, uninstall the remote access program they used, such as AnyDesk, TeamViewer, ScreenConnect or UltraViewer, and run a full and offline scan.
If you paid or gave bank details, call your bank at once on the number printed on your card. Change any passwords you typed while they were connected, and report the call.
Will Fortect remove RarGenie virus?
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds on your Mac before you decide anything.
For RarGenie virus, follow the plan on this page as well: removing a launch item or an app is done in macOS itself, and a scanner cannot undo what was typed or entered on the infected Mac, such as saved passwords that were copied.
Change your passwords from another device first, and if the page tells you to erase the Mac, a scan is not a substitute. The free scan costs nothing and the full-featured product needs a license.
Sources
- DieViren: DieViren (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)
- Microsoft Learn: How Microsoft names malware (read October 6, 2026)