
BloodyStealer and Stolen Game Accounts in 2026
- BloodyStealer and game account theft in 2026: the short answer
- Timeline: from BloodyStealer to malware in Steam games
- What changed since 2021
- Risks for gamers in 2026 (our analysis)
- Six steps to protect your gaming accounts
- What is still unknown
- Our original 2021 report
- Information gathering and exfiltration functionalities
- Data-stealers continue globe-trotting
- Related guides on 2-Spyware
BloodyStealer and game account theft in 2026: the short answer
BloodyStealer was a 2021 trojan that stole logins for Steam, Epic Games Store, EA Origin and other gaming platforms, and the accounts it took were sold on dark web markets.[2][3] We found no new public research on BloodyStealer itself after 2021. The threat it stood for is still active in 2026.
Two things are different today. EA retired the Origin app on April 17, 2025, so EA accounts now live in the EA app.[6][7] And malware has moved into game stores themselves: the FBI is seeking victims of Steam games embedded with malware that it says targeted users between May 2024 and January 2026.[8]
| Question | Answer |
|---|---|
| What BloodyStealer targeted | Steam, Epic Games Store, EA Origin and other gaming accounts[2] |
| Price in 2021 | About 10 dollars a month or 40 dollars for life[3] |
| Other stolen data | Cookies, passwords, card details, screenshots[3] |
| Origin client status | Retired on April 17, 2025, replaced by the EA app[6] |
| Steam malware games | Seven titles named in an FBI victim request[8] |
| Is buying accounts safe | No, many come from stealer infections[3] |
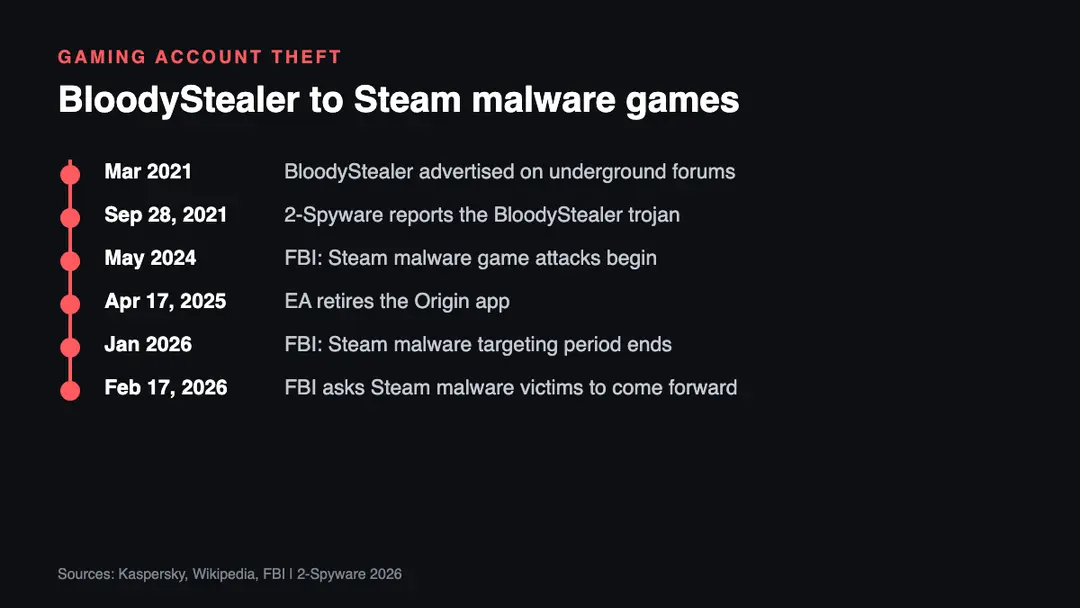
Timeline: from BloodyStealer to malware in Steam games
| Date | Event |
|---|---|
| March 2021 | BloodyStealer first seen in ads on Russian-speaking forums[3] |
| September 28, 2021 | 2-Spyware publishes its report |
| May 2024 to January 2026 | Period in which, per the FBI, a threat actor targeted users with Steam malware games[8] |
| April 17, 2025 | EA retires the Origin app[6] |
| February 17, 2026 | FBI publishes its request for Steam malware victims[8] |
What changed since 2021
Origin is gone. Wikipedia records that the Origin app was retired on April 17, 2025, and EA confirms that the EA app has replaced Origin on PC and Mac.[6][7] Anyone searching for "Origin accounts for sale" today is looking at EA accounts, which are just as attractive to thieves.
The delivery has also changed. In 2021, BloodyStealer mostly came with other threats, fake game downloads and links on social media.[3] By 2024 and 2026, malware was reaching players through games listed on Steam itself. The FBI's Seattle Division named BlockBlasters, Chemia, Dashverse/DashFPS, Lampy, Lunara, PirateFi and Tokenova.[8] Bitdefender reported that Valve removed a free horror game, Beyond The Dark, after players found infostealer malware in it.[9]
The market for stolen game accounts has not gone away. The Kaspersky research on BloodyStealer showed accounts with many games and items sold at big discounts.[3] We found no source showing that this trade has shrunk.
Risks for gamers in 2026 (our analysis)
This list is our own analysis based on the cases described above.
- Malware inside store games. Small, free or early access titles that ship a stealer in an update.[8][9]
- Account sales. Cheap Origin, EA, Steam or Epic accounts that the original owner can reclaim, often stolen by stealers.[3]
- Fake cheats, mods and cracks. Downloads that promise free items but install a stealer.
- Direct invitations. The FBI asks victims whether someone told them to download a game, which points to targeted lures over chat apps.[8]
- Session cookie theft. Stolen cookies can let a thief into an account without the password.[3]
Six steps to protect your gaming accounts
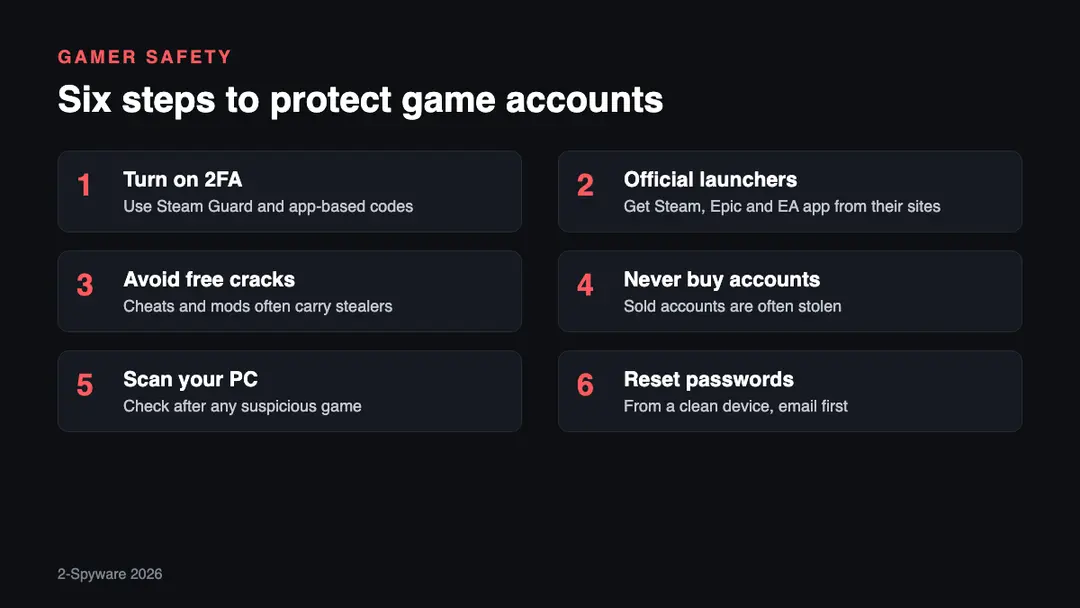
1. Turn on two-factor sign-in. Use the strongest login protection each platform offers, so a stolen password alone does not open your account.
2. Use official launchers. Download Steam, the Epic Games Launcher and the EA app only from their official websites.[7]
3. Avoid free cracks and cheats. Downloads that promise free games, items or cheats are a classic way to spread stealers.[3]
4. Never buy accounts. A cheap account for sale is often a stolen one. The original owner can recover it, and your money is lost.
5. Scan your PC. If you installed one of the games named by the FBI or any game later pulled for malware, run a full scan.[8][9] Our malware removal guides can help.
6. Reset passwords. From a clean device, change your email password first, then game, browser and banking passwords. Check your email with our leak check.
What is still unknown
- Whether BloodyStealer is still sold or was replaced by newer stealers. We found no post-2021 research on it.
- Who is behind the Steam malware games in the FBI case. The FBI has not named a suspect on its victim page.[8]
- How many EA, Steam and Epic accounts are stolen each year. We found no current public figure.
Our original 2021 report
The text below is our report as first published in 2021. We keep it unchanged for the record; the sections above bring it up to date.
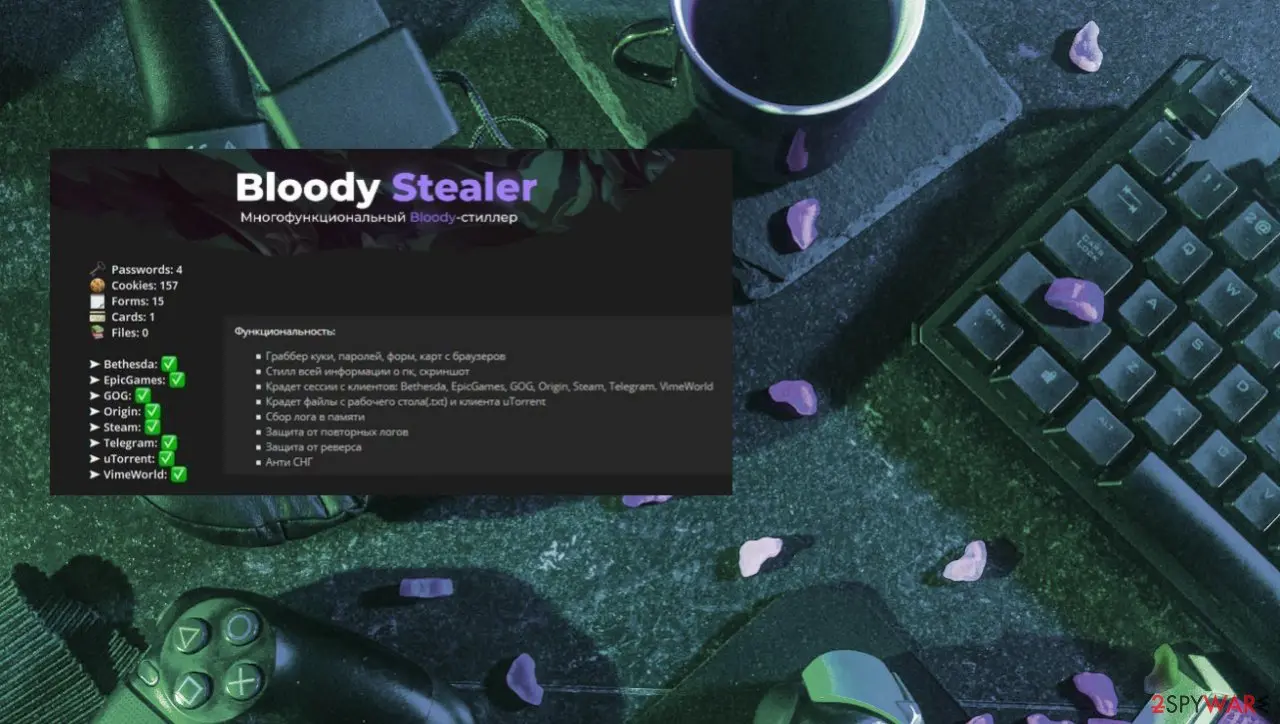
The new advanced trojan targets accounts of various gaming platforms since these details are valuable and in demand in various underground markets. BloodyStealer trojan analysis revealed the malware is stealing account details of gaming platforms like Steam, Epic Games Store, EA Origin, VimeWorld, and more.[1] Detection evading, low price and other trojan capabilities made the piece attractive when particular advertisements were posted online.[2]
The Kaspersky research team report[3] shows all the functions of the piece and lists what data got stolen, sold on the dark web. These game-related products and gaming accounts are in demand, and the research report also illustrates that. Julia Glazova states in her statement:
Unsurprisingly, accounts with many games, add-ons, and expensive items hold particular value. Typically cybercriminals sell them at huge discounts.
The trojan was first detected in March due to the active advertising campaigns in Russian-speaking underground forums. At the time, the trojan was offered for 700 RUB a month (equivalent to $10). The lifetime subscription for the malicious tool then was on sale for $40. Attacks started, and research shows that BloodyStealer was detected in attacks across Europe, Latin America, and Asia-Pacific regions.
Information gathering and exfiltration functionalities
Information obtained from those popular gaming applications got obtained via a remote server. Gathered data can be easily monetized using darknet platforms and channels on programs like Telegram created for criminals to purchase access to online accounts like this. Trojan-stealer manager to access and steal various details:
- cookies;
- passwords;
- forms;
- banking card details from browsers directly;
- screenshots;
- login information;
- uTorrent files;
- logs;
- device data;
- session details related to other applications.
The creation of the infection ensures difficulty to reverse-engineer[4] the malware piece. The piece stands out in these underground forums with its functions helping to evade antivirus detection. It is not particularly indicated how the trojan was delivered, but many attackers distributed this Bloodystealer with other threats. However, the most common method includes scams, including game downloads, links on social media with redirects to rogue sites, and triggering the download of this virus.
Data-stealers continue globe-trotting
When the obtained data gets sent to a C&C server[5] protected against other attacks like DDoS and web campaigns, cybercriminals control the stolen details and ensure the later use for the information. There are tons of different data stealers that have been on the market. Underground forums often have such advertisements for tools that have pushing functions and other information-gathering-related functions. Monetization is the primary purpose of these campaigns, as with any other cyber threat campaign and attack.
Login information to accounts like this can be exceptionally valuable. Archives with tens of thousands of records linked with people in the US or Europe can be put up for $100-$200 for the whole archive. Such data typically goes for 20 – 50 cents per piece. Hackers who know what they are doing can speculate that the library contains old, useless information. Often, sellers allow buyers to check these logs to confirm that information is available before purchasing.
Unfortunately, anyone can fall victim to such malware and stealer campaigns. You need to consider all the risks and make sure to keep your accounts secure as well as your information on the machine. Strong passwords, tho-factor-authentication can help. Also, be cautious about the risk behind links in emails, social media messages from strangers, double-check if the site is legitimate when you put any of your credentials. Use proper security solutions and anti-malware to avoid significant virus attacks.
Related guides on 2-Spyware
Frequently asked questions
What is BloodyStealer?
BloodyStealer is a trojan that steals data from gaming platforms such as Steam, Epic Games Store and EA Origin, along with browser passwords, cookies and card details.{2}{3} Kaspersky researchers described it in 2021, when it was advertised on Russian-speaking forums for about 10 dollars a month or 40 dollars for a lifetime licence.{3}
Are Origin accounts for sale safe to buy?
No. Many game accounts offered for sale come from infections with stealers like BloodyStealer, and the original owner can recover the account at any time.{3} Buying one also funds the theft. Origin itself was retired on April 17, 2025, and EA accounts now run through the EA app.{6}{7} Buy games only from official stores.
Is Epic Games Store spyware?
We found no evidence in our sources that the Epic Games Store client itself is spyware. The risk comes from malware such as BloodyStealer that targets Epic accounts stored on an infected computer.{2} Install the launcher only from the official Epic website and keep your account protected with two-factor sign-in.
Is the EA app spyware?
We found no source that calls the EA app spyware. It is EA's official PC client and replaced Origin on PC and Mac.{7} Like Origin before it, the EA app account can be a target for stealer malware on an infected computer. The safe route is to download it only from ea.com and turn on extra login protection.
Can Steam games contain malware?
Yes, it has happened. The FBI is seeking victims who installed Steam games with embedded malware, naming BlockBlasters, Chemia, Dashverse/DashFPS, Lampy, Lunara, PirateFi and Tokenova.{8} Valve also removed a free game called Beyond The Dark after reports that it carried an infostealer.{9} If you installed one of them, scan your PC and change your passwords.
What should I do if my game account was stolen?
Act from a clean device. Use the platform's official account recovery, change the password, and turn on two-factor sign-in. Then scan the infected PC, because stealers also take browser passwords and cookies.{3} Change passwords for email and banking too, and watch your card statements for unknown charges.
Sources
- Kotaku. Breaking news and reports (no longer online)
- Bleepingcomputer. IT and security news
- Kaspersky. Cybersecurity reports
- Networkworld. Network expertise
- Trendmicro. Security solutions
- Wikipedia
- Electronic Arts
- FBI
- Bitdefender
Log in to comment
No comments yet. Be the first.