Exploited now
9 this week
Data breaches
Gîtes de France
Is it safe?
check a site
Browser updates
Chrome 155.0.8059.85
Scam emails
examples
12,318
guides
5,616
members
Removal guides
Pop-ups & adware
Browser hijackers
Ransomware
Trojans & backdoors
Spyware & keyloggers
Rogue anti-spyware
Malware
Unwanted programs
Scams
Scam alerts
Fake alerts
News
Malware news
Data breaches
Human cost
Exploited flaws
Browser security
Security
Browsers & vulnerabilities
General
Software
Files
System files
Spyware-related files
Log in
Exploited now
9 this week
Data breaches
Gîtes de France
Is it safe?
check a site
Browser updates
Chrome 155.0.8059.85
Scam emails
examples
Now
18 Oct
genovaw.com: a Mac stealer download site (AMOS, MacSync, ClickFix) and what to do if you pasted its command
18 Oct
viewgit.sbs: a server listed for a PowerShell script tagged RedHiveStealer, and what to do if you ran a command from it
18 Oct
gitview.sbs: a server handing out a PowerShell script, a 7-Zip tool and a locked zip tagged RedHiveStealer, and what to do on Windows
18 Oct
gitsl.xyz: a server listed for a PowerShell script tagged RedHiveStealer, and what to do if you ran its command on Windows
18 Oct
gitrm.sbs: a server handing out PowerShell scripts and files tagged RedHiveStealer, and what to do if a PC ran them
18 Oct
massgravel.net: a look-alike of the Windows activation tool site, reported for PowerShell malware, and what to do if you ran its command
18 Oct
nvwgf2umx.dll: NVIDIA's DirectX driver file, or a copy that does not belong?
18 Oct
opencl.dll: genuine Windows or driver file, or a copy that a program loads instead?
5,616 members
· read and write here
All members
Rubric
News
Page
@news
· 2 followers
Reporting on attacks, breaches and security fixes.
Malware news
Data breaches
Human cost
Exploited flaws
Browser security
Security
Browsers & vulnerabilities
General
Anti-spyware software
Spam and phishing
Spyware related issues
Tutorials
Vulnerabilities
Web browsers
What's new
Everything
Posts 61
Human cost
Webcam blackmail: the real cases behind "Shut Up and Dance"
Court records and police reports show how remote-access trojans turn on cameras, how blackmail follows, and how to check your PC and phone.
Lucas Reed ·
Oct 16, 2026
Human cost
Ransomware's human toll: hospital patients and owners who broke down
What ransomware has done to hospital patients, nurses and small business owners, what is proven and what is only alleged, and where people can get help.
Emily Carter ·
Oct 16, 2026
Human cost
Leaked secrets as a weapon: Ashley Madison, a clinic, Medibank
When intimate or medical data leaks, criminals write to the people in the files. Three documented cases, the harm, and what to do if it happens to you.
Nathan Cole ·
Oct 16, 2026
Human cost
Financial sextortion: the boys lost within hours, and what stops it
Scammers posing as girls push teenage boys to pay within hours. What the cases show, why shame keeps boys silent, and what to do in the first hour.
Emily Carter ·
Oct 16, 2026
Human cost
Vastaamo: when hackers stole therapy notes and blackmailed patients
In 2020 hackers stole the therapy records of about 33,000 people in Finland and blackmailed patients directly. What happened, what it did to them, and what helps.
Nathan Cole ·
Oct 16, 2026
Spam and phishing
Google Calendar Phishing Scam 2026: Fake Meeting Invites
2-Spyware Editorial Team ·
Oct 12, 2026
Data breaches
Cash App and AT&T Settlement Payments 2026
2-Spyware Editorial Team ·
Oct 12, 2026
Data breaches
ASOS Data Breach 2026: H&M Probe and What To Do
2-Spyware Editorial Team ·
Oct 12, 2026
Browsers & vulnerabilities
Facebook Messenger Malware Flaw: 2026 Status and Safety
Gabriel E. Hall ·
Oct 10, 2026
Browser security
3 h ago
gHacks reports that Microsoft is testing a seamless update system for Edge that would apply updates in the background without a restart prompt. The company says the goal is to close the patch gap and that Edge already has options to update when the device is idle or to alert administrators when a release includes fixes, including zero-day vulnerabilities. Windows users should keep Edge set to update and restart when prompted, or let it update while idle.
Exploited flaws
7 h ago
SecurityWeek reports that attackers exploited multiple Fortinet flaws in an attack on a telecommunications organization, including a FortiManager bug patched in October 2024 and a path traversal flaw in FortiOS, FortiPAM, FortiProxy and FortiSwitchManager. CISA has added the path traversal issue to its Known Exploited Vulnerabilities list and urged immediate patching. Home and small-office users running Fortinet products should install the latest updates as soon as possible.
Data breaches
8 h ago
Infosecurity Magazine reports that ConnectWise suspended several cloud services after finding unauthorized access to application identities in its ConnectWise Cloud Backup environment. The company says the access could let an attacker reach customers’ Microsoft 365 data, including mailboxes, OneDrive, SharePoint, Teams and directory information. ConnectWise advises customers to keep affected apps disabled, preserve sign-in and audit records, and review authentication, credentials, roles, consent grants, mailbox forwarding rules and other suspicious changes.
Malware news
8 h ago
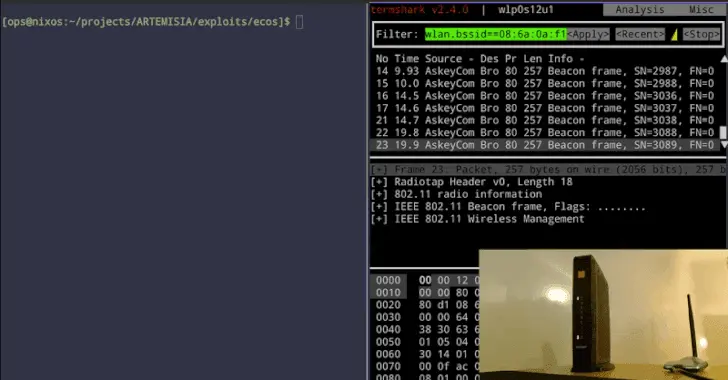
The Hacker News reports that a flaw in Broadcom’s Wi‑Fi setup software lets an attacker within radio range run code as root on Broadcom-based routers, without the network password or any pairing step. It was shown on home gateways from three Belgian internet providers, and no fix has been deployed to the affected routers. Windows users should check their router model and firmware status, and replace or isolate affected gear if no patch is available.
Security
Exploit as a Service and Buying Zero-Days in 2026
Exploit-as-a-service and zero-day buying in 2026: a broker was sanctioned, 90 zero-days were exploited in 2025, and what to do now.
Jake Doevan ·
Oct 10, 2026
News
Government Spying in 2026: How to Protect Yourself
Government spying in 2026: Section 702 lapsed in June, yet collection can run to March 2027. What it means for you, plus six steps to protect yourself.
Gabriel E. Hall ·
Oct 10, 2026
Security
Development Bank of Seychelles Ransomware: 2026 Update
Development Bank of Seychelles ransomware in 2026: the September 2020 timeline, what the bank said, what is still unknown and lessons for readers.
2-Spyware Editorial Team ·
Oct 10, 2026
Security
Brno Hospital Cyberattack: What Happened and 2026 Status
The Brno hospital cyberattack of March 2020 was ransomware that shut down the IT network. Here is what happened next, who was blamed and what it means now.
2-Spyware Editorial Team ·
Oct 10, 2026
Security
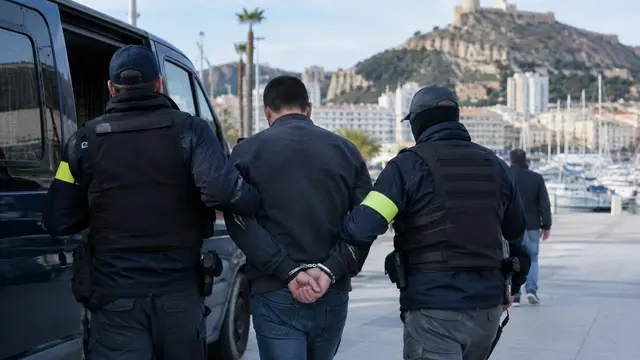
Carbanak Leader Arrested in Spain: 2026 Update
The Carbanak and Cobalt leader was arrested in Alicante in 2018. We found no public trial result for him, but other gang members were jailed.
Linas Kiguolis ·
Oct 10, 2026
TYPE
Security
FILED
Oct 10, 2026
Security
Log4j Zero-
Day in 2026: What Happened and Is It Fixed
Security
Log4j Zero-Day in 2026: What Happened and Is It Fixed
2-Spyware Editorial Team ·
Oct 10, 2026
Security
Japanese Computer Virus Plan in 2026: What Happened
Gabriel E. Hall ·
Oct 10, 2026
Malware news
Maastricht University Ransomware Attack: 2026 Update
Gabriel E. Hall ·
Oct 10, 2026
Security
Protect Your Phone From Hackers in 2026: What Works
Lucia Danes ·
Oct 10, 2026
Data breaches
1 d ago
The Record reports that Russian authorities detained three suspected DataSuckers hackers after a cyberattack on Dodo Pizza exposed customer information. The breach reportedly involved names, addresses, phone numbers, email addresses, dates of birth, order details and stored passwords. People affected should change any reused passwords and watch their accounts for suspicious activity.
Malware news
1 d ago
The Hacker News reports that UAT-11985 used fake event invites and malicious QR codes to target people affiliated with Taiwan research organizations. The phishing pages copied Google login screens to steal Google account credentials and MFA codes, so Windows users should be careful with event invitations, avoid scanning unknown QR codes, and check the sender and sign-in page before entering any login details.
Exploited flaws
1 d ago
The Hacker News reports that attackers are abusing a compromised ConnectWise Cloud Backup credential to sign in to Microsoft 365 tenants. ConnectWise has shut off Cloud Backup access while it investigates and says there is no evidence the backup data was compromised. Windows users and small offices using the service should check for the vendor’s guidance, review Microsoft Entra sign-in logs, and watch for unusual access to mail, OneDrive, SharePoint and Teams.
Malware news
2 d ago
The Hacker News reports that a malicious npm package called imgdecode is part of the MALFEX campaign targeting Windows systems. The package hides a loader in a Windows native addon and can download encrypted shellcode from GitHub, then inject it into a new dllhost.exe process. Windows users should avoid untrusted npm packages and check what software they install from developer tools and command lines.
News
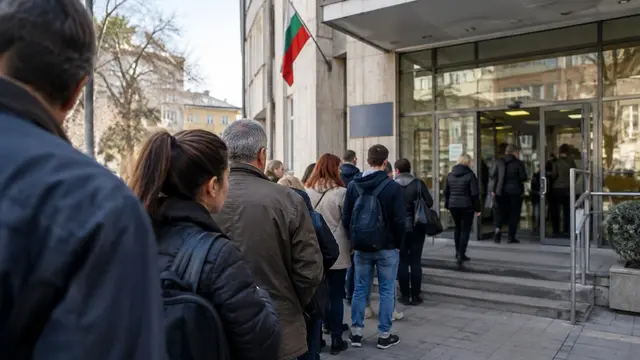
Bulgaria Tax Agency Data Leak: 2026 Facts and Status
The July 2019 hack of Bulgaria's tax agency exposed data on about 5 million people. What was taken, who was charged, what is unknown in 2026 and what to do.
Jake Doevan ·
Oct 7, 2026
Malware news
Flappy Birr Dog Spyware in 2026: MobSTSPY Facts
Flappy Birr Dog was a Google Play game with MobSTSPY spyware. Google has removed it. Here is what it stole, which apps carried it and how to check your phone.
2-Spyware Editorial Team ·
Oct 7, 2026
TYPE
Malware news
FILED
Oct 7, 2026
Malware news
Clop MOVEit Breach 2026: Siemens Energy and Victims
Malware news
Clop MOVEit Breach 2026: Siemens Energy and Victims
Clop's MOVEit attack hit Siemens Energy and over 600 organizations. CVE-2023-34362, the timeline, what changed and how to protect file transfer tools.
Gabriel E. Hall ·
Oct 7, 2026
Malware news
Is the TikTok Pro App Safe in 2026? No, It Is Spyware
The TikTok Pro app is not safe: it is Android spyware that steals SMS, photos, location and Facebook logins. There is no real TikTok Pro. How to remove it.
Julie Splinters ·
Oct 7, 2026
TYPE
Security
FILED
Oct 7, 2026
Security
Nissan Data Breach 2026: Settlement and New Notices
Security
Nissan Data Breach 2026: Settlement and New Notices
Nissan North America's 2023 breach reached a $1.5 million settlement in 2026, and new notices followed in June. Dates, deadlines and steps to take.
2-Spyware Editorial Team ·
Oct 7, 2026
Security
Facebook Privacy Scandal 2026: Fines and Settlements
Jake Doevan ·
Oct 7, 2026
Anti-spyware software
CCleaner and Avast Bundle: 2026 Update
Julie Splinters ·
Oct 7, 2026
News
UNNAMED1989 WeChat Ransomware: 2026 Facts and Tencent Strings
Gabriel E. Hall ·
Oct 7, 2026
Security
Fxmsp Antivirus Breach 2026: Charges and Lessons
Lucia Danes ·
Oct 7, 2026
Browser security
2 d ago
Microsoft says the October KB5127648 security update for Windows 11 can stop some users from turning on Smart App Control. On affected devices, the option is grayed out in Windows Security. Microsoft has published temporary registry and Group Policy workarounds, but no permanent fix yet. Users who want this protection should check whether Smart App Control is already on and apply the workaround if needed.
Data breaches
2 d ago
The Record reports that Anne Arundel County, Maryland, confirmed hackers stole files from government systems during an incident in August. Officials said they found irregular activity on August 28 and later determined an unauthorized actor copied certain files from a limited number of systems. Residents should watch for any breach notices and monitor accounts and records if they get one.
Exploited flaws
3 d ago
The Hacker News reports that attackers tampered with AOMEI Backupper’s update servers for short periods between May and July 2026, so some Windows copies that checked for updates during those windows downloaded and ran a backdoor. AOMEI says it fixed its servers, but that does not remove the backdoor from machines already hit. Windows users with AOMEI Backupper installed should update and check their systems for signs of compromise.
Browser security
3 d ago
Chrome’s Extended Stable channel has been updated to 152.0.7977.169 for Windows, with 10 security fixes included. Google says bug details may stay restricted until most users are protected. Windows users should update Chrome as soon as the new build reaches their devices.
Loading…
No more articles
Could not load, try again
Try again
1
2
3
…
9
Next »
5,616 members already here
Reading, writing, commenting and voting. 0 verified · 341 joined this year
All members
Join
News
Members
Publish
Me