
XKCD Forum Data Breach: What It Means in 2026
- The XKCD forum breach in 2026: the short answer
- Timeline of the XKCD forum breach
- What changed since 2019
- Risks that come from old forum leaks (our analysis)
- What to do if you had an XKCD forum account
- What is still unknown
- Our original 2019 report
- The XKCD has provided the warning message regarding the breach
- Speculations: the exposure might has occurred due to old forum software
- XKCD breach is not the only one that has shook the Internet lately
- Related guides on 2-Spyware
The XKCD forum breach in 2026: the short answer
The XKCD forum breach is an old incident, but the leaked data still circulates. Have I Been Pwned lists it as a July 2019 breach of the phpBB forum that affected 562,000 accounts.[6] The leak held usernames, email addresses, IP addresses and passwords stored in the MD5 phpBB3 format.[6] The webcomic itself was not the target; the separate user forum was.
If you had a forum account and reused that password anywhere, treat that password as known to attackers. Old hashes in the MD5 phpBB3 format can be cracked offline, and leaked email lists are reused in phishing for years. We found no official notice from XKCD as of 2026 that the old forums came back in their former shape.
Many people reach this page while searching for XKCD jokes about security, passwords, GDPR or phishing. The comic often makes fun of weak passwords and bad security habits. This page is about the real incident behind the joke: a forum that the comic's own readers used, and what its leak means for them today.
| Question | Answer |
|---|---|
| What was breached | The phpBB user forum of the XKCD webcomic, not the comic site[6] |
| When | July 2019; added to Have I Been Pwned on September 1, 2019[6] |
| How many accounts | About 562,000[6] |
| Data exposed | Usernames, emails, IP addresses, MD5 phpBB3 password hashes[6] |
| Who reported it | Researcher Adam Davies passed the data to Have I Been Pwned[6] |
| Status in 2026 | We found no official notice that the old forums reopened |
Timeline of the XKCD forum breach
| Date | Event |
|---|---|
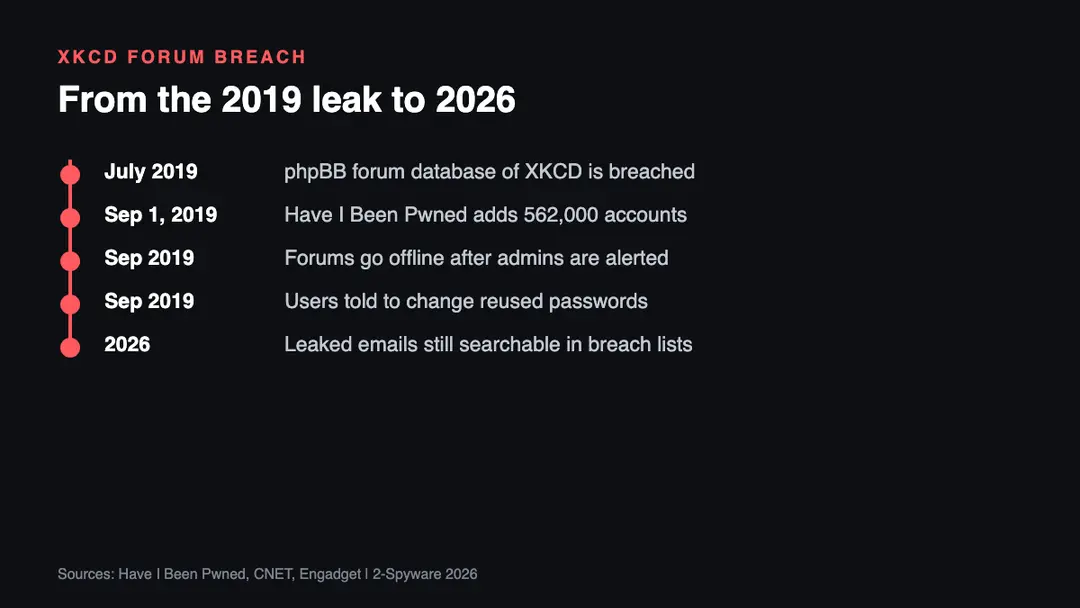
| July 2019 | The XKCD phpBB forum suffers a data breach[6] |
| September 1, 2019 | Have I Been Pwned adds the breach with 562,000 accounts[6] |
| September 2019 | The forum is shut down after administrators are alerted to the breach[8] |
| September 2019 | Users are told to change the password on any account that shared it[7] |
| 2026 | The breach is still listed and searchable on Have I Been Pwned[6] |
What changed since 2019
The facts of the breach did not change. What changed is how long such data stays useful to criminals. Have I Been Pwned still lists the XKCD breach and still advises affected users to change the password on every account where it was used and to turn on two-factor authentication.[6]
Press reports from 2019 described the data as salted and hashed passwords, plus an IP address from the time of registration in some cases.[7] At the time, Have I Been Pwned said that 58% of the affected email addresses were already in its database from earlier breaches.[8] That overlap means many of these users were already exposed elsewhere.
Our 2019 report speculated that old forum software was the cause. We found no later official statement that named the exact cause, so that point stays open.
Risks that come from old forum leaks (our analysis)
This is our own analysis of how leaks like this one are used, not a statement about specific attacks on XKCD users.
- Credential stuffing. Attackers try leaked email and password pairs on email, shopping and gaming accounts. A cracked old forum password works if you reused it.
- Targeted phishing. A message that mentions a forum you really used looks more believable. Expect fake notices that say your old account must be verified.
- Sextortion and threat emails. Scammers quote an old password in the subject line to make a false threat feel real. Do not pay and do not reply.
- Combined lists. Old leaks are merged into large lists and resold, so one forum leak can feed many later attacks.
- Fake breach checkers. Sites that ask for your password to check a leak are a trap. A real checker only needs your email.
What to do if you had an XKCD forum account
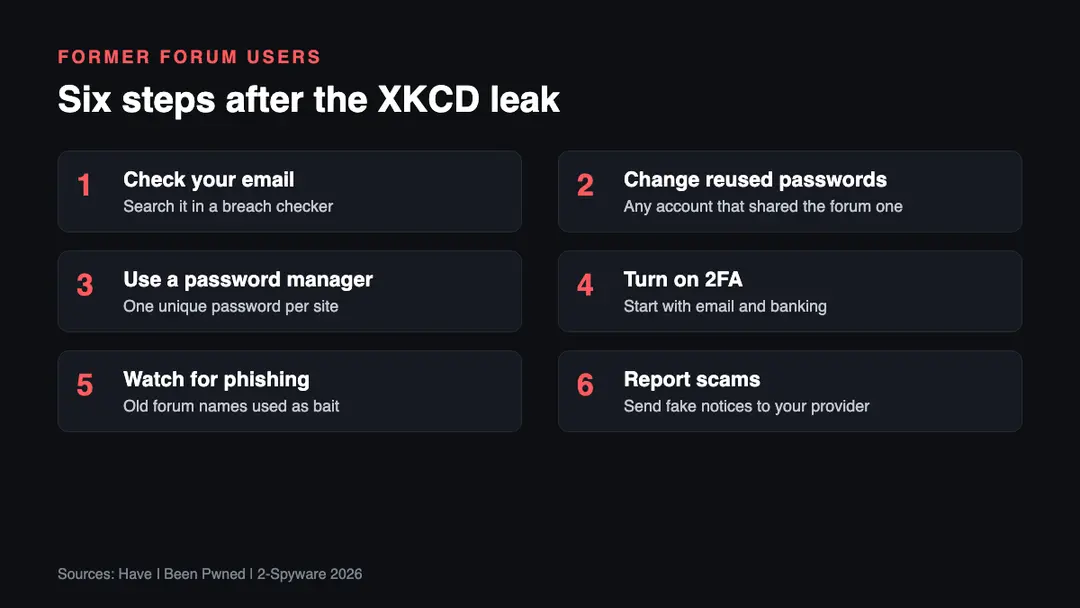
1. Check your email. Search your address in our leak check or on Have I Been Pwned. If XKCD appears in the results, your forum data was in the 2019 leak.[6]
2. Change reused passwords. Change the password on every account where you used the same or a similar one, as Have I Been Pwned advises.[6] Start with your email account, since it can reset all others.
3. Use a password manager. A manager creates and stores a different password for each site, so one leak cannot open other accounts.
4. Turn on two-factor authentication. Add a second step wherever it is supported.[6] An app or a security key is safer than SMS codes.
5. Watch for phishing. Be careful with any message that mentions XKCD, echochamber.me or an old forum account and asks you to log in or pay.
6. Report scams. Forward phishing to your email provider and follow our guide on how to report phishing.
What is still unknown
- The exact technical cause of the breach. We found no official post-incident report.
- Who stole the data and whether it was sold. The sources we read do not say.
- Whether the original forums will return. We found no official notice about this as of 2026.
Our original 2019 report
The text below is our report as first published in 2019. We keep it unchanged for the record; the sections above bring it up to date.
XKCD platform that is known as one of the most popular webcomic services is dealing with a data breach involving over 560,000 users. Created and released by Randall Munroe 14 years ago, XKCD aims to provide a catchy dose of humor and black comedy for users all over the world daily.[1]
Unfortunately, due to unknown reasons, hundreds of thousands of XKCD phpBB forum users got their usernames, IP addresses, email addresses, and even encoded passwords leaked.[2] Nevertheless, according to security researchers, about 58% of the breached emails have already ended up on the Have I Been Pwned network.[3] XKCD acknowledged the incident and has put the forum offline.
The XKCD has provided the warning message regarding the breach
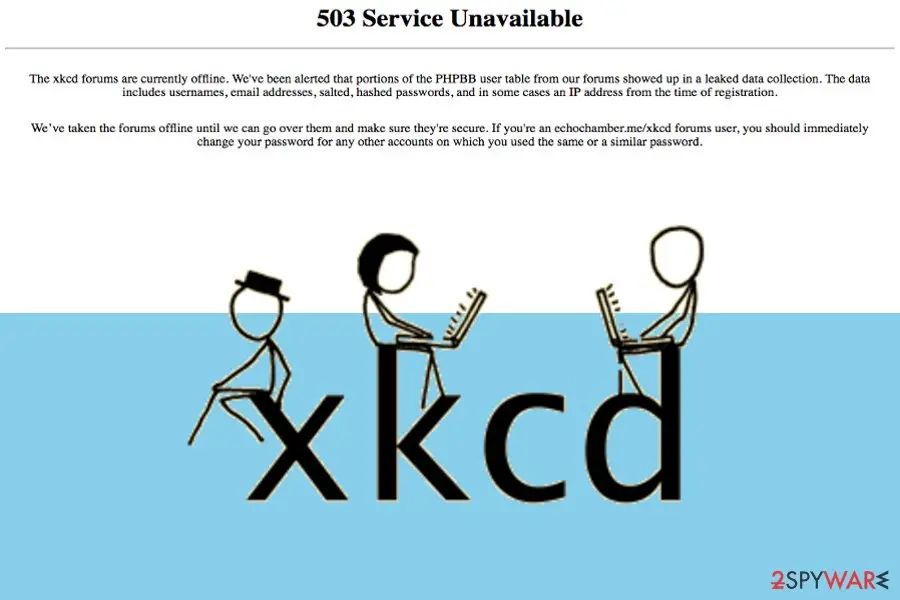
If you try to visit the xkcd.com website, you will be provided with a 503 Service Unavailable message and also an information note regarding the data breach. Here, the owner of the service is claiming that the forums have been made inaccessible for safety measures and users are urged to change their passwords right away:
We've taken the forums offline until we can go over them and make sure they're secure. If you're an echochamber.me/xkcd forums user, you should immediately change your password for any other accounts on which you used the same or a similar password.
The first one to discover the data leak was Adam Davies who shared this discovery with Troy Hunt directly.[4] Currently, the author of XKCD comics has taken required security measures: deactivated the forums, put their efforts to find ways to fix things and is constantly contacting potential victims via email.
Speculations: the exposure might has occurred due to old forum software
The main reasons of the XKCD breach still remain unknown. However, there have been numerous speculations that the information was exposed due to an outdated version of the forum. It should be noticed that older versions of the software are very easy to hack and misuse for illegitimate tasks due to numerous vulnerabilities.
As a result, older XKCD forum users might have a bigger chance of getting their passwords exposed as the security was less advanced then. At the moment, XKCD might be running over a more protective phpBB variant.
XKCD breach is not the only one that has shook the Internet lately
Data breaches, unfortunately, are quite frequent and every user needs to be concerned about the safety of their personal information. Ensure that strong and advanced passwords are always chosen to secure your online accounts. In this case, if you were the member of XKCD forums, make sure you change your password to all accounts with the same password.
Besides, using multi-factor or two-factor authentication settings will also harden the hacking process for cybercriminals. If such step seems boring and time-consuming, note that all of these steps are necessary to save your data and even funds.
Data leakages have mostly been targeting worldwide healthcare organizations, big manufacturers, financial institutions, and even some governmental companies. One of the most recent breaches has touched Foxit Software. This incident related to the exposure of over 525 million records.[5]
Related guides on 2-Spyware
Frequently asked questions
Was XKCD hacked?
The XKCD user forum was breached in July 2019, not the comic site. About 562,000 forum accounts were affected, with usernames, emails, IP addresses and MD5 phpBB3 password hashes exposed, according to Have I Been Pwned.{6} The administrators took the forum offline after they were alerted to the breach.{8}
How do I know if my XKCD forum account was in the leak?
Search your email address in a breach checker such as our leak check or Have I Been Pwned, which lists the XKCD breach.{6} If it shows up, change the password on any account where you reused the forum password, and turn on two-factor authentication where you can.
What data leaked in the XKCD breach?
Usernames, email addresses, IP addresses and passwords in the MD5 phpBB3 hash format leaked.{6} Press reports said the IP address was from the time of registration in some cases.{7} We found no report that payment data was part of the leak.
Are the XKCD forums back online in 2026?
We found no official notice that the old XKCD forums reopened in their former shape as of 2026. The forum was shut down in September 2019 after the breach.{8} Treat any site or email that asks you to log in to the old forum with suspicion, since it may be phishing.
Does XKCD have comics about passwords and security?
Yes, XKCD is known for comics about passwords, security and data, and that is why many people search for them. This page covers the real 2019 breach of the forum that XKCD readers used. The practical lesson is the same as in the jokes: use a unique password for every site.
Is an old 2019 password leak still dangerous?
Yes, if you still use that password anywhere. Leaked lists stay online for years and are merged into bigger lists used for credential stuffing. Have I Been Pwned still advises changing the password on every account where it was used.{6}
Log in to comment
No comments yet. Be the first.