
CCleaner 5.33 Hack Explained in 2026: Floxif and CBkdr.dll
- CCleaner 5.33 malware in 2026: the short answer
- Timeline: from the break-in to the clean-up
- What changed since 2017
- What the old warning signs mean (our analysis)
- How to check a PC for CCleaner 5.33 leftovers
- What is still unknown
- Our original 2017 report
- What does Floxif virus do?
- Is it safe to download CCleaner now?
- Related guides on 2-Spyware
CCleaner 5.33 malware in 2026: the short answer
The CCleaner 5.33 attack is over, and it is a closed case for ordinary users. In 2017 attackers slipped a backdoor into the official, signed CCleaner 5.33.6162 installer. Avast, which owned the developer Piriform, says the altered file reached 2.27 million computers between August 15 and September 15, 2017.[6]
Most of those computers only received the first stage, which collected basic system data. The attackers then installed a second stage on just 40 PCs at high-tech and telecommunications companies.[4][5] If you see CBkdr.dll, Floxif or the 601 second delay in an old log, it points to this 2017 incident. A current CCleaner from the official site does not contain it.
| Question | Answer |
|---|---|
| Affected version | CCleaner 5.33.6162, 32-bit systems[6] |
| Exposure window | August 15 to September 15, 2017[6] |
| Downloads of the altered file | 2.27 million[4][6] |
| Second stage installed on | 40 PCs at high-tech and telecom companies[4][5] |
| Planned third stage | ShadowPad, found on four Piriform computers[5] |
| How attackers got in | Through TeamViewer on a Piriform computer, Avast found[4] |
Timeline: from the break-in to the clean-up
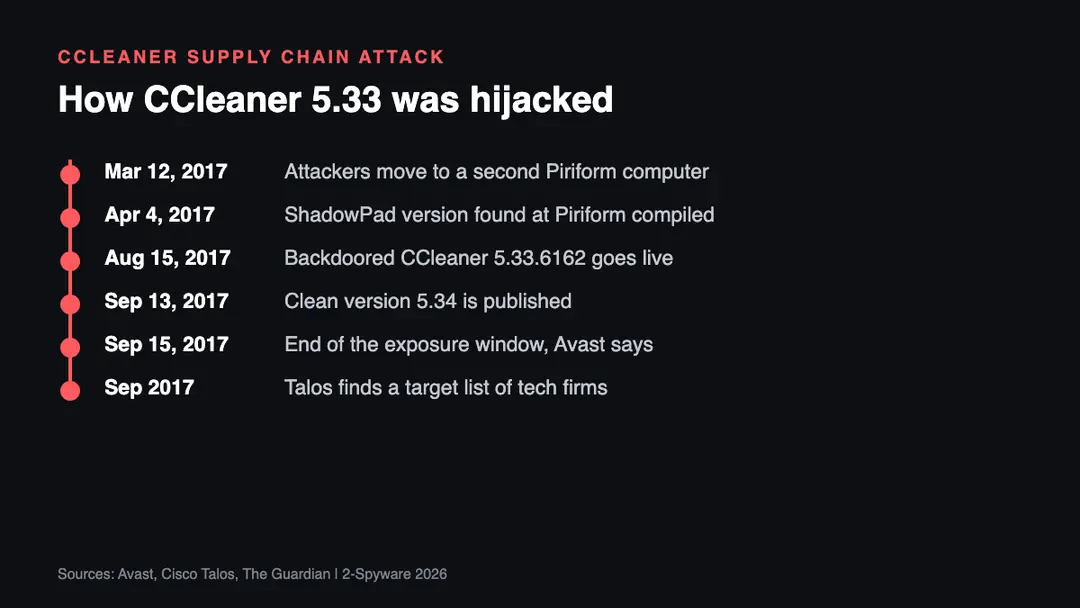
| Date | Event |
|---|---|
| March 12, 2017 | Attackers move laterally to a second computer in the Piriform network[4] |
| April 4, 2017 | The ShadowPad library found on a Piriform computer carries this compile date[4] |
| August 15, 2017 | The altered CCleaner 5.33.6162 starts reaching users[6] |
| September 12 to 13, 2017 | Our original report notes 5.34 published on September 13 |
| September 15, 2017 | End of the window Avast gives for affected computers[6] |
| September 2017 | Cisco Talos analyses the command server and finds a list of targeted organizations, including Cisco[2][7] |
What changed since 2017
The full picture came out after our first report. In 2017 the case looked like a data-collecting backdoor. Cisco Talos then looked at the attackers' command server and found that the delivery code held a list of organizations, including Cisco, that were singled out for more malware.[7] So the mass infection was a wide net used to pick a few targets.
Avast later traced how the attackers got in. Its investigation says they entered the Piriform network via TeamViewer and, on March 12, 2017, moved to a second computer outside working hours.[4] On that network Avast found ShadowPad, a remote control platform, installed on four Piriform computers. The ShadowPad version found there was compiled on April 4, 2017.[4][5]
Avast believes ShadowPad was meant as the third stage for selected CCleaner users, with keylogger features, but says it found no sign that it reached customers' computers.[5] Avast also named the Chinese group Axiom as the group it considered likely behind the attack.[5] We found no court case or official government attribution in the sources we read.
The incident is now a standard example of a supply chain attack. The installer was signed and came from the real website, so users could not have spotted it.[1][3] That is why the remedy was an update and a cleanup, not user caution.
What the old warning signs mean (our analysis)
Many readers reach this page by searching for a file name, a delay or an IP address from an old log. Here is how we read them in 2026. This is our analysis.
- CBkdr.dll. The file name tied to the CCleaner 5.33 incident, as our original report describes. On a computer that never ran 5.33, a file with this name is worth a closer look.
- 601 seconds. The first stage waited 601 seconds before it ran, to slip past sandboxes that only watch a program for a few minutes. A security tool that reports this delay is describing the 2017 code.[2]
- Floxif. Some antivirus products named the first stage Floxif. The name in a 2026 scan usually points to an old CCleaner 5.33 installer kept in a downloads folder or an archive.
- 216.126.225.148. The command server address Talos reported in 2017.[2] Seeing it in old firewall logs means a computer ran the affected version back then.
- Fake CCleaner downloads. A wider risk today is CCleaner copies on unofficial download sites. Get the program only from its official site.
How to check a PC for CCleaner 5.33 leftovers
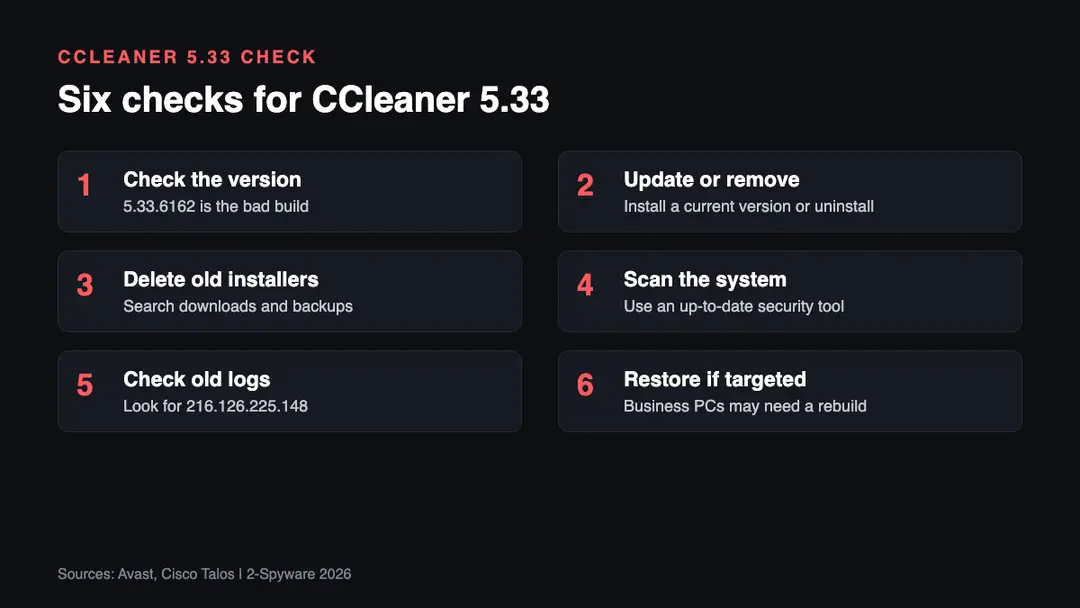
1. Check the version. Only CCleaner 5.33.6162 carried the backdoor, and our original report notes that only 32-bit systems were affected.[6] If you run a newer version, the 2017 code is not in it.
2. Update or remove. Install the current version from the official site, or uninstall CCleaner if you no longer use it. Version 5.34 removed the problem in 2017, as our original report says.
3. Delete old installers. Search your downloads folder, old backups and USB drives for CCleaner 5.33 installer files. A forgotten installer is the most common reason a scanner still flags Floxif today.
4. Scan the system. Run a full scan with an up-to-date security tool. Our virus and malware removal guides explain how to clean up anything it finds.
5. Check old logs. On company networks, search old firewall or proxy logs for 216.126.225.148.[2] A hit shows which machines ran the affected build.
6. Restore if targeted. A machine that may have received the second stage should be rebuilt or restored from a backup older than August 15, 2017, rather than just cleaned. That is our advice, and it mostly concerns the 40 business PCs that got that stage.[4] Change passwords used on any affected machine and check whether your email appeared in a leak with our leak check.
What is still unknown
- Who exactly ran the attack. Avast pointed to the Axiom group, but we found no official government attribution.[5]
- Which 40 companies received the second stage. Avast described them only as high-tech and telecommunications firms.[4]
- What data the attackers took from those 40 PCs. We found no public account.
Our original 2017 report
The text below is our report as first published in 2017. We keep it unchanged for the record; the sections above bring it up to date.
CCleaner, a widely-known and popular tool for cleaning computers from adware and other sorts of malware and maintaining the optimized processes, failed to escape the assault of cyber felons. All users, who downloaded 5.33 version between August 15 and September 12, risked getting entangled by Floxif malware.
Over 2 million users[1] in the US, Russia, and West Europe were likely to have been affected due to significant popularity of the software in these countries and area. While only 32-bit systems were affected, all users are recommended to update the software to the latest edition.
What does Floxif virus do?
IT researchers have discovered that the Floxif virus collects data about victim's technical specifications and transmits it to the remote Command and Control server. Cisco Talos researchers, who have identified the corrupted version, also revealed that the malware makes requests to the specific 216.126.225.148 IP address[2].
In the beginning, the corrupted version did not trigger any suspicion as it was written by the valid digital signature. Thus, the malware was delivered as the supposed 5.33 version published by Piriform (the original developer of the threat; now owned by Avast).
Additionally, the infection embedded in the software waited for 601 seconds before the execution. This was done to escape sandboxing. Interestingly, the Floxif virus executed itself only in the system with administrative rights.
After downloading and running the update process, the malware locates and replaces the existent CBkdr.dll with the identical but corrupted variant. Besides tracking the information and then transmitting it to the server, the infection did not exhibit any other behavior.
Cyber security specialists suspect how the malware managed to get past Avast anti-malware detection system. Some speculate that the offender might have communicated with the insider who had access to the software development.[3]
Is it safe to download CCleaner now?
While the installers of 5.33 version are still available, the malware has been successfully eliminated. Avast already published 5.34 version on September 13.
Though ordinary users did not have any chance to prevent this invasion as the tool posed to legitimate version, they might find the following advice useful:
- keep a couple of different malware prevention and elimination tools
- download them from the official sites and install the latest version as soon as it is published
Related guides on 2-Spyware
Frequently asked questions
What is CBkdr.dll in CCleaner?
CBkdr.dll is the file name linked to the backdoor in CCleaner 5.33, as our original 2017 report describes. The altered 5.33.6162 installer carried the malicious code and reached 2.27 million computers between August 15 and September 15, 2017.{6} Updating or removing that old version removes the problem.
Why did the CCleaner malware wait 601 seconds?
The delay was meant to evade automatic analysis. Cisco Talos found that the code paused for 601 seconds before running, which is longer than many sandboxes watch a new program.{2} Our original report adds that it ran only with administrator rights and then sent system information to the attackers.
What is Floxif and is it the same as the CCleaner malware?
Floxif is the name some antivirus products gave to the first stage of the CCleaner 5.33 backdoor. It collected basic system data and sent it to the attackers' server.{2} If a scanner reports Floxif in 2026, look for an old CCleaner 5.33 installer in downloads or backups and delete it.
How many people installed the infected CCleaner?
Avast says the altered installer was downloaded by 2.27 million CCleaner customers worldwide.{4}{6} Only 40 PCs, all at high-tech and telecommunications companies, received the more dangerous second stage.{4}{5} The Guardian reported the figure as over 2 million users at the time.{1}
How did hackers get into CCleaner?
They broke into the network of Piriform, the company that made CCleaner. Avast's investigation found that the attackers entered via TeamViewer and moved to a second computer on March 12, 2017.{4} They then added their code to the official build, which is why the installer had a valid signature.
Is CCleaner safe to use in 2026?
The 2017 backdoor is not in current versions; it affected only build 5.33.6162.{6} We found no newer supply chain attack on CCleaner in the sources we read. Download it only from the official site, and decide for yourself whether you need a cleaning tool at all.
Log in to comment
No comments yet. Be the first.