
TrickBot virus: what it is and how to remove it
TrickBot is a financial Trojan first discovered in 2016 and targeted customers of leading banks in the UK, US, Australia, and other countries. The virus is well-known for its ability to mimic online banking windows and steal personal information, such as log-in names and passwords, with the help of the post-exploitation tool Mimikatz.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Unsure whether grabber.dll is safe? A free scan checks the file and what starts it.
Do it yourself · free Remove TrickBot virus yourself 6 steps, about 18 minutes, no software needed.
Start the steps
TrickBot virus: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | TrickBot virus |
| Type | Loader |
| Symptoms | An unknown process in Task Manager |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 4 more facts
| Evidence | 15 write-ups by security sites; details still limited |
|---|---|
| File names | grabber.dll |
| First seen | 13 July 2020 |
| Facts checked | 6 October 2026 |
What TrickBot virus does on an infected PC
From our report of Jul 2020 · not reviewed since
Latest TrickBot's appearances
TrickBot's update came in March 2018, when hackers improved the code by making its detection and defense more complicated.
It has also been utilized to provide screen-locking capabilities, working similarly to ransomware. However, it seems that this aspect of the virus is not fully developed yet, as the module that is meant to encrypt files does not accomplish its goal.
In May same year, security researchers noted a collaboration of two viruses - TrickBot and IcedID. While most Trojans would usually remove previously installed malware, authors of these malicious threats decided to work together and share profits. Apparently, computers infected with IcedID were also injected with TrickBot, making the operation of malware much more efficient.
In June 2018, TrickBot targeted UK citizens, sending them spoofing HM Revenue & Customs emails, which claimed that there is an outstanding amount of money that victims need to pay back. Users were then prompted to click on a malicious link or on the attachment, which delivered TrickBot malware.
In 2019, Trickbot was seen in several campaigns that were also infecting users with such threats as Ryuk ransomware or Emotet. In summer, more than 250 million email accounts were compromised by the malware, sending out malspam to other targets worldwide.
Additionally, security experts also noticed several updates to TrickBot during 2019, including its "TrichBooster" module that allows the exploitation of SMB (Server Message Block) vulnerability in order to send spam and avoid detection from deleting sent emails from the outbox.
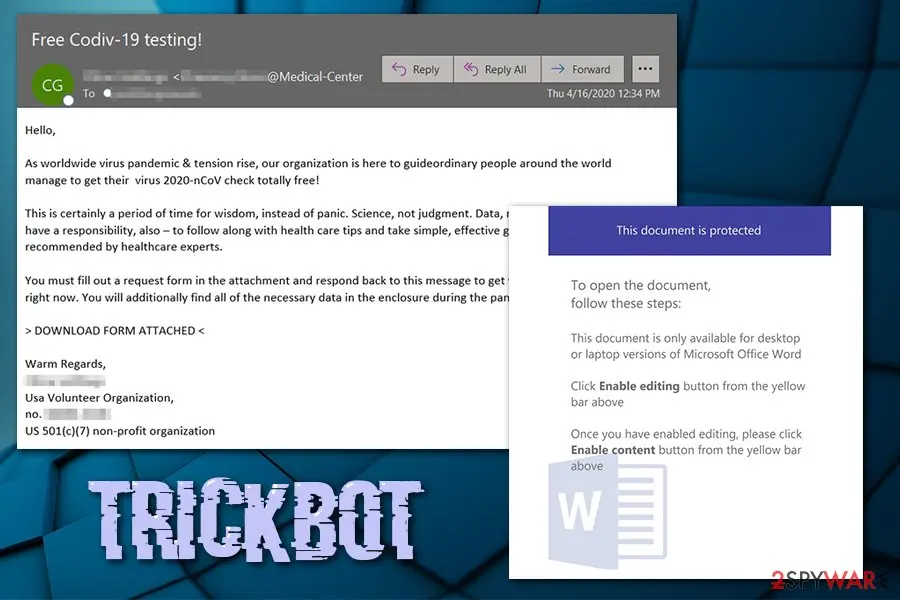
During the 2020 COVID-19 pandemic, TrickBot was also employed in malicious coronavirus-themed spam emails, where the attackers use WHO (World Health Organization) and other entities. Security experts are warning organizations that more variations of phishing emails are targeting companies and businesses with TrickBot and other malware:
From our report of Jul 2020 · not reviewed since
Terminate TrickBot virus using trusted security software
The only way to clean your system from Trojan horse is to employ a reliable security software for TrickBot removal.
This malicious program has the ability to imitate legitimate computer processes or files.
Therefore, trying to find and eliminate all malware-related files from the computer is a difficult and complicated task that might lead to irreparable damage to the system.
We highly recommend installing powerful anti-malware software and running a full system scan. In case the malware managed to affect the whole network or a server, appropriate scans should be executed. We want to remind you that you have to remove TrickBot immediately because this data-stealing trojan might lead to money loss and other serious privacy-related issues.
It is also important to change all the server/system-related passwords and tokens (if such were used) in order to avoid future compromise.
[GI=method-1]If TrickBot does not let you operate the anti-virus program properly, enter Safe Mode with Networking:
[GI=method-2]Another way to get rid of the virus is by using System Restore function:
From our report of Jul 2020 · not reviewed since
More from our earlier report on TrickBot virus
- Trojan.Trickbot.e, Trojan.Trickbot, Trojan:W32/Trickbot, and many others
- Some users might experience increased CPU usage, inability to access certain websites, slowdown in computer response, errors, crashes, and similar.
- However, Trojans rarely exhibit any symptoms
- TrickBot possesses a wide array of capabilities: Steals logins and passwords by mimicking online banking sites Harvests Bitcoin wallet data Hijacks email accounts to send malspam with the help of "TrickBooster" module Downloads and installs other malware, such as Ryuk ransomware or Emotet stealer Updates itself with new features Employs botnet-like capabilities Uses EternalBlue exploit to spread laterally, etc.
- Steals logins and passwords by mimicking online banking sites
- Hijacks email accounts to send malspam with the help of "TrickBooster" module
- Downloads and installs other malware, such as Ryuk ransomware or Emotet stealer
- Updates itself with new features
- Uses EternalBlue exploit to spread laterally, etc.
- While the infection of malware remains the biggest threat to corporation networks and businesses, regular computer users can be victims as well
- Companies and consumers might suffer significant financial losses, sensitive data compromise, identity theft, customer data exposure, and other devastating ramifications
- To get rid of malware, a network-wide scan with anti-malware should be initiated.
- Virus damage and system remediation can be performed with the help of
- Look for an attachment (Protected.doc) ( typically at the top or bottom; location varies by email service).
- Your Authorization code is: 430SJAOPS982XXS.
- Enter the authorization code when prompted.
- Attacks/campaigns using COVID-themed lures has continued to increase over the last week.
- We continue to observe increasing amounts of malicious messages and websites preying on the fear and uncertainty around the pandemic.
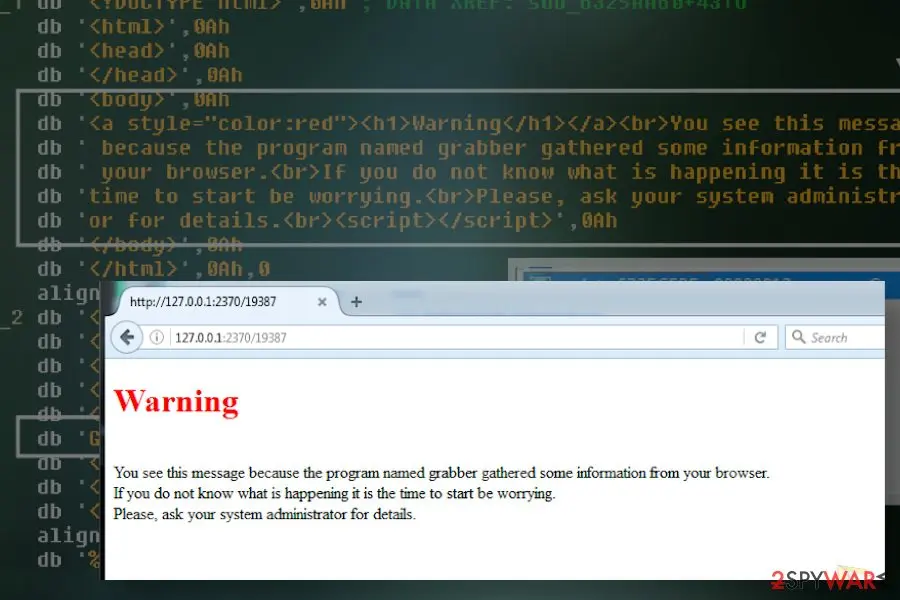
- You see this message because the program named grabber gathered some information from your browser.
- If you do not know what is happening it is the time to start be worrying.
- Please, ask your system administrator for details.
What TrickBot virus can steal or download
From our report of Jul 2020 · not reviewed since
TrickBot - a modular banking malware employed by criminals in different campaigns to steal sensitive data
TrickBot is a financial Trojan first discovered in 2016 and targeted customers of leading banks in the UK, US, Australia, and other countries.
The virus is well-known for its ability to mimic online banking windows and steal personal information, such as log-in names and passwords, with the help of the post-exploitation tool Mimikatz. It is also capable of stealing information from Bitcoin wallets, acquiring access to email accounts and stealing network/system data to proliferate laterally. Additionally, the compromised system might start sending spam emails boobytrapped with Trickbot's payload.
Analysts revealed that this malicious program was invented and released to the cyberspace after cybercriminals noticed the significant success of Dyre trojan , and began using it as malware-as-a-service.TrickBot was actively performing attacks on CRMs (Customer relationship management) and Payment Processors, and over the years, has seen a variety of malspam campaigns.
In 2019, malware managed to hijack 250 million email accounts to increase its operations. During the coronavirus pandemic, cybercriminals behind Trick bot virus employed medical advice and testing lures to make users click on attachments and execute malicious macro commands.
Analysis revealed that this banking Trojan employs similar encryption techniques and hijack strategies as Dyre (alternatively known as Dyreza). Malware can bypass some security applications and infiltrates the system when users click on the malicious link or download a fake program.
After the invasion, TrickBot injects its malicious scripts and codes into banking websites. In other words, the cyber threat switches the original version of the site with its malignant substitute. In order to enforce this technique, C encryption language is used. In this regard, the newly detected Trick Bot malware also uses the improved version of the algorithm – C++.
What is more, the technique is supplemented with Microsoft CryptoAPI algorithm unlike AES and SHA256, previously employed by Dyre. Unlike the previous version of the virus, Trojan.TrickBot executes COM and TaskScheduler commands to maintain the computer under control.
The first campaigns were targeted Australian banks only. However, on April 2017 TrickBot Trojan has been spotted attacking banks in The United States, Canada, United Kingdom, Ireland, Germany, France, Switzerland, and New Zealand.
While TrickBot Trojan mainly targets corporate networks and businesses, regular users might encounter it as well. In case of the attack, you need to run a full system scan with a reputable malware removal program, such as or . It will help to remove TrickBot from the system entirely.
Due to excessive malware's capabilities, systems that the infection occurred on might struggle to operate properly, even after TrickBot removal.
From our report of Jul 2020 · not reviewed since
Criminals released a test version of the password-stealing grabber.dll module by mistake
In the first half of July 2020, cybersecurity researcher Vitaly Kremez shared the news about the infamous credential-stealer TrickBot on Twitter.
In fact, it turns out that the managers of this deadly dangerous Trojan failed to initiate their latest attack. According to the researcher, crooks released a test module of password-stealing grabber.dll, which once installed informs the victim via the default web browser that the system has been infected. Google Chrome, Mozilla Firefox, Internet Explorer, Microsoft Edge, Opera, and users of other web browsers started reporting the following message last week:
TrickBot trojan is being distributed via spam email attachments and, usually, initiates its malicious activities in a way to remain unnoticed. Thus, the above message showing up on web browsers indicates the fact that it's the first time when criminals failed and the current campaign is not going to be very successful.
The notification saying "the program named grabber gathered some information from your browser" is genuine. It's not a scam as many consider it. The alert is triggered by the grabber.dll, which is one of the main TrickBot virus executables aiming at harvesting saved passwords and browser credentials. In case of success, the virus gets all credentials that are required for the connection to the victim's bank account or other accounts.
People who have received the notification about "program named grabber" while web browsing must immediately close the browser, restart the machine into Safe Mode, and run a full system scan with a professional anti-malware program. This notification means that a TrickBot Grabber has been recently installed and has to be removed to prevent data leakage, identity theft, and money loss.
How TrickBot virus got on your PC
From our report of Jul 2020 · not reviewed since
Fake Lloyd's bank emails help to distribute Trick Bot
Experts have recently spotted a new way which was employed to distribute TrickBot trojan.
The malware was spreading inside the email letters from fake Lloyds Bank . It was disguised as an attachment holding confidential account documents. Note that official Lloyds Bank is not related to this malspam campaign in any way, except that its name was used for malevolent purposes.
Victims report receiving an email from <secure@lloyds-commercial.com> on December 6, 2017, which contained Protected32.doc attachments. Obviously, the letter was designed to look extremely genuine and has convinced many people to believe its legitimacy.
The email briefly explained to the recipients that it is an automatically sent message which does not require a reply. It simply encouraged the gullible people to check the attachment and included the following instructions:
Remember, that you should not open any email attachments which look suspicious or unrelated to you. We want to remind you about the previous techniques which hackers used to spread TrickBot malware. The hackers have tried to employ a similar malspam campaign in June 2017 which was almost identical to the one spreading Jaff ransomware.
Cybercriminals used social engineering techniques to trick users into opening a malicious email attachment. They included an obfuscated PDF file that opens a Word document.
This file asked to enable macro command in order to see the content. Clicking "Enable Macros" button executes Trojan on the system. New victims of TrickBot were banks in India, Singapore, Netherlands, and Bulgaria.
However, financial institutions were not the only ones who have been suffering from TrickBot Trojan. Now it is also targeting two Customer Relationship Manager (CRM) SaaS providers and PayPal users. In May security researchers discovered two malware distribution campaigns that targeted 210 URLs.
From our report of Jul 2020 · not reviewed since
Trojan has mostly been spread via phishing emails
Experts have detected that phishing emails are still the primary distribution method used by hackers to infiltrate TrickBo .
They might disguise under genuine looking PDF or DOC documents and contain Invoice or Private Details subject line. People are easily tricked to open malicious attachments since criminals imitate well-known companies.
Malware also aims at PayPal users. Thus, if you receive an email from PayPal about suspicious activities in your account or reporting about other problems, you should login into their website directly instead of clicking provided links or attached documents.
The crooks develop different techniques to access personal information. Thus, such emails are usually very convincing. Do not fall into their trap even if they ask you to review suspicious invoice documents or tax reports.
Furthermore, the Trojan can attach itself to a free application. So you should give it a second thought before installing even a new media player. The latter often happens to be the carrier of more malicious cyber threats. By exercising additional caution, you will reduce the probability of TrickBot hijack.
How to check the PC for TrickBot virus
- File:
grabber.dll
How to remove TrickBot virus
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where grabber.dll runs from and stop it
grabber.dllis the part you can see, and its location tells you whether it belongs there. Right-click it on the Processes page of Task Manager and choose Open file location, then right-click the file > Properties > Digital Signatures to see who signed it.An unsigned file, or one in a user folder such as
%AppData%, is the one to remove: end the task, then delete the file.Note the folder name, because the same folder usually holds its other files. This is the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to TrickBot virus or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 3: Remove it from startup
Whatever TrickBot virus installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
After removal: passwords, accounts and prevention
Your passwords after TrickBot virus
Removing TrickBot virus does not undo what it may already have sent out while the PC showed an unfamiliar process called grabber.dll in Task Manager.
Treat saved browser passwords and logged-in sessions on this PC as known to the attacker.
From another device, change the e-mail password first and end all its sessions. Then do the same for the bank, PayPal, Microsoft, Google and Apple accounts. Stolen session cookies keep working after a password change until you sign out everywhere.
Move crypto to a new wallet created on a clean device. A step-by-step order for every kind of account is in our guide to account security after an infection.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about TrickBot virus
Is grabber.dll safe?
It depends on where the file is and who signed it, not on the name. Open Task Manager, go to the Details tab, right-click grabber.dll and choose Open file location. A file inside Program Files or System32 with a valid digital signature from a known company is usually part of a legitimate program.
A file in AppData, Temp or ProgramData with no signature, especially one that restarts itself after you end it, is suspicious. If you cannot tie the process to anything you installed, uninstall recent unfamiliar programs and run a Microsoft Defender Offline scan.
grabber.dll keeps coming back. What should I do?
A process that returns after you end it has a restart mechanism, and that is a reason to treat grabber.dll as unwanted. Check Settings > Apps > Startup, Task Scheduler and the Services list for entries pointing to its folder, and disable them.
Look in Installed apps for anything added the same day and uninstall it. Then delete the folder and run a Microsoft Defender Offline scan, which works before Windows starts and can remove files that are locked or hidden while the system is running.
Can I just delete grabber.dll?
Deleting grabber.dll by hand rarely removes TrickBot virus. While the trojan runs, Windows may refuse to delete the file, and if you succeed, a scheduled task, a service or a second copy may bring it back at the next restart.
The file can also be only one part of the infection: loaders and remote access tools often install other programs. Use the Microsoft Defender offline scan, which removes the file together with its startup entries before Windows loads, and then check startup items and scheduled tasks as described in the plan.
Why can't I find TrickBot virus in antivirus databases?
Because it is new or because it is listed under a different name. Antivirus companies name threats after the family they belong to, and a program that appears as TrickBot virus on your PC may carry a generic or unrelated label in their databases.
Many new samples are first detected only by behaviour, without a family name. What you saw, an unfamiliar process called grabber.dll in Task Manager, is enough to act on:
- end the program
- remove its startup entry
- run a Microsoft Defender offline scan
- secure your accounts
A detection name from a scan is worth noting for later.
Can TrickBot virus spread to other devices on my network?
Most trojans aimed at home users stay on the PC they infected, but an attacker with remote access can look at the network, open shared folders and try passwords on other devices. Loaders sometimes deliver worms or ransomware that do spread.
Disconnect the PC while cleaning, run a full scan on other Windows PCs, change the router's admin password and the Wi-Fi password if they were saved on the infected PC, and update the router's firmware. If other PCs show the same detection, treat them as infected too.
What are the signs of a trojan infection?
Most trojans try to leave no visible signs, so look for side effects. Common ones:
- Windows Security turned off or unable to update
- new entries in Startup apps or Task Scheduler
- programs in Installed apps you did not install
- browser settings that changed by themselves
- unusual network activity while the PC is idle
- password-reset or login-alert e-mails you did not trigger
None of these proves an infection on its own. Together with an antivirus alert naming TrickBot virus, they are a strong reason to follow the full plan.
Is a trojan infection worth reporting to the police?
If there was harm, yes. Unauthorised payments, accounts used for fraud, blackmail or a remote session during a scam call all belong in a report, and banks often ask for its reference number before they refund anything.
If antivirus caught TrickBot virus before it ran and nothing was misused, there is nothing to report. Keep the evidence anyway:
- protection history
- the original download
- the dates
Businesses may also have to notify a data protection authority if personal data could have been accessed.
Can a normal remote support program be a backdoor?
Yes. Tools such as AnyDesk, TeamViewer and ScreenConnect are legitimate, but whoever controls the account behind them controls the PC. Scammers install them during fake support calls, and some trojan campaigns install them silently because antivirus programs do not flag a genuine, signed product.
If you find one you did not set up, uninstall it, check Startup apps for related entries and change passwords from another device. If money or accounts were involved, call your bank and report the incident.
How dangerous is TrickBot virus?
Treat it as serious until proven otherwise. The visible sign is an unfamiliar process called grabber.dll in Task Manager, and programs that behave this way often have more abilities than they show:
- copying passwords
- downloading other malware
- giving remote access
Its family is not known yet, so nobody can say which of these it uses. The good news is that the response is the same in every case and takes about an hour:
- cut the network
- remove the startup entry
- run an offline scan
- change passwords from a clean device
If someone had remote control, a full reset is safer.
Will Fortect remove TrickBot virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For TrickBot virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Malwarebytes Labs: Trick Bot – Dyreza's successor (read October 6, 2026)
- TechCrunch: TrickBot malware learns how to spam, ensnares 250M email addresses (read October 6, 2026)
- Twitter: Based on Office 365 ATP data, Trickbot is the most prolific malware operation using COVID-19 themed lures (read October 6, 2026)
- F-Secure: What is TrickBot? (read October 6, 2026)
- My Online Security: Trickbot delivered via fake Lloyds Bank Confidential account documents malspam (read October 6, 2026)
- F5 Labs: TrickBot Expands Global Targets Beyond Banks And Payment Processors To CRMs (read October 6, 2026)
- Flashpoint: Trickbot and IcedID Botnet Operators Collaborate to Increase Impact (read October 6, 2026)
- My Online Security: Fake HMRC "Important : Outstanding Amount " delivers Trickbot via CVE-2018-8174 (read October 6, 2026)
- Trend Micro: TRICKBOT's newly released modules makes it even trickier (no longer online) (read October 6, 2026)
- SentinelLabs: Threat Intel | Cyber Attacks Leveraging the COVID-19/CoronaVirus Pandemic (read October 6, 2026)
- Twitter: Vitali Kremez profile (read October 6, 2026)