
Andromeda: what it is and how to remove it
Andromeda virus is a family of Trojans that was first introduced in 2011 and has been active ever since. With dozens of variants released, it serves the purpose of propagating other malicious software (backdoor functionality) and stealing confidential information from the victim.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan can look at msiexec.exe and the other programs installed around the same time.
Do it yourself · free Remove Andromeda yourself 6 steps, about 18 minutes, no software needed.
Start the steps
Andromeda: summary
| Distribution | Malicious actors are known to use several distribution methods, including phishing campaigns, spam email attachments, illegal software downloads, and various exploit kits (Angler, Neutrino, Nuclear, etc,) |
|---|---|
| Name | Andromeda |
| Type | Trojan, backdoor |
| Active since | 2011 |
| Related to | Research showed that Andromeda shares multiple source code similarities with Zbot/Zeus |
| Encryption used | Various parts of the payload and malware files use RC4 and custom encryption |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Main process | msiexec.exe |
|---|---|
| Functionality | Opens a backdoor on the compromised system, allowing malware to install other malicious payloads Steals sensitive information from the computer, such as login credentials or banking information Installs other malware, for example, ransomware Extracts various information from the machine, including IP address, timezone, keyboard language, etc. Avoids AV analysis and detection with the help of various API functions Imports various plugins and modules that help to control the computer, including TeamViewer, rootkit, Keylogger, and others |
| Detection and termination | Andromeda and all its variants are particularly evasive, as the authors implement various obfuscation techniques. Nevertheless, most of the reputable security solutions should be able to detect the malicious payload and delete all the malicious files related to the infection (note that in some cases you might have to access Safe Mode – check the instructions on how to do that below); no Microsoft detection name is known for this name |
| Damage | Not recorded in the old report |
| Symptoms | An unknown process in Task Manager |
| Evidence | 7 write-ups by security sites; details still limited |
| File names | msiexec.exe |
| First seen | 4 January 2021 |
| Facts checked | 6 October 2026 |
What Andromeda does on an infected PC
From our report of Jan 2021 · not reviewed since
More from our earlier report on Andromeda
- Since the malware infects various Windows system files, it may corrupt the operation of the OS.
- Researchers from Avast believe that the Andromeda Trojan family stems from ngrBot/DorkBot malware, although they also spotted multiple source code similarities with Zbot, otherwise known as Zeus, which is probably the most prolific malware ever created.
- Andromeda's authors put a lot of effort into diversifying their portfolio of infection droppers and to disable, or at least complicate the sample submission and exchange between AV companies and their regular process used to scan and thoroughly analyze files.
- To achieve this, they update the custom packers daily and as a bonus, they bloat the binaries with more than 70 MB of garbage.
What Andromeda can steal or download
From our report of Jan 2021 · not reviewed since
Andromeda is an evasive malware downloader that is capable of stealing information from the infected users
Andromeda virus is a family of Trojans that was first introduced in 2011 and has been active ever since.
With dozens of variants released, it serves the purpose of propagating other malicious software (backdoor functionality) and stealing confidential information from the victim. Various criminal gangs behind Andromeda used different attack vectors over the years, including exploit kits, infectious software cracks, spam email campaigns, and others.
Initially, it was used to steal banking credentials from Windows users, although many malicious parties abused the name later in online scam campaigns.
Andromeda is very sophisticated, which it comes to obfuscation and evasion techniques. It uses several uncommon API functions to avoid infecting environments that are used for malware analysis, such as sandboxes and other analysis tools. Distributors also put a lot of effort to prevent AV companies from establishing a malware profile:
Besides, the virus uses executable compression techniques (PE packers) to prevent Andromeda removal and detection by AV solutions. Nevertheless, the most up-to-date anti-malware tools like or should be able to detect and eliminate the malicious files that were populated by the Andromeda virus.
Because malware performs various changes to the system and infects some system-related files (for example, modifies msiexec.exe and creates a new value, "Software\Microsoft\Windows\CurrentVersion\Policies\Explorer\Run" in the registry), it may also destabilize the Windows, even after the malware is eliminated.
Interestingly, malware is programmed to detect the language settings of the keyboard. If one of the following languages are identified, Andromeda Trojan will completely eliminate itself from the system:
It is not uncommon for the attackers to exclude countries they are coming from to prevent the interest of local authorities.
- Russian
- Ukrainian
- Belorussian
- Kazakh
From our report of Jan 2021 · not reviewed since
Andromeda virus: presence and possible consequences
Andromeda virus is a dangerous Trojan horse, and it can be used for multiple malicious activities.
As soon as the malware infiltrates the system, it starts controlling it, so you might notice that your computer is much slower than usual. Of course, Andromeda was not created only for that.
You should also know that this virus can easily infect your machine with additional malware, update it, disable it, remove it, and implement other malicious tasks on your computer. To perform all these tasks, Andromeda connects to its C&C server - all the communications are encrypted with the RC4 algorithm.
The C&C server communication is performed in JSON format, and the following servers are used:
Both of these domains are connected to dozens of DNS servers that are located all over the world, including the U.S., Germany, the United Kingdom, etc. Anti-malware solutions detect the malicious domains as URL:Mal, so users with comprehensive online traffic protection software can prevent these communications.
Andromeda Trojan is also known to import various tracking modules and plugins into the system, including the well-known remote control tool TeamViewer. Nevertheless, victims would not be aware of its presence, as it is operated in the background. Besides the remote control, the virus also injects a rootkit, keylogger, and other plugins that help malicious actors to achieve their goals.
In the meantime, users may suffer great losses due to Andromeda virus infection, including monetary loss, sensitive information compromise, and even identity theft/fraud. With the help of malware, hackers can establish a vast botnet, which helps them to harvest data on a mass scale. All the stolen information is typically sold on the Dark Web for large sums of money.
Therefore, remove Andromeda Trojan as soon as your security software flags it, as the consequences may be disastrous for you otherwise. If you had no anti-malware installed, the virus might run on your system for a prolonged time, and you will not know about its existence - this is another reason to keep a powerful security tool installed at all times.
- hxxp://disorderstatus.ru/order.php
- hxxp://differentia.ru/diff.php
How Andromeda got on your PC
From our report of Jan 2021 · not reviewed since
As previously mentioned, the Andromeda virus uses a variety of techniques to infect users around the world.
Just as much other malware, the early campaigns include spam emails - this technique is still prevalent to this day, even though email providers implemented a variety of techniques to prevent such emails from reaching users. Despite that, threat actors always come up with new ways of presenting a phishing email to victims.
These emails include an attachment, typically of a .doc, .xls, .pdf, or .zip format, which, once opened, asks users to allow a macro function to run (i.e., "Enable Content" prompt). If granted, a PowerShell command will contact a remote server and download the malware payload. Thus, it is important not to allow macros to be run on ANY document that is clipped to a suspicious email.
Other techniques used by the criminals include Angler, Neutrino, Nuclear, and other exploit kits, which and be rendered useless by those who use software that is patched by the latest security updates. The infection is triggered automatically as victims who use vulnerable software access a malicious or a hacked site - even a reputable site SourceForge (hosts open-source applications) was compromised by the attackers.
Also, stay away from torrent and warez sites that host illegal software installers and cracks/keygens - these are known to be infested with various types of malware, including ransomware like Djvu.
How to check the PC for Andromeda
- File:
msiexec.exe
How to remove Andromeda
How to remove Andromeda and lock the attacker out
Someone may have had remote control of the PC.
Cut the connection first, then remove the trojan and secure your accounts.
Step 1: Remove remote access tools and lock the attacker out
Unplug the network cable or turn off Wi-Fi first, so any remote session drops.
In Settings > Apps > Installed apps (Windows 11) or Apps & features (Windows 10), uninstall remote access programs you did not set up yourself, such as AnyDesk, ScreenConnect, TeamViewer or an unknown "support" tool.
Check Settings > Accounts > Other users (Family & other users in Windows 10) for accounts you did not create. Turn off Remote Desktop under Settings > System unless you use it.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 2: Check where msiexec.exe runs from and stop it
msiexec.exeis the part you can see, and its location tells you whether it belongs there. Right-click it on the Processes page of Task Manager and choose Open file location, then right-click the file > Properties > Digital Signatures to see who signed it.An unsigned file, or one in a user folder such as
%AppData%, is the one to remove: end the task, then delete the file.Note the folder name, because the same folder usually holds its other files. This is the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 3: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Andromeda or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 4: Remove it from startup
Whatever Andromeda installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
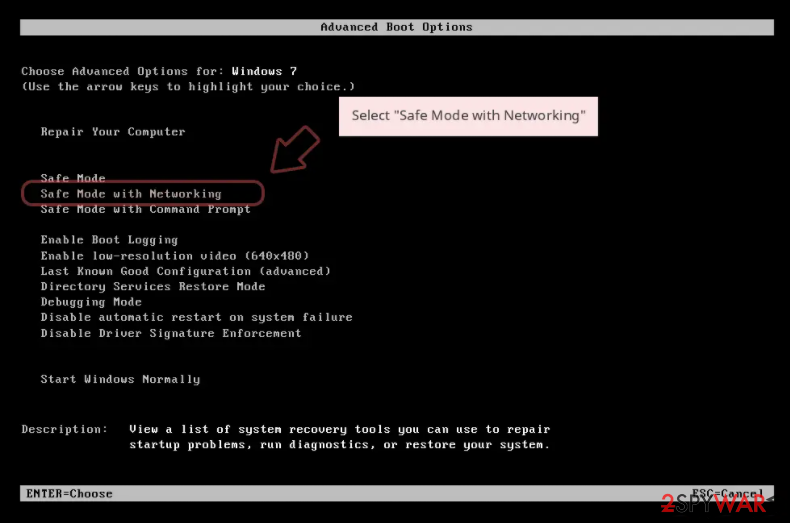
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
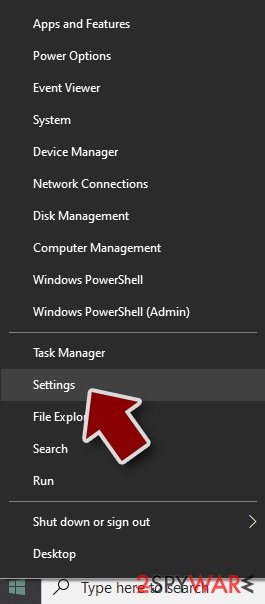
Windows 10 / Windows 8
- Right-click on Start button and select Settings.
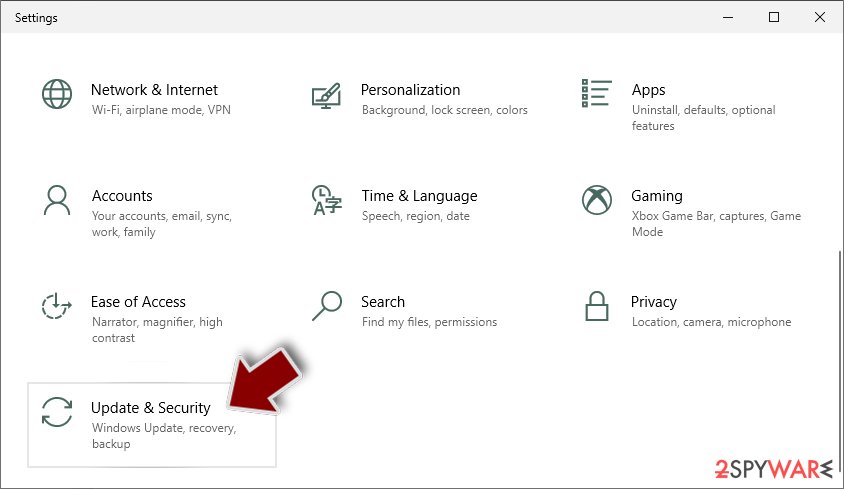
- Scroll down to pick Update & Security.
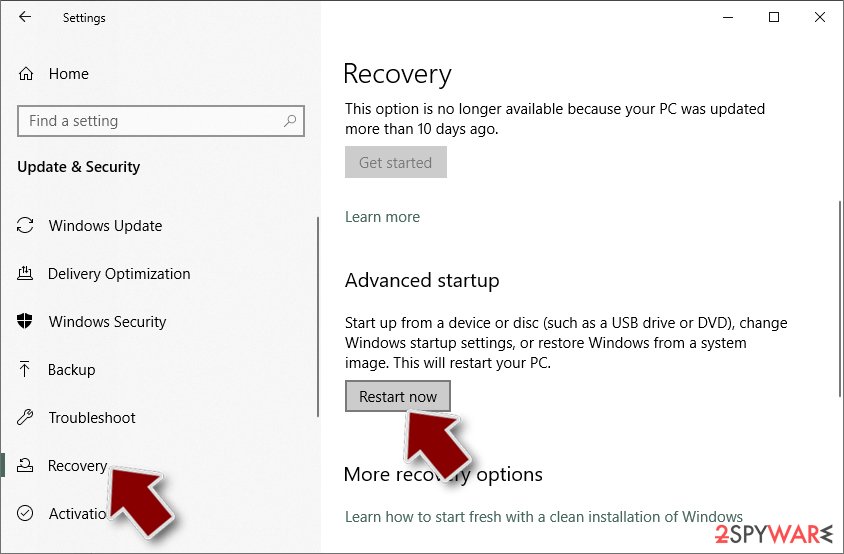
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
- Select Troubleshoot.
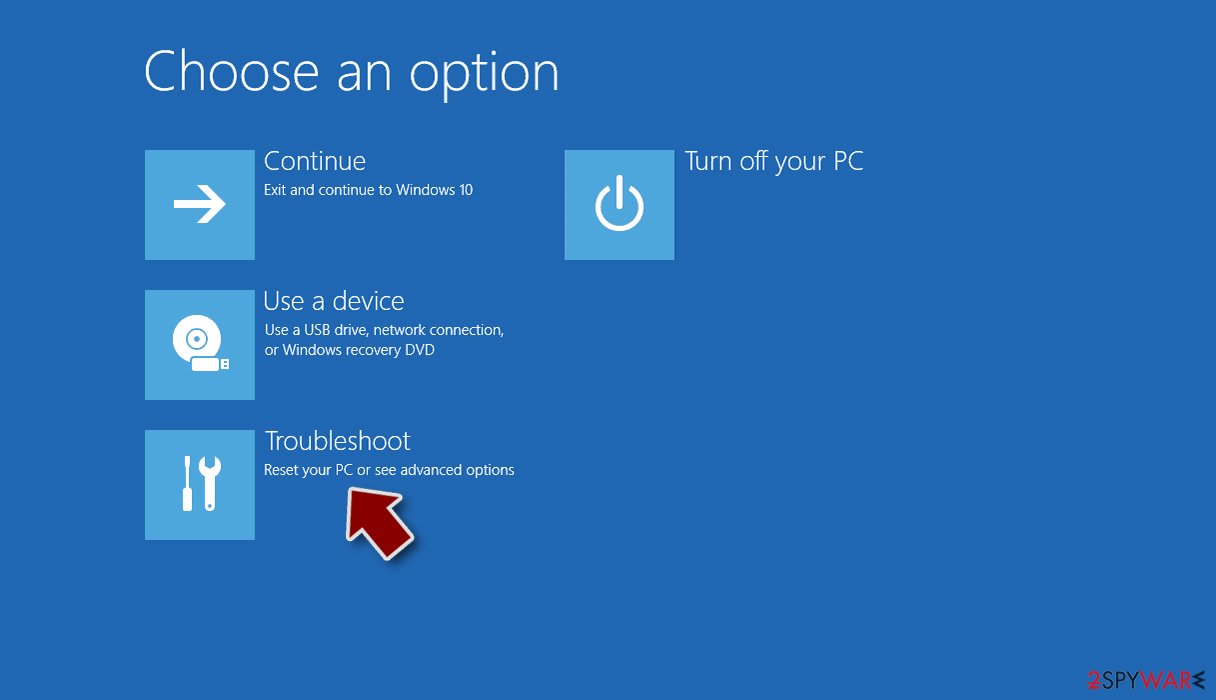
- Go to Advanced options.
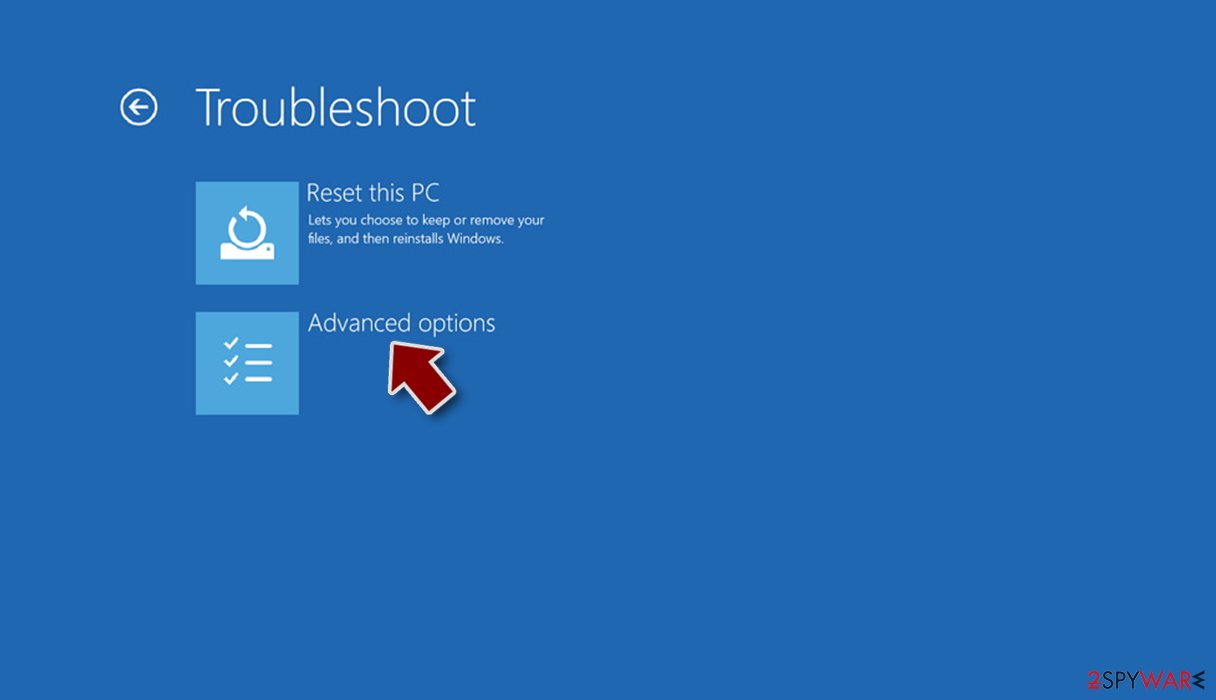
- Select Startup Settings.
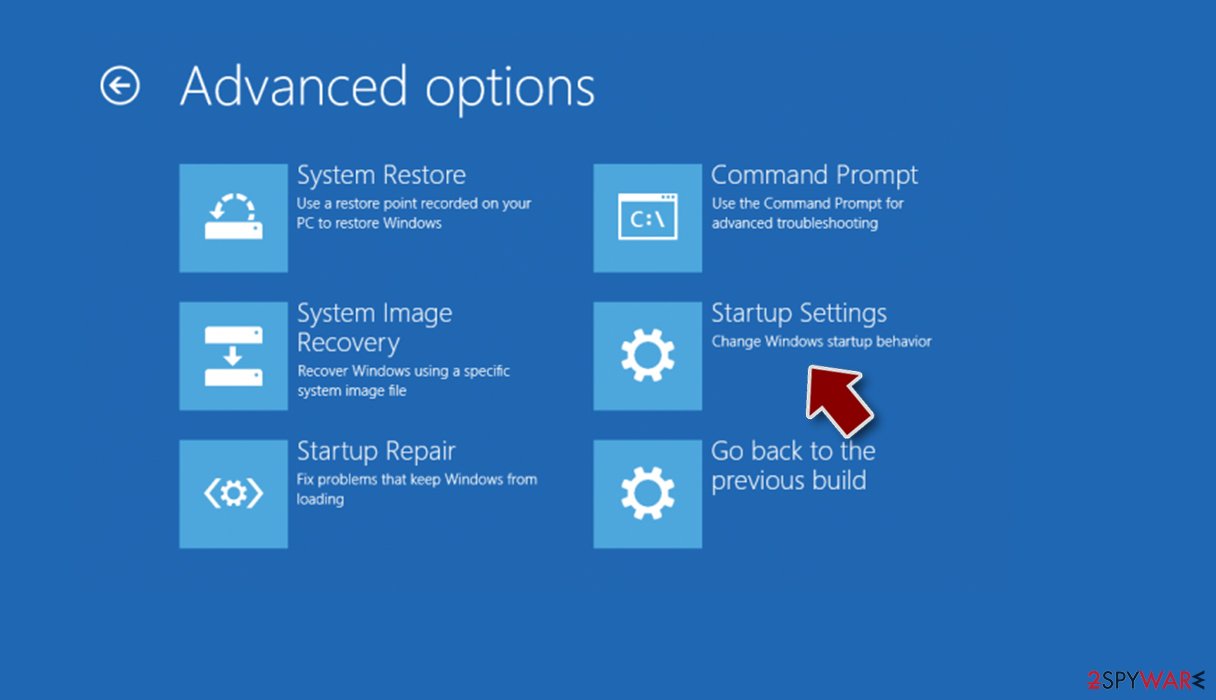
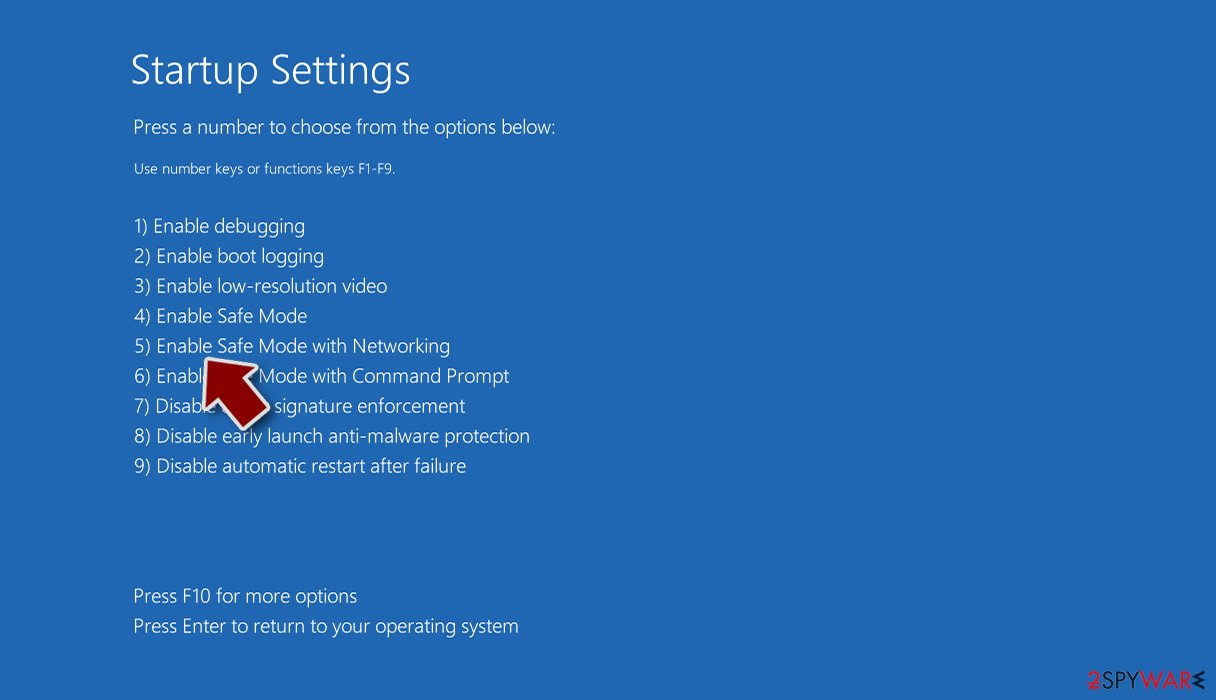
- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.
Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
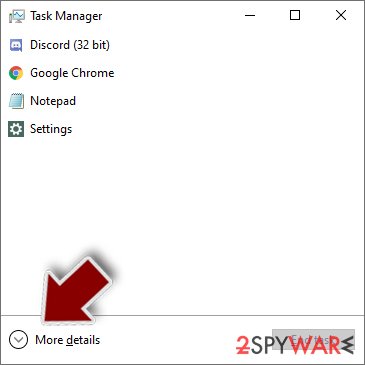
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.
- Scroll down to Background processes section, and look for anything suspicious.
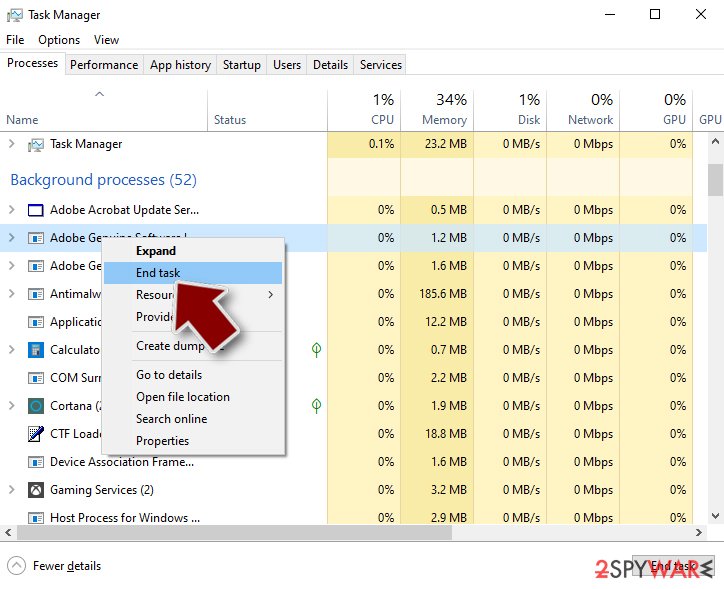
- Right-click and select Open file location.
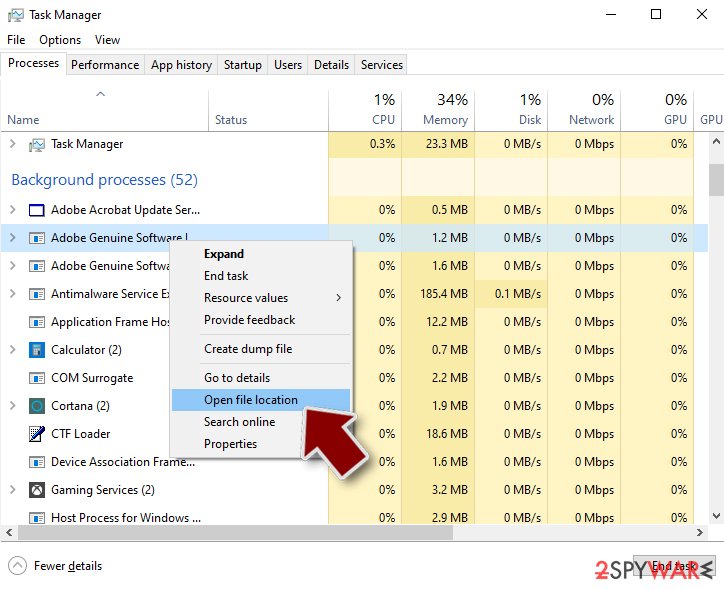
- Go back to the process, right-click and pick End Task.
- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
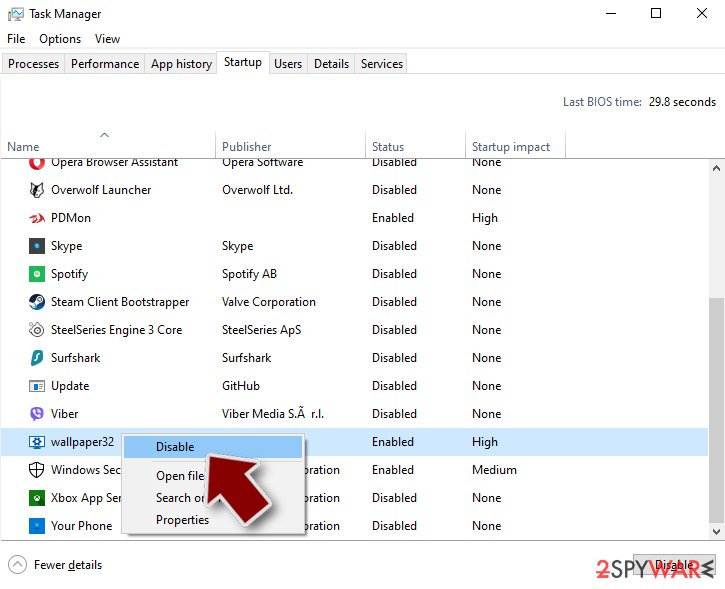
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.
Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
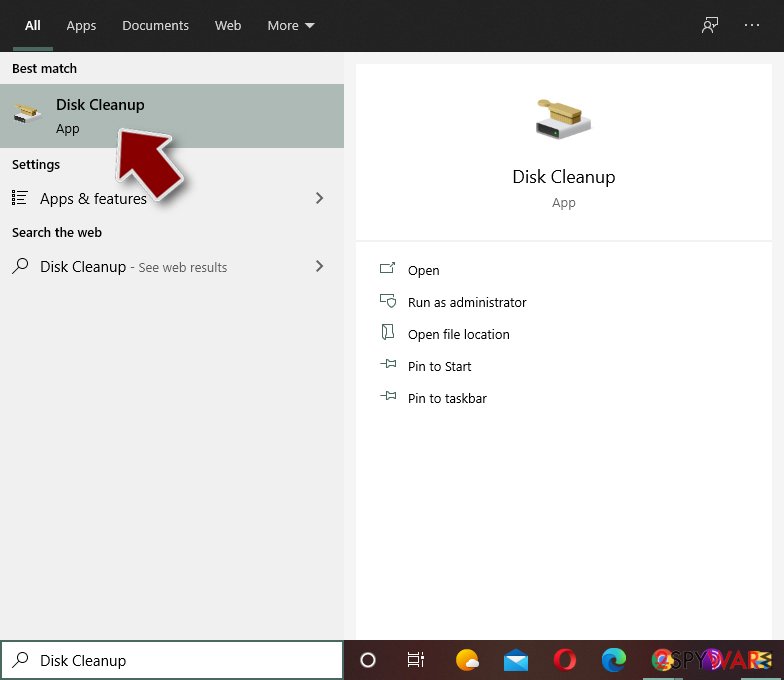
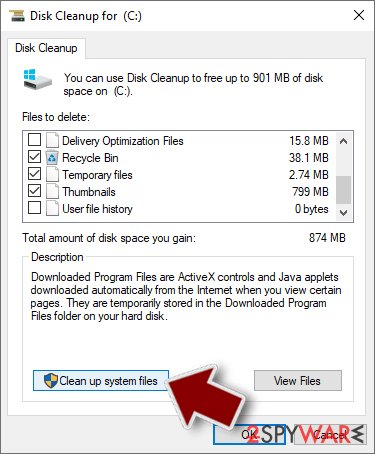
- Type in Disk Cleanup in Windows search and press Enter.
- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.
- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Jan 2021 · not reviewed since
Andromeda virus removal steps
Andromeda virus is a sophisticated piece of malware, and threat actors use various techniques in order to increase its persistence and ensure that the malware stays on the system as long as possible.
This is especially true if no anti-malware is not present on the machine, as it allows the infection to spread without interruptions. Once infected, the computer may remain in the state for weeks or even months, until security software is installed, and a prompt Andromeda removal can be performed.
In some cases, you might not be able to remove Andromeda Trojan immediately, as it may start tampering with your anti-malware software. In such a case, access Safe Mode with Networking, and perform a full system scan from there.
[GI=method-1]If you are struggling to remove Andromeda Trojan in normal mode, access Safe Mode with Networking:
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed an unfamiliar process called msiexec.exe in Task Manager, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about Andromeda
Is msiexec.exe a virus?
The name msiexec.exe is not enough to say. Malware often uses technical-sounding names, and harmless updaters often use odd ones. Check three things:
- the folder the file runs from
- the Digital Signatures tab in its properties
- the program that starts it (Startup apps, Task Scheduler or services)
A signed file from a company whose product you use is almost certainly fine. An unsigned file in a user folder that no installed program explains should be removed, and the PC scanned with Microsoft Defender in offline mode.
msiexec.exe keeps coming back. What should I do?
A process that returns after you end it has a restart mechanism, and that is a reason to treat msiexec.exe as unwanted. Check Settings > Apps > Startup, Task Scheduler and the Services list for entries pointing to its folder, and disable them.
Look in Installed apps for anything added the same day and uninstall it. Then delete the folder and run a Microsoft Defender Offline scan, which works before Windows starts and can remove files that are locked or hidden while the system is running.
Can I just delete msiexec.exe?
Deleting msiexec.exe by hand rarely removes Andromeda. While the trojan runs, Windows may refuse to delete the file, and if you succeed, a scheduled task, a service or a second copy may bring it back at the next restart.
The file can also be only one part of the infection: loaders and remote access tools often install other programs. Use the Microsoft Defender offline scan, which removes the file together with its startup entries before Windows loads, and then check startup items and scheduled tasks as described in the plan.
How dangerous is Andromeda?
Treat it as serious until proven otherwise. The visible sign is an unfamiliar process called msiexec.exe in Task Manager, and programs that behave this way often have more abilities than they show:
- copying passwords
- downloading other malware
- giving remote access
Its family is not known yet, so nobody can say which of these it uses. The good news is that the response is the same in every case and takes about an hour:
- cut the network
- remove the startup entry
- run an offline scan
- change passwords from a clean device
If someone had remote control, a full reset is safer.
Should I reset my PC because of Andromeda?
Only if the signs point to deeper access. Reset when you see an unfamiliar process called msiexec.exe in Task Manager again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
Is a trojan infection worth reporting to the police?
If there was harm, yes. Unauthorised payments, accounts used for fraud, blackmail or a remote session during a scam call all belong in a report, and banks often ask for its reference number before they refund anything.
If antivirus caught Andromeda before it ran and nothing was misused, there is nothing to report. Keep the evidence anyway:
- protection history
- the original download
- the dates
Businesses may also have to notify a data protection authority if personal data could have been accessed.
Why didn't my antivirus stop Andromeda?
New trojan builds are packed and changed often so that signatures do not match, and some are signed with stolen or bought certificates. Many arrive inside password-protected archives, which scanners cannot open until you extract them.
Some downloads also tell the user to turn off the antivirus "because it gives false alarms", a common line in cracked software instructions. Keep real-time protection on, never disable it for an installer, and run the offline scan whenever you suspect something slipped through.
Can Andromeda spread to other devices on my network?
Most trojans aimed at home users stay on the PC they infected, but an attacker with remote access can look at the network, open shared folders and try passwords on other devices. Loaders sometimes deliver worms or ransomware that do spread.
Disconnect the PC while cleaning, run a full scan on other Windows PCs, change the router's admin password and the Wi-Fi password if they were saved on the infected PC, and update the router's firmware. If other PCs show the same detection, treat them as infected too.
Can a normal remote support program be a backdoor?
Yes. Tools such as AnyDesk, TeamViewer and ScreenConnect are legitimate, but whoever controls the account behind them controls the PC. Scammers install them during fake support calls, and some trojan campaigns install them silently because antivirus programs do not flag a genuine, signed product.
If you find one you did not set up, uninstall it, check Startup apps for related entries and change passwords from another device. If money or accounts were involved, call your bank and report the incident.
Will Fortect remove Andromeda?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Andromeda, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wired: Hacker Lexicon: What Is a Backdoor? (read October 6, 2026)
- NJCCIC: Exploit Kits (read October 6, 2026)
- Avast: Andromeda under the microscope (read October 6, 2026)
- Wikipedia: Executable compression (read October 6, 2026)
- Wikipedia: RC4 (read October 6, 2026)
- Imperva: Rootkit (read October 6, 2026)