
Citadel virus: what it is and how to remove it
Citadel trojan is a data-stealing malware that was first spotted in the wild back in 2011 and was based on the Zeus virus. Its impressive keylogging and evasion capabilities allowed its developer Mark Vartanyan, also known as "Kolypto," and his affiliates to harvest the login credentials from the most popular password managers, including Keepass or Password Safe.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If Citadel virus keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove Citadel virus yourself 5 steps, about 15 minutes, no software needed.
Start the steps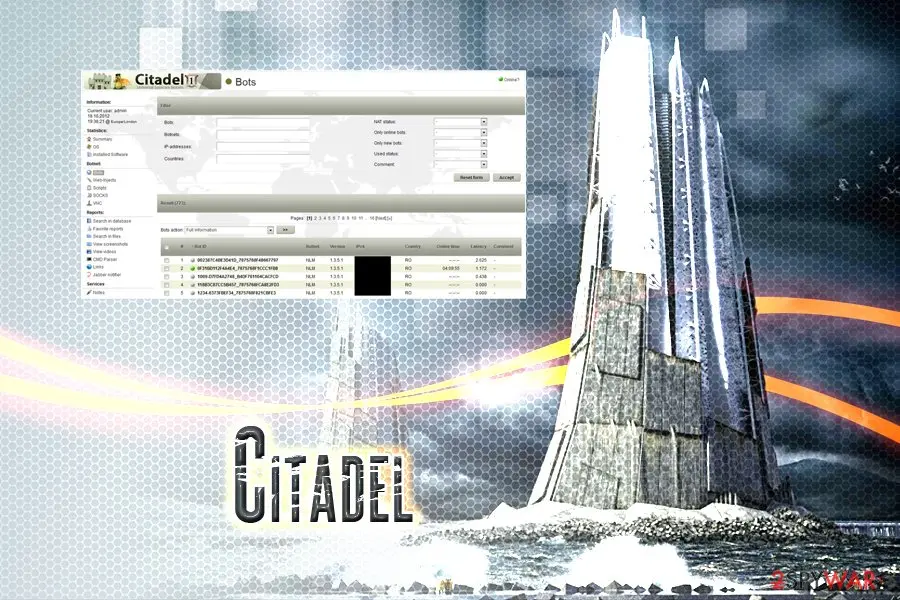
Citadel virus: summary
| Name | Citadel virus |
|---|---|
| Type | Trojan |
| Stems from | Zeus banking malware |
| Developer | Mark Vartanyan or "Kolypto" |
| Start of the operation | 2011 |
| Business model | Malware-as-a-service (MaaS) |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Capabilities | Stealing master passwords, locking users out of security sites, compiling a botnet, etc. |
|---|---|
| Distribution means | Exploit kits, vulnerabilities, spam emails, etc. |
| Termination | Use anti-malware software |
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Symptoms | An unknown program in Installed apps |
| Evidence | 6 write-ups by security sites; details still limited |
| First seen | 19 March 2021 |
| Facts checked | 6 October 2026 |
What Citadel virus does on an infected PC
From our report of Mar 2021 · not reviewed since
Citadel virus is a notorious banking trojan that stole the credentials of millions and caused immense financial losses
Citadel trojan is a data-stealing malware that was first spotted in the wild back in 2011 and was based on the Zeus virus.
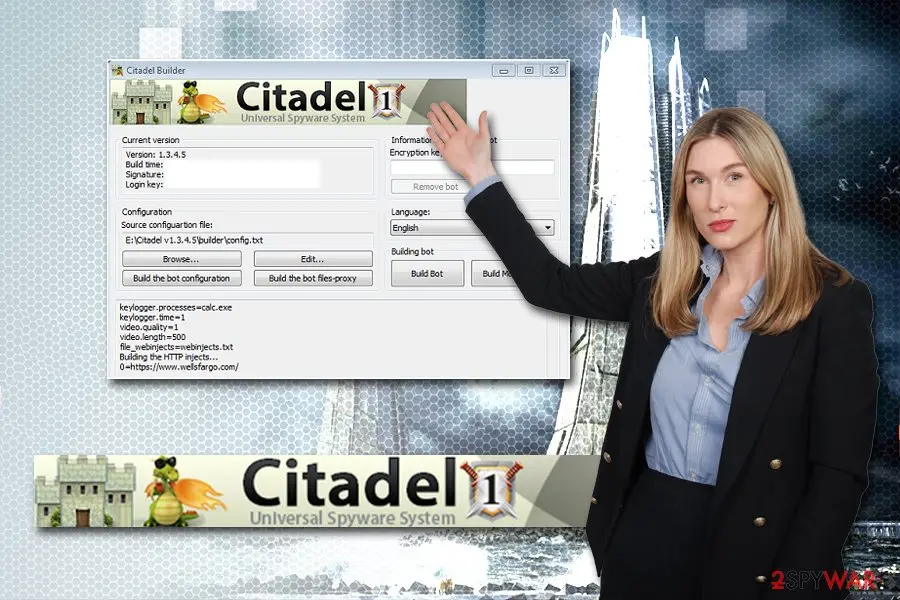
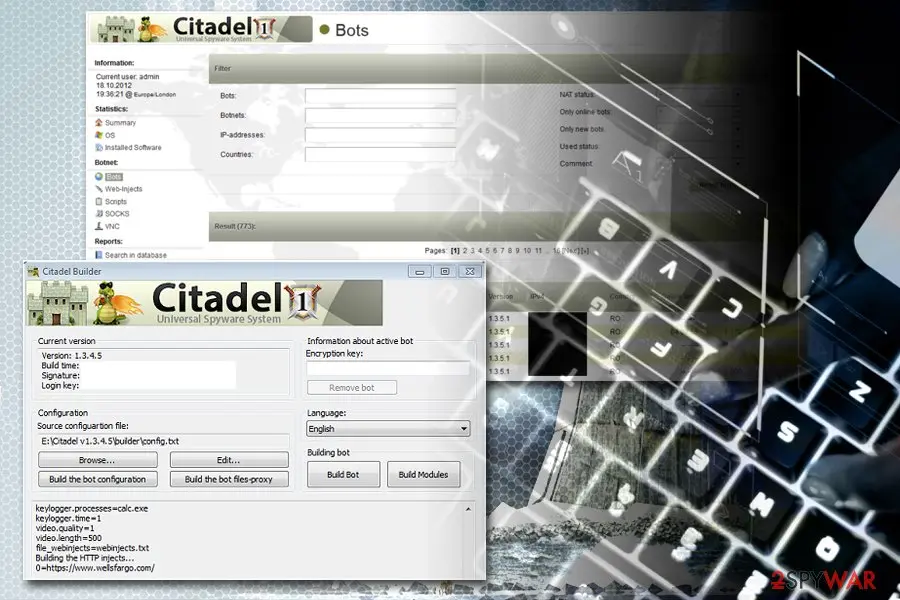
Its impressive keylogging and evasion capabilities allowed its developer Mark Vartanyan, also known as "Kolypto," and his affiliates to harvest the login credentials from the most popular password managers, including Keepass or Password Safe.
During its successful years of operation, Citadel trojan managed to infect over 11 million computers worldwide, which resulted in $500 million worth of damage to users. Fortunately, with the help of combined efforts of the FBI and Microsoft, the operator was extradited to the United States in March 2017 to face criminal charges related to malware and sentenced to five years in federal prison later that year.
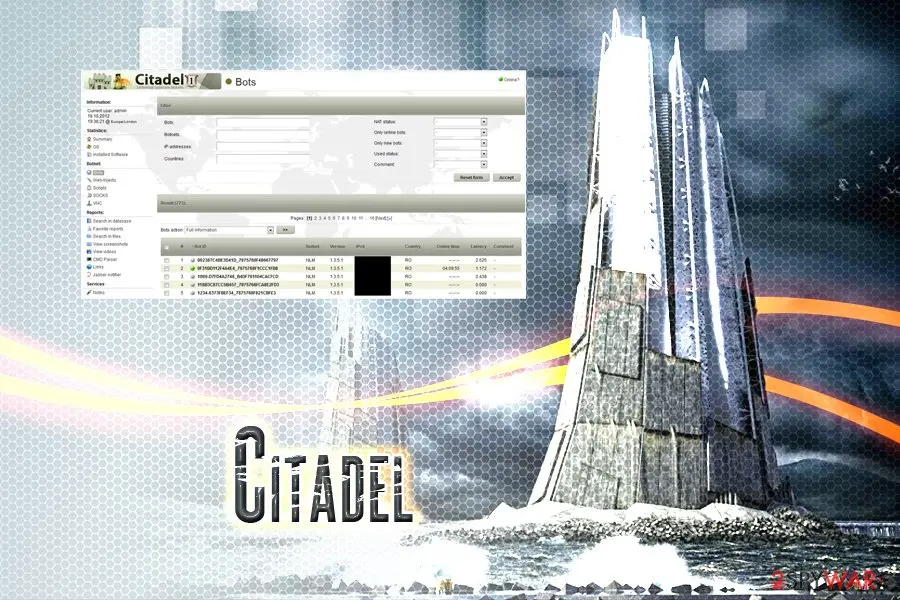
Citadel trojan was offered on the underground forums for years and was one of the first viruses that were used for malware-as-a-service (MaaS) scheme. The affiliates used a variety of infection methods, such as Blackhole EK, to infect users with a malicious payload and then included the computer network into a botnet, further proliferating malware.
While the developer Kolypto is already behind bars, it does not mean that Citadel virus is gone forever, mainly because it was operating the malware-as-a-service program. Therefore, users should beware of older threats, as the presence of a trojan can result in money loss, installation of other malicious software, or even identity theft.
Soon after the distribution of Citadel virus seized in 2016, a version based on it was released - Atmos. It was mainly developed to perform targeted attacks against banks. However, it later turned out that the malware was also used to drop TeslaCrypt ransomware, initially infecting users via malicious web injects.
What's so special about the malware is that it is capable of entering the machines and idling for months, meaning that no security solutions can detect it during that time. However, the updated versions of security applications should be able to help with Citadel virus removal and prevention.
The complex nature of the trojan requires users to be extremely careful when browsing the internet, as the infection can come when its least expected. Citadel virus might be delivered using a variety of methods, so the prevalence is guaranteed.
From our report of Mar 2021 · not reviewed since
More from our earlier report on Citadel virus
- Tools like should also help with virus damage
How to remove Citadel virus
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Citadel virus or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever Citadel virus installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Mar 2021 · not reviewed since
Prevent malware by employing adequate security options
Unlike potentially unwanted programs that are considered less harmful, various malware, including ransomware, and banking trojans are usually operated by a sophisticated criminal group.
Therefore, the distribution methods of such threats are usually much more complex and advanced - it ensures the benefit of infecting millions of users. Here are a few examples of malware distribution methods:
Let's make it clear: having comprehensive anti-malware software installed is one of the major steps towards infection prevention. However, it is not enough just to be safe online. We can recommend trying or for the proper malware termination.
You should also make sure you update your operating system along with all the installed applications as soon as new security patches are deployed. Updates can fix security flaws, which would consequently stop the trigger of the exploit, which would otherwise install malware automatically as soon as you enter the compromised site. Tools like can also help with malware damage.
Additionally, you should avoid torrent and crack sites that offer illegal software - these are full of malicious software and should not be tampered with.
- Exploits
- Software vulnerabilities
- Spam emails
- Web injects
- Fake updates
- Pirates software installers, etc.
From our report of Mar 2021 · not reviewed since
Remove Citadel banking trojan and prevent the intrusion of other malware
Besides Citadel's capability of stealing credentials, credit card details, and operating a botnet, it was also capable of proliferating other malware.
As we previously mentioned, ransomware like TeslaCrypt might be delivered - the infection that can lock personal files on the hard drive and all the connected networks. In most cases, data recovery is impossible, unless security experts come up with the decryption tool.
Therefore, manual Citadel virus removal might not be enough, as other malware might be operating in the background. We suggest you refrain from tampering with system files and rather trust comprehensive anti-malware programs to do the work automatically. Try or for this.
In some cases, Citadel virus removal might be difficult as it can tamper with anti-virus software. If that is the case, you should enter Safe Mode with Networking - a safe environment that stops malware-initiated tasks from running.
We explain how to enter the mode below - please check it out and perform a full system scan. You might also want to run a tool that repairs system files and fixes other problems for you.
[GI=method-1]In case the malware does not let your security application function normally, access Safe Mode with Networking as explained below and complete Citadel malware removal by scanning your computer:
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed citadel virus in the list of installed apps has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
Questions about Citadel virus
What is Citadel virus and why is it on my PC?
Citadel virus is a program that was installed on the PC, most likely together with something else you downloaded. Free software sites and many installers add extra programs on setup pages with pre-ticked boxes, so the extra install looks like your choice even though nobody read the page.
Check the install date in Settings, Apps, Installed apps: the program you installed that day is the probable carrier. If you do not need Citadel virus, uninstall it. If it belongs to your hardware or to a program you use, search its exact name and publisher first, because drivers and their tools can have unfamiliar names.
Citadel virus came back after I uninstalled it. Why?
Something else is reinstalling it. Common causes are a second program from the same publisher, a scheduled task that downloads it again, or a browser extension that keeps prompting for it. Sort Installed apps by install date and uninstall each entry from the same day that you did not choose.
Then open Task Scheduler and look in the Task Scheduler Library for tasks with updater-style names that you do not recognise. Check Startup apps in Task Manager too. If Citadel virus still returns, start Windows in Safe Mode, uninstall it there and run a Microsoft Defender offline scan, which looks for loaders that ordinary scans can miss.
Should I reset my PC because of Citadel virus?
Only if the signs point to deeper access. Reset when you see citadel virus in the list of installed apps again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
Is a trojan infection worth reporting to the police?
If there was harm, yes. Unauthorised payments, accounts used for fraud, blackmail or a remote session during a scam call all belong in a report, and banks often ask for its reference number before they refund anything.
If antivirus caught Citadel virus before it ran and nothing was misused, there is nothing to report. Keep the evidence anyway:
- protection history
- the original download
- the dates
Businesses may also have to notify a data protection authority if personal data could have been accessed.
Can a normal remote support program be a backdoor?
Yes. Tools such as AnyDesk, TeamViewer and ScreenConnect are legitimate, but whoever controls the account behind them controls the PC. Scammers install them during fake support calls, and some trojan campaigns install them silently because antivirus programs do not flag a genuine, signed product.
If you find one you did not set up, uninstall it, check Startup apps for related entries and change passwords from another device. If money or accounts were involved, call your bank and report the incident.
How dangerous is Citadel virus?
Treat it as serious until proven otherwise. The visible sign is citadel virus in the list of installed apps, and programs that behave this way often have more abilities than they show:
- copying passwords
- downloading other malware
- giving remote access
Its family is not known yet, so nobody can say which of these it uses. The good news is that the response is the same in every case and takes about an hour:
- cut the network
- remove the startup entry
- run an offline scan
- change passwords from a clean device
If someone had remote control, a full reset is safer.
Can Citadel virus spread to other devices on my network?
Most trojans aimed at home users stay on the PC they infected, but an attacker with remote access can look at the network, open shared folders and try passwords on other devices. Loaders sometimes deliver worms or ransomware that do spread.
Disconnect the PC while cleaning, run a full scan on other Windows PCs, change the router's admin password and the Wi-Fi password if they were saved on the infected PC, and update the router's firmware. If other PCs show the same detection, treat them as infected too.
What are the signs of a trojan infection?
Most trojans try to leave no visible signs, so look for side effects. Common ones:
- Windows Security turned off or unable to update
- new entries in Startup apps or Task Scheduler
- programs in Installed apps you did not install
- browser settings that changed by themselves
- unusual network activity while the PC is idle
- password-reset or login-alert e-mails you did not trigger
None of these proves an infection on its own. Together with an antivirus alert naming Citadel virus, they are a strong reason to follow the full plan.
Which malware family is Citadel virus?
That is not known yet. Citadel virus has been reported by people who saw citadel virus in the list of installed apps, but no sample has been analysed publicly, so security companies have not assigned it to a family. The name you see may be a file or program name chosen by the authors, not a family name.
This does not stop you from removing it: the startup points, the offline scan and the account steps are the same for most families of this type. If Microsoft Defender or another scanner gives the file a detection name, write it down; that name is the best clue to the family and is useful when you report the incident.
Will Fortect remove Citadel virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Citadel virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Department of Justice: Russian Citizen who Helped Develop the "Citadel" Malware Toolkit is Sentenced (read October 6, 2026)
- Sophos: Exploring the Blackhole exploit kit (read October 6, 2026)
- ThreatPost: ZeuS Banking Trojan Resurfaces As Atmos Variant (read October 6, 2026)
- NJCCIC: Citadel (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)