
DKOM.doublepulsar: what it is and how to remove it
DKOM.doublepulsar is a computer virus that exploits out of date Windows computers. This backdoor is an advanced trojan that leaves an open gate for a hacker to connect to your PC.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like DKOM.doublepulsar usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove DKOM.doublepulsar yourself 5 steps, about 15 minutes, no software needed.
Start the steps
DKOM.doublepulsar: summary
| Distribution | Spam emails, software bundles, deceptive ads, file-sharing platforms |
|---|---|
| name | DKOM.doublepulsar |
| Type | Trojan, backdoor virus |
| Category | Malware |
| Symptoms | Most of backdoors are programmed to remain on the system undetected, so the only symptom you might see is a warning from your security software |
| possible Purposes | Stealing financial and personal data, spying through webcam and microphone, downloading/uploading files, disabling features, taking screenshots, etc. |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Name | DKOM.doublepulsar |
| Evidence | 4 write-ups by security sites; details still limited |
| First seen | 19 January 2021 |
| Facts checked | 6 October 2026 |
What DKOM.doublepulsar does on an infected PC
From our report of Jan 2021 · not reviewed since
DKOM.doublepulsar – a backdoor that could be used by criminals to install more malware on your system
DKOM.doublepulsar is a computer virus that exploits out of date Windows computers.
This backdoor is an advanced trojan that leaves an open gate for a hacker to connect to your PC. It was used for spreading a well-known ransomware WannaCry and accessed PCs through Windows vulnerability. It is very important to follow up with updates to avoid such infections.
DKOM.doublepulsar can collect various data, such as financial and personal info, copy/steal files, etc. It also disables security software that's installed on the computer, thus making the device unprotected. This allows the trojan to upload and install any other malicious software that it's programmed to.
While the infiltration can be entirely prevented by patching Windows with the latest version, the threat is still extremely prevalent in the wild. So if your anti-malware tool flagged it, or you see any suspicious symptoms of the infection (crashing, slower performance,errors) - you came to the right place.
Double Pulsar was developed by the U.S. National Security Agency, although it was later stolen by cybercriminals who spread the infection worldwide. Malware places a backdoor on the system and exploits a vulnerability inside the Windows kernel known as EternalBlue. In 2017, more than 200,000 computers were infected with the infamous WannaCry ransomware thanks to the usage of this backdoor, resulting in a worldwide cybersecurity disaster.
Trojans like DKOM.doublepulsar, are one of the most hazardous types of malware that are created. They can have an array of built-in functions. To name just a few:
In the past years, an increasing number of Remote access Trojans (RATs) surfaced, which let the threat actors gain remote control over a victim's computer. That way, the hackers can infect other computers on the network or do whatever they please with the infected one.
Trojans are very hard to detect, as they can be camouflaged as a legitimate application and wait for a trigger to begin what it's developed for. That's why professional anti-malware tools such as or must be installed on every computer. This type of software is designed to catch malware, just keep its virus databases up to date.
To effectively mitigate the infection and remove DKOM.doublepulsar, users need to disconnect the infected PC from the network, apply the MS17-010 Windows update, reboot the device, and then perform a full system scan with reliable anti-malware. Run the software, perform an entire system scan, and get rid of any suspicious files that the tool flags.
Malware, especially backdoors, insert themselves in the system registry and other core settings and files. That's why after DKOM.doublepulsar removal, cybersecurity experts from LesVirus.fr recommend using powerful system repair tools such as the app to delete any new entries and correct any system irregularities.
- Copying all files on the infected machine and uploading them to a pre-determined server
- Deleting all data or some system files that would disable the machine
- Downloading and installing additional malicious software
- Displaying an abnormal amount of ads
- Disabling anti-malware software and any security-related services
- Stealing financial info, such as credit card details, logins, passwords, etc.
From our report of Jan 2021 · not reviewed since
More from our earlier report on DKOM.doublepulsar
- Malicious software should be taken care of by using trustworthy anti-malware applications
- Malware corrupts system files and settings.
- This impacts the system's performance by slowing it down, showing errors, and so on.
- To get your machine back on track, use the tool
How DKOM.doublepulsar got on your PC
From our report of Jan 2021 · not reviewed since
Trojans are spread using different techniques, but they can't execute themselves.
That's why cybercriminals spread them as deceptive ads. As soon as a user downloads the software and installs it, a trojan plants roots.
Another popular way the trojans are distributed is via file-sharing platforms.
And last but not least - spam emails, yet another way to deliver trojans. Payload files are usually hidden either in email attachments or in hyperlinks to malicious websites. To avoid trojan infections, please refrain from clicking any deceptive ads, don't use file-sharing platforms, and don't open any phony emails and their contents.
How to remove DKOM.doublepulsar
How to remove DKOM.doublepulsar and lock the attacker out
Someone may have had remote control of the PC.
Cut the connection first, then remove the trojan and secure your accounts.
Step 1: Remove remote access tools and lock the attacker out
Unplug the network cable or turn off Wi-Fi first, so any remote session drops.
In Settings > Apps > Installed apps (Windows 11) or Apps & features (Windows 10), uninstall remote access programs you did not set up yourself, such as AnyDesk, ScreenConnect, TeamViewer or an unknown "support" tool.
Check Settings > Accounts > Other users (Family & other users in Windows 10) for accounts you did not create. Turn off Remote Desktop under Settings > System unless you use it.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 2: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to DKOM.doublepulsar or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 3: Remove it from startup
Whatever DKOM.doublepulsar installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
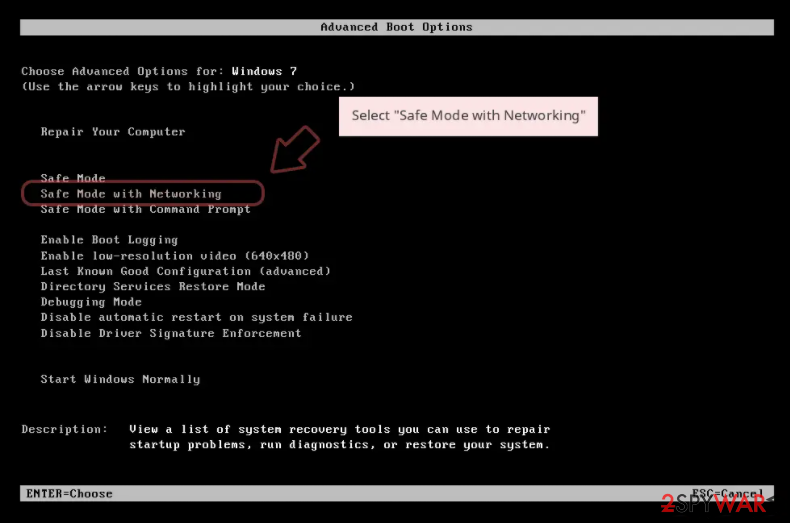
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
Windows 10 / Windows 8
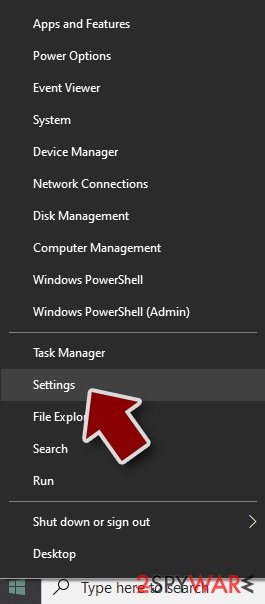
- Right-click on Start button and select Settings.
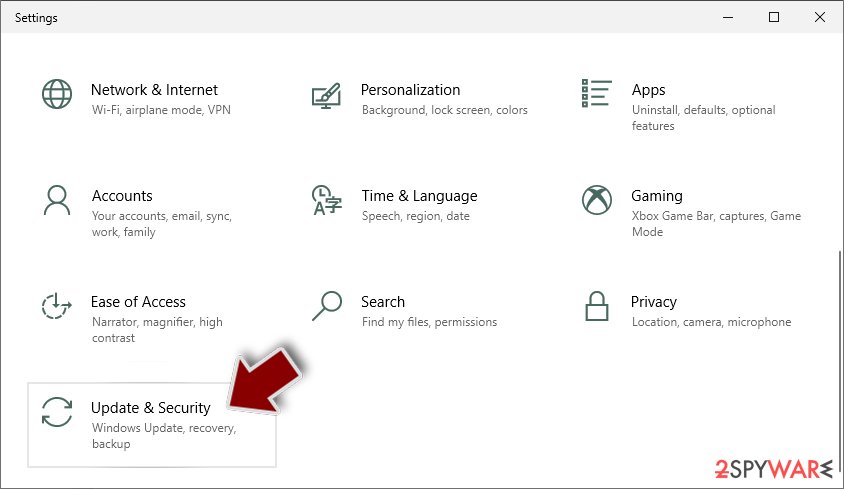
- Scroll down to pick Update & Security.
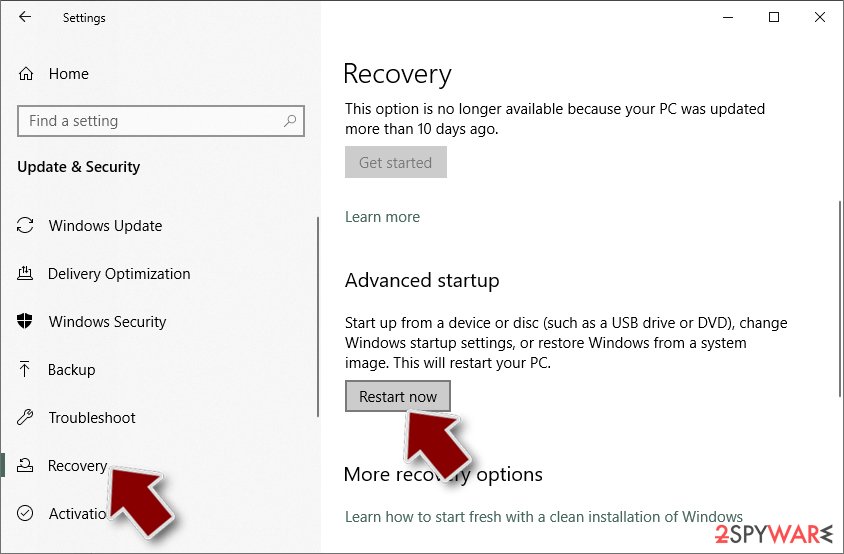
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
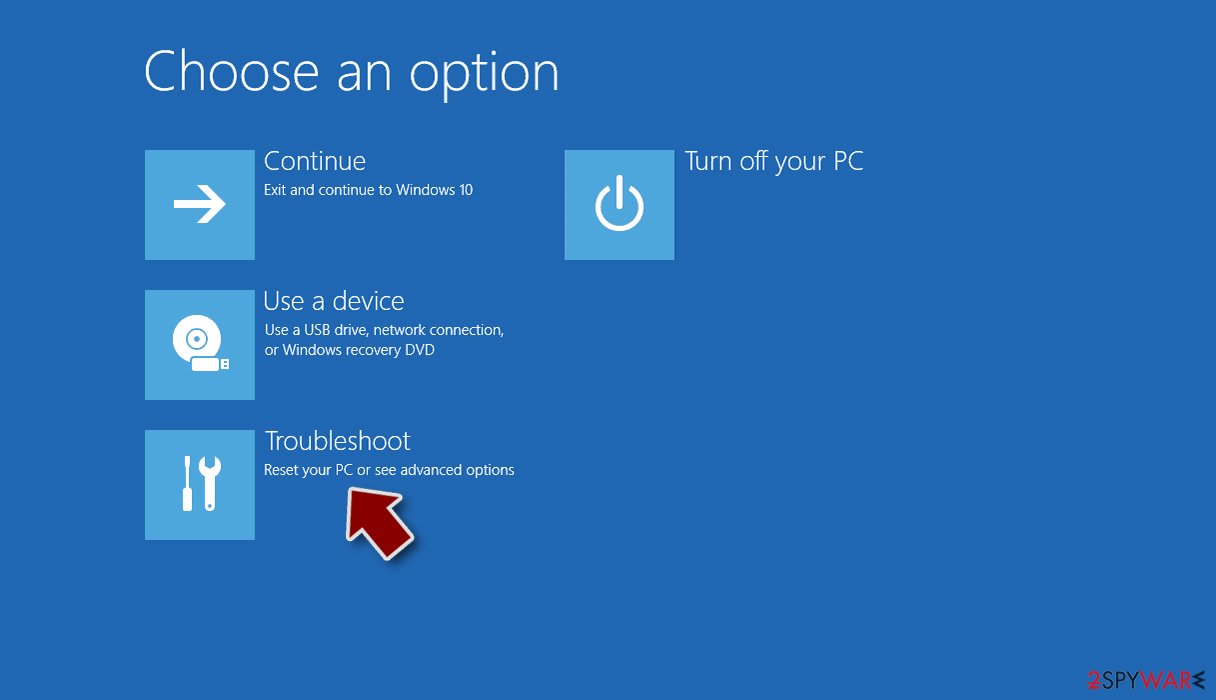
- Select Troubleshoot.
- Go to Advanced options.
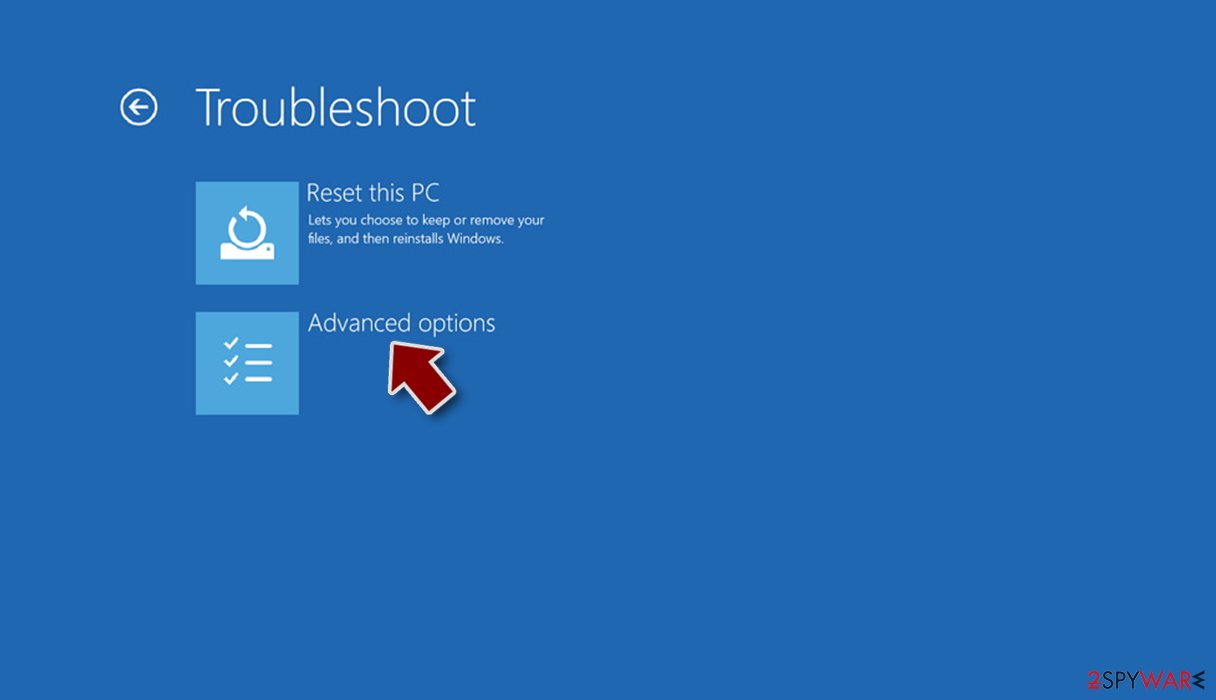
- Select Startup Settings.
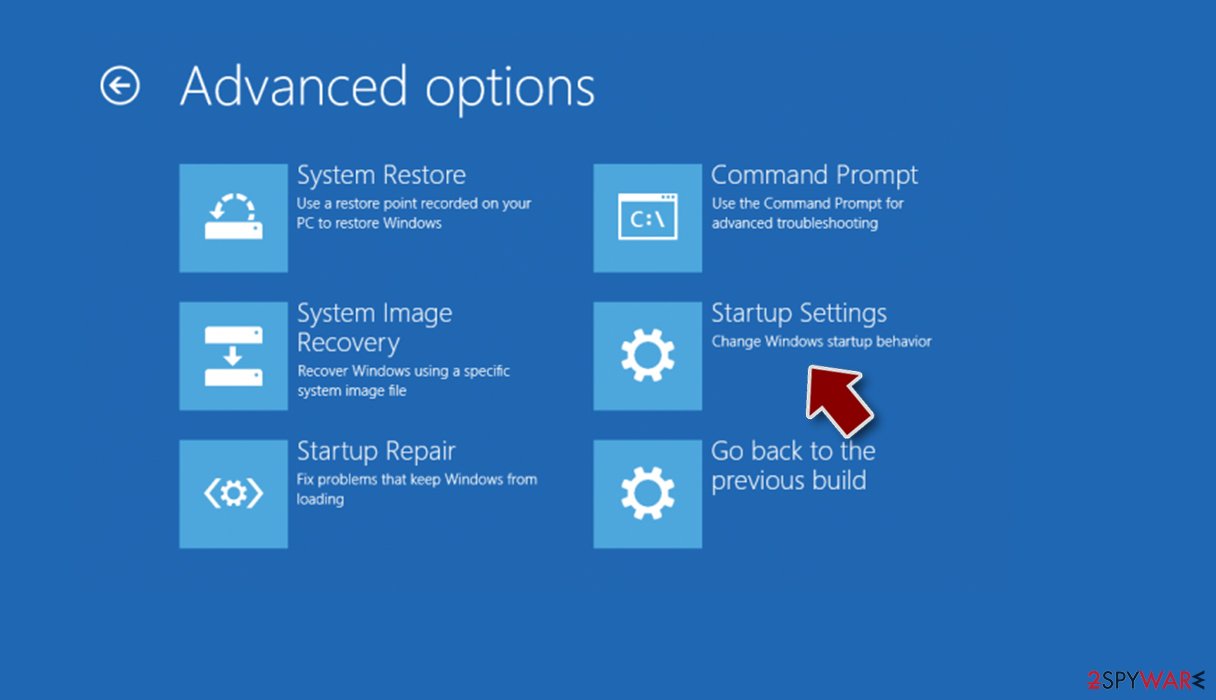
- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.
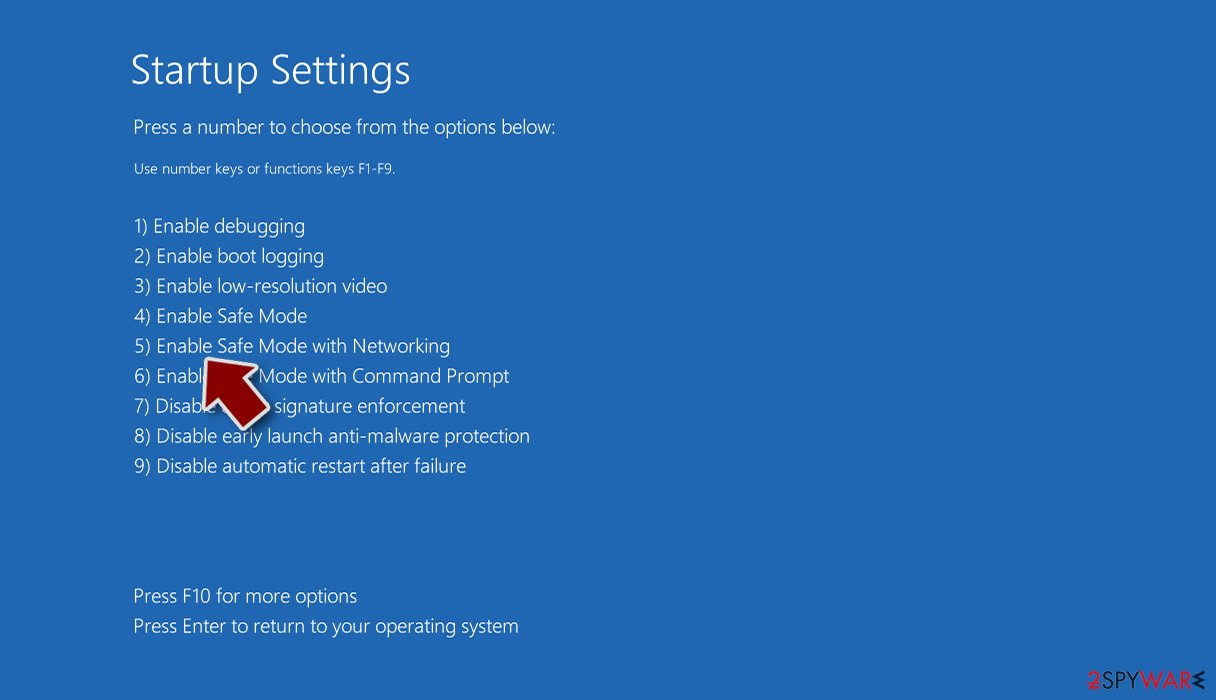
Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.
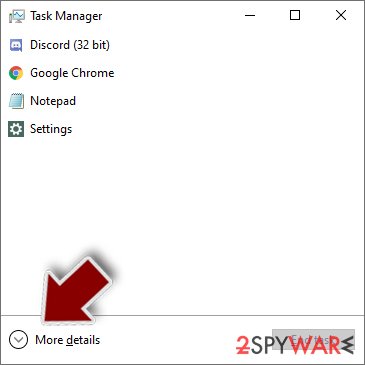
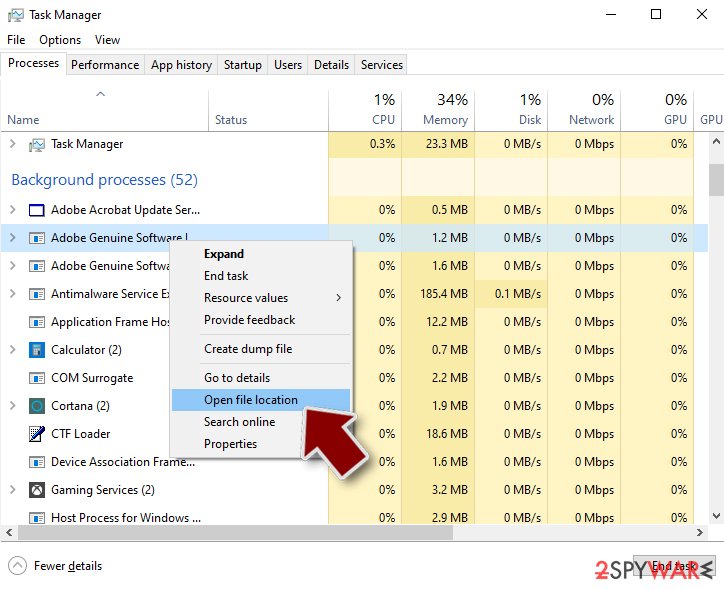
- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.
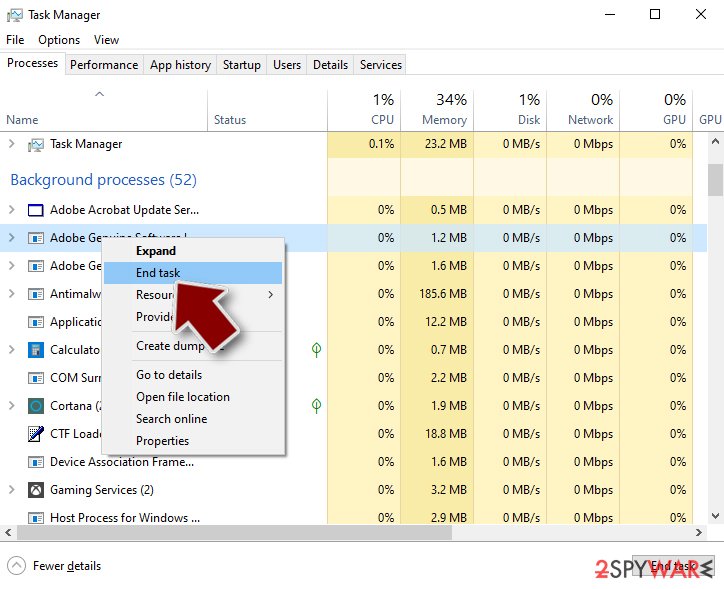
- Go back to the process, right-click and pick End Task.
- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
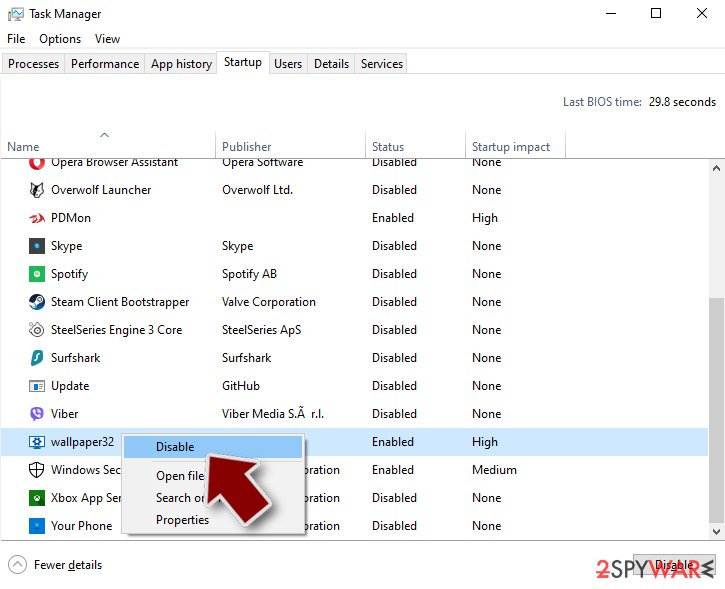
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.
Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
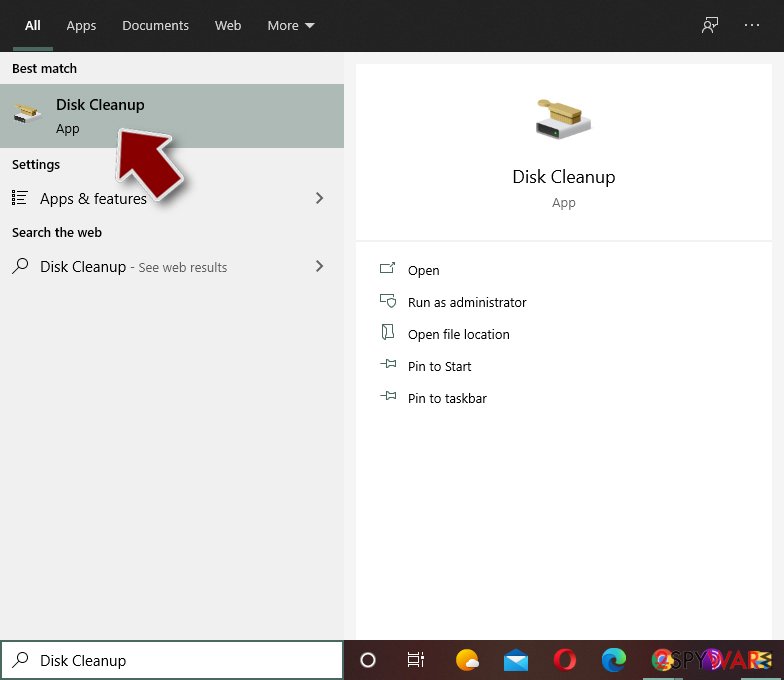
- Type in Disk Cleanup in Windows search and press Enter.
- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.
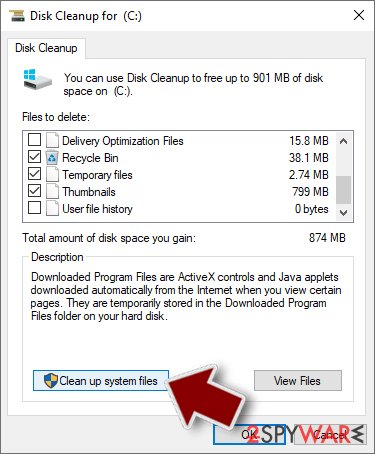
- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Jan 2021 · not reviewed since
Tutorial for DKOM.doublepulsar removal and system repair
If you feel that your computer performance is down, you see an abnormal amount of ads, new programs are installed, the internet connection is extremely slow, that might mean that your device is infected with a trojan or other kind of malware. You have to take action immediately and perform DKOM.doublepulsar removal correctly.
There are several steps that you have to do in order to eliminate this backdoor fully. It consists of the following steps:
Once you remove DKOM.doublepulsar from your device, you should also take care of your system stability after infection elimination. Malware is developed to disable certain features by making changes to system files and settings. You can fix all system irregularities by performing a system tune-up with powerful system repair tools such as the app or similar software.
[GI=method-1]In case you have other malware installed on your machine through the backdoor, you can use Safe Mode to eliminate all the infections without disruptions in Safe Mode:
- Disconnect your PC from the network if it is connected to one.
- Restart your computer.
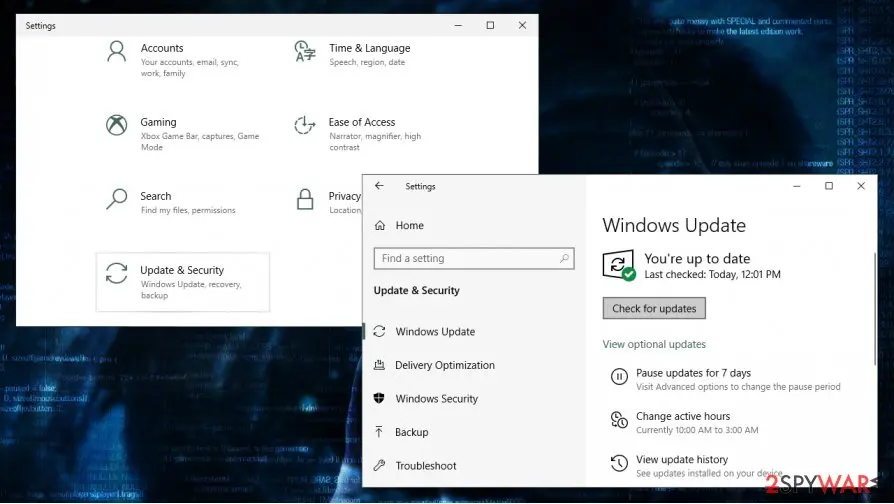
- Update Windows to the latest version. You can do that by right-clicking on Start and then selecting Settings > Update & Security > Windows update and clicking Check for updates.
- Wait till the system is fully updated, and patches applied.
- Reboot the machine and perform a full system scan with , , or another robust security application.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed DKOM.doublepulsar in the list of installed apps, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
Questions about DKOM.doublepulsar
What is DKOM.doublepulsar and why is it on my PC?
DKOM.doublepulsar is a program that was installed on the PC, most likely together with something else you downloaded. Free software sites and many installers add extra programs on setup pages with pre-ticked boxes, so the extra install looks like your choice even though nobody read the page.
Check the install date in Settings, Apps, Installed apps: the program you installed that day is the probable carrier. If you do not need DKOM.doublepulsar, uninstall it. If it belongs to your hardware or to a program you use, search its exact name and publisher first, because drivers and their tools can have unfamiliar names.
DKOM.doublepulsar will not uninstall. What can I do?
First restart the PC and try again, because the program may have been running and locked its own files. If the uninstaller is missing or fails, start Windows in Safe Mode, where most third-party programs do not start, and remove DKOM.doublepulsar from Installed apps there.
If it still refuses, delete its startup entry and its scheduled task, restart, and try once more. A program that actively prevents removal is behaving like malware, so finish with a Microsoft Defender offline scan. Avoid third-party uninstallers offered on search ads; several of them are unwanted programs themselves.
Is a trojan infection worth reporting to the police?
If there was harm, yes. Unauthorised payments, accounts used for fraud, blackmail or a remote session during a scam call all belong in a report, and banks often ask for its reference number before they refund anything.
If antivirus caught DKOM.doublepulsar before it ran and nothing was misused, there is nothing to report. Keep the evidence anyway:
- protection history
- the original download
- the dates
Businesses may also have to notify a data protection authority if personal data could have been accessed.
Is DKOM.doublepulsar a known trojan?
Not as a documented family, at least not yet. What is known is the visible sign, DKOM.doublepulsar in the list of installed apps, which matches a hidden program working for someone else.
New threats are often seen by victims weeks before researchers publish anything about them. Treat DKOM.doublepulsar as you would any trojan:
- remove what starts it
- run an offline scan
- change passwords from another device
If a scan reports a detection name, keep it; it usually reveals the family and whether it is known to download other malware. We update this guide when an analysis appears.
Should I reset my PC because of DKOM.doublepulsar?
Only if the signs point to deeper access. Reset when you see DKOM.doublepulsar in the list of installed apps again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
Why didn't my antivirus stop DKOM.doublepulsar?
New trojan builds are packed and changed often so that signatures do not match, and some are signed with stolen or bought certificates. Many arrive inside password-protected archives, which scanners cannot open until you extract them.
Some downloads also tell the user to turn off the antivirus "because it gives false alarms", a common line in cracked software instructions. Keep real-time protection on, never disable it for an installer, and run the offline scan whenever you suspect something slipped through.
Can a normal remote support program be a backdoor?
Yes. Tools such as AnyDesk, TeamViewer and ScreenConnect are legitimate, but whoever controls the account behind them controls the PC. Scammers install them during fake support calls, and some trojan campaigns install them silently because antivirus programs do not flag a genuine, signed product.
If you find one you did not set up, uninstall it, check Startup apps for related entries and change passwords from another device. If money or accounts were involved, call your bank and report the incident.
How dangerous is DKOM.doublepulsar?
Treat it as serious until proven otherwise. The visible sign is DKOM.doublepulsar in the list of installed apps, and programs that behave this way often have more abilities than they show:
- copying passwords
- downloading other malware
- giving remote access
Its family is not known yet, so nobody can say which of these it uses. The good news is that the response is the same in every case and takes about an hour:
- cut the network
- remove the startup entry
- run an offline scan
- change passwords from a clean device
If someone had remote control, a full reset is safer.
Can DKOM.doublepulsar spread to other devices on my network?
Most trojans aimed at home users stay on the PC they infected, but an attacker with remote access can look at the network, open shared folders and try passwords on other devices. Loaders sometimes deliver worms or ransomware that do spread.
Disconnect the PC while cleaning, run a full scan on other Windows PCs, change the router's admin password and the Wi-Fi password if they were saved on the infected PC, and update the router's firmware. If other PCs show the same detection, treat them as infected too.
Will Fortect remove DKOM.doublepulsar?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For DKOM.doublepulsar, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: DoublePulsar (read October 6, 2026)
- Lesvirus: LesVirus (read October 6, 2026)
- Cso: 9 types of malware and how to recognize them (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)