
TA505 ServHelper and FlawedGrace RAT: 2026 Guide
- TA505 ServHelper and FlawedGrace in 2026: the short answer
- Timeline: from ServHelper to the MOVEit data theft
- What changed since 2019
- Risks around the TA505 name (our analysis)
- Steps to protect a business from this kind of attack
- What is still unknown
- Our original 2019 report
- First targeted attacks by TA505 were noticed in November 2018
- ServHelper is a new malware and is being actively developed by cibercriminals
- Related guides on 2-Spyware
TA505 ServHelper and FlawedGrace in 2026: the short answer
ServHelper and FlawedGrace are two pieces of malware that the TA505 group spread by phishing email in late 2018. ServHelper is a Delphi backdoor that gives the attacker remote desktop access, and FlawedGrace is a large C++ remote access trojan that ServHelper can download.[1] We found no 2026 report of a new ServHelper campaign, so treat both names as a historical case study of how a ransomware crew pivots.
TA505 itself did not go away. The Canadian Centre for Cyber Security describes it as a group active since at least 2014 that runs financial fraud, phishing and ransomware work, and that is linked to Cl0p.[6] In 2023 the group, also called the CL0P Ransomware Gang, exploited the MOVEit Transfer flaw CVE-2023-34362 to steal data.[7] That is the more important lesson of this story today.
| Item | What we can confirm |
|---|---|
| ServHelper | Backdoor written in Delphi; a tunnel variant sets up reverse SSH tunnels to the infected host's RDP port[1] |
| FlawedGrace | Large C++ remote access trojan; first seen in November 2017 and kept a low profile[1] |
| First ServHelper campaign | November 9, 2018, thousands of emails to financial businesses[1] |
| Delivery | Word, Publisher or PDF attachments with macros or malicious links[1] |
| TA505 status | Linked to Cl0p; active since at least 2014 per the Canadian Cyber Centre[6] |
| New ServHelper news in 2026 | We found none |
Timeline: from ServHelper to the MOVEit data theft
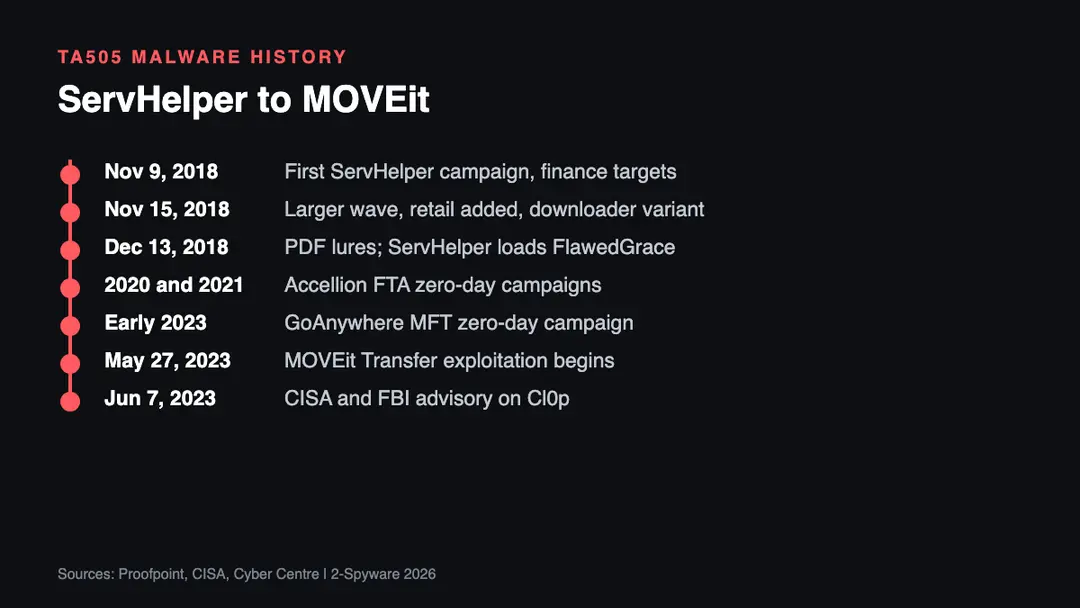
| Date | Event |
|---|---|
| November 9, 2018 | Proofpoint sees the first ServHelper campaign, aimed at financial businesses[1] |
| November 15, 2018 | A much larger campaign also targets retail and uses the downloader variant[1] |
| December 13, 2018 | PDF attachments with links appear, and ServHelper also downloads FlawedGrace[1] |
| 2020 and 2021 | TA505 runs zero-day campaigns against Accellion File Transfer Appliance devices[6] |
| Early 2023 | TA505 runs a zero-day campaign against Fortra GoAnywhere MFT servers[6] |
| May 27, 2023 | Exploitation of MOVEit Transfer vulnerability CVE-2023-34362 begins[7] |
| June 7, 2023 | CISA and the FBI publish a joint advisory on the Cl0p gang[7] |
What changed since 2019
The 2019 report described a crew that was moving from crypto ransomware to backdoors, RATs and info-stealers. The record since then shows a different pattern. According to the Canadian Centre for Cyber Security, TA505 later ran zero-day campaigns against file transfer products, first Accellion devices in 2020 and 2021, then Fortra GoAnywhere servers in early 2023.[6]
The biggest step came in May 2023. CISA and the FBI wrote that the Cl0p gang, also known as TA505, exploited a previously unknown SQL injection flaw in Progress Software's MOVEit Transfer file transfer tool, starting on May 27, 2023. They planted a web shell named LEMURLOOT to steal data from the underlying databases.[7] The Canadian Centre adds that the group claimed on June 6, 2023 it would publish data of hundreds of companies if ransoms were not paid.[6]
So the ServHelper era was one stage in a longer story. The same operators that sent Word macros in 2018 later went after internet-facing software that many companies run. We did not find a recent public report of ServHelper or FlawedGrace in use, which does not prove they are gone.
Risks around the TA505 name (our analysis)
Our analysis of the pattern is that old malware names keep attracting search traffic, and that attracts fake help.
- Fake removal tools. Pages that promise to remove "ServHelper" or "FlawedGrace" with a paid scanner you never heard of. Use a known security product and our virus removal guides.
- Macro lures that look like invoices. The 2018 emails used Word and Publisher files that asked to enable macros.[1] The same trick still works on tired staff.
- Open remote desktop. ServHelper's tunnel variant aimed at the RDP port 3389.[1] CISA still advises strict limits on RDP use.[7]
- Ransom follow-up emails. After a data theft, criminals may email employees or customers with threats. Do not pay or reply before checking with the affected company.
Steps to protect a business from this kind of attack
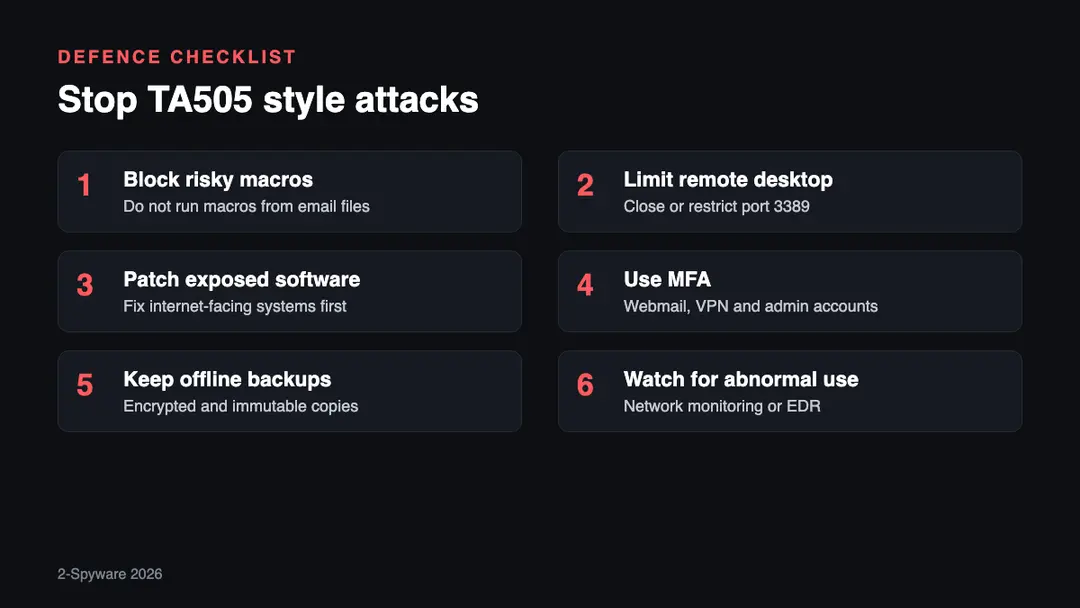
1. Block risky macros. Do not let staff run macros from email attachments. The 2018 campaigns depended on Word and Publisher macros.[1]
2. Limit remote desktop. CISA advises strictly limiting RDP and other remote desktop services, and blocking common remote access ports at the network edge.[7]
3. Patch exposed software. CISA advises prioritizing patches for known exploited flaws in internet-facing systems, such as file transfer tools.[7]
4. Use multifactor sign-in. CISA recommends multifactor authentication for all services where possible, especially webmail, VPNs and critical accounts.[7]
5. Keep offline backups. CISA advises a recovery plan with offline backups that are regularly maintained, encrypted and immutable.[7]
6. Watch for abnormal activity. Use network monitoring or endpoint detection to spot odd traffic, new accounts and unexpected tools.[7] You can also check whether staff emails leaked with our leak check.
What is still unknown
- Whether ServHelper or FlawedGrace are still used. We found no public 2026 report either way.
- Who writes FlawedGrace. The old report says the coding style suggests it was not written by the ServHelper authors, and we found no later attribution.
- How many organizations were hit by the 2018 campaigns. Proofpoint described thousands of emails, not a victim count.[1]
Our original 2019 report
The text below is our report as first published in 2019. We keep it unchanged for the record; the sections above bring it up to date.
Security researchers from Proofpoint have published a report[1] that detailed the new malware string that is connected to the TA505 group. Experts observed two new malware strains that started being distributed last year with the help of phishing emails: two variants of ServHelper backdoor and FlawedGrace remote access trojan.[2]
According to research, several phishing campaigns were launched at the end of 2018 and targeted banks, restaurants, and retail businesses. The malicious emails contained MS Word or PDF files that, once launched with macro function, would download and install malware on the victims' computers.
TA505 has been one of the most active threat actors in the past few years, responsible for GlobeImposter[3] and Locky ransomware. Nevertheless, researchers observed the group shifting from crypto viruses to backdoor trojans, RATs and info-stealers. Just as the mentioned Locky, the newly-discovered campaigns were using the Necrus botnet for the distribution.
First targeted attacks by TA505 were noticed in November 2018
Proofpoint reported that the new malware family ServHelper (the name was based on the file name associated with malware – ServHelper.dll) was first encountered on 9th of November when bad actors sent thousands of emails to financial businesses. The emails contained MS Word or Publisher attachments that used macro features to download the payload of ServHelper that used "tunnel" variant.
Researchers then noticed a much bigger campaign on 15th of November, which now also targeted the retail industry with attachments that used .doc, .pub or .wiz. file extensions. Similarly to the previous operation, malicious documents used macros to enable ServHelper, but this time it did not have the tunneling feature, and replaced it with a "downloader."
The final campaign was executed on December 13th. This time, cybercriminals relied on PDF attachments with malicious links in addition to standard MS Word files. The significant difference is that this variant of ServHelper malware also downloaded an additional payload FlawedGrace, which was first observed in November 2017, and kept a low profile for the next two years.
ServHelper is a new malware and is being actively developed by cibercriminals
According to Proofpoint researchers, ServHelper is a new malware family that is being improved by adding new features and commands with each new phishing campaign. It is written in Delphi programming language, it uses the tunnel or downloader variant, as explained by security experts:[1]
As noted, there are two distinct variants of ServHelper: a "tunnel" variant and a "downloader" variant. The "tunnel" variant has more features and focuses on setting up reverse SSH tunnels to allow the threat actor to access the infected host via Remote Desktop Protocol (RDP). Once ServHelper establishes remote desktop access, the malware contains functionality for the threat actor to "hijack" legitimate user accounts or their web browser profiles and use them as they see fit. The "downloader" variant is stripped of the tunneling and hijacking functionality and is used as a basic downloader.
The malware posses multiple different features, such as:
- maintains the keep-alive[4] type of functionality;
- connects the C&C to the host's RDP[5] port (3389) with the help of reverse SSH tunnel;
- copies Firefox and Chrome web browser profiles;
- runs an executable downloaded from a specific URL;
- removes the malware payload;
- many other commands.
Unlike ServHelper, the secondary payload FlawedGrace remote access trojan is written in C++ and is quite difficult to crack:
It is a very large program and makes extensive use of object-oriented and multithreaded programming techniques. This makes reverse engineering and debugging the malware both difficult and time consuming. The coding style and techniques suggest that FlawedGrace was not written by the same developer as ServHelper.
Upon the inspection of the campaigns and malware samples, researchers concluded that ransomware authors are shifting from ransomware to information stealers, RATs and similar malware that can remain on the system unnoticed for longer and bring more benefits for threat actors.
Related guides on 2-Spyware
Frequently asked questions
What is ServHelper?
ServHelper is a backdoor written in Delphi that Proofpoint linked to TA505 in late 2018. Its tunnel variant sets up reverse SSH tunnels so the attacker can reach the infected computer through its RDP port, and its downloader variant fetches more malware.{1} We found no 2026 report of a new campaign using it.
What is FlawedGrace?
FlawedGrace is a remote access trojan written in C++ that Proofpoint saw first in November 2017. Researchers called it a very large program that is difficult to reverse engineer.{1} In the December 13, 2018 campaign, ServHelper downloaded it as an extra payload.
Who is TA505?
TA505 is a cybercrime group that the Canadian Centre for Cyber Security says has been active since at least 2014. It has been tied to the Dridex banking trojan, Locky ransomware and the Cl0p ransomware.{6} CISA says the CL0P gang is also known as TA505.{7}
Is the TA505 backdoor a rat backdoor?
Yes, in effect. A backdoor lets an attacker enter a computer later, and a remote access trojan, or RAT, lets them control it. ServHelper gave remote desktop access, and FlawedGrace worked as a full RAT.{1} Both are used to steal data or prepare ransomware.
How did TA505 spread ServHelper?
It used phishing emails with Word, Publisher or PDF attachments. Word and Publisher files used macros to download the payload, and the December 2018 wave added PDFs with malicious links.{1} Blocking macros from email is the simplest defence.
What did TA505 do after ServHelper?
According to the Canadian Centre for Cyber Security, it ran zero-day campaigns against Accellion devices in 2020 and 2021 and Fortra GoAnywhere in early 2023.{6} CISA says Cl0p began exploiting MOVEit Transfer on May 27, 2023.{7}
Sources
- Proofpoint. Threat Insight
- CompariTech. Tech researched, compared and rated
- 2-spyware. Cybersecurity news and articles
- Stackpath. American content delivery network and cloud service (no longer online)
- SC Media. Cybersecurity News, analysis and Product Reviews
- Canadian Centre for Cyber Security
- CISA
Log in to comment
No comments yet. Be the first.