
Are Facebook Links Safe in 2026? Link Shim and Spoofing
- Facebook link safety in 2026: the short answer
- Timeline of Facebook link protection and spoofing
- What changed since 2017
- Risky Facebook links to watch for (our analysis)
- How to check a Facebook link and what to do if you clicked
- What is still unknown
- Our original 2017 report
- How spoofing links on Facebook works
- Facebook does not admit that there's a problem
- Security tips for Facebook users
- Related guides on 2-Spyware
Facebook link safety in 2026: the short answer
Most links on Facebook are safe, but you cannot judge a link by its preview. The title, picture and address shown under a post come from tags on the target page, and our original report below explains how attackers abused them to show a fake YouTube address.[2] Facebook's Link Shim adds a check when you click, not a guarantee.[7]
The stakes are higher than in 2017. The FTC says people reported $2.1 billion lost in 2025 to scams that started on social media, and more money was lost to scams that started on Facebook than on any other platform.[9] A safe-looking link is still the most common first step.
| Question | Answer in 2026 |
|---|---|
| What is Link Shim? | Facebook's redirect that checks an outside link when you click it[6][7] |
| Does it stop every bad link? | No. It checks against known bad lists, so new scam pages can slip through[7] |
| Can a preview be faked? | Yes. Researchers showed the shown address can differ from the real one[2] |
| Can a link alone infect a phone? | Rarely. The risk is the page that asks for logins, payments or downloads |
| Where do most losses start? | Facebook led all platforms for reported scam losses in 2025[9] |
| Best check | Long-press or hover to see the real address before you open it |
Timeline of Facebook link protection and spoofing
| Date | Event |
|---|---|
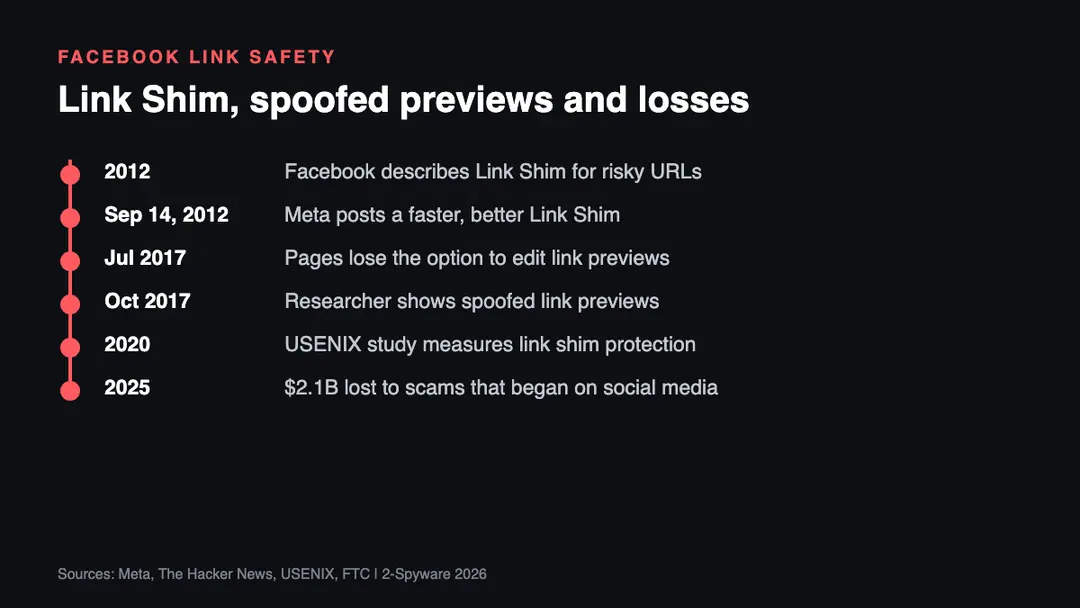
| 2012 | Facebook's Site Integrity team describes Link Shim to warn about spammy or malicious links[3][6] |
| September 14, 2012 | Meta engineers publish a faster, updated Link Shim[6] |
| July 2017 | Pages can no longer edit link preview details before publishing[2] |
| October 2017 | Researcher Barak Tawily shows that link previews can be spoofed[2] |
| 2020 | A USENIX Security paper evaluates the security role of link shimming[8] |
| 2025 | $2.1 billion reported lost to scams that started on social media[9] |
What changed since 2017
Link Shim still works the way it was designed. Every time a link is clicked, Facebook routes it through its own address and checks the target at click time rather than when the post is shown, so a page that turns bad later can still be blocked.[7] That is why links on Facebook often start with an l.facebook.com address.
Researchers have measured how much this helps. A 2020 USENIX Security paper found that link shimming serves real security purposes beyond analytics, mainly by protecting users from visiting suspicious destinations, and that it can protect users even as older browsers fade away.[8] It is still a filter based on known bad sites, not a full guarantee.
The scams changed more than the tools. Fake shopping ads, investment pitches and romance contacts now cause most social media losses, and shopping scams were the most reported type in 2025.[9] We found no public statement from Meta about whether it now checks that a preview address matches the real landing page, the flaw described below.[2]
Risky Facebook links to watch for (our analysis)
- Video links from friends in Messenger with text like "is this you?" that lead to a fake login page.
- Previews that show a famous site such as YouTube, while the real address after the click is a different domain.[2]
- Ads for deals that look too good, which open copycat shops. Shopping scams were the top reported social media scam in 2025.[9]
- Links that ask you to log in to Facebook again to see content. Facebook does not need a second login for a normal post.
- Short links and redirect chains that hide the final address until the page loads.
How to check a Facebook link and what to do if you clicked
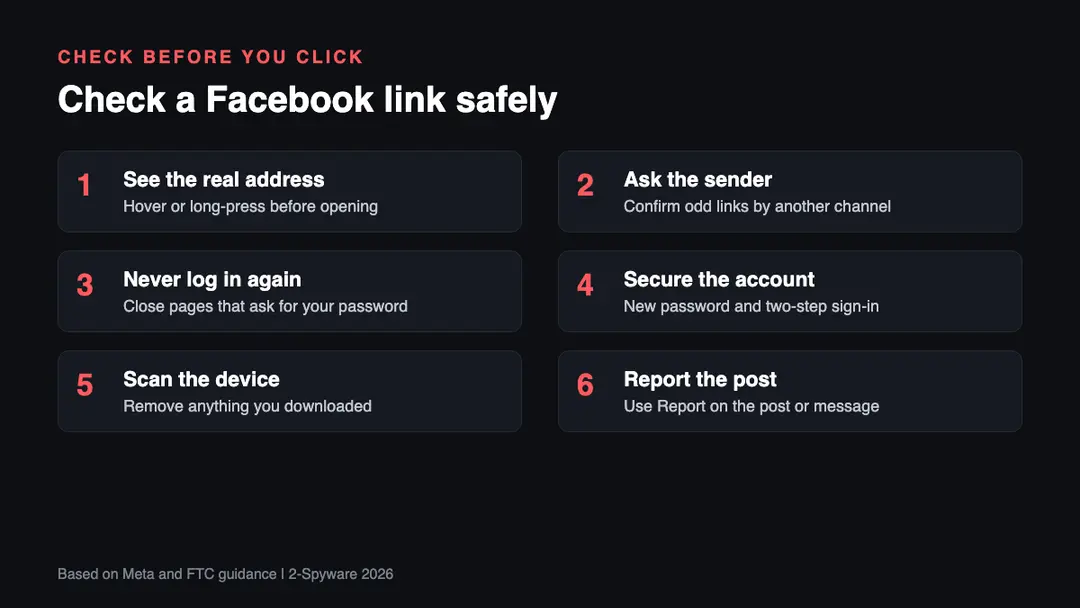
1. See the real address. Hover over the link on a computer or long-press it on a phone. If the domain differs from the preview or looks odd, do not open it.[2]
2. Ask the sender. If a friend sends a strange video or link, ask them by phone or another app whether they meant to. Hacked accounts send these links without the owner knowing.
3. Never log in again. Close any page that asks for your Facebook password after a click. That is the main sign of a phishing page.
4. Secure the account. If you typed your password, change it from the real Facebook app or site, turn on two-step sign-in and log out other sessions. Check our leak check for other exposed accounts.
5. Scan the device. If the page made you download a file or extension, remove it and run a security scan. Our virus removal guides explain how.
6. Report the post. Use Report on the post, ad or message so Link Shim and Facebook's lists can learn the address. See how to report phishing for other places to report.
What is still unknown
- Whether Facebook now checks that the preview address matches the landing page. We found no Meta statement on that in the sources we read.
- How many malicious links Link Shim blocks each year. Meta has not published a recent figure that we found.
- How much of the 2025 social media losses began with a clicked link rather than a message or ad. The FTC does not split the data that way.[9]
Our original 2017 report
The text below is our report as first published in 2017. We keep it unchanged for the record; the sections above bring it up to date.
Fake news,[1] click-fraud and phishing campaigns are the part of Facebook's community. Unfortunately, the world's largest social network is no longer a safe place to be. You cannot trust every link on timeline and message received on Messenger. Cybercriminals and crooks managed to launch various illegal activities in order to reach users and steal their personal information.
During the past several years, numerous versions of the Facebook virus appeared. However, it seems that this cyber threat will not go away anytime soon. Researchers have just discovered a flaw that allows spammers or attackers spoof links shared on Facebook. Therefore, you should not click on each exciting YouTube or other links your friends shared because it might lead to dangerous websites.
How spoofing links on Facebook works
Each link posted on Facebook has a few main components: the title, description, image and URL address. It doesn't matter if you share a link to the article or video, these elements will appear in the post. Not so long ago pages were able to edit this content before hitting the "Publish" button. However, due to phishing attacks and fake news, this feature was disabled in July 2017.
However, Barak Tawily, a 24-year-old security researcher, discovered that evil-minded people can still post malicious links without being banned from Facebook. Spammers can post spoofing URLs by taking advantage of how the social network fetches link previews.
When a user shares a link, the social network scans it and looks for the Open Graph meta tags. In order to display link's URL, image, description and other entries, Facebook scans for "og:url," "og:image" and "og:title" tags. However, the problem is that social network does not verify if the link in "og:url" tag is the same as the landing page.
Therefore, spammers, scammers, and other crooks can take advantage of this flaw. They can enter their preferred URL address and hide it under legit website's address. For this reason, users can get easily tricked into clicking a fake YouTube link that leads to tech support scam, phishing or even malicious website.
Facebook does not admit that there's a problem
According to the media,[2] Facebook does not agree that there's a flaw. The social media giant tells that they use "Link Shim"[3] system which protects users from phishing attacks and blocks malicious links. However, security experts doubt that this security system can work as good as Facebook claims. The issue with link verification allows attackers including spoofing links that might be hard to detect for the "Link Shim."
Indeed, the reports about new Facebook video virus versions that spread on social network or Messenger prove that there're some security vulnerabilities. Apart from spams and ridiculous scams asking to tell friends not to accept friend requests from hackers,[4] malicious viruses, such as Locky ransomware,[5] has also managed to step inside Facebook. Therefore, users have to stay vigilant in order not to lose their files or personal information.
Security tips for Facebook users
It might be hard to identify which link on the Timeline is malicious. However, you should always be vigilant and pay attention to these details:
- Hover over the link without clicking it in order to see the URL address it will redirect. If it has random words or unusual end of the domain, do not click it.
- Strange sentences, grammar or word of use mistakes also warn about potentially dangerous content, especially if a user shares a link from a popular website.
- Click-bait headlines, shocking or entertaining news are often the ones that are dangerous to click.
- If a person who is not active on Facebook starts sharing strange content, it's likely that his or her account has been hacked and spreads potentially dangerous content.
- If you receive a video or other link on Messenger, always ask a person if he or she wanted to share this content with you. It's possible that this message was sent without user's knowledge.
Related guides on 2-Spyware
Frequently asked questions
What is Link Shim on Facebook?
Link Shim is the system Facebook uses to check outside links. When you click a link, Facebook first routes it through its own address and checks the destination against its list of malicious sites, then warns you or blocks it if needed.{6}{7} That is why many Facebook links start with l.facebook.com.
Are Facebook links safe?
Most are, but not all. Link Shim checks links at click time against known bad sites, which cannot catch every new scam page.{7} Previews can also show a different address than the real one.{2} Check the real address and be careful with any page that asks for logins or payments.
Can a Facebook link be a virus?
A link by itself is not a virus, and simply opening one rarely infects a modern phone or computer. The danger is what the page asks you to do next: enter your password, pay, install an app or a browser extension. Refuse those requests and you avoid most of the risk.
How do I know if a Facebook link is safe?
Look at the real address before opening it. Hover over the link on a computer or long-press it on a phone, and compare the domain with the preview.{2} Be wary of short links, misspelled domains, and messages that push you to act fast.
I clicked on a Facebook virus link. What should I do?
Close the page and do not enter anything. If you typed your Facebook password, change it from the real app, turn on two-step sign-in and log out other sessions. If something downloaded, delete it and scan the device. Then tell your friends not to open links sent from your account.
How can I check a link shared on Facebook?
Copy the link and look at its domain before you open it. Facebook's own Link Shim checks it again when you click.{7} If the domain is unknown, search for its name plus the word scam, and report suspicious posts with the Report button.
Sources
- Forbes. Business, investing, technology, entrepreneurship, leadership, and lifestyle website
- The Hacker News. Cyber security and hacking news
- Facebook Security. The official website
- Ugetfix. How to fix a computer
- Esolutions blog. Latest cyber security news (no longer online)
- Engineering at Meta
- ZDNET
- USENIX Security
- Federal Trade Commission
Log in to comment
No comments yet. Be the first.