
APPLE SECURITY BREACH on Mac: what it is and how to remove it
Apple security breach scam is a popup that might be encountered after accessing a malicious website on the internet. Upon entry, visitors are shown a brief notification that allegedly comes from Apple support - it is claimed that the security system has crashed and that personal information such as pictures is being transferred. This page covers it on macOS.
Facts checked October 7, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
An automatic scan checks installed programs, startup items and browser extensions for anything that came with APPLE SECURITY BREACH.
Do it yourself · free Remove APPLE SECURITY BREACH yourself 7 steps, about 21 minutes, no software needed.
Start the steps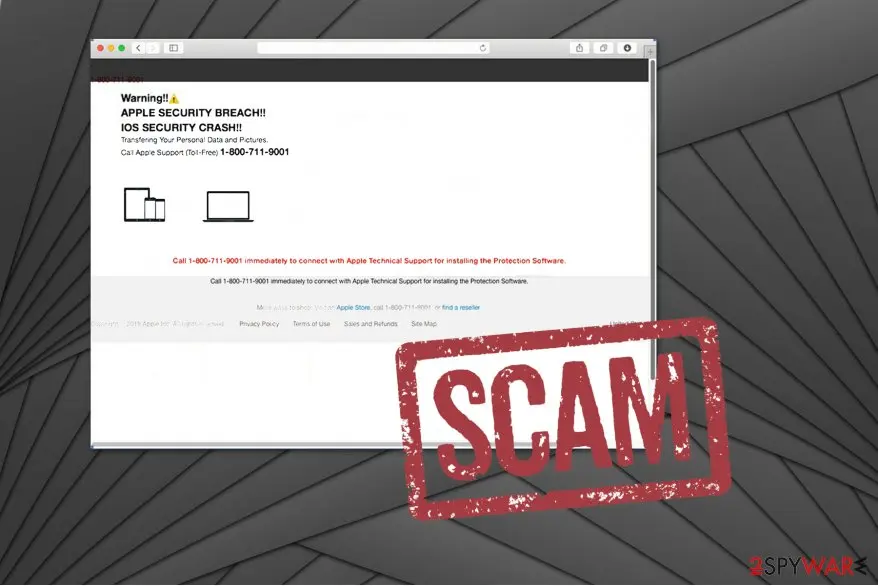
APPLE SECURITY BREACH: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | APPLE SECURITY BREACH |
| Type | Loader |
| Symptoms | An unknown program in Installed apps |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 3 more facts
| Evidence | 4 write-ups by security sites; details still limited |
|---|---|
| First seen | 17 December 2020 |
| Facts checked | 7 October 2026 |
What APPLE SECURITY BREACH does on an infected Mac
From our report of Dec 2020 · not reviewed since
APPLE SECURITY BREACH - an online scam that opens your Mac's camera automatically
Apple security breach scam is a popup that might be encountered after accessing a malicious website on the internet.
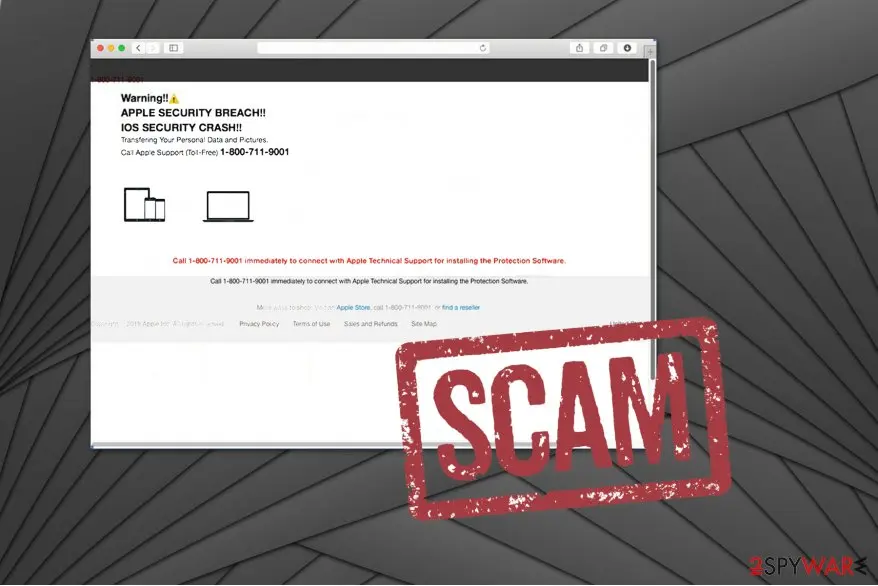
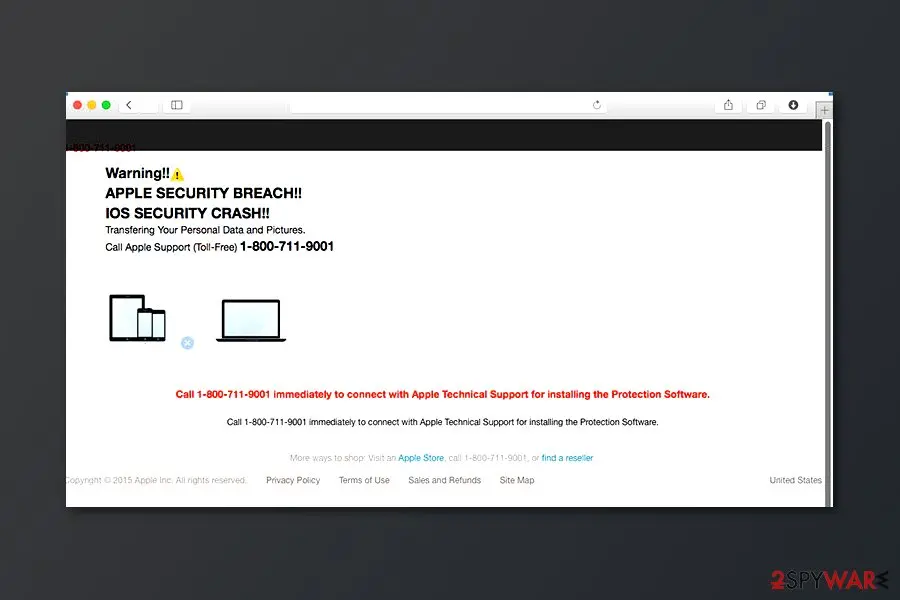
Upon entry, visitors are shown a brief notification that allegedly comes from Apple support - it is claimed that the security system has crashed and that personal information such as pictures is being transferred. The fake alert then proceeds with a statement that claims a full computer lockout and urges users to call the alleged tech support at 1-800-711-9001 (can vary) to resolve the seemingly frightening situation.
Crooks behind the Apple security breach scam are trying to manipulate visitors by intimidating them and scaring them. Besides displaying false claims, the website also shows the camera view, and opens a fake FaceTime login screen.
Warning: No matter what you do, never call the provided phone number, as the attackers might ask you to grant permission to access your Mac remotely and steal your credentials or install data-tracking malware.
Simply ignore the fake virus alert and close down the website displaying it immediately. While what the message said is completely falsified, persistent redirects to scam and phishing sites might indicate adware infection, so this should be investigated. For more details, please check the bottom section below.
Usually, APPLE SECURITY BREACH pop up shows up in the browser when some potentially unwanted program (PUP) gets installed on the device. Typically, redirects to the tech support scam website are triggered by adware. This ad-supported application can modify Chrome's, Firefox's, or Safari's settings in order to open new browser tabs and show a fake message.
The Apple security breach scam website claims that there is an iOS security crash that might compromise your personal data and pictures. Likewise, the victims are urged to call via toll-free 1 800 711 9001 number to Apple Support:
The criminals also encourage to call 1-800-711-9001 immediately to connect with Apple Technical Support for installing the Protection Software several times. However, it's just one of the phone numbers used by scammers. People report that they received similar pop-ups with the following numbers:
Note that Apple security breach popup might display a dozen other different phone numbers and warn about other serious issues. However, we do not suggest trusting the offenders since your computer is not corrupted. This is merely a redirect to a phishing site that is most likely to be used to swindle money from you by purchasing an expensive and useless antivirus tool.
Instead, you should get professional security software like to uninstall the adware and remove APPLE SECURITY BREACH pop-up. The elimination procedure will take only several minutes, and shortly after, you will no longer receive any scam messages. Besides, can be used to perform further checks to ensure the system is working as well as before.
Additionally, if you call for the so-called Apple Technical Support, the criminals might ask you to let them access your computer remotely to fix the "iOS security crash." In reality, they would probably infiltrate other high-risk computer infections to encourage you even more to purchase various third-party antivirus tools.
Note, this Apple scam message is not real, and the original support number is not provided elsewhere than on the original website. Therefore, if you do not want to receive any fake pop-ups, start APPLE SECURITY BREACH removal right now. You can find the manual elimination instructions just below this article.
- 1-844-749-1071
- 1-800-457-5916
- 1-800-235-66
From our report of Dec 2020 · not reviewed since
Apple security breach scam targets iPhone users too
APPLE SECURITY BREACH pop up might also show up on your iPhone too.
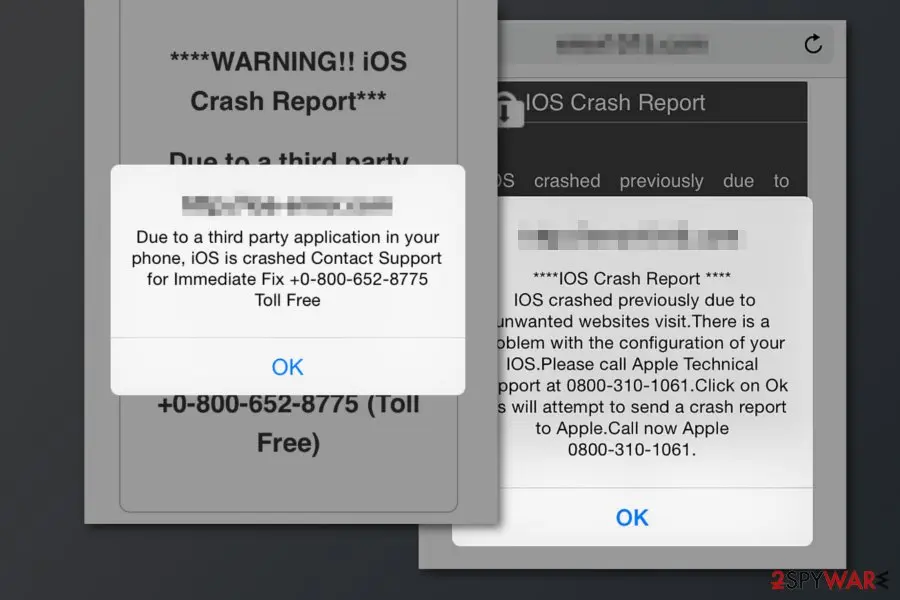
The mobile version of the tech support scam usually targets the Safari web browser. However, the tech support scam site displays a similar warning message:
Just like the desktop version of the scam, this one also uses a bunch of fake support phone numbers, including 1-800-556-2901, 0800-310-1061, 0-800-652-8775, etc. It goes without saying that you should not trust this pop-up. Just leave this website and reset Safari to stop redirects to the scam website. If you still receive this fake alert, you should use mobile antivirus software to remove APPLE SECURITY BREACH virus automatically.
From our report of Dec 2020 · not reviewed since
Redirects to scam website begin after silent infiltration of adware
Most of the potentially unwanted programs are infiltrated on your computer when you recklessly download free applications.
Developers of adware programs bundle their bogus products with regular software to benefit from people who rush to finish the download/installation process.
Once the user aims to install regular programs with Quick or Recommended settings, they are unable to identify the potentially unwanted program which is bundled together. Therefore, you should always install software only with Advanced or Custom parameters.
Additionally, it is necessary to do not skip steps and search for any suspicious marks, which might permit the installation of adware . If you find any, un-tick them right away and employ a reliable security system to examine your computer for cyber threats.
From our report of Dec 2020 · not reviewed since
More from our earlier report on APPLE SECURITY BREACH
- Google Chrome, Mozilla Firefox, Safari
- 1 800 711 9001 1-844-749-1071 1-800-457-5916 1-800-235-66 1-866-855-3442 1-800-556-2901 0800-310-1061 0-800-652-8775
- Call Apple Support (Toll-Free) 1-800-711-9001
- Call Apple Support (Toll-Free) 1-866-855-3442 Call 1-866-855-3442 immediately to connect with Apple Technical Support for installing the Protection Software.
How to remove APPLE SECURITY BREACH
How to remove APPLE SECURITY BREACH from a Mac
Start with the passwords and crypto, from another device: a stealer copies them in seconds.
Then clean the Mac, or erase it.
Step 1: Change passwords from another device first
If you pasted a command into Terminal or opened a downloaded file from APPLE SECURITY BREACH, assume the passwords saved in the browsers and in Keychain on this Mac are known to the attacker.
From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and work accounts, and sign out of all other sessions on each one.
Move any cryptocurrency to a new wallet created on a clean device, because a seed phrase that was stored on this Mac is compromised. Do this before cleaning the Mac: cleaning does not undo the theft.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Quit what is running that you do not recognize
Open Activity Monitor (in Applications > Utilities, or search for it with Command + Space).
In the CPU or Network tab, look for a process you did not install or whose name is random, select it, click the stop button (the octagon with an X) and choose Quit or Force Quit.
Note the name first: you will look for the same name in the next steps. Malware that comes back after a restart is handled in the next two steps.
Step 3: Remove unknown login items and background items
Open System Settings > General > Login Items & Extensions. Under Open at Login and Allow in the Background, switch off or remove anything you do not recognize, especially items whose developer is shown as an unknown name or that appeared on the day you ran the command.
Then open Finder, choose Go > Go to Folder and check
~/Library/LaunchAgents,/Library/LaunchAgentsand /Library/LaunchDaemons for property list (.plist) files you did not add. Drag suspicious ones to the Bin, then restart the Mac.Step 4: Delete apps and downloads you did not intend to install
Open the Applications folder and your Downloads folder. Drag any app you did not install, and any disk image (
.dmg), installer (.pkg) or archive (.zip) that came from APPLE SECURITY BREACH or a site you do not trust, to the Bin, then empty the Bin.Also check
~/Library/Application Supportfor a folder with the same name as the app you removed.Step 5: Check the browsers for extensions and changed settings
In Safari open Settings > Extensions and General (homepage). In Chrome open
chrome://extensions, in Firefoxabout:addons.Remove any extension you did not add, and reset the homepage and search engine if they changed. Browsers hold saved passwords and cookies, which is why the password step comes first.
Step 6: If it was an infostealer, erase and reinstall macOS
Stealers copy data and often leave persistence you cannot be sure you found.
The only complete fix is to back up your personal files only (documents, photos, not apps or settings), then open System Settings > General > Transfer or Reset > Erase All Content and Settings, or use macOS Recovery to erase the disk and reinstall macOS, as Apple describes in its support articles.
Restore only your files afterwards, and install apps again from their official sources.
Step 7: Report it and watch your accounts
Report the site and the command to the authorities in your country, and tell your bank if any card was saved in a browser or in Keychain.
Over the next weeks watch your e-mail, bank and exchange accounts for sign-ins and transfers you did not make. Keep the notes you made, such as the process names and the file dates, in case a bank or the police ask for them.
Full procedure with screenshots: Report a cyber attack or scam to the authorities
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
Uninstall from Windows 10/8:
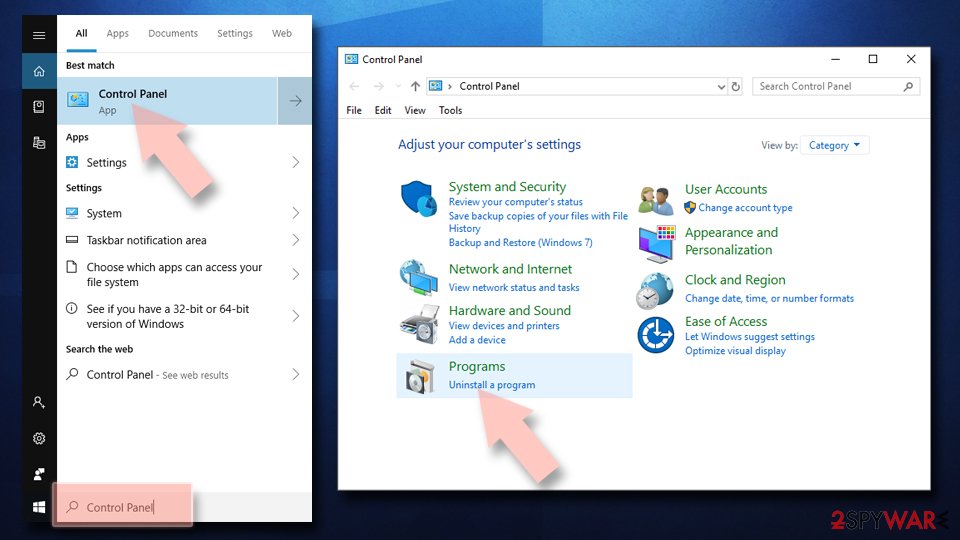
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
Uninstall from Windows 7/XP:
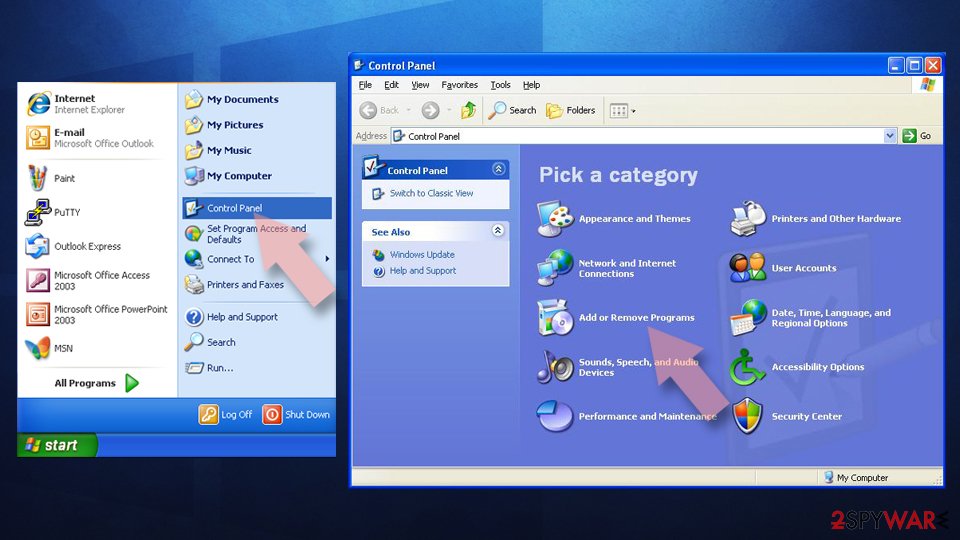
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
Remove the unwanted program:
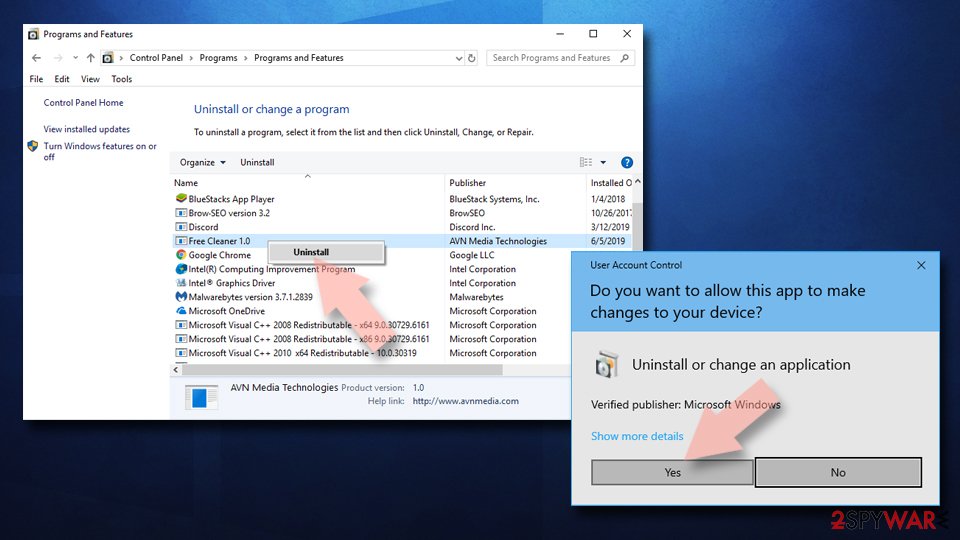
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
Fix Chrome by following the instructions below:
Delete malicious extensions from Google Chrome:
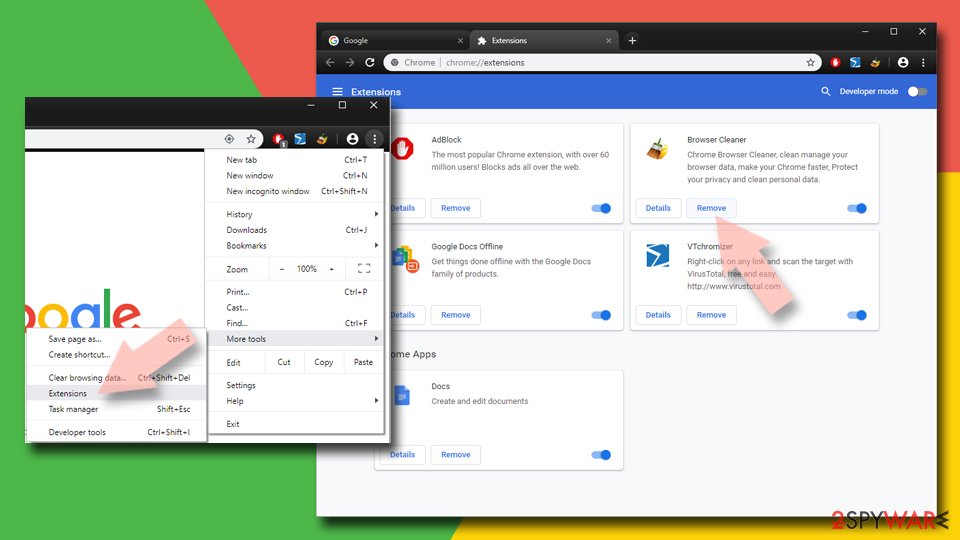
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
Clear cache and web data from Chrome:
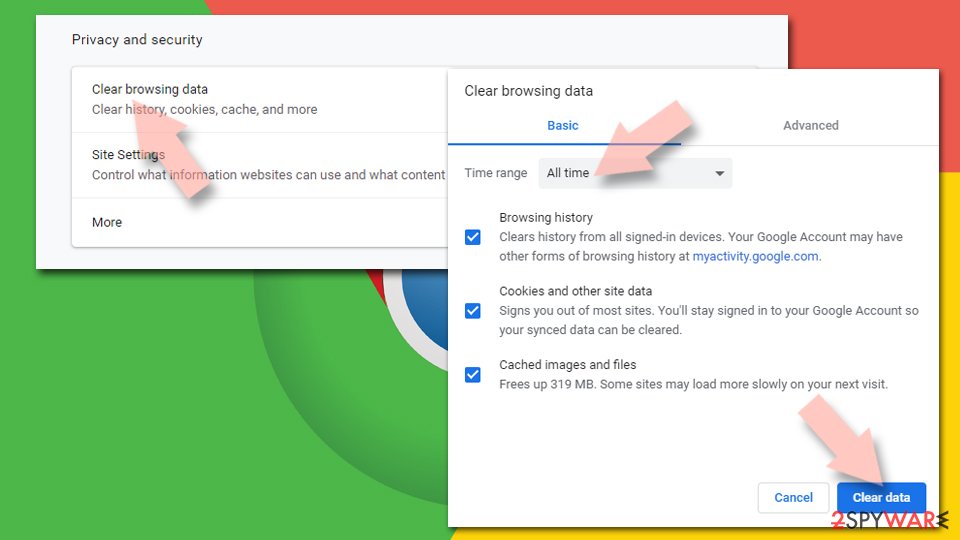
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
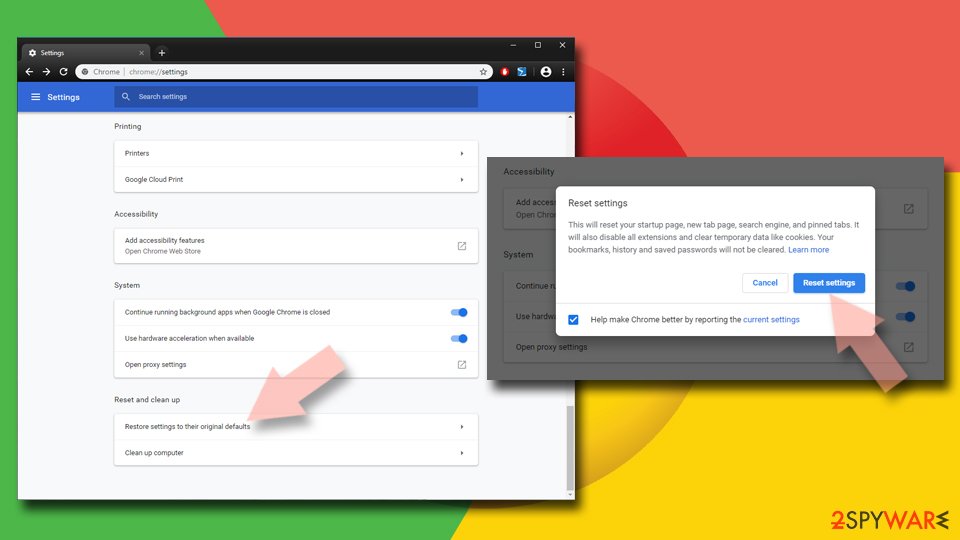
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
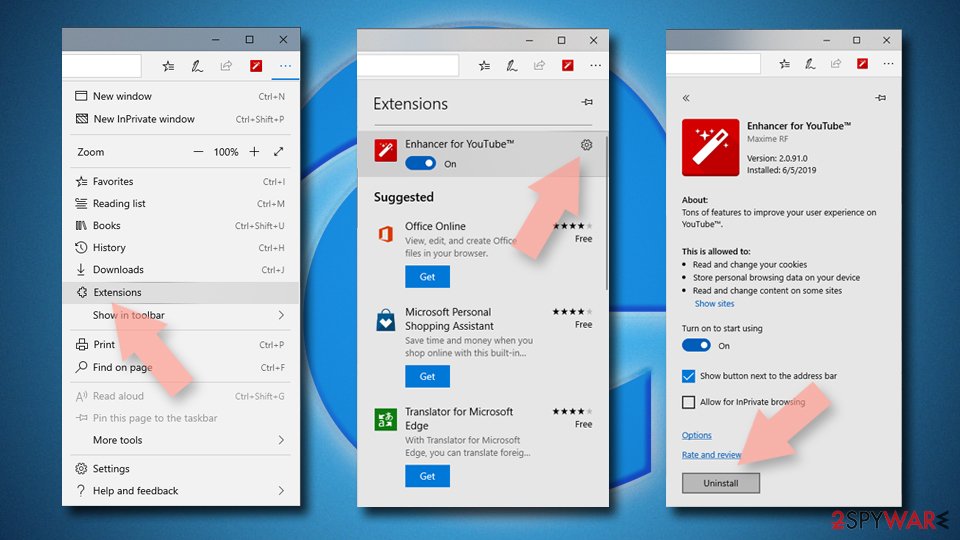
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
Clear cookies and other browser data:
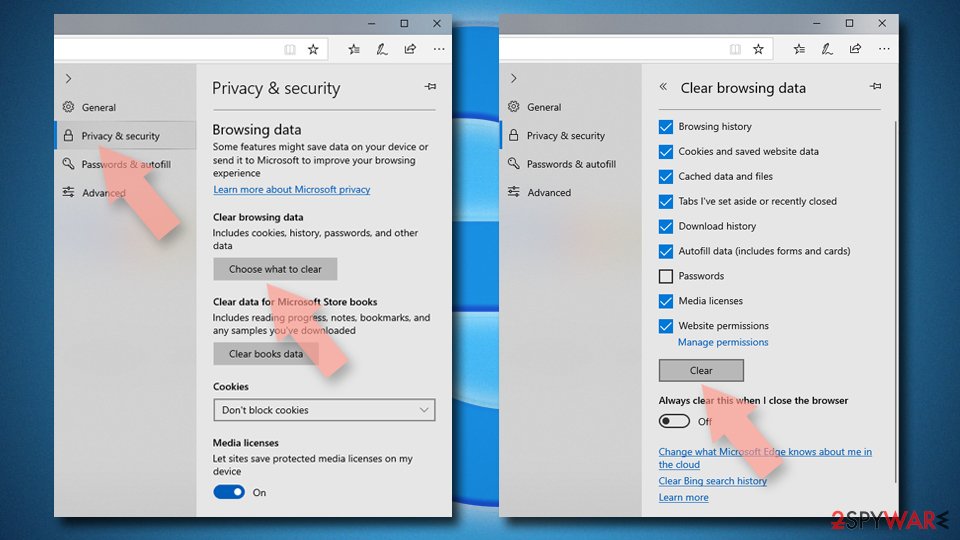
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
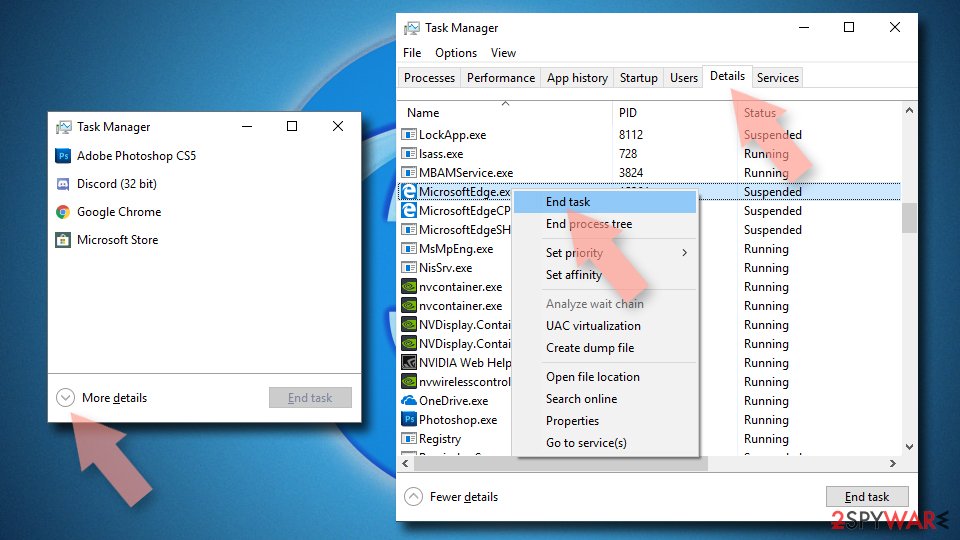
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
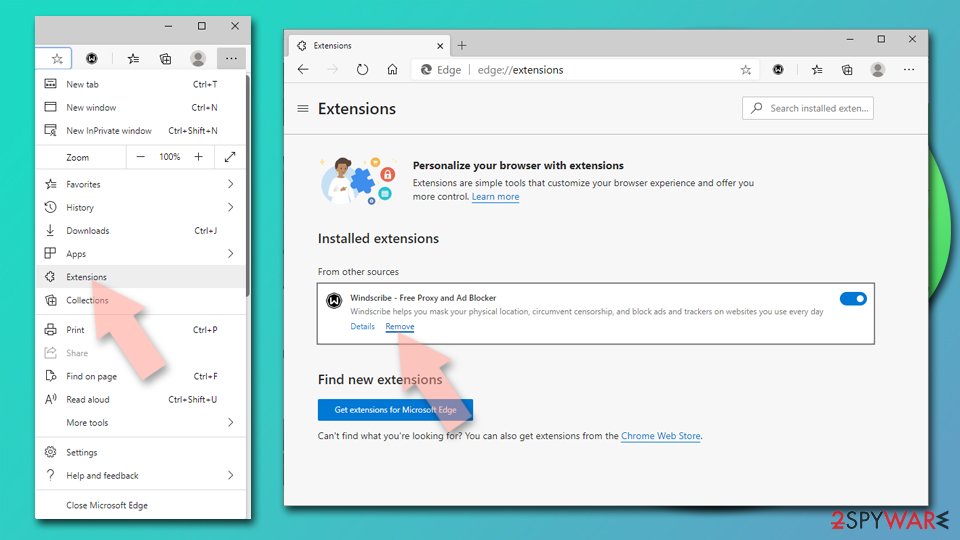
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
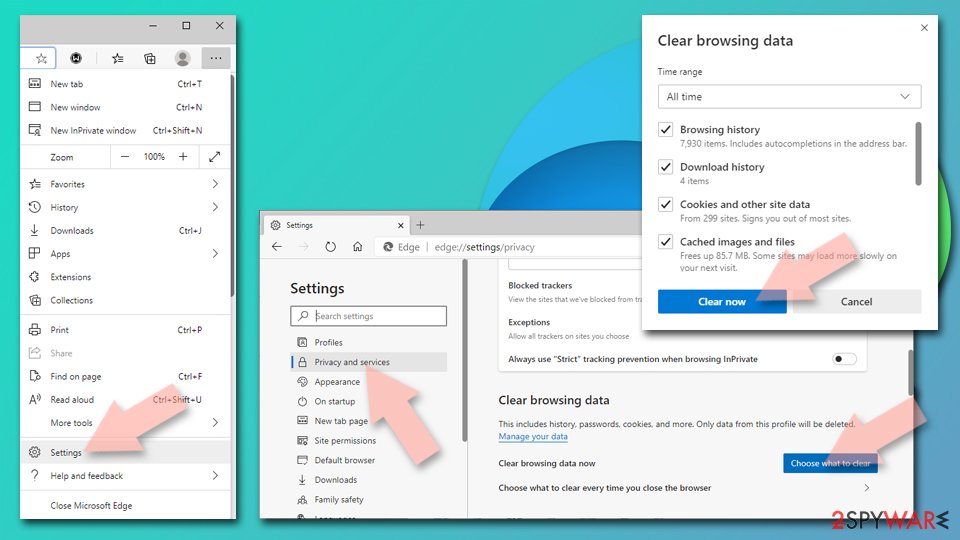
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
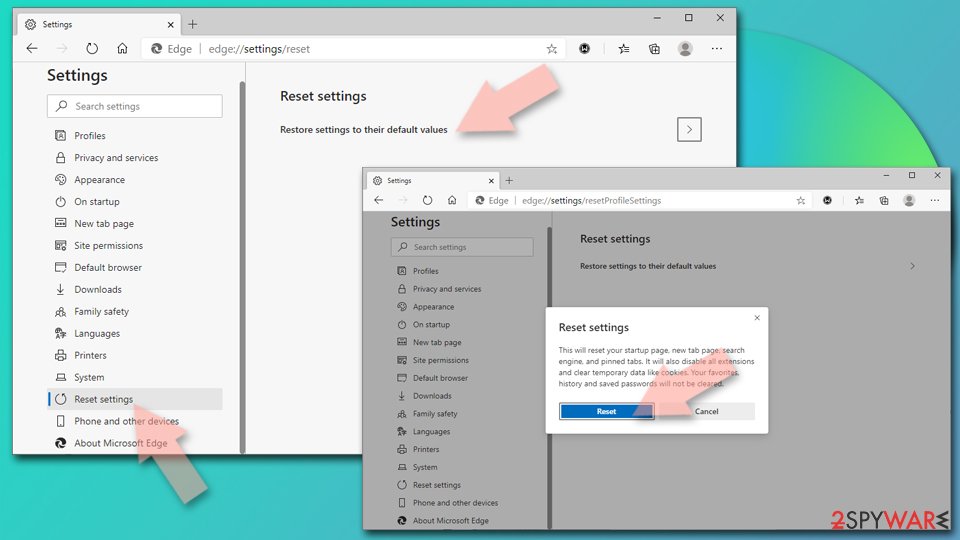
Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
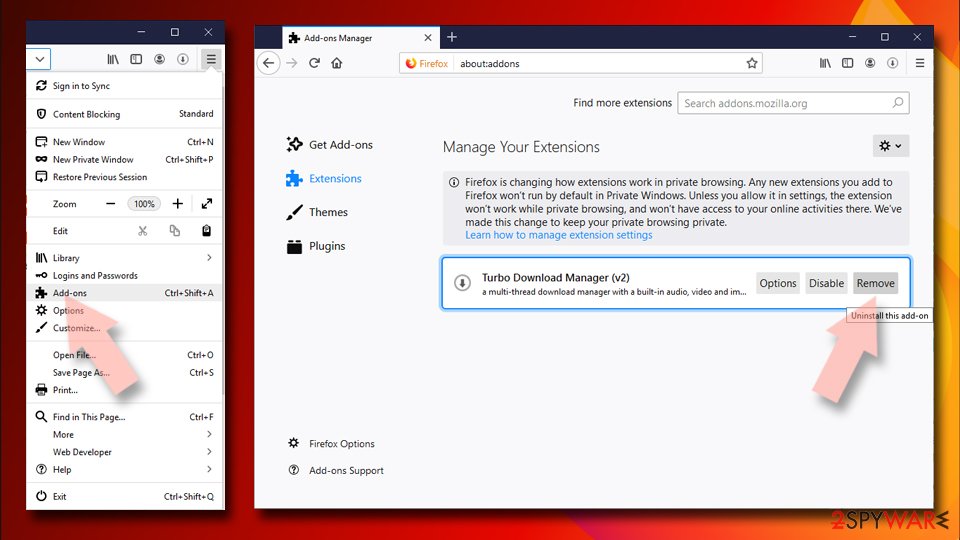
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
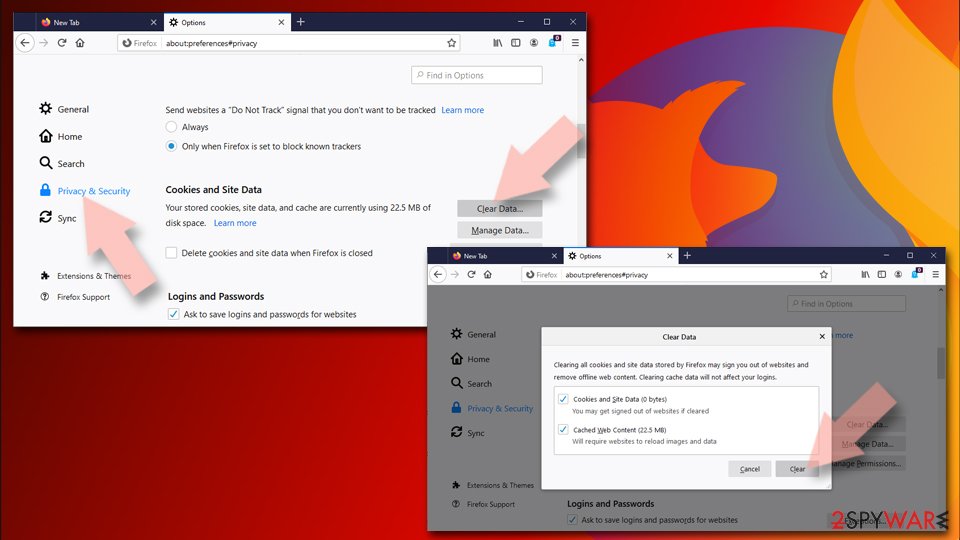
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
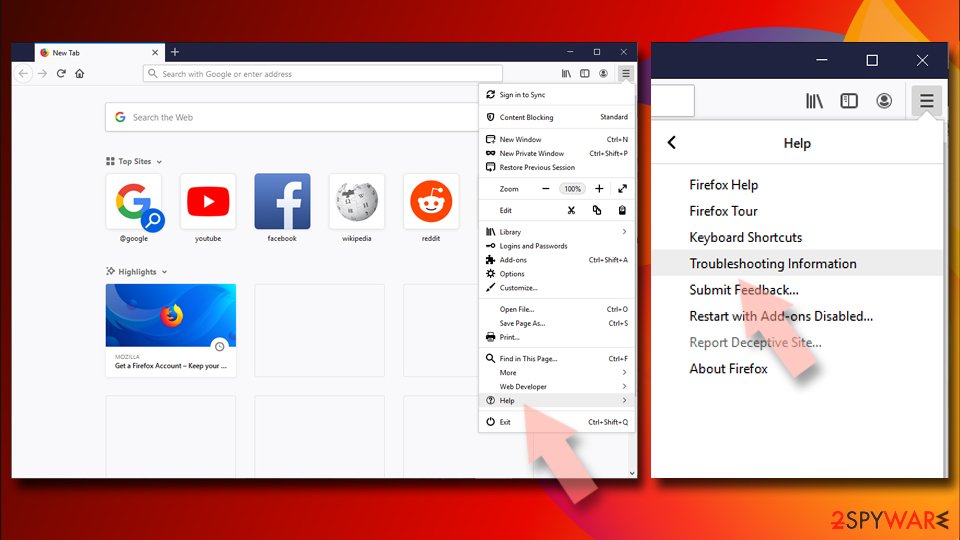
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
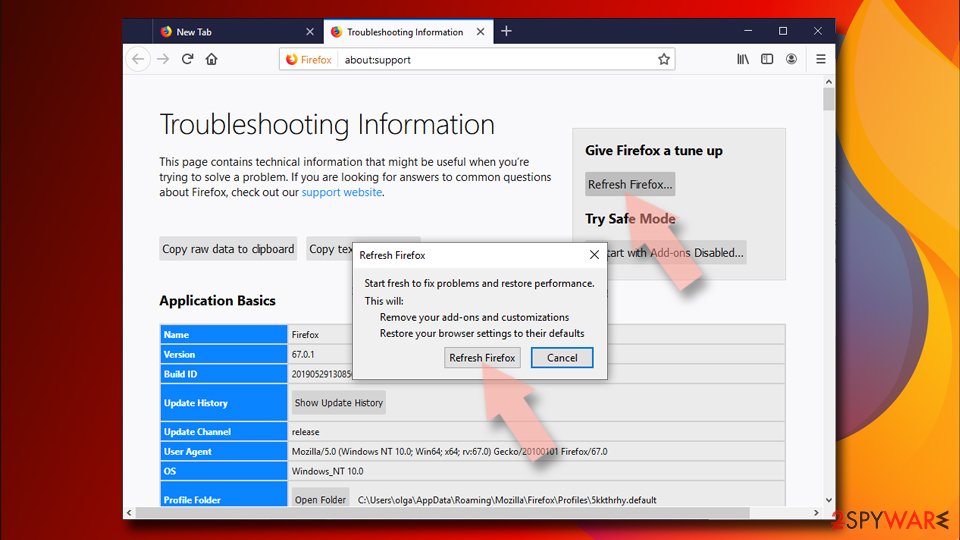
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
To remove the potentially unwanted program, you have to uninstall suspicious browser extensions and reset Safari:
Remove dangerous extensions:
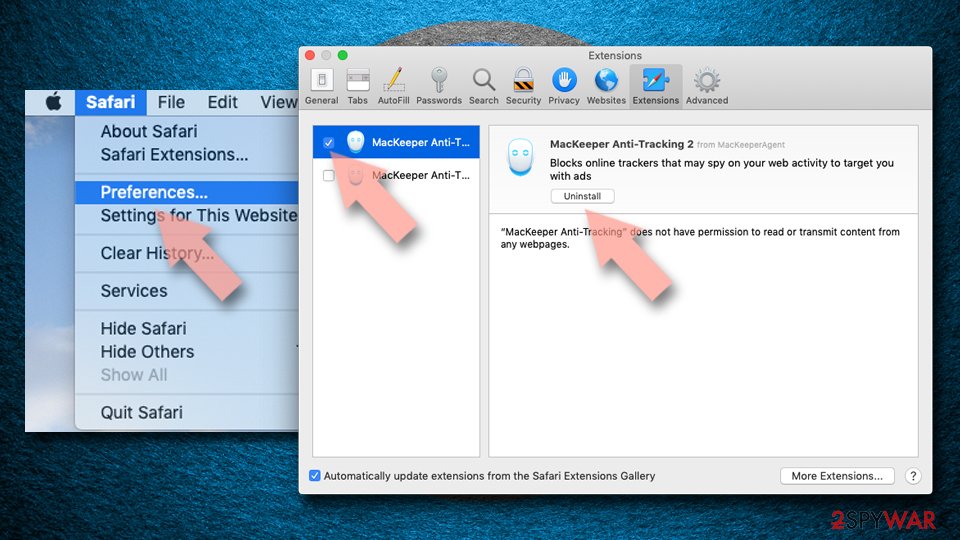
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
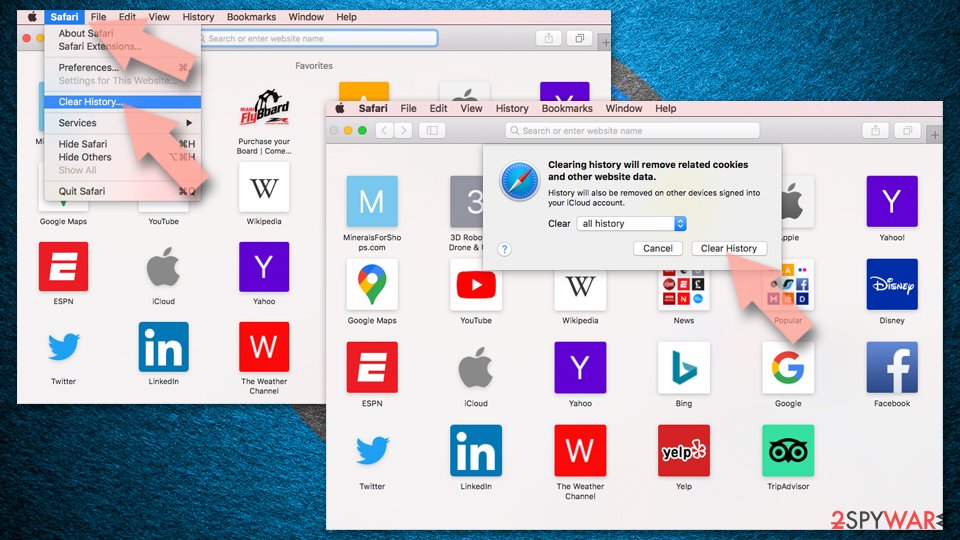
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
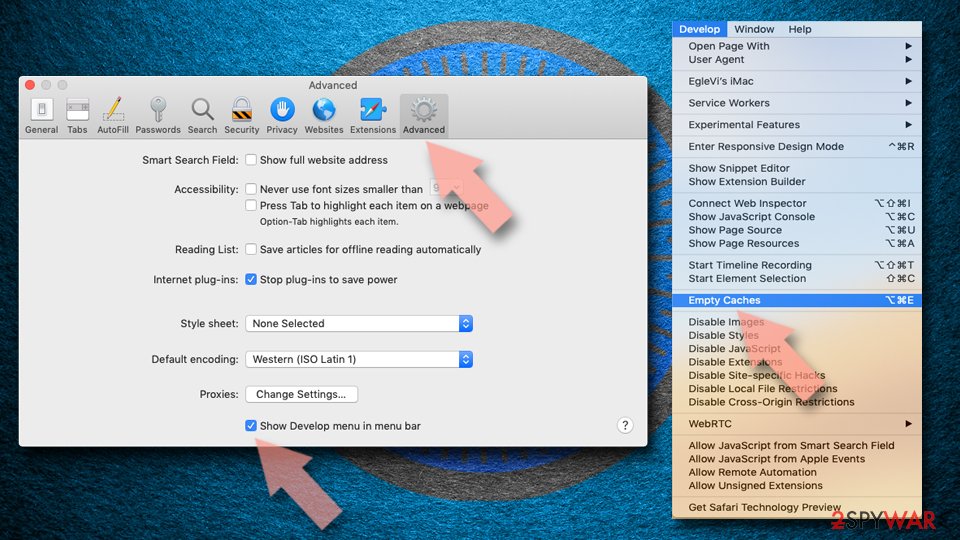
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
If you have encountered an APPLE SECURITY BREACH scam pop-up on your Mac, remove the adware together with elements that are related to it.
Remove the unwanted application:
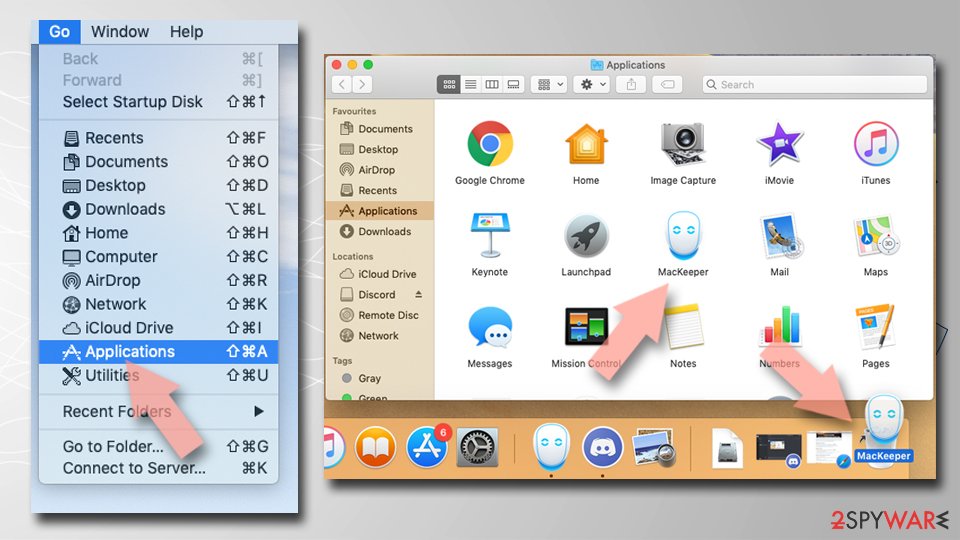
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
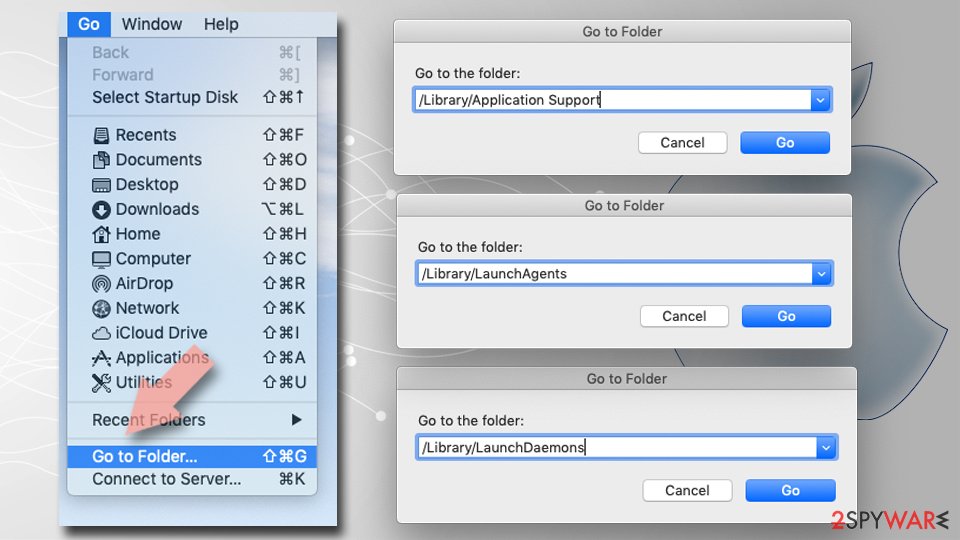
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
Remove dangerous add-ons:
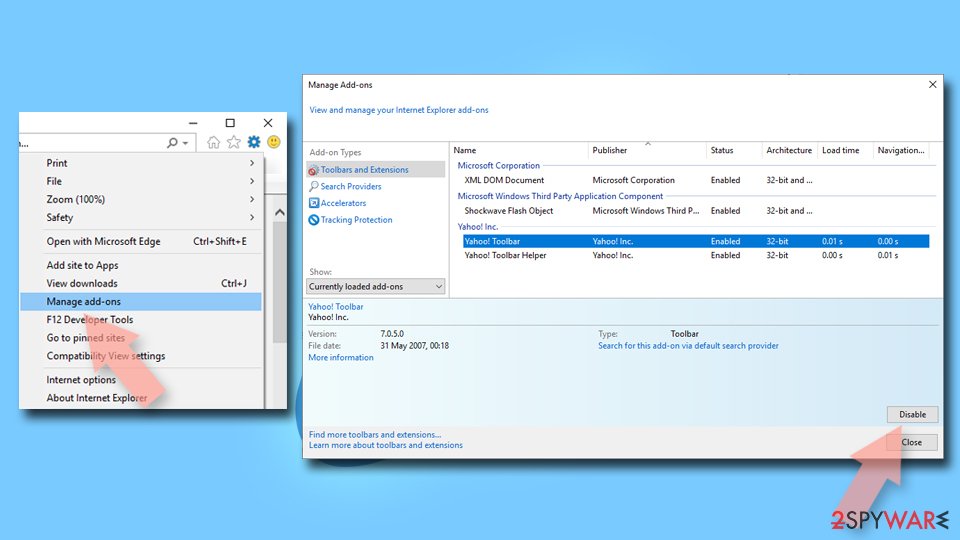
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
Change your homepage if it was altered:
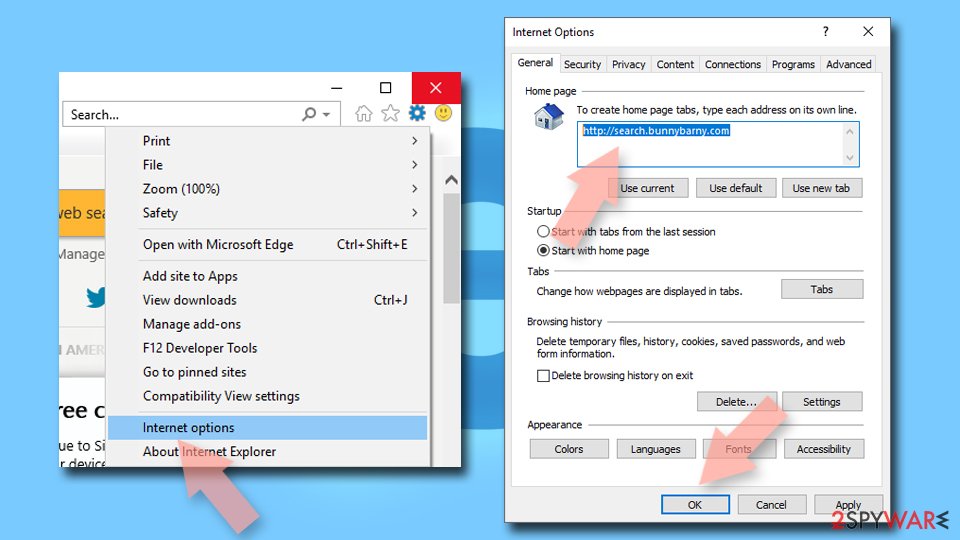
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
Delete temporary files:
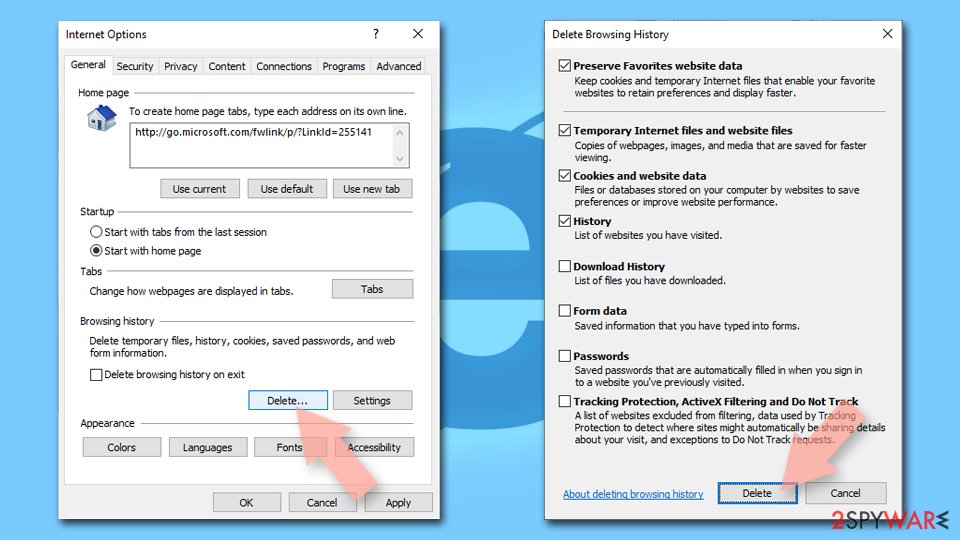
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
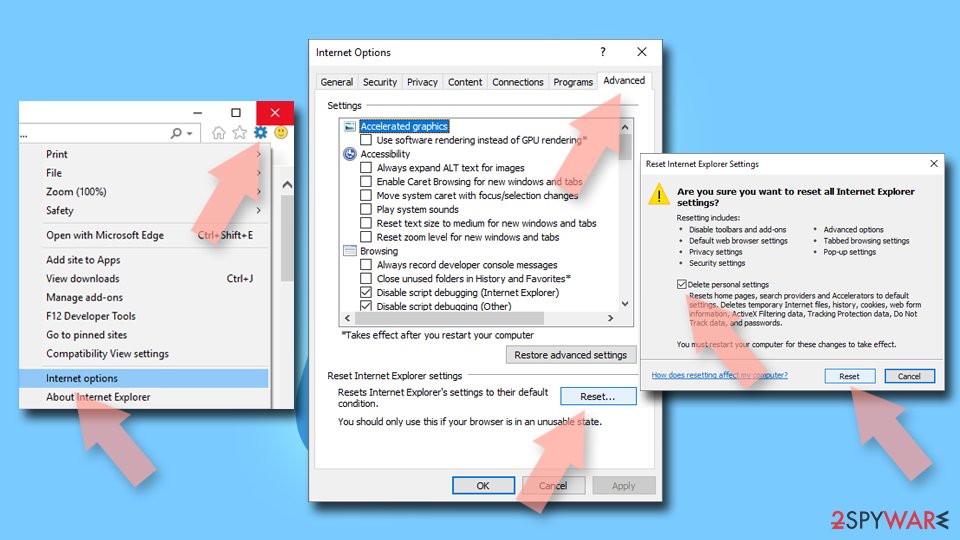
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
From our report of Dec 2020 · not reviewed since
Get rid of APPLE SECURITY BREACH scam
Start APPLE SECURITY BREACH removal by downloading a powerful antivirus tool that will be able to detect all potentially unwanted programs and their components on your computer.
You can pick one from the list below since they are professional tools widely used by IT professionals.
Experts from BedyNet.ru warn that any attempts to uninstall the adware yourself might lead to further PC damage. Likewise, do not try to delete the components of the potentially unwanted program without any assistance.
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed APPLE SECURITY BREACH in the list of installed apps has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
Questions about APPLE SECURITY BREACH
What is APPLE SECURITY BREACH and why is it on my PC?
APPLE SECURITY BREACH is a program that was installed on the PC, most likely together with something else you downloaded. Free software sites and many installers add extra programs on setup pages with pre-ticked boxes, so the extra install looks like your choice even though nobody read the page.
Check the install date in Settings, Apps, Installed apps: the program you installed that day is the probable carrier. If you do not need APPLE SECURITY BREACH, uninstall it. If it belongs to your hardware or to a program you use, search its exact name and publisher first, because drivers and their tools can have unfamiliar names.
How do I stop programs like APPLE SECURITY BREACH from being installed again?
Most unwanted programs arrive through installers, so the fix is in how you install software. Download programs from their official sites or the Microsoft Store, not from download portals or ads above search results. During setup, choose Custom or Advanced installation and untick every extra offer, including browsers, toolbars and optimizers.
Decline update prompts that appear inside other programs unless you know them. In Windows Security, turn on reputation-based protection and potentially unwanted app blocking. These steps would most likely have stopped APPLE SECURITY BREACH before it reached the app list.
Why can't I find APPLE SECURITY BREACH in antivirus databases?
Because it is new or because it is listed under a different name. Antivirus companies name threats after the family they belong to, and a program that appears as APPLE SECURITY BREACH on your PC may carry a generic or unrelated label in their databases.
Many new samples are first detected only by behaviour, without a family name. What you saw, APPLE SECURITY BREACH in the list of installed apps, is enough to act on:
- end the program
- remove its startup entry
- run a Microsoft Defender offline scan
- secure your accounts
A detection name from a scan is worth noting for later.
I found AnyDesk or ScreenConnect that I did not install. Is that APPLE SECURITY BREACH?
Not necessarily APPLE SECURITY BREACH, but it is a warning sign. These are legitimate remote support tools, and criminals use them as ready-made backdoors, especially after tech support scams or fake invoice calls.
If you did not install it and no one you trust set it up, uninstall it, change passwords from a clean device and check your bank account. If someone connected to your PC through it, follow the steps for remote access trojans and consider a Windows reset. Installed apps sorted by date shows when it appeared.
Should I check my other computers too?
Yes, it takes little time and removes doubt. APPLE SECURITY BREACH itself usually stays on one PC, but the download that carried it may have been copied to other computers, shared drives may hold the same installer, and an attacker who had access could have tried saved passwords on other devices.
Run a full scan on every Windows PC in the home or office, check shared folders for the original download, and change Wi-Fi and router passwords if they were stored on the infected machine.
How do I know if my PC has APPLE SECURITY BREACH?
Often you do not, which is the point of a trojan. Possible signs are an antivirus alert naming APPLE SECURITY BREACH or a generic trojan detection, unknown programs or scheduled tasks, processes with random names in Task Manager, browser extensions you did not add, security settings turned off, slower performance, or account alerts about logins from unknown places.
The reliable check is a full scan followed by Microsoft Defender's offline scan. If you recently ran a crack, a fake installer or a command a website told you to paste, scan even without symptoms.
Should I report APPLE SECURITY BREACH?
Report it if you lost money, if accounts were taken over, if you are a business, or if the trojan came through a scam call. A police or national cybercrime report gives you a reference number for your bank and insurer and helps link cases.
You do not need to report a trojan that antivirus blocked before it ran. Before reporting, write down the dates, the detection name, file names and any messages or transactions linked to the attack; screenshots of antivirus alerts are useful evidence. The country list is in the report section above.
Do I need to reinstall Windows to get rid of APPLE SECURITY BREACH?
Usually not. A thorough clean-up is enough when the offline scan finds nothing afterwards and you do not see APPLE SECURITY BREACH in the list of installed apps again. A reset is the safer choice if an attacker had remote control, if security tools were switched off, or if detections come back after every clean-up.
Windows 11 can reset itself without a USB stick under Settings > System > Recovery > Reset this PC. Copy documents and photos out first and scan the copies. A reset does not change passwords or undo stolen data, so the account steps still apply.
Is it safe to do online banking after seeing APPLE SECURITY BREACH in the list of installed apps?
Not on that PC until it is clean. A program that produces APPLE SECURITY BREACH in the list of installed apps runs with your rights and could read what you type or what the browser shows. Use a phone or another computer for banking and for changing passwords.
When the offline scan of the affected PC is clean and nothing suspicious starts with Windows any more, you can go back to using it. Check your bank statements for the past weeks either way, and call the bank if anything looks unfamiliar; banks can block cards and reset access quickly.
Will Fortect remove APPLE SECURITY BREACH?
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds on your Mac before you decide anything.
For APPLE SECURITY BREACH, follow the plan on this page as well: removing a launch item or an app is done in macOS itself, and a scanner cannot undo what was typed or entered on the infected Mac, such as saved passwords that were copied.
Change your passwords from another device first, and if the page tells you to erase the Mac, a scan is not a substitute. The free scan costs nothing and the full-featured product needs a license.
Sources
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 7, 2026)
- Microsoft Learn: How Microsoft names malware (read October 7, 2026)