
Atilla stealer: what it is and how to remove it
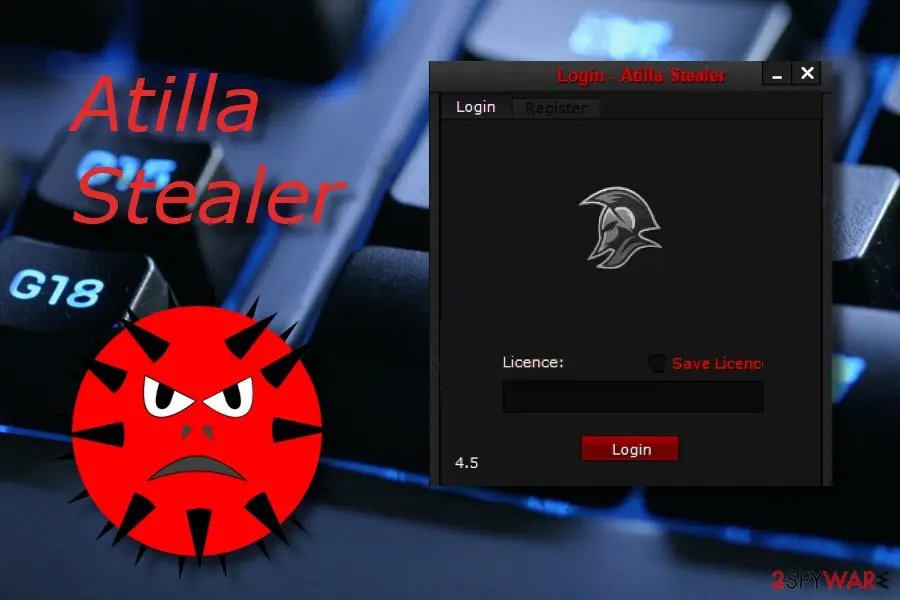
Atilla stealer is described as a RAT (Remote Access Trojan) that is created to carry out illicit activities by activating malicious processes in the background. This suspicious software is promoted on the Dark Web and its original website atilla.vip.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If Atilla stealer keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove Atilla stealer yourself 3 steps, about 9 minutes, no software needed.
Start the steps
Atilla stealer: summary
| Distribution | Trojans can be found in email attachments or third-party networks |
|---|---|
| Name | Atilla stealer |
| Program type | RAT |
| Promotion | Via official website |
| Purpose | To steal personal information |
| Location | Malicious files can be found in the Task Manager |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Type | Information stealer |
| Symptoms | An unknown program in Installed apps |
| Evidence | 5 write-ups by security sites; details still limited |
| First seen | 18 April 2019 |
| Facts checked | 6 October 2026 |
What Atilla stealer does
From our report of Apr 2019 · not reviewed since
More from our earlier report on Atilla stealer
- can help you to detect malware-laden content
- Eliminate the threat by using automatical software to avoid harmful mistakes
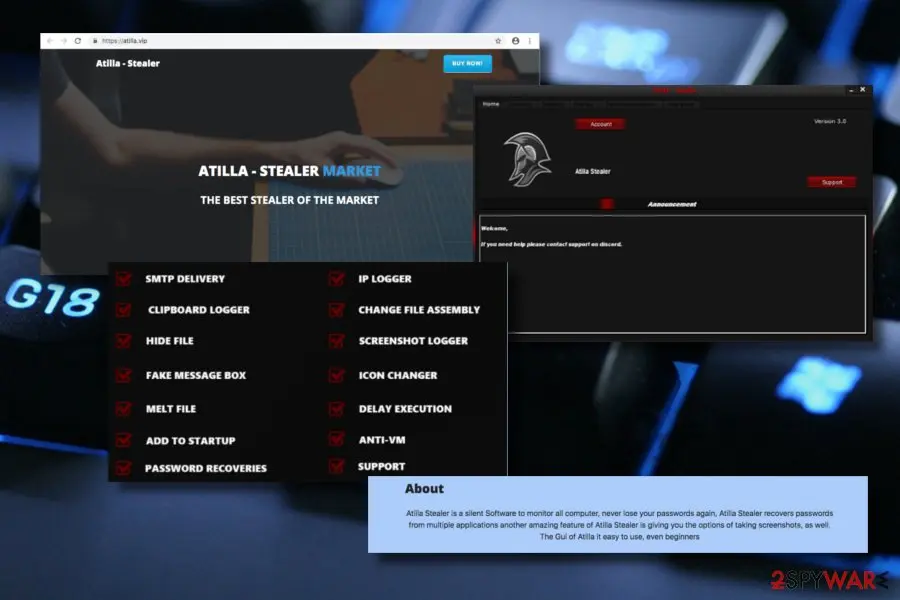
- Atilla Stealer is a silent Software to monitor all computer, never lose your passwords again, Atilla Stealer recovers passwords from multiple applications another amazing feature of Atilla Stealer is giving you the options of taking screenshots, as well.
- The Gui of Atilla it easy to use, even beginners
What Atilla stealer collects and where it sends it
From our report of Apr 2019 · not reviewed since
Atilla stealer is a Remote Access Trojan that runs in the machine's background and might relate in data theft
Atilla stealer is described as a RAT (Remote Access Trojan) that is created to carry out illicit activities by activating malicious processes in the background.
This suspicious software is promoted on the Dark Web and its original website atilla.vip. Atilla stealer virus convinces people to download its app and install it on the computer system.
After that, the malicious program can start running without showing any signs and users often do not even notice any questionable or malware-laden activities until they scan the system or encounter suspicious executables running in the Task Manager section. Once the malware gets on a particular machine, it might result in data theft of the user's personal information.
Atilla stealer malware is promoted on its official website which gives the program a look of legitimacy. The developers of this malicious software provide this type of review for the application:
However, if you are an accurate person, you will supposedly spot some grammar mistakes in the above-given quote. You should know that companies who promote reliable software do not make mistakes in their promotion texts. Another sign for you should be the stealer word in Atilla stealer. It may look like some aim is hidden behind the name.
If you install Atilla stealer, there is a big possibility that you will not notice anything suspicious at first. However, later on, you might start experiencing some changes in your computer system. For example, programs and applications might be taking more time to launch, the machine is facing sluggishness what did not happen before, software is crashing, etc.
Additionally, Atilla stealer trojan might leave suspicious-looking executables in your computer system. You might overcome rogue processes running in the Task Manager section of your Windows computer. Also, some anti-malware tools are capable of detecting the malware in these names:
We also suggest using a program such as or . If these programs spot some malicious changes in the machine, you can proceed with the Atilla stealer removal process.
You need to remove Atilla stealer from all locations of your computer, otherwise, the program will supposedly start eating your computer resources to perform its malicious activities. Also, it might relate to personal data theft, some privacy problems, banking credential theft, and money losses, other computer infections.
- Spyware.PasswordStealer;
- Gen:Variant.MSILPerseus.184538;
- Artemis!4FFF22A0771A.
From our report of Apr 2019 · not reviewed since
Atilla stealer trojan should be terminated by performing the process automatically
If you have detected this trojan infection on your computer system, better not to try to eliminate the malware manually as you might make harmful mistakes or miss some crucial components that need to be terminated. For detecting malware-laden objects you can use tools such as , , or . When you finish scanning the system, you can proceed with the Atilla stealer removal.
You need to remove Atilla stealer virus from your Windows computer system to avoid all possible damaging consequences and prevent money, personal data losses. The infection needs to be terminated as soon as you discover the cyber threat on your machine. Ensure that all trojan-related objects are also removed, otherwise, the infection might launch again within the next system restart.
[GI=method-1]Turning on Safe Mode with Networking might allow you to disable the activities of the trojan. If you need some help with this process, take a look at the below-given instructions:
[GI=method-2]Use System Restore if you want to deactivate the malware on your computer system. Turn in this function by following the guide:
How Atilla stealer got on your PC
From our report of Apr 2019 · not reviewed since
Even though some malicious programs have their official websites where developers try to promote their malware-laden apps in various ways, the most popular technique for malware such as trojan distribution is through spam email messages and their infectious attachments (mostly, executables or word documents).
Experts from NoVirus.uk urge users to be aware of questionable email messages and avoid opening them, especially their attached files or documents. A way to identify the legitimacy of the received content is to use an anti-malware or antivirus tool and scan the component which is clipped to the email message.
Cautious on the Internet sphere is the main precautionary measure for malware avoidance. Computer infections such as trojans might also be injected into suspicious hyperlinks or infectious banner ads. Do not click on any content that you cannot recognize, and even better, immediately close all third-party pages that you accidentally enter.
How to remove Atilla stealer
A stealer usually takes what it wants within minutes and may already be gone.
The scan comes first, then the accounts.
Step 1: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 2: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
Questions about Atilla stealer
What is Atilla stealer and why is it on my PC?
Atilla stealer is a program that was installed on the PC, most likely together with something else you downloaded. Free software sites and many installers add extra programs on setup pages with pre-ticked boxes, so the extra install looks like your choice even though nobody read the page.
Check the install date in Settings, Apps, Installed apps: the program you installed that day is the probable carrier. If you do not need Atilla stealer, uninstall it. If it belongs to your hardware or to a program you use, search its exact name and publisher first, because drivers and their tools can have unfamiliar names.
Atilla stealer came back after I uninstalled it. Why?
Something else is reinstalling it. Common causes are a second program from the same publisher, a scheduled task that downloads it again, or a browser extension that keeps prompting for it. Sort Installed apps by install date and uninstall each entry from the same day that you did not choose.
Then open Task Scheduler and look in the Task Scheduler Library for tasks with updater-style names that you do not recognise. Check Startup apps in Task Manager too. If Atilla stealer still returns, start Windows in Safe Mode, uninstall it there and run a Microsoft Defender offline scan, which looks for loaders that ordinary scans can miss.
What happens to the stolen data?
Stolen data is packed into "logs", one per infected PC. The criminal who ran the stealer uses them directly or sells them in online markets, where others search them for bank, crypto, e-mail, gaming and business accounts.
This can happen days or months after the infection. That is why changing passwords and ending sessions matters even if nothing has happened yet. Breach notification services such as Have I Been Pwned can tell you when your e-mail address appears in known leaks.
Do I need to tell my bank about Atilla stealer?
Yes, if any card was saved in a browser on the affected PC or if you did online banking there while atilla stealer in the list of installed apps was going on.
Call the number on the back of the card, explain that malware may have copied the card details, and ask for a replacement and a check of recent payments. Banks act faster when you call early. Also change the online banking password from another device and look for new payees, changed contact details or unfamiliar devices in the banking app.
Should I stop using this PC?
Only for sensitive things, and only until it is clean. Do not log in to banking, e-mail or crypto on it until the offline scan finds nothing. You can keep using it to follow the removal steps.
If the scans keep finding new items, or protection keeps switching off, back up your documents and reset Windows. After that the PC is as safe as a new one, but the accounts still need the steps in this guide, because a reset cannot undo data that was already sent.
Which stealer caused Atilla stealer?
It has not been identified. People who reported Atilla stealer saw atilla stealer in the list of installed apps, but without the file that caused it, nobody can tell which stealer family was involved. Several families are sold to many criminals at once, and they produce the same result.
If you still have the program or archive you downloaded before this started, keep it unopened; a scan or an upload to a multi-engine scanner can reveal the family. Whatever it was, the steps are the same:
- secure accounts from another device
- scan the PC offline
- remove the download that carried it
How can someone log in without my two-step code?
By using a session instead of a login. When you sign in, the site gives the browser a cookie that says you already passed both steps. Spyware like Atilla stealer copies that cookie, and the attacker loads it into their own browser, so the site sees a logged-in user and asks for nothing.
The fix is to end all sessions in the account's security settings, which makes the copied cookie worthless, and then change the password. Some services also show active sessions with locations, which helps spot misuse.
Should I reset my PC because of Atilla stealer?
Only if the signs point to deeper access. Reset when you see atilla stealer in the list of installed apps again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
Is Atilla stealer still on my computer?
Possibly, possibly not. Some stealers stay and keep collecting; others delete themselves after one run. The sign you saw, atilla stealer in the list of installed apps, only shows that data was used, not where the program is now.
A Microsoft Defender offline scan answers the first question; checking Startup apps, Task Scheduler and the Downloads folder for files from the days before helps too. Either way, the account steps are needed, because stolen passwords and cookies keep working after the program is gone, sometimes for weeks.
Will Fortect remove Atilla stealer?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Atilla stealer, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Search Security: RAT (remote access Trojan) (read October 6, 2026)
- Wikipedia: Dark Web (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)
- Microsoft Learn: How Microsoft names malware (read October 6, 2026)