
Exocrypt ransomware: what it is and how to remove it
Exocrypt ransomware is a malicious program that claims to be created for educational purposes. Recently, security experts reported about its second version called as Exocrypt XTC v2.0.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Make sure nothing will rename more files to .xtc: an automatic scan checks the PC first.
Do it yourself · free Remove Exocrypt ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps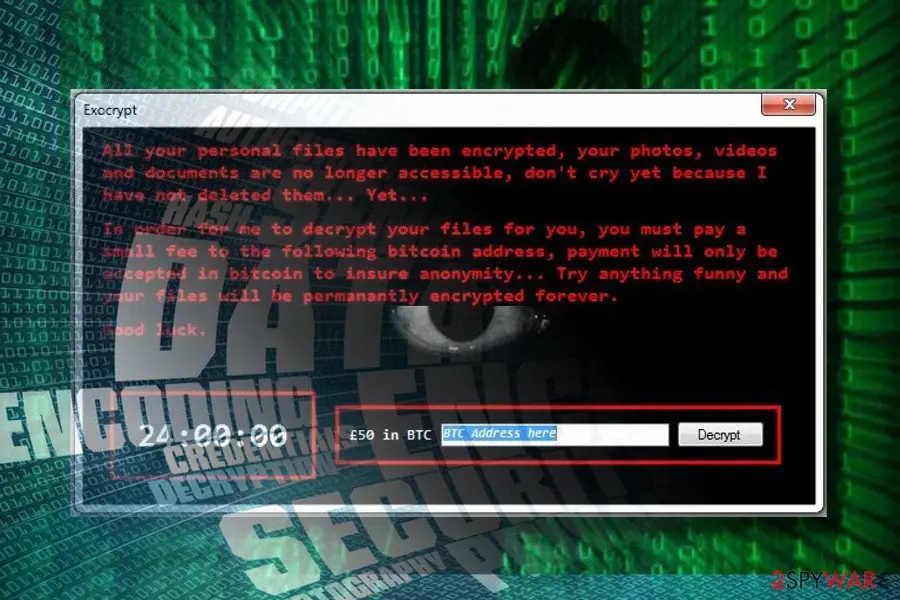
Exocrypt ransomware: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Ransom note | Not recorded in our earlier report |
| Contact | Not recorded in our earlier report |
| Encrypted file extension | .xtc |
| Decryptor | No free decryptor is known for this variant; check No More Ransom (nomoreransom.org) for updates |
| Distribution | Not recorded in the old report |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Damage | Not recorded in the old report |
|---|---|
| Name | Exocrypt ransomware |
| Type | File-encrypting ransomware |
| Symptoms | Files renamed with a new extension |
| Evidence | 5 write-ups by security sites; details still limited |
| Encrypted files | .xtc |
| Free decryptor | No free decryptor is known (checked 6 October 2026) |
| First seen | 8 May 2018 |
| Facts checked | 6 October 2026 |
- File extension:
.xtc
From our report of May 2018 · not reviewed since
More from our earlier report on Exocrypt ransomware
- Spam email attachments, fake software updates
- Locks data and asks for redemption
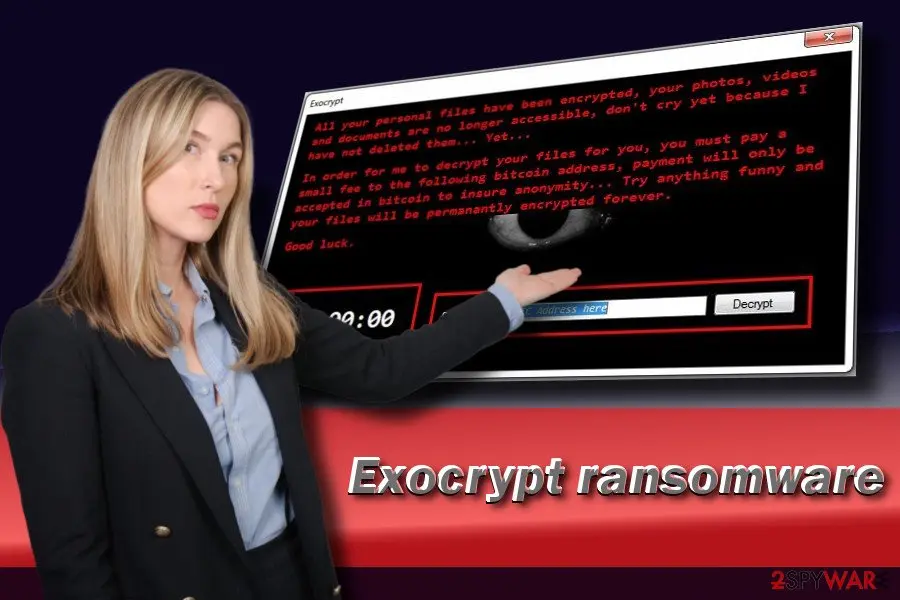
- All your personal files have been encrypted, your photos, videos and documents are no longer accessible, don't cry yet because I have not deleted them...
- Try anything funny, and your files will be permanently encrypted forever.
- 24:00:00 $50 in BTC ***
- This ransomware was made for educational purposes, we will not send out any copies of this virus, unless it is for forensic purposes!
How Exocrypt ransomware behaves
From our report of May 2018 · not reviewed since
Exocrypt is a malicious program that belongs to ransomware category
Exocrypt ransomware is a malicious program that claims to be created for educational purposes.
Recently, security experts reported about its second version called as Exocrypt XTC v2.0. Each of these crypto-viruses are set to lock personal victim's files and block the access to them until he or she pays the ransom. Ransomware is still using AES encryption algorithm to create a hardcoded password for archived data on the victimized PC.
Following the encryption, the virus scans the system for compatible file types and renders AES-256 cryptography to make them inaccessible. It's not clear yet what file extension it uses, but experts consider it to be .xtc.
In most of the cases, the Exocrypt ransomware infiltrates on PCs via malicious email attachments or fake software updates. It seems current that extortionists do not take advantage of exploit kits and unprotected Remote Desktop services.
As soon as all the detected data is encrypted by Exocrypt XTC v2.0, user receives a .html ransom note which, once opened, demands $50 that should be paid in Bitcoins within 24 hours. While the ransom is believed to be one of the smallest ones, the time given for exchanging currencies and performing a transaction is quite limited.
The ransom note of the first version reads:
The second version notes its victims:
No matter what is reported, you should realize that you are dealing with a serious virus. It's not advisable to pay the ransom anyway. Even if you have some Bitcoin coins in your digital wallet, do not rush to give them away for criminals. No one can assure you that you'll get your files back after the payment.
By the way, do not fall into a panic if Exocrypt removal is not permitted. Ransomware-type viruses use scripts to disable security programs to evade removal. To bypass the restriction, you should restart your PC into Safe Mode with Networking and then try to run a scan.
From our report of May 2018 · not reviewed since
Most common ways how ransomware enters the system
As we have already pointed out, this ransomware virus spreads either inside spam email as an attachment or as obfuscated software updates.
Both ways criminals render social engineering strategies to convince potential victims that the attachment or installer is reliable.
They impersonate legitimate companies, such as Amazon, eBay, etc. or camouflage legitimate products that belong to Microsoft, Adobe, and similar. The usunwirusa.pl team of security researchers points out the following precautionary measures that you should take to protect the system from ransomware attack:
- Always use professional security software and make sure it's up-to-date;
- Exploit the Real-time protection feature of the security program;
- Do not open email messages from unknown senders or companies you do not recognize having business with;
- Be careful with peer-to-peer (P2P) networks as instead of a video, audio file or software you can end up with the virus.
- Finally, restrain from clicking on questionable ads, even if they promote popular products for a small prize.
How to remove Exocrypt ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove Exocrypt ransomware and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so Exocrypt ransomware cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
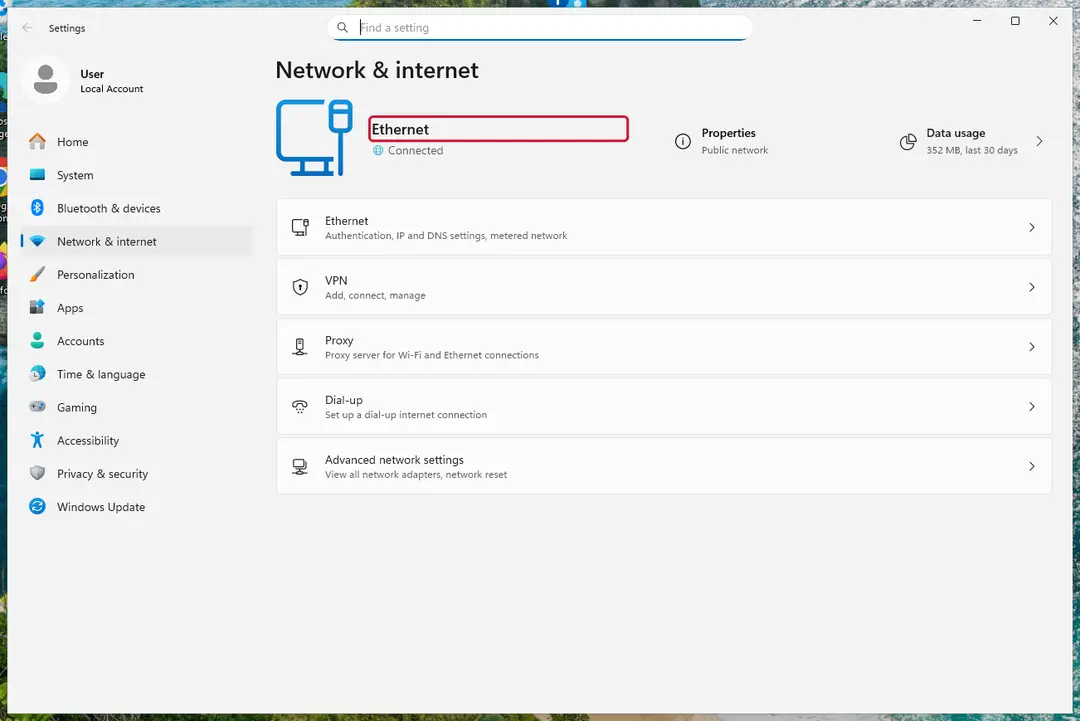
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and identify the family
The name of the family decides whether a free decryptor can help. Copy the ransom note and two small encrypted files to a USB stick, and check them on another device with ID Ransomware or Crypto Sheriff.
Note the extension added to the files, the contact address and the victim ID shown in the note. Keep the originals on the Windows 11 or Windows 10 PC untouched.
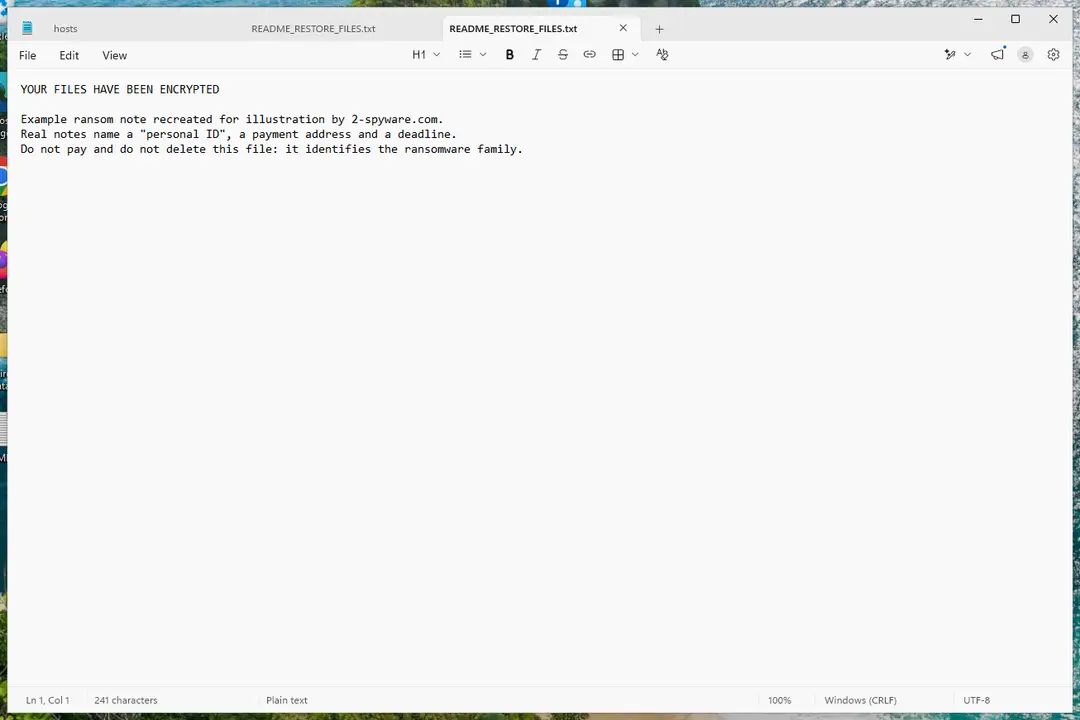
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for Exocrypt ransomware, no free decryptor is known (checked 6 October 2026). Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing Exocrypt ransomware does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
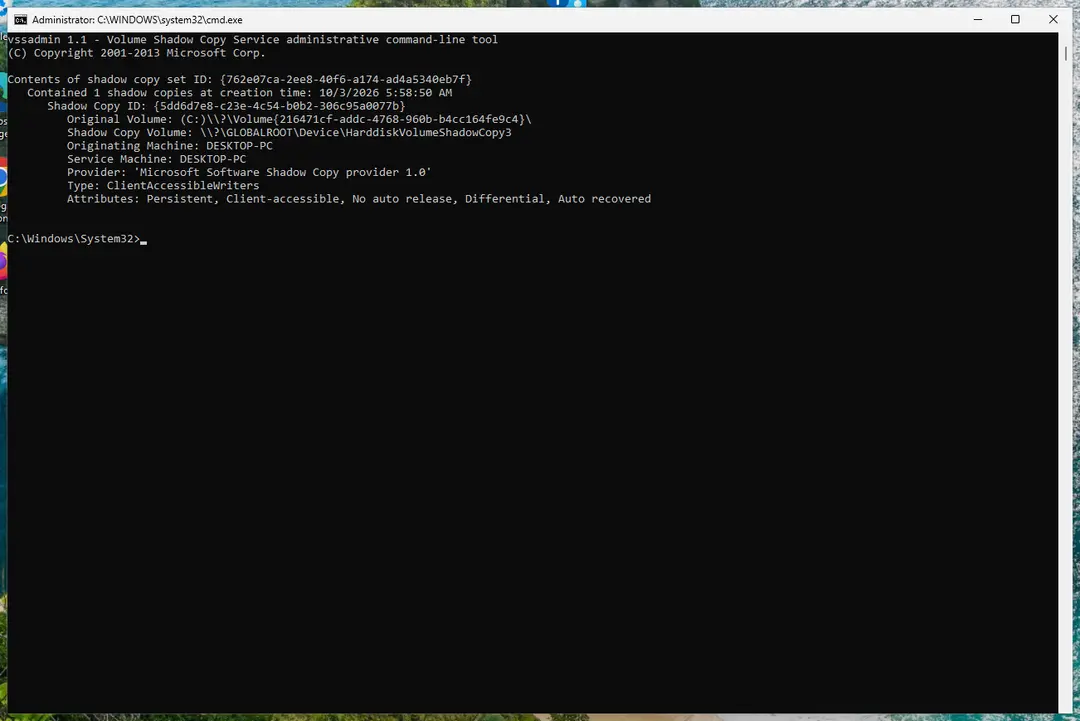
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that Exocrypt ransomware deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of May 2018 · not reviewed since
Home users should rely on professional anti-virus to remove Exocrypt ransomware
IT specialists that are oriented to cybersecurity and viruses are well-equipped and skilled in running various scripts to remove Exocrypt and similar ransomware.
If you are not that tech-savvy, we would not recommend trying to eliminate this pest manually as you may not only lose personal files permanently but also damage your PC.
Upon Exocrypt removal, use your backups to unlock files encrypted by XTC virus or render third-party software recovery tools. But before that, double check if the virus has been removed by running a repeatable system's scan with an anti-malware. Otherwise, your files will be encrypted again.
[GI=method-1]To unblock your anti-virus and run a scan that is essential to ransomware removal, you need to restart your PC into Safe Mode with Networking. Our team has submitted a step-by-step tutorial for those who have never tried safe mode.
There's currently no information about what changes this virus causes on the affected system. Besides, it's unknown whether it deleted Volume Shadow Copies and Previous Windows versions. Therefore, we would strongly recommend you to try each method on how to decrypt files encrypted by Exocrypt ransomware one-by-one.
This software features a powerful scan engine and is capable of exploited deleted, corrupted or encrypted files. Thus, it's worth giving a try.
Exploit previous Windows versions
Exocrypt malware is a severe cyber infection, which may initiate various system's changes, including removal of the System Restore Points that you've created before the attack. However, there's only one way to check that - try to enable the previous Windows version.
ShadowExplorer is a piece of software capable of detecting Volume Shadow Copies stored on Windows OS and recovering the corresponding files if required.
When the Exocrypt decryptor occur, we will notify you immediately.
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Make the next attack harmless
Exocrypt ransomware could only hurt the files that had no second copy, and the signs (files that end in .xtc and no longer open) showed exactly which ones those were.
The 3-2-1 rule fixes that:
- three copies
- two media
- one disconnected
A practical version for a home PC: OneDrive or another cloud backup with version history, plus an external disk that you plug in once a week for File History and then unplug. Test a restore now and then by opening a few files from the backup on another device.
Details, schedules and what not to back up are in our 3-2-1 backup guide for Windows.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about Exocrypt ransomware
Is there a decryptor for .xtc files?
That depends on the family behind the .xtc extension, which this guide cannot confirm yet from the reports alone. Check No More Ransom and ID Ransomware with your ransom note and one encrypted file; they list families with free tools.
If none exists today, keep the encrypted files and a copy of the note on a separate drive, because decryptors are sometimes published months later after flaws are found or servers are seized. Never buy a decryptor from a website that is not the security company that made it.
How do I open .xtc files?
You cannot open them by renaming or by choosing another program. The .xtc ending shows that Exocrypt ransomware encrypted the content, and only the matching key can reverse it. Renaming a file back to .docx or .jpg changes nothing except the icon, and it can confuse a future decryptor, so leave the names as they are.
To get the content back, use a backup, an unencrypted copy elsewhere, or a decryptor listed on No More Ransom if one exists for Exocrypt ransomware. Store the encrypted files on an external disk until then.
How did Exocrypt ransomware get on my computer?
The way Exocrypt ransomware spreads has not been documented yet, so look at your own recent activity. On home PCs, ransomware most often comes with cracked programs, game cheats, key generators and fake updates, or with an e-mail attachment that was opened. On business networks, attackers usually log in through Remote Desktop with a stolen or guessed password.
Think back to what was downloaded or installed in the days before files that end in .xtc and no longer open, and check the Downloads folder and Installed apps sorted by date. Keep anything suspicious for your report, but do not run it again.
Should I pay the ransom?
We advise against it, and so do the FBI, Europol and national cyber agencies. Payment does not guarantee a working tool: some attackers never reply, some tools damage files, and some variants have no decryptor at all. Paying also funds further attacks and can make you a target again.
Before considering payment, try every recovery option in this guide and report the attack. Companies must involve their legal adviser and insurer, because payments to sanctioned groups can be illegal. If files are truly irreplaceable, store the encrypted copies and wait; decryptors sometimes appear later.
Can a data-recovery company decrypt my files for a fee?
Only if a decryptor already exists or the company pays the attackers for you. Some "ransomware recovery" services advertise that they can decrypt families with no known flaw; in practice they negotiate with the attackers and add their own fee. Others use the same free tools listed on No More Ransom.
Before you hire anyone, ask in writing how they will recover the files, whether they will contact the attackers and what happens if they fail. A legitimate service answers clearly. If a free decryptor exists for your family, you can run it yourself.
Did Exocrypt ransomware steal my files or passwords?
We do not know yet. Nothing published so far shows data theft by Exocrypt ransomware, but the only confirmed sign is files that end in .xtc and no longer open, which says nothing about what happened before. Many current ransomware attacks copy files or run a password stealer first, so it is wise to act as if they did.
From a clean device, change the passwords that were saved in the browsers on this PC, starting with e-mail and banking, sign out of all sessions and turn on two-step verification. Watch bank statements and account activity for the next few weeks.
Is Exocrypt ransomware the same as other ransomware with a similar name?
Not necessarily. Ransomware names come from the file extension, the note or a word in the code, so unrelated families often end up with similar names, and one family can appear under several names. The difference matters: a decryptor or advice for one family does not fit another and can damage files.
Compare the ending added to your files and the exact name of the note with the summary table at the top of this guide, then upload the note and one encrypted file to ID Ransomware from a clean device. If the result names another family, follow the guide for that family instead.
My files got .xtc overnight. What happened?
Ransomware often runs at night or when the PC is idle, so the encryption finishes before anyone notices. It usually entered earlier through a cracked program, a fake installer, an e-mail attachment or remote desktop with a weak password.
The .xtc extension marks every file it reached. Start by disconnecting the PC from the network, then identify the family from the ransom note and one encrypted file, check for a decryptor, and look for copies in backups and OneDrive before you consider anything else.
Will removing Exocrypt ransomware unlock my .xtc files?
No. Removing Exocrypt ransomware stops it from encrypting more files and from starting again, but it does not decrypt the files that already end in .xtc. The scanner does not have the attackers' key.
Files come back only from a backup, from copies the ransomware did not reach, such as OneDrive version history, Previous Versions, e-mail attachments or a phone, or with a working decryptor if one exists.
Remove the ransomware first anyway: if you restore files while it is still active, it can encrypt them again. Keep the encrypted files; a decryptor may be published later.
Will Fortect remove Exocrypt ransomware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Exocrypt ransomware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- MalwareHunter Team: New Exocrypt version sample (read October 6, 2026)
- Usunwirusa: Usunwirusa (read October 6, 2026)
- CISA: StopRansomware (read October 6, 2026)
- No More Ransom (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)