
Mail.ru: what it is and how to remove it
Go.mail.ru virus is a browser hijacker forcing redirects to Mail.ru search engine, primarily targeting Russian speakers. It resists removal through installed helper programs.
Facts checked October 12, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If mail.ru returns after you change the search engine back, a free scan can find the program that keeps setting it.
Do it yourself · free Remove Mail.ru yourself 5 steps, about 15 minutes, no software needed.
Start the steps
Mail.ru: summary
| Distribution | Software bundles, third-party websites |
|---|---|
| Name | Mail.ru |
| Type | Browser hijacker/adware/PUP |
| Detection | PUP.Optional.MailRu; Adware.MailRu; no Microsoft detection name is known for this name |
| Main targets | Google Chrome and Mozilla Firefox browsers |
| Useful features stated | A legitimate source of Russian news |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Main issues | Delivers intrusive ads, redirects to sponsored websites that are filled with suspicious content, tracks its victims and collects various user-related data |
|---|---|
| System changes | Changes the homepage, the default search engine, the new tab page |
| Damage | Not recorded in the old report |
| Symptoms | A changed search engine |
| Evidence | 6 write-ups by security sites; details still limited |
| Search page | mail.ru |
| Browsers | Chrome, Edge and Firefox |
| First seen | 1 December 2021 |
| Facts checked | 5 October 2026 |
Mail.ru in 2026: what we found
We opened go.mail.ru in a clean desktop Chrome browser on 4 October 2026 and clicked nothing. This is one visit from one location: ad pages often behave differently on a second visit, in another country, on a phone or after a click, and many hide from automated browsers, so a quiet result is not proof that the page is clean.
go.mail.ru · desktop Chrome · 4 October 2026
- Notification requestNone on this one visit.
- Pop-ups and new tabsNone on this one visit.
- Where it ledIt stayed on
go.mail.ru. - Ad networksGoogle AdSense, Google Ad Manager only.
- Page title"Mail: Почта, Облако, Календарь, Заметки, Покупки — сервисы для работы и жизни"
Quiet on one visit The page made no request and sent us nowhere on this visit. That does not clear it: adware often shows nothing at first and sits quietly for a long time. What it showed you earlier may still be in your browser, so check the permissions below.
Searching my.mail.ru with adult words: what to know
A search such as "my.mail.ru porno" does not point to a virus by itself, and this guide does not list adult pages.
The address my.mail.ru belongs to the Mail.ru portal, which in our reading hosts user profiles and the media they post. Anything found there is posted by users, and we cannot vouch for it.
Adult search terms are a common bait for browser hijackers and fake video pages. If a page that came up after such a search sends you to Mail.ru, changes your start page or asks you to install a player, stop there. Close the tab and do not run the download.
If your browser now opens Go.mail.ru or Mail.ru search without you choosing it, follow the removal steps above. Remove unknown programs first. Then reset the homepage and search engine.
Run a full scan with Microsoft Defender. A quiet result does not prove the computer is clean, so recheck your browser settings after a restart.
Is Mail.ru dangerous? What it collects
What readers reported about Mail.ru
Why cannot I replace Go.mail.ru with Google?. Why cannot I replace Go.mail.ru with Google? It was changed for some reason and now I cannot switch it back.
Can't remove go.mail.ru redirect virus!. Help! I am infected with some kind of virus that continuously redirects me to go.mail.ru site. I tried everything - the malware won't go away. How can I solve this issue?
WHAT?? Go.mail.ru virus AGAIN?. Go.mail.ru virus has hijacked my browser AGAIN. I swear it's like the third time this parasite tries to tell me how to browse... This is absolutely ridiculous. How do i remove Go.mail.ru for good? Looking forward to your answer!
From the comments under our earlier guide; names and contact details removed.
Mail.ru: what changed since our report
December 2021
Our first report
We described Mail.ru on 1 December 2021.
October 2026
Our new check
We opened the address again in a clean browser; the results are above.
From our report of Oct 2026 · not reviewed since
Mail.ru redirect might indicate a presence of a potentially unwanted application
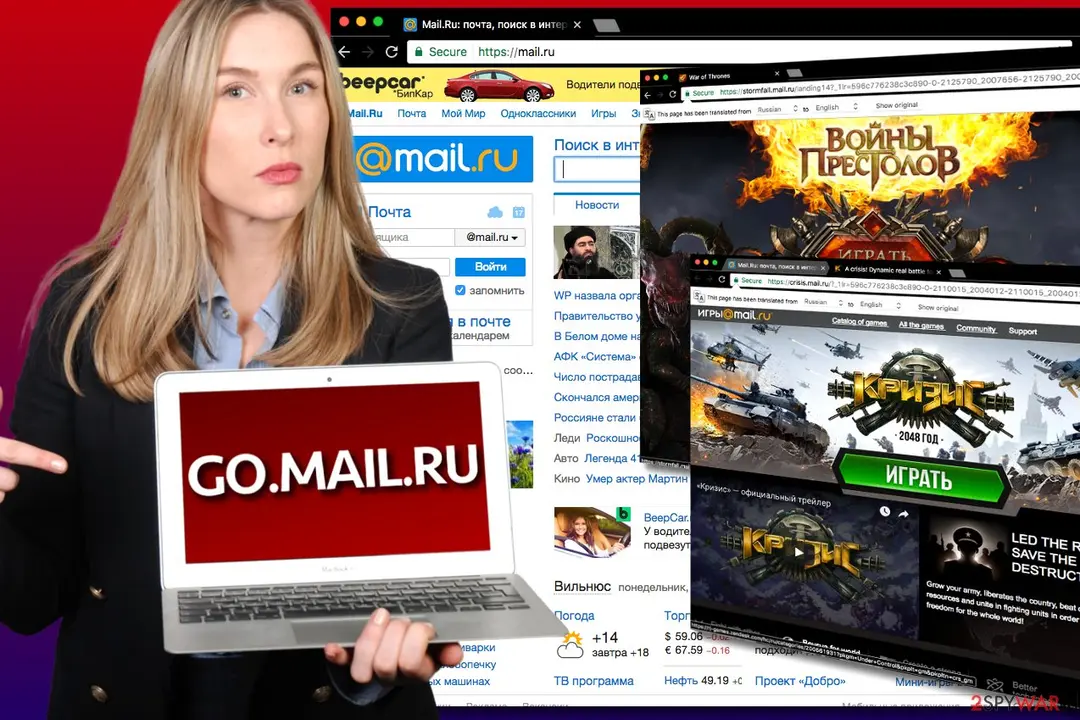
Mail.ru is a website that has been actively promoted with the help of potentially unwanted programs (PUP).
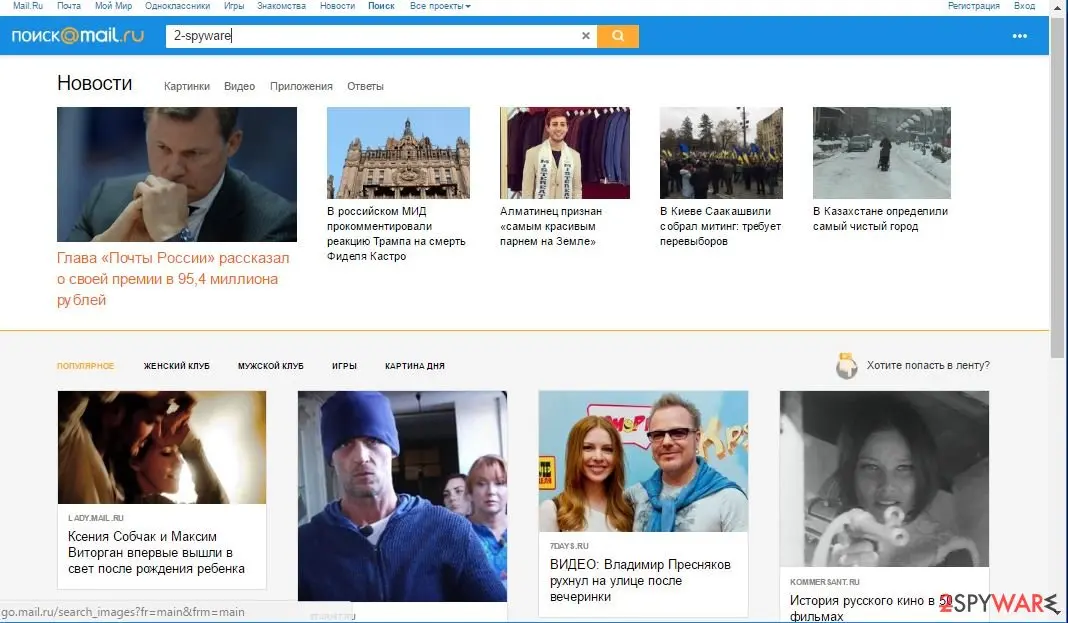
It operates as a browser hijacker and mostly targets Russian-speaking users. In most cases, people experience suspicious redirects to this site after a certain event on the system, mainly, when a new browser extension or application is installed on the device.
There could be many different apps that promote Mail.ru, so its removal varies from person to person. The threat mostly aims at Google Chrome and Mozilla Firefox browsers, although other browsing tools can be affected as well.
Once inside the computer, the virus redirects them to desired locations by presenting forged search results. As a result, the PUP negatively affects the performance of your browser or device in general.
One of the most common symptoms of browser hijacking is changes made not only to the homepage/new tab URL but also to the search provider. For example, if you previously used google.com for your searches, now you would see an alternative provider instead, namely, Mail.ru.
Another distinctive trait of a hijacker is its ability to insert promotional links at the top of search results. These links might sometimes show misleading information or urge users to subscribe to useless services. Thus, we strongly recommend staying away from ads at the top of the results provided by this hijacker.
Mail ru virus is designed to take control over the targeted web browsers and users' browsing habits. This browser hijacker might:
As you can see, the program that promotes the suspicious page is designed to complicate browsing sessions on the affected computer. One of the most annoying features is that users cannot set their preferred startup page and built-in search engine due to the hijacker's functionality.
The virus protects itself by installing additional browser add-ons and extensions which will automatically set the malicious domain as a homepage once the user tries to delete or reset them. It is also known that the hijacker creates C:\Program Files (x86)\Mail.Ru\ and C:\Users\Home\AppData\Local\Mail.Ru folders in the system.
However, the removal is still possible and recommended due to suspicious redirect tendencies and possible privacy-related issues. For quick hijacker elimination, you should use and then either reset the browser or clean it with (you can also do it manually - we explain how below).
- set hxxp://go.mail.ru/search as a search provider and default start page;
- include sponsored links among search results;
- redirect to suspicious third-party websites;
- display ads, pop-ups, in-text, and other types of commercial content on visited websites;
- track information about users;
- prevent users from Go.mail.ru removal.
From our report of Oct 2026 · not reviewed since
Redirects might bring you to malicious websites
Mail.ru virus forces people to use a questionable search engine that might contain links to highly suspicious sites.
Some of the links on the results page might be altered, meaning that you might be tricked into clicking sponsored links that barely have something in common with the information you searched for.
However, the main issues related to the redirect tendencies are that the hijacker might trick you into visiting phishing, tech support scam, or infected websites. Therefore, your chances to suffer from cybercrime increase after browser hijack.
Nevertheless, the Mail ru virus is not dangerous itself; it creates the right conditions to browse through insecure or potentially harmful sites. Keep in mind that the same problem exists with ads that might be displayed on any website too.
The problem with ads displayed by the virus is that they might look legitimate and useful. However, the reason why is very simple. The PUP can collect information about your browsing activities, including search queries, browsing history, IP address, and other personally non-identifiable information with the help of tracking cookies and web beacons.
Aggregated details help to display targeted ads that you are more willing to click. Keep in mind that authors of the hijacker generate revenue from ad clicks and boost traffic to sponsored sites. To make as much money as possible, the hijacker might display an enormous amount of commercial content which diminishes the browsing experience. Hence, it's necessary to remove the infection to get back to safe browsing.
From our report of Oct 2026 · not reviewed since
Freeware bundles may contain browser hijackers
As you already know, Go.mail.ru is a Russian website, but it does not imply that you can only infect your computer if you live in this specific region, visit Russian websites, or download software originating from this country. In fact, this potentially unwanted program mainly travels via software bundles, so there is no actual difference to what programs is it attached to.
The important thing is to know how to disclose such programs and stop them from being installed on your computer. Fortunately, it is quite simple. When installing new programs on your computer, choose "Advanced" installation settings and follow the installation stages carefully. If some shady software package components emerge, eliminate them immediately and proceed with the installation safely.
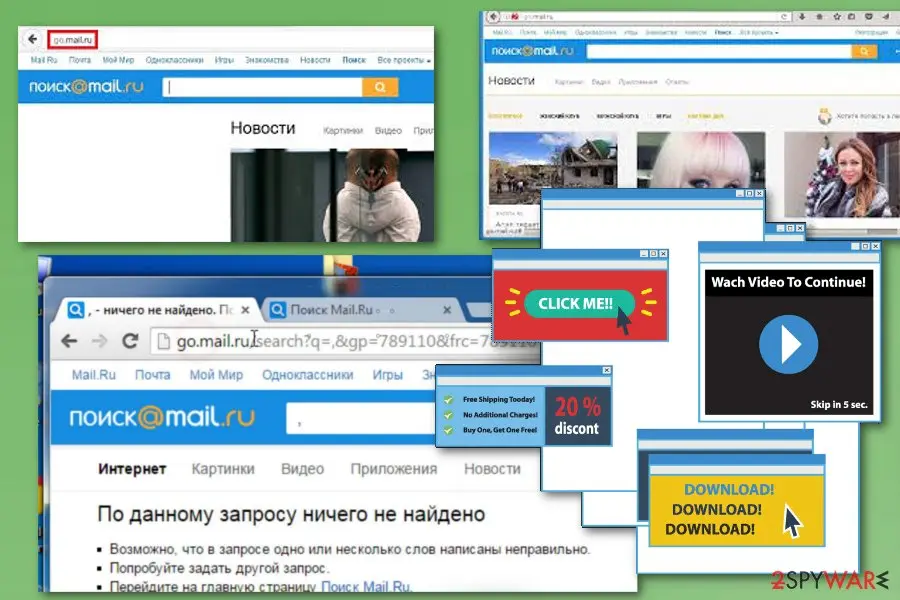
From our report of Oct 2026 · not reviewed since
More from our earlier report on Mail.ru
- Repair virus damage and clean your browsers with PC maintenance and repair utility
Check your browser and PC
- Address:
mail.ru
How to remove Mail.ru
How to remove Mail.ru and get your search engine back
Remove the extension first.
The search settings only stay fixed once nothing on the PC can change them again.
Step 1: Remove extensions you did not add
Mail.ru often works through an extension, so go through the extension list of each browser:
chrome://extensionsedge://extensions- Extensions and themes in Firefox
Switch suspicious extensions off one at a time and reload the page where the problem shows, then remove the one that stops it, and any other you did not add.
Remember the other browsers and profiles on the PC. If Remove is missing or greyed out, a policy forces the extension, which the policy step deals with. Windows 11 and Windows 10 show the same pages.
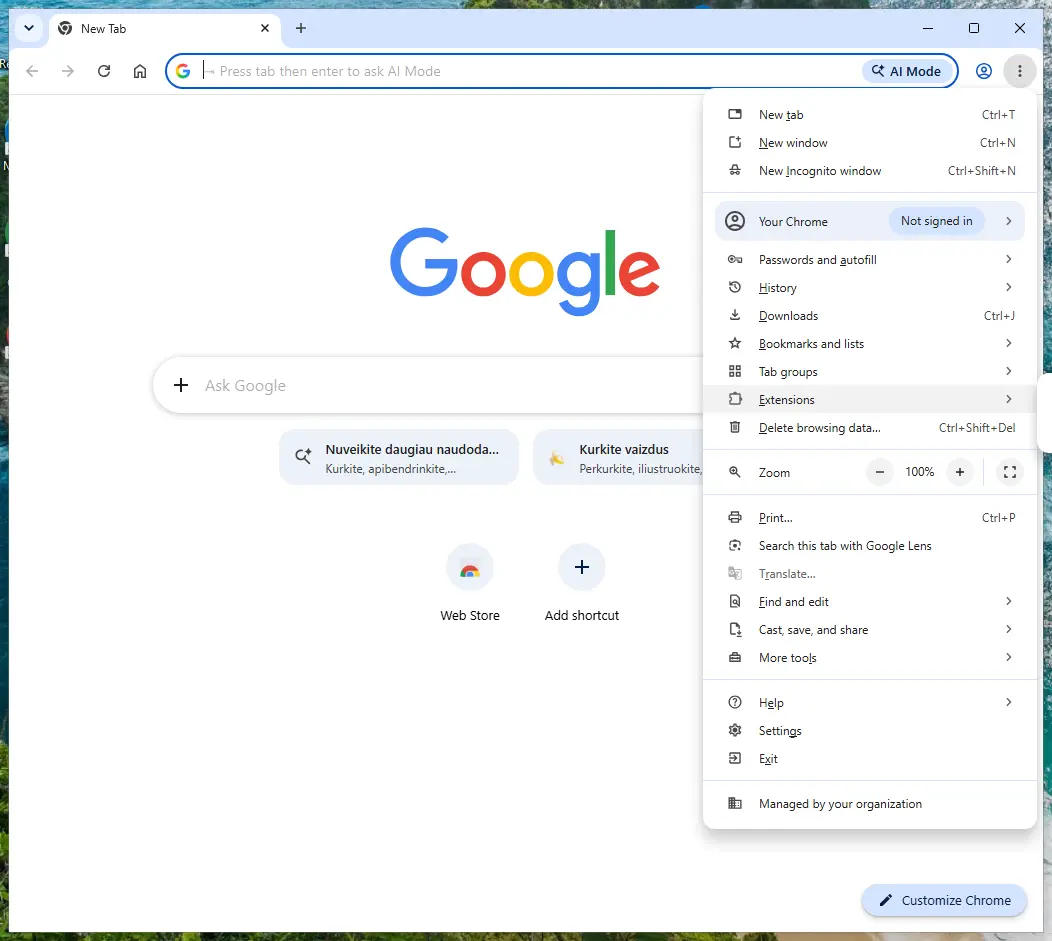
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Put the search engine back and delete mail.ru
Searches that pass through
mail.rumean the browser's default search engine was replaced. Chrome: Settings > Search engine > Manage search engines and site search, then Make default on Google, Bing or another engine you chose, and Delete on mail.ru.Edge has the same list under Manage search engines (search the Settings page for it), and Firefox under Settings > Search.
Look at On startup and the homepage settings too and remove the hijacker's address there. Nothing in this step differs between Windows 11 and Windows 10.
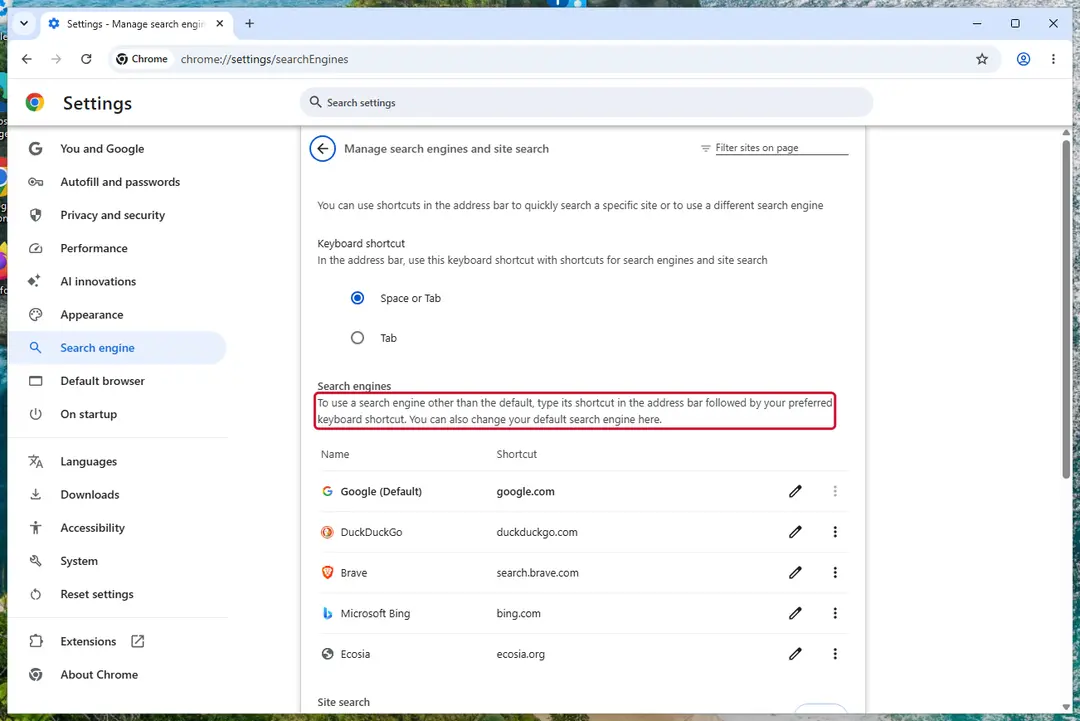
Chrome on Windows 11: check Search engine and On startup. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 3: Uninstall programs you did not mean to install
Open Settings > Apps > Installed apps in Windows 11, or Settings > Apps > Apps & features in Windows 10, and sort the list by install date. Look at what appeared around the day the problem started and uninstall every program you do not recognise or did not choose.
Free converters, PDF and video tools, "system optimizers" and unknown browsers are the usual carriers of Mail.ru. If a name is unclear, search for it before you remove it, so you do not uninstall a driver or a Windows component.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 4: Reset the browser
Finish the browser part with a reset, which puts the search engine, start page, new tab page and site permissions back to their defaults and switches extensions off. Chrome: Settings > Reset settings > Restore settings to their original defaults.
Edge: Settings > Reset settings. Firefox: Help > More troubleshooting information > Refresh Firefox, which also removes its extensions. Your bookmarks and saved passwords are kept, and the menus are the same on Windows 11 and Windows 10.
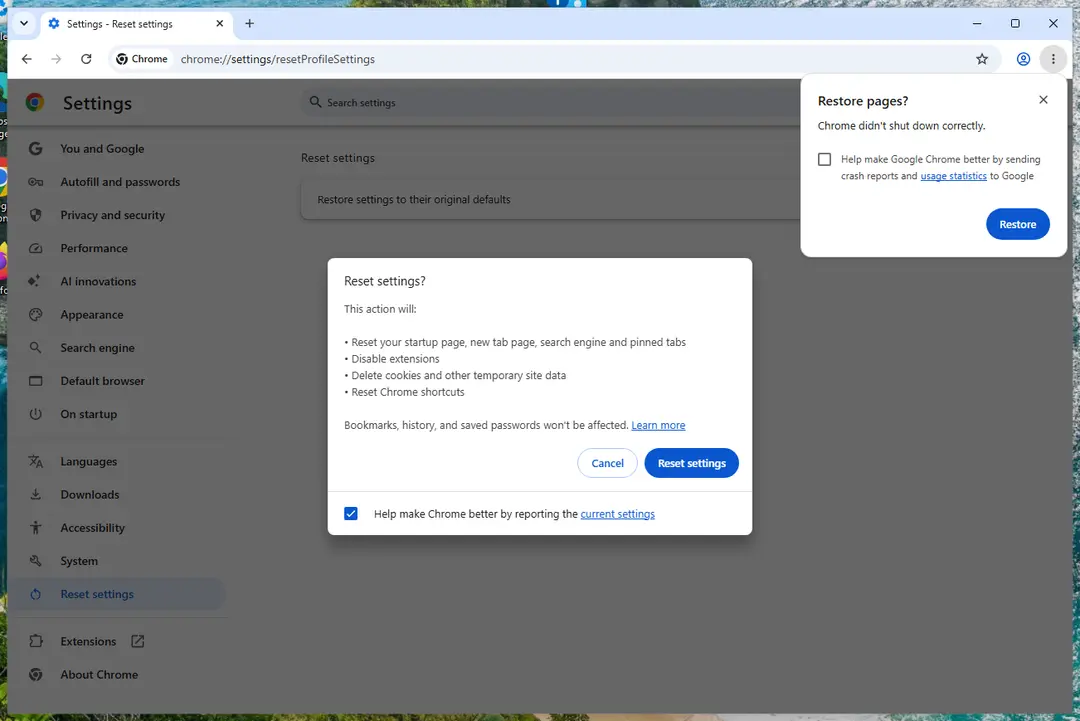
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
To delete the virus from Windows, you need to uninstall programs that are related to it. Keeping them on your computer system is a major problem and not all of the antivirus systems are capable of identifying them, as the criteria for potentially unwanted program detection differs from vendor to vendor. Thus, we have prepared these instructions to help you get rid of the virus manually. We hope that you will manage to find the virus (which may be hiding under different titles) and banish it from the system successfully. What is even more important is that you check shortcuts of Chrome, Firefox, and other popular browsers the way that we described below. Sometimes browser hijackers compromise these shortcuts so that the user would experience redirects to the suspicious search site each time he opens a web browser. TIP: This browser hijacker often tries to modify Registry keys, browser shortcuts, and other system settings just to keep itself in the system. System settings, especially Windows Registry should be altered by experienced IT professionals only, so if you do not want to spend a day trying to delete the virus manually, we highly recommend using an automatic spyware/malware removal tool. Make sure you update it to the latest version and run a couple of system scans to entirely eliminate the threat.
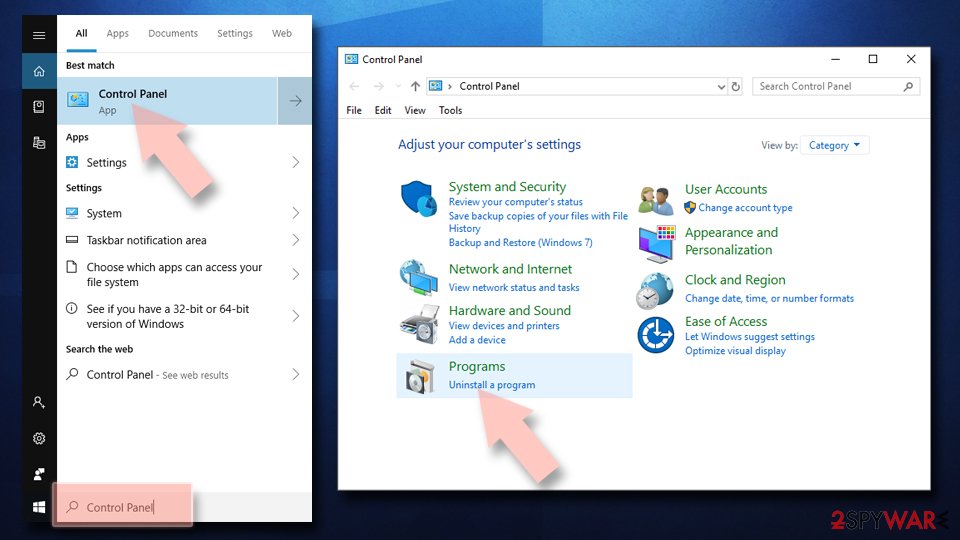
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
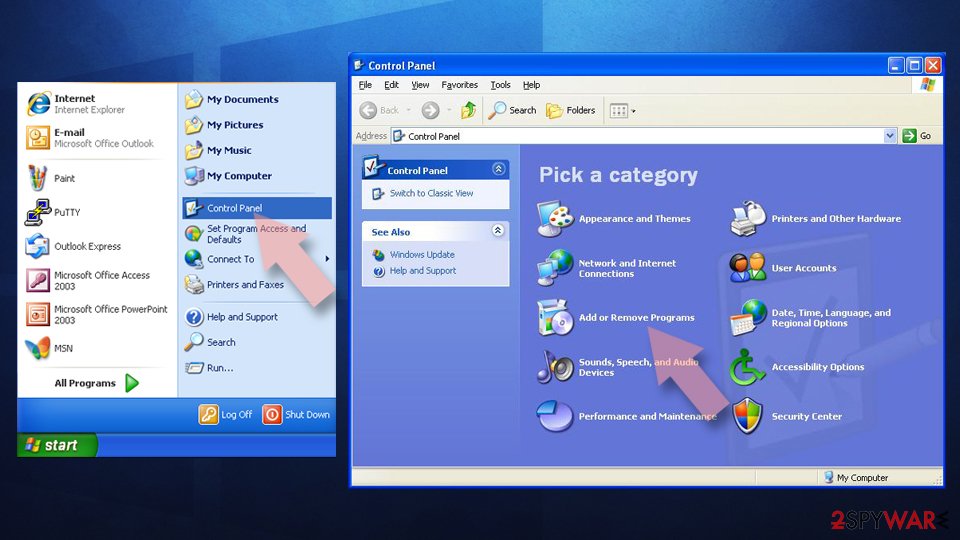
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
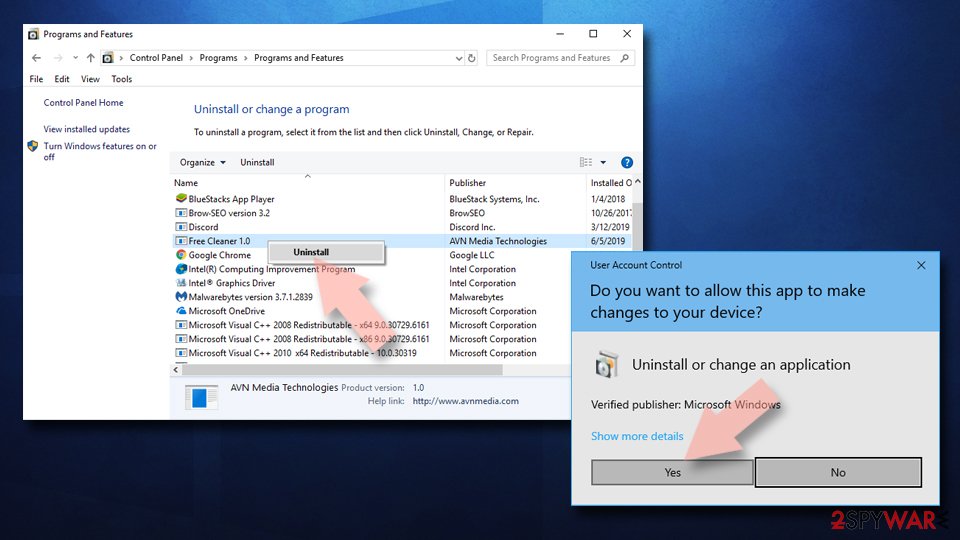
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
To remove the PUP from Chrome, you need to: 1. Delete associated browser extensions. 2. Delete suspicious URLs from the "On Startup" setting and also from the "Default Search" setting. 3. Reset Chrome browser.
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
To uninstall the virus from Firefox, you need to delete Firefox add-ons related to it. We suggest looking for all kinds of suspicious add-ons, especially ones that promise you an "improved search experience." Once you delete the suspicious Firefox add-ons, refresh your browser.
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
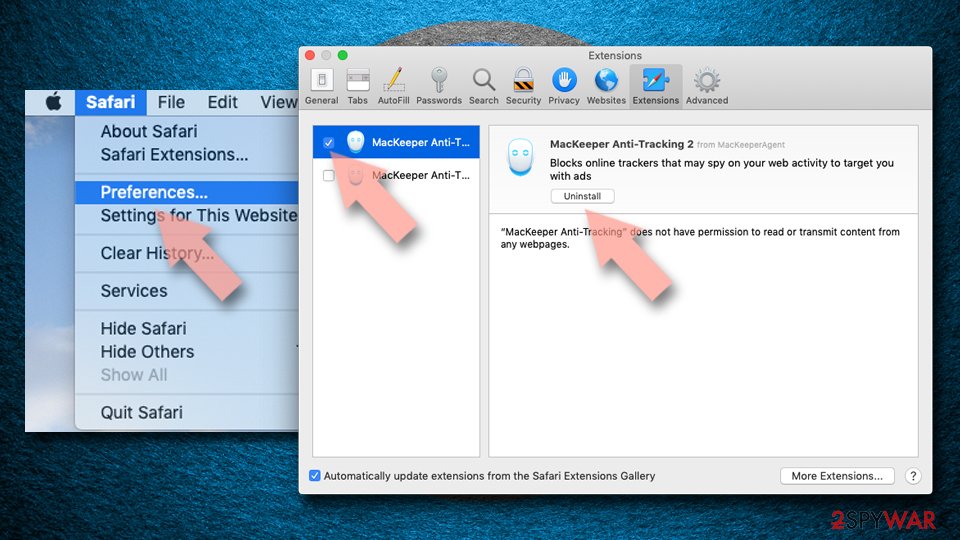
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
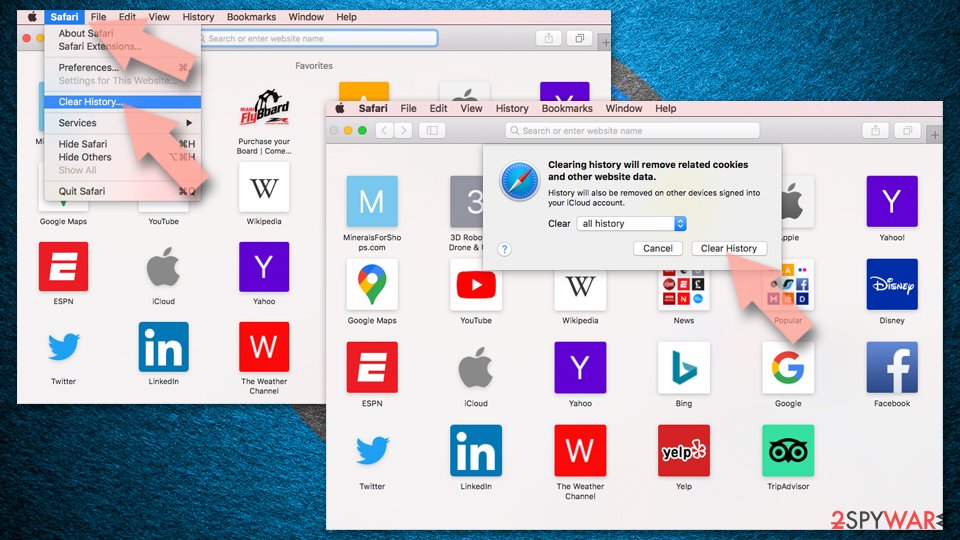
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
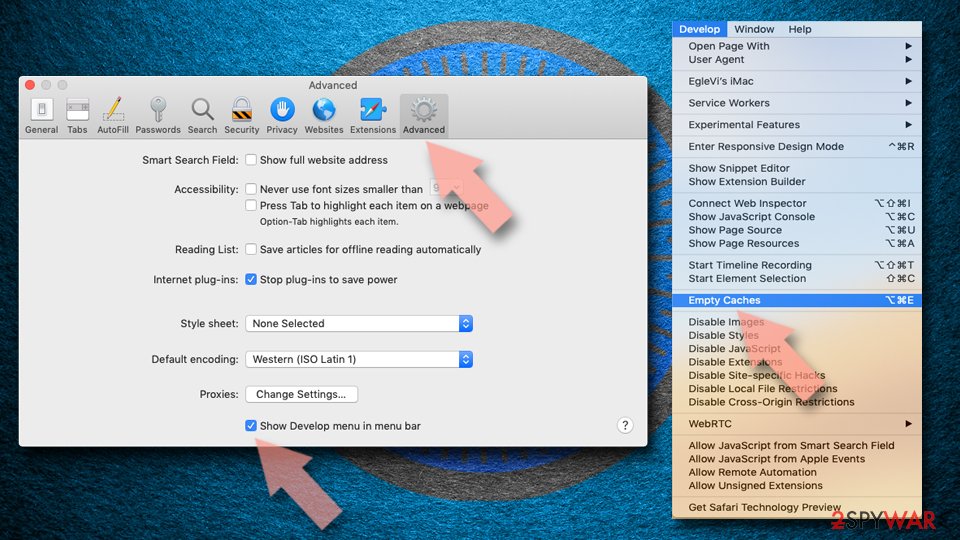
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
Remove the unwanted application:
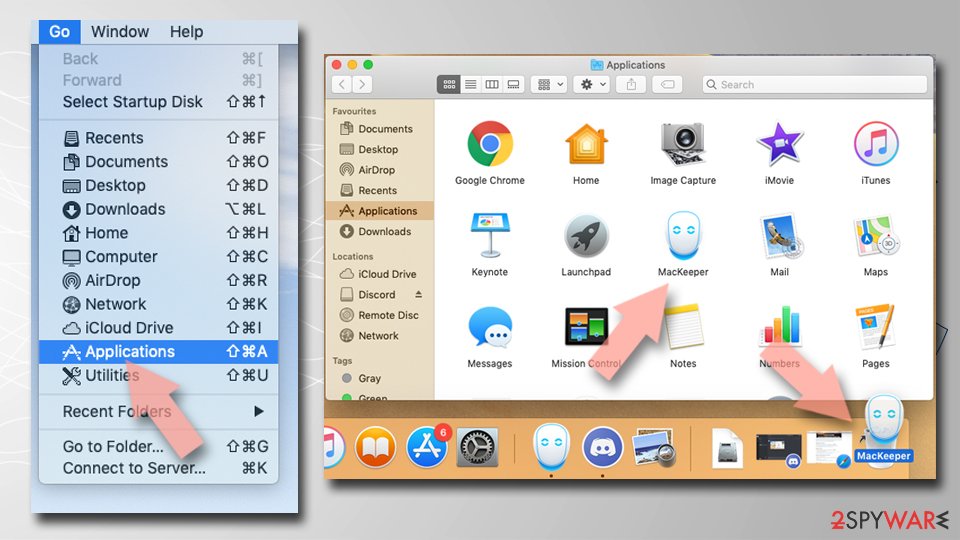
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
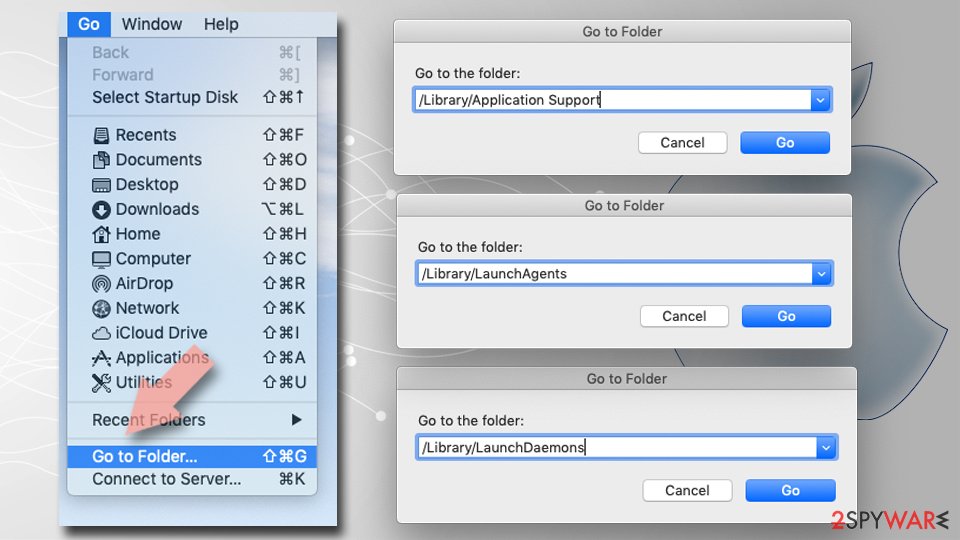
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
From our report of Oct 2026 · not reviewed since
Get rid of browser hijacker
After a browser hijack, many users struggle with the removal process of the unwanted program.
The hijacker might be hard to remove because it might alter the browser's settings and Windows Registry. Hence, all the attempts to change this Russian website with a preferred startup page are designed to fail.
You can find our suggested removal tools below, or you can choose any other reliable anti-malware/anti-spyware.
Additionally, you can follow our prepared instructions at the end of the article and opt for manual Go.mail.ru removal. This method requires uninstalling suspicious extensions from the browser. Keep in mind that the name of the app might be literally anything, and even seemingly trusted add-ons might sometimes be the reason for browser hijacking.
Don't forget that one of the main reasons why browser hijackers return is due to incomplete removal procedures. Therefore, make sure you either reset your browsers or clean them appropriately as we explain below.
Thus, we have prepared these instructions to help you get rid of the virus manually. We hope that you will manage to find the virus (which may be hiding under different titles) and banish it from the system successfully.
What is even more important is that you check shortcuts of Chrome, Firefox, and other popular browsers the way that we described below. Sometimes browser hijackers compromise these shortcuts so that the user would experience redirects to the suspicious search site each time he opens a web browser.
TIP: This browser hijacker often tries to modify Registry keys, browser shortcuts, and other system settings just to keep itself in the system.
System settings, especially Windows Registry should be altered by experienced IT professionals only, so if you do not want to spend a day trying to delete the virus manually, we highly recommend using an automatic spyware/malware removal tool. Make sure you update it to the latest version and run a couple of system scans to entirely eliminate the threat.
1. Delete associated browser extensions.
2. Delete suspicious URLs from the "On Startup" setting and also from the "Default Search" setting.
3. Reset Chrome browser.
Questions about Mail.ru
What is Go.mail.ru virus?
Go.mail.ru virus is a browser hijacker that redirects users to Mail.ru, a Russian email and web services platform. The potentially unwanted program forces users to navigate to go.mail.ru by modifying browser settings. Mail.ru is a legitimate Russian website, but the hijacker's deceptive distribution and forced redirection classify it as malware.
The threat primarily targets Russian-speaking users but also affects speakers worldwide. When tested on 2026-10-04, go.mail.ru loaded with Google AdSense and Google Ad Manager advertising networks. The hijacker was first reported in 2021 and continues actively infecting computers through potentially unwanted programs bundled with software.
How does Go.mail.ru virus hijack your browser?
Go.mail.ru hijacking involves modifying multiple critical browser settings simultaneously. The virus changes your homepage to go.mail.ru/search and sets your default search engine to Mail.ru services. The new tab page redirects to the Mail.ru homepage instead of displaying your preferred start page.
The hijacker may also alter your startup preferences and browser toolbar settings. Once installed, the threat sets hxxp://go.mail.ru/search as your search provider, inserting sponsored links among search results.
The program protects itself by installing additional browser add-ons and extensions that automatically revert any user attempts to change these settings back to defaults. Even when users manually restore their settings, the hijacker's helper programs automatically re-enable the redirects.
Why does Go.mail.ru keep resetting your browser settings?
Go.mail.ru installation creates multiple protection mechanisms preventing permanent removal of the hijack. The virus installs dedicated browser extensions and add-ons designed to monitor browser settings.
When users attempt changing their homepage or search engine, these helper programs detect the change and immediately revert settings back to Mail.ru. Additionally, the hijacker creates registry entries in Windows that automatically launch the redirection service whenever your computer starts.
The program modifies Windows Registry folders at C:\Program Files (x86)\Mail.Ru\ and C:\Users\Home\AppData\Local\Mail.Ru\ containing configuration files maintaining the hijack. This multilayered protection makes temporary setting changes ineffective. Complete removal requires eliminating the main program and all associated helper components simultaneously.
Is Go.mail.ru virus dangerous?
Go.mail.ru virus is not inherently dangerous but creates conditions enabling dangerous situations. The hijacker itself doesn't directly damage your computer, but redirects may lead you to malicious websites. Altered search results mix legitimate links with dangerous content, potentially directing you to phishing sites designed to steal credentials.
Tech support scams frequently target hijacked browsers, claiming your computer is infected and urging expensive fake software purchases. The redirect tracking enables cybercriminals to monitor your searches and browsing patterns, potentially identifying valuable personal information for targeted attacks. Additionally, forced use of less secure search providers and advertising networks increases exposure to malicious advertisements promoting malware installations.
How does Go.mail.ru reach your computer?
Go.mail.ru predominantly spreads through potentially unwanted program bundling within freeware and shareware installations. When users download seemingly legitimate programs from third-party websites, Go.mail.ru arrives as an bundled component.
Using Quick or Recommended installation settings automatically installs bundled PUPs without user awareness. Additionally, Go.mail.ru may arrive through fake software updates, malicious websites, or compromised advertising networks. Some users intentionally download the hijacker unaware of its malicious characteristics.
The Russian origin often leads developers to specifically target Russian-language systems, but the threat affects users worldwide. Users selecting Advanced installation modes and carefully reviewing included components significantly reduce infection risk.
How do you identify Go.mail.ru infection?
Several warning signs indicate Go.mail.ru hijacker infection requiring immediate attention. Your homepage changes to go.mail.ru without your permission, appearing every time you open your browser. Your default search engine changes to Mail.ru services, even after attempting to restore Google.
Your browser's new tab page opens to Mail.ru instead of your preferred page. Search result pages include promotional links at the top that don't match your search query accurately.
You cannot permanently change browser settings, as they revert automatically. Your browser displays excessive advertisements, particularly Russian-language promotional content. These symptoms collectively indicate successful Go.mail.ru installation.
How do you remove Go.mail.ru hijacker?
Removing Go.mail.ru requires both automatic anti-malware software and manual browser cleaning. First, scan your computer with reputable anti-malware that recognizes PUPs. The software should detect and eliminate the main Go.mail.ru program and all associated registry entries.
After removal, reset your browser to default settings. In Chrome, click the menu, select Settings > Advanced > Reset and clean up. In Firefox, help > Troubleshooting > Refresh Firefox.
In Edge, three-dot menu > Settings > Reset settings. After browser reset, check all installed extensions and remove any unfamiliar entries. Check your Windows Control Panel Programs & Features for suspicious applications installed around the infection date and uninstall them.
How do you prevent Go.mail.ru infection?
Prevent Go.mail.ru infection by downloading software exclusively from official developer websites. When installing any program, select Advanced or Custom installation modes instead of Quick or Recommended options. These advanced modes reveal bundled components, allowing deselection of unwanted applications.
Read all installation screens carefully and uncheck any pre-ticked boxes offering additional software. Avoid third-party software repositories and freeware download sites known for bundling PUPs. Install and maintain reputable antivirus software with updated threat definitions.
Keep your operating system and browsers updated, as older versions lack security patches protecting against newer hijackers. Be extremely cautious when clicking browser advertisements, as malvertising campaigns frequently distribute Go.mail.ru and similar hijackers.
Will Fortect remove Mail.ru?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Mail.ru, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- MakeUseOf: Which Websites Are Most Likely to Infect You with Malware? (read October 5, 2026)
- The Guardian - Technology: Tracking the trackers: What are cookies? An introduction to web tracking (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)
- Microsoft Learn: How Microsoft names malware (read October 5, 2026)