
Hancitor: what it is and how to remove it
Hancitor Trojan first emerged in 2014 and immediately spread relatively widely thanks to extensive malspam campaigns. This is not the only method used by cybercriminals to spread it, as later phishing and fake links were also used to infect Windows computers worldwide.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Unsure whether ReimageRepair.exe is safe? A free scan checks the file and what starts it.
Do it yourself · free Remove Hancitor yourself 6 steps, about 18 minutes, no software needed.
Start the steps
Hancitor: summary
| Distribution | Malware typically spreads via contaminated MS Office email attachments or fake online ads |
|---|---|
| Name | Hancitor |
| Other names | Tordal, Chanitor |
| Type | Trojan, downloader |
| Release | 2014, operates as a malware-as-a-service |
| Purpose | Download and install additional malware |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Symptoms | An unknown process in Task Manager |
| Evidence | 4 write-ups by security sites; details still limited |
| File names | ReimageRepair.exe |
| First seen | 10 December 2021 |
| Facts checked | 6 October 2026 |
What Hancitor does on an infected PC
From our report of Dec 2021 · not reviewed since
Malware-as-a-service
As previously mentioned, Hancitor operates under the MaaS scheme, which is becoming even more popular over the years.
This behavior is typical of large-scale malware strains such as WannaCry, which created a mass-havoc in 2017, infecting high-profile organizations and institutions worldwide with over 300,000 computer infections.
What makes MaaS so appealing is that the whole process is fully automated - it's not that different from a person buying an item on Amazon, except that the shopping list is something that is meant for malicious purposes.
It allows even non-proficient people to buy access to even the most complex malware and distribute it as they please, all while getting a big chunk of the profits earned from the illegal activity.
The developers of malware are the ones who update and improve it, distributors spread it around, and administrators make sure that the business runs smoothly. Of course, all these operations happen underground and, since a lot of obfuscation is used, it becomes more difficult for law enforcement to tackle it. Nonetheless, there have been many successful operations where MaaS schemes were shut down and operators put in prison.
From our report of Dec 2021 · not reviewed since
More from our earlier report on Hancitor
- Perform a full system scan with or another reputable anti-malware
How Hancitor got on your PC
From our report of Dec 2021 · not reviewed since
Hancitor is a widespread Trojan that downloads other malware onto infected systems or networks
Hancitor Trojan first emerged in 2014 and immediately spread relatively widely thanks to extensive malspam campaigns.
This is not the only method used by cybercriminals to spread it, as later phishing and fake links were also used to infect Windows computers worldwide. Since its release, the virus authors developed multiple versions with various improvements and polished its functionality over time.
Hancitor operates as Malware-as-a-Service (MaaS) - a popular technique where the developers allow customers (who can be at any level of skill or experience within the field) to rent the rights to distribute malware, as long as a certain portion of the profit is shared. Typically, the distributors are allowed to keep the bigger part of the money.
The main purpose of the virus is to compromise the affected machine and the network it is connected to, which would allow the attackers to deliver any type of payloads.
In other terms, the malware is used as a middle-man in order to infect targets with other malicious software. The secondary payload can be literally anything; most recently, in May 2021, it was spotted being delivering Cuba ransomware, mainly targeting governmental, healthcare, IT, manufacturing, and financial sectors.
As evident, the presence of the Hancitor virus can be devastating, as its activity can allow any type of malware to be delivered and installed. Victims might have their personal formation stolen, files encrypted, or credit card details exposed.
From our report of Dec 2021 · not reviewed since
Distribution
Malware distribution is vital for its success, and many experienced malware creators are well aware of that.
If anything, malware is a business and, while it is highly illegal, it operates in a similar manner, as we already explained in the previous section.
Due to the large number of people who can get access to Hancitor, numerous different distribution techniques could be applied. It is evident that new, advanced methods are developed over time (for example, fileless infection), although some old ones work just as well, and the Trojan is mostly delivered via malicious spam emails and phishing campaigns.
Spam emails are probably the most common malware distribution technique of all and have been used since the begging of the internet. There are all sorts of emails that could be used - some are very plain, including just a few words and an attachment; others might not even include any text in them.
There are plenty of more sophisticated email spam campaigns, however. Quite often, cybercriminals use familiar brand names (UPS, Google, Microsoft, etc.) and the formatting of the email to make it look more legitimate. Email spoofing is another technique that is widely used - where the sender's email matches a legitimate one.
It is vital to be extremely wary when dealing with emails, especially those that include attachments or links. Employing additional protection tools that recognize spam can help, although awareness is the best remedy.
How to check the PC for Hancitor
- File:
ReimageRepair.exe
How to remove Hancitor
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where ReimageRepair.exe runs from and stop it
In Task Manager (Ctrl + Shift + Esc) find
ReimageRepair.exeon Processes, right-click it and choose Open file location before ending anything.Windows' own files live in
C:\Windows\System32; the same name in%AppData%, %Temp% or C:\Users\Public is an impostor. If the folder is wrong, right-click the process again, choose End task and delete the file.If it starts again within seconds, a task or another process restarts it, so run the scan step in Safe Mode. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Programs like Hancitor add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 3: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after Hancitor, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
A scan finds the parts of Hancitor that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Hancitor can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
From our report of Dec 2021 · not reviewed since
Hancitor removal
It is important to remove all the malicious components and secondary payloads that the malware brings as soon as possible.
The longer malware runs in the background, the more damage it is capable of causing. For example, the secondary payload of ransomware could encrypt all file backups if they are not adequately protected.
From our report of Dec 2021 · not reviewed since
Step 1. Disconnect your computer from the internet and network
To start the removal process, you should disconnect every infected computer from the network.
If only one or a few machines are affected, this can be done by simply unplugging the network cable or disconnecting the WiFi. However, for larger networks, the following method should be used:
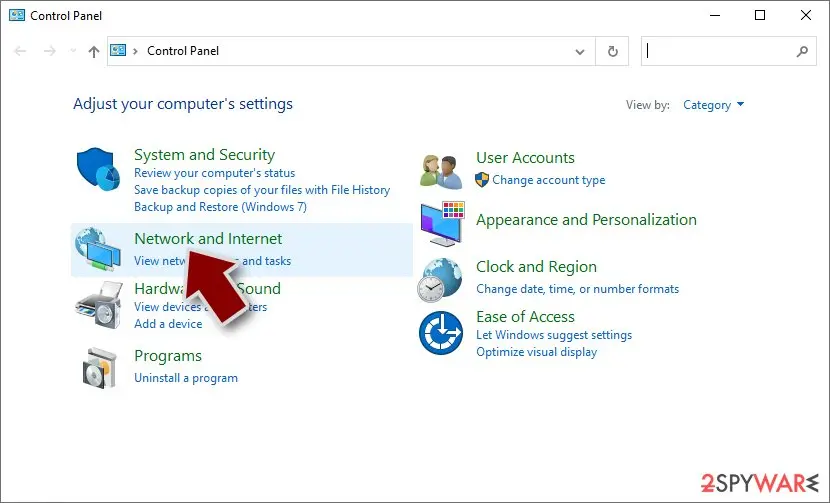
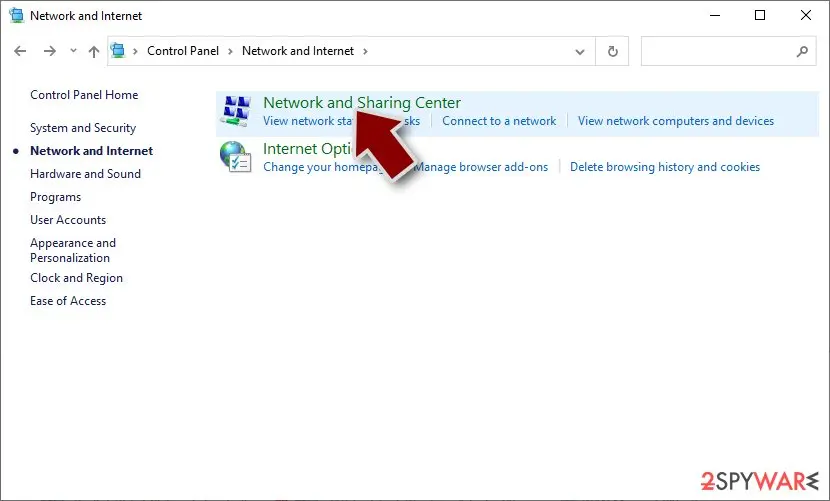
- Type in Control Panel in Windows search and press Enter
- Go to Network and Internet
- Click Network and Sharing Center
- On the left, pick Change adapter settings
- Right-click on your connection (for example, Ethernet), and select Disable
From our report of Dec 2021 · not reviewed since
Step 2. Perform a full system scan
Complex malware is unlikely to be removed properly using manual steps.
Instead, victims should employ powerful security software, such as or , and perform a full system scan with it. Keep in mind that this step should only be done after the infected machine is segregated from any other computers (disconnected from the network and internet).
Since there could be multiple infections within a compromised system, Hancitor removal might be difficult.
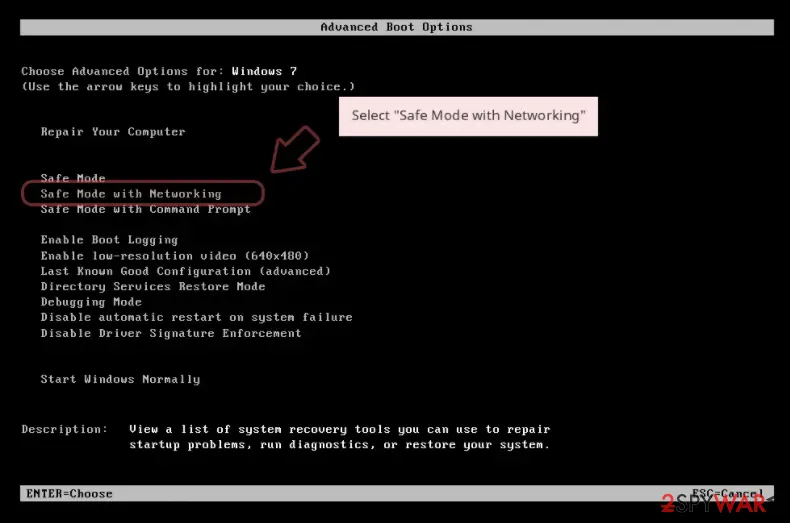
Windows 7 / Vista / XP
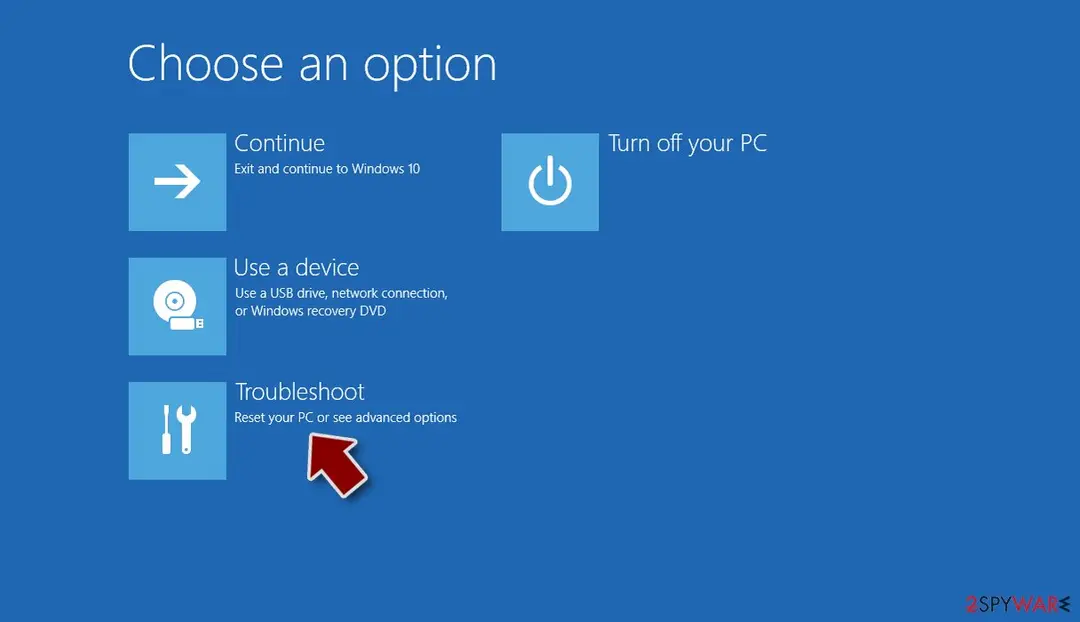
Windows 10 / Windows 8
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing the F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
- Right-click on the Start button and select Settings.
- On the left side of the window, pick Recovery.
- Click Restart now.
- Select Troubleshoot.
- Go to Advanced options.
- Select Startup Settings.
- Click Restart.
- Press 5 or click 5) Enable Safe Mode with Networking.
From our report of Dec 2021 · not reviewed since
Step 3. Other security tips
Security experts always advise corporations and home users to be aware of cyberattacks and their dangers.
Being neglectful is one of the main reasons why the illegal business of malware thrives, and MaaS operations are so successful. Here are a few security tips that should help you avoid having your device getting infected with Trojans or other malicious software in the future:
- Install , , or another reputable anti-malware software to prevent the infiltration of malware;
- Always use strong passwords for all the accounts, especially those for remote connections (RDP);
- Make sure all software, including the operating system, is applied with the most recent security updates as soon as they are available;
- Enable two-factor authentication for any incoming connections or other important accounts;
- Beware of emails that include attachments (especially if they require to enable macro function upon being opened);
- Employ phishing protection tools and be wary of any third-party links - do not download software cracks and similar high-risk components from the internet.
From our report of Dec 2021 · not reviewed since
Repair damaged system files
Once malware manages to breach the system, It compromises its integrity and sometimes can corrupt vital components of the OS.
This might result in serious stability issues, such as program crashes, system reboots, BSODs, and similar, in the future.
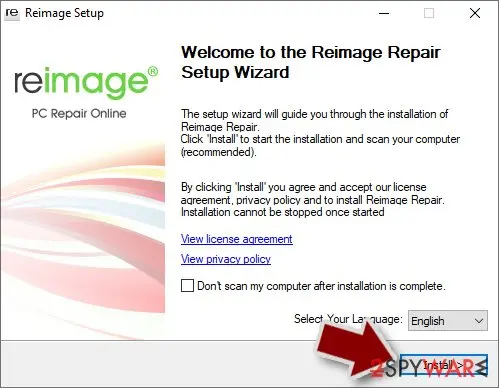
- Download
- Click on the ReimageRepair.exe
- If User Account Control (UAC) shows up, select Yes
- Press Install and wait till the program finishes the installation process
- The analysis of your machine will begin immediately
- Once complete, check the results - they will be listed in the Summary
- You can now click on each of the issues and fix them manually
After removal: passwords, accounts and prevention
Your passwords after Hancitor
Removing Hancitor does not undo what it may already have sent out while the PC showed an unfamiliar process called ReimageRepair.exe in Task Manager.
Treat saved browser passwords and logged-in sessions on this PC as known to the attacker.
From another device, change the e-mail password first and end all its sessions. Then do the same for the bank, PayPal, Microsoft, Google and Apple accounts. Stolen session cookies keep working after a password change until you sign out everywhere.
Move crypto to a new wallet created on a clean device. A step-by-step order for every kind of account is in our guide to account security after an infection.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about Hancitor
Is ReimageRepair.exe safe?
It depends on where the file is and who signed it, not on the name. Open Task Manager, go to the Details tab, right-click ReimageRepair.exe and choose Open file location. A file inside Program Files or System32 with a valid digital signature from a known company is usually part of a legitimate program.
A file in AppData, Temp or ProgramData with no signature, especially one that restarts itself after you end it, is suspicious. If you cannot tie the process to anything you installed, uninstall recent unfamiliar programs and run a Microsoft Defender Offline scan.
Can I end ReimageRepair.exe in Task Manager?
Ending an unknown process is safe in the sense that Windows will warn you before you close anything critical, and a restart brings back whatever Windows needs. Ending ReimageRepair.exe will not remove it, though: if a task or startup entry launches it, it returns at the next sign-in.
Use ending the process as a test. If something important stops working, it belonged to a program you use. If nothing changes and it comes back by itself, find and disable its starter, delete the file and scan the PC.
Is ReimageRepair.exe a virus?
If it sits outside the Windows and Program Files folders and your antivirus links it to Hancitor, yes. ReimageRepair.exe is the file name used by this trojan. Some trojans borrow the names of real Windows components, so the name alone does not decide it:
- right-click the process in Task Manager
- choose Open file location
- look at the folder and the publisher under Properties > Details
A file in a user folder with no publisher is the trojan. Do not delete it by hand while it runs; use the offline scan in the plan above.
How do I know if my PC has Hancitor?
Often you do not, which is the point of a trojan. Possible signs are an antivirus alert naming Hancitor or a generic trojan detection, unknown programs or scheduled tasks, processes with random names in Task Manager, browser extensions you did not add, security settings turned off, slower performance, or account alerts about logins from unknown places.
The reliable check is a full scan followed by Microsoft Defender's offline scan. If you recently ran a crack, a fake installer or a command a website told you to paste, scan even without symptoms.
Do I need to reinstall Windows to get rid of Hancitor?
Usually not. A thorough clean-up is enough when the offline scan finds nothing afterwards and you do not see an unfamiliar process called ReimageRepair.exe in Task Manager again. A reset is the safer choice if an attacker had remote control, if security tools were switched off, or if detections come back after every clean-up.
Windows 11 can reset itself without a USB stick under Settings > System > Recovery > Reset this PC. Copy documents and photos out first and scan the copies. A reset does not change passwords or undo stolen data, so the account steps still apply.
Can I keep using the PC while Hancitor is on it?
Not for anything that matters. As long as the program behind an unfamiliar process called ReimageRepair.exe in Task Manager runs, it can see what you type and what the browser stores, and it may download more malware. Disconnect the PC from the internet while you remove it, and do your banking, e-mail and password changes from another device.
Once the offline scan finds nothing and the sign does not return after a few restarts, normal use is fine. If the scan keeps finding new items, or you cannot remove the startup entry, a reset of Windows is the safer choice.
Which malware family is Hancitor?
That is not known yet. Hancitor has been reported by people who saw an unfamiliar process called ReimageRepair.exe in Task Manager, but no sample has been analysed publicly, so security companies have not assigned it to a family. The name you see may be a file or program name chosen by the authors, not a family name.
This does not stop you from removing it: the startup points, the offline scan and the account steps are the same for most families of this type. If Microsoft Defender or another scanner gives the file a detection name, write it down; that name is the best clue to the family and is useful when you report the incident.
Should I check my other computers too?
Yes, it takes little time and removes doubt. Hancitor itself usually stays on one PC, but the download that carried it may have been copied to other computers, shared drives may hold the same installer, and an attacker who had access could have tried saved passwords on other devices.
Run a full scan on every Windows PC in the home or office, check shared folders for the original download, and change Wi-Fi and router passwords if they were stored on the infected machine.
I found AnyDesk or ScreenConnect that I did not install. Is that Hancitor?
Not necessarily Hancitor, but it is a warning sign. These are legitimate remote support tools, and criminals use them as ready-made backdoors, especially after tech support scams or fake invoice calls.
If you did not install it and no one you trust set it up, uninstall it, change passwords from a clean device and check your bank account. If someone connected to your PC through it, follow the steps for remote access trojans and consider a Windows reset. Installed apps sorted by date shows when it appeared.
Will Fortect remove Hancitor?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Hancitor, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- ZDNet: FBI: Cuba ransomware group hit 49 critical infrastructure organizations (read October 6, 2026)
- Clario: Malware-as-a-Service: Who Can Put an End to It? (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)
- Microsoft Learn: How Microsoft names malware (read October 6, 2026)