
Heavypcnetwork.com e-mail scam: how to spot it and what to do
Heavypcnetwork.com stands as a deceptive scam website strategically designed to dupe users into thinking their computers are plagued by malware. This message falsely asserts that the user's system has been infiltrated by malicious viruses and harmful websites, invoking immediate alarm.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove Heavypcnetwork.com e-mail scam yourself 4 steps, about 12 minutes, no software needed.
Start the steps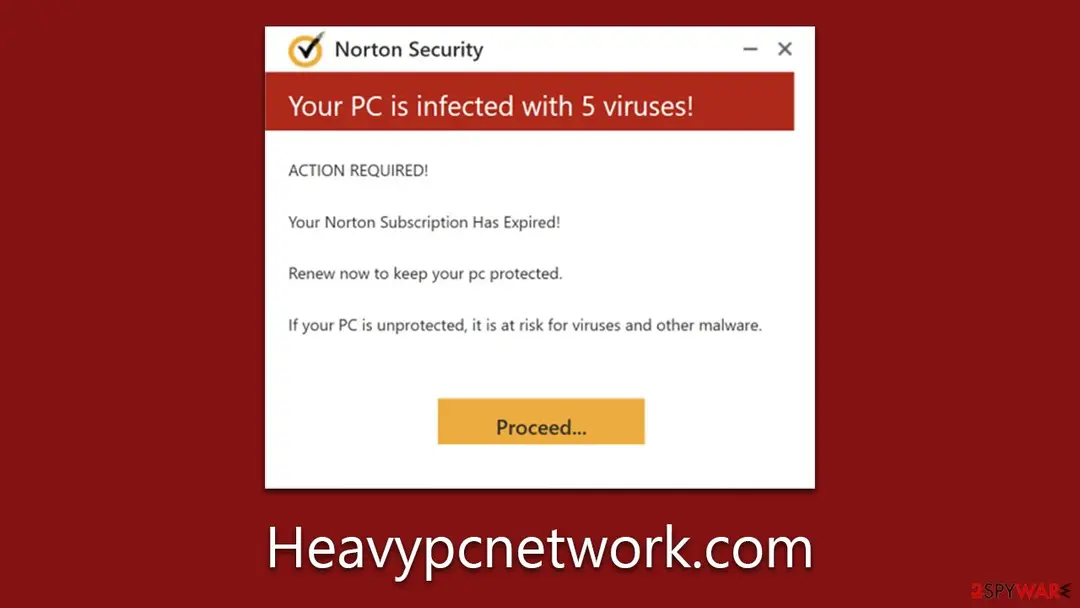
Heavypcnetwork.com e-mail scam: summary
| Distribution | Redirects from other malicious websites, adware |
|---|---|
| Damage | Loss of finances due to fake subscriptions; redirects to other malware-laden, scam websites; installation of potentially unwanted or malicious software |
| Name | Heavypcnetwork.com |
| Type | Scam, phishing, redirect |
| Scam content | The scam is based on scaring users into believing that their systems are infected and that they need to remove those infections with promoted software |
| Symptoms | A phishing e-mail asking you to sign in |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Evidence | One write-up by a security site; details still limited |
|---|---|
| Arrives as | |
| Pretends to be | A well-known company |
| Claim | Your account needs urgent attention |
| Asks for | Your password |
| First seen | 15 September 2023 |
| Facts checked | 7 October 2026 |
What the Heavypcnetwork.com e-mail scam e-mail looks like
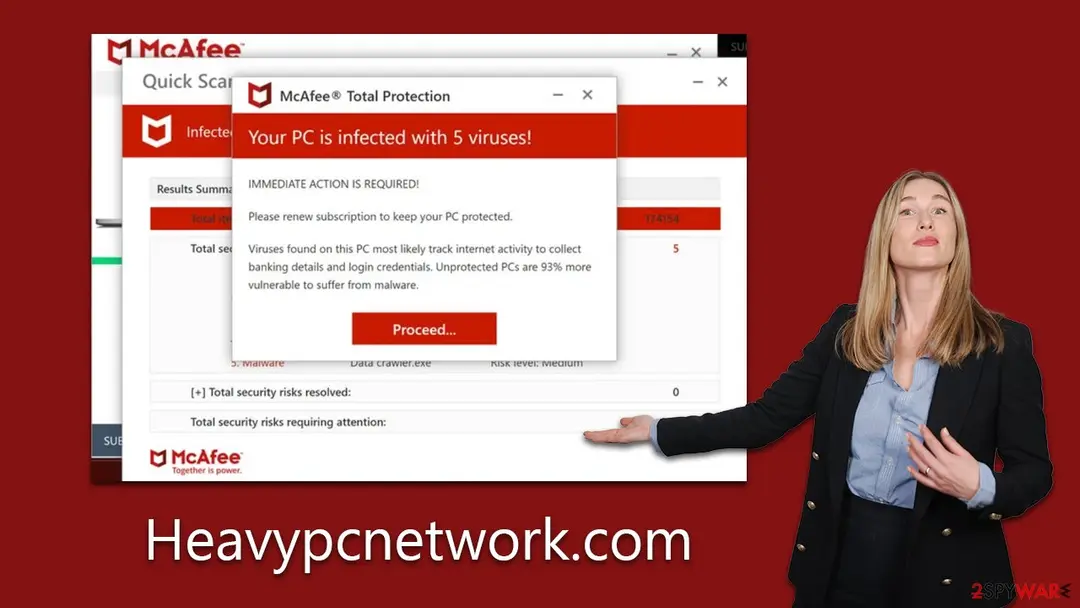
Your PC is infected with 5 viruses!
IMMEDIATE ACTION REQUIRED!
Your McAfee subscription has expired!
Renew now to keep your PC protected.
Viruses found on this PC most likely track internet activity to collect banking details and login credentials. Unprotected PCs are 93% more vulnerable to suffer from malware.
How to tell the Heavypcnetwork.com e-mail scam e-mail is fake
From our report of Sep 2023 · not reviewed since
Heavypcnetwork.com is a scam website designed to scare visitors and make them believe system infections
Heavypcnetwork.com stands as a deceptive scam website strategically designed to dupe users into thinking their computers are plagued by malware.
This message falsely asserts that the user's system has been infiltrated by malicious viruses and harmful websites, invoking immediate alarm.
Such fictitious alerts are tools wielded by scammers seeking monetary gain from advertisements and affiliate marketing through dubious methods.
Furthermore, Heavypcnetwork.com slyly encourages users to activate push notifications. Succumbing to this request can lead to recurrent appearances of these sham virus alerts. It's recommended to steer clear of any engagements with Heavypcnetwork.com and to scan one's system for potential adware. Maintaining awareness and exercising caution is essential in safeguarding one's device against these cunning tactics.
From our report of Sep 2023 · not reviewed since
More from our earlier report on Heavypcnetwork.com
- When accessed, it immediately displays a message, mimicking the familiar appearance of a McAfee security alert.
- However, it's crucial to understand that this warning is a complete fabrication, bearing no ties to genuine McAfee products.
- Interacting with the scam content is dangerous, as scammers may promote fake versions of antivirus software.
- Instead, use reputable tools for your system safety
Is Heavypcnetwork.com e-mail scam dangerous? What the senders want
From our report of Sep 2023 · not reviewed since
Accidental access is one of the main ways users reach Heavypcnetwork.com
Users frequently encounter scam websites through two predominant routes: inadvertent interactions on compromised sites or as a consequence of adware and other malware.
The initial scenario involves unsuspecting users accessing otherwise legitimate websites. Sometimes, due to factors like security loopholes or outdated platform versions, hackers manage to exploit these sites.
They subtly embed malevolent codes that, when clicked on, redirect visitors to malicious domains. These compromised links can cunningly mimic authentic ones, making detection challenging. Often, users only become aware of the deception when it has already caused damage.
In the alternative situation, a user's device gets infected by adware or similar malware. Defined as software that thrusts unsolicited advertisements, adware can be clandestinely bundled with other online downloads. When this happens, it's common for users to find themselves suddenly redirected to unrequested websites or pestered by pop-ups guiding them toward malicious sites.
Whichever route, the ramifications of being lured into these deceptive websites can be dire, ranging from financial repercussions to identity compromise. It underscores the importance of proactive system defense and cautious online navigation.
From our report of Sep 2023 · not reviewed since
Scammers use fake alerts to intimidate people
Scammers capitalize on fear, employing a range of tactics to exploit individuals, especially those unfamiliar with the intricacies of technology.
They tap into anxieties, using them as a weapon to manipulate and defraud.
One widespread approach involves conveying alarming malware threats. This is particularly prevalent on malicious websites that rely on advertising networks with lax scrutiny over ad content. As a result, visitors of websites offering unauthorized content—like torrent repositories or unsanctioned video streaming sites—are more susceptible to confronting scam messages or malicious advertisements.
For instance, there's a scam tactic mirrored by sites like Heavypcnetwork.com, where the design and alerts are made to appear akin to established security software interfaces. These alerts might display daunting messages such as:
It's essential to highlight that only legitimate security tools installed on a device can truly identify and neutralize malware threats. The red flags with these scam alerts include their generic nature, presenting the same message to every user, irrespective of their device's security condition. Furthermore, genuine security alerts aren't delivered via browser animations, revealing the superficial nature of such scam warnings.
From our report of Sep 2023 · not reviewed since
Checking the system for infections and cleaning browsers
In response to the deceptive tactics of Heavypcnetwork.com, the steps you take for system remediation can differ based on your actions and the current software on your device.
If you interacted with the dubious prompts or engaged with compromised links from this site, there's a likelihood that harmful applications found their way onto your computer.
Even if you didn't directly interact with such prompts, maintaining robust system security is paramount. This is because adware, a prevalent culprit, can significantly contribute to the penetration of phishing websites into your system. To ensure your device is thoroughly purged of any potential adware, it's advised to conduct a comprehensive scan using trusted security tools like or . These applications swiftly and decisively tackle and remove any malicious entities.
While one might consider manually deleting unwanted programs, the automated process stands out as the more straightforward and safer approach. Erroneously removing essential software can have detrimental effects. After ensuring your system is void of any malevolent programs and intrusive ads, it's crucial to cleanse any cookies or trackers that might be lingering on your browser. Either utilize a specialized cleaner such as or adhere to the following straightforward steps:
MS Edge (Chromium)
Scam sites, such as Heavypcnetwork.com, have expanded their deceptive tactics beyond just direct site interactions. One of their more insidious strategies involves exploiting the push notification system. Push notifications are typically used by legitimate websites to provide timely updates or alerts directly to a user's screen.
However, scam sites abuse this feature by coaxing users, often through misleading prompts or fake alerts, into granting them permission to send notifications. Once granted, these websites can incessantly bombard the user with dubious messages, even when they are not actively browsing the site.
Even after users have diligently removed suspicious programs from their computers, this doesn't always spell the end of intrusive alerts. The reason is that these notifications operate separately from any software installed on the system. They are linked directly to the browser's permissions, meaning that even with the malicious software gone, the push notifications can continue to disrupt the user's experience.
These relentless pop-ups can serve multiple malicious purposes, from phishing attempts to promoting further scam websites. Thankfully, there's a way to combat this nuisance. Instructions to halt these malicious push notifications can be found below.
MS Edge (Chromium)
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
- Click Menu and pick Options.
- Go to Privacy & Security section.
- Click on Clear Data...
- Select Cookies and Site Data, as well as Cached Web Content, and press Clear.
- Click on Menu and go to Settings.
- Select Privacy and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
- Click Safari > Clear History...
- From the drop-down menu under Clear, pick all history.
- Confirm with Clear History.
- Open the Google Chrome browser and go to Menu > Settings.
- Locate the Privacy and security section and pick Site Settings > Notifications.
- Look at the Allow section and look for a suspicious URL.
- Click the three vertical dots next to it and pick Block. This should remove unwanted notifications from Google Chrome.
- Open Mozilla Firefox and go to Menu > Options.
- Click on Privacy & Security section.
- Under Permissions, you should be able to see Notifications. Click the Settings button next to it.
- In the Settings – Notification Permissions window, click on the URL's drop-down menu.
- Select Block and then click on Save Changes. This should remove unwanted notifications from Mozilla Firefox.
- Click on Safari > Preferences...
- Go to the Websites tab and, under General, select Notifications.
- Select the web address in question, click the drop-down menu and select Deny.
- Open Microsoft Edge, and go to Settings.
- Select Site permissions.
- Go to Notifications on the right.
- Under Allow, you will find the unwanted entry.
- Click on More actions and select Block.
What to do after the Heavypcnetwork.com e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you entered a password after clicking the link in the Heavypcnetwork.com message, treat that account as known to the sender.
Open the provider's real site by typing its address yourself, not through any link in the e-mail, and change the password there. Choose a new one you have never used before, and change it on every other account that shared the old one.
Then use the option to sign out of all other sessions or devices, if the provider has one. This works the same in any browser on Windows 11 and Windows 10.
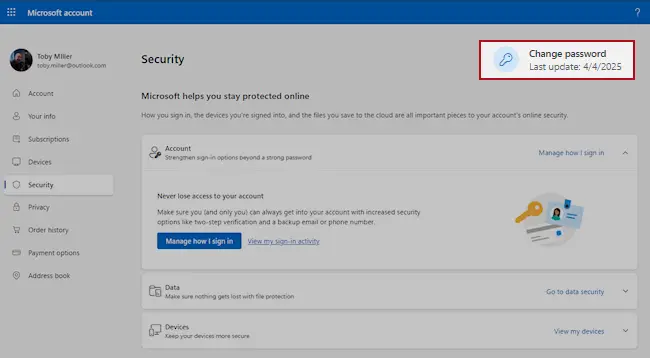
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
Two-step verification asks for a code from your phone or an authenticator app whenever someone signs in from a new device. A stolen password alone is then not enough to open the mailbox.
Turn it on in the security settings of the e-mail account first, then for the bank, shop and social accounts that send their reset links to that address.
While you are there, check the recovery e-mail and phone number and the forwarding rules, which attackers sometimes change to keep access. The settings pages look the same on Windows 11 and Windows 10.
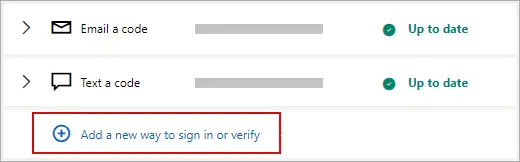
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Report the message instead of only deleting it. In Outlook choose Report > Report phishing, in Gmail the three-dot menu > Report phishing; the provider then blocks the same message for other people.
Do not reply and do not click anything else in it. On a work account, forward it to your IT team as an attachment first. Web mail and the mail apps on Windows 11 and Windows 10 offer the same options.
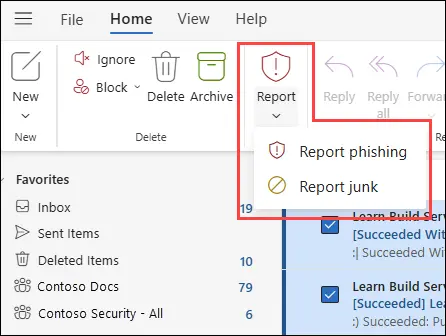
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A page that only asked for a password installs nothing, so most readers can skip this step.
If the Heavypcnetwork.com e-mail or the page it opened made you download or open a file, delete it and run a full scan, then a Microsoft Defender Offline scan.
In Windows 11 and Windows 10 open Windows Security > Virus & threat protection > Scan options, select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts and the scan takes about 15 minutes, so save your work first.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about Heavypcnetwork.com e-mail scam
Does getting "Your PC is infected with 5 viruses!" mean my account was compromised?
Not by itself. Phishing waves are sent to long lists of addresses collected from old breaches, websites and guessing, and the sender does not know whether you even have the account the message mentions. Getting "Your PC is infected with 5 viruses!" only means your address is on such a list.
It becomes a problem if you sign in through the link. To be sure, open the real service from a bookmark and check recent activity and security alerts. If you see nothing unusual and you did not type your password into the fake page, your account is fine.
How fast do I need to react after signing in on the "Your PC is infected with 5 viruses!" page?
As fast as you can. Stolen passwords are often tried within minutes, and the first thing an attacker usually changes is the recovery e-mail or phone, which locks you out. Change the password from a clean device first, then sign out everywhere and review the recovery settings.
If you are already locked out, use the provider's account recovery form straight away and mention that the page behind "Your PC is infected with 5 viruses!" took your password. Warn your contacts, since a taken-over mailbox is often used to send the same phishing to them.
Is Heavypcnetwork.com really from a well-known company?
No. It is sent by scammers who copy the name and look of a well-known company. The sender address and the links do not belong to it, and the message asks for your password, which a real company does not request through an unexpected message.
If you want to be sure about your account, open the website or app of a well-known company the way you normally do, not through the message, and look for notices there. Then delete the message and report it as phishing. If you already followed its instructions, use the steps in this guide for your case.
Is it true that your account needs urgent attention?
No. The claim that your account needs urgent attention is the hook of Heavypcnetwork.com, invented to give you a reason to act quickly. Scammers pick a story that could plausibly apply to many people, so it may feel relevant to you, but nothing in the message is based on your real accounts or devices.
If the claim concerns a service you use, check it there directly, by opening the website or app yourself. You will find no such problem. Then delete the message and report it as phishing.
What happens if I do what Heavypcnetwork.com asks?
The scammers get your password, and they use it quickly. Passwords are tried on the real service within minutes, cards are charged or added to phone wallets, remote access is used to open your bank, and crypto is moved on at once.
Documents surface later as accounts in your name. If you already did what the message asked, do not wait to see what happens; follow the steps in this guide for your case today. Speed matters more than anything else here.
Will a well-known company refund me if I fell for Heavypcnetwork.com?
A well-known company did not send the message and is not responsible for it, so a refund usually comes from your bank or card issuer, not from the brand. Call the bank first if you paid.
It still helps to tell the real company: they can secure your account, add notes for their fraud team and take down pages that use their name. Contact them through their official website or app only, never through the message or a search ad. Keep the message as evidence.
How quickly do scammers use a phished password?
Often within minutes. Phishing kits send each password to the operators as soon as it is typed, and many test it automatically on the real service. Some kits also pass the two-step code through in real time.
That is why the first hour matters: change the password, end all sessions and check that the recovery details are still yours. If nothing has changed by then, you were probably fast enough, but keep watching for login alerts and password-reset e-mails for a few weeks.
Can just reading Heavypcnetwork.com harm my PC?
No. Reading the e-mail does nothing to the PC. The risk lies in what the message wants you to do: your password. Every one of those needs an action from you, such as a click, a typed password, a payment or a call.
If you stopped at reading, you are fine. Delete it and report it. If you are unsure whether you clicked something, check your browser history for the time you read the message, and act on what you find there.
Does receiving Heavypcnetwork.com mean I was hacked?
No. A e-mail like this is sent to huge lists at once, and your address or number is on one of them, most likely because it appeared in a data breach or on a public page. Nothing on your PC caused it.
What would matter is whether anyone signed in to your accounts; check recent sign-in activity in your e-mail and bank accounts if you are worried. Turn on two-step verification for the important ones, then delete the message and report it as phishing.
Will Fortect remove Heavypcnetwork.com?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Heavypcnetwork.com, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- FTC: How to recognize and avoid phishing scams (read October 7, 2026)
- CISA: Recognize and report phishing (read October 7, 2026)
- Microsoft Support: Protect yourself from phishing (read October 7, 2026)
- NCSC: Phishing attacks, dealing with suspicious e-mails and messages (read October 7, 2026)
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)