
HEUR:Trojan.MSIL.Miner.gen: what the alert means and what to do
HEUR:Trojan.MSIL.Miner.gen is a Kaspersky detection name for a .NET program that its heuristic rule judges to be a cryptocurrency miner; it is a label, not a program you can uninstall. Find out which file it names and where it came from, then scan and remove only what you can show does not belong.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan checks installed programs, startup items and browser extensions for anything that came with a Kaspersky alert for HEUR:Trojan.MSIL.Miner.gen naming a .NET file.
Do it yourself · free Remove HEUR:Trojan.MSIL.Miner.gen yourself 5 steps, about 15 minutes, no software needed.
Start the steps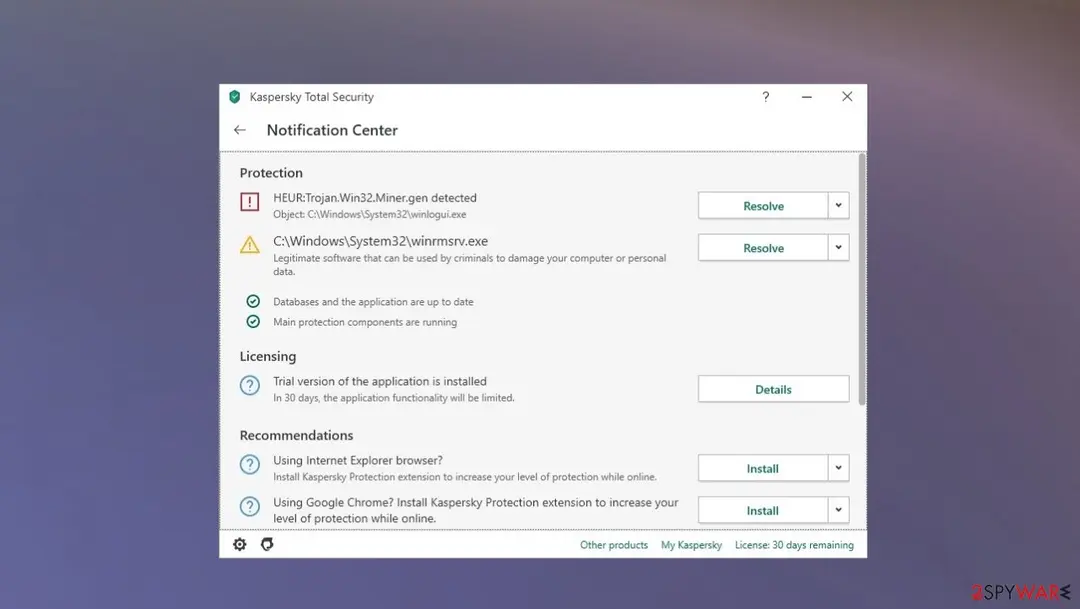
HEUR:Trojan.MSIL.Miner.gen: summary
| Type | A Kaspersky detection name for a .NET cryptocurrency miner (heuristic); not a program you can uninstall |
|---|---|
| Risk | Medium until you know which file it names: a harmless tool can be flagged, and a real miner can come with remote access to the PC |
| Symptoms | Often only the alert; in a real miner case a slow, hot PC with high processor or graphics-card use when idle, and unknown startup items |
| How to get rid of it | Find the flagged file's path and source; Defender full scan; Kaspersky Virus Removal Tool; Safe Mode and Microsoft Defender Offline scans; remove only startup items and exclusions you can explain |
| Our check (6 October 2026) | No PC test: we read Kaspersky's pages for the name and family, one forum case and a Microsoft report; no sample was run |
| First seen | Kaspersky's miner family page shows 07/01/2016; our guide first appeared on 28 July 2021 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Detection | Kaspersky: HEUR:Trojan.MSIL.Miner.gen (also seen as UDS:Trojan.MSIL.Miner.gen). No Microsoft detection name is known for this Kaspersky name. Microsoft uses Trojan:MSIL/CoinMiner!MS for the .NET miner in its 2026 report, which is not shown to be the same files |
|---|---|
| Not to be confused with | HEUR:Trojan.Win32.Miner.gen (native Windows) and HEUR:Trojan.Script.Miner.gen (script) |
| Name | HEUR:Trojan.MSIL.Miner.gen |
| Evidence | 0 write-ups by security sites; details still limited |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against Kaspersky's threat pages for the name and the miner family, its encyclopedia page on heuristic detections, one public forum case from 2024, a Microsoft Security Blog report of 26 May 2026 and Microsoft's pages. We ran no sample and tested no PC; the checks and removal steps follow Microsoft's and Kaspersky's pages and were not tried on a live infection.
What HEUR:Trojan.MSIL.Miner.gen is, and what it is not
HEUR:Trojan.MSIL.Miner.gen is the name Kaspersky products give to a .NET program they judge to be a cryptocurrency miner. It is a detection label, not a program you can uninstall, and it is a verdict from a rule, not a finding about your PC.
- 1
What the name says
Kaspersky's own threat page for the name gives the class Trojan, the platform MSIL (the Microsoft .NET intermediate language) and the family Trojan.MSIL.Miner. The family page says that malware in this family secretly uses the processor of an infected computer to generate cryptocurrency. So the name points to a miner written for .NET.
- 2
Why the old guide called it a possible false alarm
The name begins with HEUR:, which Kaspersky's encyclopedia says marks an object found by its heuristic module, a rule that looks at what a file does and how it is built. A rule can be wrong, and the cases we found show both a real campaign and a flagged tool that was harmless. That is why this page first helps you decide which one you have.
- 3
What the old guide got wrong
Our 2021 guide listed key logging, click fraud, remote access and phishing as things this detection can do, and said it may be linked to "compatibility or file corruption". Kaspersky's page lists spying behaviour only in its generic text for the Trojan class; the family text says mining. File corruption is not given by any source we found as a cause. We have rewritten those parts and say in each chapter what changed.
- 4
What to do first
Write down the full path of the file that was flagged. A flagged file inside a game-modding or development tool you downloaded yourself is a different case from a flagged file in a temporary folder, a Startup folder or a folder you do not recognise.
- Shown by
- Kaspersky products. The prefix can also read UDS:, as in a 2024 forum case, which Kaspersky's pages do not explain
- Class and platform
- Trojan on MSIL, so the file is a .NET program or library
- Family
- Trojan.MSIL.Miner: malware that secretly uses processor capacity to generate cryptocurrency, per Kaspersky
- Is it a program?
- No. It is the label of a detection; the file behind it can differ from case to case
- Not the same as
- HEUR:Trojan.Win32.Miner.gen (the name on the pictures in our 2021 guide), which is a native Windows detection, not a .NET one
- Kaspersky page
- Updated 08/09/2026 as shown on the page; two sample hashes listed
A miner uses your processor or graphics card to earn coins for someone else. The cost to you is power, heat and a slow PC, and, when a real miner got in through a remote access tool, the loss of control of the PC.
What HEUR:Trojan.MSIL.Miner.gen does on an infected PC
How to read the name, part by part
Kaspersky explains some parts of this name on its own pages and leaves others undefined, so the right-hand column says where each reading comes from.
| Part | What it means | Source of the meaning |
|---|---|---|
| HEUR: | Found by Kaspersky's heuristic module, which analyses what an object does | Kaspersky IT Encyclopedia: since 2007 an object found by this module begins with HEUR: |
| UDS: | Seen in place of HEUR: in a 2024 forum case for the same family name | Not defined on the Kaspersky pages we read. We do not guess its meaning |
| Trojan | The behaviour class. Kaspersky's class text describes a program that spies on the user | Kaspersky threat page for the name. The class text is general and does not describe mining |
| MSIL | The platform: code written for the .NET Framework and compiled to the intermediate language | Kaspersky's platform text on the same page |
| Miner | The family: secretly uses processor capacity to generate cryptocurrency | Kaspersky's page for the family Trojan.MSIL.Miner |
| gen | A generic rule that covers many samples | Our reading of the usual naming; not defined on the pages we found |
Search for the whole string you were shown. HEUR:Trojan.Win32.Miner.gen, HEUR:Trojan.Script.Miner.gen and HEUR:Trojan.MSIL.Miner.gen are three different detections, for a Windows program, a script and a .NET program.
What we checked on 6 October 2026, and what we could not
There is no website to test and no file to run, because a detection name is not a program. We read Kaspersky's pages for the name, a Microsoft report on a real .NET miner campaign and a public forum case, and we ran nothing on a PC.
Our reading of the sources, 6 October 2026
- The name is a real vendor detectionKaspersky has a threat page for HEUR:Trojan.MSIL.Miner.gen with two sample hashes and a family page that describes secret mining.
- .NET miners are a real, current threatMicrosoft's security blog of 26 May 2026 describes a cryptojacking campaign whose payload Microsoft detects as Trojan:MSIL/CoinMiner!MS. It is not tied to this name by any source; it shows what a real case looks like.
- What the name means on your PCNot settled by the name alone. The one forum case we found was a set of executables in a game-modding tool that the tool's author said to check with VirusTotal, and no source says the files were harmful.
- Which files carry the detectionKaspersky's page lists two sample hashes and no file names or paths. We cannot say which programs are flagged in your case.
- One vendorA single product can be right, wrong or out of date. The advice in the forum case was to look for agreement among many scanners and to report a wrong verdict to the vendor.
- A quiet checkDoes not clear a PC. Real miners in the Microsoft report checked for virtual machines and stopped mining when the user was active, so a PC that looks calm for a while can still be infected.
Check the flagged file before you delete anything We saw no sign of harm in the sources for this exact name, and we also cannot rule it out. Use the checks below: where the file sits, who it came from, whether other scanners agree, and whether anything starts with Windows that you did not install. This is one reading of public sources, not a scan of your PC.
The name from 2016 to 2026
Our guide dates from 28 July 2021. The picture below is from it; the other entries are the vendor and forum sources we found.
2016
Kaspersky starts the family Trojan.MSIL.Miner
The Kaspersky page for the family shows a detect date of 07/01/2016 and describes malware that secretly uses processor capacity to generate cryptocurrency. The page does not say whether the date is 7 January or 1 July.
28 July 2021
Our first guide
The 2021 guide called the name a heuristic alert that may be a real virus or a false alarm, and listed what trojans can do. Its pictures are Kaspersky notification windows. They show a different name, HEUR:Trojan.Win32.Miner.gen for C:\Windows\System32\winlogui.exe, and adware warnings for a downloaded video-editing installer, so they illustrate a Kaspersky alert, not this detection.
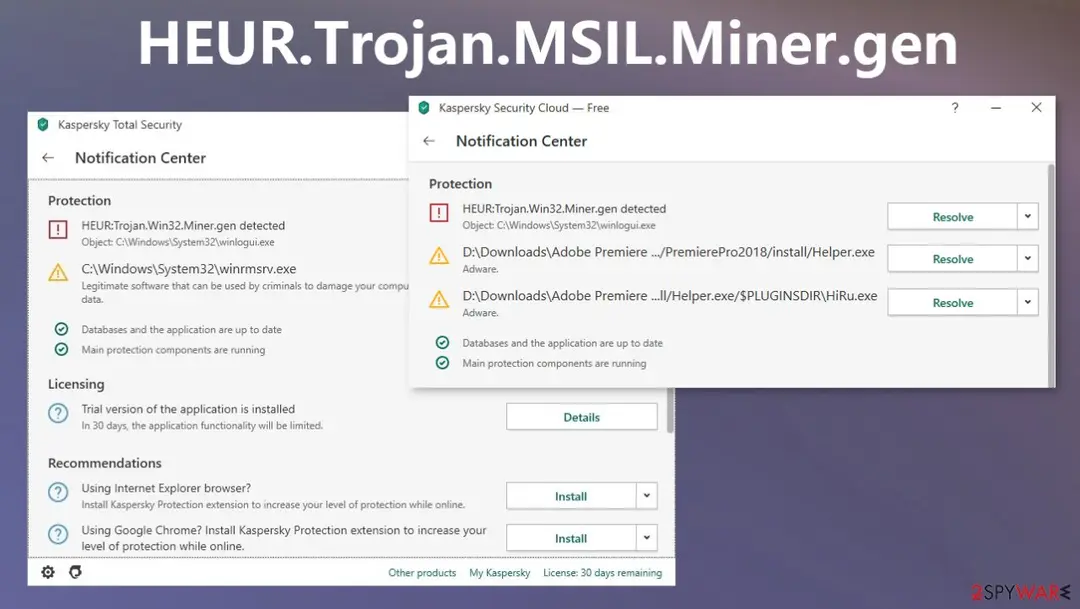
The cover picture of our 2021 guide: two Kaspersky Notification Center windows. They name HEUR:Trojan.Win32.Miner.gen (a native Windows detection) for winlogui.exe, not the .NET name of this guide. 14 August 2024
A modding tool is flagged as UDS:Trojan.MSIL.Miner.gen
A user of the game-modding tool DynDOLOD wrote on the tool's support forum that Kaspersky reported UDS:Trojan.MSIL.Miner.gen in all executables in the tool's Edit Scripts folder after he downloaded it from Nexus Mods. The tool's author answered with a link to the FAQ: check the Nexus scan result and VirusTotal, treat it as a false positive when most tests find nothing, and report it to the antivirus vendor. The user said he had thought the download site was infected.
26 May 2026
Microsoft describes a real .NET miner campaign
Microsoft Defender Experts wrote about fake download sites for system utilities, reached through search results and AI chatbot answers, that delivered a legitimate program with a malicious DLL, then remote access software, then a .NET miner that Microsoft detects as Trojan:MSIL/CoinMiner!MS. It is the closest current picture of a real case, though no source ties it to the Kaspersky name.
8 or 9 September 2026
Kaspersky updates the page
The threat page for HEUR:Trojan.MSIL.Miner.gen shows the update date 08/09/2026. It lists the behaviours its rule can map to, among them scheduled tasks, services, registry Run keys, process injection and hidden windows, and it lists resource hijacking as the impact. We take that as the range of what the rule covers, not as what one file did.
Across the years the name is a vendor label that sometimes marks a real miner and sometimes a harmless tool. That is a reason to check the file, not a verdict on it.
What HEUR:Trojan.MSIL.Miner.gen can steal or download
What it can cost you
The old guide listed eight things this detection can do. Only some belong to a miner, so each item below says what supports it. Read the list as what a real miner case can do, not as a finding about every alert.
- High
A stranger with access to the PC
In the Microsoft campaign the miner arrived through a remote access tool. That is an open door, and it can be used to download and install other malware, which the old guide also listed.
- Medium
Your processor or graphics card works for someone else
Kaspersky's family text says the malware secretly uses processor capacity to generate cryptocurrency. In the Microsoft report the miner used the graphics card.
- Medium
A slow, hot, noisy PC and a larger power bill
Mining runs the hardware hard for hours. The old guide's performance problems fit this and it is the most common sign of a real miner.
- Medium
Security tools switched off for the miner
The Microsoft miner added Defender exclusions and re-applied them every five seconds. An exclusion you did not make is a sign of tampering.
- Low
Spying on keys and websites
The old guide listed keystroke recording and site tracking. Kaspersky's text for the Trojan class describes this, but its family text for the miner does not. We found no case of it for this name.
- Low
Click fraud, redirecting ads and phishing material
These were in the old guide's list. No source we found ties them to this name, and a miner has no need for them.
- Low
A false alarm costing you time
If the detection is wrong, the cost is the hours you spend and a quarantined file that your program may need. The DynDOLOD case was of this kind.
What you may notice, and what the sources show
The old guide said users mostly report the alert itself and not real problems, and that performance problems appear when a real infection is present. Both fit the sources. The alert is often the only sign.
| Sign | What we found |
|---|---|
| The alert itself, with the full name | The first and in the 2024 forum case the only sign: the user reported no other symptom. |
| High processor or graphics-card use when you are idle | The sign a miner is meant to cause. Check Task Manager. Microsoft's miner stopped mining when it saw user activity, so look when the PC has been idle, not while you work. |
| A fan that runs hard and a hot laptop | Follows from heavy use of the hardware. It also has many harmless causes, such as a game or an update. |
| Scheduled tasks, Run entries or Startup shortcuts you did not make | In the Microsoft campaign there were six such items. Look at the checks below. |
| A Defender exclusion you did not add | In the campaign the miner added them itself. Check Windows Security. |
| A remote access program you did not install | In the campaign, ScreenConnect. Check the installed apps. |
| No sign at all | Does not clear a PC, and does not prove an infection either. |
How to check the PC for HEUR:Trojan.MSIL.Miner.gen
How it gets onto a PC: what our old guide said and what the sources show
The old guide said trojans come from hacked pages, spam email, files and malicious sites. None of those is tied to this name by a source. The table says what supports each claim.
| The old guide said | What the sources show |
|---|---|
| Hacked pages and malicious spam email are the main methods of distribution | Not in Kaspersky's page for the name, which lists no distribution. Microsoft's 2026 report, about a different campaign, shows search results and AI chatbot answers leading to fake download sites. |
| Files and malicious sites trigger the installation of the payload | Microsoft's report: the fake site gave a ZIP file with a real utility and a malicious DLL called autorun.dll; running the utility loaded the DLL. The 2024 forum case shows the opposite: a tool downloaded from Nexus Mods and flagged. |
| A malicious email attachment or a website visit installs it without any other action | Not shown for this name. Kaspersky's list for the name includes spread by removable media, which we take as a possibility only. |
| Hackers use names of shipping companies or shopping site links | Not mentioned in any source we found about this name. It is a common phishing method, so the advice to read links carefully stays. |
| A potentially unwanted program installs only when you accept false claims | Compatible with the Microsoft report: the user chose to download and run a fake utility. |
- 1
What this means for you
Ask where the flagged file came from. A fake download of a system or hardware monitoring tool, a crack, a cheat or a mod, and a remote access tool you did not install are the routes with a source behind them. A flagged file from a developer you trust points the other way.
What a real .NET miner can look like: Microsoft's May 2026 report
This is the most detailed current description of a .NET miner that we found. It is about one campaign and is not tied to the Kaspersky name, so read it as a list of places to look, not as what every alert means.
- 1
A lookalike download
People searched for common system utilities or asked AI chatbots for downloads and landed on lookalike sites. The ZIP file held a legitimate executable and a malicious autorun.dll that Windows loads when the executable starts (DLL sideloading).
- 2
Remote access software is installed
The DLL silently installed a second DLL that was a packaged installer for the remote access product ScreenConnect. That gave the attacker a session on the PC.
- 3
The miner is dropped
Through that session the attacker dropped a program named SimpleRunPE.exe, which copied itself into a hidden folder as RuntimeHost.exe and set up six ways to start again: scheduled tasks, registry Run entries and a Startup folder shortcut.
- 4
It hides inside Microsoft .NET programs
It tried to run its code inside signed Microsoft .NET programs such as InstallUtil.exe, RegAsm.exe and MSBuild.exe, added Windows Defender exclusions with PowerShell, and downloaded a graphics-card miner (gminer, lolMiner or SRBMiner-MULTI) at run time.
- 5
It tries not to be seen
Microsoft wrote that it re-applied the Defender exclusions every five seconds, repaired its persistence and ended mining processes when high graphics-card use, user activity or monitored programs were seen.
| Where to look | What Microsoft found in this campaign |
|---|---|
| Task Scheduler | Tasks named Windows System Health, Windows System Health Monitor and Windows System Health Check |
| Registry Run keys | A value named WinSysCache under HKLM and HKCU, Software\Microsoft\Windows\CurrentVersion\Run |
| Startup folder | A shortcut called RuntimeHost.lnk in the user's Start Menu Programs Startup folder |
| Hidden folder | RuntimeHost.exe under a user's AppData Local Microsoft Windows Caches folder |
| Defender exclusions | Path exclusions and 13 process-name exclusions, including lolMiner.exe, SRBMiner-MULTI.exe, miner.exe and gminer.exe |
We print no wallet, server address or certificate value from the report. Nothing here needs them for a home PC.
Check the file and the PC before you delete anything
Write down exactly what the alert says and which file it names before you click Delete. Then look for what could start a miner again. We did not run these checks on an infected PC; they use the Windows tools named in each step.
- 1
Copy the alert
Take a screenshot. Note the full name including HEUR: or UDS:, the product and its version, the date and the full path of the file.
- 2
Where is the file?
A file in a folder of a program you installed on purpose, such as a game, a mod tool or a developer tool, is a candidate for a false positive. A file with a random name in a temporary folder, in AppData or in a Startup folder, or a file that looks like a Microsoft program outside C:\Windows, is more worrying.
- 3
Where did it come from?
Think about the last download. A crack, a cheat, a mod, a fake driver or monitoring tool, or a utility found through a search or a chatbot answer are the routes with a source behind them.
- 4
Ask more scanners about the same file
Upload the file, or only its hash, to VirusTotal. The DynDOLOD author's rule of thumb was that a false positive is one where most of the tests find nothing wrong. A file that many engines call a miner is a different case. Do not upload files with private contents.
- 5
Look at the load
Press Ctrl + Shift + Esc, open Performance and Processes, sort by CPU and GPU, and look when you are not using the PC. A program you do not know that keeps the processor busy is the thing to find.
- 6
Look at what starts with Windows
In Task Manager open Startup apps. Open Task Scheduler and look at tasks you do not recognise, especially names that imitate Windows such as System Health. Microsoft's Autoruns, from Sysinternals, lists more places.
- 7
Look at your Defender exclusions
Open Windows Security > Virus & threat protection > Manage settings > Add or remove exclusions. Any exclusion you did not add is a reason to go on to the removal chapter.
- 8
Look for remote access programs
Open Settings > Apps > Installed apps. A remote access tool such as ScreenConnect that you did not install is a serious find.
- 9
Scan twice
Scan with Microsoft Defender and with a second on-demand scanner and compare the names. If only the product that gave this name reports it, update that product first and scan again.
How to remove HEUR:Trojan.MSIL.Miner.gen
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to HEUR:Trojan.MSIL.Miner.gen or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever HEUR:Trojan.MSIL.Miner.gen installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Remove it from Windows 11 and Windows 10
The old guide said to boot in Safe Mode with Networking, scan, and try System Restore. We keep the Safe Mode scan, add the checks above and the offline scan, and leave out System Restore and the repair-tool walkthrough. The steps follow Microsoft's pages and Kaspersky's tool page; we did not run them against a live infection.
- 1
Decide first whether it is a false alarm
If the file sits in a program you trust, VirusTotal shows no agreement and the checks above found nothing, do not delete the program. Go to the false-alarm chapter. Otherwise go on.
- 2
Disconnect and back up documents
If you think a remote access tool is on the PC, turn off Wi-Fi or unplug the cable. Copy documents and photos, not programs, to an external drive that you unplug afterwards.
- 3
Run a full scan with Microsoft Defender
In Windows Security > Virus & threat protection > Scan options choose Full scan and Scan now.
- 4
Scan memory and startup objects with a second tool
Download Kaspersky Virus Removal Tool from Kaspersky's page. Kaspersky says it is a free on-demand tool that needs no installation, can run alongside your own antivirus and lets you choose scan areas that include system memory and startup objects.
- 5
Start in Safe Mode with Networking
Windows 11: open Settings > System > Recovery, next to Advanced startup select Restart now. Windows 10: Settings > Update & Security > Recovery. Or hold Shift and select Power > Restart. Then choose Troubleshoot > Advanced options > Startup Settings > Restart and press 5 for Safe Mode with Networking. Microsoft says Safe Mode starts Windows in a basic state with a limited set of files and drivers. If you use BitLocker you will need the recovery key.
- 6
Run Microsoft Defender Offline
In Windows Security > Virus & threat protection > Scan options choose Microsoft Defender Offline scan and Scan now. Microsoft says it runs from outside the normal Windows kernel, takes about 15 minutes and restarts the PC. It does not apply to Windows Server editions or ARM PCs, and with BitLocker you should suspend protection first. Review the result under Protection history.
- 7
Remove what you found in the checks
Delete scheduled tasks, Startup shortcuts and Run entries only when you have confirmed that they belong to the miner and not to a program you installed. Remove Defender exclusions you did not add, and uninstall a remote access program you did not install from Installed apps. Write down what you removed.
- 8
Quarantine only what you cannot account for
If scans agree that a file is harmful, let the product quarantine it and then delete it. Quarantine can be undone, deleting cannot.
- 9
Last resort: reset Windows
Back up documents, then use Settings > System > Recovery > Reset this PC and choose Remove everything, or reinstall from a USB installer. Restore documents only, no programs and no full system image.
Never install a repair tool because a pop-up or a stranger tells you to. The old guide's walkthrough of a PC repair program is gone from this page: a registry or system repair tool is not a malware remover.
Could it be a false alarm?
Quite possibly, and the one case we found was one. The old guide said the same: a heuristic name can come from a compatibility or file problem. Use the table to decide how careful to be.
| Points to a real infection | Points to a false positive |
|---|---|
| The file has a random name and sits in AppData, a temporary folder or a Startup folder | The file is part of a program you installed on purpose, from its maker or a known download site |
| You downloaded a crack, a cheat, a fake utility or a file that a chatbot or an ad recommended | The download site shows its own scan result and the maker answers questions about it |
| Many engines on VirusTotal call it a miner or a trojan | Most engines find nothing and only one product reports it |
| The PC is slow and hot when idle, or Task Manager shows a program you do not know using the processor or graphics card | Nothing is slow, hot or odd |
| Scheduled tasks, Run entries or Defender exclusions you did not make; a remote access tool you did not install | Both lists hold only things you know |
- 1
Update the product and scan again
Make sure the antivirus databases are up to date, then scan the same file again. Old versions can report names that newer ones no longer do.
- 2
Report a wrong verdict
The DynDOLOD FAQ advises reporting a false positive to the antivirus developer. Use the vendor's own form, and send the file or its hash.
- 3
Do not turn off protection
Do not switch off your security product or exclude a whole folder to stop the alert. Exclude one file only when the maker and VirusTotal back it and you accept the risk.
- 4
Do not act on pop-ups
A pop-up in a browser that says your PC has this infection and tells you to call or buy something is a scam. A detection name is shown by your own security product, not by a web page.
After removal: passwords, accounts and prevention
Your passwords after HEUR:Trojan.MSIL.Miner.gen
Removing HEUR:Trojan.MSIL.Miner.gen does not undo what it may already have sent out while the PC showed A Kaspersky alert for HEUR:Trojan.MSIL.Miner.gen naming a .NET file in the list of installed apps. Treat saved browser passwords and logged-in sessions on this PC as known to the attacker.
From another device, change the e-mail password first and end all its sessions. Then do the same for the bank, PayPal, Microsoft, Google and Apple accounts. Stolen session cookies keep working after a password change until you sign out everywhere.
Move crypto to a new wallet created on a clean device. A step-by-step order for every kind of account is in our guide to account security after an infection.
If it was real: what to do about your accounts
The old guide said to repair the damage and change passwords after a real infection. A miner itself does not need your passwords, but the remote access that brought it may have exposed them. Start from another device.
- 1
Change passwords from another device
Email first, then banking, then everything else. Turn on two-step sign-in.
- 2
Sign out everywhere
Use the sign out of all sessions option in your Google, Microsoft and social accounts so stolen cookies stop working.
- 3
Check your money
Look at card statements and any wallets for payments you did not make.
- 4
Tell the right people
At work, tell your security team and your manager. At home, report the incident to your national cybercrime reporting service or the police if money or accounts were lost. We list no agencies, because contact links differ by country and we have not checked them all.
- 5
Scan again in a week
A clean scan today does not clear code that hides. Run another full scan and a Defender Offline scan a week later and check Task Scheduler and your Defender exclusions again.
Keep miners off your PC
The old guide's advice was to stay ahead of the threat and watch emails and links. It still holds. Microsoft's 2026 report adds where to be careful: downloads of system tools.
Do
- Download system and hardware tools only from the maker's own site, typed or bookmarked, not from a search ad, a search result you do not know or a chatbot answer.
- Keep one security product with Real-time protection on. Microsoft Defender is built into Windows 11 and 10; turn on Cloud-delivered protection.
- Install Windows Update monthly, and update browsers and other programs.
- Open email attachments only when you expected them, and read a link before you click it.
- Use a standard account for daily work and keep the administrator account for changes.
- Use a different password for every account and a password manager, and turn on two-step sign-in.
- Keep a backup of documents on a disk you unplug (File History or OneDrive), so a bad infection costs you a reinstall, not your files.
Don't
- Do not run cracks, cheats, keygens or files from torrent sites.
- Do not install a remote access program because someone on a call or a web page asks you to.
- Do not add Defender exclusions that a download tells you to add.
- Do not install a repair tool or a second antivirus because a pop-up said your PC is infected.
- Do not leave Remote Desktop open to the internet.
Questions about HEUR:Trojan.MSIL.Miner.gen
What is HEUR:Trojan.MSIL.Miner.gen?
It is the name Kaspersky products give to a .NET program that a heuristic rule judges to be a cryptocurrency miner. Kaspersky's page classes it as a Trojan on the MSIL platform, in the family Trojan.MSIL.Miner, which it describes as malware that secretly uses processor capacity to generate cryptocurrency.
It is a detection label, not a program name, and not a file you can uninstall. The name tells you what Kaspersky's rule thought of a file, not what the file did on your PC. To find out, check which file was flagged, where it came from and whether other scanners agree.
Is HEUR:Trojan.MSIL.Miner.gen a false positive?
It can be, and the one case we found was a likely one. In August 2024 a user reported that Kaspersky flagged UDS:Trojan.MSIL.Miner.gen in all executables in the Edit Scripts folder of the modding tool DynDOLOD, and the tool's author pointed to the Nexus scan and VirusTotal and called it a false positive when most tests find nothing.
That is one case, not a rule. A file from an unknown source, with a random name, that many engines flag, is a different matter. Check the path, the source and a second opinion before you decide.
What does HEUR mean in a Kaspersky detection?
HEUR: means the object was found by Kaspersky's heuristic module. Kaspersky's IT Encyclopedia says the company introduced a separate heuristic module in 2007 and that objects it finds begin with the HEUR: prefix. The module analyses the activity of an object, and if that activity is typical of a malicious program, it reports a name.
So a HEUR: name is a judgement from behaviour or structure, not a match to a known sample. That is why it can be right about a new miner and also wrong about a harmless tool. A different prefix, UDS:, appeared in a 2024 forum case, and Kaspersky's pages do not define it.
What does MSIL mean in the name?
MSIL is the platform: code written for the Microsoft .NET Framework. Kaspersky's page explains that the Common Intermediate Language, formerly called Microsoft Intermediate Language or MSIL, is the language that all Microsoft .NET compilers produce, including Visual Basic .NET, Visual C++ and Visual C#.
So the flagged file is a .NET program or library, usually an .exe or .dll. It does not tell you the file is dangerous, since many ordinary programs are written in .NET. It also helps you search: the same family has separate detections for native Windows programs (Win32) and for scripts.
Can this detection steal my passwords or record my keys?
Not as far as the miner family text goes. Kaspersky's class text for Trojan describes spying:
- capturing keys
- screenshots
- a list of active applications
The family text for Trojan.MSIL.Miner describes secret mining. Our 2021 guide listed key logging, click fraud and phishing for this name, and we found no source for them.
A miner that arrived through remote access software, as in Microsoft's 2026 report, is a different risk: someone had access to the PC. If you see that, change your passwords from another device and check your accounts.
How do I know if a miner is really running?
Look at the load when you are not using the PC. Open Task Manager with Ctrl + Shift + Esc, sort Processes by CPU and GPU and look for a program you do not know that keeps the hardware busy.
Microsoft's report says its miner stopped mining when the user was active, so a PC that is calm while you use it can still be affected. Also check Task Scheduler, Startup apps, Windows Security exclusions and installed apps. None of these alone proves a miner, and none being odd does not clear the PC.
How do I remove HEUR:Trojan.MSIL.Miner.gen?
Check first, then scan. Find the path of the flagged file and decide whether it is a program you installed on purpose. Run a full Microsoft Defender scan, scan memory and startup objects with Kaspersky Virus Removal Tool, boot into Safe Mode with Networking and run Microsoft Defender Offline.
Remove only the scheduled tasks, Run entries, Defender exclusions and remote access programs you can show do not belong, and let your product quarantine files that scans agree on. If the PC is still not right, back up documents and reset Windows with Remove everything.
Can I use System Restore to get rid of it?
We do not recommend it as the removal step. Our 2021 guide offered System Restore as an option, but it is not a malware scan: a restore point made after the file arrived can hold the file too, and a restore does not tell you what started the miner.
This is our reading and we did not test it. Use the scans, the Safe Mode and Defender Offline steps, and remove what you can show is wrong. System Restore remains a way to undo a bad driver or program change, which was the old guide's other point: a heuristic alert can come from such a problem.
How does a miner get onto a PC?
The sources we found give a few routes and none is tied to this exact name. Microsoft's May 2026 report describes lookalike download sites for system utilities, reached through search results and AI chatbot answers, that delivered a real utility with a malicious DLL and then remote access software, followed by a .NET miner.
Cracks, cheats and fake drivers are other common routes. Our 2021 guide named hacked pages, spam email and malicious files, which are general routes for trojans. The practical step is the same: download tools only from the maker's own site and keep real-time protection on.
Will Fortect remove HEUR:Trojan.MSIL.Miner.gen?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For HEUR:Trojan.MSIL.Miner.gen, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Kaspersky Threats: HEUR:Trojan.MSIL.Miner.gen (updated 08/09/2026) (read October 6, 2026)
- Kaspersky Threats: Trojan.MSIL.Miner (family) (read October 6, 2026)
- Kaspersky IT Encyclopedia: Heuristic and proactive detections (read October 6, 2026)
- Step Modifications forum: DynDOLOD support thread, page 614 (14 August 2024) (read October 6, 2026)
- Microsoft Security Blog: From poisoned search results to GPU mining (26 May 2026) (read October 6, 2026)
- Kaspersky: Free Virus Removal Tool, frequently asked questions (read October 6, 2026)
- Microsoft Support: Windows startup settings (Safe Mode) (read October 6, 2026)
- Microsoft Support: Windows recovery environment (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline scan in Windows (read October 6, 2026)