
Hgfu virus: what it is and how to remove it
Hgfu is a Djvu-family ransomware detected in 2023 that encrypts files with RSA encryption and demands $490-$980 for decryption. No decryptor exists except for limited victims using Emsisoft's tool.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
A free scan checks for the encryptor still on the PC; it does not decrypt .hgfu files.
Do it yourself · free Remove Hgfu virus yourself 6 steps, about 18 minutes, no software needed.
Start the steps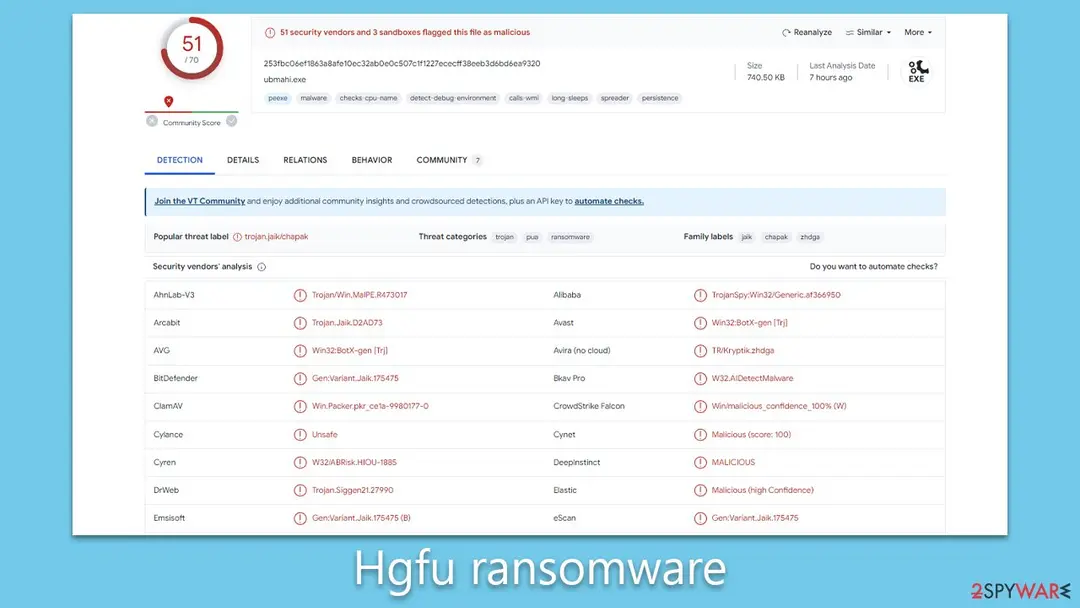
Hgfu virus: summary
| Name | Hgfu virus |
|---|---|
| Type | Ransomware, file-locking malware |
| File extension | Malware appends .Hgfu extension to all affected files |
| Family | Djvu |
| Ransom note | _readme.txt dropped at every location where encrypted files are located |
| Contact | support@freshmail.top and datarestorehelp@airmail |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 14 more facts
| File Recovery | There is no guaranteed way to recover locked files without backups. Other options include paying cybercriminals (not recommended, might also lose the paid money), using Emisoft's decryptor (works for a limited number of victims), or using third-party recovery software |
|---|---|
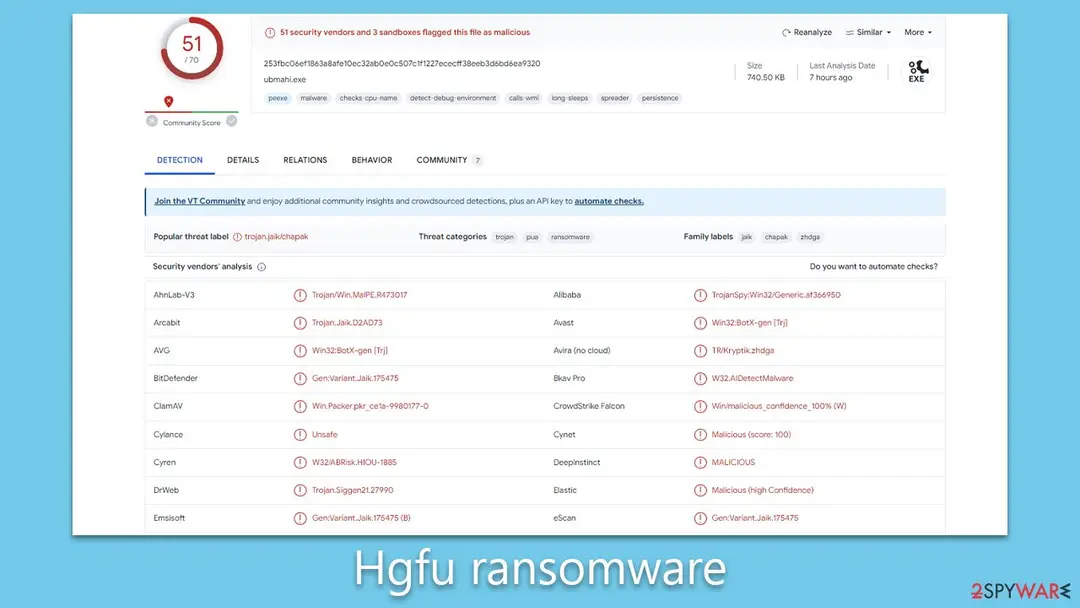
| Detection names | Microsoft: Trojan:Win32/Recordbreaker.RPY!MTB; Avast: Win32:BotX-gen [Trj]; Combo Cleaner: Gen:Variant.Jaik.175475; ESET-NOD32: A Variant Of Win32/Kryptik.HUON; Kaspersky: HEUR:Trojan.Win32.Chapak.gen |
| Encrypted file extension | .hgfu |
| Decryptor | No free decryptor is known for this variant; check No More Ransom (nomoreransom.org) for updates |
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Symptoms | Files renamed with a new extension and a ransom note left in folders |
| Evidence | One write-up by a security site; no sample analysed yet |
| Encrypted files | .hgfu |
| Attacker contacts | support@freshmail.top |
| Free decryptor | No free decryptor is known (checked 5 October 2026) |
| First seen | 6 December 2023 |
| Microsoft Defender name | Trojan:Win32/Recordbreaker.RPY!MTB |
| Facts checked | 5 October 2026 |
What antivirus programs call Hgfu virus
Microsoft Defender reports Hgfu virus as Trojan:Win32/Recordbreaker.RPY!MTB.
In a Defender name, the part before the colon is the category, the part after it is the platform, and the part after the slash is the family Microsoft assigned. A suffix after ! is an internal Microsoft marker, not a different threat.
Generic labels such as Agent, GenericKD or Malware.AI only say that a file looks malicious, not what it does; our guide to antivirus detection names shows how to read them.
- File extension:
.hgfu - Note file:
_readme.txt - Contact:
support@freshmail.top
From our report of Dec 2023 · not reviewed since
More from our earlier report on Hgfu virus
- After disconnecting the computer from the network and the internet, do a complete system scan using the security program
- As soon as it is installed, malware has the potential to severely harm some system files, causing instability problems, including crashes and errors.
- Any such damage can be automatically repaired by using PC repair
How Hgfu virus behaves
From our report of Dec 2023 · not reviewed since
Hgfu is a file-encrypting virus that demands money for its victims
Hgfu ransomware is a menacing derivative of the widely recognized Djvu ransomware lineage, which is known for its potent threat to digital data.
Like its predecessors, this virus typically gains unauthorized access to computer systems. The primary avenues for its infiltration are through unofficial software downloads and counterfeit software activation tools.
Once the Hgfu ransomware finds its way into a system, it swiftly initiates an exhaustive file encryption operation. Key targets include essential files such as documents, multimedia content, and other significant data. To lock users out of their files, it uses the intricate RSA encryption algorithm, ensuring that without a distinct decryption key, the files remain unreachable.
After the encryption, all affected files receive an ".hgfu" extension. In tandem with this, a ransom message named "_readme.txt" manifests, urging victims to pay a ransom, usually ranging between $980 and $490, in hopes of regaining access to their files.
For those who encounter the Hgfu ransomware, immediate response is crucial. It's recommended to isolate the infected device from any networks promptly and to execute a comprehensive system analysis using sophisticated security tools. The most effective strategy for safeguarding against such threats lies in routine data backups and stringent security protocols.
From our report of Dec 2023 · not reviewed since
Ransom note demands payment
A ransomware attack is not just a silent infiltration; it comes with a stark reminder of the intrusion: a ransom note.
This message serves as the primary conduit between the victim and the attacker, detailing the conditions under which the encrypted data may be released.
The communication typically outlines the process for the victim to pay the demanded ransom in exchange for the decryption tool. It's not uncommon for some ransom notes to incorporate a ticking clock, threatening escalating damages or the complete obliteration of data if the deadline isn't met.
Yet, Djvu-related strains, like the Hgfu, often adopt a less menacing, seemingly more professional demeanor. These messages often materialize as text documents, visuals, or even accessible web pages on the infiltrated device.
For those unfortunate enough to be targeted by the Hgfu virus, a jarring ransom note appears soon after their files are encrypted. The note's content broadly communicates the following:
Cyber attackers, in an attempt to appear credible, might offer gestures like discounted payments or even a trial decryption service. Such strategies aim to sedate the victim's apprehensions, leading them into the mirage of trust and collaboration.
Yet, it's imperative to maintain skepticism. Even with the Hgfu ransomware, there's an absence of guaranteed reciprocity post-payment. These cybercriminals navigate the murky waters of illicit activities, prioritizing their interests, which renders their guarantees dubious at best.
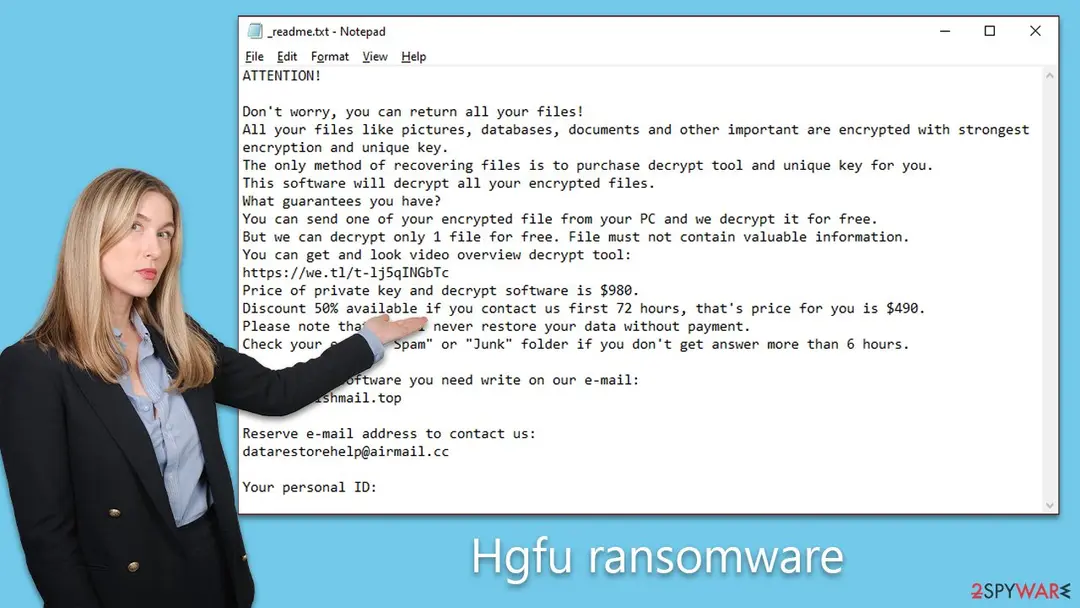
The Hgfu virus ransom note
ATTENTION!
Don't worry, you can return all your files!
All your files like pictures, databases, documents and other important are encrypted with strongest encryption and unique key.
The only method of recovering files is to purchase decrypt tool and unique key for you.
This software will decrypt all your encrypted files.
What guarantees you have?
You can send one of your encrypted file from your PC and we decrypt it for free.
But we can decrypt only 1 file for free. File must not contain valuable information.
You can get and look video overview decrypt tool:
https://we.tl/t-sD0OUYo1Pd
Price of private key and decrypt software is $980.
Discount 50% available if you contact us first 72 hours, that's price for you is $490.
Please note that you'll never restore your data without payment.
Check your e-mail "Spam" or "Junk" folder if you don't get answer more than 6 hours.
To get this software you need write on our e-mail:
support@freshmail.top
Reserve e-mail address to contact us:
datarestorehelp@airmail.cc
Your personal ID:
How to remove Hgfu virus
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove Hgfu virus and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so Hgfu virus cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Your files now end in
.hgfuand the instructions are in_readme.txt. Save both to a USB stick, a copy of the note and two small encrypted files, before anything else.On another device, check them with ID Ransomware or Crypto Sheriff: the family name decides which decryptor, if any, can help. Keep the note's ID and contact line for your report.
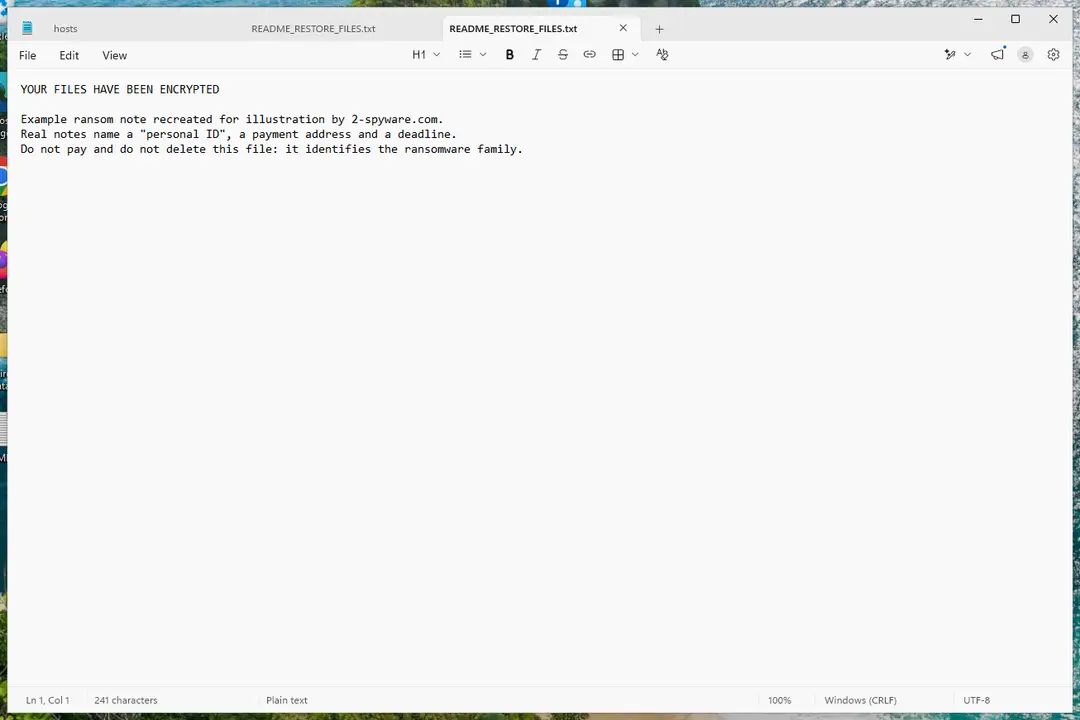
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for Hgfu virus, no free decryptor is known (checked 5 October 2026). Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing Hgfu virus does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
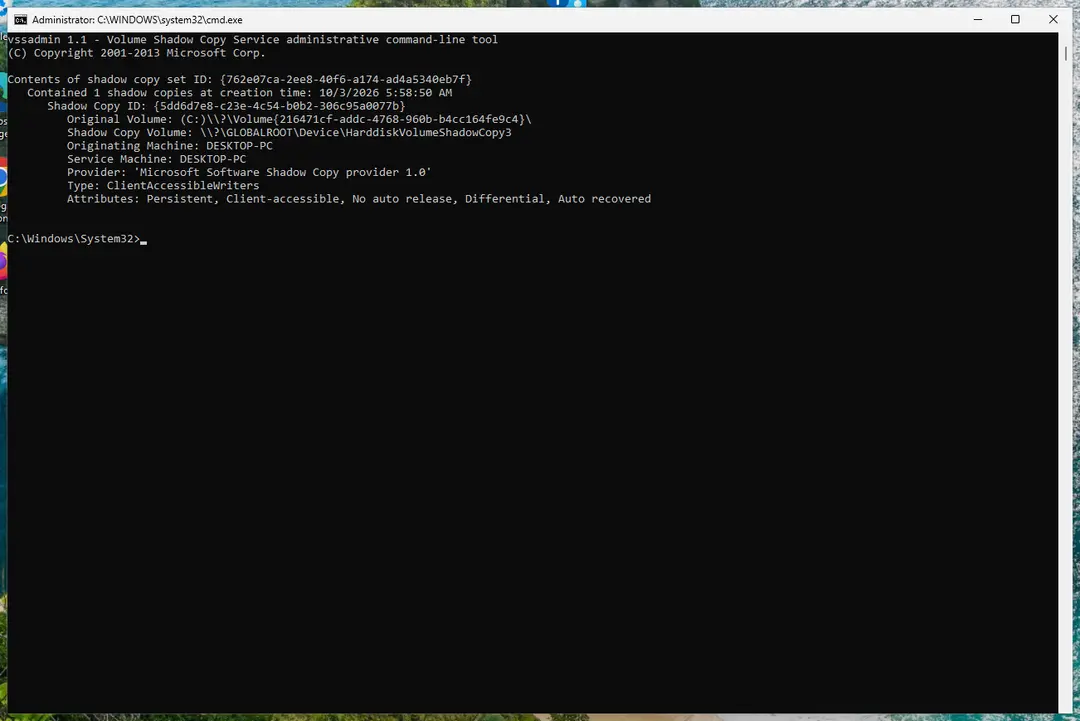
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that Hgfu virus deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Restore Windows "hosts" file to its original state
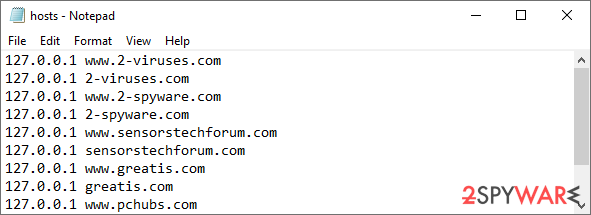
Some ransomware might modify Windows hosts file in order to prevent users from accessing certain websites online. For example, Djvu ransomware variants add dozens of entries containing URLs of security-related websites, such as 2-spyware.com. Each of the entries means that users will not be able to access the listed web addresses and will receive an error instead.
Here's an example of "hosts" file entries that were injected by ransomware:
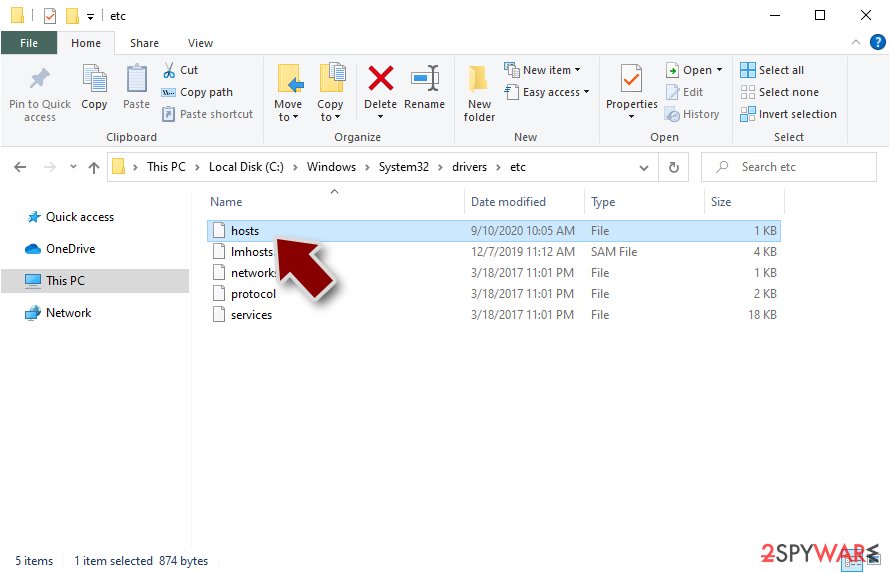
In order to restore your ability to access all websites without restrictions, you should either delete the file (Windows will automatically recreate it) or remove all the malware-created entries. If you have never touched the "hosts" file before, you should simply delete it by marking it and pressing Shift + Del on your keyboard. For that, navigate to the following location:
C:\\Windows\\System32\\drivers\\etc\\
Find a working decryptor for your files
File encryption is a process that is similar to applying a password to a particular file or folder. However, from a technical point of view, encryption is fundamentally different due to its complexity. By using encryption, threat actors use a unique set of alphanumeric characters as a password that can not easily be deciphered if the process is performed correctly.
There are several algorithms that can be used to lock data (whether for good or bad reasons); for example, AES uses the symmetric method of encryption, meaning that the key used to lock and unlock files is the same. Unfortunately, it is only accessible to the attackers who hold it on a remote server - they ask for a payment in exchange for it. This simple principle is what allows ransomware authors to prosper in this illegal business.
While many high-profile ransomware strains such as Djvu or Dharma use immaculate encryption methods, there are plenty of failures that can be observed within the code of some novice malware developers. For example, the keys could be stored locally, which would allow users to regain access to their files without paying. In some cases, ransomware does not even encrypt files due to bugs, although victims might believe the opposite due to the ransom note that shows up right after the infection and data encryption is completed.
Therefore, regardless of which crypto-malware affects your files, you should try to find the relevant decryptor if such exists. Security researchers are in a constant battle against cybercriminals. In some cases, they manage to create a working decryption tool that would allow victims to recover files for free.
Once you have identified which ransomware you are affected by, you should check the following links for a decryptor:
- No More Ransom Project
- Free Ransomware Decryptors by Kaspersky
- Free Ransomware Decryption Tools from Emsisoft
- Avast decryptors
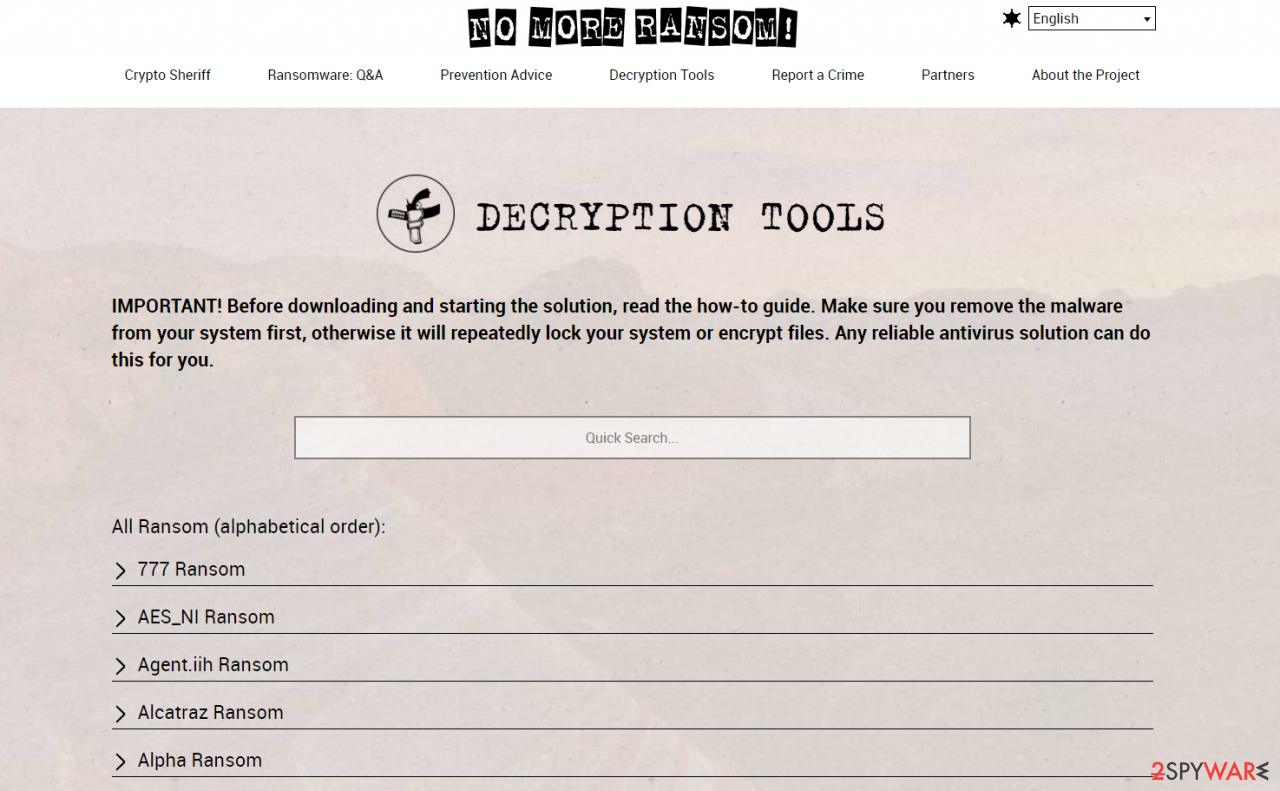
If you can't find a decryptor that works for you, you should try the alternative methods we list below. Additionally, it is worth mentioning that it sometimes takes years for a working decryption tool to be developed, so there are always hopes for the future.
Create data backups to avoid file loss in the future
Report the incident to your local authorities
Ransomware is a lucrative, highly illegal business, and authorities are actively targeting ransomware operators. The level of investigation and follow-up depends on the country, the scale of the incident, and whether the attack is linked to known ransomware groups. To increase the likelihood of identifying the culprits, the agencies need information. In many cases, reports are used primarily for intelligence gathering, trend analysis, and victim support rather than immediate identification of attackers.
Therefore, by reporting the crime, you could help stop the cybercriminal activities and catch the threat actors. Reporting does not guarantee investigation or recovery of data, but it contributes to broader efforts to track ransomware campaigns. Make sure you include all the possible details, including how did you notice the attack, when it happened, etc. Relevant details may also include affected systems, ransom demands, cryptocurrency wallet addresses, and any communication with the attackers. Additionally, providing documents such as ransom notes, encrypted files, or malware executables would be beneficial.
Law enforcement agencies typically deal with online fraud and cybercrime, although it depends on where you live. Here is the list of local authority groups that handle incidents like ransomware attacks, sorted by country:
- USA - Internet Crime Complaint Center IC3
- United Kingdom - ActionFraud
- Canada - Canadian Anti-Fraud Centre
- Australia - ScamWatch
- New Zealand - ConsumerProtection
- Germany - Polizei
- France - Ministère de l'Intérieur
If your country is not listed above, you should contact the local police department or communications center.
From our report of Dec 2023 · not reviewed since
Malware removal
When confronted with Hgfu or similar ransomware, it's vital to recognize that merely addressing the encryption might not cleanse the system of the malware entirely.
Residual components could linger, maintaining a latent threat, and it's not rare for such ransomware to be paired with additional malicious entities. For instance, certain Djvu variants had been observed to be packaged with the malicious Vidar Trojan, introducing another dimension of risk to the compromised machine.
The foremost step in the malware cleansing process should be severing the system's internet connection. This move curtails any further malicious activities or spread. Subsequently, users should perform a comprehensive system sweep using trusted security software like or . Such tools come fortified with mechanisms tailored to pinpoint and eradicate a spectrum of malware, spanning ransomware to Trojans.
A proactive measure involves venturing into:
Within this directory, it's imperative to identify and excise the "hosts" file. This file often undergoes alterations by ransomware to obstruct users from accessing certain web portals, predominantly those proffering malware mitigation or data salvage solutions. To further bolster system health, consider deploying a robust PC repair application . Such utilities excel at mending compromised Windows components, ensuring an error-free, stable operating environment, and minimizing hazards like system crashes.
Once convinced of the comprehensive eviction of the ransomware and its potential allies, the spotlight can shift to data restoration. Before embarking on this recovery phase, affirming the total absence of any malware trace is paramount. This wards off potential setbacks like further data compromise or repeat encryptions.
The realm of ransomware is often shrouded in misconceptions, particularly concerning the dynamics of data encryption and the functioning of such malware. A common notion harbored by many ransomware victims is the presumption that a comprehensive system scan using security tools is a panacea for their encrypted files.
Some even embark on manual interventions, like renaming and re-extending files, hoping this would miraculously restore their data. However, the reality is considerably more intricate.
The encryption deployed by ransomware, including the Hgfu variant, is built on sophisticated algorithms. These tools generate cryptographic sequences that are Herculean to decipher or bypass, dispelling the idea of tricking ransomware into releasing files. Exorcising the malware doesn't liberate the files; they remain encrypted and unreachable sans the decryption key—a piece of information zealously guarded by cyber adversaries.
Ransomware's modus operandi involves encrypting data, associating each with a distinctive identifier and a convoluted encryption key. This data is relayed to the malicious actors, empowering them with the tools needed to produce a decryption key, subsequently granting them unfettered access to the entrapped data. Their objective is lucid: capitalize on the victim's desperation, transforming it into monetary gains, underscoring why ransomware is a goldmine for cybercriminal syndicates.
While the allure of paying ransoms might seem compelling, we advocate for alternative avenues, delineated below. Prior to venturing into any recovery techniques, it's pivotal to have a backup of the ensnared data. This prudence prevents further data degradation during restoration attempts.
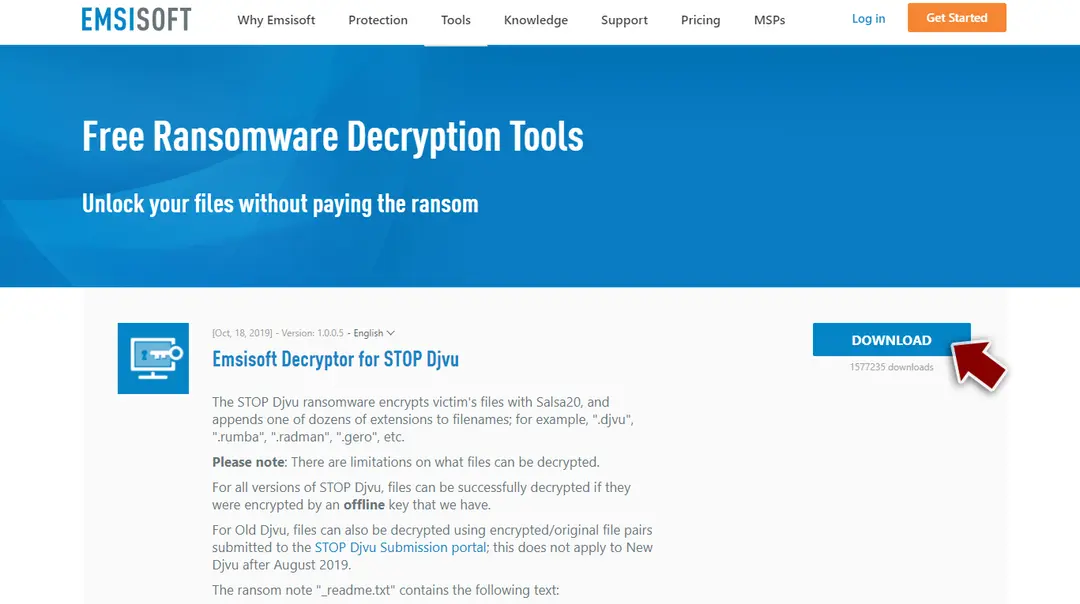
A logical starting point would be the Emsisoft decryption utility. However, it's paramount to acknowledge its efficacy is contingent on the specific ransomware strain and an array of other determinants.
From here, there are three available outcomes:
If your data was encrypted with an online ID, Emsisoft's tool won't work.
- C:\Windows\System32\drivers\etc
- After pressing Download button, a small pop-up at the bottom, titled decrypt_STOPDjvu.exe should show up - click it.
- If User Account Control (UAC) message shows up, press Yes.
- Agree to License Terms by pressing Yes.
- After Disclaimer shows up, press OK.
- The tool should automatically populate the affected folders, although you can also do it by pressing Add folder at the bottom.
- Press Decrypt.
- "Decrypted!" will be shown under files that were decrypted successfully - they are now usable again.
- "Error: Unable to decrypt file with ID:" means that the keys for this version of the virus have not yet been retrieved, so you should try later.
- "This ID appears to be an online ID, decryption is impossible" - you are unable to decrypt files with this tool.
- Download .
- Double-click the installer to launch it.
- Follow on-screen instructions to install the software.
- As soon as you press Finish, you can use the app.
- Select Everything or pick individual folders which you want the files to be recovered from.
- Press Next.
- At the bottom, enable Deep scan and pick which Disks you want to be scanned.
- Press Scan and wait till it is complete.
- You can now pick which folders/files to recover - don't forget you also have the option to search by the file name!
- Press Recover to retrieve your files.
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Protect the files you restore
Restore only after the scans are clean and the PC no longer shows files that end in .hgfu and no longer open; otherwise the restored copies can be damaged again.
Then build a backup that survives the next infection:
- one copy in the cloud with version history
- one on an external drive that is disconnected between backups
- the working copy on the PC
Version history matters because a backup that syncs damaged files overwrites the good ones.
How to do this with the tools built into Windows: the 3-2-1 backup rule on Windows.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
Questions about Hgfu virus
What is Hgfu ransomware?
Hgfu is a file-encrypting ransomware virus that demands payment for file recovery. According to the 2023 guide, it is a menacing derivative of the widely recognized Djvu ransomware lineage, known for its potent threat to digital data.
Once it infiltrates a system, typically through unofficial software downloads and counterfeit software activation tools, it swiftly initiates an exhaustive file encryption operation targeting documents, multimedia content, and other significant data.
The ransomware uses the intricate RSA encryption algorithm to lock users out of files. After encryption, all affected files receive an .hgfu extension. A ransom message named _readme.txt manifests, urging victims to pay between $980 and $490 (50% discount if contacted within 72 hours).
How did Hgfu ransomware get on my PC?
According to the 2023 guide, Hgfu typically gains unauthorized access through unofficial software downloads and counterfeit software activation tools like cracks or keygens. The primary avenues for infiltration include downloading software from questionable sources rather than official websites and using pirated activation tools.
The ransomware is sometimes packaged with additional malicious entities; certain Djvu variants have been observed bundled with the Vidar Trojan, introducing another dimension of risk. For those unfortunate enough to be targeted, immediate response is crucial. It's recommended to isolate the infected device from networks promptly and execute a comprehensive system analysis using sophisticated security tools.
Is there a decryptor for Hgfu ransomware?
According to the 2023 guide, there is no guaranteed way to recover locked files without backups. Limited options exist: Emsisoft has released a decryptor that works for a limited number of victims, or third-party recovery software may be used with mixed results.
However, the 2023 guide emphasized there is no panacea for encrypted files. The encryption deployed by Hgfu is built on sophisticated algorithms that generate cryptographic sequences that are extremely difficult to decipher or bypass.
Merely removing the malware does not liberate the files; they remain encrypted and unreachable without the decryption key, a piece of information zealously guarded by cyber adversaries. Regular data backups and stringent security protocols represent the most effective safeguarding strategy.
Should I pay the ransom?
No, you should not pay the ransom. Even with Hgfu ransomware, there is an absence of guaranteed reciprocity post-payment. According to the 2023 guide, cyber criminals navigate murky waters of illicit activities, prioritizing their interests, which renders their guarantees dubious at best.
Cyber attackers may offer discounted payments or trial decryption services to appear credible, but such strategies aim to seduce victims into the mirage of trust and collaboration.
The 2023 guide noted that paying ransoms might also result in losing the paid money without receiving decryption keys. Alternative options like Emsisoft's decryptor for limited victims or third-party recovery software are safer choices than trusting cybercriminals.
Do paid decryption services or data recovery companies work?
According to the 2023 guide, paid decryption services and data recovery companies have mixed success rates. Emsisoft has released a decryptor that works for a limited number of victims, and third-party recovery software may offer some options with varying results.
However, these are not guaranteed solutions. The sophisticated RSA encryption used by Hgfu generates cryptographic sequences that are extremely difficult to decipher. The 2023 guide emphasized that some data recovery approaches might succeed where others fail, but there is no panacea.
Before employing any service, ensure your system is completely free of malware. The foremost step should be severing the system's internet connection to curtail further malicious activities, then performing a comprehensive system sweep using trusted security software.
Was my data stolen by Hgfu ransomware?
Possibly. According to the 2023 guide, when Hgfu ransomware infiltrates a system, malware sends encryption-related data to the malicious actors, providing them with information that could include details about your files and potentially your identity. Ransomware's modus operandi involves encrypting data and associating each with a distinctive identifier and a convoluted encryption key.
This data is relayed to the malicious actors, empowering them with tools to produce a decryption key and potentially granting access to information about the trapped data. After disconnecting from the network and performing a complete system scan using security programs, it is imperative to verify the total absence of any malware trace before shifting focus to data restoration.
How do I open .hgfu files that were encrypted?
You cannot open .hgfu files without the decryption key held by the cybercriminals. According to the 2023 guide, once files are encrypted with RSA encryption and receive the .hgfu extension, they remain unreachable without the unique decryption key.
Many victims mistakenly believe that comprehensive system scans using security tools will unlock encrypted files, or attempt manual interventions like renaming and re-extending files hoping for miraculous restoration.
However, the 2023 guide confirmed this reality is considerably more intricate than such simple approaches. The only reliable recovery methods are restoring from backups made before the infection, using Emsisoft's decryptor if applicable, or employing third-party recovery software with limited success rates.
Is Hgfu different from other ransomware with a similar name?
Yes. Hgfu is specifically a derivative of the Djvu ransomware lineage according to the 2023 guide. While it shares the Djvu family characteristics and encryption methods, it is distinct from other ransomware variants.
Djvu-related strains like Hgfu often adopt a less menacing, seemingly more professional demeanor in their ransom notes compared to other ransomware families.
The 2023 guide noted that different variants use different file extensions (Hgfu uses .hgfu), demand different ransom amounts, and may employ slightly different communication methods. However, the fundamental threat mechanism remains the same: RSA encryption that creates an absence of guaranteed decryption without payment.
How do I remove Hgfu ransomware from my system?
According to the 2023 guide, the foremost step should be severing the system's internet connection immediately to curtail any further malicious activities or spread. Subsequently, perform a comprehensive system sweep using trusted security software designed to detect and eradicate ransomware.
To further bolster system health, deploy a robust PC repair application to mend compromised Windows components, ensuring an error-free, stable operating environment. Identify and excise the hosts file, which ransomware often modifies to obstruct users from accessing malware mitigation or data salvage solution websites.
Once convinced of the comprehensive eviction of ransomware and its potential allies from Task Manager entries, only then shift focus to data restoration. Affirm the total absence of malware before attempting any recovery efforts.
Will Fortect remove Hgfu virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Hgfu virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- VirusTotal: analysis of a Hgfu virus sample (read October 5, 2026)
- CISA: StopRansomware (read October 5, 2026)
- No More Ransom (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)