
Kovter.C virus: what it is and how to remove it
Kovter.C is the malware that gets installed on the machine without users permission and malicious files get stored in the Windows registry directly. This fact makes the trojan even more dangerous and difficult to remove.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan can look at mshta.exe and the other programs installed around the same time.
Do it yourself · free Remove Kovter.C virus yourself 6 steps, about 18 minutes, no software needed.
Start the steps
Kovter.C virus: summary
| Distribution | Maliciously infected email attachments, exploit kits |
|---|---|
| Name | Kovter.C virus |
| Type | Trojan |
| Possible danger | Can cause damage to the system, infiltrate other malware |
| Main purpose | Perform click-fraud operations |
| Known since | 2013 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Associated files | mshta.exe; powershell.exe |
|---|---|
| Symptoms | The computer acts sluggishly, programs take a long time to start, processes run in the background causing high usage of resources |
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Evidence | 7 write-ups by security sites; no sample analysed yet |
| File names | mshta.exe |
| First seen | 12 May 2019 |
| Microsoft Defender name | Trojan:Win32/Kovter.C |
| Facts checked | 6 October 2026 |
What Kovter.C virus does on an infected PC
From our report of May 2019 · not reviewed since
Kovter Trojan is closely related to file-encrypting viruses
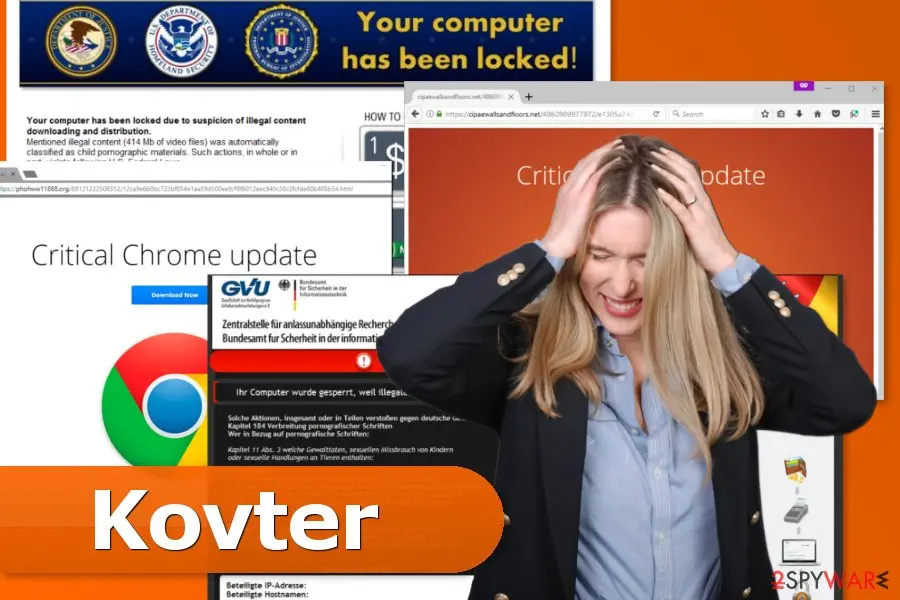
In 2013 and 2014, Kovter virus acted as a police ransomware virus.
According to the security experts, it might be related to Kovter ransomware. After the infiltration, malware delivered a pop-up message telling that the user has violated a law. For this reason, files on the computer were locked, and users have to pay a ransom.
In 2016 malware has been noticed spreading crypto-viruses again. Nevertheless, this version of Kovter ransomware had an efficient infiltration mechanism; its ability to encrypt files was not as good. Encrypted data can be easily recovered without following hackers instructions provided in the ransom note.
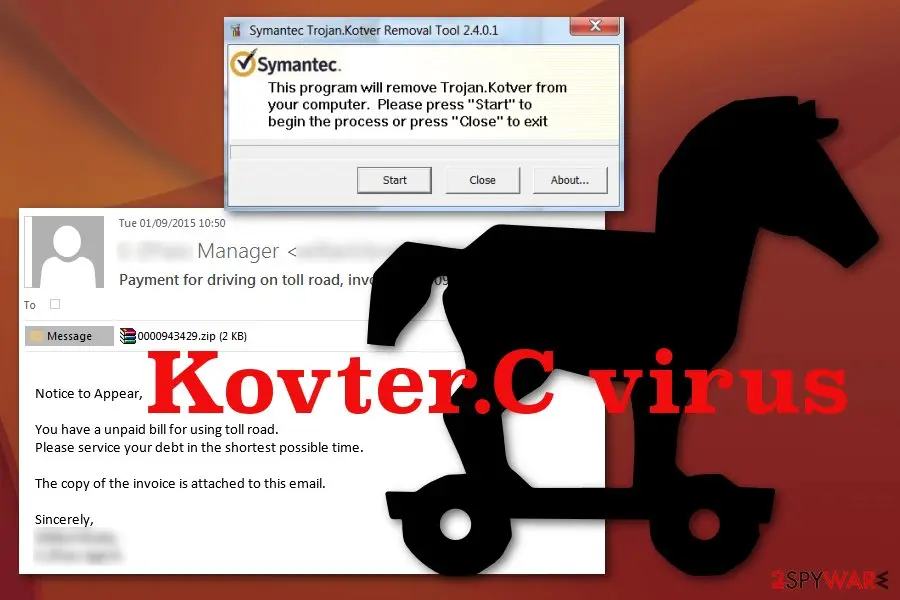
Finally, at the beginning of 2017, Kovter has been noticed spreading the infamous Locky ransomware virus. Malware has been spreading via malicious spam emails that included a ZIP archive with JScript file. Once victims executed the file, both Locky and Kovter ad-fraud trojan was installed on the computer.
From our report of May 2019 · not reviewed since
Kovter 2017: click fraud adware attacked millions of Pornhub visitors
In 2014, authors of the Trojan used it for click-fraud activities.
Nevertheless, they changed the specifics of their cybercrimes; this year they came back to illegal money-making strategy. In October 2017, malware researchers reported about massive malvertising campaign that targeted millions of Pornhub users. This pornographic website is known as one of the most popular sites in the world. Therefore, there's no doubt that hackers decided to launch the attack there.
Criminals arranged advanced attack towards the US, Canada, UK and Australian people who accessed this adult-themed website with Google Chrome, Mozilla Firefox, Internet Explorer or Microsoft Edge. While Microsoft's web browser users were asked to install Adobe Flash Player update, Chrome and Firefox users were notified about the necessity to install a critical update.
When users installed one of these fake updates, the malware was installed on the computer and started illegally making incomes from online advertising. No matter that this activity does not seem as dangerous as a ransomware attack, users are advised to act quickly. If you visited porn website and installed one of the mentioned updated, obtain antivirus and remove Kovter ASAP.
From our report of May 2019 · not reviewed since
More from our earlier report on Kovter.C virus
- Get reputable anti-malware like and remove Kovter.C virus
- Try using for the additional system check and fixing virus damage
How Kovter.C virus got on your PC
From our report of May 2019 · not reviewed since
Kovter.C virus is the trojan that performs click-fraud while running on victims computer and using resources
Kovter.C is the malware that gets installed on the machine without users permission and malicious files get stored in the Windows registry directly.
This fact makes the trojan even more dangerous and difficult to remove. This is a trojan that is known for cybersecurity specialists at least since 2013. Back then it was acting like a file-encrypting virus that pretended to be a notice from police. However, in 2014, cybercriminals decided to use a new tactic and utilized trojan for click frauds.
During the time trojan's operation become more sophisticated. In the middle of 2015, researchers spotted a brand new version of Kovter that has adopted similar techniques as Poweliks virus, meaning that malware became fileless.
Typically, Kovter spreads via exploit kits. Malware has been noticed spreading via popular trojan downloader Nemucod. Once installed on the system, malware places itself in Windows registry. This feature makes malware hard to detect.
However, antivirus utilities might discover these malicious programs under the names of Trojan:Win32/Kovter.C, Troj/Kovter-C, or similar. Kovter.C virus itself can be designed to spread malware on the targeted machines. Other malware like trojans is one of the more common vectors that are known to deliver crypto malware.
After the attack, Kovter virus can give its owner remote access to the affected PC system. After doing so, the attacker gets the ability to control everything that is installed on a PC. This activity is usually initiated from a command and control server (C&C).
During a few years of activity, Kovter.C virus has been noticed spreading ransomware or more dangerous malware like Locky, click fraud adware and other malicious programs. Nevertheless, these cyber infections function differently on the targeted system; users can suspect about trojans existence from these symptoms:
If you recognized a few of these problems, you should obtain or another antivirus and run a full system scan. The updated malware elimination tool will remove Kovter malware from the computer quickly and safely.
We do not recommend locating and stopping malicious processes on the computer yourself. Manual Kovter.C removal might lead to irreparable damage to the system. Thus, you should not risk and rely on professional security tool.
- Several mshta.exe or powershell.exe processes running in the Task Manager;
- Sluggish computer's performance;
- Program startup takes more time;
- Inability to access particular websites;
- An increased amount of suspicious online ads;
- Windows PowerShell errors pop up informing about the stopped program;
- Unusual disk activity.
From our report of May 2019 · not reviewed since
Distribution methods of the trojan horse and how to avoid it
If you have read the article attentively, you should have already realized that different versions of Kovter.C virus are distributed using specific methods.
However, we want to stress out the most popular distribution channels:
In order to avoid Kovter hijack, you should stay away from illegal programs and malicious websites, including adult-themed sites. Security experts from Les Virus also warn that you should also never open unknown email attachments or click on suspicious ads that offer to download critical updates. Keep in mind that legit updates NEVER pop up in your browser.
- exploit kits;
- malicious spam emails;
- malvertising.
How to check the PC for Kovter.C virus
Which name will your scanner show?
Microsoft's name for Kovter.C virus is Trojan:Win32/Kovter.C.
Defender sorts threats by category first, so the word before the colon tells you what kind of program was found, even if the family name means nothing to you.
Do not search for a removal tool by the detection name alone; fake "removal tools" use the same keywords. How the naming works is explained in our guide to antivirus detection names.
- File:
mshta.exe
How to remove Kovter.C virus
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where mshta.exe runs from and stop it
In Task Manager (Ctrl + Shift + Esc) find
mshta.exeon Processes, right-click it and choose Open file location before ending anything.Windows' own files live in
C:\Windows\System32; the same name in%AppData%, %Temp% or C:\Users\Public is an impostor. If the folder is wrong, right-click the process again, choose End task and delete the file.If it starts again within seconds, a task or another process restarts it, so run the scan step in Safe Mode. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Programs like Kovter.C virus add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 3: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after Kovter.C virus, its publisher or created on the day the problem started.Delete those folders, and check
C:\Program FilesandC:\Program Files (x86)too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
A scan finds the parts of Kovter.C virus that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Kovter.C virus can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
From our report of May 2019 · not reviewed since
Kovter.C virus elimination requires your attention and professional anti-malware
If you think that your PC was infected by Kovter.C virus, you should not waste your time and scan it with , or .
It doesn't matter which malware's version affected your device; professional security tools can easily detect and eliminate the infection immediately. However, you should not forget to update your chosen tool first.
Also, remember that choosing the professional and reliable anti-malware tool for Kovter malware termination is crucial. Don't risk getting more threats installed on the PC and get the program from the official source.
If your computer is locked and you cannot remove Kovter.C virus automatically, you have to follow manual elimination guidelines. Please, be careful in order not to damage the system and uninstall all trojan-related files.
Manual Kovter.C virus removal instructions:
- Reboot you infected PC to "Safe mode with command prompt" to disable virus (this should be working with all versions of this threat).
- Run Regedit.
- Search for WinLogon Entries and write down all the files that are not explorer.exe or blank. Replace them with explorer.exe.
- Search the registry for these files you have written down and delete the registry keys referencing the files. Reboot and run a full system scan with updated to remove leftovers of this virus.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed an unfamiliar process called mshta.exe in Task Manager, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
Questions about Kovter.C virus
What is mshta.exe and why is it running?
Every process is started by something:
- a program you installed
- a Windows service
- a scheduled task
- a startup entry
To learn why mshta.exe runs, find its file with Open file location in Task Manager, then look for an entry pointing to that file in Settings > Apps > Startup and in Task Scheduler.
Sort Installed apps by date to see what arrived when the process first appeared. Once you know the owner, you can decide whether to keep it, switch it off at startup or uninstall it completely.
Is Trojan:Win32/Kovter.C a false positive?
Sometimes. Names ending in !ml or describing behaviour are generated by machine learning and occasionally flag cracked tools, game mods or small unsigned utilities. A false positive is likely only when the file is a program you installed from its official developer, it is signed by that developer and other scanners do not flag it.
Files from cracks, cheats, fake updates or unknown downloads are rarely false positives, whatever the detection name. If you are sure the file is genuine, you can report it to Microsoft as a false positive; never add an exclusion for Trojan:Win32/Kovter.C just to make the alert stop.
Can I end mshta.exe in Task Manager?
Ending an unknown process is safe in the sense that Windows will warn you before you close anything critical, and a restart brings back whatever Windows needs. Ending mshta.exe will not remove it, though: if a task or startup entry launches it, it returns at the next sign-in.
Use ending the process as a test. If something important stops working, it belonged to a program you use. If nothing changes and it comes back by itself, find and disable its starter, delete the file and scan the PC.
Should I change my passwords after Trojan:Win32/Kovter.C?
It depends on the category and on whether the file ran. If the name begins with PWS, Spy, Backdoor or Trojan and the file sat in AppData, ProgramData or Temp, assume it ran and change your important passwords from a different device, starting with e-mail, then banking.
Sign out of all sessions too. If Trojan:Win32/Kovter.C is a PUA or was caught in Downloads before you opened anything, a password change is a precaution rather than a must. When in doubt, change the e-mail password and turn on two-step verification; it is quick and protects everything else.
Is mshta.exe a virus?
If it sits outside the Windows and Program Files folders and your antivirus links it to Kovter.C virus, yes. mshta.exe is the file name used by this trojan. Some trojans borrow the names of real Windows components, so the name alone does not decide it:
- right-click the process in Task Manager
- choose Open file location
- look at the folder and the publisher under Properties > Details
A file in a user folder with no publisher is the trojan. Do not delete it by hand while it runs; use the offline scan in the plan above.
Is Microsoft Defender enough to remove Kovter.C virus?
For most home PCs it is a solid first step. Defender detects this threat as Trojan:Win32/Kovter.C, and a full scan followed by an offline scan covers the places where Kovter.C virus usually hides. The offline scan runs before Windows starts, so malware that hides while Windows is running cannot interfere: Run a Microsoft Defender Offline scan.
Defender does not undo everything, though. It does not restore browser settings, decrypt files or change passwords that may have been copied, which is why this guide has separate steps for those. If Defender finds the same item again after removal, something else keeps reinstalling it.
Do I need to reinstall Windows to get rid of Kovter.C virus?
Usually not. A thorough clean-up is enough when the offline scan finds nothing afterwards and you do not see an unfamiliar process called mshta.exe in Task Manager again. A reset is the safer choice if an attacker had remote control, if security tools were switched off, or if detections come back after every clean-up.
Windows 11 can reset itself without a USB stick under Settings > System > Recovery > Reset this PC. Copy documents and photos out first and scan the copies. A reset does not change passwords or undo stolen data, so the account steps still apply.
My antivirus was on. How did a trojan get past it?
Antivirus programs see a file only when it is written or run, and criminals test each new build against popular scanners before release. Detection catches up within hours or days, which is often after the first victims ran it.
Archives with passwords, installers that fetch the malware later, and scripts run through PowerShell make the job harder. That is why behaviour such as downloading cracks or pasting commands matters more than any setting. Keep Windows and Defender updated, and turn on Reputation-based protection in App & browser control.
I found AnyDesk or ScreenConnect that I did not install. Is that Kovter.C virus?
Not necessarily Kovter.C virus, but it is a warning sign. These are legitimate remote support tools, and criminals use them as ready-made backdoors, especially after tech support scams or fake invoice calls.
If you did not install it and no one you trust set it up, uninstall it, change passwords from a clean device and check your bank account. If someone connected to your PC through it, follow the steps for remote access trojans and consider a Windows reset. Installed apps sorted by date shows when it appeared.
Will Fortect remove Kovter.C virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Kovter.C virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Symantec: Kovter malware learns from Poweliks with persistent fileless registry update (read October 6, 2026)
- Check Point: KOVTER RANSOMWARE – THE EVOLUTION: From Police Scareware to Click Frauds and then to Ransomware (read October 6, 2026)
- Trend Micro: KOVTER: An Evolving Malware Gone Fileless (read October 6, 2026)
- Threat Post: Locky ransomware, Kovter click-fraud malware spreading in same campaigns (read October 6, 2026)
- Les Virus: Les Virus (read October 6, 2026)