
More_eggs: what it is and how to remove it
More_eggs virus is a backdoor written in JavaScript programming language. Also known as Terra Loader and SpicyOmelette, the malware allows malicious actors to perform various tasks on the host machine, including executing shell commands, downloading or deleting files/payloads, executing code, transferring information, etc.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan can look at cmd.exe and the other programs installed around the same time.
Do it yourself · free Remove More_eggs yourself 6 steps, about 18 minutes, no software needed.
Start the steps
More_eggs: summary
| Damage | Trojan Backdoors are especially dangerous as they can be used for a variety of malicious activities, including the delivery of secondary payloads, data tracking, retrieving commands from cybercriminals, and much more. Consequently, users might suffer from money loss, identity theft, loss of personal data, etc. |
|---|---|
| Name | More_eggs |
| Type | Backdoor Trojan |
| Also known as | Terra Loader and SpicyOmelette |
| Associated crybercriminal gangs | Cobalt Group, FIN6 |
| Delivery method | Malicious actors mostly deliver the malicious payload of the backdoor in a sophisticated and multi-stage malicious email campaign |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Symptoms | Trojans are programmed to remain on the system without being detected – they rarely emit any symptoms and usually remain hidden on the infected systems as long as possible |
|---|---|
| Termination | In some cases, More_eggs trojan might self-delete. Nevertheless, it is known that bad actors load the host machine with other payloads that can remain on the system for weeks or even months. Regardless of what type of infection you are dealing with, you should employ reputable anti-malware software to terminate all the malicious components from your system |
| Detection names | No Microsoft detection name is known |
| Distribution | Not recorded in the old report |
| Evidence | 7 write-ups by security sites; details still limited |
| File names | cmd.exe |
| First seen | 19 November 2019 |
| Facts checked | 6 October 2026 |
What More_eggs does on an infected PC
From our report of Nov 2019 · not reviewed since
More_eggs virus is a backdoor Trojan that is utilized by Cobalt Group and other criminal gangs to attack corporations and regular users
More_eggs virus is a backdoor written in JavaScript programming language.
Also known as Terra Loader and SpicyOmelette, the malware allows malicious actors to perform various tasks on the host machine, including executing shell commands, downloading or deleting files/payloads, executing code, transferring information, etc. In other words, thanks to More_eggs malware, the attackers can control the machine over an HTTPS-based C2 protocol and, although the functionality of the commands is limited, it is enough to initiate the download of more sophisticated payload.
More_eggs backdoor is used to target all versions of Windows machines, and several variants of it have been released, including version 2.0 and 4.4. The malware has been prevalent for at least a couple of years (first described by Trend Micro specialists in August 2017), , and has been actively distributed with the help of malicious spam email attachments or hyperlinks that reach out financial organizations or regular PC users.
More_eggs malware has been one of the main assets of financially-motivated Cobalt Group and FIN6 cybercriminal gangs, which are also believed to be involved in a highly-evasive PureLocker ransomware and open-source software Cobalt Strike delivery campaign.
More_eggs backdoor is sold on the Dark Web as Malware-as-a-Service, i.e., anyone can buy and use the payload as long as the developers receive a predetermined percentage of the profits obtained from malware attacks. Thus, there is a high chance that there are multiple other malicious actors that distribute the More_eggs virus.
More_eggs virus might be a high threat to any computer user, as a backdoor is designed to remain on the system undetected for as long as possible. During its operation, it can send the attackers the required information, such as the installed anti-malware program, IP address, computer name, OS versions, and other data.
Due to this, More_eggs removal might be fairly hard, although most up-to-date security programs should be able to take care of its elimination in the Safe Mode environment.
From our report of Nov 2019 · not reviewed since
More_eggs malware performs multiple actions after infiltration
Upon infiltration, the More_eggs virus establishes a connection between a compromised machine and the attacker's Command and Control server.
After that, it uses WMI and PowerShell commands to move laterally and escalate privileges on the impacted system. This method is often known as "living off the land" by security experts and is often associated with fileless attacks - malware resides in the system's memory instead of the hard drive, complicating AV detection.
Nevertheless, most of the up-to-date security applications should be capable of detecting post-infection activities and remove More_eggs without much trouble.
More_eggs Trojan also allows the attackers to download secondary payload, such as Mimikatz post-exploitation tool. It will enable them to extract sensitive information from the host machine and access various systems with the help of harvested credentials, resulting in privilege escalation and further movement within the IT infrastructure.
Process injection is not the only sophisticated ability of More_eggs virus, however. Several malware components, along with communications between the host machine and the malicious server, are encrypted by such encryption algorithms like RC4. Additionally, the backdoor modifies Windows registry files, sends out HTTP GET requests, writes information on text files (that are later deleted), and much more. These actions are performed with the help of the following commands:
- d&exec - Download and execute an executable (.exe or .dll).
- more_eggs - Delete the current More_eggs and replace it.
- Gtfo - Uninstall activity.
- more_onion - Execute a script.
- via_c - Run a command using "cmd.exe/C".
From our report of Nov 2019 · not reviewed since
More from our earlier report on More_eggs
- Malware might cause significant damage to system files, which might prompt the need to reinstall the operating system due to crashes or other malfunctions.
- Simple campaigns typically use a single technique and often embed the final executable payload into the exploit document.
- However, more complex campaigns require meticulous planning on the part of the attacker and include more sophisticated techniques to hide the presence of the malicious code, evade operating system protection mechanisms and eventually deliver the final payload, likely to be present only in the memory of the infected computer and not as a file on the disk.
How More_eggs got on your PC
From our report of Nov 2019 · not reviewed since
In 2018, More_eggs was closely analyzed by Talos Intelligence experts, that described the malspam campaigns as "highly sophisticated and evasive":
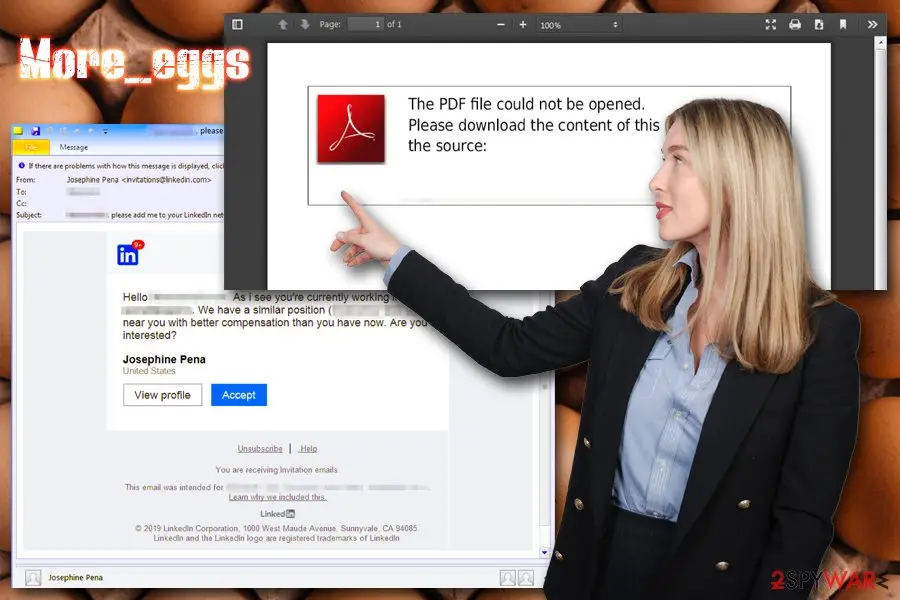
Several different More_eggs malware delivery campaigns were observed in the past, although most of the time, a fake (but legitimately-created) Linkedin account is made by the attackers. Using this account, the attacker delivers an email to a particular user of the targeted organization - it contains a subject line "Hi , please add me to your professional network."
More_eggs actors pretend to offer users a new job in a similar position with allegedly much better prospects. In some cases, the emails are embedded with a Google Drive link, which, once clicked, displays a message "Online preview is not available" and prompts users to click on another link, that is actually malicious.
The URL, once clicked, automatically downloads a WSF file inside a ZIP archive. Once executed, it would initiate the More_eggs virus infection process.
Other times, attackers opted to direct potential victims to sites that use stolen branding, which makes the campaign much more believable. Users were prompted to download the alleged job description inside an MS Word file, which, once opened, would not display anything until the "Enable Content" button is pressed - Macros enabled.
The mentioned documents are often used to abuse software vulnerabilities, including:
- CVE-2017-0199;
- CVE-2017-8570;
- CVE-2017-8759;
- CVE-2017-11882;
- CVE-2018-0802;
- CVE-2018-8174.
How to check the PC for More_eggs
- File:
cmd.exe
How to remove More_eggs
How to remove More_eggs and lock the attacker out
Someone may have had remote control of the PC.
Cut the connection first, then remove the trojan and secure your accounts.
Step 1: Remove remote access tools and lock the attacker out
Unplug the network cable or turn off Wi-Fi first, so any remote session drops.
In Settings > Apps > Installed apps (Windows 11) or Apps & features (Windows 10), uninstall remote access programs you did not set up yourself, such as AnyDesk, ScreenConnect, TeamViewer or an unknown "support" tool.
Check Settings > Accounts > Other users (Family & other users in Windows 10) for accounts you did not create. Turn off Remote Desktop under Settings > System unless you use it.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 2: Check where cmd.exe runs from and stop it
cmd.exeis the part you can see, and its location tells you whether it belongs there. Right-click it on the Processes page of Task Manager and choose Open file location, then right-click the file > Properties > Digital Signatures to see who signed it.An unsigned file, or one in a user folder such as
%AppData%, is the one to remove: end the task, then delete the file.Note the folder name, because the same folder usually holds its other files. This is the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 3: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to More_eggs or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 4: Remove it from startup
Whatever More_eggs installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Nov 2019 · not reviewed since
Ways to prevent being deceived by sophisticated malspam campaigns
Phishing emails or websites have been around for many years now and were often poorly executed.
In most of the cases, users can find suspicious indicators due to poor grammar, spelling mistakes, bad formatting, and other symptoms. However, cybercriminal gangs are sophisticated individuals, and they take time and effort to craft phishing emails that are identical to original ones. Besides, they also leverage multi-stage infection mechanisms that are not as obvious for many computer users.
Therefore, it is vital to recognize phishing emails before they manage to inflict major damage to computer systems and connected networks. Regardless of how well worded the email is, you can always check the sender's address - it is often a good indicator that it is illegitimate (nevertheless, beware of emails spoofing).
Additionally, you should NEVER enable content by turning on the Macro function unless you have been expecting a document with such a feature.
Additionally, because some of the malware campaigns have been actively using software vulnerabilities to proliferate the malicious payload, it is vital to patch all the operating systems on time (along with all the installed software, e.g., Drupal). Finally, make sure your computer is equipped with a sophisticated anti-malware solution.
From our report of Nov 2019 · not reviewed since
Delete More_eggs backgood with all its components from your system
Due to highly evasive infection mechanisms (fileless infection), detecting and preventing More_eggs virus becomes an almost impossible task for most modern security solutions.
Nevertheless, by employing powerful anti-malware software, you should be able to remove More_eggs virus with all its components. The best way to do that is by accessing Safe Mode with Networking, as explained below - it would temporarily disable the main functions of the malware.
While More_eggs removal might not be necessary in every case (the malware can delete itself under particular circumstances), the termination of other components introduced by the Trojan is mandatory. In other words, just because the main payload is deleted after the infection, it does not mean that there is nothing else to eliminate.
[GI=method-1]Accessing Safe Mode with networking will help you to stop the main functions of More_eggs malware:
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed an unfamiliar process called cmd.exe in Task Manager has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
Questions about More_eggs
What is cmd.exe and why is it running?
Every process is started by something:
- a program you installed
- a Windows service
- a scheduled task
- a startup entry
To learn why cmd.exe runs, find its file with Open file location in Task Manager, then look for an entry pointing to that file in Settings > Apps > Startup and in Task Scheduler.
Sort Installed apps by date to see what arrived when the process first appeared. Once you know the owner, you can decide whether to keep it, switch it off at startup or uninstall it completely.
Can I end cmd.exe in Task Manager?
Ending an unknown process is safe in the sense that Windows will warn you before you close anything critical, and a restart brings back whatever Windows needs. Ending cmd.exe will not remove it, though: if a task or startup entry launches it, it returns at the next sign-in.
Use ending the process as a test. If something important stops working, it belonged to a program you use. If nothing changes and it comes back by itself, find and disable its starter, delete the file and scan the PC.
Can I just delete cmd.exe?
Deleting cmd.exe by hand rarely removes More_eggs. While the trojan runs, Windows may refuse to delete the file, and if you succeed, a scheduled task, a service or a second copy may bring it back at the next restart.
The file can also be only one part of the infection: loaders and remote access tools often install other programs. Use the Microsoft Defender offline scan, which removes the file together with its startup entries before Windows loads, and then check startup items and scheduled tasks as described in the plan.
What are the signs of a trojan infection?
Most trojans try to leave no visible signs, so look for side effects. Common ones:
- Windows Security turned off or unable to update
- new entries in Startup apps or Task Scheduler
- programs in Installed apps you did not install
- browser settings that changed by themselves
- unusual network activity while the PC is idle
- password-reset or login-alert e-mails you did not trigger
None of these proves an infection on its own. Together with an antivirus alert naming More_eggs, they are a strong reason to follow the full plan.
Can I keep using the PC while More_eggs is on it?
Not for anything that matters. As long as the program behind an unfamiliar process called cmd.exe in Task Manager runs, it can see what you type and what the browser stores, and it may download more malware. Disconnect the PC from the internet while you remove it, and do your banking, e-mail and password changes from another device.
Once the offline scan finds nothing and the sign does not return after a few restarts, normal use is fine. If the scan keeps finding new items, or you cannot remove the startup entry, a reset of Windows is the safer choice.
Is a trojan infection worth reporting to the police?
If there was harm, yes. Unauthorised payments, accounts used for fraud, blackmail or a remote session during a scam call all belong in a report, and banks often ask for its reference number before they refund anything.
If antivirus caught More_eggs before it ran and nothing was misused, there is nothing to report. Keep the evidence anyway:
- protection history
- the original download
- the dates
Businesses may also have to notify a data protection authority if personal data could have been accessed.
Should I reset my PC because of More_eggs?
Only if the signs point to deeper access. Reset when you see an unfamiliar process called cmd.exe in Task Manager again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
Which malware family is More_eggs?
That is not known yet. More_eggs has been reported by people who saw an unfamiliar process called cmd.exe in Task Manager, but no sample has been analysed publicly, so security companies have not assigned it to a family. The name you see may be a file or program name chosen by the authors, not a family name.
This does not stop you from removing it: the startup points, the offline scan and the account steps are the same for most families of this type. If Microsoft Defender or another scanner gives the file a detection name, write it down; that name is the best clue to the family and is useful when you report the incident.
Can a normal remote support program be a backdoor?
Yes. Tools such as AnyDesk, TeamViewer and ScreenConnect are legitimate, but whoever controls the account behind them controls the PC. Scammers install them during fake support calls, and some trojan campaigns install them silently because antivirus programs do not flag a genuine, signed product.
If you find one you did not set up, uninstall it, check Startup apps for related entries and change passwords from another device. If money or accounts were involved, call your bank and report the incident.
Will Fortect remove More_eggs?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For More_eggs, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Mitre: Cobalt Group (read October 6, 2026)
- Cisco Talos: Multiple Cobalt Personality Disorder (read October 6, 2026)
- Proofpoint: Fake Jobs: Campaigns Delivering More_eggs Backdoor via Fake Job Offers (read October 6, 2026)
- Crowdstrike: Going Beyond Malware: The Rise of "Living off the Land" Attacks (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)