
PUA:Win32/ICBundler: what the Defender alert means and how to remove it
PUA:Win32/ICBundler is the name Microsoft Defender gives to a potentially unwanted application, most likely an installer that bundles other software, and Microsoft does not count it as a virus. Find which file raised it and what came with it, then remove it in Windows Security and run a full scan.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If a Microsoft Defender alert for PUA:Win32/ICBundler on a downloaded installer keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove PUA:Win32/ICBundler yourself 5 steps, about 15 minutes, no software needed.
Start the steps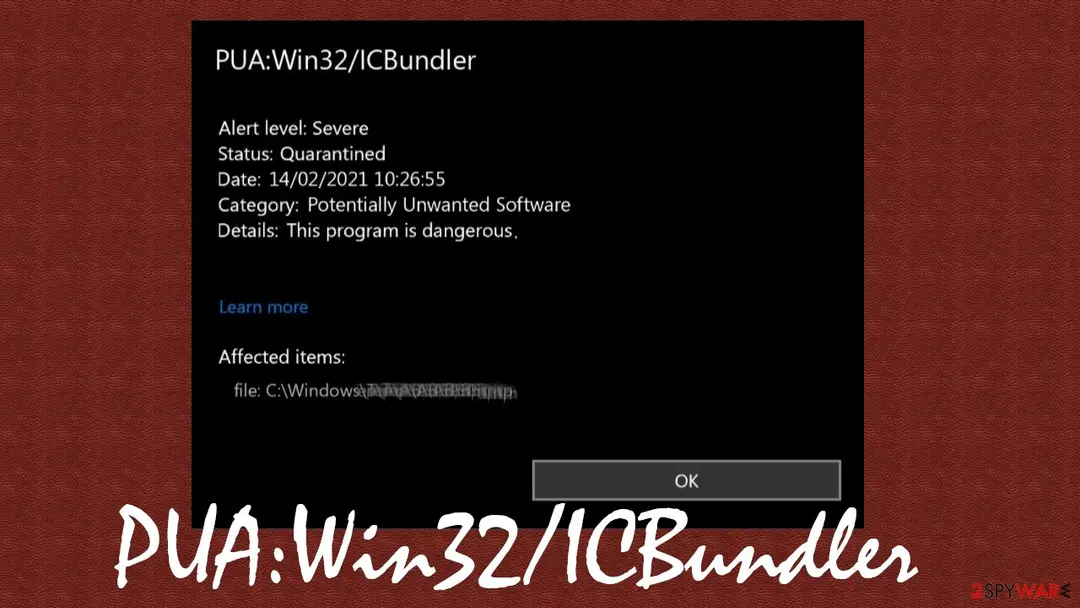
PUA:Win32/ICBundler: summary
| Type | A Microsoft Defender detection name for a potentially unwanted application, most likely a bundling installer; not one program and not malware by Microsoft's definition |
|---|---|
| Risk | Low to medium: the reports we read show blocked installers, not a trojan, but the extras that came with an installer you ran can be unwanted |
| Symptoms | The Defender alert, often the only sign; Microsoft lists slow performance and changed settings for the group; ads or redirects only if a bundled extra installed |
| How to get rid of it | Remove the item in Protection history, delete the installer, uninstall what came with it, run a Full scan and a Microsoft Defender Offline scan |
| Our check (6 October 2026) | No PC test: we read Microsoft's entry, its PUA and Offline scan pages, a Microsoft Q&A thread and a forum post; no installer was run |
| First seen | Microsoft entry published 11 December 2020; our first guide 23 February 2021; newest report we found November 2022 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Detection | Microsoft Defender: PUA:Win32/ICBundler, also written PUABundler:Win32/ICBundler in 2022 reports |
|---|---|
| Not to be confused with | PUA:Win32/InstallCore, a separate Microsoft detection, and with the Mac or browser pop-ups in our old picture, which are not this detection |
| Name | PUA:Win32/ICBundler |
| Evidence | 0 write-ups by security sites; details still limited |
| Microsoft Defender name | PUA:Win32/ICBundler |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against Microsoft Security Intelligence, Microsoft Learn (PUA protection and Defender Offline), a Microsoft Q&A thread, a Windows 10 Forums post, Adobe's Flash end-of-life page and Microsoft's Internet Explorer lifecycle page.
We ran no installer and tested no PC; the removal steps follow Microsoft's pages and were not tried on a live infection, and the browser menu names were not rechecked today. A quiet result from any check does not clear a PC.
What PUA:Win32/ICBundler is, and what it is not
PUA:Win32/ICBundler is a detection name used by Microsoft Defender Antivirus, not the name of one program. It says Defender judged one file to be a potentially unwanted application, most likely an installer that carries other software with it. It does not say the file is a virus.
- 1
What the name is
Microsoft's own entry for the name is titled PUA:Win32/ICBundler, was published on 11 December 2020 and is marked as detected by Microsoft Defender Antivirus. It lists no aliases. Our 2021 guide called it an intrusive adware infection and a virus; Microsoft does not call it either.
- 2
What Microsoft says about it
Very little. The entry says technical details are currently not available. Its symptom list is the general one for the whole group: slow performance, added or modified files, changes in desktop settings, freezing or crashing, and less free storage. None of these is tied to this name in particular.
- 3
What a PUA is
Microsoft describes potentially unwanted applications as software that can make a PC run slowly, show unexpected ads or install other software you did not expect. Its examples are advertising software, bundling software that offers to install other programs, and evasion software. Microsoft adds that a PUA is not considered a virus or other malware.
- 4
What the reports point to
A helper on Microsoft's Q&A forum read the name as a software installer that bundles other apps, possibly from a torrent client. That is one volunteer's reading, not a Microsoft statement. The letters IC in the name are not explained anywhere we looked.
- 5
What our 2021 guide got wrong
It called the detection a virus, described pop-ups, banners and redirects that no source we read ties to this name, and sent readers to a paid anti-malware tool and a system tune-up tool. Defender is the tool that raised the alert and can handle it, and a tune-up tool repairs nothing a PUA changed.
- Shown by
- Microsoft Defender Antivirus (Windows Security). Forum posts also show it as PUABundler:Win32/ICBundler
- Category
- Potentially unwanted application, not malware by Microsoft's definition
- Platform
- Windows program files. Win32 does not mean your Windows is 32-bit
- Is it one program?
- No. Reports name a downloaded uTorrent.exe, a Logitech software install and an installer that came with Anaconda
- Microsoft entry published
- 11 December 2020, with no update date and no technical details
- Newest report we found
- November 2022 on Microsoft's Q&A forum. Defender still carries the name, but we found no newer public report
So the useful questions are which file triggered the alert, whether it ran, and what came with it. The next chapters help you answer them.
What PUA:Win32/ICBundler does on an infected PC
How to read the alert, part by part
Microsoft's page does not explain the name, so the table separates what the words show from what we can only read into them.
| Part | What it shows | What it does not show |
|---|---|---|
| PUA: | The detection is for a potentially unwanted application. Microsoft says these notifications are prefaced with PUA: | That the file is malware. Microsoft does not count a PUA as a virus |
| Win32/ | A Windows program file | That your Windows is 32-bit |
| ICBundler | The label Defender gave the file. A forum helper read it as an installer that bundles other apps | What the file installs. Microsoft gives no technical details |
| PUABundler: | The form some 2022 reports show, for the same name | A different threat; we found no description of a difference |
| Remove, Quarantine, Allow on device | The three choices in our 2021 picture for an active detection | That any of them is needed if Defender already blocked the file |
| Status: Failed | A 2022 reader's alert said the threat or app might not be fully remediated | That the PC is infected. It means Defender did not finish the action |
What we checked on 6 October 2026, and what we could not
There is no website to test here and we ran no installer. We read Microsoft's pages and the public reports that name the detection.
Our reading of the sources, 6 October 2026
- The name is a real Defender detectionMicrosoft's Security Intelligence has an entry for PUA:Win32/ICBundler, published 11 December 2020. It is not an invented scam alert.
- What the detection looks forNot documented. The entry says technical details are not available.
- Which file is behind itDiffers per case: a file called uTorrent.exe in Downloads, a Logitech software install, and an installer that came with Anaconda. One name covers different files.
- Blocked at download or installA volunteer Microsoft forum moderator wrote that if Defender blocked the installer, the PUA part was blocked from installing and the PC was safe, and that the installer can simply be deleted. That is one helper's view, not Microsoft's.
- A bundled program that did installIn one 2022 case the reader traced the alert to Lavasoft's Web Companion, which came with Anaconda; the helper had named it from the alert. The reader cleaned the Temp folder and found nothing under the name afterwards.
- Our 2021 claims about ads and redirectsNot confirmed. No source we read shows ICBundler itself displaying ads or redirecting a browser.
- A quiet scan afterwardsDoes not clear the PC. A second scan that finds nothing is one data point, because scanners label files differently and some software hides from some of them.
Treat as an unwanted installer until you know the file The reports we read describe a bundling installer that Defender blocked, not a trojan. We saw nothing on any PC, and a quiet result is never proof. Find the file, check what came with it, then follow the check and removal chapters.
Where the name has been reported
These are the cases we could read. They show how different the files are. They are not a list of what your alert is.
| Case | What the source says | How it ended |
|---|---|---|
| uTorrent.exe in Downloads (23 February 2021) | A reader's Windows 10 alert: Detected PUA:Win32/ICBundler, status Removed, file C:\Users\...\Downloads\uTorrent.exe. The file had been on the PC for about a day. He saw only the Allow action and could not tell if the file was gone | The replies in the thread did not answer; they quoted other readers' uTorrent installation problems |
| Installer with Anaconda (28 November 2022) | A reader's alert showed the name with status blocked, not deleted. A helper named Lavasoft's Web Companion and pointed to the Temp folder; the reader traced it to a bundle with Anaconda | The reader deleted the Temp folder contents and found no trace of Lavasoft or Web Companion |
| Logitech software (28 November 2022) | A reader installed Logitech Options and Options+, and four days later Defender showed PUABundler with status Failed and 'might not be fully restored' | The thread has no verdict on that file |
| Reddit threads, around 2022 | Search results show posts titled 'Windows Defender is not deleting PUA:Win32/ICBundler' and 'PUAbundler:Win32\ICbundler virus? quarantine or delete it?' | We read only the titles and excerpts, not the replies |
How the name has turned up, 2020 to 2022
Microsoft's entry is from December 2020. Every public report we found is from February 2021 to November 2022.
11 December 2020
Microsoft adds the entry
The Security Intelligence page for PUA:Win32/ICBundler is published. It has no update date and no technical details.
12 February 2021
The Windows Security entry in our guide
A Windows Security entry for the name, level Low, with Remove, Quarantine and Allow on device.
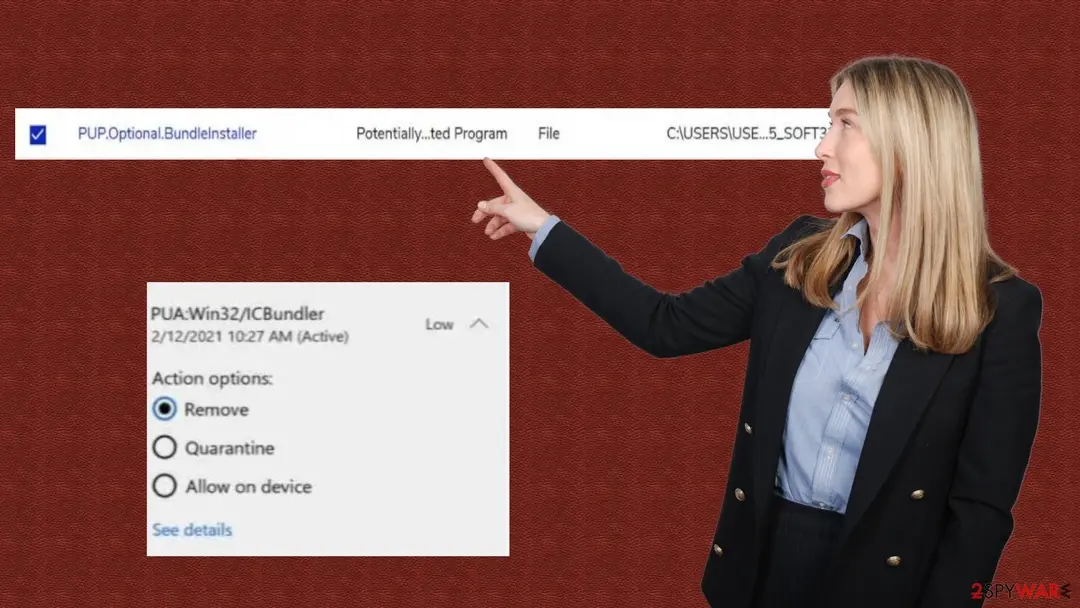
From our 2021 guide: the Windows Security entry for PUA:Win32/ICBundler, 12 February 2021, level Low, with the choices Remove, Quarantine and Allow on device. The row above it is a different name, PUP.Optional.BundleInstaller, from a scanner we could not identify. The woman and the background were added by us. 14 February 2021
The alert window in our guide
Our cover picture shows the same name as a quarantined item in the category Potentially Unwanted Software. Two days earlier the other picture shows level Low.
23 February 2021
Our first guide, and a uTorrent report
Our guide called the name an adware infection. The same day a reader on Windows 10 Forums posted an alert for a uTorrent.exe download.
25 to 29 November 2022
Microsoft Q&A threads
Readers asked if the PC was safe after PUABundler:Win32/ICBundler was blocked but not deleted, and two traced it to bundled installers.
2026
No newer report found
We found no public report newer than November 2022 in the sources we read. We could not tell if Defender still raises the name often.
What the old guide said about ads and redirects, checked
Our 2021 guide described adware: pop-ups, banners, redirects and tracking. The parts below separate what Microsoft says about PUAs from what nobody has shown for this name.
| Old claim | What we found | Our reading |
|---|---|---|
| It shows pop-ups, banners, in-text links and sponsored search results | Microsoft lists advertising software among PUAs, but its entry for this name shows no ad behaviour | Not confirmed for ICBundler. Ads, if you see them, usually come from a program that was installed with it |
| It redirects to affiliated sites, sometimes without a click | No source we read shows this | Not confirmed. A redirect is a reason to check your browser, not proof of this detection |
| Adware does not change browser settings, a hijacker does | Our 2021 guide drew this line between the two | A fair description of the two kinds. Which one a bundled extra is must be checked on the PC |
| Ads show imaginary news and amazing deals | This is how fake-update and bundle ads are written | Kept as a warning in the entry chapter |
| The PUP or its advertisers collect your browsing habits | Microsoft's page lists no data collection for the name | Not confirmed. Treat it as a risk of bundled programs, not a fact about this file |
What PUA:Win32/ICBundler can steal or download
What an unwanted installer can cost you
None of the reports we read shows a real infection behind the name. These are the risks of the bundled software, not of the detection.
- Medium
Other unwanted programs
Microsoft defines bundling software as software that offers to install other software. Our 2021 guide warned the same: a bundle can bring more PUPs.
- Medium
Ads and redirects
If an ad-showing program came along, you may see unwanted ads or sudden redirects. Our guide said ads can lead to pages with explicit or malicious content, so do not click them.
- Medium
Browsing data
Our 2021 guide said the PUP or its advertisers can track your habits. Nothing we read shows ICBundler doing this; a bundled extra could.
- Medium
Lost privacy and more infections
Our guide named loss of privacy and more infections as the cost of clicking deceptive ads. That holds for any bundled program you leave installed.
- Low
Slower PC
Microsoft lists slow performance, changed settings and less free storage as signs of the PUA group. They can come from any unwanted program.
- Low
Nothing at all
If Defender blocked the installer at download, the volunteer on Microsoft's forum said it never reached the PC. The danger is the case in which you ran it.
What you may notice, and what the sources show
The alert itself is often the only sign. Our 2021 guide listed more ads than usual, sudden redirects and a slower device; Microsoft's list is shorter.
| Sign | What we found |
|---|---|
| The Defender alert | The usual and often the only sign. It came after a download or an install in every report we read |
| More ads than usual, sudden redirects | Our 2021 guide's sign. No source ties it to this name. If it happens, check your browser extensions, not only this file |
| Slow performance, changed settings, freezing, less storage | Microsoft's list for the PUA group. Not specific to this name |
| Crashing, lag, freezing, blue screens | Our 2021 guide linked these to changes in system files. A blocked installer changes none; they are reasons to scan, not proof |
| The alert says Failed or comes back | A 2022 reader's alert said the threat might not be fully restored. It means a leftover or a restart is needed; it does not prove infection |
| Nothing | Adware is made to stay quiet, which is why our 2021 guide called it a silent infection |
How to check the PC for PUA:Win32/ICBundler
What antivirus programs call PUA:Win32/ICBundler
Microsoft Defender reports PUA:Win32/ICBundler as PUA:Win32/ICBundler.
In a Defender name, the part before the colon is the category, the part after it is the platform, and the part after the slash is the family Microsoft assigned. A suffix after ! is an internal Microsoft marker, not a different threat.
Generic labels such as Agent, GenericKD or Malware.AI only say that a file looks malicious, not what it does; our guide to antivirus detection names shows how to read them.
How a file like this gets onto a PC
Our 2021 guide named three routes: freeware bundles, deceptive ads and fake Flash updaters. Microsoft's PUA page describes the same trick.
- 1
Freeware bundles
Our guide said PUPs are delivered with software bundles in which all apps in the pack are preselected for installation. Microsoft calls this bundling software: it offers to install other software that is not signed by the same publisher.
- 2
Custom or Advanced setup
Our guide said to pick Custom or Advanced over Recommended, Quick or Standard, and to take your time. That still works: untick each extra, decline the offer, and close the installer if a page asks for a browser or search change you did not want.
- 3
Deceptive ads
We have all met misleading ads. They show an amazing deal or a tool that will speed up the internet and send you to a page that has nothing to do with the ad. The promised tools usually do nothing, or slow the device and bring more ads.
- 4
Free software from copy sites
The readers' cases involve a torrent client, an Anaconda download and Logitech software. A helper said the installer was possibly a torrent client. Take programs only from their makers' sites.
- 5
Fake Flash updaters
Adobe stopped supporting Flash Player on 31 December 2020 and blocked Flash content from 12 January 2021, and says unauthorised Flash downloads are a common source of malware. Any 'Flash update' offered to you now is not a real update.
The habits that cover all of them: install from the maker, read each installer screen, choose Custom, and keep Defender on.
Check your PC before you delete anything
Do not click Allow on device. Write down what the alert says first, then look at what is on the PC.
- 1
Open Protection history
Open Windows Security > Virus & threat protection > Protection history. Find the PUA:Win32/ICBundler entry and expand it. Note the status (Quarantined, Removed, Blocked, Failed), the date and the file path.
- 2
Read the file name and folder
A path in Downloads or Temp points to an installer. An installer you ran yourself, for example a torrent client or a utility, tells you which program carried it. Microsoft says a blocked PUA file is moved to quarantine and its notification starts with PUA:.
- 3
Ask whether it ran
If Defender blocked the file at download, the volunteer helper on Microsoft's forum said it never got to the PC. If you opened the installer, the bundled extras may have tried to install; check the next step.
- 4
Look at what installed recently
Open Settings > Apps > Installed apps and sort by install date. Note programs you did not choose, such as a browser, a 'companion', a coupon tool or a PC cleaner. In the Anaconda case the extra was Lavasoft's Web Companion.
- 5
Look at what starts with Windows
Press Ctrl + Shift + Esc and open Startup apps. Note names you do not know and the ones that started recently.
- 6
Read every name in the report
Write down every detection, not only this one. Other names beside it, for example PUA:Win32/InstallCore, which appears in Microsoft's own sample output, show what else was in the same file.
How to remove PUA:Win32/ICBundler
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Programs like PUA:Win32/ICBundler add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 2: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after PUA:Win32/ICBundler, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of PUA:Win32/ICBundler that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
PUA:Win32/ICBundler can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Remove it from Windows 11 and Windows 10
Do the steps in order and stop when a full scan is clean and the alert has not returned. We did not run these steps on a live infection; they follow Microsoft's pages. Microsoft Defender is the program that found the file, and it is enough for this detection.
- 1
Remove the item in Protection history
In Protection history open the PUA:Win32/ICBundler entry and choose Remove. If you see only Allow on device, as the uTorrent reader did, close the window and run the scan in the next step instead. Do not choose Allow.
- 2
Delete the installer
Delete the installer you downloaded, for example from Downloads, and empty the Recycle Bin. The Microsoft forum helper's advice for a blocked installer was the same: if you have the installer, delete it.
- 3
Uninstall what came with it
Open Settings > Apps > Installed apps, find the programs you noted, choose the three dots and Uninstall. Do this for any browser, companion or cleaner you did not pick.
- 4
Clear leftovers in Temp
The Microsoft helper told the Anaconda reader to empty the Temp folder. Do it with Settings > System > Storage > Temporary files, or delete only the file Defender listed, rather than everything by hand.
- 5
Run a full scan
Update Windows Security first. Then open Virus & threat protection > Scan options, choose Full scan and click Scan now. Our 2021 guide said to run a full system scan and follow the security software's recommendations; that is still right.
- 6
Run a second opinion with Microsoft Defender Offline
In Scan options choose Microsoft Defender Offline scan and click Scan now. Microsoft says it takes about 15 minutes, restarts the PC and runs outside the normal Windows kernel. Save your work first. If BitLocker is on, Microsoft says to suspend it first. Afterwards read Protection history.
- 7
Check the status again
If the entry still says Failed or Active after a restart, scan again and then run the offline scan. If it keeps returning, the installer or a bundled program is still on the PC.
After a clean scan you do not need a tune-up or optimizer tool. Our 2021 guide recommended one for 'repairing' system damage; we found no damage to repair and no source showing such a tool fixes it.
If you see ads or changed settings: check your browser
Our 2021 guide said the adware mainly affects Chrome, Firefox and Edge. That belongs to the programs bundled with the file, not to the detection, so do this only if you see ads, redirects or a changed start page. These menu names are the browsers' own as we know them; we did not recheck them today.
| Browser | Extensions to look at | Reset |
|---|---|---|
| Google Chrome | Menu (three dots) > Extensions > Manage extensions. Remove any you did not install | Settings > Reset settings > Restore settings to their original defaults |
| Microsoft Edge | Menu > Extensions > Manage extensions. Remove any you do not know | Settings > Reset settings > Restore settings to their default values |
| Mozilla Firefox | Menu > Add-ons and themes > Extensions. Remove any you do not know | Menu > Help > More troubleshooting information > Refresh Firefox |
- 1
Clear cookies from the browser, not with a tool
Our guide told readers to use an optimizer to wipe tracking cookies. The browser can do it: open its settings, find Delete browsing data or Clear data, and select cookies and site data.
- 2
Turn on PUA blocking in Edge
Microsoft says Chromium Edge can block potentially unwanted app downloads. Open Settings > Privacy, search, and services and under Security turn on Block potentially unwanted apps.
Could it be a false alarm? When to restore or allow
Possibly, but a PUA detection is not a claim of malware, so the question is rather whether you want the program. Microsoft says a file blocked by PUA protection can be added to an exclusion list when a task needs it.
| Points to a bundled or unwanted installer | Points to a program you wanted |
|---|---|
| The file came from a copy site, a torrent or an ad | The file came from the maker's own site |
| The file is an installer that offers extras | The file is the program itself, not an installer |
| Other detections appear next to it | Only one detection, and the PC works normally |
| New programs, extensions or a changed browser appeared | Nothing new appeared |
| The alert returns after you remove it | The alert came once and stayed quarantined |
- 1
Do not allow it first
Allow on device lets the file run. If you want the program, download it again from its maker's site, choose Custom setup and decline the extras.
- 2
Exclusions are the last step
Microsoft documents exclusions by file extension and folder location. Add one file, never a whole folder such as Downloads.
- 3
Test with audit mode, if you manage the PC
Microsoft says PUA protection has an audit mode that detects without blocking, and events are logged under event ID 1160. It is meant for companies checking their software.
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed A Microsoft Defender alert for PUA:Win32/ICBundler on a downloaded installer in the list of installed apps has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
If you ran the installer or clicked an ad
The scans above deal with the file. These steps deal with what the extras could have done.
- 1
Uninstall the extras
Do the Installed apps step again, with the install date of the installer as your guide, and remove everything that arrived with it.
- 2
Do not follow what the ad asked
Our guide said that clicking can lead to explicit, malicious or other shady pages. Close the tab. Do not enter passwords or card details on a page an ad opened.
- 3
Change passwords from another device
If you typed passwords or card details after the installer ran, change the email password first, then banking, and turn on two-step sign-in.
- 4
Check browser settings
If the homepage, new tab page or search engine changed, remove the extension and reset the browser as in the browser chapter.
- 5
Scan again in a week
Run a full scan and a Defender Offline scan a week later. Keep a screenshot of the first alert.
Keep unwanted installers off your PC
The advice from 2021 still holds: pick Custom setup and do not click deceptive ads. Here it is with current details.
Do
- Choose Custom or Advanced in an installer and untick every extra. Take your time on the offer screens.
- Download programs from their makers' sites or the Microsoft Store.
- Keep Microsoft Defender or another security product on with real-time protection, and let it update.
- Keep Block potentially unwanted apps on in Edge, and keep PUA protection on in Windows Security.
- Keep a backup of your documents on a disk you unplug (File History or OneDrive). This replaces our 2021 data-recovery tool advice.
- Install Windows Update monthly, and update your browser.
Don't
- Do not click pop-ups, banners or ads that promise news, deals or a speed-up. Our 2021 guide said they should never be clicked.
- Do not install a Flash update. Flash ended in 2020 and no real update exists.
- Do not use installers from copy sites, torrent portals or cracks.
- Do not click Allow on device to make an alert go away.
- Do not buy a cleaner or tune-up tool because an alert told you to.
Questions about PUA:Win32/ICBundler
What is PUA:Win32/ICBundler?
It is a detection name used by Microsoft Defender Antivirus for a potentially unwanted application, most likely an installer that bundles other software. Microsoft's entry, published on 11 December 2020, lists no aliases and says technical details are not available. A volunteer on Microsoft's forum read it as a software installer that bundles other apps, possibly a torrent client.
The name covers different files in different reports, so it is not one program. Treat the alert as a prompt to find out which file raised it, whether it ran and what came with it, not as the name of a single infection you can look up.
Is PUA:Win32/ICBundler a virus?
No, by Microsoft's own definition. Microsoft says a potentially unwanted application is not considered a virus, malware or other threat, although it can slow the PC, show unexpected ads or install other software. Our 2021 guide called it an adware infection and a virus, and we have corrected that.
A PUA can still bring unwanted extras, so do not ignore the alert. Check which file was flagged, whether you ran it and what installed beside it. A quiet result from one scan does not clear a PC, because scanners label files differently.
How do I remove PUA:Win32/ICBundler from Windows 11 or 10?
Open Windows Security, go to Virus & threat protection and Protection history, and choose Remove on the entry. Delete the installer from Downloads, then uninstall programs that came with it in Settings, Apps, Installed apps.
Run a Full scan from Scan options, and then a Microsoft Defender Offline scan as a second opinion; Microsoft says it takes about 15 minutes and restarts the PC.
Do not click Allow on device. If the entry says Failed, restart and scan again. We did not run these steps on a live infection; they follow Microsoft's pages.
Is my computer safe if Defender blocked it but did not delete it?
Most likely, but not proven. A volunteer moderator on Microsoft's forum wrote that if Defender blocked the installer at download, it never reached the PC, and that if it was run, the PUA part was blocked from installing. That is one helper's view, not Microsoft's statement.
Check Protection history for the status, delete the installer and look in Installed apps for anything you did not choose. If you ran the installer, run a Full scan and the offline scan as well. A status of Failed means the action did not finish, so scan again.
Why did uTorrent.exe trigger PUA:Win32/ICBundler?
One reader reported it in February 2021 for a file named uTorrent.exe in his Downloads folder, with status Removed and only the Allow action offered. We cannot tell from the post whether that file was the real installer or a copy.
Installers that bundle extra software are a known source of this kind of alert, and the Microsoft forum helper said the detection looked like a bundling installer, possibly a torrent client. Download programs only from their makers' sites and choose Custom setup so extras can be declined.
Should I click Allow on device?
No, unless you have confirmed the file is something you want. Allow on device lets a detected file run, and our 2021 picture shows it next to Remove and Quarantine.
If you want the program, download it again from its maker's site, decline the extras in a Custom setup, and add an exclusion for one file only as a last step. Microsoft documents exclusions by file extension and folder location. Never exclude a whole folder such as Downloads to silence an alert.
Why does PUA:Win32/ICBundler keep coming back or say Failed?
A Failed status or a repeat alert usually means a copy of the installer is still on the PC, or a bundled program recreates it.
A 2022 reader's alert said the threat might not be fully restored. Delete every copy of the installer, empty the Recycle Bin, remove programs that arrived with it in Installed apps, restart and run a Full scan.
Then run the Microsoft Defender Offline scan. If a Temp folder holds the file, clear temporary files in Settings, System, Storage. A repeat alert does not prove an infection.
Do I need to buy anti-malware or a system tune-up tool?
No. Our 2021 guide told readers to buy a professional anti-malware tool and a system tune-up tool, and we have dropped that. Microsoft Defender raised the alert, can remove the item, and has a free offline scan.
A tune-up tool repairs nothing a PUA installer changed, and no source we read says otherwise. If you want a second scanner, pick one by its own tests, not because an alert recommends it. Spend the effort on checking Installed apps and your browser extensions.
Does it affect Chrome, Firefox, Edge or Mac?
The detection is for Windows files, not for a browser. Our 2021 guide said the adware mainly affects Chrome, Firefox and Edge, but the browser trouble comes from programs that were bundled with the installer, if any.
Check each browser's extensions and reset it only if you see ads, redirects or a changed start page. Mac and Safari are not covered: Win32 is a Windows label, and the Mac-style Flash windows in our old picture were an illustration, not a sample. Internet Explorer 11 was retired on 15 June 2022.
Will Fortect remove PUA:Win32/ICBundler?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For PUA:Win32/ICBundler, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Microsoft Security Intelligence: PUA:Win32/ICBundler threat description (read October 6, 2026)
- Microsoft Learn: Detect and block potentially unwanted applications (read October 6, 2026)
- Microsoft Learn: Run and review the results of a Microsoft Defender Offline scan (read October 6, 2026)
- Microsoft Q&A: Windows defender blocked but did not delete virus (November 2022) (read October 6, 2026)
- Windows 10 Forums: PUA:Win32/ICBundler out of nowhere from uTorrent.exe (23 February 2021) (read October 6, 2026)
- Adobe: Flash Player End of Life general information (read October 6, 2026)
- Microsoft Lifecycle: Internet Explorer 11 (read October 6, 2026)
- Reddit r/antivirus: Windows Defender is not deleting PUA:Win32/ICBundler (title and search excerpt only) (read October 6, 2026)