
Pushisback.com ads: what it is and how to remove it
Pushisback.com is the potentially unwanted program that manages to send advertisements directly to your screen with the help of pop-ups and banners, redirects and flashy images. This program is focused on generating views and visits on affiliated domains that lead to push notifications coming directly to your computer or phone screen.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Not sure what sends your browser to pushisback.com? An automatic scan looks at the usual sources for you.
Do it yourself · free Remove Pushisback.com ads yourself 3 steps, about 9 minutes, no software needed.
Start the steps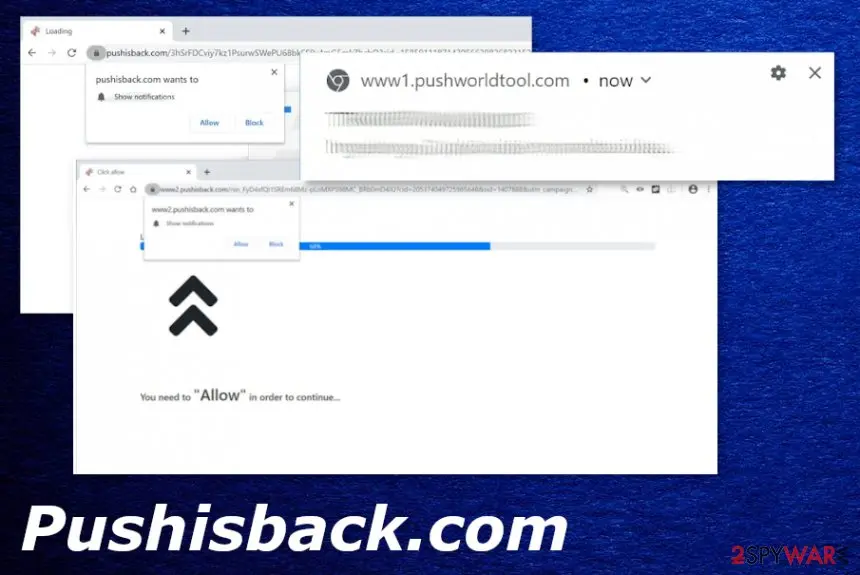
Pushisback.com ads: summary
| Distribution | Potentially unwanted programs can be installed by the user when freeware installations are not secure due to software bundling[3] methods or different techniques that involve deceptive material and misleading claims |
|---|---|
| Name | Pushisback.com |
| Type | Adware/ Redirect virus |
| Category | Potentially unwanted program[2] |
| Symptoms | The program can inject various advertisements and other commercial content on the web browsers, so there are more possibilities to redirect your online traffic to sponsored sites and domains filled with more shady advertisements that trigger the appearance of intrusive pop-ups, banners, and other material |
| Danger | The PUP can install applications directly on your machine and alter more settings, processes this way. when the user is exposed to possibly dangerous online content there is a huge possibility to install more severe cyber infections unknowingly |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Purpose | Adware-type intruders focus on delivering useless material to redirect online traffic to sponsored and otherwise related sites where the views and visits can be monetized |
|---|---|
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Evidence | 4 write-ups by security sites; details still limited |
| Domains | pushisback.com |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 20 April 2020 |
| Facts checked | 6 October 2026 |
Is Pushisback.com ads dangerous?
From our report of Apr 2020 · not reviewed since
Pushisback.com is the adware program that sends browser-based scam messages to trick you into visiting additional shady sites
Pushisback.com is the potentially unwanted program that manages to send advertisements directly to your screen with the help of pop-ups and banners, redirects and flashy images.
This program is focused on generating views and visits on affiliated domains that lead to push notifications coming directly to your computer or phone screen. There are tons of sites like this that show loads of questionable advertisements and redirects visitors to untrustworthy pages that also triggers unreliable ads and pop-ups of shady pages.
Visiting these sites can lead to the installation of the potentially unwanted program or more questionable material that leads to malware-laced sites where the installation of a computer virus is possible. You should avoid clicking on anything related to the domain and most importantly to get rid of the main PUP as soon as possible, so there are not many changes that can be done on your device.
Even though the main purpose and goal of the Pushisback.com virus are to generate pay-per-click revenue adware is the one that created all the frustration with your time spent online, and the PUP runs in the background and can alter particular settings to keep the persistence up and control additional features and processes.
These changes can significantly diminish not only your time online but damage the machine, so the sooner you delete this useless application, the better.
Pushisback.com is the redirect-based threat, so when you get exposed to this page there are many other windows and domains that appear not he screen after one click. These ad-supported sites all focus on getting your attention and views on the advertisements and pages.
Pushisback.com makes the user unwillingly visit these sites that display shady pages, and pop-ups lead to exposure to possibly malicious content. It opens tons of different pages, so there is a bigger opportunity to trick you into visiting pages and triggering particular scripts that allow downloads to happen. In most cases, ad-supported sites can inject adware and other PUP-type application on the system from visiting these domains only.
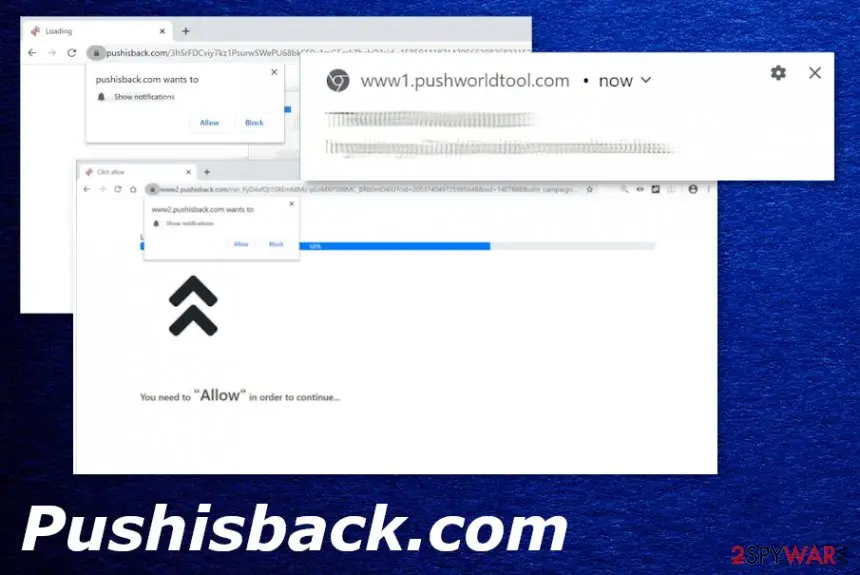
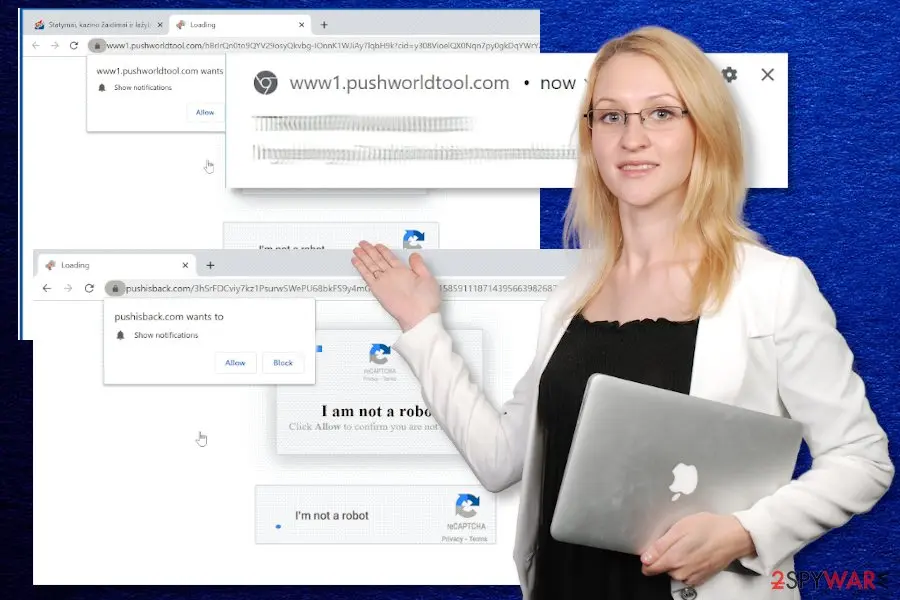
Pushisback.com as any other page that focuses on redirects and the push notifications, open pop-ups and displays the following message:
This is the reason to remove Pushisback.com as soon as possible. Even though these messages are common for legitimate sites and can appear on the browser all the time, you need to note that any interaction with such shady service and site that is related to malware creators can lead to really severe issues and malware.
You may agree to install a dangerous system tool or give permission to the attacker without even knowing or noticing when the screen is filled with all these pop-ups and banners.
Try to ignore messages and redirects that Pushisback.com PUP causes to avoid further damage and all the changes to the settings and performance of the device.Even though Pushisback.com is not considered to be malware or damaging to the system, there are many changes that PUP makes in the background without you noticing.
Since the infiltration is stealthily this intruder can also run for a long time until any symptoms are displays before your eyes. You cannot be sure how long the adware has been running on the PC.
Pushisback.com removal using anti-malware tools comes in handy, in such instances. Antivirus detection engines run the check on various places of the machine and can find, indicate, and remove any traces of the PUP infections and more severe viruses. You need to go for tools like this if you want to terminate the adware once and for all.
Also, remember that these browser-based threats can trigger changes in system settings and performance, processes related to registry and startup.
To ensure that Pushisback.com or any other PUPs are not running, you can manually go through Google Chrome, Mozilla Firefox, Internet Explorer and other web browsing tools. Any suspicious applications that you find can be deleted, and then all your browsing sessions should be secure. For full browser rest - follow the guide below.
From our report of Apr 2020 · not reviewed since
More from our earlier report on Pushisback.com
- You need to remove Pushisback.com as soon as you can, so the anti-malware tool can find all the programs and files related to the intruder and clean all of them off of the device
- To recover after the PUP infection, you should run the system tool like that can repair files and functions damaged or altered by the virus
- Pushisback.com wants to Show notifications You need to Allow in order to continue…
How Pushisback.com ads got into your browser
From our report of Apr 2020 · not reviewed since
The internet is not the safest place, especially when you are visiting pages with shady purposes and questionable content.
You cannot be sure that free download sites that promote and distribute freeware and applications or different content can be trusted. Misleading and advertisement-based domains are not reliable since the commercial content is intrusive, and the main purpose of the page is to collect views.
PUPs also get included in freeware installation setups when you download anything from torrent sites and similar services. If you go for recommended or quick options, you automatically get to agree to anything that is listed to get installed. Advanced or Custom options can help you to choose and deselect anything suspicious, but there is an issue of paying closer attention o these details.
You should always choose the reliable source of any program you install, even the browser application or the system app. This is the best way to keep the machine clear of any dangerous intruders. This and professionals anti-malware tools that can check for PUPs before any changes can get made.
Check your browser and PC
- Address:
pushisback.com
How to remove Pushisback.com ads
How to stop the Pushisback.com redirects
Work in this order and test a few links after each step, so you know which one was the cause.
Step 1: Check the browser's extensions
Redirects to
pushisback.comon sites that normally behave mean something in the browser is sending you there. In Chrome openchrome://extensions, in Edge edge://extensions, in Firefox the menu > Extensions and themes.Remove every extension you do not remember adding, especially new tab, search, coupon, PDF or video downloader add-ons. The extension pages look the same on Windows 11 and Windows 10.
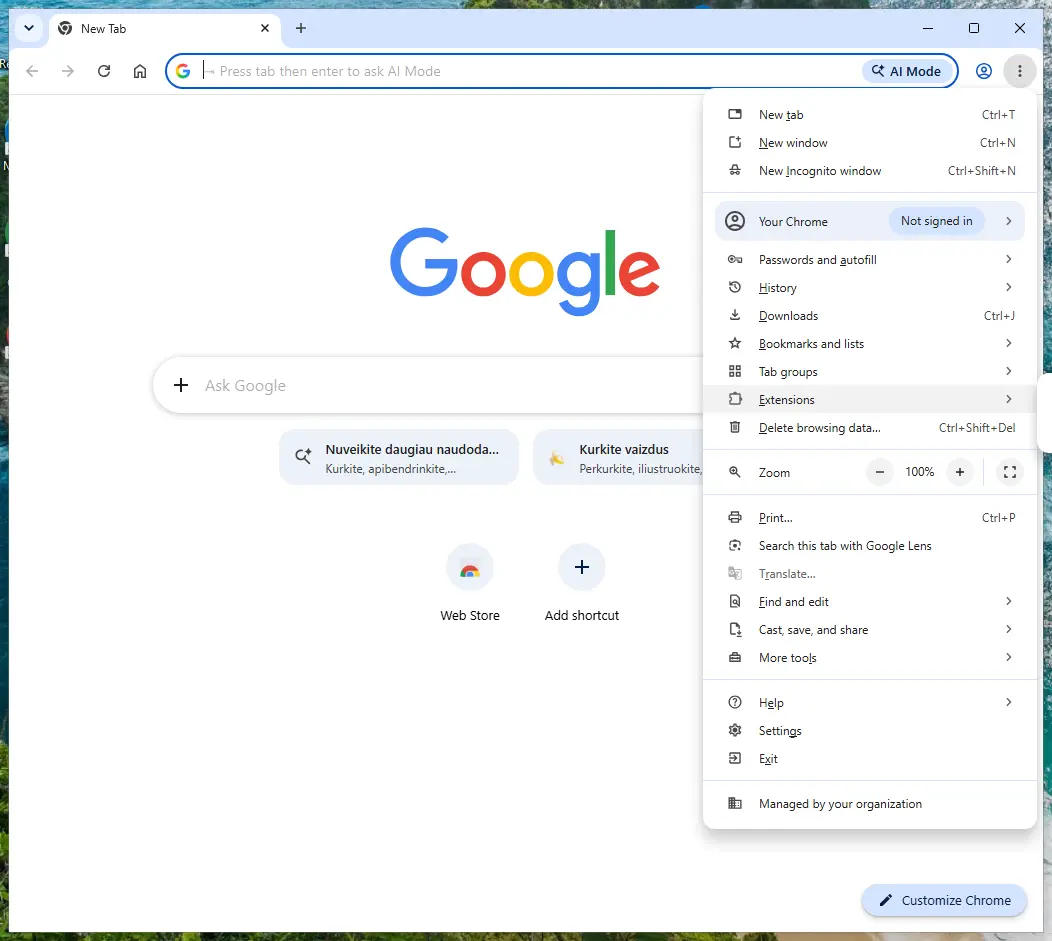
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Reset the browser if the redirects continue
If
pushisback.comstill opens after the extensions are gone, put the browser's settings back to their defaults. In Chrome open Settings > Reset settings > Restore settings to their original defaults; in Edge Settings > Reset settings; in Firefox Help > More troubleshooting information > Refresh Firefox.Tip: Bookmarks and saved passwords stay, while site permissions, the start page and the search engine are reset.
Redirects that survive a reset in every browser point to a program installed in Windows 11 or Windows 10, so uninstall anything you do not recognise in Settings > Apps > Installed apps.
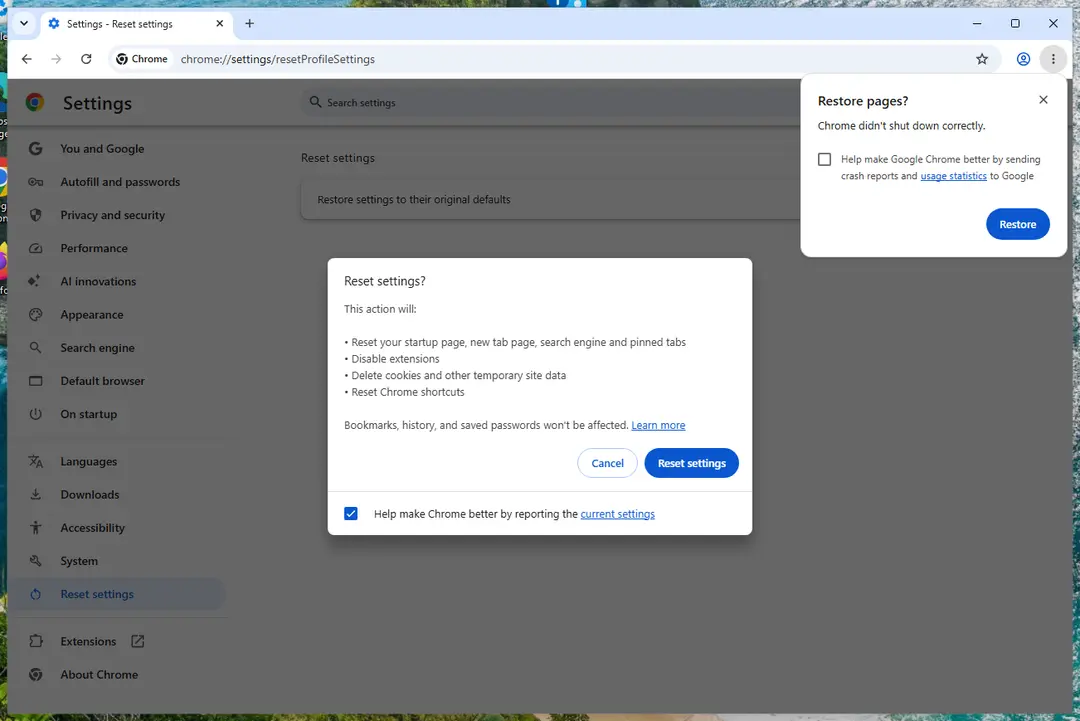
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 3: Scan the PC if you downloaded anything from the ads
If you only saw the notifications and clicked nothing, you can stop before this step. If a notification led you to download or run something, delete that file, then scan Windows.
In Windows Security > Virus & threat protection > Scan options, run a Full scan, then choose Microsoft Defender Antivirus (offline scan) and Scan now. The offline scan restarts the PC and takes about 15 minutes on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
You should get rid of the shady Pushisback.com program fro your machine
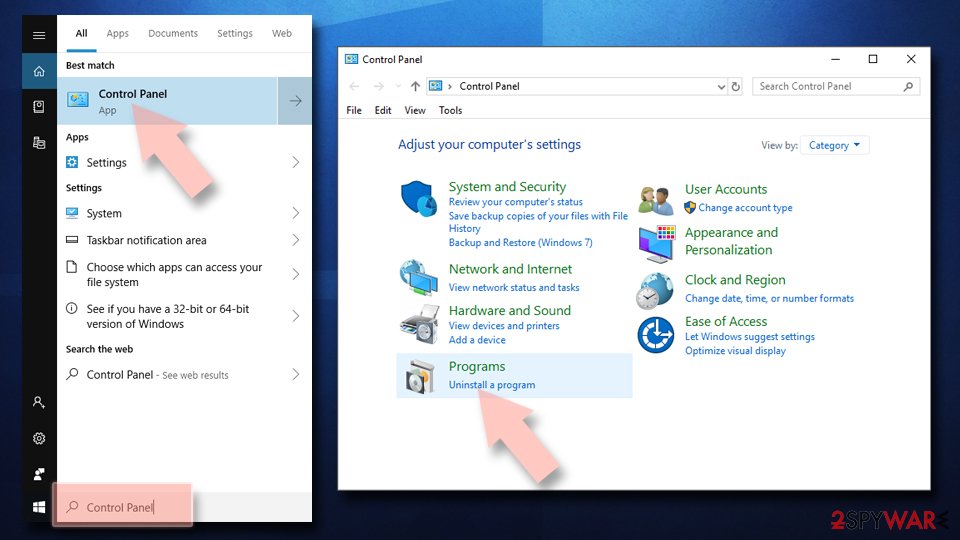
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
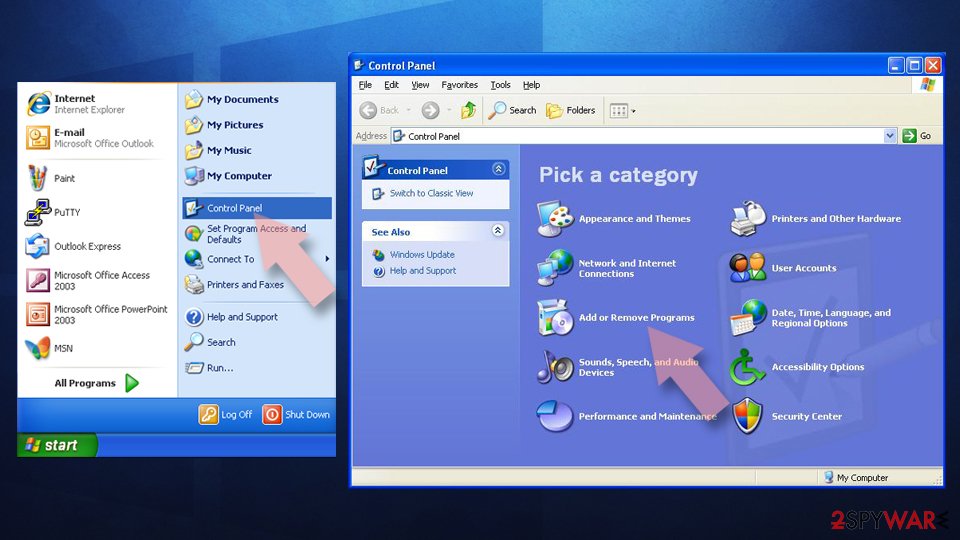
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
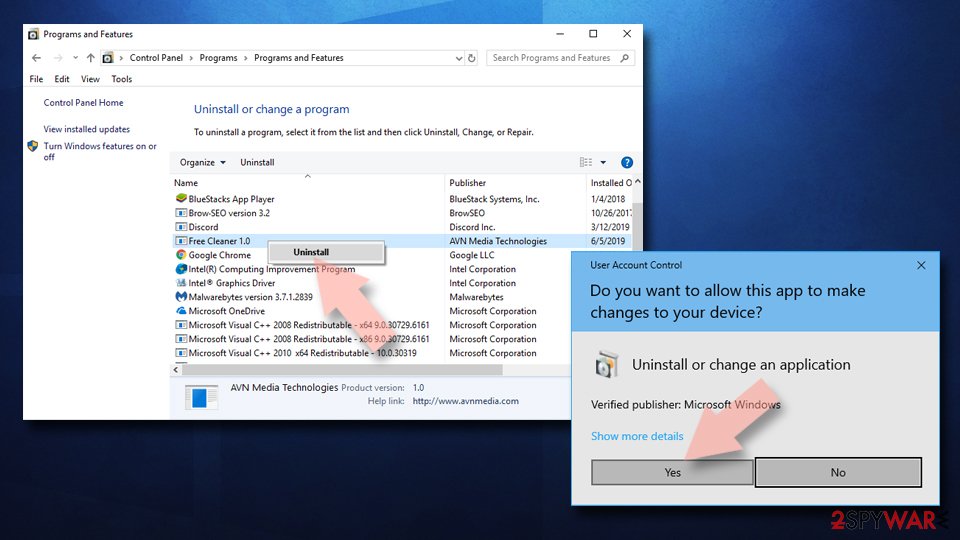
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
Clear all the suspicious extensions and applications from the browser yourself by resetting Chrome to default
Delete malicious extensions from Google Chrome:
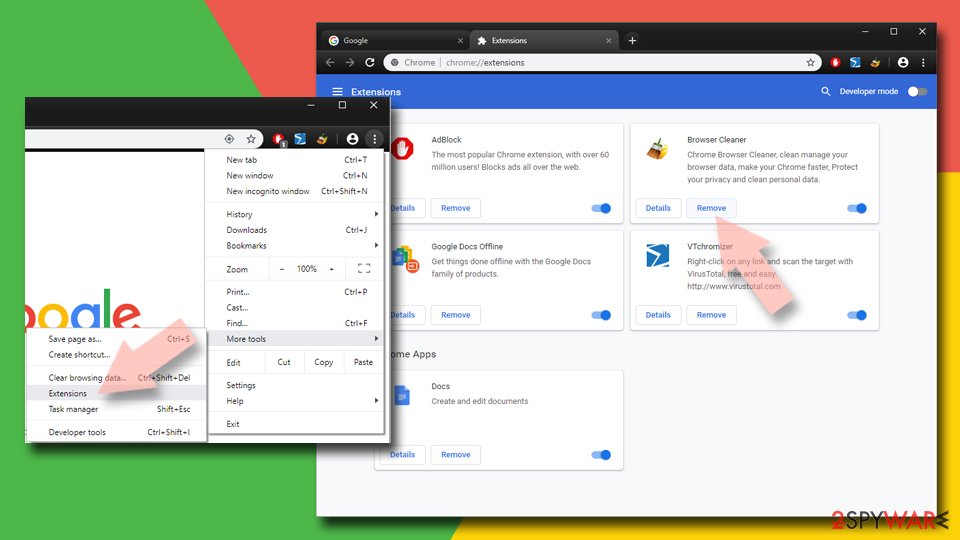
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
Clear cache and web data from Chrome:
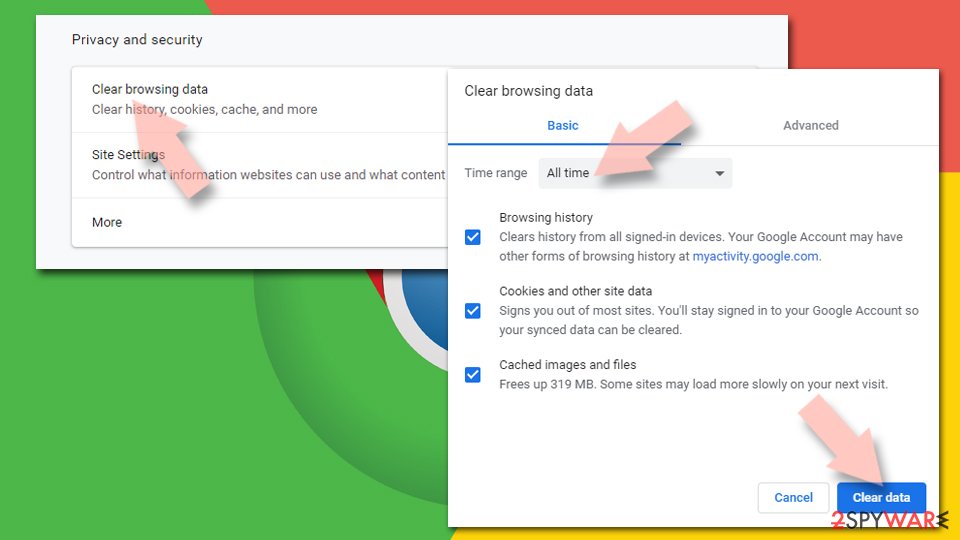
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
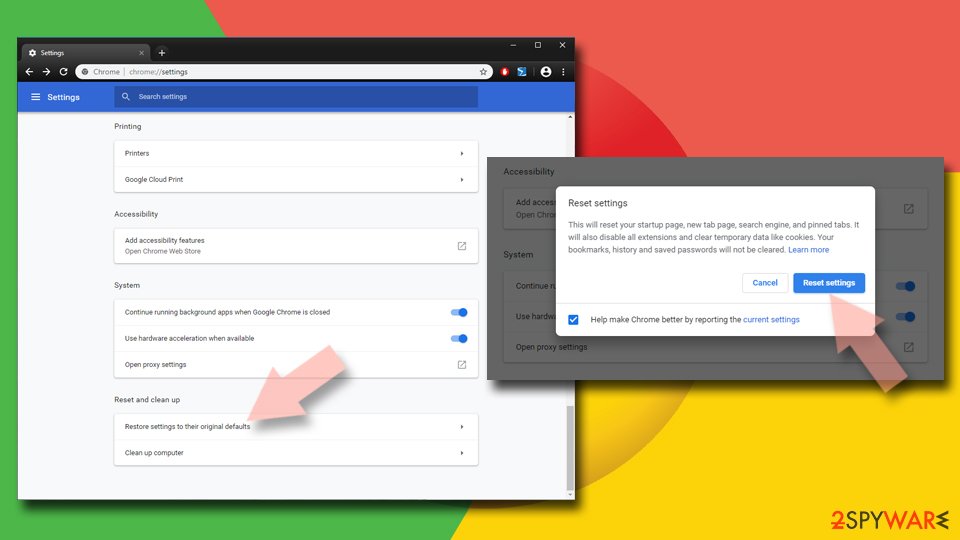
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
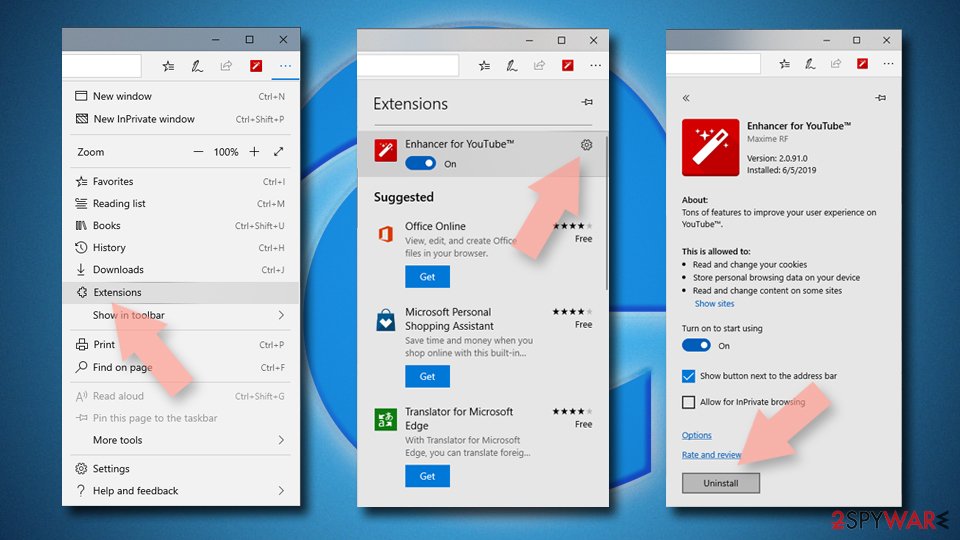
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
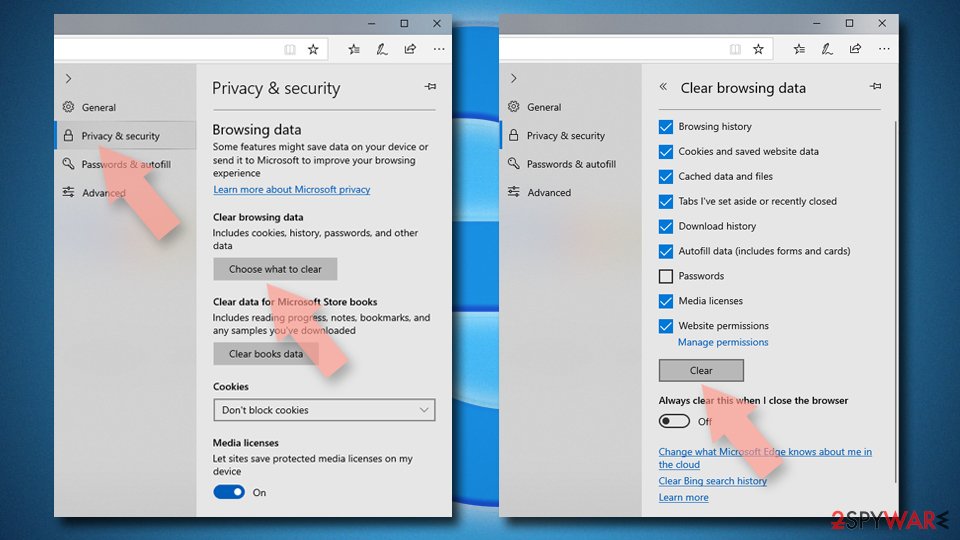
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
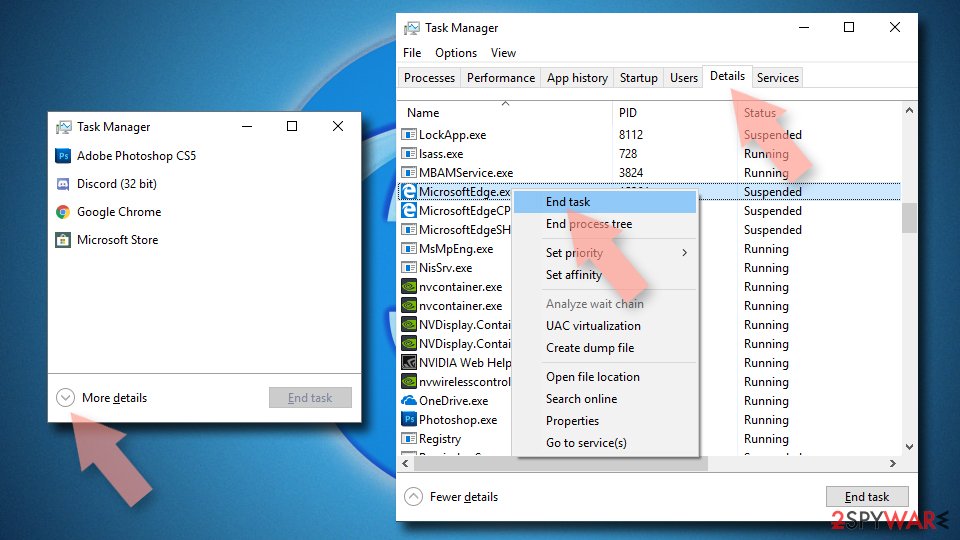
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
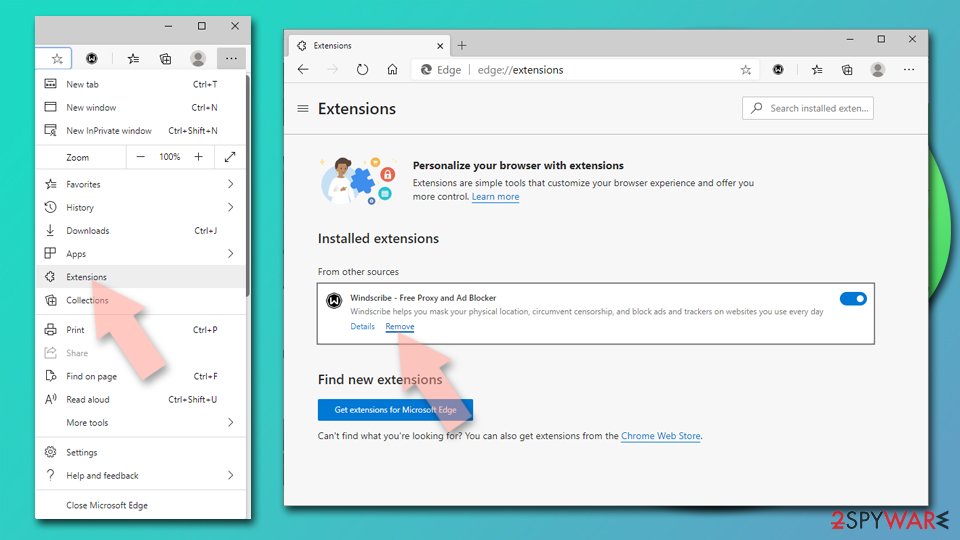
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
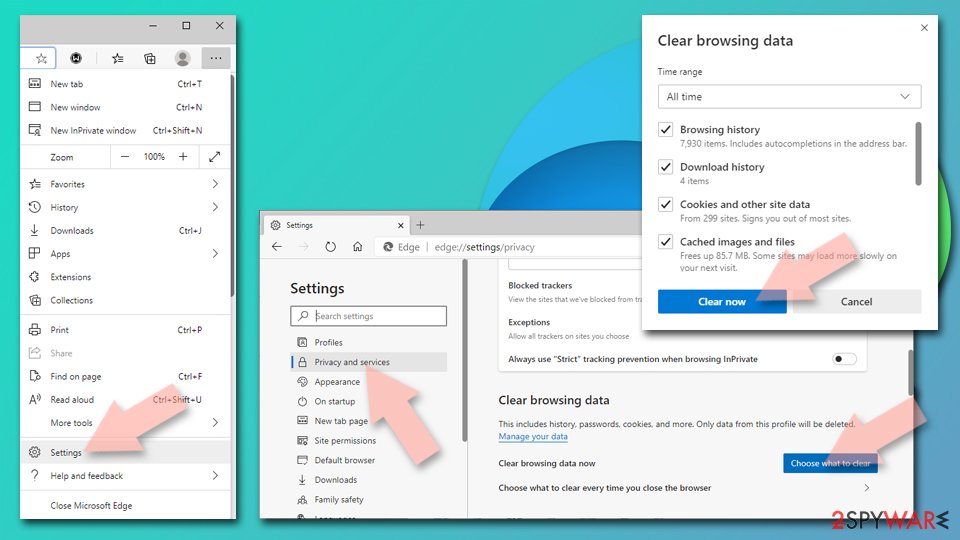
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
Reset Chromium-based MS Edge:
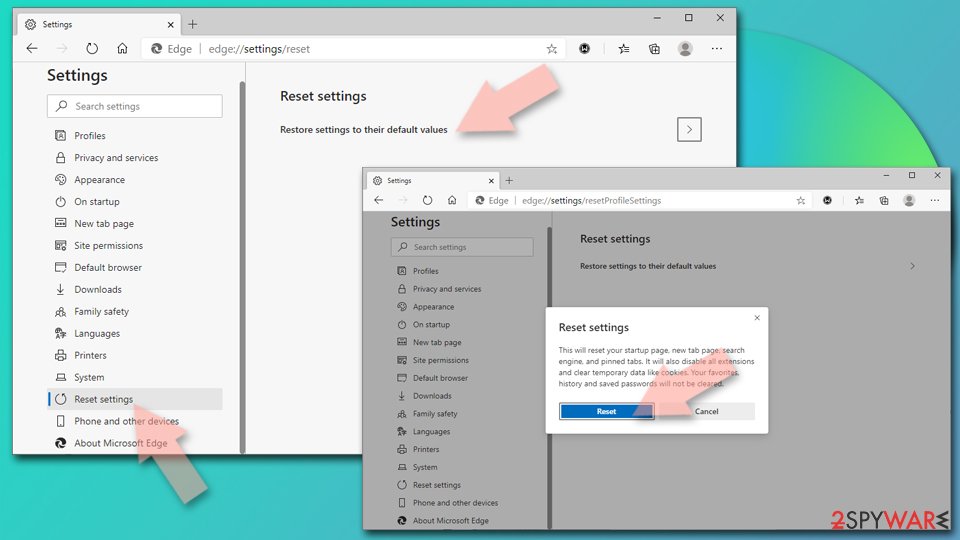
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
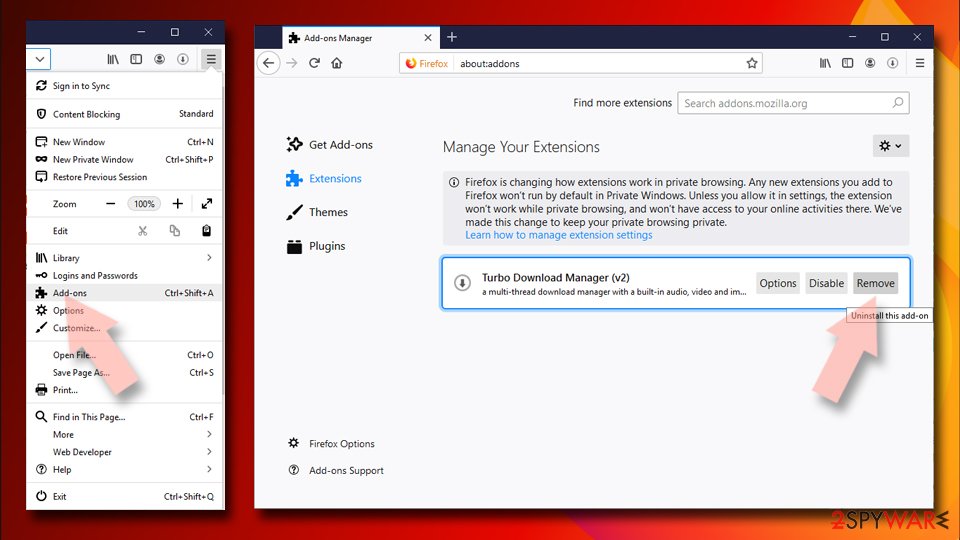
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
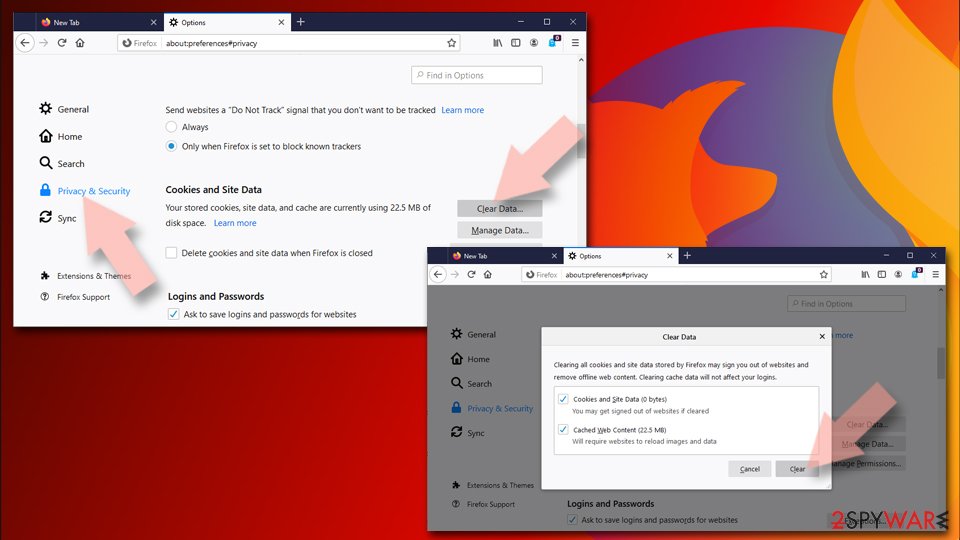
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
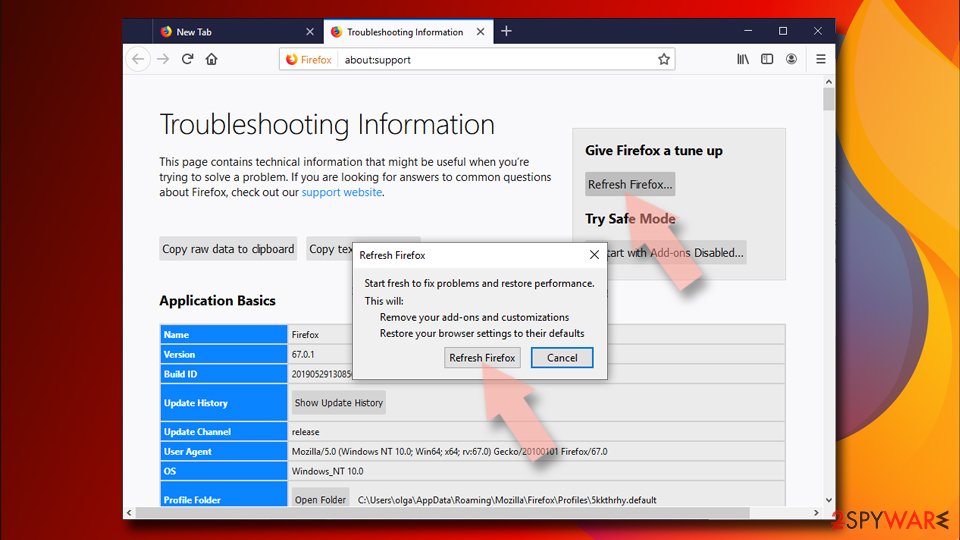
- Go to Help and then choose Troubleshooting Information.
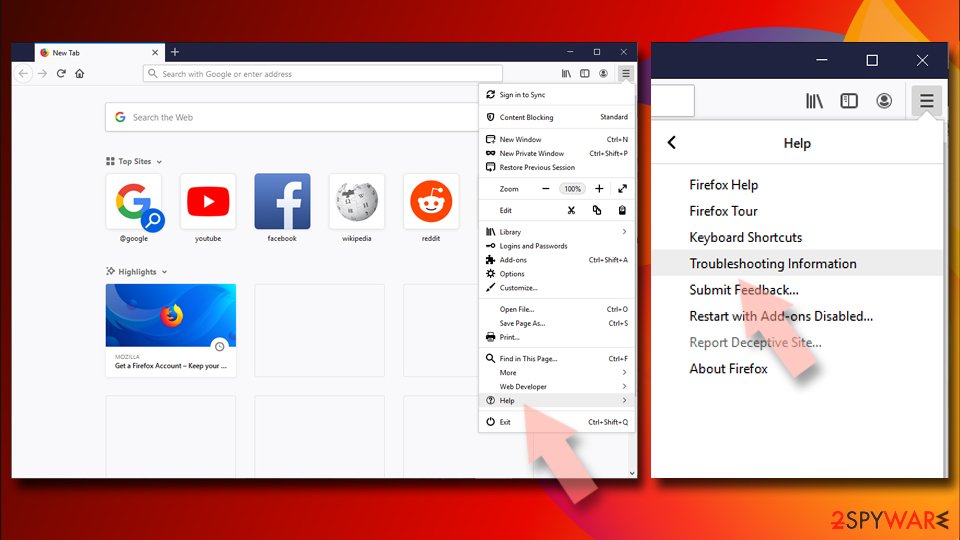
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
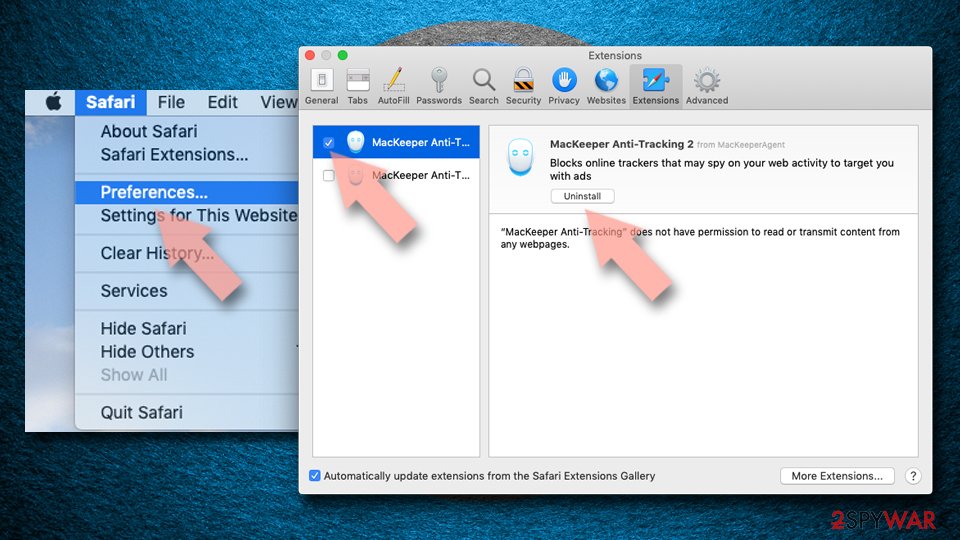
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
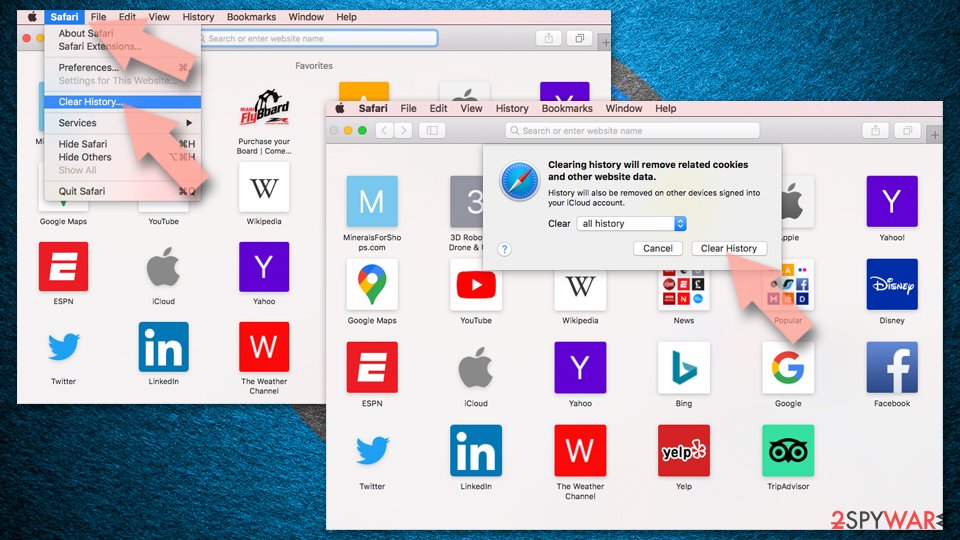
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
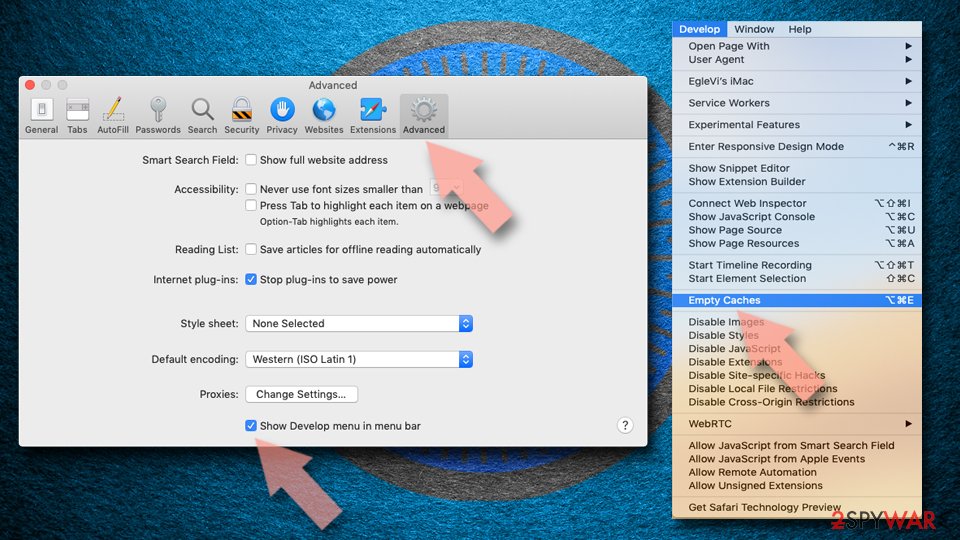
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
Pushisback.com may interfere with your system, so follow these steps to remove the adware fully
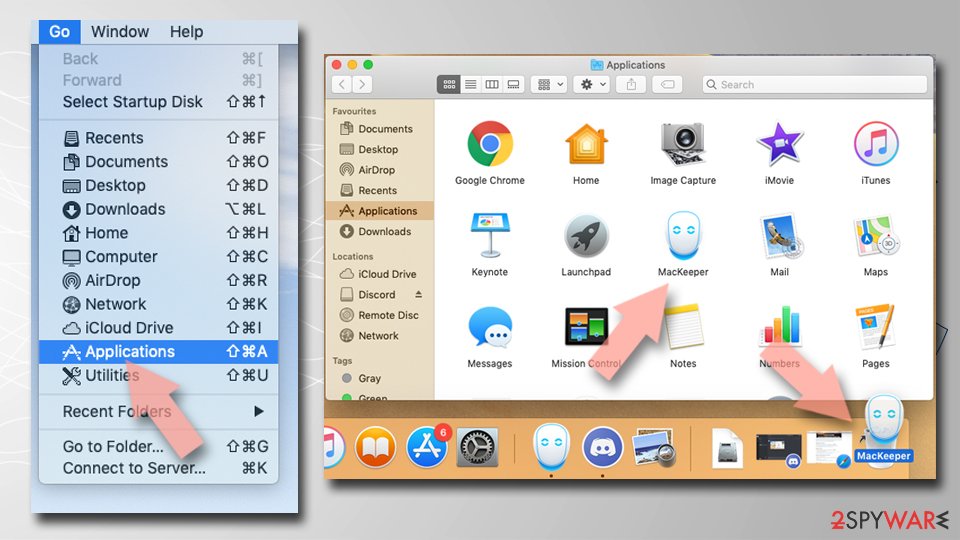
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
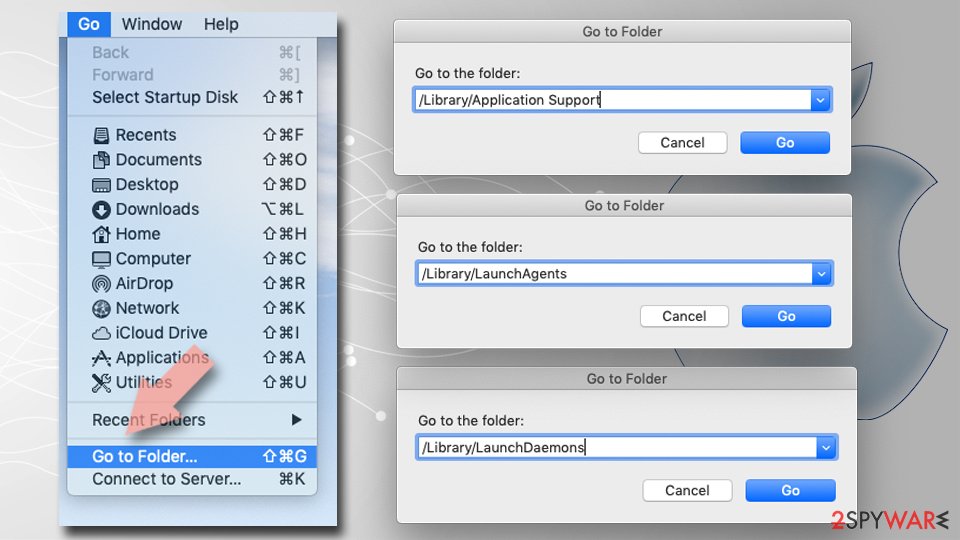
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
Remove dangerous add-ons:
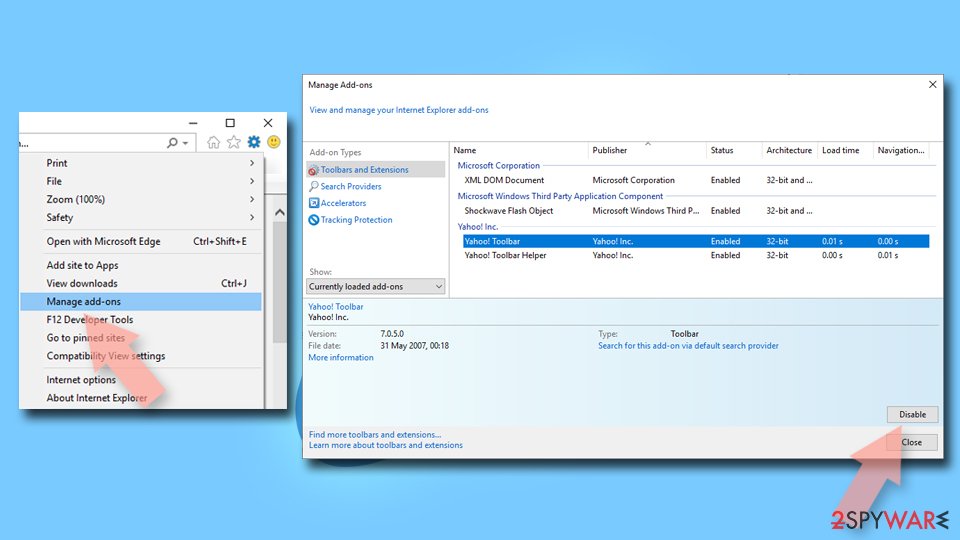
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
Change your homepage if it was altered:
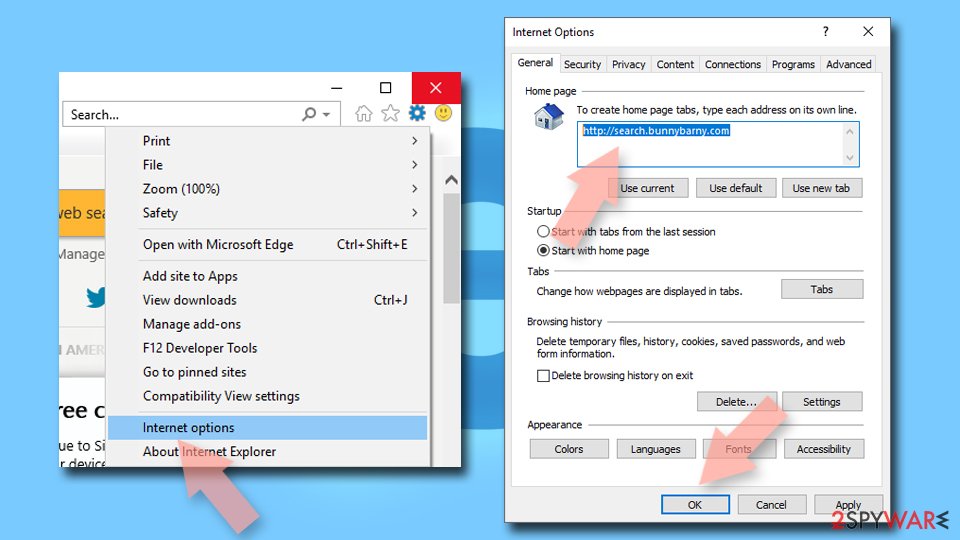
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
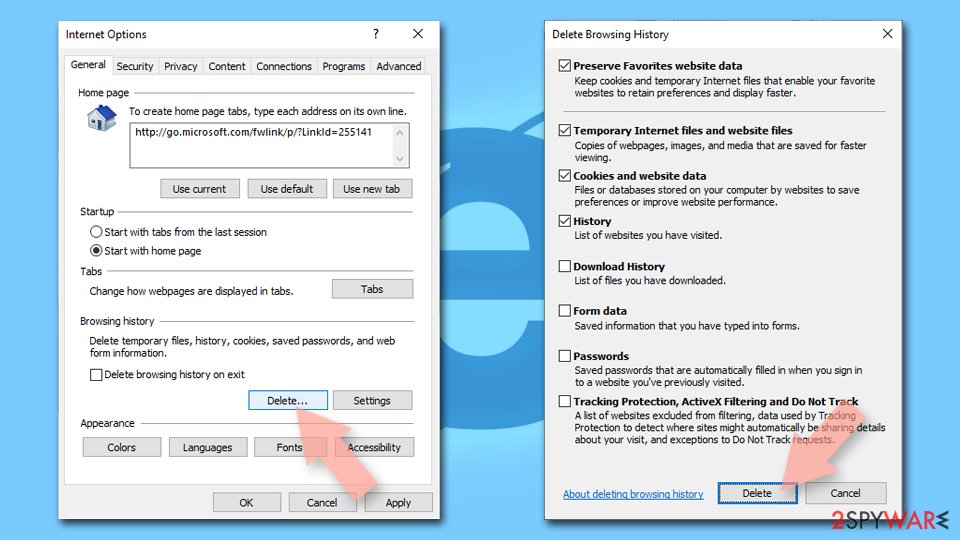
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
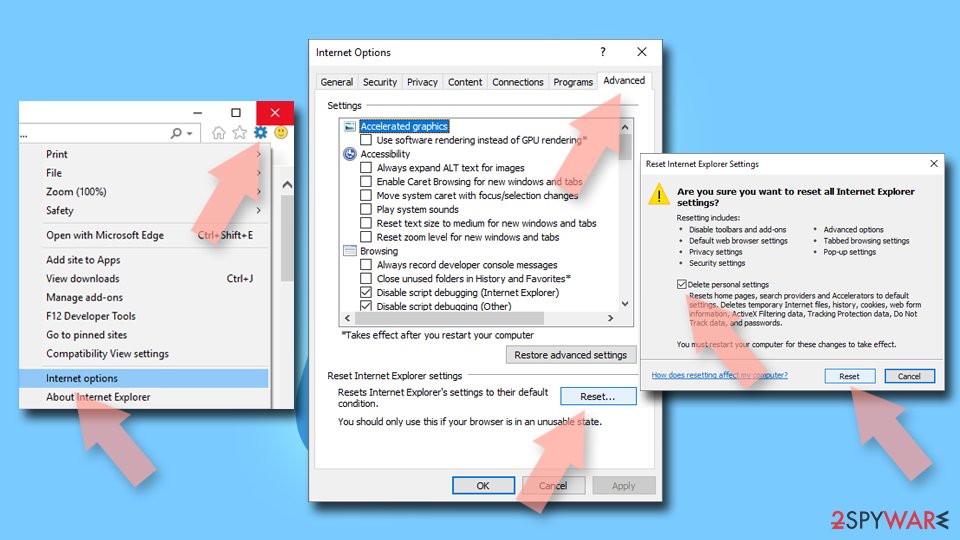
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
From our report of Apr 2020 · not reviewed since
Eliminate Pushisback.com adware to get the normal speed and performance back
Pushisback.com virus is nothing but a potentially unwanted program that manages to interfere with your online traffic, damage the performance of the computer or mobile device, and keep from accessing useful material online. Over time, this adware can even cause serious issues to the settings and affect much more than commercial material delivery.
You can try to remove Pushisback.com by exiting the website and closing the web browser. However, that is not enough to tackle the main intruder - the PUP. This cyber infection runs in the background and affects more than you think, so you need additional help to target all the activities and damage that this threat causes.
Pushisback.com removal can get quick and easy if you go straight to anti-malware tools and run the full system scan that can indicate all the possible intruders and clean the machine fully for you. Also, remember to check web browsers separately and remove any suspicious applications and addons. For that, follow the steps below.
Questions about Pushisback.com ads
Why does my browser keep going to pushisback.com?
Something is sending it there. On one site only, that site's ads are the cause and leaving the site ends it.
On many different sites, the usual causes are an extension you installed with something else, a site you once allowed to send notifications, or an ad-supported program in Windows that changes how the browser behaves. pushisback.com itself is only a stop on the way: it records the visit and forwards you to whatever advertiser pays most.
Check the extensions page, then the list of sites allowed to send notifications, then Installed apps sorted by date. Removing the cause stops the redirects; blocking the domain alone usually does not, because the network moves to a new one.
Is it safe that my browser was redirected to pushisback.com?
Landing on pushisback.com does not infect the PC by itself. A browser does not run programs from a page without your action. The danger is in the pages that come next:
- some ask you to allow notifications
- some show fake virus warnings
- some offer downloads
- ask for card details
If you only saw those pages and closed them, nothing more is needed than removing whatever caused the redirect. If you allowed notifications, remove that permission.
If you downloaded a file, delete it unopened, or uninstall it if you ran it. If you typed a password or card number on one of the pages, change the password and call your bank.
Why does Pushisback.com show me ads?
Because that is its whole purpose. Pushisback.com is an ad redirect domain, and its operators are paid for every ad it displays and every click it gets. In this case the ads take the form of redirects through ad pages.
They are chosen by ad networks that accept almost any advertiser, which is why so many look like warnings or prizes. The ads are not a sign that your PC is broken or infected with something worse; they are a sign that something on it, or in the browser, has permission to advertise. Removing that permission or program stops them.
Is pushisback.com safe to visit?
No. The site pushisback.com exists to push visitors towards ads, and the pages it leads to include fake virus warnings, fake updates, prize scams and notification prompts. Visiting it once does not infect an up-to-date PC, but anything you click or download there is a gamble.
Do not enter personal details, do not allow notifications and do not call phone numbers it shows. If it opens by itself, close the tab and check the browser's extensions and notification permissions. Blocking the single domain helps little, because the operators register new names regularly.
Do I have to clean every browser?
Yes, if you use more than one. We saw Pushisback.com in Chrome, Edge and Firefox, and each browser keeps its own extensions, notification permissions and settings. Chrome and Edge share the same extension format, so one installer can add the same adware to both, while Firefox has its own add-ons.
Check every browser on the PC, including ones you rarely open. If you sync a browser with an account, clean it while signed in, so that the removal reaches your other computers rather than the adware returning from them.
How do I know the ads come from Pushisback.com?
Look for redirects to pushisback.com. That is the trace Pushisback.com leaves, and it shows up as redirects through ad pages. Ads that appear on every site, including ones that never carried ads before, point to something on your PC or in the browser rather than to the sites themselves.
A quick test is a private window, where extensions are off by default: if the ads disappear there, an extension is responsible. If they appear even with the browser closed, the source is a notification permission or a program in Windows.
Can adware slow down my PC?
Yes. Adware runs in the background, loads ad scripts, opens extra tabs and contacts its servers, all of which use processor time, memory and bandwidth. Ad-heavy extensions also slow down every page, because they inspect and change it before you see it.
The effect is strongest on older PCs and when several adware programs arrived together. After removal, restart the PC and check Task Manager for anything still using a lot of resources that you do not recognise. Speed usually returns to normal once the ads stop.
An ad showed a phone number and I called it. What now?
The number belongs to scammers, not to Microsoft or an antivirus company. If you only talked, hang up and do not call back. If you let them connect to the PC, disconnect it from the internet, uninstall the remote access program they used, such as AnyDesk, TeamViewer, ScreenConnect or UltraViewer, and run a full and offline scan.
If you paid or gave bank details, call your bank at once on the number printed on your card. Change any passwords you typed while they were connected, and report the call.
I clicked on one of the ads. Am I infected?
Probably not. Clicking an ad usually only opens a page, and a page cannot install programs on an up-to-date Windows PC without your help.
You are at risk only if you then downloaded and ran a file, allowed notifications, entered card or login details, or called a phone number shown on the page. Delete any download and run a full and offline scan.
Change passwords you typed, from a clean device. Call your bank if you gave card details. If you called a number or allowed remote access, see the next question.
Will Fortect remove Pushisback.com?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Pushisback.com, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: Pay-per-click (read October 6, 2026)
- TechTarget: PUP (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)