
s3.amazonaws.com ads: what it is and how to remove it
Redirects to fake s3.amazonaws.com pages display deceptive update prompts to distribute malware. Clicking these prompts downloads trojans, ransomware, or other dangerous threats instead of legitimate software.
Facts checked October 10, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Not sure what sends your browser to s3.amazonaws.com? An automatic scan looks at the usual sources for you.
Do it yourself · free Remove s3.amazonaws.com ads yourself 4 steps, about 12 minutes, no software needed.
Start the steps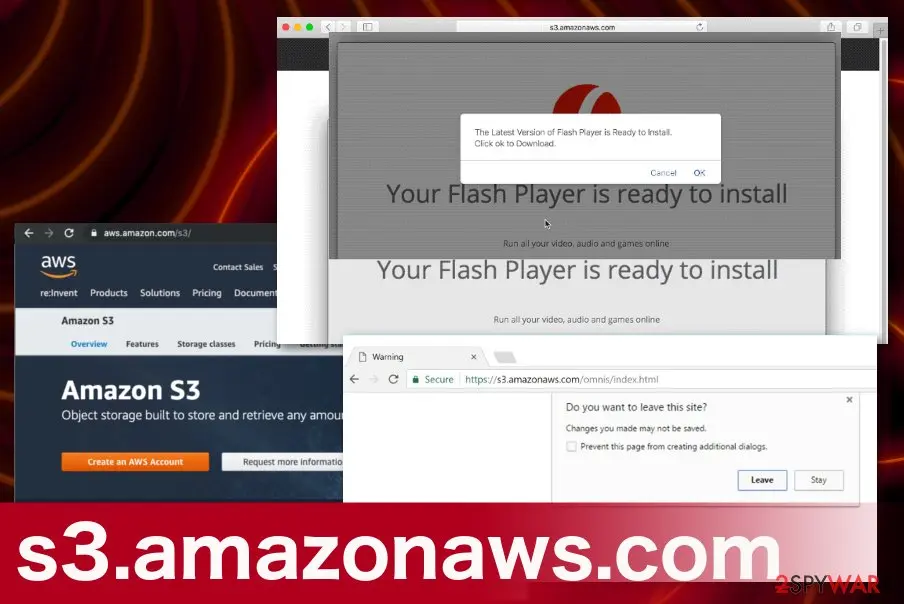
S3.amazonaws.com ads: summary
| Distribution | Deceptive pages, pop-ups with advertisements, redirects to dubious online services, commercial material. Freeware installations can lead to PUP infiltrations that later on trigger such redirects to scammy sites |
|---|---|
| Name | s3.amazonaws.com |
| Type | Adware/ Scam |
| Tactics | Deliver update messages, encourage people to install the needed software and deliver PUPs this way |
| Symptoms | Promotional content shows up on the screen, and fake software updater manages to download malicious programs or infect the machine directly with harmful threats |
| Main danger | Scam delivers malware with various purposes and can lead to serious privacy and security issues |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Evidence | 6 write-ups by security sites; details still limited |
| Domains | s3.amazonaws.com |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 5 May 2021 |
| Facts checked | 5 October 2026 |
s3.amazonaws.com in 2026: what we found
We opened s3.amazonaws.com in a clean desktop Chrome browser on 4 October 2026 and clicked nothing. This is one visit from one location: ad pages often behave differently on a second visit, in another country, on a phone or after a click, and many hide from automated browsers, so a quiet result is not proof that the page is clean.
s3.amazonaws.com · desktop Chrome · 4 October 2026
- Notification requestNone on this one visit.
- Pop-ups and new tabsNone on this one visit.
- Where it ledIt forwarded our browser to
aws.amazon.com. - Ad networksGoogle Ad Manager only.
- Page title"Cloud Object Storage – Amazon S3 – Amazon Web Services"
Use with care Nothing was forced on us, but the page works with ad networks or sends visitors elsewhere; they change what they show by country, device and time.
What s3.amazonaws.com/mathvc, schoolsucks, vcsa-sux, fernisbest and bullguardian pages are
Addresses like s3.amazonaws.com/mathvc/index.html or s3.amazonaws.com/schoolsucks/index.html are pages stored in Amazon S3 buckets, not pages made by Amazon.
The vcsa-sux and fernisbest pages follow the same pattern. Amazon's documentation calls this a path-style URL. The first part after the slash is the bucket name, chosen by whoever created the bucket. Searches without the dot or the .com ending point to the same pages.
We found no reliable source for these four buckets. In our reading, names like schoolsucks or vcsa-sux suggest pages that students share, often game or proxy pages meant to get around school filters. That is not confirmed.
Anyone with an AWS account can publish such a page, and its owner can change it at any time. Do not enter passwords there or allow notifications. Never run a file such a page downloads.
bullguardian.s3.amazonaws.com/index.html uses the other address form, which Amazon calls virtual-hosted style. The bucket name bullguardian comes before s3.amazonaws.com. The name resembles a security brand, but we found no source linking this bucket to any security company. In our reading, a security name on an S3 page is a warning sign, because fake scan and fake update pages, like the ones this guide describes, borrow trusted names.
s3.amozonaws.com is a misspelling of s3.amazonaws.com. The real Amazon storage addresses always end in amazonaws.com. To check any such name yourself, read the bucket name in the address and ask who made it.
Amazon hosts the file but does not write it, so the bucket owner decides what you see. If a page shows an alert or asks you to install something, close the tab and scan your PC.
What the s3.amazonaws.com ads ads look like
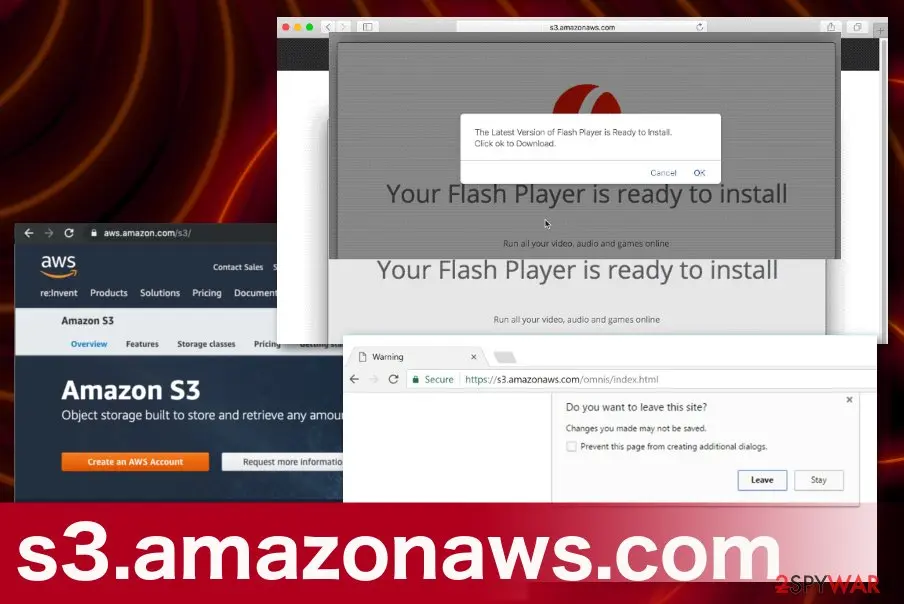
The Latest Version of Flash Player is Ready to Install.
Is s3.amazonaws.com ads dangerous?
s3.amazonaws.com: what changed since our report
May 2021
Our first report
We described s3.amazonaws.com on 5 May 2021 and updated the report on 17 June 2021.
October 2026
Our new check
We opened the address again in a clean browser; the results are above.
From our report of May 2021 · outdated details corrected in October 2026
s3.amazonaws.com is the website that shows pop-ups with false claims about outdated software to load malicious programs on the PC
S3.amazonaws.com is the site claiming about updates and needed installations with the purpose of tricking people into allowing potentially unwanted programs.
The domain is hosted by Amazon AWS that is a legitimate service and intended to provide IT resources for users even though it gets misused by malicious actors with shady goals. Redirects and revenue generation is the main purpose of such adware-type intruders and pages that promote infections with alleged browser or codec updates.
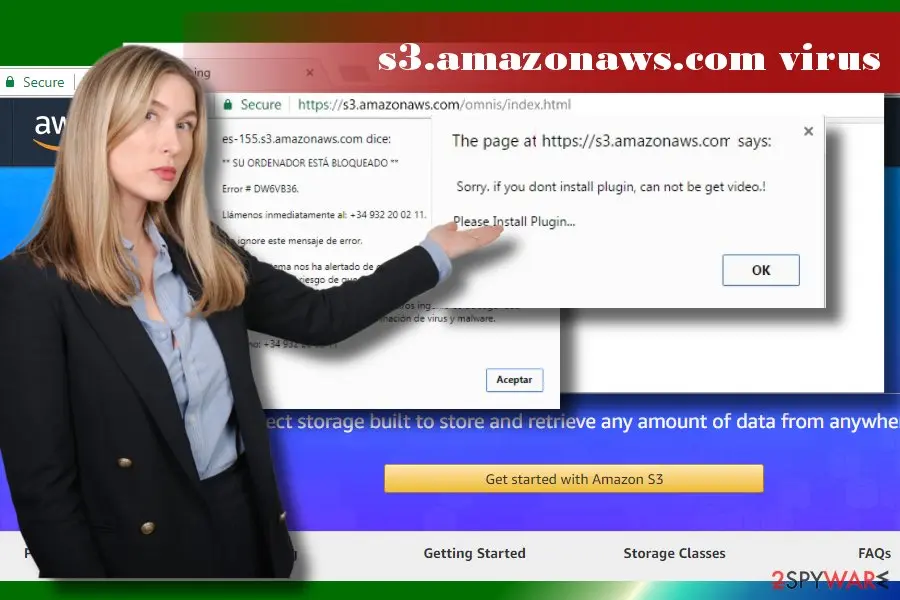
Users who encounter these intrusive redirects can also get exposed to other advertisements, PUP distribution pages, and websites containing malicious scripts or even triggers malware infiltration. This page delivers pop-ups about the prepared installation, and users only need to click the OK button to download the said update.
Unfortunately, the process is not related to Adobe or another software developer - the background process is leading to cyber infection, and audio or video software is nor installed nor updated during such process. By allowing the alleged update, you agree to install malicious content onto the system that can differ from potentially unwanted programs, in-browser intruders to really dangerous trojans, or malware.
S3.amazonaws.com is a misleading domain, which has been reported for hijacking web browser's new tab URL and causing frequent web browsers redirects to Amazonaws related websites and malicious online services. It works as an advertising platform and may be used for promoting expensive items, useless services, or even malware.
However, unexpected pop-ups should not be ignored. Original Amazon aws S3 or Amazon Web Service (AWS) is not malicious. It's a legitimate cloud storage web service that belongs to Amazon Inc.
Many people prefer using this service due to the multiplicity of functions and fair pricing. Nonetheless, cybersecurity experts warn that cybercriminals might misuse the the services for malicious activities, such as scam or malware dissemination.
The scam pop-ups state:
Mainly, virus is dubbed as adware and potentially unwanted program (PUP) because misleading pop-ups usually start emerging soon after the installation of freeware. According to people who encountered this problem, they started seeing https://s3.amazonaws.com/addns/CH3088/CvCHff.html as a default new tab URL on Google Chrome and Mozilla Firefox. Mac users also encounter these pop-ups on their Safari browsers, so there is no exclusion to a particular OS.
In some of the cases, this doubtful URL is replaced by www.adfactorytech.com/resources/Re/Chnh/mov.php domain, which redirects to third-party search domains. In addition to that, people may also see the following status at the top-left corner of the web browser's window when trying to access any website:
Usually, the content provided on the ads is rather professional-looking. Interestingly, most of the promoted things may match your web browsing history, so if you have recently searched for some makeup, shoes, vacation offers, etc. virus can display your appealing offers. That's because this dubious adware-related program may employ tracking cookies and accumulate browsing-related data, including search queries, websites visited, IP address, geographical location, email address, and so on.
Note that some of the ads can be dangerous. According to cybersecurity researchers, criminals found out a way to exploit publicly-readable and publicly-writeable servers and misuse it for disseminating malware or even ransomware. Thus, if you keep receiving an excessive amount of pop-up and new tab ads, our recommendation would be to remove adware from the system.
Removal can be initiated in two ways – manual and automatic. The latter method is time-saving and more reliable. To initiate it, you have to employ a reputable anti-malware and run a full system check to terminate anything suspicious.
Also, system tools like might provide the needed help for file issues caused by background processes and changes in the registry or startup settings. If nevertheless, you opt for manual removal, you can follow the steps provided at the end of this article.
Trusting such sites with claims about updating required or suspicious installations can lead to more issues than you think. Installing third-party updaters leads to system infiltration and issues with the safety of your PC. Such scammy pages ca even deliver pop-up messages with details about malware infiltration.
All these claims are false and note that Apple, Microsoft, or any other OS or software provider don't show such messages through web browsers. The fake updater delivered via random redirects is included in the database of many AV tools for a reason.
- Waiting for S3.amazonaws.com
- Connected to S3.amazonaws.com
- Looking up S3.amazonaws.com
From our report of May 2021 · not reviewed since
More from our earlier report on s3.amazonaws.com
- Getting a proper anti-malware tool can make a huge difference in PUP removal because AV tools can find various malicious files and delete them what improves the general performance of the machine
- There are many background processes this intruder may run on the machine once it gets infected, so you should additionally check your device with a PC repair or cleaner tool like that may find and fix affected or even corrupted registry entries, system files
- Your Flash Player is ready to install Run all your video, audio and games online Update the latest version for optimal performance Install
How s3.amazonaws.com ads got into your browser
From our report of May 2021 · not reviewed since
Cybersecurity experts warn people that PUPs like adware and browser hijackers can be distributed via software bundling.
Freeware developers agree to attach free add-ons, toolbars, plug-ins, and extensions for monetization purposes.
The problem is not such a distribution method, technically known as bundling, but the way freeware developers disclose them. Usually, additional installers are hidden under Quick or Basic installation methods. If the user selects this method, he or she unintentionally agree to install all of them. As a consequence, the web browser may be hijacked and start initiating various unwanted activities.
According to NoVirus.co team, the only way to prevent malware from installing onto your PC, you have to install free programs this way:
Additionally, you should avoid browsing on suspicious websites. Hackers can inject malicious codes into websites and misuse them for malware distribution.
- Select freeware download source carefully;
- Then opt for Advanced or Custom installation method;
- Read License Terms;
- Remove checkmarks from additional components;
- Then finish the installation and check if the freeware did not drop malware. You can do that by opening Control Panel, sorting programs by date and look for unknown programs installed recently.
Check your browser and PC
- Address:
s3.amazonaws.com
How to remove s3.amazonaws.com ads
How to remove the s3.amazonaws.com extension
Do the browser steps in every browser and profile on the PC, then check Windows for the program that installed the extension.
Step 1: Remove extensions you did not add
S3.amazonaws.com often works through an extension, so go through the extension list of each browser:
chrome://extensionsedge://extensions- Extensions and themes in Firefox
Switch suspicious extensions off one at a time and reload the page where the problem shows, then remove the one that stops it, and any other you did not add.
Remember the other browsers and profiles on the PC. If Remove is missing or greyed out, a policy forces the extension, which the policy step deals with. Windows 11 and Windows 10 show the same pages.
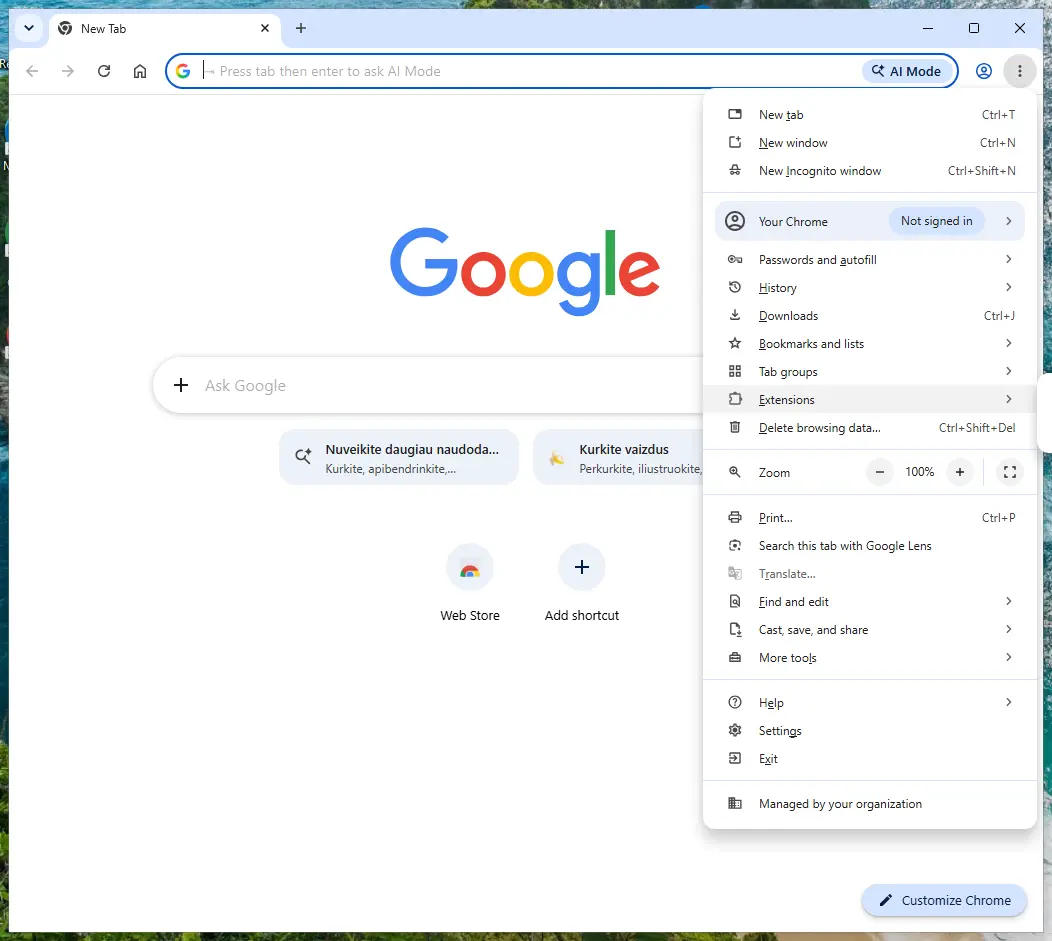
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Uninstall programs you did not mean to install
Open Settings > Apps > Installed apps in Windows 11, or Settings > Apps > Apps & features in Windows 10, and sort the list by install date. Look at what appeared around the day the problem started and uninstall every program you do not recognise or did not choose.
Free converters, PDF and video tools, "system optimizers" and unknown browsers are the usual carriers of s3.amazonaws.com. If a name is unclear, search for it before you remove it, so you do not uninstall a driver or a Windows component.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 3: Reset the browser
Finish the browser part with a reset, which puts the search engine, start page, new tab page and site permissions back to their defaults and switches extensions off. Chrome: Settings > Reset settings > Restore settings to their original defaults.
Edge: Settings > Reset settings. Firefox: Help > More troubleshooting information > Refresh Firefox, which also removes its extensions. Your bookmarks and saved passwords are kept, and the menus are the same on Windows 11 and Windows 10.
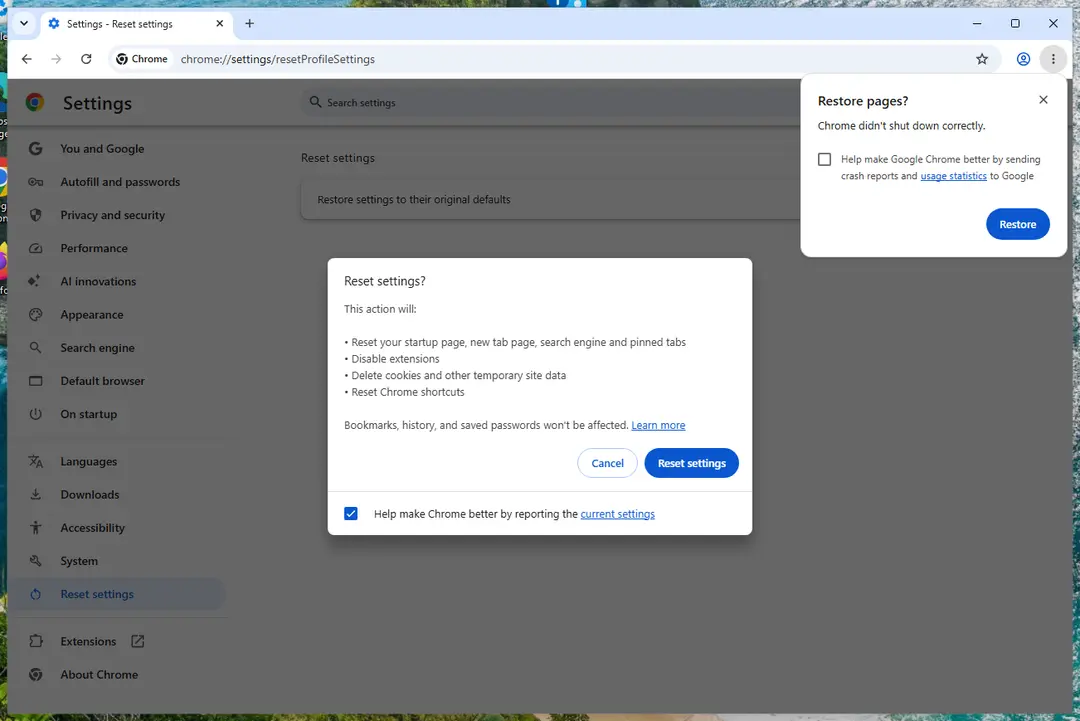
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
Get rid of pop-up from Windows without delay. The following instructions will help you to do so easily:
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
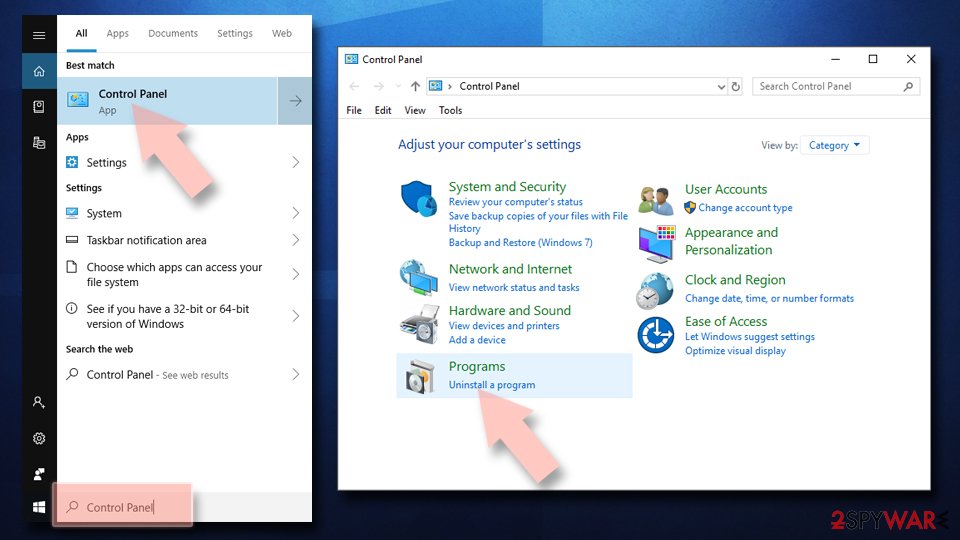
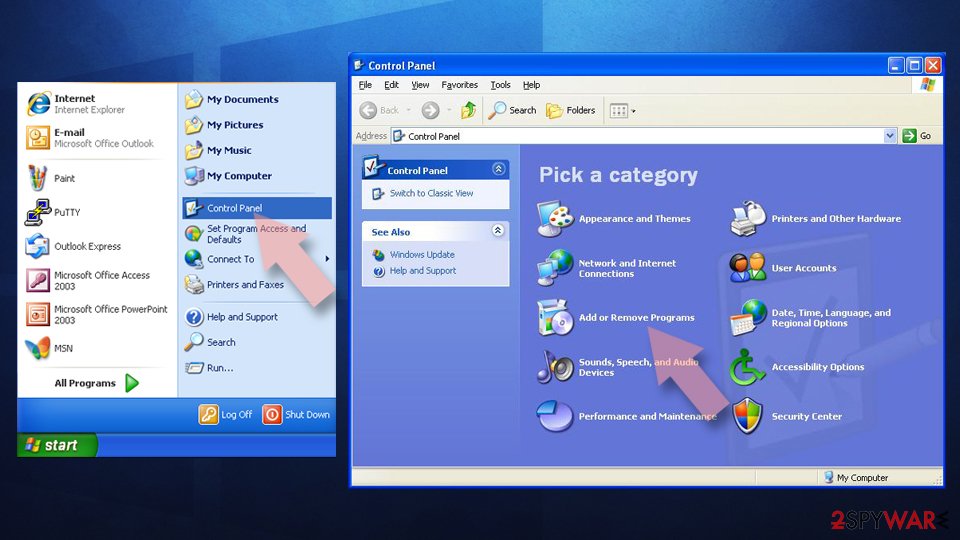
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
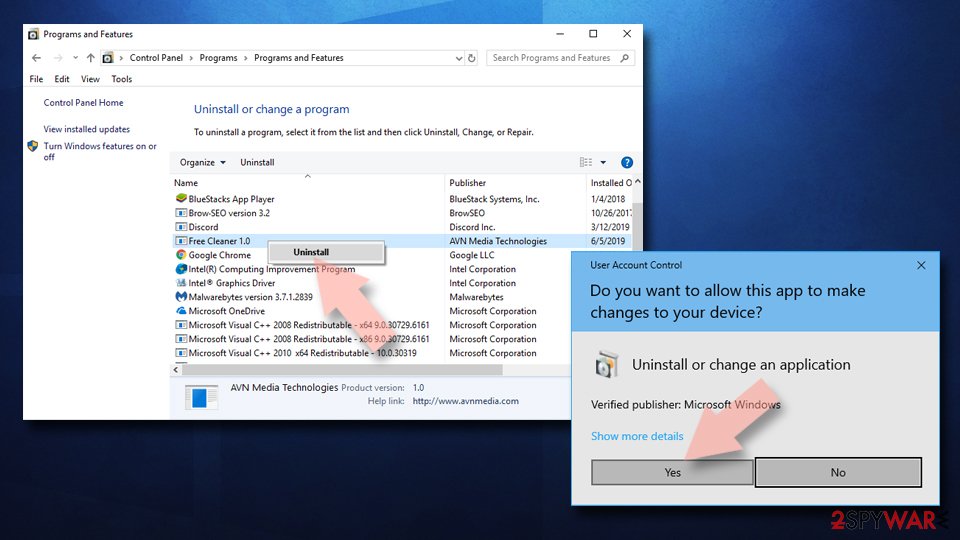
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
One you delete malware, please follow these steps to reset Google Chrome's settings:
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Uninstall adware-related entries from Mozilla Firefox by following these steps:
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
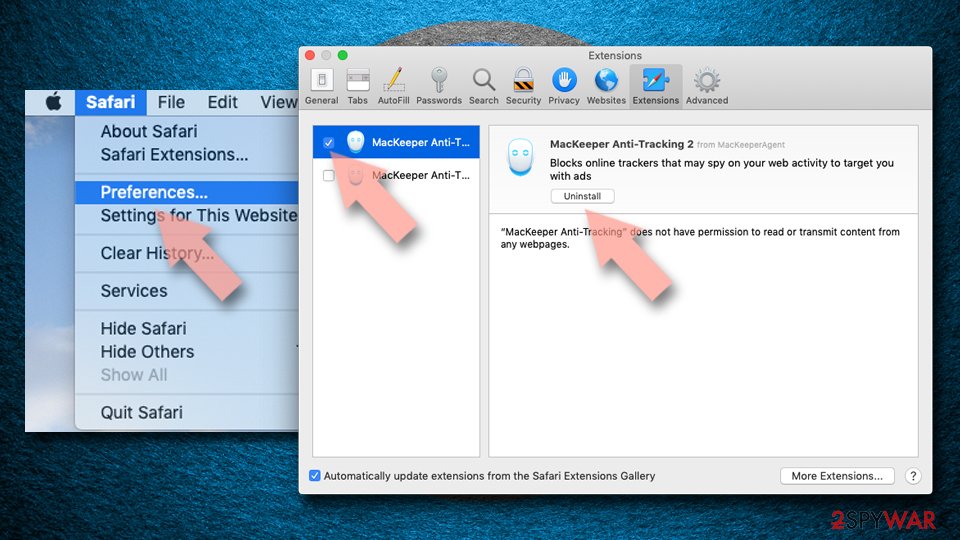
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
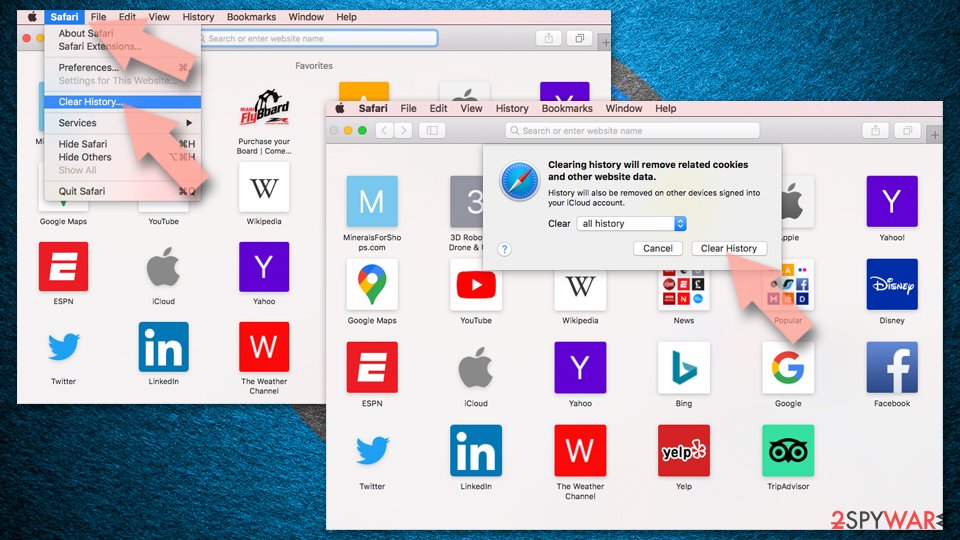
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
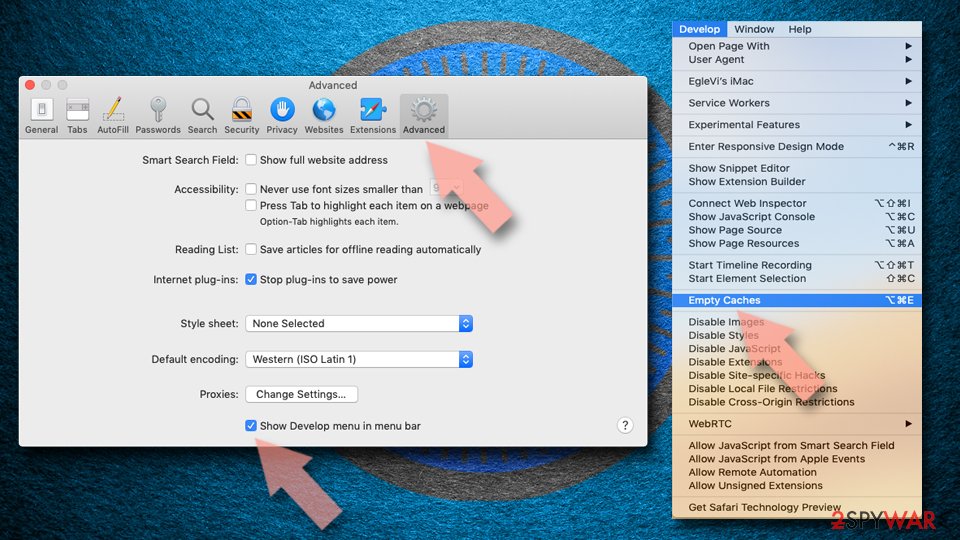
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
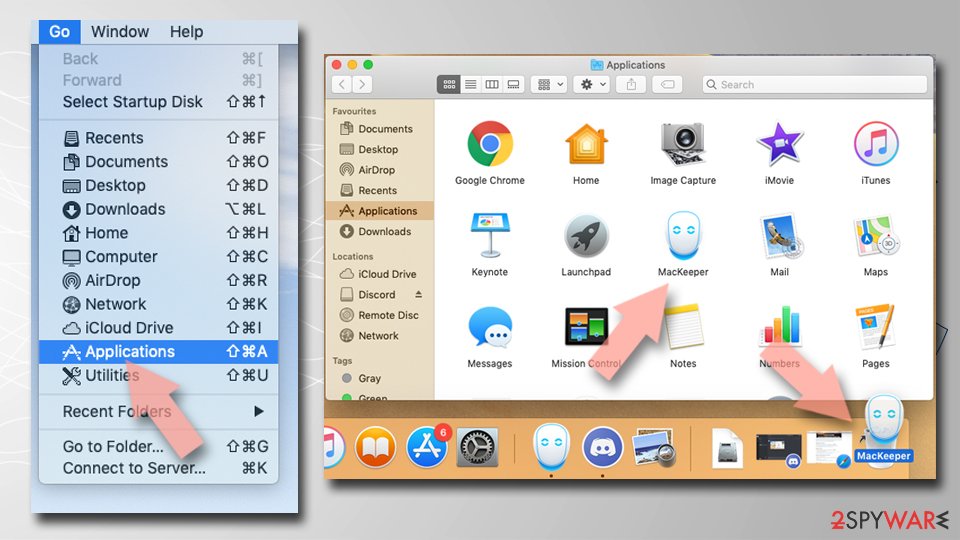
Delete from macOS
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
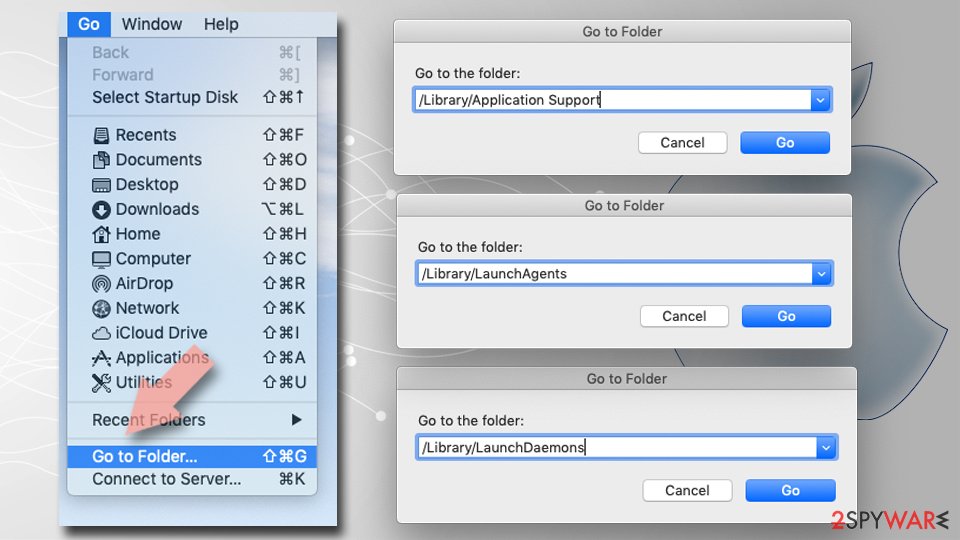
- Finally, empty the Trash to permanently remove the leftovers.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
From our report of May 2021 · not reviewed since
Learn how to remove redirect virus automatically
If malware keeps ruining your web browsing experience, you should not delay the removal of PUPs from your PC.
The easiest way to do that is to run a full system scan with a professional anti-malware tool. Professional tools will help you find all unwanted programs that are responsible for causing havoc on your computer.
Remember that to remove s3.amazonaws.com from the system and prevent its reappearance, you have to uninstall all suspicious apps. Anything left behind affects the persistence and causes different intrusive behavior.
Nonetheless, if you think about yourself as an experienced PC user and prefer the typical software removal technique, you can use the guide submitted by our research team. Make sure to follow each step carefully, and don't forget that the complete removal will be counted only after resetting your web browser.
Questions about s3.amazonaws.com ads
What is s3.amazonaws.com?
s3.amazonaws.com appears to be a misused domain related to Amazon Web Services' legitimate S3 cloud storage service. However, cybercriminals redirect users to fake versions of this page that display deceptive pop-ups claiming software updates are needed. These scams typically show fake Flash Player or Adobe update prompts to trick users into downloading malware.
The legitimate Amazon AWS S3 is a genuine cloud storage service, but criminals exploit the familiar domain name to make scams appear credible. The fake pages use professional-looking layouts and positioning to increase the likelihood that users will click the deceptive prompts.
Is s3.amazonaws.com a virus?
The legitimate s3.amazonaws.com is not a virus; it's part of Amazon's cloud services. However, redirects to pages that impersonate this domain often contain malware distribution mechanisms. When you see pop-ups claiming updates are needed, clicking Allow can download trojans, ransomware, or other dangerous threats instead of legitimate software.
Security researchers have confirmed that cybercriminals misuse S3 servers and similar infrastructure to host malware. If you encounter these pop-ups, the threat is not from Amazon but from the malicious redirects that brought you to the fake page.
How do I get redirected to the fake s3.amazonaws.com?
Users typically encounter these redirects after visiting suspicious websites or clicking on pop-up advertisements. The redirects may also occur after installing free software bundled with adware or potentially unwanted programs. Malicious websites inject code that automatically redirects your browser to the fake s3.amazonaws.com pages.
Some browser hijackers change your new tab URL to point to these scam pages. Visiting forums, torrent sites, or other low-security websites increases your exposure to such redirects. Once compromised, your browser may repeatedly navigate to these pages regardless of your browsing habits.
What happens when I click the update pop-ups?
Clicking the Allow or OK button initiates a download of malware instead of legitimate software updates. The downloaded file may contain trojans designed to steal personal information or banking credentials. Ransomware can encrypt your files and demand payment for decryption.
The malware runs background processes that slow your computer and compromise system stability. Your browsing may be hijacked to additional malicious pages, and additional unwanted programs may install automatically. In severe cases, your system may become unusable without professional repair or complete reinstallation.
Can I trust Amazon AWS or Microsoft with these update alerts?
No. Apple, Microsoft, and Amazon never distribute software updates through web browser pop-ups or notifications. Official updates come through your operating system settings or the software manufacturer's legitimate website. Any update alerts appearing in a browser window are scams.
Major companies will not use unexpected notification prompts to request permission for installations. Always verify software updates through official channels, such as Windows Update for Microsoft products or the Mac App Store for Apple applications. Be skeptical of urgent warnings about outdated software appearing in browser notifications.
What should I do if I clicked on a fake update?
Immediately close the browser window and do not complete any download or installation. Run a full system scan with anti-malware software to detect and remove any malware that may have been downloaded. Check your browser settings to ensure they have not been altered or hijacked.
If a file was downloaded, locate it in your Downloads folder and delete it permanently. Monitor your computer for unusual activity such as new windows opening or slow performance. Change passwords for sensitive accounts like email and banking from a different clean device if the infection was significant.
How can I prevent these scams?
Avoid visiting suspicious websites and be cautious with pop-up advertisements. Install reputable ad-blocking software to prevent many malicious redirects. Download free software only from official sources and use Advanced installation settings to avoid bundled adware.
Keep your operating system and all software updated with the latest security patches. Install and maintain security software that blocks known malicious sites and scams.
Never click Allow on unexpected browser notifications asking for permissions. If you see warnings about urgent updates, close the page immediately and verify through official channels instead.
What should I do after removing the malware?
Run a complete system scan with updated anti-malware software to ensure all traces are removed. Reset your web browser to default settings to eliminate any malicious extensions or settings changes.
Clear your browser cache, cookies, and browsing history to remove any remaining tracking data. Check installed programs and uninstall anything suspicious or unfamiliar.
Monitor your system for unusual activity and be alert for additional signs of infection. Consider using a password manager to change compromised passwords securely. Keep your security software active and updated to prevent future infections.
Will Fortect remove s3.amazonaws.com?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For s3.amazonaws.com, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: Malvertising (read October 5, 2026)
- Official websit of AWS Amazon: AWS Amazon (read October 5, 2026)
- Virustotal: Fake updater detection rate (read October 5, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Amazon S3 User Guide: Virtual hosting of general purpose buckets (path-style and virtual-hosted-style URLs) (read October 10, 2026)