
Shortcut virus: what it is and how to remove it
Shortcut virus is a trojan that hides files and replaces them with inaccessible shortcuts, primarily spreading through USB drives and exploiting Windows Autorun features. It may also function as spyware to steal personal data.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Unsure whether Trojan.VBS is safe? A free scan checks the file and what starts it.
Do it yourself · free Remove Shortcut virus yourself 6 steps, about 18 minutes, no software needed.
Start the steps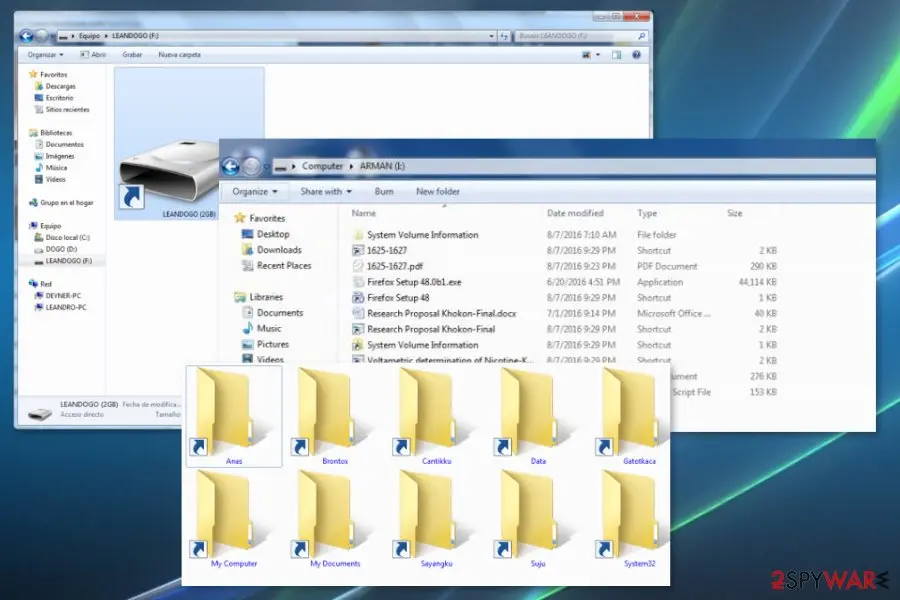
Shortcut virus: summary
| Distribution | This threat can get on the system via infected email attachments, sites that rigger malware downloads, or even other malware that is set to spread such intruders directly on the targeted system |
|---|---|
| Name | Shortcut virus |
| Type | Malware |
| Issues | This intruder has trojan and worm functionalities and can affect the machine significantly when it runs in the background for a while. It degrades system performance and affects the speed, disables or adds various features, and programs on the machine to affect the persistence |
| Symptoms | Files get altered when the virus replaced data using shortcuts with the same name. Data becomes inaccessible and can even get damaged |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Damage | Not recorded in the old report |
|---|---|
| Evidence | 4 write-ups by security sites; no sample analysed yet |
| File names | Trojan.VBS |
| First seen | 8 June 2020 |
| Microsoft Defender name | Worm:VBS/Cantix.A. |
| Facts checked | 5 October 2026 |
What Shortcut virus does on an infected PC
What readers reported about Shortcut virus
problems removing aristotlesearch.com from chrome. I don't know why aristotlesearch.com became my browser's homepage. This search engine looks suspicious, and I don't want to use it. I tried to clean Chrome's shortcut and reset settings, but it wouldn't work. Help me, please.
What is Mofeb? And why can't I access my files anymore??. I cannot access my files anymore! Everything is turned into shortcuts!! HEELP!
How do I remove extension from my files??. There is something wrong with my PC. The files on it are all displayed as shortcuts and feature a extension instead of the regular ones. Plus, I cannot seem to open none of them! How do I remove this suspicious extension and regain access to my files?
Why is .Cerber2 extension pinned to my files?. Hey. There is seriously something wrong with my PC. All the files on my computer are now turned to shortcuts and feature .Cerber2 file extensions.. Plus I cannot access any of them anymore. How do I remove .Cerber2 extensions and get my files back?
From the comments under our earlier guide; names and contact details removed.
From our report of Oct 2026 · outdated details corrected in October 2026
Shortcut virus is the malware that hides files and replaces them using inaccessible shortcuts but can cause more damage to the OS
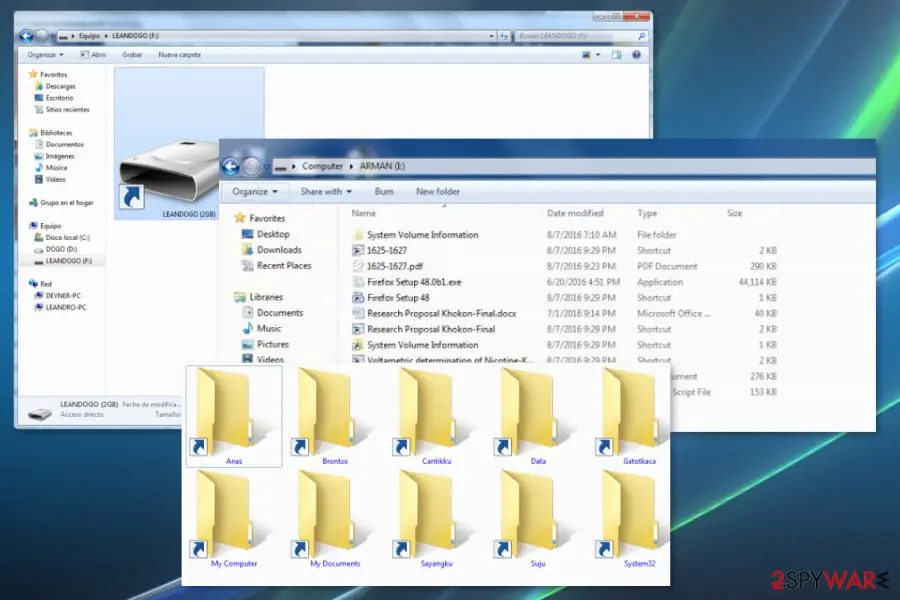
Shortcut virus is the trojan-type malware that also has features of the worm threat because it hides your files and folders, replaces them with shortcuts.
Even those shortcuts look the same those files are malicious. It often targets USB drives and computers and converts valid files into inaccessible forms. Actual files are not deleted, but you cannot normally use the needed file. You can remove this virus, and once that is done, you will recover your files.
However, some of the users claim that it damages data permanently and that file loss is a real issue. This threat can also be called the USB Shortcut virus because it makes files unopenable and inaccessible on USB drivers mainly.
Trojan hides your files and replaces them with the same name. It is easily spreadable too, unfortunately. Any link once clicked can trigger the download of the malware script and affect the operating system, all connected devices.
Shortcut virus is a Trojan horse that is designed to transform files on the corrupted device into shortcuts. Thus, it makes data inaccessible. However, the vast majority of antivirus can detect this cyber threat as a Trojan.VBS.TTE (B), Worm:VBS/Cantix.A., Troj/Agent-NXIMal/FakeAV-BW, and other names.
Shortcut malware spreads via portable devices, such as USB drives, Pen-drives, SD cards, etc. However, they might affect desktop computers and laptops. Most of the time it happens when a user connects an infected external device to the PC. Due to the operation peculiarities, security researchers excluded three main versions of the virus:
However, the latter two - File and Folder viruses - are often combined and referred to as File and Folder shortcut virus. Despite slightly different behaviors, the termination of these cyber threats remains the same. The best way to remove Shortcut virus is to employ malware removal tool and scan the device. To recover files affected in system folders after the removal procedure - rely on .
This version of Shortcut virus can infect USB, SD cards, or any other portable device. As soon as it infiltrates, it puts all the files stored on the device into a hidden folder. Then it creates a shortcut.exe which prevents from accessing personal data.
However, the execution of shortcut.exe may lead to even bigger problems. This Trojan horse might act like spyware or keylogger. Thus, it might collect personally identifiable or even banking-related information. Therefore, immediate Shortcut virus removal is needed.
- File shortcut virus;
- Folder shortcut virus.
From our report of Oct 2026 · not reviewed since
The main features of the File and Folder Shortcut virus
This version of Shortcut malware aims at files and folders.
On the affected device, it hides and replaces files with these extensions:
After the Shortcut virus hijacks, it might also install other malicious software to the affected device which might pose a danger to the victim's privacy. Thus, this malware might monitor and even steal personal information, including credit card details.
- shortcuts.exe;
- shortcut.lnk;
- file.ini (desktop.ini);
- shortcut.vbs.
From our report of Oct 2026 · not reviewed since
The virus takes advantage of Windows Autorun and Autoplay feature
Users can get infected with malware if they:
Security experts from Norway say that such silent virus is a popular cyber threat that spreads via USB and other external devices. When a user connects an infected device to the computer, malware exploits Windows Autorun and Autoplay feature.
The virus uses a vulnerability in a way how Windows operating system handles shortcut files. Such files with .lnk extension belong to Windows and are designed to run various programs when a user clicks on it. However, this USB malware does not need victim's click in order to be executed. It can be launched automatically.
Thus, to avoid this cyber threat, users are suggested to use reputable and updated antivirus to scan all attached external devices. Additionally, do not connect USB or other gadgets to other computers if you are not sure that they are virus-free.
- do not scan an external device with an updated antivirus once they connect it to the computer;
- plug a portable device to the infected computer;
- download malicious programs or files.
From our report of Oct 2026 · not reviewed since
More from our earlier report on Shortcut virus
- Shortcut virus removal is the process that can be difficult due to the purpose of malware and particular features the threat has, so running the full system scan on the machine using AV tools can help significantly
- File recovery and fix for affected files can help you with the damage and further use of the computer
How to check the PC for Shortcut virus
What antivirus programs call Shortcut virus
Microsoft Defender reports Shortcut virus as Worm:VBS/Cantix.A..
In a Defender name, the part before the colon is the category, the part after it is the platform, and the part after the slash is the family Microsoft assigned. A suffix after ! is an internal Microsoft marker, not a different threat.
Generic labels such as Agent, GenericKD or Malware.AI only say that a file looks malicious, not what it does; our guide to antivirus detection names shows how to read them.
- File:
Trojan.VBS
How to remove Shortcut virus
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where Trojan.VBS runs from and stop it
Trojan.VBSis the part you can see, and its location tells you whether it belongs there. Right-click it on the Processes page of Task Manager and choose Open file location, then right-click the file > Properties > Digital Signatures to see who signed it.An unsigned file, or one in a user folder such as
%AppData%, is the one to remove: end the task, then delete the file.Note the folder name, because the same folder usually holds its other files. This is the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Shortcut virus or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 3: Remove it from startup
Whatever Shortcut virus installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Oct 2026 · not reviewed since
Instructions for Shortcut virus termination
Nevertheless, it is recommended to remove Shortcut virus using malware removal software or security tools, such as , or ; there are also a few ways how you can get rid of it manually. However, if you choose manual elimination, please follow the instructions carefully. This is not the simplest threat to get rid of, so you may need some additional tips and tricks.
However, the main Shortcut virus removal method could be the full system scan using anti-malware tools. Once the threat is indicated for you, it can be deleted using the same AV detection engine. Nevertheless, you still need to repair files and system functions when the malware affects them.
The best option for such malware is to remove Shortcut virus and clean the machine fully. Anti-malware tools focus on cleaning threats from the system. Tools like or optimizer applications, PC repair programs can find damaged data and fix virus damage where needed.
Method 1. Delete the virus using command prompt to clear the external devices
Method 2. Shortcut virus removal using Registry editor
Method 3. Tweak CONFIG to eliminate Shortcut malware
- Go to Run.
- Type cmd and click OK button.
- Connect the infected removable drive.
- Enter this command to the command prompt window: attrib -h -r -s /s /d e:\ NOTE: instead of e: you have to write the name of the infected removable drive.
- Press Enter.
- The virus should be eliminated. Furthermore, you have to copy and save necessary information from the removal drive.
- Then format a removable drive. Once it's done, you can copy back previously saved data.
- Open Windows Task Manager by clicking Ctrl + Shift + Esc on a keyboard.
- Go to Process tab.
- Find process .exe.
- Right-click it and choose End Process.
- Access Registry editor: Click Windows key + R and type regedit.
- Click Enter.
- In the Registry editor, navigate to this key: HKEY_CURRENT_USER/Software/Microsoft/Windows/CurrentVersion/Run
- Find odwcamszas.exe and delete it.
- Restart the computer to save the changes.
- Access Temporary Files folder by entering %temp% in Run.
- Find .vbs and delete it.
- Open Run and type msconfig.
- Go to Startup Tab.
- Delete vbs.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed an unfamiliar process called Trojan.VBS in Task Manager, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about Shortcut virus
What is Shortcut virus?
Shortcut virus is a trojan-type malware with worm features that hides your files and folders, replacing them with shortcuts that appear identical but are actually malicious. It primarily targets USB Flash drives and external storage devices but can infect computers.
When infected, files become inaccessible despite not being deleted—they're simply hidden. Users claim it damages data permanently, though in most cases files can be recovered after removal. This threat is highly spreadable through infected external devices and email attachments.
How does Shortcut virus spread?
Shortcut virus primarily spreads via USB drives, SD cards, and other portable devices. Infection typically occurs when connecting an infected external device to a computer.
The virus exploits Windows Autorun and Autoplay features to execute automatically without user interaction, using a vulnerability in how Windows handles shortcut files with .lnk extensions. Email attachments and malicious download sites also distribute the threat. Once on your system, any connected portable device can become infected, and the cycle continues.
What file types does Shortcut virus affect?
The File and Folder Shortcut virus affects multiple file extensions, effectively targeting documents, media files, databases, and other important data stored on infected devices. All files become hidden and inaccessible. While the original files aren't deleted, shortcuts replace them with the same names, preventing normal usage.
File recovery tools can restore these hidden files after removing the malware. Some users report permanent data loss, though this typically results from improper recovery attempts rather than actual file deletion.
Does Shortcut virus steal personal information?
Yes. Shortcut virus may act like spyware or a keylogger, collecting personally identifiable information and banking-related data. After hijacking files, it may install additional malicious software to enable surveillance capabilities.
The trojan can monitor and even steal sensitive information including credit card details and login credentials. This dual threat—both file hiding and data theft—makes immediate Shortcut virus removal critical to protect your privacy and financial security.
How do I remove Shortcut virus?
The best removal method is running a full system scan with reputable anti-malware software that can detect various aliases including Trojan.VBS.TTE, Worm:VBS/Cantix.A, and others. After malware removal, use file recovery tools to restore files affected by the virus.
Manual removal via command prompt is possible: connect the infected removable drive, type 'attrib -h -r -s /s /d e:\' (replacing 'e:' with your drive letter) to unhide files, then manually delete virus components. Professional anti-malware scanning remains the most effective approach.
Will my files be permanently lost?
No. While Shortcut virus hides and makes files inaccessible, the actual files remain intact on your storage device. After removing the malware, files become recoverable using file recovery tools.
Some users claim data is permanently damaged, but this usually results from improper recovery attempts or attempts to access corrupted shortcut files. The vast majority of antivirus solutions can detect this threat, and proper removal procedures allow restoration of all hidden files to working condition.
Can Shortcut virus affect desktop computers?
Yes. While Shortcut virus primarily spreads through USB drives and portable devices, it can infect desktop computers and laptops. When an infected external device connects to a computer, the virus exploits Windows Autorun features to install itself.
Once on a desktop, it can affect all local drives and any subsequently connected devices. This is why scanning external drives with updated antivirus before connecting them is crucial for protection.
How do I protect my computer from Shortcut virus?
Use reputable and updated antivirus software to scan all attached external devices before connecting them to your computer. Never connect USB drives or other gadgets to your computer if you're uncertain they're virus-free. Also avoid connecting your devices to potentially infected computers.
Disable Windows Autorun and Autoplay features to prevent automatic malware execution. Maintain current antivirus definitions and perform regular system scans. Be cautious when downloading files from untrusted sources.
Will Fortect remove Shortcut virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Shortcut virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: Trojan horse (computing) (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)
- Microsoft Learn: How Microsoft names malware (read October 5, 2026)