
Trojan:Win32/Bluteal.B!rfn: what it is and how to remove it
Trojan:Win32/Bluteal.B!rfn is a detection that may be a false positive or real malware infection. Windows Defender began flagging this threat in May 2018, sometimes incorrectly.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Unsure whether ni.dll is safe? A free scan checks the file and what starts it.
Do it yourself · free Remove Trojan:Win32/Bluteal.B!rfn yourself 6 steps, about 18 minutes, no software needed.
Start the steps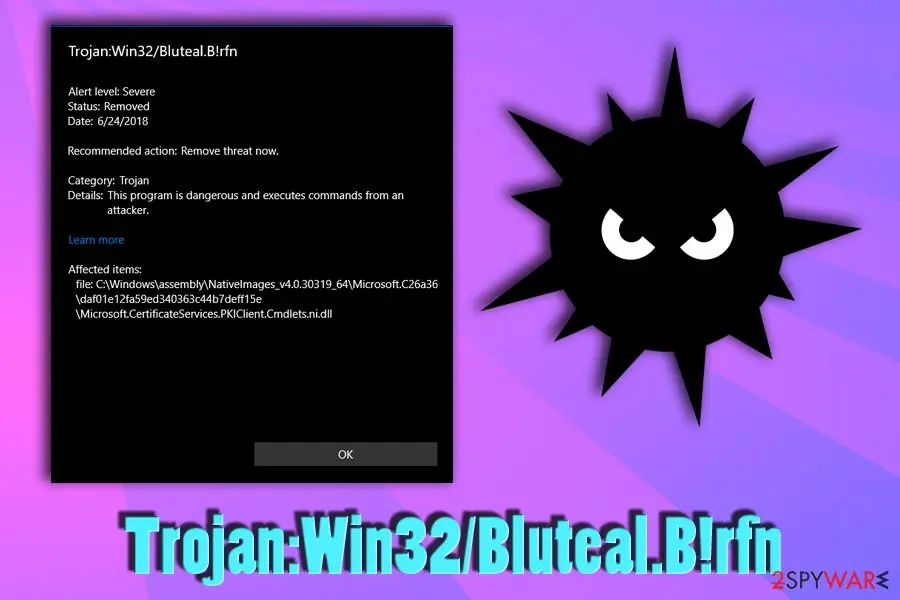
Trojan:Win32/Bluteal.B!rfn: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | Trojan:Win32/Bluteal.B!rfn |
| Type | Loader |
| Symptoms | An unknown process in Task Manager and a Windows Security "Threats found" notification |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Evidence | 4 write-ups by security sites; no sample analysed yet |
|---|---|
| File names | ni.dll |
| First seen | 28 June 2018 |
| Microsoft Defender name | Trojan:Win32/Bluteal.B!rfn |
| Facts checked | 5 October 2026 |
What Trojan:Win32/Bluteal.B!rfn does on an infected PC
From our report of Jun 2018 · not reviewed since
Trojan:Win32/Bluteal.B!rfn - a false positive by Windows Defender, although users should not let their guard down
Trojan:Win32/Bluteal.B!rfn might be a malicious application that infected your machine without you noticing, such as a trojan horse or a crypto miner (this malicious software became quite popular among cybercriminals recently).
Microsoft forums were flooded with questions, as users reported that Windows Defender is also detecting files of legitimate programs as malicious. Although Microsoft confirmed that it might be a false positive in some cases, it can also indicate a severe computer infection.
False positives happen from time to time to every single AV engine, and it is due the code particular programs are written in. Users can report certain detections as false positives so that security researchers could investigate further. Additionally, users can also set the detected program as an exception, if they are entirely sure that it is not malware.
Nevertheless, we do not recommend doing that, especially if you are not that computer-savvy. In some cases, the detection might be real - Trojan:Win32/Bluteal.B!rfn removal would be required.
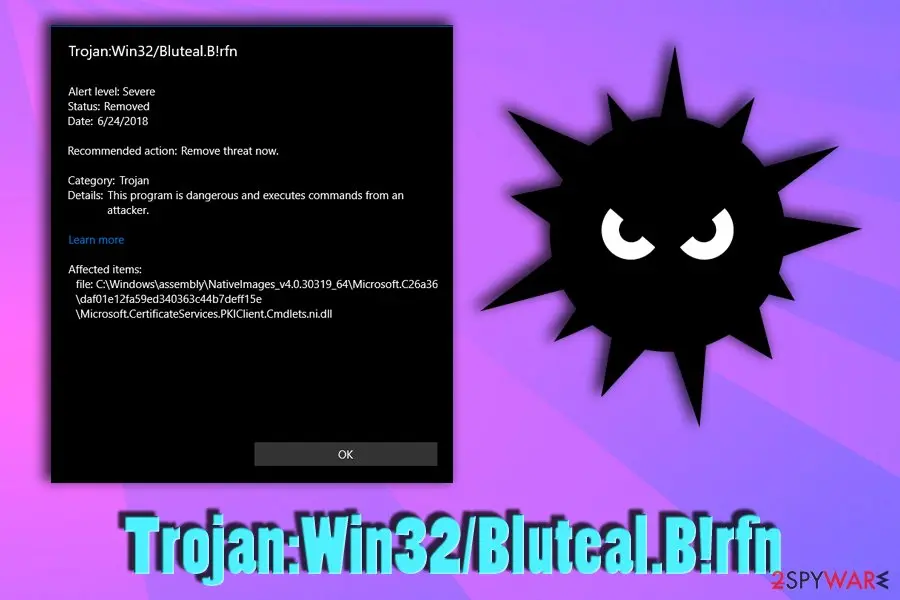
Users also reported that even Windows files could be flagged as a BluTeal trojan, such as Microsoft.CertificateServices.PKIClient.Cmdlets.ni.dll or Microsoft.VisualStudio.Utilities.Internal.ni.dll. These reports started to occur at around May when it was added to Windows Defender. The description of the threat seems to be not quite definite:
However, according to Microsoft's definition version 1.271.37.0, an update has been made to the Trojan:Win32/Bluteal.B!rfn, and possibly removed the change of it being a false positive.
Nevertheless, there is no official confirmation that is has been fixed yet, and users might have to wait for the next Windows Defender update. Still, security experts recommend to keep security software up to date - make sure the version of your security software is the latest one.
As of now, we advise you not to rush if your anti-virus detected a trojan. It might be a false positive, and it might be not. If the latter is true, you would have to remove Trojan:Win32/Bluteal.B!rfn virus from your machine carefully, especially if your computer is experiencing error messages, BSoDs, slowdowns, high CPU/GPU usage, increased amounts of ads, and similar behavior.
From our report of Jun 2018 · not reviewed since
Trojan horses can be avoided by being careful online
False positives may confuse users, as they might see a legitimate program being flagged as malicious.
However, security experts recommend always to take a great interest if the AV engine flagged something. It can still be a virus which can significantly damage your computer or steal personal data. Therefore, it is vital to be careful online. Even though nothing can make you secure from viruses 100% but there is still something you can do to lessen the chance of infection:
- install anti-malware software - that is the basic rule which can save you hundreds of dollars and your precious files;
- back-up your data on a remote server or an external HDD;
- avoid visiting websites of dubious content, such as free online gaming, adult, file-sharing, gambling, etc.;
- do not download software or its updates from third-party sites;
- do not click on the suspicious spam emails - phishing emails is the most prominent malware distribution method;
- patch your operating system and software regularly;
From our report of Jun 2018 · not reviewed since
More from our earlier report on Trojan:Win32/Bluteal.B!rfn
- Trojan horse - can range from false positive to crypto-malware
- Use or to make sure the file is malicious
- If file is malicious, it can range from intense CPU/GPU usage, frequent error messages to increased amount of ads
- Malicious files spread via contaminated spam email attachments, infected of hacked websites, file-sharing sites, etc.
- This threat can perform a number of actions of a malicious hacker's choice on your PC.
How to check the PC for Trojan:Win32/Bluteal.B!rfn
What antivirus programs call Trojan:Win32/Bluteal.B!rfn
Microsoft Defender reports Trojan:Win32/Bluteal.B!rfn as Trojan:Win32/Bluteal.B!rfn.
In a Defender name, the part before the colon is the category, the part after it is the platform, and the part after the slash is the family Microsoft assigned. A suffix after ! is an internal Microsoft marker, not a different threat.
Generic labels such as Agent, GenericKD or Malware.AI only say that a file looks malicious, not what it does; our guide to antivirus detection names shows how to read them.
- File:
ni.dll
How to remove Trojan:Win32/Bluteal.B!rfn
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where ni.dll runs from and stop it
In Task Manager (Ctrl + Shift + Esc) find
ni.dllon Processes, right-click it and choose Open file location before ending anything.Windows' own files live in
C:\Windows\System32; the same name in%AppData%, %Temp% or C:\Users\Public is an impostor. If the folder is wrong, right-click the process again, choose End task and delete the file.If it starts again within seconds, a task or another process restarts it, so run the scan step in Safe Mode. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Programs like Trojan:Win32/Bluteal.B!rfn add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 3: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after Trojan:Win32/Bluteal.B!rfn, its publisher or created on the day the problem started.Delete those folders, and check
C:\Program FilesandC:\Program Files (x86)too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
A scan finds the parts of Trojan:Win32/Bluteal.B!rfn that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Trojan:Win32/Bluteal.B!rfn can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Jun 2018 · not reviewed since
Make sure you remove Trojan:Win32/Bluteal.B!rfn if it is malicious
In some cases, malware can be hard to detect and not all anti-virus tools are capable of doing that.
If the file is indeed malicious, do not delay Trojan:Win32/Bluteal.B!rfn removal. Do not even try eliminating the cyber threat manually, as this action can only be performed successfully by IT experts. Trojans and similar infections have a complicated code which modifies system files, and it is hard to set everything back to normal without the anti-virus tool.
If you struggle to remove Trojan:Win32/Bluteal.B!rfn virus, you should reboot your Windows machine and enter Safe Mode with Networking, as explained below.
[GI=method-1]To eliminate Trojan:Win32/Bluteal.B!rfn virus safely, you should enter Safe Mode with Networking:
[GI=method-2]You can attempt the virus extermination by using System Restore:
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed an unfamiliar process called ni.dll in Task Manager, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about Trojan:Win32/Bluteal.B!rfn
What is Trojan:Win32/Bluteal.B!rfn?
It is a Windows-specific threat detection that may indicate either a false positive or genuine malware infection. Reports of this detection increased around May 2018 when it was added to Windows Defender.
In some cases, legitimate Windows files like Microsoft.CertificateServices.PKIClient.Cmdlets.ni.dll and Microsoft.VisualStudio.Utilities.Internal.ni.dll were flagged incorrectly. According to Microsoft's definition version 1.271.37.0, an update was made addressing this detection, though official confirmation of complete resolution remains unavailable.
Is this a false positive or real malware?
It may be either one. Windows Defender false positives occur due to code that antivirus engines interpret as suspicious. Microsoft confirmed that Bluteal.B!rfn may be a false positive in some cases, while in others it can indicate genuine trojan horse or crypto miner infections.
Security experts recommend taking the detection seriously regardless, as the threat can range from a false alarm to severe malware. Do not rush into deletion without verification, but investigate the source file.
What damage can real Bluteal infections cause?
If the detection represents actual malware, it can range from intense CPU and GPU usage to frequent error messages and increased advertising. Trojan horses and crypto miners can cause significant system performance degradation.
Some infections trigger blue screens of death, system slowdowns, and repeated crashes. The malware may steal personal data or use system resources for cryptocurrency mining without your knowledge. Verify the file before assuming it is legitimate.
How can I verify if the detected file is malicious?
Check the file location first; suspicious files typically appear outside standard Windows system directories. If it is in C:\Windows\System32 or similar protected folders, it is more likely legitimate.
Run additional security scans using alternative antivirus tools to get second opinions. Users can check detection details through antivirus vendor websites. Avoid setting flagged programs as exceptions unless you are completely certain of their legitimacy.
Should I delete files flagged as Bluteal.B!rfn?
Not immediately without verification. If the detection occurred for legitimate Windows files, deletion can damage your operating system. However, if the file appears in suspicious locations or multiple antivirus tools flag it, removal may be necessary.
Do not attempt manual deletion unless you are confident about the file's origin. Use your antivirus software to quarantine or remove the threat, or seek expert assistance.
How do I prevent trojan horse infections?
Practice safe browsing habits by avoiding websites of dubious content including free gaming sites, adult sites, file-sharing platforms, and gambling sites. Do not download software or updates from third-party sources; use only official websites.
Avoid clicking on suspicious spam emails, which remain the most prominent malware distribution method. Back up your data to an external drive and keep your operating system and software regularly patched.
What if my antivirus keeps detecting this threat?
Ensure your security software is updated to the latest version, as updates may improve detection accuracy and reduce false positives. Run full system scans in Safe Mode to prevent interference from malware.
If repeated detections occur, consider running alternative antivirus software for comparison. If legitimate files keep getting flagged, check the vendor's website to confirm whether the issue has been resolved in newer antivirus definitions.
Is there a way to remove it if confirmed malicious?
If confirmed as malware, reboot your computer and enter Safe Mode with Networking before attempting removal. Run your antivirus software and allow it to quarantine or delete the threat.
Never attempt manual removal of trojans, as their complicated code modifies system files making restoration difficult. After removal, run System Restore to return your machine to a previous state before infection. Consider using a professional repair tool to fix remaining damage.
Will Fortect remove Trojan:Win32/Bluteal.B!rfn?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Trojan:Win32/Bluteal.B!rfn, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Microsoft: Trojan:Win32/Bluteal.B!rfn (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)
- Microsoft Learn: How Microsoft names malware (read October 5, 2026)