
Trojan:Win32/CryptInject!ml: what it is and how to remove it
Trojan:Win32/CryptInject!ml is silent malware that injects additional threats into infected systems. Detection typically shows no early symptoms, making immediate removal critical.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If you want to confirm nothing else came with Trojan:Win32/CryptInject!ml, a full scan checks the usual places in one pass.
Do it yourself · free Remove Trojan:Win32/CryptInject!ml yourself 5 steps, about 15 minutes, no software needed.
Start the steps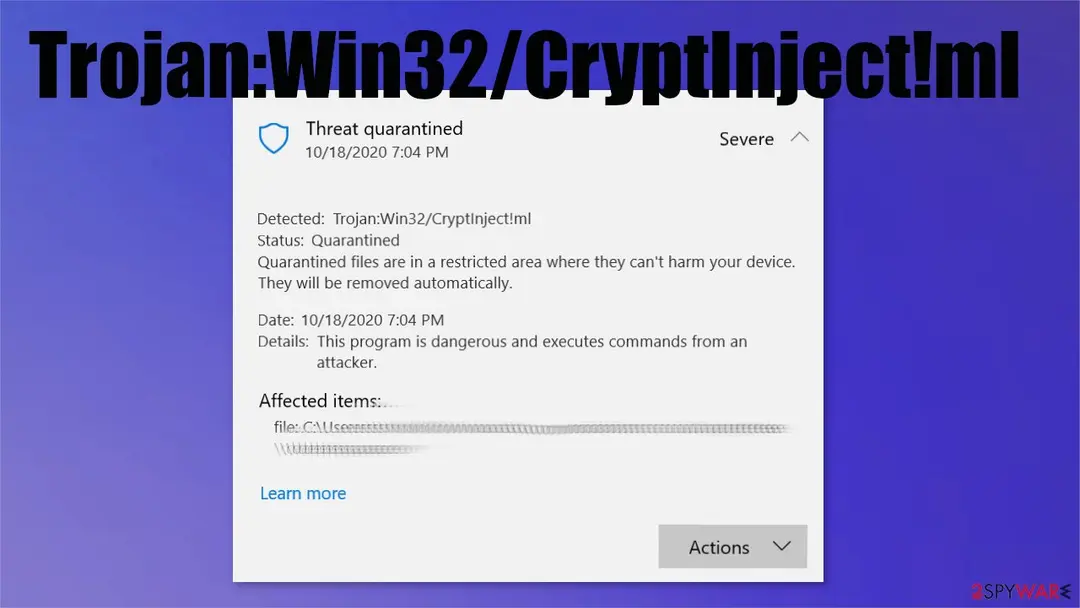
Trojan:Win32/CryptInject!ml: summary
| Distribution | These malicious programs mainly get distributed via infectious files forme emails, hacked sites, and similar online material |
|---|---|
| Name | Trojan:Win32/CryptInject!ml |
| Type | Trojan/ malware |
| Issues | The indication of the malicious program shows up on the security tool out of nowhere. The system gets affected or even damaged |
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Symptoms | A Windows Security "Threats found" notification |
|---|---|
| Evidence | 4 write-ups by security sites; details still limited |
| First seen | 1 December 2020 |
| Microsoft Defender name | Trojan:Win32/CryptInject!ml |
| Facts checked | 5 October 2026 |
What Trojan:Win32/CryptInject!ml does on an infected PC
From our report of Dec 2020 · not reviewed since
Threats come from suspicious content and misleading or deceiving pages
The main method that viruses get distributed using, includes malicious files and hacked sites, problematic programs.
Torrent sites, pirating services, and p2p platforms and free download sites can be used to distribute trojans, ransomware, and other malware.
Unfortunately, these methods of malware distribution also include email spam and phishing or social engineering even. Malicious actors have many techniques that help them in distributing malicious files, payloads of malware, threat injection files, direct malware.
You can avoid such infections by running anti-malware tools more often and relying on proper software distributors, official sites. Also, paying more attention to details on email notifications and sites that you visit wouldn't hurt.
From our report of Dec 2020 · not reviewed since
Trojan:Win32/CryptInject!ml virus termination procedures
To properly remove Trojan:Win32/CryptInject!ml, you should run an anti-malware or security tool, so the full system scan can show detected threats, malicious programs, and possibly dangerous applications or files.
Security software like or can help you find all the intruders and remove them from the PC.
You should also worry about possible virus damage and things that malware like this affects on the machine. This is why experts recommend going for the automatic malware removal process with AV tools and then running a program like that can possibly fix virus damage.
[GI=method-2]System restore feature can help with virus termination
From our report of Dec 2020 · not reviewed since
Trojan:Win32/CryptInject!ml is the malware that can act in the background and damage the machine significantly
Trojan:Win32/CryptInject!ml is the malware detection name that can indicate a threat running in the background.
These viruses can be set to perform various malicious activities from injecting malware on the infected machine to mining cryptocurrency, and even using the additional tools to exfiltrate data. You might not notice any issues besides the detection alert or the result coming on the screen after a regular system check. If so happens - run the same AV tool and make sure to clear the infection off of the PC.
The virus can be set to inject secondary payloads on the machine. Often trojans do not run any other processes but only trigger the injection of ransomware, data-stealing malware. There are various viruses that rely on these silent intruders as on spreading method.
You should note that any issues with the system, speed problems, performance interruptions, crashes, or freezes might be related to this infection. This is not the PUp or any other browser-based intruder that would show particular symptoms for you, so you need more attention to the procedure of eliminating the virus too.
You might notice some issues with the machine when the Trojan is installed, but there are no files or programs that can be deleted manually. Trojans mainly are set to:
Trojan:Win32/CryptInject!ml removal procedure might be difficult if the threat already was active for a while. Process in the background might be masked using executable files or different format data that shows up on Task Manager, but people do not pay close attention.
You can remove malware by running a security tool or anti-malware program like or and finding all the possible infection pieces automatically for you. It can be easier if you reboot the system in Safe Mode with Networking, so the AV engine runs without interruption.
Otherwise, Trojan:Win32/CryptInject!ml affects the performance of the computer overall by disabling security tools, altering registry, startup preferences, other functions. Ensure the proper system cleaning and file repair with or a similar tool for system optimization. You can find additional tips below.
- inject other threats;
- mine cryptocurrency;
- open backdoors for attackers;
- steal data from the OS;
- log credentials and logins, passwords actively.
From our report of Dec 2020 · not reviewed since
More from our earlier report on Trojan:Win32/CryptInject!ml
- To remove malware from your system, you should use anti-malware tools or security software that can find and eliminate all threats
- The malware of various types can interfere with functions and files on the system, so this trojan is no exception.
- Make sure to repair damage and fix issues with tools like
How to check the PC for Trojan:Win32/CryptInject!ml
Microsoft's name for Trojan:Win32/CryptInject!ml is Trojan:Win32/CryptInject!ml.
Defender sorts threats by category first, so the word before the colon tells you what kind of program was found, even if the family name means nothing to you.
Do not search for a removal tool by the detection name alone; fake "removal tools" use the same keywords. How the naming works is explained in our guide to antivirus detection names.
How to remove Trojan:Win32/CryptInject!ml
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Programs like Trojan:Win32/CryptInject!ml add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 2: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after Trojan:Win32/CryptInject!ml, its publisher or created on the day the problem started.Delete those folders, and check
C:\Program FilesandC:\Program Files (x86)too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of Trojan:Win32/CryptInject!ml that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Trojan:Win32/CryptInject!ml can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
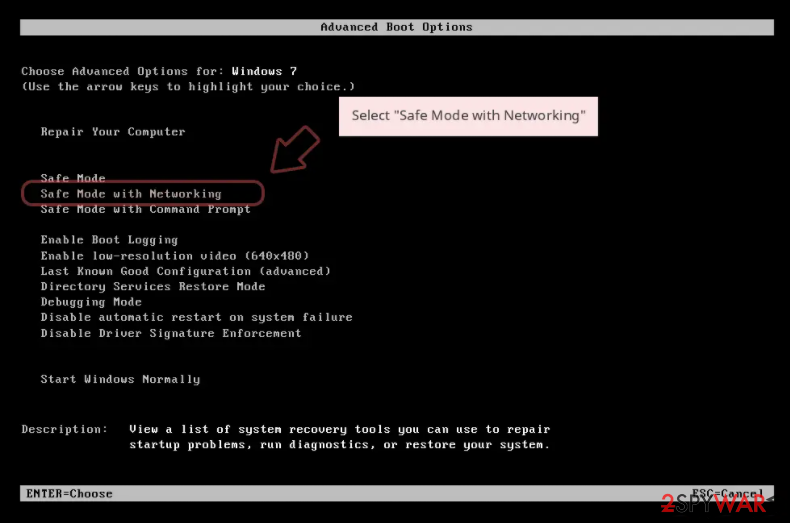
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
Windows 10 / Windows 8
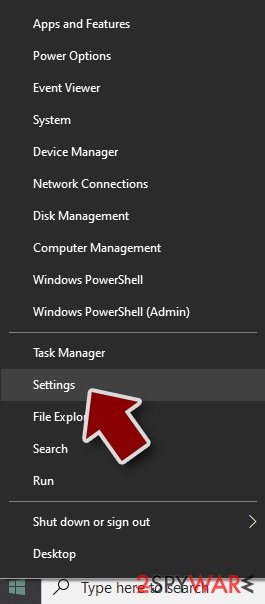
- Right-click on Start button and select Settings.
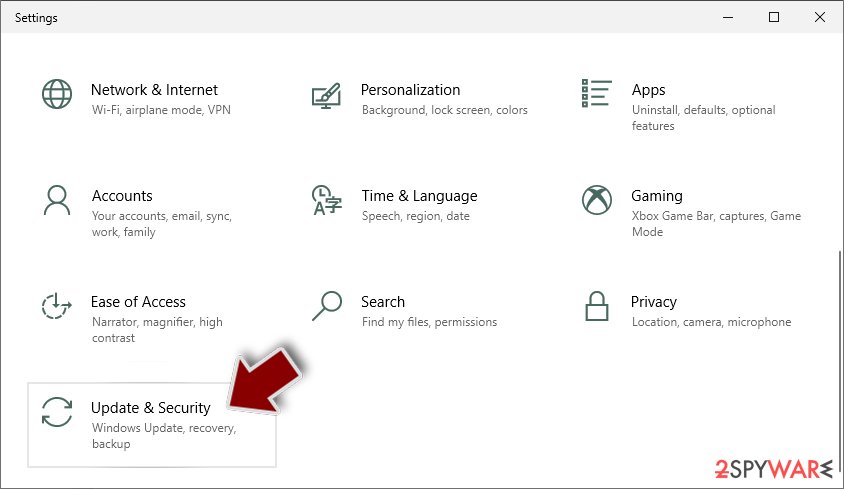
- Scroll down to pick Update & Security.
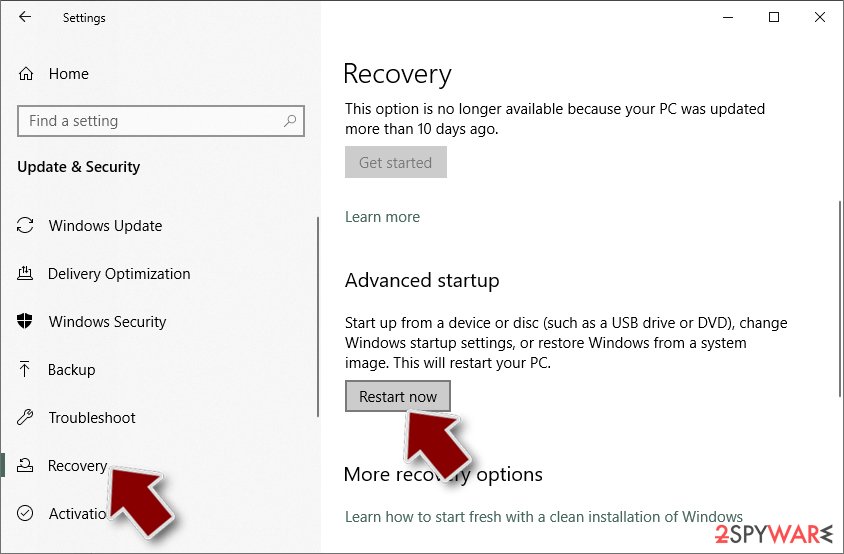
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
- Select Troubleshoot.
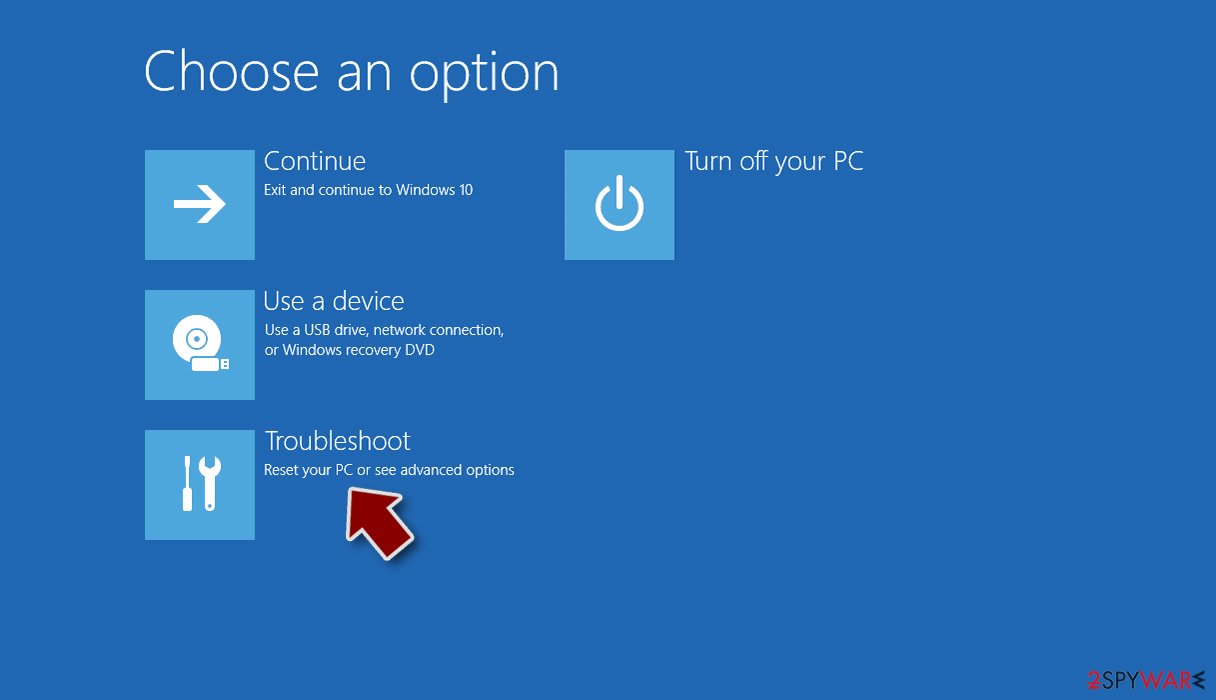
- Go to Advanced options.
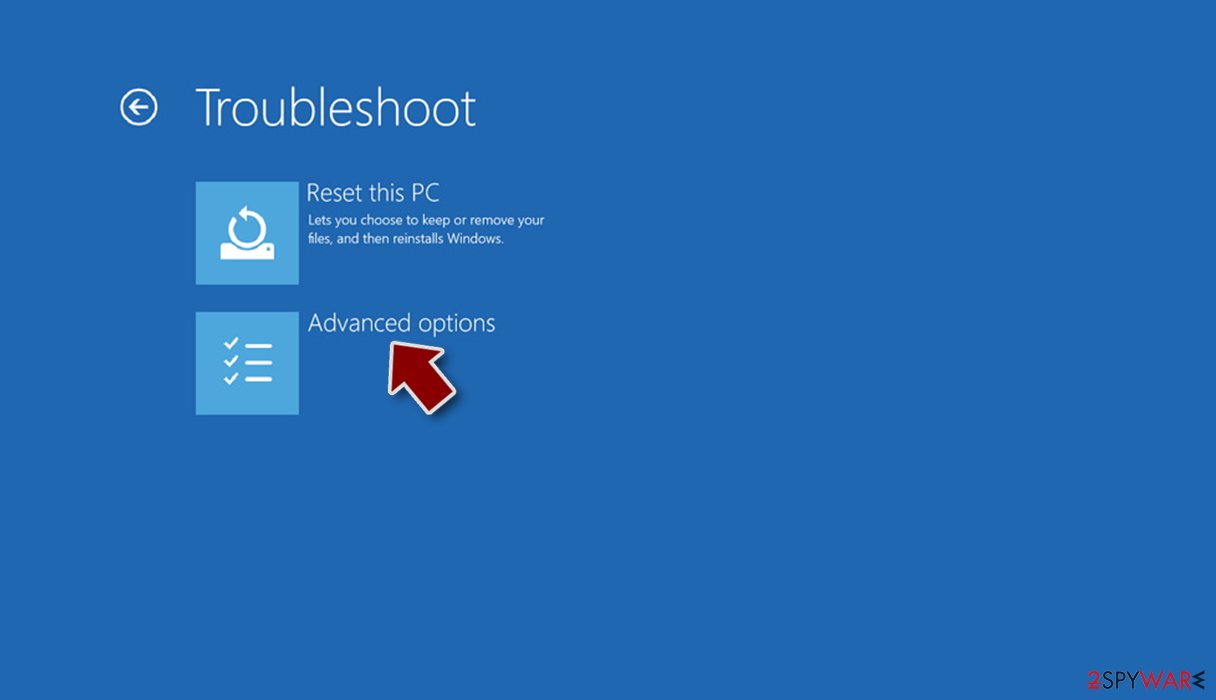
- Select Startup Settings.
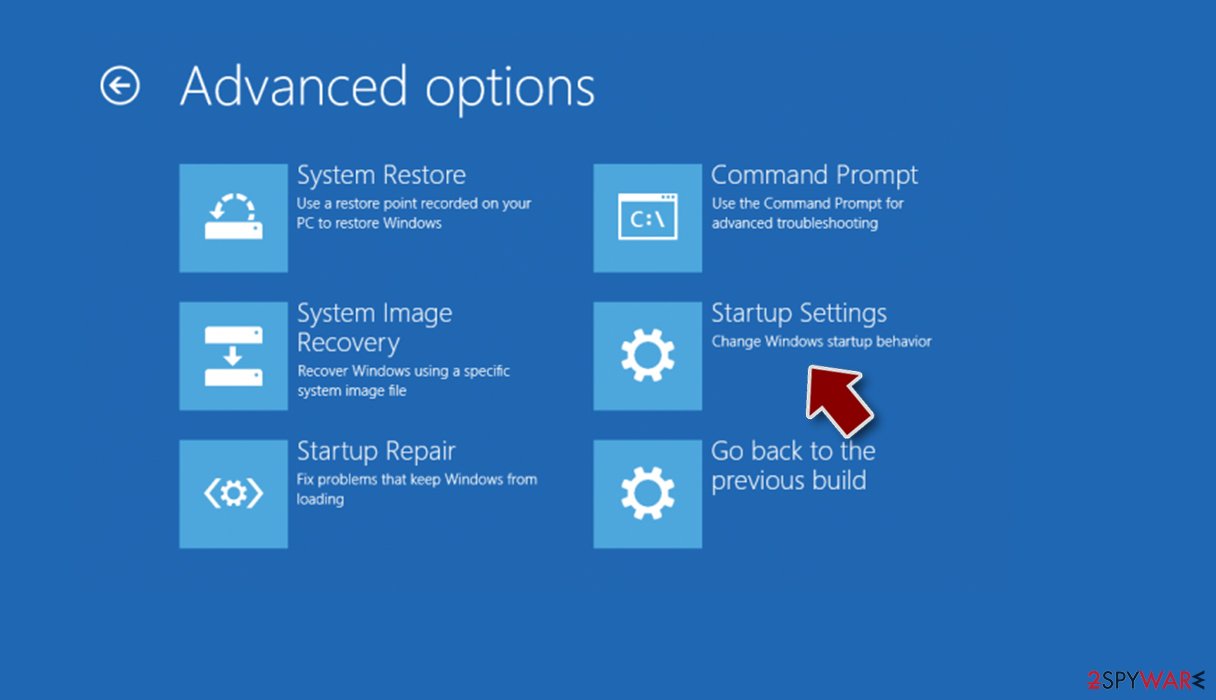
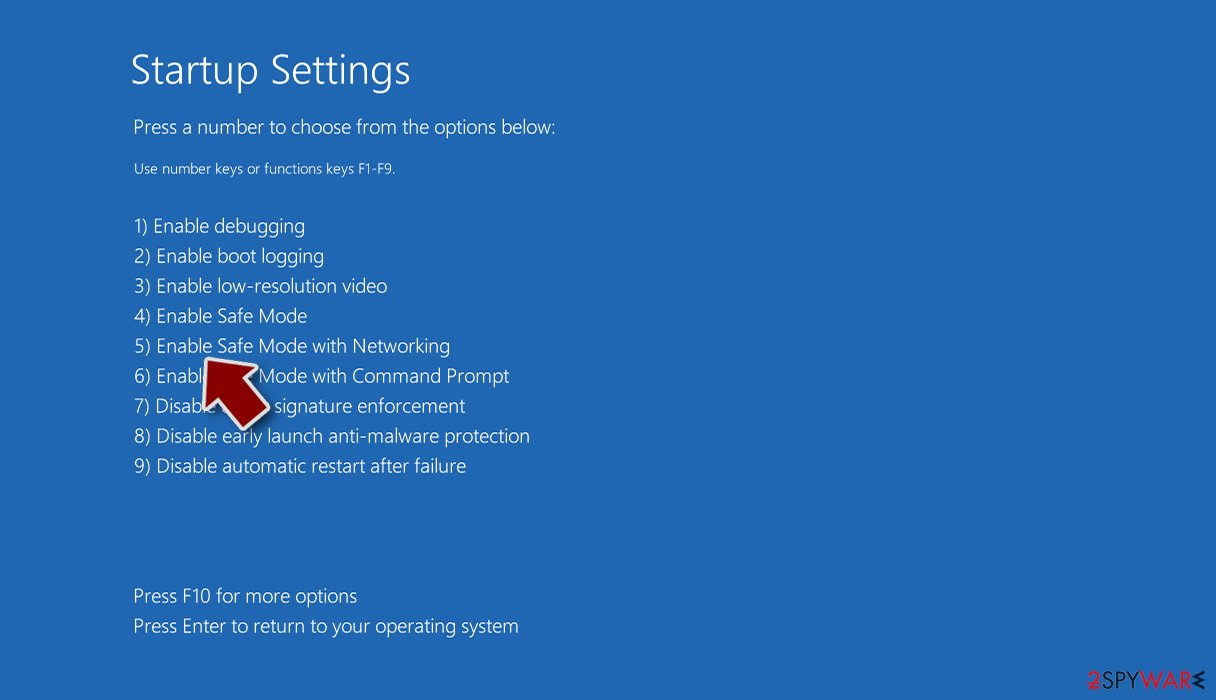
- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.
Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.
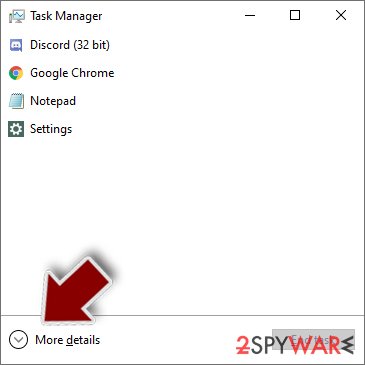
- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.
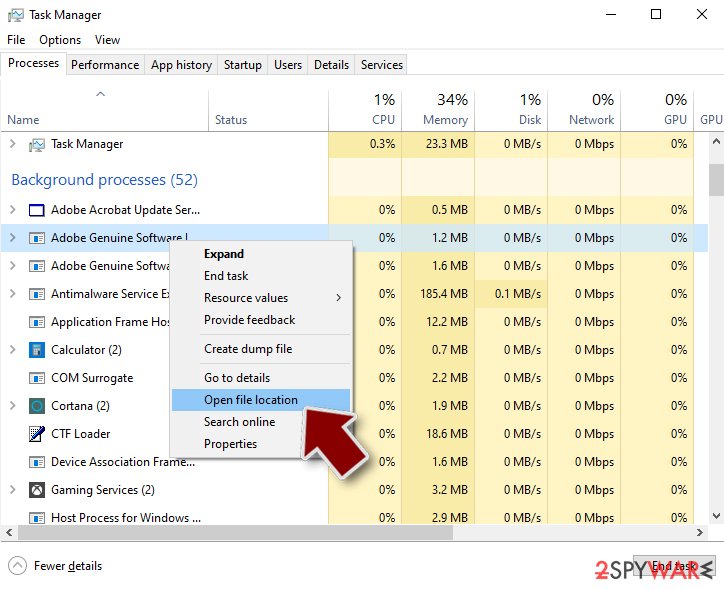
- Go back to the process, right-click and pick End Task.
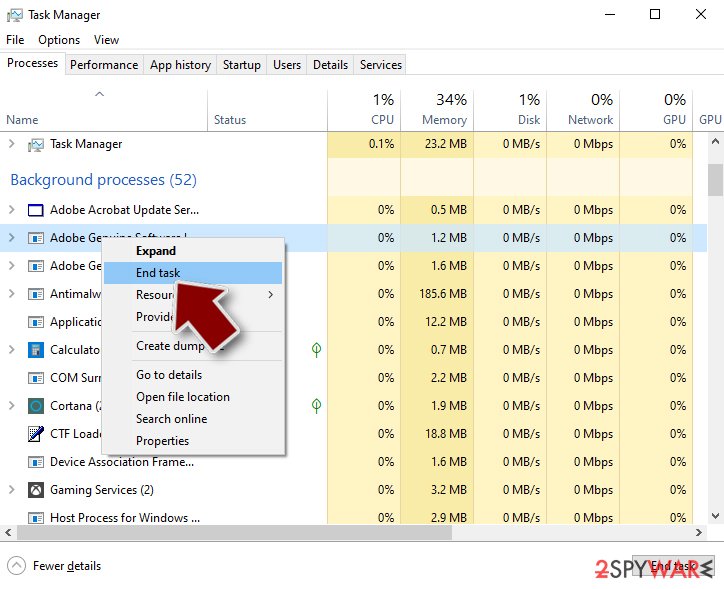
- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.
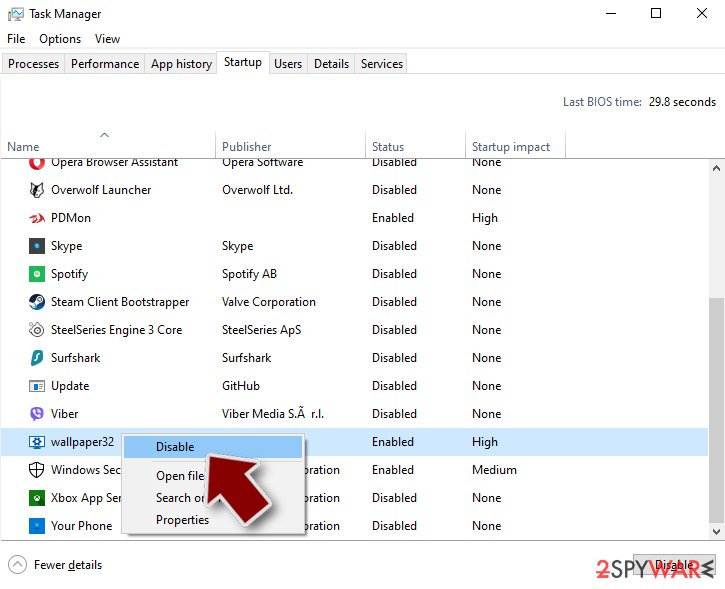
Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.
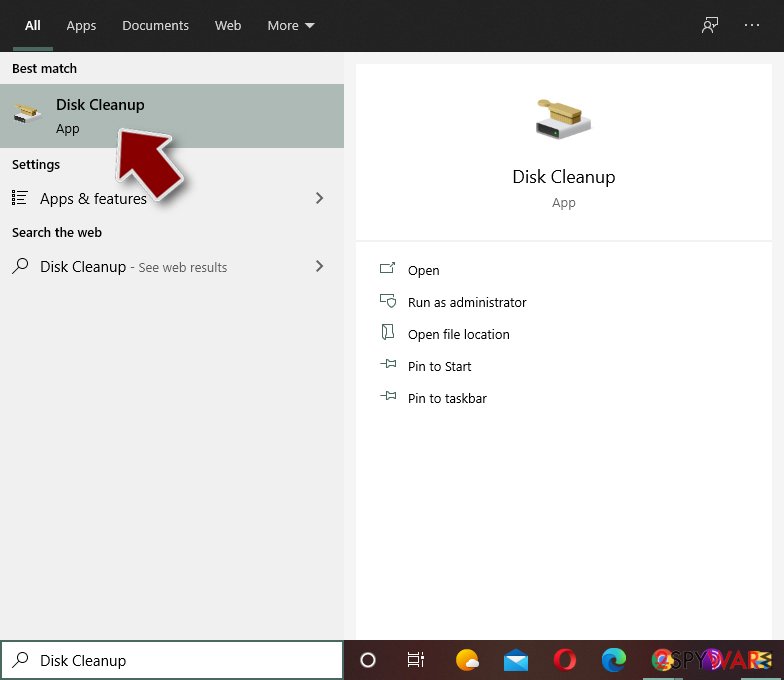
- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.
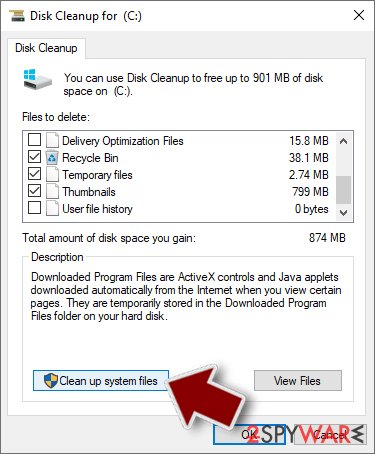
- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed the Windows Security detection Trojan:Win32/CryptInject!ml has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
Questions about Trojan:Win32/CryptInject!ml
What is Trojan:Win32/CryptInject!ml?
It is malware that acts in the background and can damage machines significantly. This detection name indicates a threat capable of injecting other malware payloads into infected systems. Trojans of this type are often used to distribute ransomware, data-stealing malware, and cryptocurrency miners.
The infection may not show obvious symptoms beyond the initial antivirus alert or results after a system check. Various viruses rely on these silent injectors as their primary spreading mechanism.
Is CryptInject silent and undetectable?
Yes, this trojan primarily operates silently without triggering noticeable symptoms. You may only notice the detection alert from your security tool or see it appear after a regular system scan.
The malware runs in the background causing system alterations and damage without clear warning signs. This silent nature makes it particularly dangerous, as users often remain unaware of infection until antivirus tools detect it. Immediate action upon detection is crucial to prevent extended damage.
What can this trojan do to my computer?
The infection can inject secondary payloads including ransomware, data-stealing malware, or additional trojans. The malware may interfere with system functions, files, and overall performance.
Issues such as speed problems, performance interruptions, crashes, or freezes might all be related to this infection. The trojan can disable security software, alter registry entries, and modify startup preferences. Without removal, the machine becomes increasingly compromised.
How does CryptInject!ml enter systems?
The malware primarily distributes through infectious files in emails, hacked websites, and similar online material. Torrent sites, pirating services, peer-to-peer platforms, and free download sites commonly distribute trojans bundled with seemingly legitimate software.
Phishing and social engineering tactics trick users into downloading infected files. Misleading or deceiving pages present download links that contain trojan payloads. Malicious actors employ multiple distribution methods to reach maximum numbers of potential victims.
How do I remove Trojan:Win32/CryptInject!ml?
Use anti-malware or security software to perform a full system scan that automatically detects and removes all infection pieces. Reboot into Safe Mode with Networking to prevent the trojan from interfering with the removal process.
After removal, run a system optimization or repair tool to fix virus damage and corrupted files. Verify the infection is completely eliminated by running another scan with your security software. Professional anti-malware tools offer the most reliable removal approach.
Should I use System Restore after removal?
Yes, System Restore can be helpful for removing trojans and their related damage. This feature allows you to recover your machine to a previous state before the infection occurred.
Run System Restore after the antivirus has detected and removed the malware. Following System Restore, run your anti-malware tool again to ensure complete removal and no lingering threats remain.
What about virus damage after removal?
Trojans often cause permanent damage to system files, registry entries, and settings that removal alone cannot fix. After antivirus removal, run a system optimization or repair tool to identify and fix corrupted files and registry issues.
These tools can repair virus damage and restore normal system functions. However, if critical files were severely corrupted, you may need professional assistance or system reinstallation in extreme cases.
How can I prevent CryptInject infections?
Download software only from official and verified websites, avoiding third-party download sources. Be cautious with email attachments and verify sender identities before opening files. Run anti-malware tools regularly to detect infections early before significant damage occurs.
Keep your operating system and software updated with security patches. Do not visit suspicious websites or download files from untrusted sources, and maintain regular backups of important data.
Will Fortect remove Trojan:Win32/CryptInject!ml?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Trojan:Win32/CryptInject!ml, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- CSOonline: What is cryptojacking? How to prevent, detect, and recover from it (read October 5, 2026)
- Wikipedia: Social engineering (read October 5, 2026)
- Dieviren: Dieviren (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)