
WeTransfer virus: what it is and how to remove it
Wetransfer virus uses fake emails impersonating WeTransfer to distribute Kryptik trojan that steals passwords and banking credentials. The platform itself is legitimate.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If WeTransfer virus keeps coming back after uninstalling, a scan can find what reinstalls it.
Do it yourself · free Remove WeTransfer virus yourself 5 steps, about 15 minutes, no software needed.
Start the steps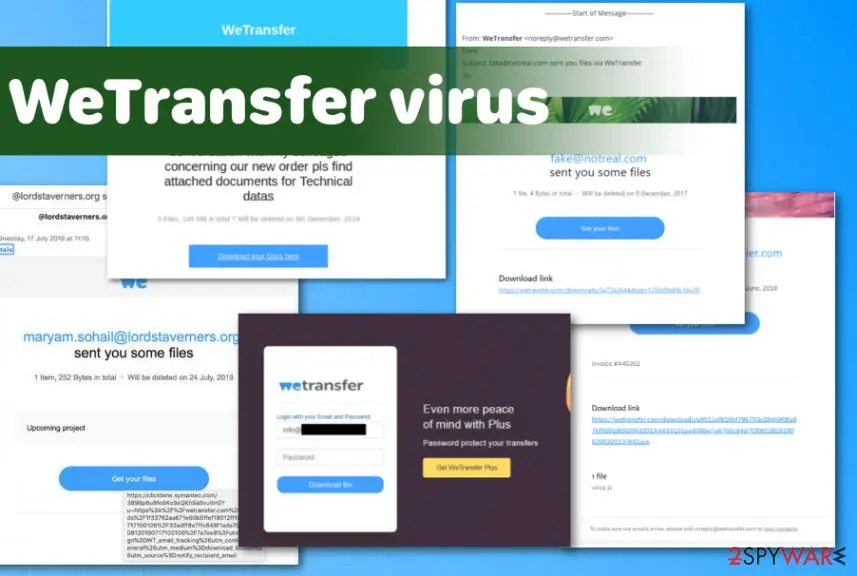
WeTransfer virus: summary
| Distribution | Social engineering campaigns allow malicious actors to obtain email addresses of people, data leaked during some security incidents and other deceptive methods allow to access such details, so various random users online receive these malicious emails with malware delivering links and file attachments |
|---|---|
| Name | WeTransfer virus |
| Type | Malware delivering email campaign/ Trojan |
| Tactics | Emails with claims about purchase details, company messages, and other requests get sent to random people and include links to file transfer platform where the people get to download archived data or an executable file malware payload |
| Spreads | It is known for delivering the payload of Kryptik trojan |
| Danger | This phishing campaign[2] can easily spread various malware and lead to hacker attacks or campaigns of data exfiltration and so on. Viruses that spread via these stealthy methods can be set to damage machines and perform other background processes |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Symptoms | An unknown program in Installed apps |
| Evidence | 5 write-ups by security sites; details still limited |
| First seen | 13 January 2021 |
| Facts checked | 5 October 2026 |
What WeTransfer virus does on an infected PC
From our report of Jan 2021 · not reviewed since
Wetransfer virus is the malicious email campaign that sends malware via WeTransfer platform
Wetransfer virus - the campaign that involves deceptive emails designed to spread various malicious programs.
Links to file downloads and even files attached to the email notification itself trigger the installation of Kryptik trojan. Text presented in these emails can go from purchase details or letters from companies or organizations, claiming about confidential business documents, contracts or legal documents and financial records, that can be commonly passed between recipients via email, so it is not causing suspicions initially.
Links that supposed to lead to bundles with important documents lead to the infection Download link states "Our company profile as requested" or "Purchase Order_PDF.cab", so people launch the download of a malicious executable or an archived file. The whole WeTransfrer service is completely legitimate and safe to use, but this phishing campaign ruins the name for the whole industry of cloud services.
The most important thing to note about this WeTransfer Email virus is that anything can be sent to you via those file transfer links, so opening any of them and following with download can lead to trojan infections and even more serious issues regarding the personal privacy and security of your device.
The trojan that is, reportedly, distributed with the help of these spam campaigns is a password-stealing trojan that also can be considered banking malware because the most valuable credentials are the ones linked to online banking sites.
This high-risk malware can possibly have a wide range of abilities and be set to take control of your device and exfiltrate data or damage the machine entirely. You need to be cautious and react to this infection as soon as possible, so crucial damage can be avoided.
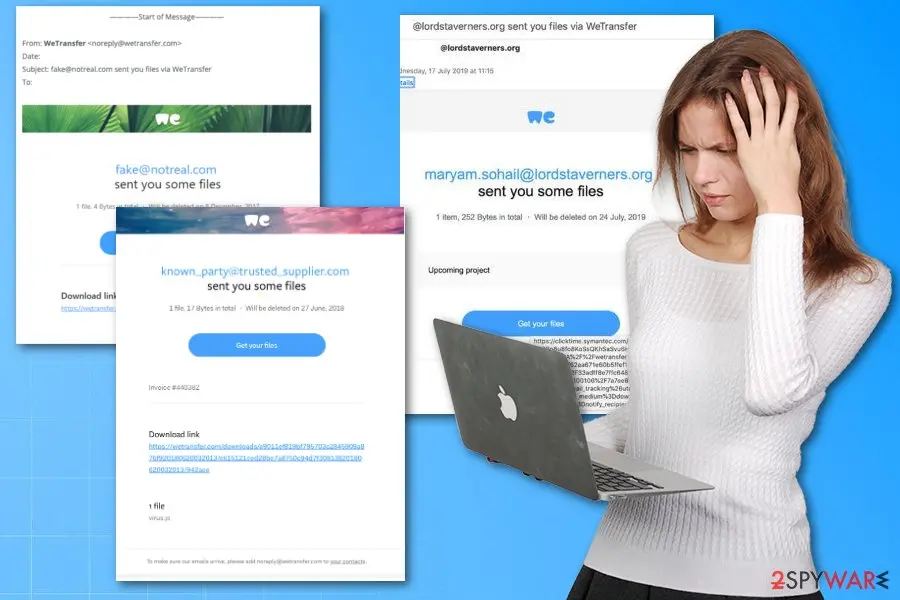
WeTransfer Email virus message can include banners, logos, and other identifiable information that resembles the legitimate platform to fake the secureness and legitimacy and trick people into downloading attached files this way. The email itself is a brief text about the file that is included in the download link.
Recipients who click on the provided link are led to the login page of the WeTransfer platform, and this is where phishing begins because this landing page is the form where you fill in the information and trigger the malicious installation.
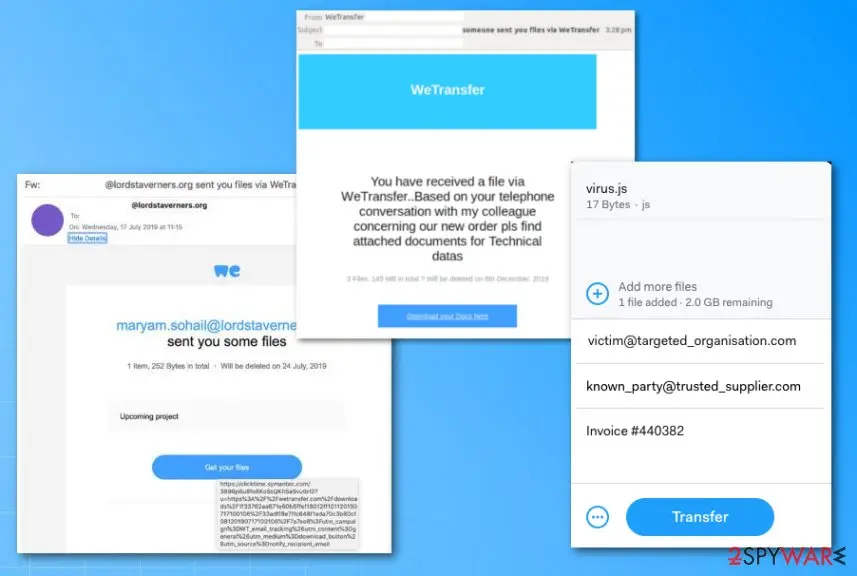
Users who encountered the Wetransfer virus message stated that once the information is put in the message states about incorrect password and the phishing stops here. The message looks like this:
Additionally, the Wetransfer virus relies on other methods that help to look like genuine notifications. High-quality graphical elements, branding, and logos allow them to mimic the popular file-sharing platforms and take advantage of more gullible people.
The email intrigues and tells receivers that a new file is arriving after the phone conversation or additional exchange of emails. Driven by their curiosity, people follow the suggestion to click on the provided link.
You need to remove Wetransfer virus infection possibility by deleting the email as soon as you receive it, so there is no opportunity for the malicious payload to get triggered and dropped on the machine. If that happens you will need more powerful tools to tackle the malicious infection.
Trojans malware and even ransomware can get installed like this, so the only way to get back the machine in your control is anti-malware programs. Wetransfer virus involves various campaigns that even the officials have noted.
These platforms and services are not viewed as potentially dangerous bu email security gateways, so malicious campaigns are possible, unfortunately. These attacks start as phishing campaigns and similar social engineering-based events but lead to stolen credentials directly from the person and target machines with malware.
WeTransfer Email virus removal can get difficult if your device gets affected further by the malware delivered from the download link. Experts comment on these issues and possible phishing ploys helping to get users' attention:
When WeTransfer Email virus campaign results in the trojan, banking malware or another virus infection, you need to get involved in serious malware-fighting procedures with tools that can detect this malicious software.
The various analysis may show that the file ad link can be detected by AV tools before it goes on the machine, but you need to keep your anti-malware tools up-to-date, so the program is properly working. This is not the case for many people.
Keep the machine safe and avoid anything related to WeTransfer virus removal by using system optimization tools, security software like that can indicate suspicious emails, sites, and links for you before you trigger any infections. These spam emails can deliver anything and everything, and there are many versions of emails, notifications, links, and file transfer forms.
WeTransfer virus baiting techniques are trendy among malicious actors, and several active campaigns employed such methods to target sensitive information. HTML elements may get used to hiding malicious URLs from the antispam features of security software.
You may encounter advanced techniques and malware that show no symptoms, so rely on AV tools that are reliable and scan the machine fully to clean the system and get rid fo the virus damage.
From our report of Jan 2021 · not reviewed since
Spotting the difference between legitimate and phishing emails
If you are communicating with any services like this platform, you may fall for the phishing campaign and install the malicious program without considering to look out for red flags.
Opening the suspicious email notification alone can trigger the drop of the trojan or virus, so pay attention to:
You need to defend your inbox by practicing good common sense and keep these scammers in mind every time you receive a suspicious email. Keep proper security tools on the machine and run it occasionally on the system, so any possibly dangerous files get blocked in advance.
- the layout of the email and differences with previous emails;
- typos, grammar mistakes;
- what domain is on the link that you got redirected to;
- senders' address;
- attachments, links, and other active buttons on the email itself.
From our report of Jan 2021 · not reviewed since
More from our earlier report on WeTransfer virus
- WeTransfer virus removal is not the easiest procedure, but you can get the best results with anti-malware tools that manage to find and remove all kinds of files and applications that may get placed all over the machine during the infection
- You should also think about the damage that virus causes on an affected system, so get or a similar tool that repairs files or at least can help with system performance and optimization
- About WeTransfer ・ Help ・ Legal ・ Report this transfer as spam
- Here, the threat actor will often write a note stating that the file is an invoice to be reviewed.
How to remove WeTransfer virus
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Programs like WeTransfer virus add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 2: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after WeTransfer virus, its publisher or created on the day the problem started.Delete those folders, and check
C:\Program FilesandC:\Program Files (x86)too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of WeTransfer virus that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
WeTransfer virus can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Jan 2021 · not reviewed since
Remove Wetransfer virus with proper tools, so all trojans get terminated
You need to take this WeTransfer Email virus seriously and clean the machine from any possible intruder or malicious file, so there are no risks of getting hacked or lose data from the machine directly or by getting on phishing sites and providing your personal details to malicious actors.
To remove Wetransfer virus properly, you need to clear any suspicious emails from the inbox and make sure to delete them from the trash too. Resetting the browser may be optional, but also helpful when some of the redirects include PUPs and shady methods of exposing the user to dangerous sites.
Wetransfer virus removal gives better results, however, when you clean the whole machine. Get , , or and run a full system check to find and eliminate all possible threats. Some of the trojans and malware can block these apps, so rely on Safe Mode first and then run the anti-malware program.
[GI=method-1]You can reboot the machine in Safe Mode and try to eliminate Wetransfer virus this way
[GI=method-2]Clean the machine with the help of System Restore feature
After removal: passwords, accounts and prevention
Your passwords after WeTransfer virus
Removing WeTransfer virus does not undo what it may already have sent out while the PC showed weTransfer virus in the list of installed apps.
Treat saved browser passwords and logged-in sessions on this PC as known to the attacker.
From another device, change the e-mail password first and end all its sessions. Then do the same for the bank, PayPal, Microsoft, Google and Apple accounts. Stolen session cookies keep working after a password change until you sign out everywhere.
Move crypto to a new wallet created on a clean device. A step-by-step order for every kind of account is in our guide to account security after an infection.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about WeTransfer virus
What is Wetransfer virus?
Wetransfer virus is a malicious email campaign that abuses the legitimate WeTransfer file-sharing platform to distribute malware. The campaign involves deceptive emails designed to spread various malicious programs, primarily Kryptik trojan. Emails with claims about purchase details, company messages, confidential documents, or financial records include links to WeTransfer where recipients download archived files or executable malware.
The phishing campaign exploits user trust in the WeTransfer platform's legitimate status to bypass email security filters. While WeTransfer itself is completely legitimate and safe, this phishing campaign ruins the platform's reputation for security-conscious users. The trojan distributed through these campaigns is a password-stealing trojan that also functions as banking malware targeting valuable banking credentials.
How does Wetransfer virus spread?
The Wetransfer virus spreads through deceptive phishing emails sent to random people claiming to contain important documents, purchase orders, company profiles, or confidential business information. Emails reference common business communications likely to be shared between recipients, increasing the likelihood victims will click suspicious links.
Download link text states things like "Our company profile as requested" or "Purchase Order_PDF.cab" to appear legitimate. Recipients who click the link are directed to a phishing landing page resembling the legitimate WeTransfer website.
This fake page requests login credentials and may trigger malicious downloads. The whole campaign exploits social engineering to trick recipients into manually downloading malware. Email addresses are obtained through data leaks from security incidents or by other deceptive methods, making widespread targeting possible.
What trojan does Wetransfer virus distribute?
Wetransfer virus primarily distributes Kryptik trojan, a high-risk malware capable of stealing passwords and banking credentials. Kryptik is classified as both a password-stealing trojan and banking malware because it specifically targets credentials linked to online banking sites.
Banking credentials are extremely valuable to cybercriminals, enabling direct theft from victims' bank accounts. The trojan can have a wide range of abilities including device control, data exfiltration, and potential system damage.
Once installed, Kryptik runs silently in the background without obvious symptoms. The malware may also deliver additional payloads including ransomware, cryptocurrency miners, or other trojans depending on attacker intentions. Kryptik's capabilities make Wetransfer virus campaigns extremely dangerous to both personal and financial security.
How can I spot a Wetransfer phishing email?
Legitimate WeTransfer notifications come directly from the platform with official formatting and branding. Phishing emails impersonating WeTransfer may display high-quality graphical elements and logos to appear authentic. However, red flags include unexpected files from unknown senders, urgency language creating pressure to download immediately, and generic greetings like "Dear User" instead of personalization.
Email domains may use variations similar to legitimate addresses but contain extra words or numbers. Phishing messages often reference conversations you don't recall having or claim files arrive after phone calls you don't remember.
The message requests login information, which legitimate WeTransfer never does through email. The landing page URL may use confusing domain names trying to imitate the real site. When in doubt, contact the claimed sender directly through independent contact information rather than clicking email links.
What happens if I click a Wetransfer virus link?
Clicking a Wetransfer virus link redirects you to a fake WeTransfer login page where you're prompted to enter credentials. If you enter login information, criminals steal your email password, enabling access to your account and associated services.
Without entering credentials, some phishing pages automatically trigger malware downloads when you land on them. Downloaded files appear to be PDFs or archives but contain executable malware. Simply opening downloaded files may automatically execute the trojan, installing Kryptik on your computer.
Once installed, Kryptik steals passwords from your browser, financial accounts, and saved credentials. The trojan can also enable remote access for attackers to control your device and steal data directly. The longer the malware remains undetected, the more complete the compromise becomes.
What damage can Kryptik trojan cause?
Kryptik trojan can cause devastating damage through password theft and banking malware capabilities. Once installed, it steals passwords, usernames, and email credentials, enabling attackers to access your personal accounts including email, social media, and online services.
Banking credentials are extracted, allowing direct theft from bank accounts. The trojan may also enable cryptocurrency theft from digital wallets. Remote access capabilities allow attackers to control your device, browse your files, and exfiltrate sensitive documents.
Criminals may use your compromised device to send phishing emails on your behalf, spreading malware to your contacts. Your identity may be stolen and used for fraudulent purposes. Financial fraud can occur rapidly once banking credentials are compromised, making immediate action critical when infection is suspected.
How do I remove Wetransfer virus if already infected?
If you clicked a Wetransfer virus link and suspect infection, immediately disconnect your computer from the internet to prevent data exfiltration. Remove the computer from network access to limit malware communication with attacker servers. Boot into Safe Mode and run reputable antimalware software like Microsoft Defender offline scan mode, which scans before the operating system fully loads.
A comprehensive full system scan in Safe Mode has the best chance of detecting and removing Kryptik trojan. After removal, change all passwords for critical accounts from a different, clean computer—do not change passwords on the infected computer as the trojan records keystrokes.
Contact your bank immediately to report potential compromise and monitor accounts for unauthorized transactions. Enable fraud alerts with credit agencies. Consider identity theft protection services.
How do I prevent Wetransfer virus infection?
Delete suspicious emails immediately upon receipt without opening attachments or clicking links, especially from unknown senders claiming to send files. Never enter login credentials on pages reached through email links—always navigate directly to legitimate websites using trusted bookmarks or typed URLs.
Verify file arrivals by contacting the claimed sender through independent contact information. Be extremely cautious with business emails from unfamiliar companies, especially those requesting downloads or credential entry. Keep your antivirus software updated with real-time protection enabled to block malware downloads before installation.
Use strong, unique passwords for each online account so stolen credentials limit damage. Enable two-factor authentication on critical accounts like email and banking for extra security. Be skeptical of email urgency tactics and threats claiming immediate action is required.
Will Fortect remove WeTransfer virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For WeTransfer virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Threatpost: Popular File-Sharing Service WeTransfer Used in Malicious Spam Campaigns (read October 5, 2026)
- Wikipedia: Phishing (read October 5, 2026)
- Virustotal: Malicious email link AV detection (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)