
Windows AntiBreach Module ads: what it is and how to remove it
Windows AntiBreach Module is a malicious application, which hails from a huge family of threats that is called FakeVimes. When it infiltrates computer, this virus starts displaying fake system scanners and pop-up notifications that are set to report about tens of different viruses.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like Windows AntiBreach Module usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove Windows AntiBreach Module ads yourself 5 steps, about 15 minutes, no software needed.
Start the steps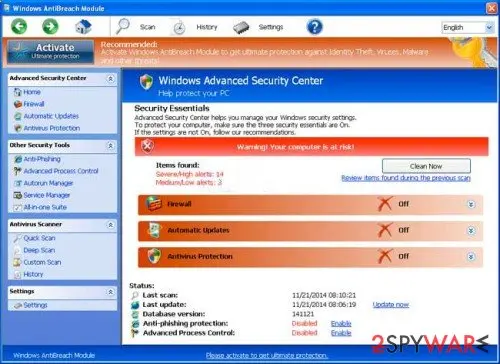
Windows AntiBreach Module ads: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | Windows AntiBreach Module |
| Type | Ad-supported program |
| Symptoms | An unknown program in Installed apps |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 4 more facts
| Evidence | One write-up by a security site; details still limited |
|---|---|
| Program | Windows AntiBreach Module |
| First seen | 26 April 2021 |
| Facts checked | 7 October 2026 |
Is Windows AntiBreach Module ads dangerous?
From our report of Apr 2021 · not reviewed since
What is Windows AntiBreach Module?
Windows AntiBreach Module is a malicious application, which hails from a huge family of threats that is called FakeVimes.
When it infiltrates computer, this virus starts displaying fake system scanners and pop-up notifications that are set to report about tens of different viruses. We must admit that its alerts look very convincing. Nevertheless, you have to realize that they are fake. By showing people warnings about different kinds of viruses, Windows AntiBreach Module seeks to scare them into thinking that they need to purchase its licensed version.
If you don't want to lose your money, you should never do that. Besides, you should get rid of this rogue anti-spyware as soon as you can because it may cause not only fake alerts reporting about invented cyber threats. Windows AntiBreach Module can also be used for spreading other viruses, so it can lead you to the infiltration of other cyber threat.
In addition, it can also start tracking you by recording your keystrokes. This is very dangerous because it can lead you to the loss of your personally identifiable information. Please, stay away from Windows AntiBreach Module virus as far as you can! If you believe that your PC has already been affected, you should run a full system scan with and get rid of this threat.
From our report of Apr 2021 · not reviewed since
How can Windows AntiBreach Module infect my computer?
It hasn't been revealed that Windows AntiBreach Module uses updated distribution methods, so the main method which is used for spreading this threat around relies on fake alerts and spam campaigns. The easiest way to fall into infecting your PC with the cyber threat is by clicking on various pop-up ads that show up during browsing sessions.
Some of these alerts claim that user should update his/hers Java, Flash Player or other program, others offer checking computer for viruses with 'online scanner'. Please, avoid such notifications because all what they seek is to trick you into downloading Windows AntiBreach Module or other potentially unwanted program/virus!
If you have been convinced that your Flash Player or other program is outdated, then you should go to its official website and look for updates. If you have been convinced that you should check your PC with some free scanner, then you should scan it with , , or other reputable anti-spyware.
We say so because there is no such thing as online scanner. If Windows AntiBreach Module virus manages to infiltrate computer. the main thing that it initiates is such and similar alerts:
Please, avoid such alerts because they seek the only thing - make you think that you need to buy Windows AntiBreach Module's licensed version. Instead of spending your money on nothing, you should follow a guide below and remove this rogue.
From our report of Apr 2021 · not reviewed since
More from our earlier report on Windows AntiBreach Module
- It is recommend to activate the protection and perform a thorough system scan to remove the malware.
- Error Software without a digital signature detected.
- Your system files are at risk.
- We strongly advise you to activate your protection.
How to remove Windows AntiBreach Module ads
How to remove Windows AntiBreach Module
Uninstall first, then remove what stays behind, so the ads do not come back after a restart.
Step 1: Uninstall Windows AntiBreach Module
Open Settings > Apps > Installed apps in Windows 11, or Settings > Apps > Apps & features in Windows 10.
Sort the list by install date and find Windows AntiBreach Module, then choose Uninstall from the three-dot menu next to it (in Windows 10, click the entry and then Uninstall).
Remove anything else installed on the same day that you do not recognise, because such programs usually arrive together in one installer. If the uninstaller opens a browser page with an offer or a survey, close it: the program is removed either way.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 2: Remove it from startup
Whatever Windows AntiBreach Module installed usually starts with Windows.
Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Reset the browser
Finish the browser part with a reset, which puts the search engine, start page, new tab page and site permissions back to their defaults and switches extensions off. Chrome: Settings > Reset settings > Restore settings to their original defaults.
Edge: Settings > Reset settings. Firefox: Help > More troubleshooting information > Refresh Firefox, which also removes its extensions. Your bookmarks and saved passwords are kept, and the menus are the same on Windows 11 and Windows 10.
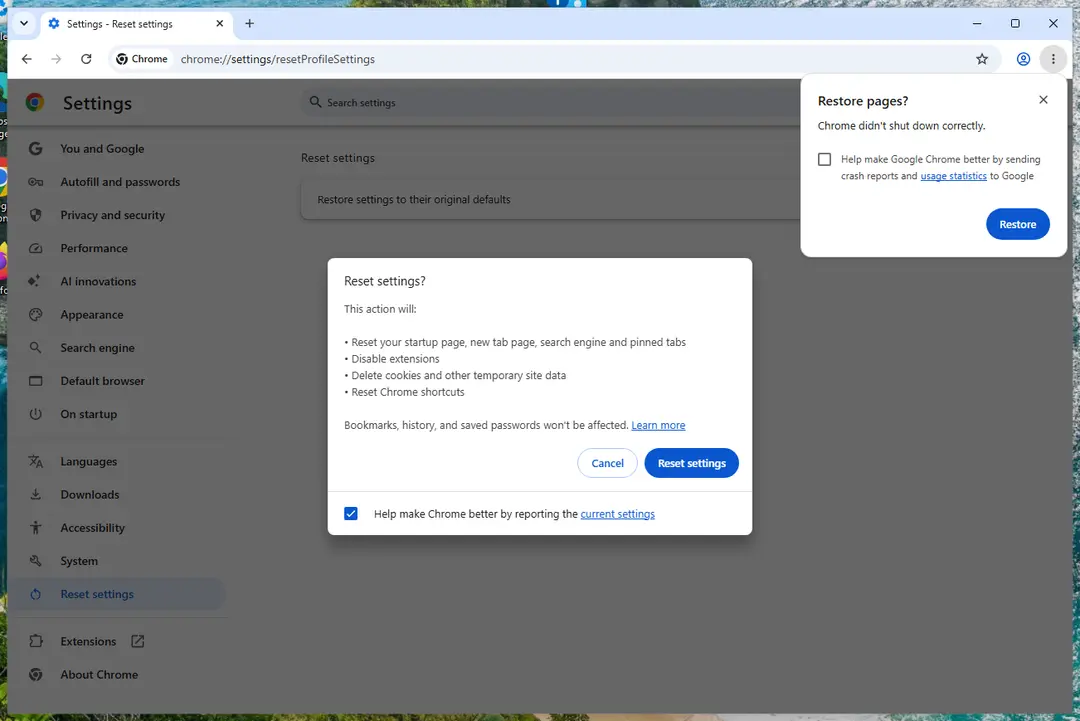
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
From our report of Apr 2021 · not reviewed since
How to remove Windows AntiBreach Module virus?
If you noticed Windows AntiBreach Module's alerts, then your PC has already been infected.
Please, don't waste your time because this virus can be used for various malicious activities. You will have to download a reputable anti-spyware, update it and run a full system scan. This will help you to avoid system damage and other issues. If you need a detailed guide explaining how to download and install anti-spyware, read this guide.
ATTENTION! If you can't download or launch any them, try these options:
1. USING SYSTEM RESTORE TO DISABLE VIRUS:
If you are using Windows 8, then follow these steps:
2. REBOOTING TO SAFE MODE WITH NETWORKING:
3. CREATING GUEST ACCOUNT FOR SCANNING COMPUTER:
If you have another user (guest) account, you can try to run a full system scan from it. You just need to log into it and download for a full system scan. You can activate your guest account with a help of these steps:
4. USING ANOTHER PC FOR DOWNLOADING ANTI-SPYWARE:
5. BLOCKING WINDOWS ANTIBREACH MODULE BEFORE A SCAN:
- Click Start -> All Programs -> Accessories -> System Tools -> System Restore.
- As soon as Restore system files and settings window shows up, select Next.
- Choose the restore point that you want and click Next .
- Click Finish to confirm and wait until your PC reboots.
- Now download and run a full system scan after updating it.
- Go to the Windows 8 Start Screen and type restore point in the Search section.
- Now click on Settings -> Create a restore point.
- When in System Protection tab, select System Restore.
- Click Next button to see your restore points and left click on the entry you need.
- Now select Scan for affected programs -> Close -> Next -> Finish.
- Once your PC reboots, download and run a full system scan after updating it.
- Restart your computer
- As soon as your computer becomes active, start pressing the F8 key continuously until you see Advanced Boot Options screen.
- Here, select Safe Mode with Networking (for that, use the arrow keys) and then hit Enter.
- Login as the same user as you were in normal Windows mode
- Now right click on IE or other browser's icon and select Run As or Run As administrator. Enter your Administrator account password (if needed).
- Enter this link to your address bar: https://www.2-spyware.com/download/hunter.exe and download a program on your desktop. Launch it to remove malicious files.
- Click Start -> Control Panel and select User Accounts and Family Safety.
- After a new window shows up, click on Add or Remove User Accounts -> Guest Account.
- Now click on Turn On button and restart your computer
- Now wait until you see Windows log on screen and select Guest account for downloading recommended anti-spyware.
- Take another computer that is not infected by this virus and download or to it.
- After completing the procedure, transfer this anti-malware to the CD/DVD, external drive, or USB flash drive.
- In the meanwhile, kill malicious processes on your infected computer. For that you can use this tutorial.
- Stick the device you used for transferring anti-spyware program to your infected PC and launch it.
- Let Windows AntiBreach Module start its work and finish its fake system scan.
- Click on Allow unprotected and close the warning message.
- Open File Explorer (click Start -> Documents) and enter %AppData% in the location bar. Click enter.
- Rename guard-agas or similar entry.
- Reboot your machine and enter this link to your address bar: https://www.2-spyware.com/download/hunter.exe
Questions about Windows AntiBreach Module ads
What is Windows AntiBreach Module and why is it on my PC?
Windows AntiBreach Module is a program that was installed on the PC, most likely together with something else you downloaded. Free software sites and many installers add extra programs on setup pages with pre-ticked boxes, so the extra install looks like your choice even though nobody read the page.
Check the install date in Settings, Apps, Installed apps: the program you installed that day is the probable carrier. If you do not need Windows AntiBreach Module, uninstall it. If it belongs to your hardware or to a program you use, search its exact name and publisher first, because drivers and their tools can have unfamiliar names.
Windows AntiBreach Module came back after I uninstalled it. Why?
Something else is reinstalling it. Common causes are a second program from the same publisher, a scheduled task that downloads it again, or a browser extension that keeps prompting for it. Sort Installed apps by install date and uninstall each entry from the same day that you did not choose.
Then open Task Scheduler and look in the Task Scheduler Library for tasks with updater-style names that you do not recognise. Check Startup apps in Task Manager too. If Windows AntiBreach Module still returns, start Windows in Safe Mode, uninstall it there and run a Microsoft Defender offline scan, which looks for loaders that ordinary scans can miss.
Is uninstalling Windows AntiBreach Module enough?
Often, but not always. Uninstalling Windows AntiBreach Module through Settings > Apps > Installed apps removes the main part. Ad-supported programs, however, frequently arrive together with others from the same installer, and some leave a scheduled task or a browser extension behind.
After uninstalling, sort the list of installed apps by date and look at what else appeared that day, check Task Manager > Startup apps, and open the extension page in every browser. A Microsoft Defender full scan at the end catches leftover files.
Can an adware pop-up infect my PC just by appearing?
No. A pop-up, a notification or a new tab is only a web page or a message. It cannot run programs on Windows by itself, provided the browser and Windows are up to date. Infection needs a step from you:
- running a downloaded file
- installing an extension
- giving a stranger remote access
That is why scam pages work so hard to make you click. Close such pages with the tab's X or by closing the browser, not with buttons inside the page, which may start a download.
Why is my browser so slow since the ads started?
Each page now does extra work. An adware extension reads the page, decides where to put ads, loads them from ad servers and reports your visit, and that happens on every tab. Ad-supported programs add their own background activity.
Removing the extension or program usually makes the browser fast again at once. If it stays slow, open the browser's own task manager with Shift+Esc in Chrome or Edge and look for extensions using a lot of memory or processor time.
I let a "support technician" from an ad connect to my PC. What should I do?
Act quickly but calmly. Disconnect the PC from the internet first, so the connection ends. Uninstall the remote access tool they asked you to install and check Installed apps for anything else added during the call.
Run a Microsoft Defender full scan and offline scan. From another device, change your e-mail and banking passwords and sign out of all sessions.
If you paid by card, bank transfer or gift card, contact your bank or the card issuer immediately, and report the scam to the police. Do not answer if they call back.
My scan found nothing, but the ads continue. Why?
Because the source may not be a file a scanner looks for. Browser notifications are a permission stored in the browser, and many adware extensions are not flagged because they come from an official store.
Some ad-supported programs are only reported if you enable detection of potentially unwanted apps. So a clean scan does not mean the job is done. Check each browser's notification permissions and extension list by hand, and turn on Potentially unwanted app blocking in Windows Security before scanning again.
Did Windows AntiBreach Module collect my data?
Adware typically collects what it needs to choose ads:
- the sites you visit
- search terms
- approximate location
- browser and system details
Extensions with permission to read and change data on all websites can technically see everything on those pages, including forms. That is a privacy problem rather than proof of theft.
If you typed card details or passwords while it was active, changing the most important passwords is a reasonable precaution. Clearing cookies after removal ends the tracking sessions it may have started.
Will Fortect remove Windows AntiBreach Module?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Windows AntiBreach Module, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 7, 2026)
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 7, 2026)
- Microsoft Learn: How Microsoft names malware (read October 7, 2026)