
Xxx ransomware (.xxx files): what it is and how to recover
Xxx ransomware is a GlobeImposter variant that encrypts your files, adds .xxx to their names and leaves a note called how_to_back_files.html asking you to e-mail the criminals. We found no public decryptor confirmed for it, so the plan is to clean the PC first and recover from copies.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Make sure nothing will rename more files to .xxx: an automatic scan checks the PC first.
Do it yourself · free Remove Xxx ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps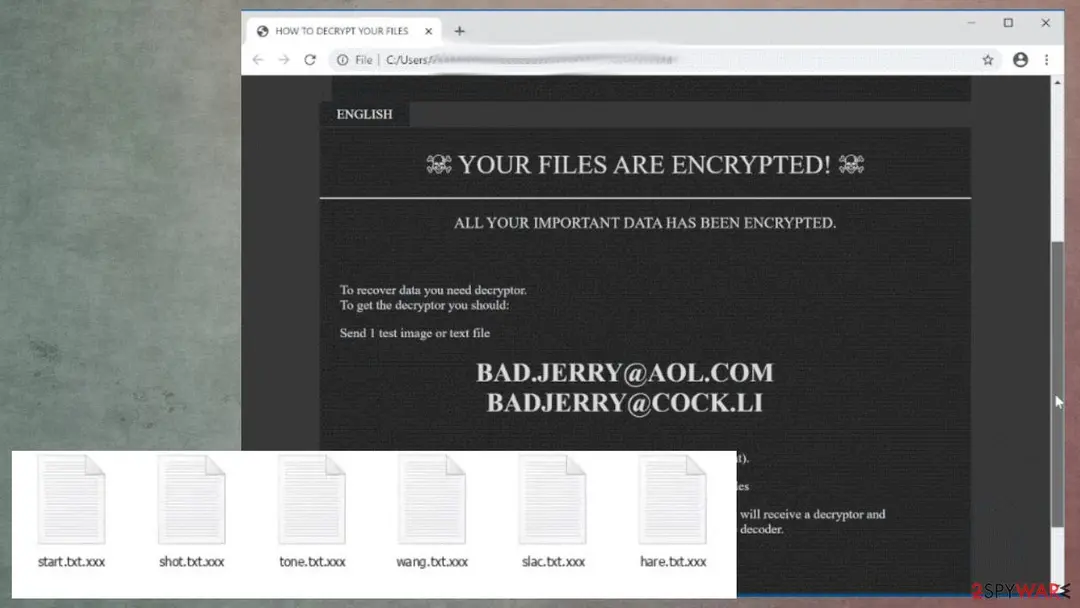
.xxx added to their names.Xxx ransomware: summary
| Type | Ransomware, GlobeImposter family: encrypts files and adds .xxx |
|---|---|
| Risk | High: files are encrypted and the originals' safety nets (shadow copies) are probably deleted |
| Symptoms | Files renamed .xxx, how_to_back_files.html in every affected folder, a personal ID and two contact e-mails |
| How to get rid of it | Disconnect, copy files, Safe Mode, Microsoft Defender full and offline scan, then restore from backup; see the plan |
| Our check | Source check on 6 October 2026 (PCrisk, Microsoft, Emsisoft, AhnLab, SentinelOne); we did not run the malware |
| First seen | Family 2016 to 2017; our first report on .xxx 9 April 2021 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 15 more facts
| Encrypted file extension | .xxx, for example 1.jpg.xxx |
|---|---|
| Ransom note | how_to_back_files.html, quoted in full below |
| Decryptor | No public tool confirmed for .xxx; Emsisoft's 2016 GlobeImposter tool not confirmed |
| Contact | bad.jerry@aol.com and badjerry@cock.li |
| Detection names | Microsoft Defender: Ransom:Win32/Globeimposter (family name, none known for this exact sample). Avast Win32:RansomX-gen; BitDefender Generic.Ransom.GlobeImposter.64DACDB0; ESET Win32/Filecoder.FV; Kaspersky HEUR:Trojan.Win32.Generic |
| Name | Xxx ransomware |
| Evidence | 0 write-ups by security sites; no sample analysed yet |
| Encrypted files | .xxx |
| Example | 1.jpg.xxx |
| Attacker contacts | bad.jerry@aol.com and badjerry@cock.li |
| Free decryptor | No free decryptor is known (checked 6 October 2026) |
| Microsoft Defender name | Ransom:Win32/Globeimposter |
| Distribution | Typically cracked programs, keygens and game cheats, fake installers, e-mail attachments, and Remote Desktop with weak passwords in small offices |
| Damage | Files on the PC and connected drives encrypted, restore points often deleted, sometimes a password stealer installed as well |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against PCrisk, Microsoft, Emsisoft, No More Ransom, AhnLab and SentinelOne. We did not run a sample, so the behaviour is the family's and is marked where we could not confirm it for the .xxx version.
What Xxx ransomware is
Xxx ransomware is a Windows file encryptor from the GlobeImposter family: it adds .xxx to your file names, drops how_to_back_files.html in every folder it touched, and tells you to e-mail the criminals for a price.
The old name "BadJerry" comes from the first contact address in the note. The same .xxx ending has appeared with other addresses, so the extension alone does not say who is behind your infection.
- Family
- GlobeImposter, a copycat of the older Globe ransomware (Emsisoft, Microsoft)
- Extension added
.xxx, after the original name and extension- Encryption
- AES for the files and RSA for the AES key, as the family does (Microsoft)
- Our first report
- 9 April 2021
Our 2021 report called the note a "pop-up window"; it is a file, so save it.
How the story went
23 December 2016
Emsisoft's first decryptor
Emsisoft's page covers the first version: files ending
.crypt. Microsoft dates the discovery to a May 2017 spam campaign; the dates differ, so we give both.9 April 2021
Our first report on
.xxxWe described the extension, the HTML note and its two contacts.
February 2023
AhnLab links the family to MedusaLocker
AhnLab reports MedusaLocker operators spreading it, probably over Remote Desktop.
6 October 2026
Our recheck
We cannot confirm that new infections still use
.xxx.
What we checked and what we did not
No website is involved and we did not run the malware, so this is a check of sources, and a source check clears nothing.
Xxx ransomware · source check · 6 October 2026
- Note textRead from PCrisk's copy of
how_to_back_files.htmland matched to our 2021 screenshot. - Behaviour of this versionNot tested by us; startup entry, key file and shadow-copy deletion come from other variants.
- DecryptorEmsisoft's tool is for the 2016 version; we could not confirm it accepts
.xxx.
Treat it as real The note is genuine GlobeImposter wording and the family encrypts for real. Plan for lost files.
Is it this one? Four signs to check
What to look for on the PC
- File namesDocuments and pictures end in
.xxx, for example1.jpg.xxxorstart.txt.xxx. - The note
how_to_back_files.htmlin the same folders, headed "YOUR PERSONAL ID". - The contacts
bad.jerry@aol.comandbadjerry@cock.li, or another pair: the same extension has appeared with other addresses. - Not thisFiles ending
.crypt,.djvuor a long.id-...pattern belong to another family with another tool.
Act now Two of the first three signs mean the files are encrypted. Cleaning the PC will not change the ending, so copy everything first.
Which name will your scanner show?
Microsoft's name for Xxx ransomware is Ransom:Win32/Globeimposter.
Defender sorts threats by category first, so the word before the colon tells you what kind of program was found, even if the family name means nothing to you.
Do not search for a removal tool by the detection name alone; fake "removal tools" use the same keywords. How the naming works is explained in our guide to antivirus detection names.
- Path:
1.jpg.xxx - File extension:
.xxx - Note file:
how_to_back_files.html - Contact:
bad.jerry@aol.com and badjerry@cock.li
One extension, several notes
Our 2021 report showed three notes.
Each lists different contacts, so compare contacts and note name before you look for a decryptor.
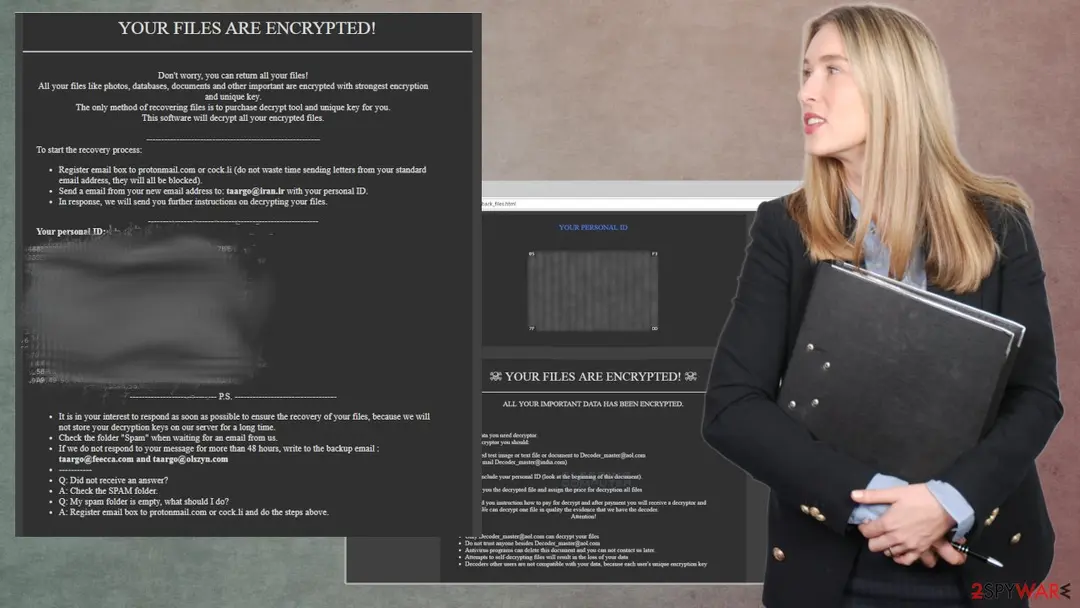
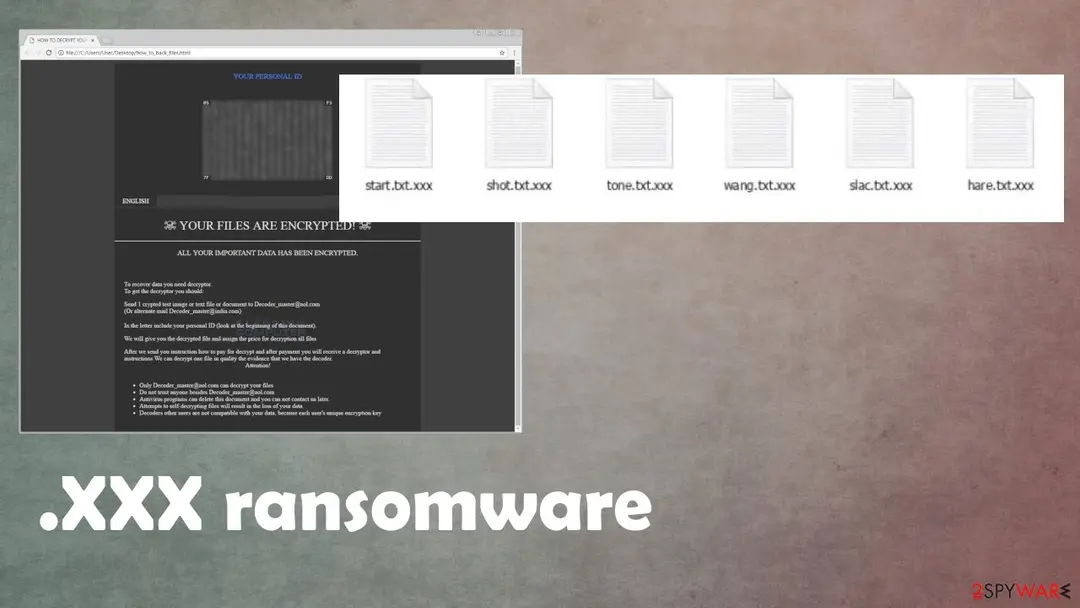
.txt.xxx pattern.Do not write to any of the addresses.
How Xxx ransomware behaves
What it does on the PC
We did not run a sample of this version. The steps come from Microsoft's description of one GlobeImposter variant and AhnLab's analysis of another, so the .xxx version may differ.
Start
Copy and startup entry
Microsoft lists a copy named
svchost.exeinAppData\Localand aRunOnceentry calledBrowserUpdateCheck.Start
Key file
A file named with a 64-character hash goes into
C:\Users\Public; the encryption skips it.End
Safety nets deleted
A batch file runs
vssadmin.exe Delete Shadows /All /Quiet, clears saved Remote Desktop entries and every Windows event log (Microsoft).End
The program deletes itself
So a scan that finds nothing does not mean your files are safe.
Our 2021 guide said the infection can stay quiet while it encrypts; Microsoft lists only a slowdown.
How it reaches PCs
No source documents the delivery of this exact sample.
These are the routes our 2021 guide and the sources name for the family.
- High
Spam with an attachment
Fake bills and DHL or FedEx notices with a macro or script; SentinelOne names 2017 waves with 7-Zip archives holding JavaScript.
- High
Remote Desktop, weak password
AhnLab ties a recent wave to MedusaLocker operators who log in this way.
- Medium
Cracks and torrents
You cannot control what is packed with a crack or keygen (PCrisk, our 2021 guide).
Was anything stolen?
Nothing we read says this note came with data theft, but a person may have been on the PC, so treat passwords as exposed.
- Medium
Other malware
PCrisk warns that password-stealing trojans can arrive with ransomware.
- Medium
Credential tools
AhnLab found Mimikatz and a port scanner beside GlobeImposter in a Remote Desktop attack; unknown for
.xxx.
The Xxx ransomware note
What a ransom note left in folders said
YOUR PERSONAL ID
YOUR FILES ARE ENCRYPTED!
ALL YOUR IMPORTANT DATA HAS BEEN ENCRYPTED.
To recover data you need decryptor.
To get the decryptor you should: Send 1 test image or text file to BAD.JERRY@AOL.COM and BADJERRY@COCK.LI
In the letter include your personal ID (look at the beginning of this document).
We will give you the decrypted file and assign the price for decryption all files.
Do not attempt to remove the program or run the anti-virus tools
What the note says and what it wants
The note asks for no money at first: it asks for a test file and your ID, and the price comes in the reply.
| The note says | Our reading |
|---|---|
| "To recover data you need decryptor" | Each infection has its own key, so the claim is plausible; paying is a different question |
| "Send 1 test image or text file" | The free test is the hook: it proves nothing about the rest |
| "Do not attempt to remove the program or run the anti-virus tools" | Pressure, not a technical fact: removal does not touch the files, and skipping it leaves the infection in place |
Can Xxx ransomware files be decrypted?
Can the .xxx files be decrypted?
Probably not for free. A free GlobeImposter tool exists, but it is for the 2016 version, and we could not confirm that it accepts .xxx files.
| Source | What it says |
|---|---|
| Emsisoft decryptor | Built December 2016 for .crypt files and the note HOW_OPEN_FILES.hta; needs one encrypted file and its unencrypted twin |
| No More Ransom | Lists that same Emsisoft tool under GlobeImposter Ransom |
| PCrisk | .xxx files cannot be decrypted without a tool held by the criminals |
| SentinelOne | Later versions came out after Emsisoft's tool, with no public decryptor |
- 1
Copy the files first
Run nothing on the only copy.
- 2
Find an unencrypted twin
An e-mail attachment, a phone or a cloud copy of one of the files.
- 3
Try the tool on a copy
Drag the pair onto the decryptor; if it refuses, nothing is lost.
- 4
Keep the encrypted copies
Tools and leaked keys are added over time.
Should you pay?
No. The note gives no price and no guarantee, and PCrisk says victims who pay are scammed: no tool arrives, even after payment.
Do
- Keep the note and the addresses for a police report
- Check No More Ransom now and then
Don't
- Do not e-mail the contacts or send them a test file
- Do not pay a third party who promises to decrypt
A decrypted test file shows only that they hold a key for that file.
How to remove Xxx ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove Xxx ransomware and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so Xxx ransomware cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
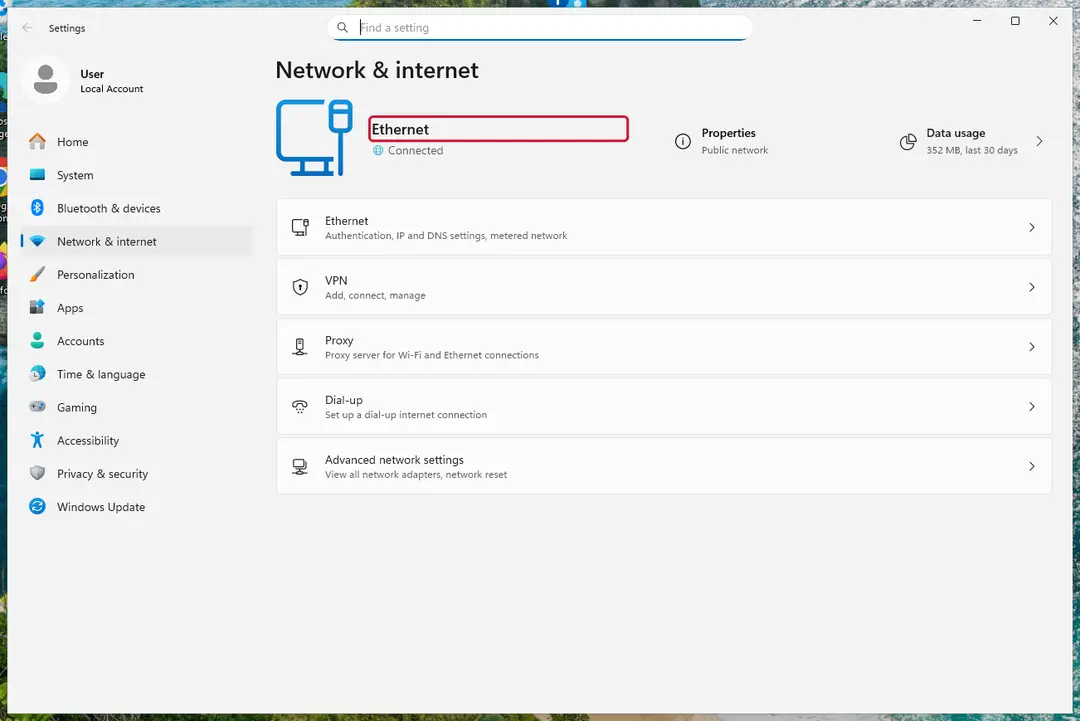
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Your files now end in
.xxxand the instructions are inhow_to_back_files.html. Save both to a USB stick, a copy of the note and two small encrypted files, before anything else.On another device, check them with ID Ransomware or Crypto Sheriff: the family name decides which decryptor, if any, can help. Keep the note's ID and contact line for your report.
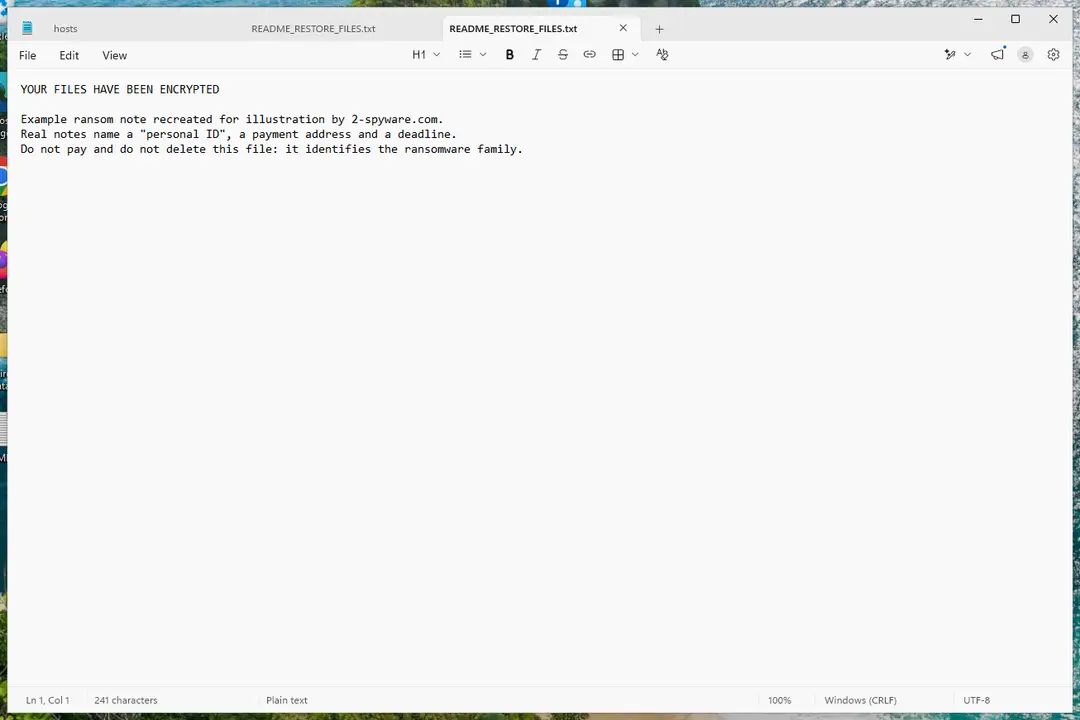
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for Xxx ransomware, no free decryptor is known (checked 6 October 2026). Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing Xxx ransomware does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
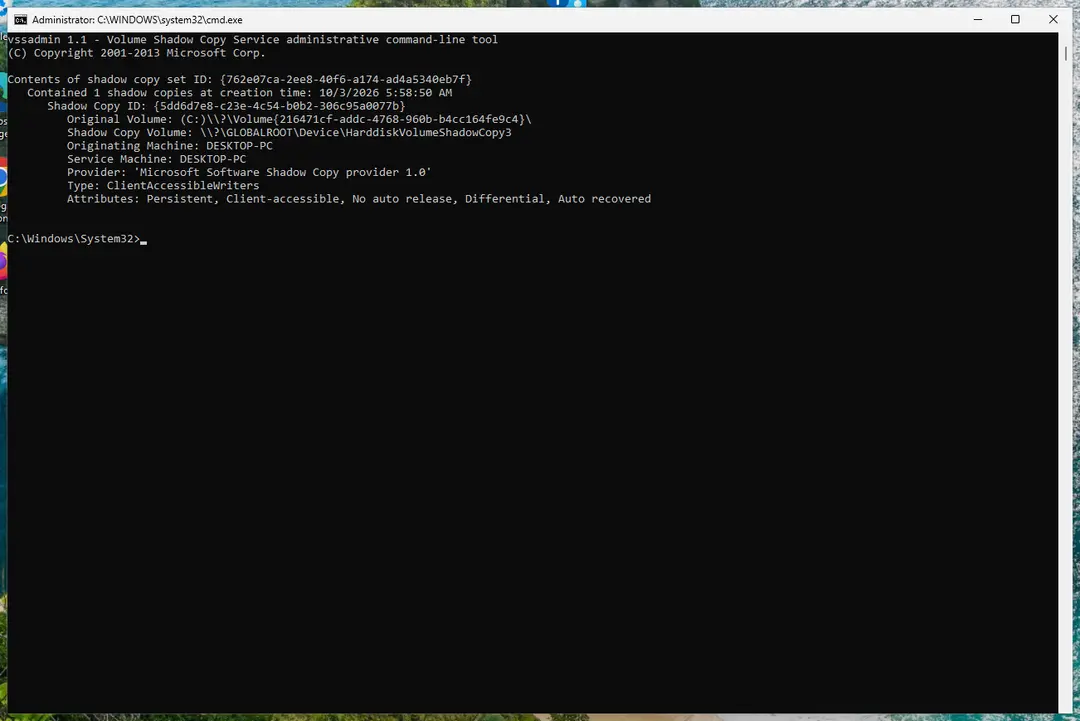
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that Xxx ransomware deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Safe Mode and the scan, in order
Removal stops new encryption; it does not decrypt anything, and restored files would be locked again if the program were still there.
- 1
Start Windows in Safe Mode with Networking
Windows 11: Settings > System > Recovery > Advanced startup > Restart now. Windows 10: Settings > Update & Security > Recovery > Restart now. Then Troubleshoot > Advanced options > Startup Settings > Restart, and press 5.
- 2
Scan twice with Microsoft Defender
Windows Security > Virus & threat protection > Scan options: run Full scan, then Microsoft Defender Antivirus (offline scan).
- 3
Look for the family's files
Microsoft lists an
svchost.exein%LocalAppData%for another variant; unconfirmed for.xxx, so treat a find as a lead. - 4
Change passwords from a clean device
Do this before you reconnect any backup drive.
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Make the next attack harmless
Xxx ransomware could only hurt the files that had no second copy, and the signs (files that end in .xxx and no longer open) showed exactly which ones those were.
The 3-2-1 rule fixes that:
- three copies
- two media
- one disconnected
A practical version for a home PC: OneDrive or another cloud backup with version history, plus an external disk that you plug in once a week for File History and then unplug. Test a restore now and then by opening a few files from the backup on another device.
Details, schedules and what not to back up are in our 3-2-1 backup guide for Windows.
How to prevent Xxx ransomware and the next attack
Do
- Turn on Controlled folder access under Virus & threat protection > Manage ransomware protection
- Close Remote Desktop to the internet, or use a long password and two-step sign-in
- Check a sender's address before you open an invoice or parcel notice
Don't
- Do not run cracks or keygens
- Do not open archives or scripts from unexpected mail
Questions about Xxx ransomware
How do I open .xxx files?
You cannot open .xxx files with any program until they are decrypted. The ransomware adds the ending to each locked file and encrypts the contents, so renaming 1.jpg.xxx back to 1.jpg does nothing. Copy the files to a USB drive and keep them.
A free decryptor exists for the 2016 GlobeImposter version, but we could not confirm that it accepts .xxx. Otherwise the way back is a backup, a cloud version-history copy, or an older copy you e-mailed or put on a phone, because those were never encrypted.
Is there a decryptor for Xxx ransomware?
Probably not a public one for this version. Emsisoft published a GlobeImposter decryptor in December 2016 and No More Ransom lists it, but its page describes files ending .crypt and a note called HOW_OPEN_FILES.hta.
SentinelOne says the authors answered with a new version without a public decryptor, and PCrisk says .xxx files need a tool only the criminals hold. We did not test Emsisoft's tool on .xxx. If you have an encrypted file and its unencrypted twin, try the tool on a copy; if it refuses, keep the copies and check again later.
Should I pay the ransom or e-mail bad.jerry@aol.com?
No, do not write to the addresses and do not pay. The note gives no price: it asks for a test file and your personal ID and sets the sum after that. A decrypted test file proves only that they hold a key for that file.
PCrisk says victims who pay are scammed and receive no tool, and sending the test file confirms that your address is read and that you will pay. Keep the note and the addresses for a police report instead.
Do paid decryption services work for .xxx files?
Mostly not. PCrisk says decryption is exceedingly rarely possible without the criminals, so a service that offers it is likely a scam or a go-between who pays the same criminals and adds a fee.
The one real exception is a free public tool for your exact version, and we could not confirm one for .xxx. Before you pay anyone, check No More Ransom, which lists free tools, and ask the service in writing which key or tool it will use.
Is Xxx ransomware the same as BadJerry and GlobeImposter?
Yes, one thing under three names. GlobeImposter is the family, a copycat of the older Globe ransomware (Emsisoft). .xxx is the ending this version adds.
BadJerry is taken from the first contact address, bad.jerry@aol.com. The same ending has appeared with other contact addresses, in notes we show on this page, so the extension does not say which operator hit you. Compare the note name and addresses before you look for a tool, because a tool for one version will not fit another.
How did Xxx ransomware get on my PC?
We cannot tell for this sample, because no source documents its delivery. PCrisk lists e-mail attachments, torrent sites and malicious ads.
For the family, SentinelOne names spam with archives holding a script, and AhnLab names Remote Desktop logins guessed by brute force. Our 2021 guide listed fake delivery notices and cracks. Ask yourself which fits:
- a program you ran
- an attachment you opened
- a PC with Remote Desktop open to the internet
The answer decides what to close before you restore anything.
Will deleting the ransomware bring my files back?
No. Removal stops new encryption but does not decrypt files already locked. Microsoft says the program deletes itself when it finishes, so the files may be all that is left.
A full Microsoft Defender scan and the offline scan are still worth running, because they find leftovers and other malware, and a restored backup would otherwise be encrypted again. Files come back only from a key, a tool that fits your version, or a copy such as a backup or a cloud version history. Clean first, then restore.
Was my data stolen by Xxx ransomware?
Nothing we read says it was. The note mentions no stolen data and no site that publishes it. PCrisk warns that password-stealing trojans can come with ransomware, and AhnLab found Mimikatz and a port scanner beside GlobeImposter in a Remote Desktop attack, so a person may have been on the PC.
We cannot say that happened here. Treat passwords as exposed: from a clean device change your e-mail, bank and cloud passwords, then the Windows account, and turn on two-step sign-in.
Will Fortect remove Xxx ransomware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Xxx ransomware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- PCrisk: Xxx ransomware (read October 6, 2026)
- Microsoft Security Intelligence: Ransom:Win32/Globeimposter (read October 6, 2026)
- Emsisoft: GlobeImposter decryptor (read October 6, 2026)
- No More Ransom: decryption tools (read October 6, 2026)
- AhnLab ASEC: GlobeImposter ransomware being distributed with MedusaLocker via RDP (read October 6, 2026)
- SentinelOne: GlobeImposter ransomware (read October 6, 2026)
- Microsoft Support: Windows startup settings (Safe Mode) (read October 6, 2026)
- Microsoft Support: Virus and threat protection in the Windows Security app (read October 6, 2026)