
89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ: what it is and how to remove it
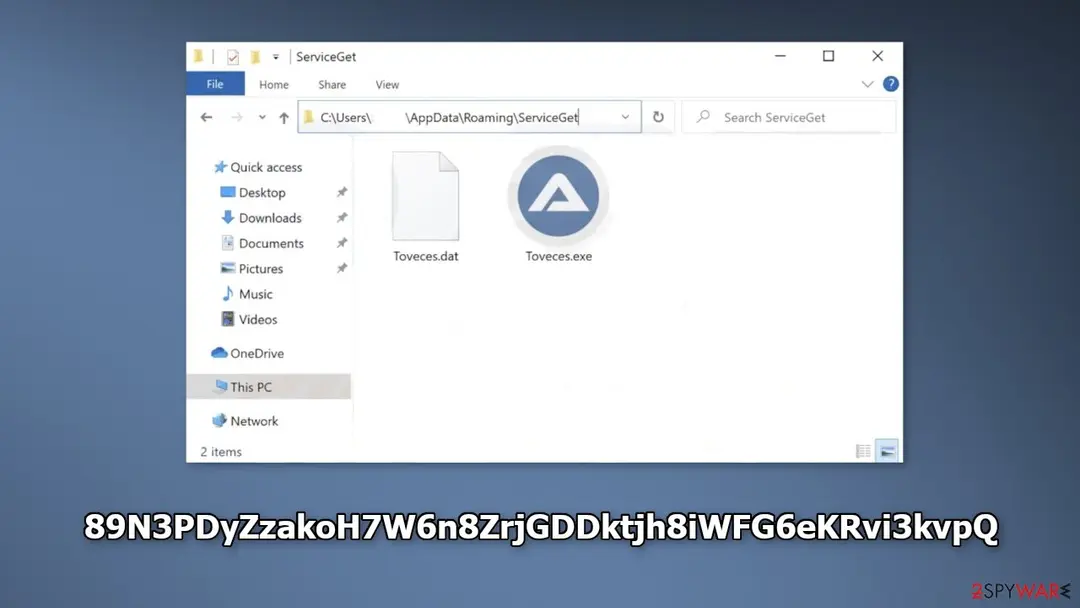
If 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ is the string that appears every time you copy and paste any text, you are affected by a malicious program. It changes the clipboard data so that the output would be the string of numbers and letters which is a cryptocurrency wallet address.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Unsure whether ReimageRepair.exe is safe? A free scan checks the file and what starts it.
Do it yourself · free Remove 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ yourself 6 steps, about 18 minutes, no software needed.
Start the steps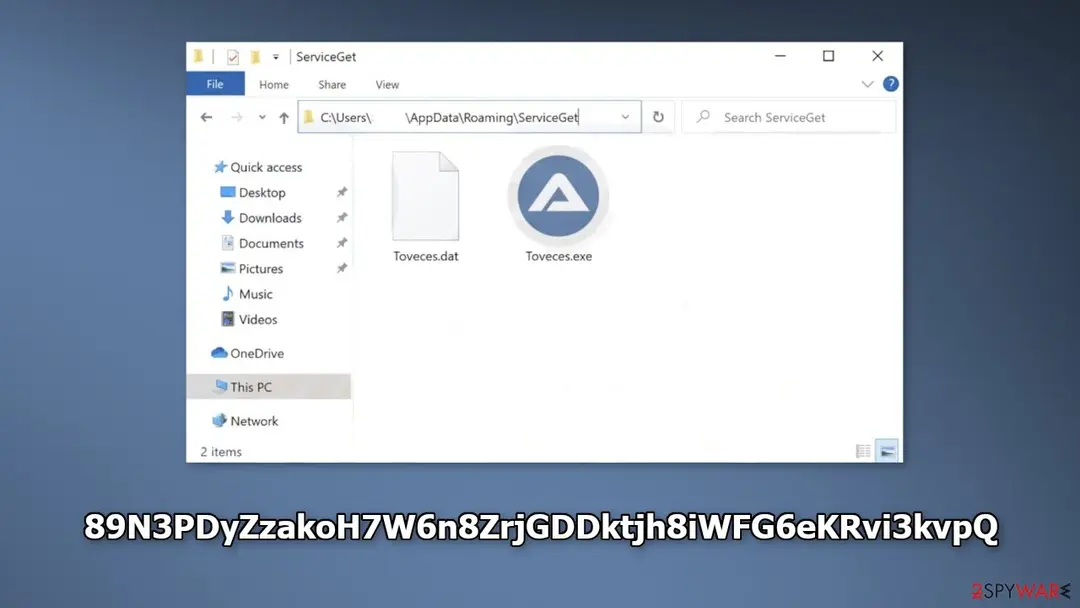
89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ: summary
| Distribution | Torrent websites; "cracked" software; malicious links |
|---|---|
| NAME | 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ |
| TYPE | Malware |
| SYMPTOMS | When users paste something into their clipboard, the text changes into a string of letters and numbers; people could also experience an increased amount of commercial content and changed browser settings |
| DANGERS | The malware can come with bundled software that could cause the installation of other malicious programs and PUAs |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Damage | Not recorded in the old report |
|---|---|
| Name | 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ |
| Type | Loader |
| Symptoms | An unknown process in Task Manager |
| Evidence | 4 write-ups by security sites; details still limited |
| File names | ReimageRepair.exe |
| First seen | 30 March 2022 |
| Facts checked | 7 October 2026 |
What 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ does on an infected PC
From our report of Mar 2022 · not reviewed since
89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ malware can change the text in your clipboard
If 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ is the string that appears every time you copy and paste any text, you are affected by a malicious program.
It changes the clipboard data so that the output would be the string of numbers and letters which is a cryptocurrency wallet address.
More sophisticated clipboard hijackers can detect when a user is performing a cryptocurrency transaction and change the address into its own seamlessly. In this case, a user would be sending his cryptocurrency to crooks instead of his own wallet.
Because this is a simple version of a clipper-type malware, users can notice that something is wrong pretty quickly as the copied text changes no matter if it is a URL or an article.
However, the clipper malware is not the only thing users should be worried about. Often, installations of malicious programs include other hidden viruses. Therefore, users may experience system infections, serious privacy issues, financial losses, and even identity theft. We highly recommend running a complete system scan and removing all detected threats.
From our report of Mar 2022 · not reviewed since
Stop the malicious background process
You can stop the disruptive copy/paste actions performed by the 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ malware by ending the process in the Task Manager:
Check program Startup
Terminating the process will not remove the program itself. Therefore, we strongly advise you to continue with our guide to remove the malware completely.
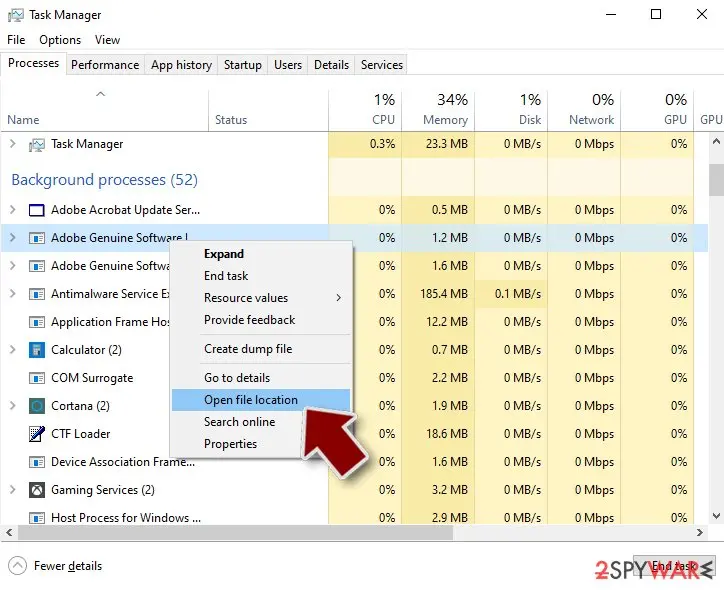
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.
- Right-click and select Open file location.
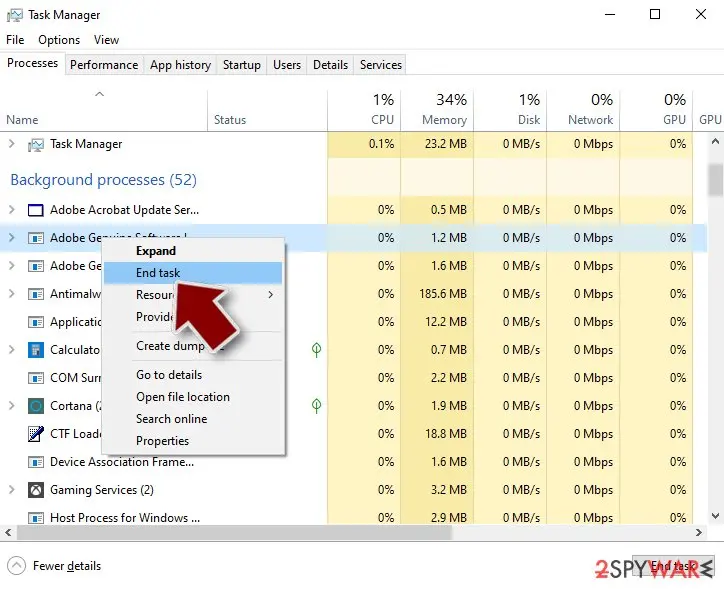
- Go back to the process, right-click and pick End Task.
- Delete the contents of the malicious folder.
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on AutoIt v3 Script (32 bit) and pick Disable.
From our report of Mar 2022 · not reviewed since
More from our earlier report on 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ
- Follow our guide to learn how to remove malware with professional security tools
How 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ got on your PC
From our report of Mar 2022 · not reviewed since
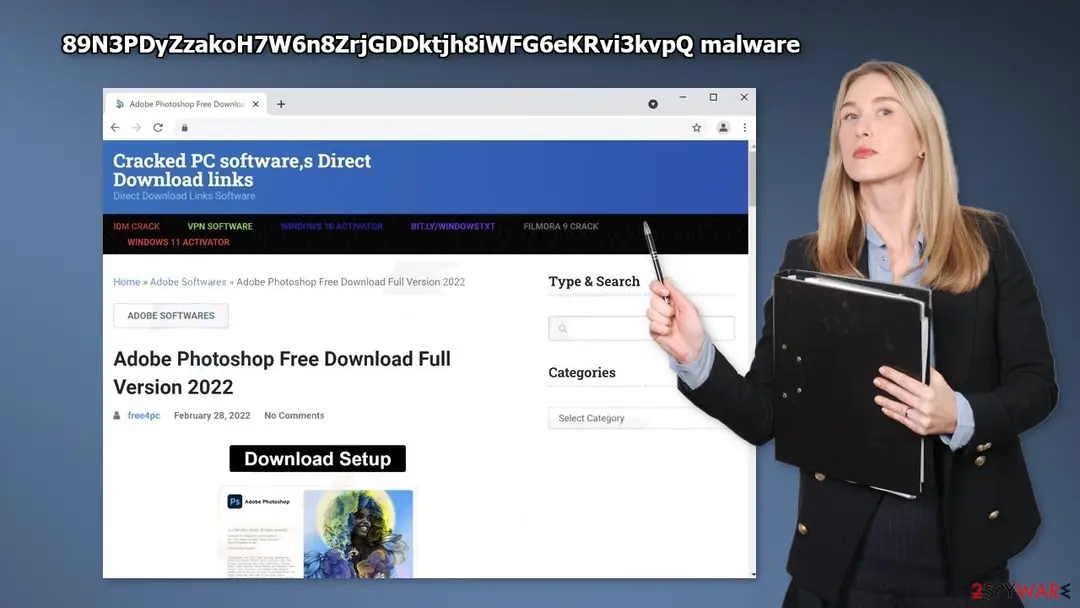
The clipboard hijacker was found to be spread through "cracked" software distribution platforms, Torrent websites, peer-to-peer file-sharing platforms.
These platforms often distribute malware because they are unregulated. Users have no way of knowing if the program they want to install is actually what the site says it is.
Such platforms also often include bundled software in the installers, like browser hijackers, adware, and other types of PUPs (potentially unwanted programs). However, they can also hide malware like Trojans, ransomware, etc. You should use only official web stores and developer sites whenever you want to install software.
Even though it might get costly, you may save in the long run by keeping your system running smoothly. You should also implement security measures during the installation process to keep the risk of infection to a minimum.
Always choose the "Custom" or "Advanced" installation methods, read the Privacy Policy and Terms of Use. The most important part is to check the file list and untick the boxes next to any unrelated programs.
How to check the PC for 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ
- File:
ReimageRepair.exe
How to remove 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where ReimageRepair.exe runs from and stop it
In Task Manager (Ctrl + Shift + Esc) find
ReimageRepair.exeon Processes, right-click it and choose Open file location before ending anything.Windows' own files live in
C:\Windows\System32; the same name in%AppData%, %Temp% or C:\Users\Public is an impostor. If the folder is wrong, right-click the process again, choose End task and delete the file.If it starts again within seconds, a task or another process restarts it, so run the scan step in Safe Mode. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Programs like 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 3: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
A scan finds the parts of 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

From our report of Mar 2022 · not reviewed since
Remove malware and PUPs from your machine
Since the clipboard malware was found to be distributed bundled together with other PUAs and malware, you should clean your system thoroughly.
PUPs can be disguised as "handy" tools that look like system optimizers, browser extensions, antivirus programs, etc.
Regular users often fail to identify these unwanted applications as they are designed to look unsuspicious. Manual removal can also sometimes result in the renewal of infection as users often do not remove all the related files and entries.
These anti-malware tools will completely eliminate the malicious processes running in the background and will warn you in the future if a suspicious program will try to enter the system. However, if you still want to do this yourself, you can follow the steps below:
Instructions for Windows 10/8 machines:
If you are Windows 7/XP user, proceed with the following instructions:
- Enter Control Panel into Windows search box and hit Enter or click on the search result.
- Under Programs, select Uninstall a program.
- From the list, find the entry of the suspicious program.
- Right-click on the application and select Uninstall.
- If User Account Control shows up, click Yes.
- Wait till uninstallation process is complete and click OK.
- Click on Windows Start > Control Panel located on the right pane (if you are Windows XP user, click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
- Pick the unwanted application by clicking on it once.
- At the top, click Uninstall/Change.
- In the confirmation prompt, pick Yes.
- Click OK once the removal process is finished.
From our report of Mar 2022 · not reviewed since
Repair the damaged operating system
Performance, stability, and usability issues, to the point where a full Windows reinstall is required, are nothing unusual after a virus infection.
These types of intruders can alter the Windows registry database, damage vital bootup, and other sections, delete or corrupt DLL files, etc. Once a system file is damaged, antivirus software cannot fix it.
Manual troubleshooting of such damage is also very complicated and can take a long time. This is why was developed. It can fix a lot of the damage caused by an infection like this.
Blue Screen errors, freezes, registry errors, damaged DLLs, etc., can make your computer completely unusable. By using this actually useful maintenance tool, you could prevent yourself from having to reinstall WIndows completely.
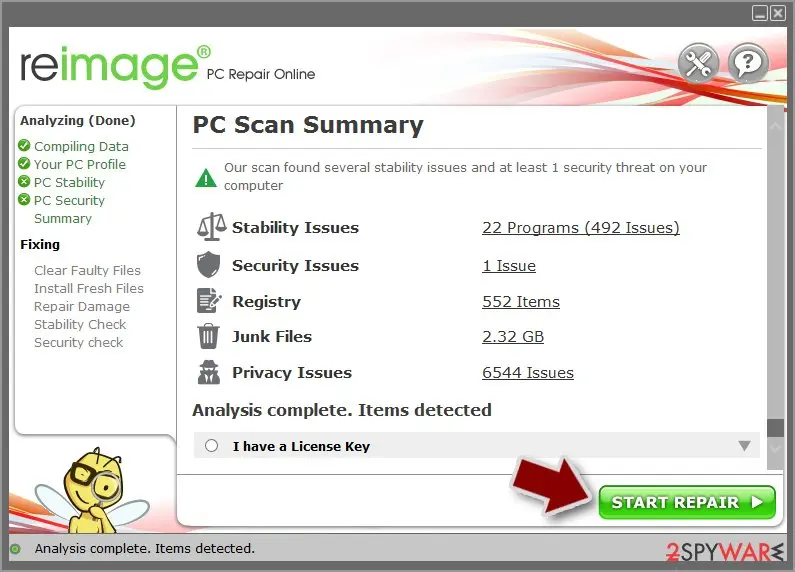
- Download the application by clicking on the link above
- Click on the ReimageRepair.exe
- If User Account Control (UAC) shows up, select Yes
- Press Install and wait till the program finishes the installation process
- The analysis of your machine will begin immediately
- Once complete, check the results - they will be listed in the Summary
- You can now click on each of the issues and fix them manually
From our report of Mar 2022 · not reviewed since
Fix browser issues
Since the clipper malware might have been bundled together with browser hijackers, you should also repair your browsers.
Browser hijackers are mild infections compared to malware but they can lead to more serious problems. Users who are infected by a browser hijacker might experience a changed homepage, new tab address, and search engine.
Some may also notice an increased amount of commercial content, like redirects, or push notifications. These advertisements can contain links leading to dangerous websites, resulting in personal information disclosure to fraudsters and more installations of PUPs and malware.
If you experience any of this erratic behavior, you can look for instructions on how to deal with it below this article. Guides are available for Google Chrome, Mozilla Firefox, and MS Edge.
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed an unfamiliar process called ReimageRepair.exe in Task Manager has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
Questions about 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ
Is ReimageRepair.exe a virus?
The name ReimageRepair.exe is not enough to say. Malware often uses technical-sounding names, and harmless updaters often use odd ones. Check three things:
- the folder the file runs from
- the Digital Signatures tab in its properties
- the program that starts it (Startup apps, Task Scheduler or services)
A signed file from a company whose product you use is almost certainly fine. An unsigned file in a user folder that no installed program explains should be removed, and the PC scanned with Microsoft Defender in offline mode.
ReimageRepair.exe keeps coming back. What should I do?
A process that returns after you end it has a restart mechanism, and that is a reason to treat ReimageRepair.exe as unwanted. Check Settings > Apps > Startup, Task Scheduler and the Services list for entries pointing to its folder, and disable them.
Look in Installed apps for anything added the same day and uninstall it. Then delete the folder and run a Microsoft Defender Offline scan, which works before Windows starts and can remove files that are locked or hidden while the system is running.
I found AnyDesk or ScreenConnect that I did not install. Is that 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ?
Not necessarily 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ, but it is a warning sign. These are legitimate remote support tools, and criminals use them as ready-made backdoors, especially after tech support scams or fake invoice calls.
If you did not install it and no one you trust set it up, uninstall it, change passwords from a clean device and check your bank account. If someone connected to your PC through it, follow the steps for remote access trojans and consider a Windows reset. Installed apps sorted by date shows when it appeared.
Can I keep using the PC while 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ is on it?
Not for anything that matters. As long as the program behind an unfamiliar process called ReimageRepair.exe in Task Manager runs, it can see what you type and what the browser stores, and it may download more malware. Disconnect the PC from the internet while you remove it, and do your banking, e-mail and password changes from another device.
Once the offline scan finds nothing and the sign does not return after a few restarts, normal use is fine. If the scan keeps finding new items, or you cannot remove the startup entry, a reset of Windows is the safer choice.
How do I know if my PC has 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ?
Often you do not, which is the point of a trojan. Possible signs are an antivirus alert naming 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ or a generic trojan detection, unknown programs or scheduled tasks, processes with random names in Task Manager, browser extensions you did not add, security settings turned off, slower performance, or account alerts about logins from unknown places.
The reliable check is a full scan followed by Microsoft Defender's offline scan. If you recently ran a crack, a fake installer or a command a website told you to paste, scan even without symptoms.
My antivirus was on. How did a trojan get past it?
Antivirus programs see a file only when it is written or run, and criminals test each new build against popular scanners before release. Detection catches up within hours or days, which is often after the first victims ran it.
Archives with passwords, installers that fetch the malware later, and scripts run through PowerShell make the job harder. That is why behaviour such as downloading cracks or pasting commands matters more than any setting. Keep Windows and Defender updated, and turn on Reputation-based protection in App & browser control.
Should I check my other computers too?
Yes, it takes little time and removes doubt. 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ itself usually stays on one PC, but the download that carried it may have been copied to other computers, shared drives may hold the same installer, and an attacker who had access could have tried saved passwords on other devices.
Run a full scan on every Windows PC in the home or office, check shared folders for the original download, and change Wi-Fi and router passwords if they were stored on the infected machine.
Why can't I find 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ in antivirus databases?
Because it is new or because it is listed under a different name. Antivirus companies name threats after the family they belong to, and a program that appears as 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ on your PC may carry a generic or unrelated label in their databases.
Many new samples are first detected only by behaviour, without a family name. What you saw, an unfamiliar process called ReimageRepair.exe in Task Manager, is enough to act on:
- end the program
- remove its startup entry
- run a Microsoft Defender offline scan
- secure your accounts
A detection name from a scan is worth noting for later.
Should I report 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ?
Report it if you lost money, if accounts were taken over, if you are a business, or if the trojan came through a scam call. A police or national cybercrime report gives you a reference number for your bank and insurer and helps link cases.
You do not need to report a trojan that antivirus blocked before it ran. Before reporting, write down the dates, the detection name, file names and any messages or transactions linked to the attack; screenshots of antivirus alerts are useful evidence. The country list is in the report section above.
Will Fortect remove 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For 89N3PDyZzakoH7W6n8ZrjGDDktjh8iWFG6eKRvi3kvpQ, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Makeuseof: 5 Security Reasons Not to Download Cracked Software (read October 7, 2026)
- Zdnet: Google: Unwanted bundled software is way more aggressive than malware (read October 7, 2026)
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 7, 2026)
- Microsoft Learn: How Microsoft names malware (read October 7, 2026)